Linux Security Hardening: firewalld, ufw, iptables, nftables, fail2ban, SELinux, AppArmor and auditd
A server on the internet is attacked within minutes: bots try SSH passwords, scan ports and look for old software. Hardening means closing every door you do not need and watching the ones you keep. This chapter teaches host firewalls (firewalld, ufw, iptables, nftables), fail2ban to block brute force, SSH hardening, SELinux and AppArmor to limit what a hacked app can do, and auditd to record who changed what.
What you'll learn in this chapter
- Open only needed ports with firewalld or ufw
- Read and write iptables and nftables rules
- Block brute force with fail2ban
- Harden SSH and updates
- Fix SELinux and AppArmor denials safely
- Audit file changes with auditd
1. An everyday example: securing your housing society
Why do we need this?
Your society in Kothrud has one main gate with a watchman, a register for visitors, a rule that delivery boys cannot go above the ground floor, and a CCTV that records the lift. If someone keeps trying wrong flat numbers, the watchman stops letting him in for the day.
What is it?
Main gate = firewall (only needed ports). Watchman blocking the repeat offender = fail2ban. Delivery-boy floor rule = SELinux/AppArmor (an app may only touch its own files). CCTV = auditd. Visitor register = logs.
How to do it (step by step)
2. Updates and the attack surface
Why do we need this?
Most break-ins use old, known bugs. Fewer running services = fewer doors.
What is it?
Update regularly: dnf upgrade --security or apt upgrade. Enable automatic security updates (dnf-automatic, unattended-upgrades). List listening ports with ss -tulpn and disable services you do not use.
How to do it (step by step)
- Security updates.
sudo dnf upgrade --security -yOutput:
Upgraded: openssl-3.0.8-2 ...What it means: Patched.
- Auto on Ubuntu.
sudo apt install -y unattended-upgrades && sudo dpkg-reconfigure -plow unattended-upgradesOutput:
Automatically download and install stable updates? YesWhat it means: Daily patches.
- Remove a service.
sudo systemctl disable --now rpcbindOutput:
Removed ... rpcbind.serviceWhat it means: One door closed.
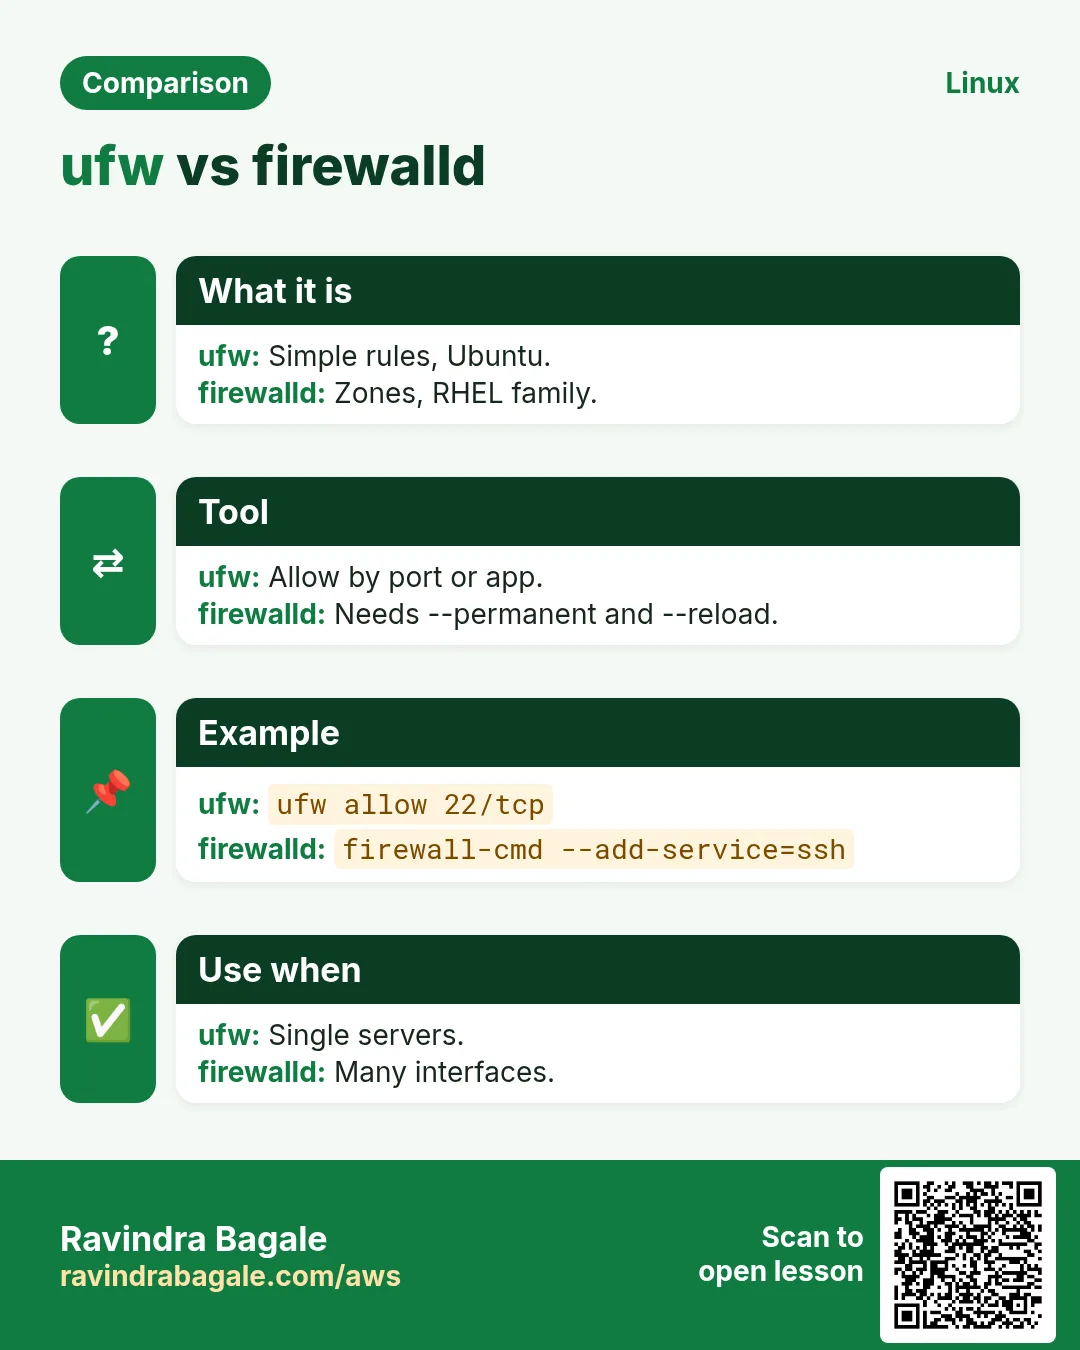
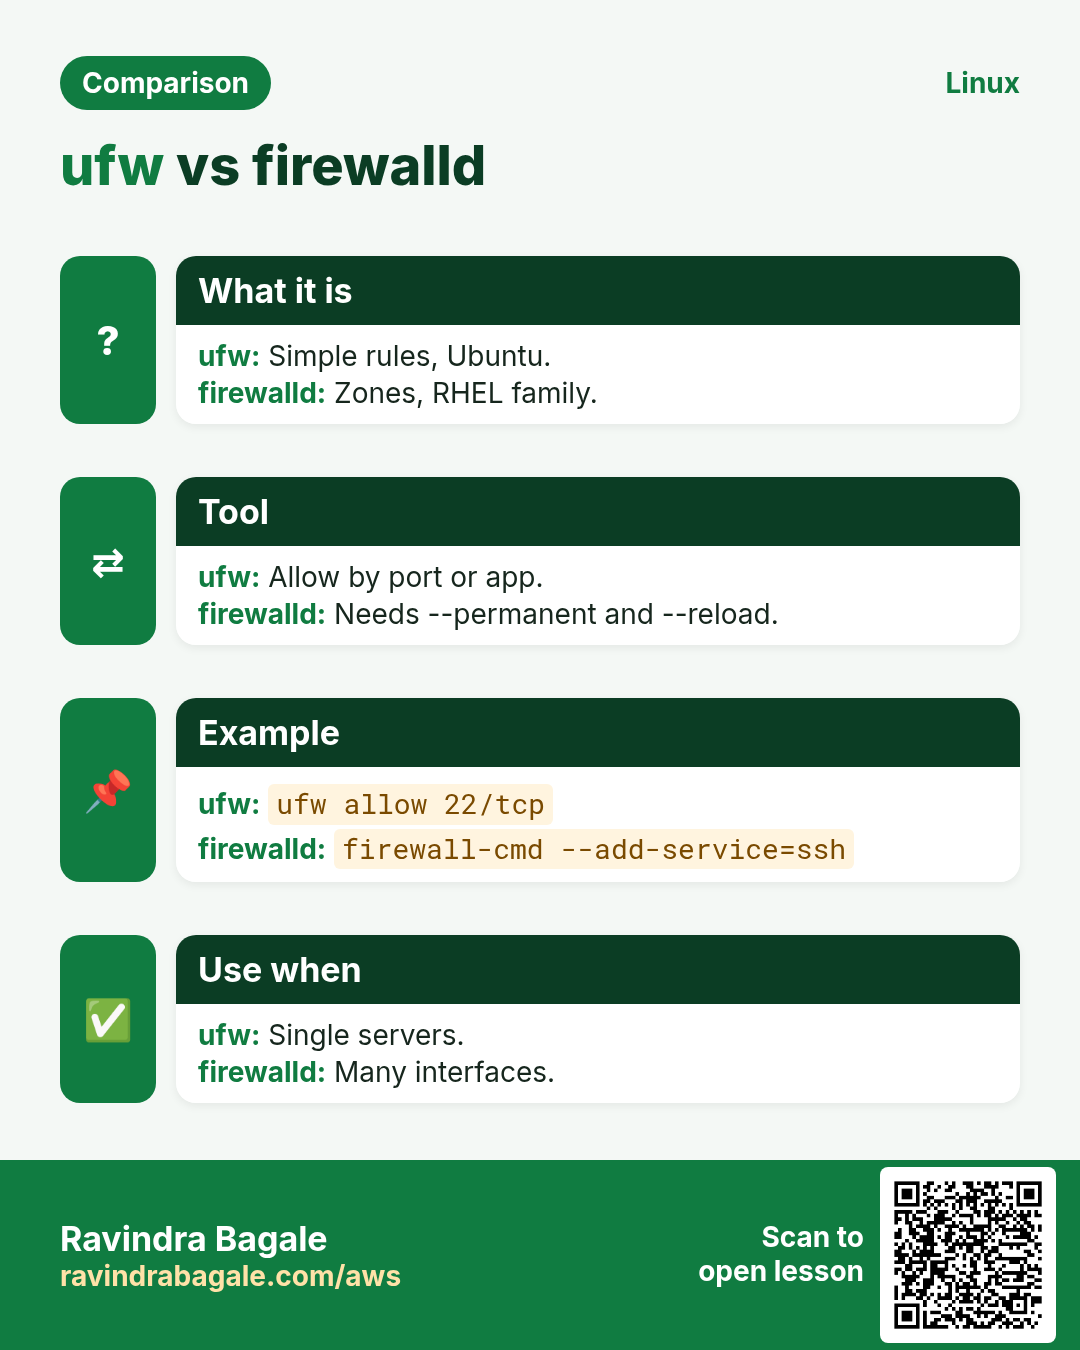
3. firewalld (RHEL, Amazon Linux, Fedora)
Why do we need this?
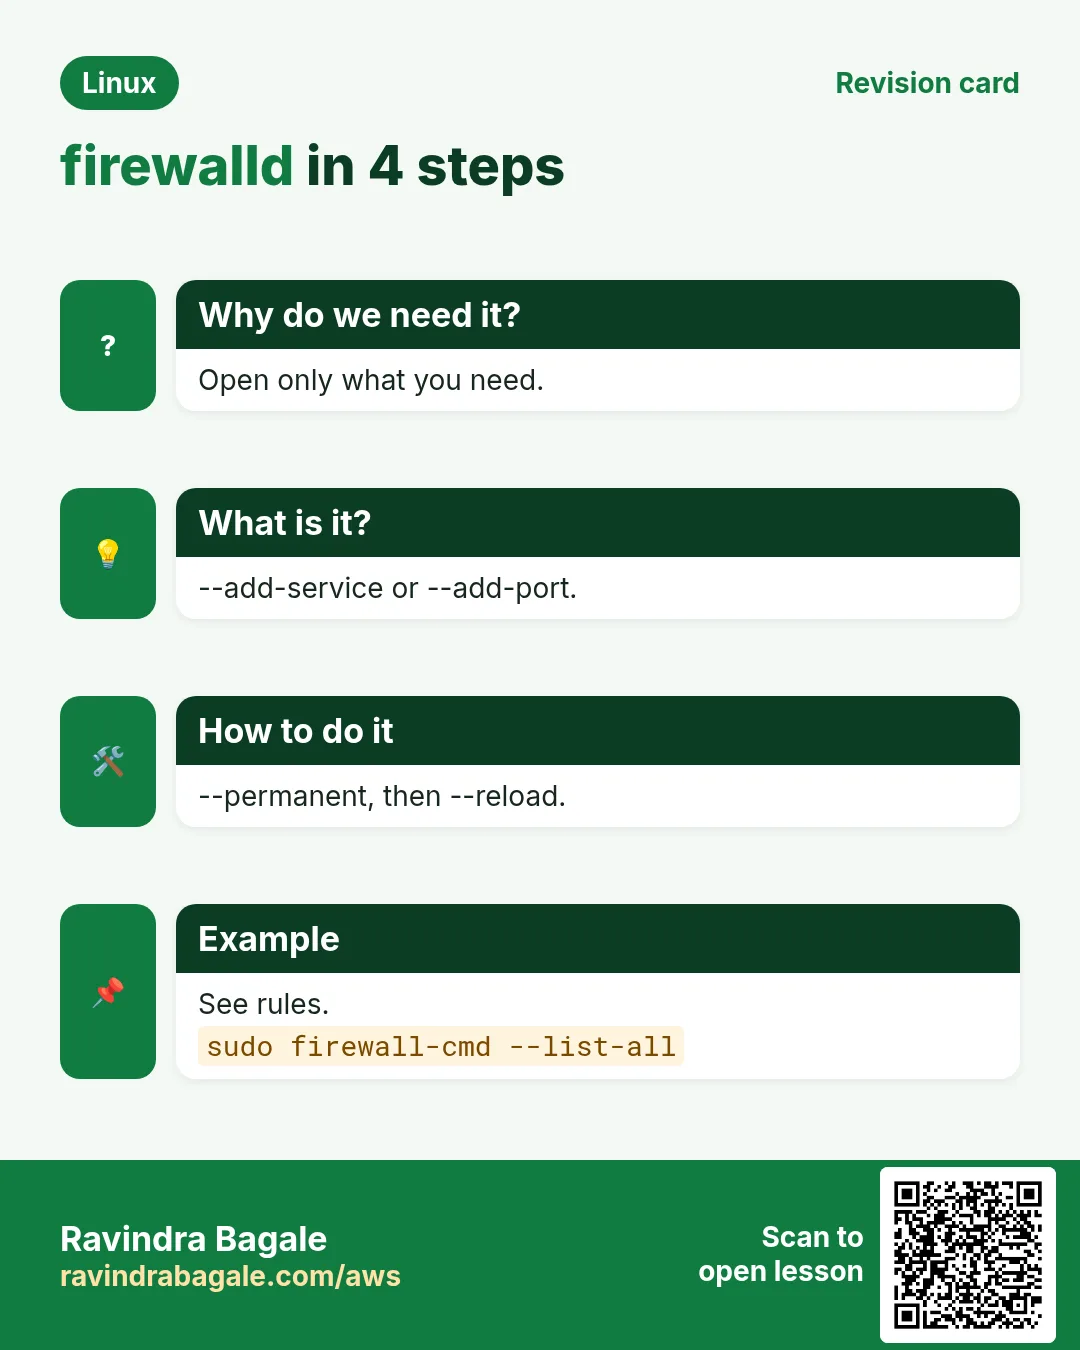
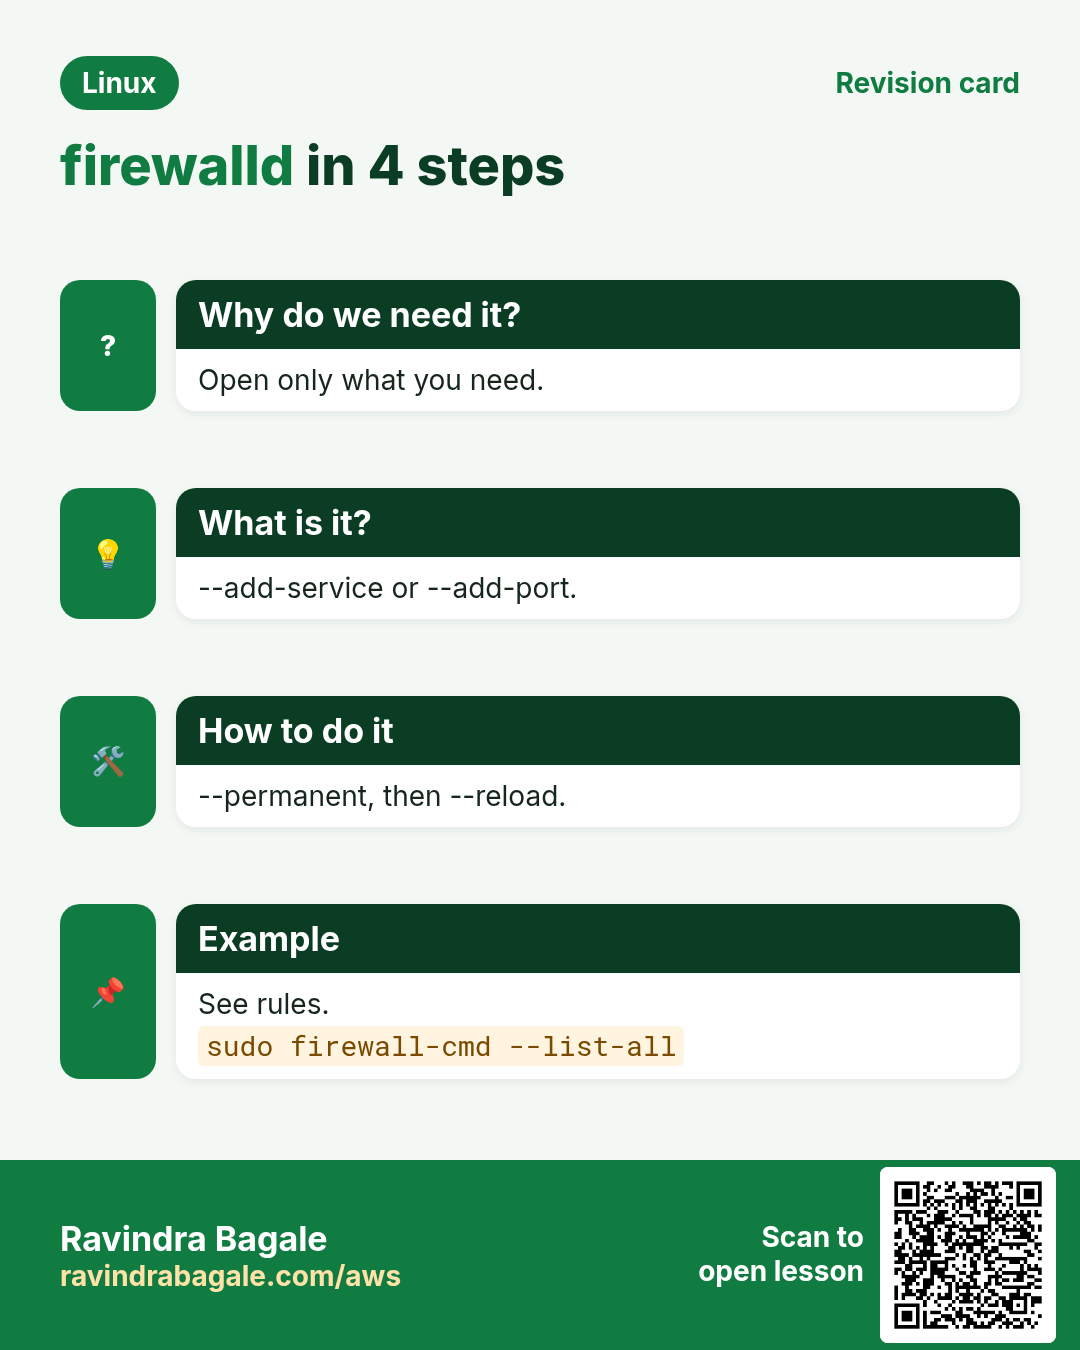
firewalld is the default host firewall on Red Hat family systems.
What is it?
Zones group rules; public is default. --add-service=http or --add-port=8443/tcp. --permanent writes to disk; then --reload. --list-all shows the zone. Rich rules allow a port only from one IP. --remove-service closes it again.
How to do it (step by step)
- State.
sudo firewall-cmd --state && sudo firewall-cmd --get-active-zonesOutput:
running
public
  interfaces: ens5
What it means: On.
- Allow web.
sudo firewall-cmd --permanent --add-service=http --add-service=https && sudo firewall-cmd --reloadOutput:
success
success
What it means: 80 and 443 open.
- Only office IP for SSH.
sudo firewall-cmd --permanent --add-rich-rule='rule family=ipv4 source address=203.0.113.10 service name=ssh accept' && sudo firewall-cmd --permanent --remove-service=ssh && sudo firewall-cmd --reloadOutput:
successWhat it means: SSH from one IP.
4. ufw (Ubuntu)
Why do we need this?
ufw is the simple firewall front end on Ubuntu and Debian.
What is it?
Allow SSH before enabling, or you lock yourself out. ufw allow OpenSSH, ufw allow 443/tcp, ufw allow from IP to any port 5432. ufw enable, ufw status numbered, ufw delete N. Default: deny incoming, allow outgoing.
How to do it (step by step)
- Safe start.
sudo ufw allow OpenSSH && sudo ufw enableOutput:
Rules updated
Firewall is active and enabled on system startup
What it means: SSH kept.
- DB from app only.
sudo ufw allow from 10.0.2.15 to any port 5432 proto tcpOutput:
Rule addedWhat it means: Least access.
- Review.
sudo ufw status numberedOutput:
[ 1] OpenSSH ALLOW IN Anywhere
[ 2] 5432/tcp ALLOW IN 10.0.2.15
What it means: Delete by number.
5. iptables: the classic rules
Why do we need this?
Many old scripts, Docker and Kubernetes still use iptables, so you must read it.
What is it?
Tables (filter, nat) hold chains (INPUT, OUTPUT, FORWARD). Rules are checked top to bottom; first match wins. -A appends, -I inserts at top, -D deletes. -j ACCEPT/DROP/REJECT. Save with iptables-save; restore with iptables-restore.
How to do it (step by step)
- Read with numbers.
sudo iptables -L INPUT -n --line-numbersOutput:
1 ACCEPT tcp -- 0.0.0.0/0 0.0.0.0/0 tcp dpt:22
2 DROP   all -- 0.0.0.0/0 0.0.0.0/0
What it means: Order matters.
- Block an attacker.
sudo iptables -I INPUT -s 198.51.100.7 -j DROPOutput:
(no output)What it means: Top of the chain.
- Save.
sudo iptables-save | sudo tee /etc/sysconfig/iptablesOutput:
*filter
:INPUT ACCEPT ...
What it means: Survives reboot (with iptables-services).
6. nftables: the modern replacement
Why do we need this?
New distros use nftables underneath firewalld and iptables-nft.
What is it?
One tool, nft, for IPv4 and IPv6. Tables of a family (inet = both), chains with a hook and policy, and rules. nft list ruleset shows everything. Config in /etc/nftables.conf; load with nft -f. Sets let one rule match many IPs.
How to do it (step by step)
- Create a table and chain.
sudo nft add table inet web && sudo nft add chain inet web input '{ type filter hook input priority 0; policy accept; }'Output:
(no output)What it means: Ready for rules.
- Allow 443.
sudo nft add rule inet web input tcp dport 443 acceptOutput:
(no output)What it means: Added.
- Blocklist set.
sudo nft add set inet web bad '{ type ipv4_addr; }' && sudo nft add element inet web bad '{ 198.51.100.7 }' && sudo nft insert rule inet web input ip saddr @bad dropOutput:
(no output)What it means: One rule, many IPs.
7. SSH hardening
Why do we need this?
SSH is the most attacked port on any Linux server.
What is it?
In /etc/ssh/sshd_config.d/10-hard.conf: PermitRootLogin no, PasswordAuthentication no, KbdInteractiveAuthentication no, MaxAuthTries 3, AllowUsers deploy, ClientAliveInterval 300. Test with sshd -t, then reload. Keep a second session open while testing.
How to do it (step by step)
- Test config.
sudo sshd -t && echo OKOutput:
OKWhat it means: No syntax errors.
- Effective values.
sudo sshd -T | grep -E 'permitrootlogin|passwordauthentication'Output:
permitrootlogin no
passwordauthentication no
What it means: Applied.
- Reload.
sudo systemctl reload sshdOutput:
(no output)What it means: Existing sessions stay.
8. fail2ban: block brute force
Why do we need this?
Thousands of failed SSH logins per day fill logs and risk weak accounts.
What is it?
fail2ban reads logs, counts failures per IP and adds a firewall ban. Configure in /etc/fail2ban/jail.local (never edit jail.conf): [sshd] enabled = true, maxretry = 5, findtime = 10m, bantime = 1h. fail2ban-client status sshd shows bans; set sshd unbanip IP removes one.
How to do it (step by step)
- Install.
sudo dnf install -y fail2ban && sudo systemctl enable --now fail2banOutput:
Created symlink ... fail2ban.serviceWhat it means: Running.
- Jail status.
sudo fail2ban-client status sshdOutput:
Currently failed: 3
Total banned: 41
Banned IP list: 198.51.100.7 ...
What it means: Working.
- Unban yourself.
sudo fail2ban-client set sshd unbanip 203.0.113.10Output:
1What it means: Removed.
9. SELinux: modes, labels, booleans
Why do we need this?
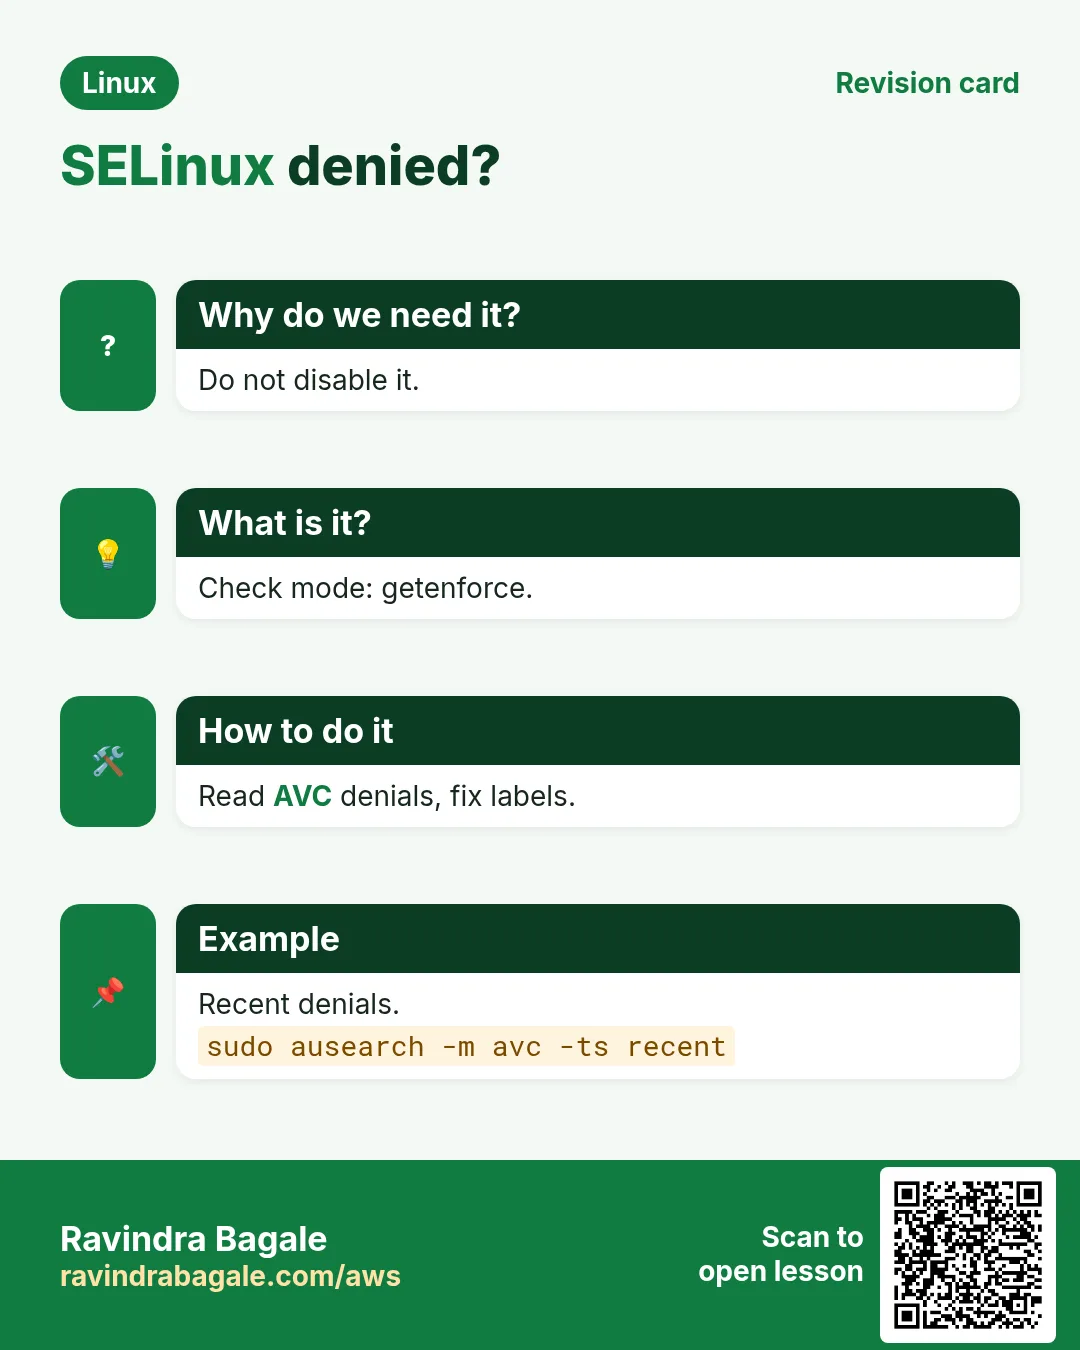
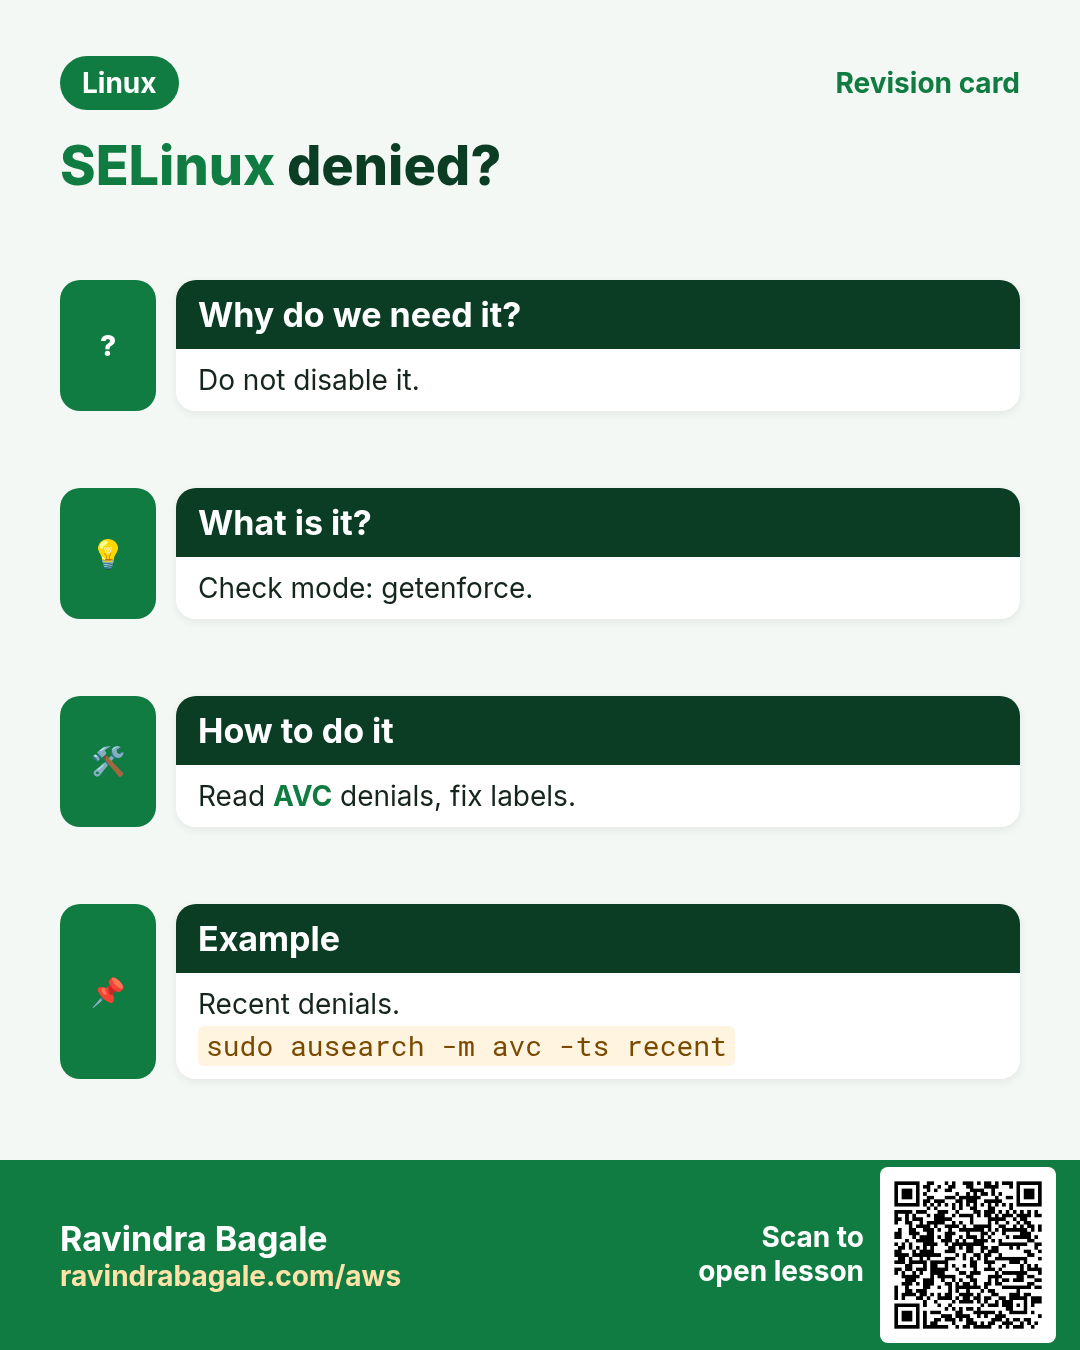
SELinux stops a hacked web server from reading /etc/shadow, but it also blocks wrong setups. Learn to fix it, not disable it.
What is it?
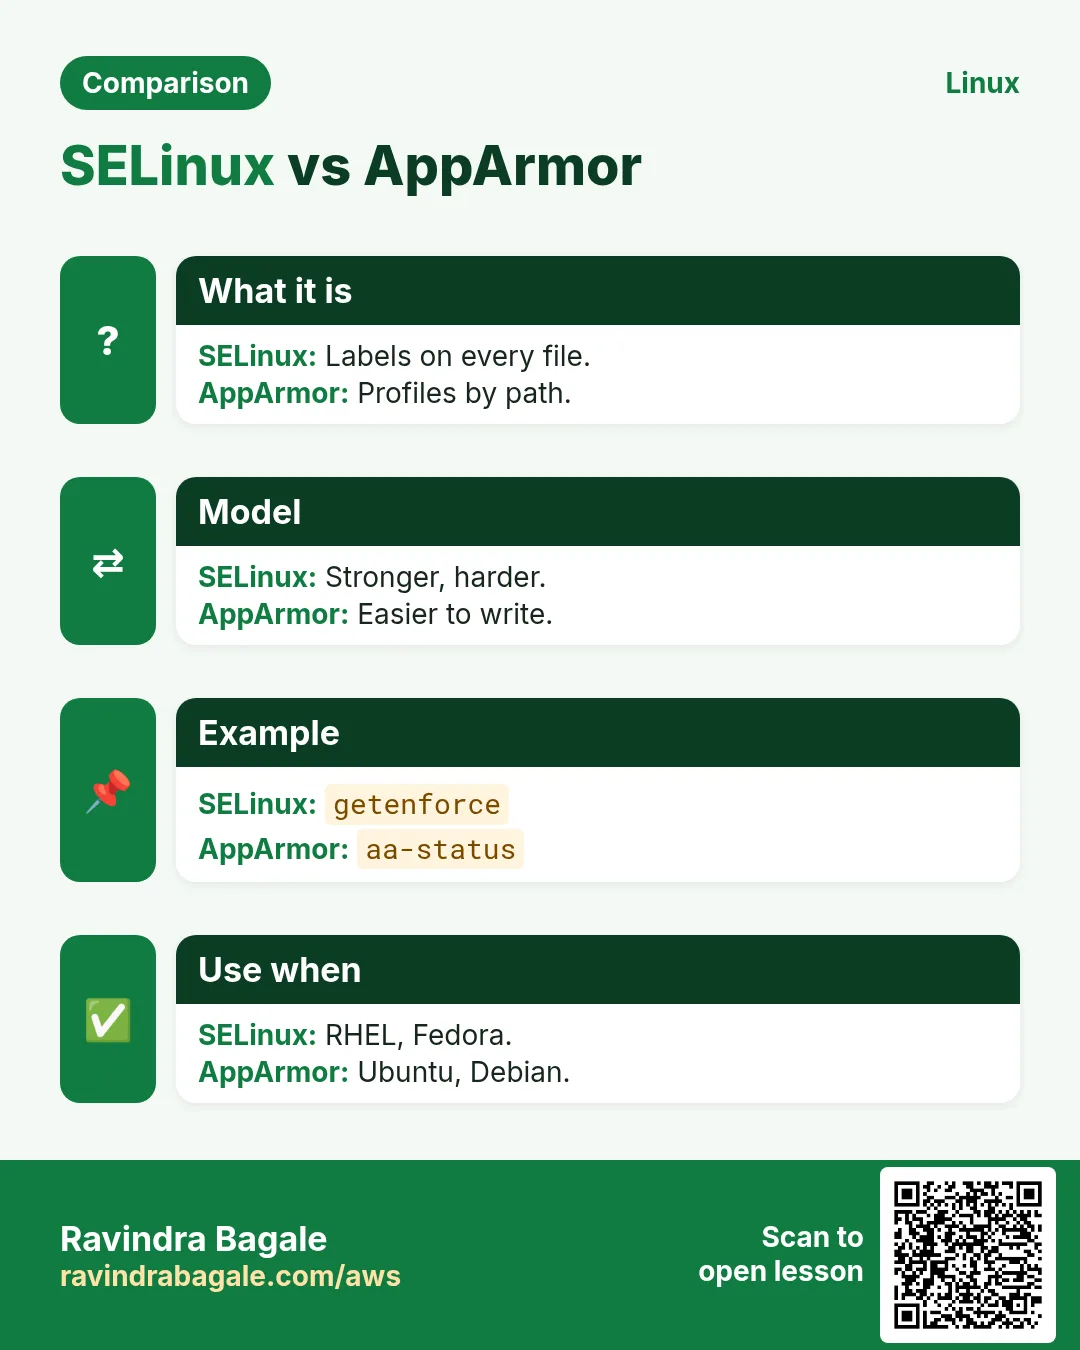
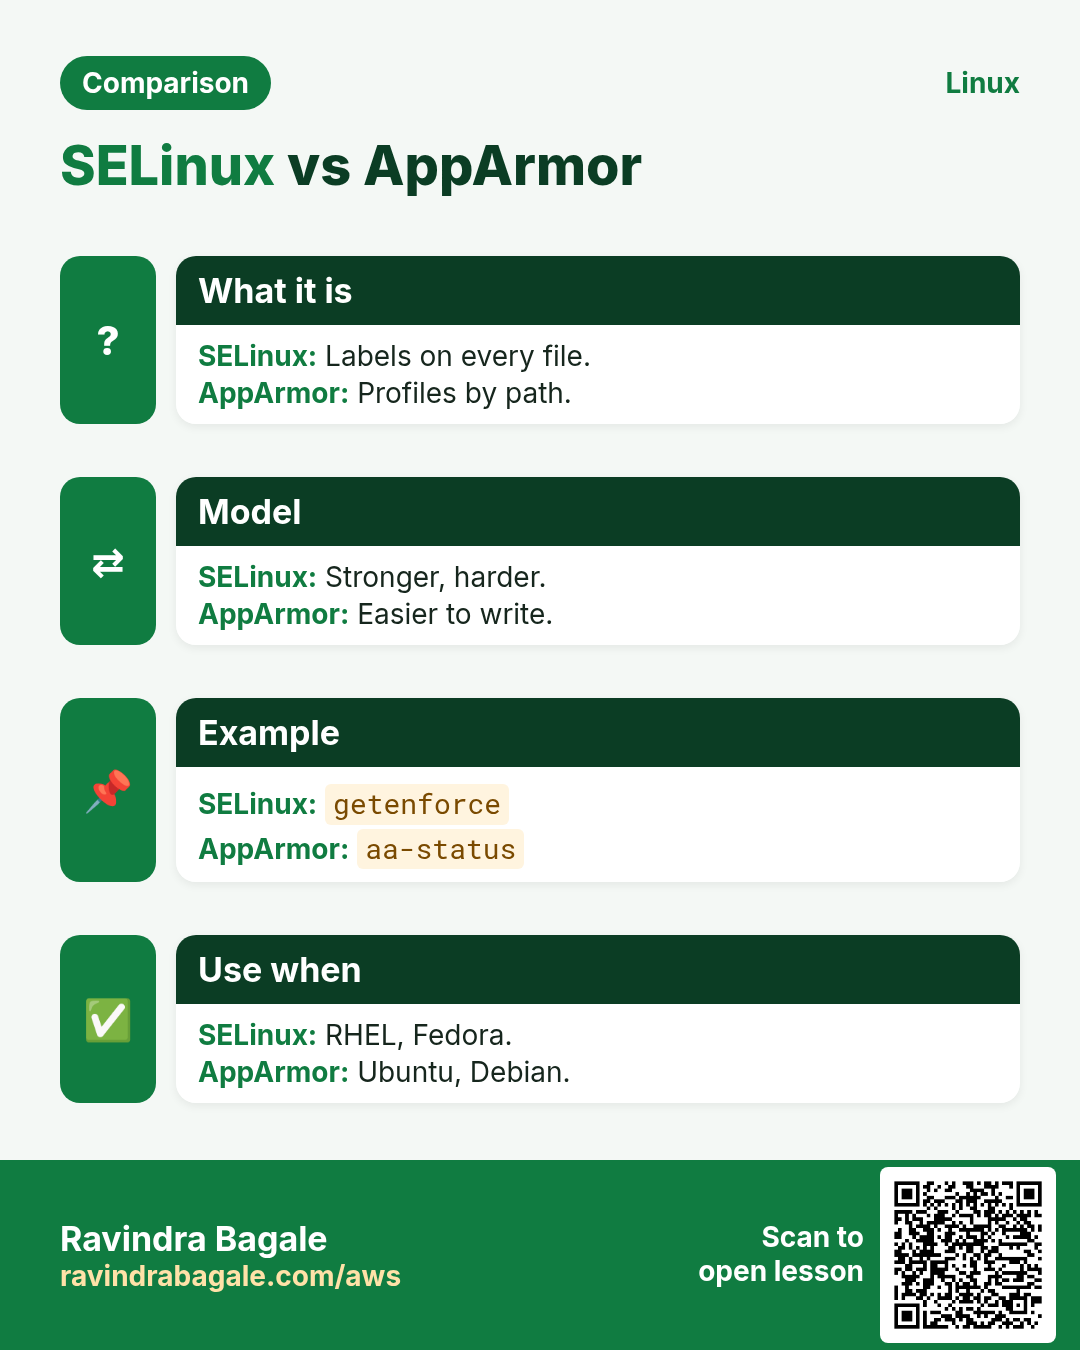
getenforce shows Enforcing, Permissive or Disabled. Every file and process has a label (ls -Z, ps -Z). A denial is logged as AVC in /var/log/audit/audit.log. Fixes: restorecon -Rv PATH (reset labels), semanage fcontext to add a rule, setsebool -P to turn on a boolean, semanage port -a for a new port. ausearch -m avc -ts recent and audit2why explain denials.
How to do it (step by step)
- Mode.
getenforceOutput:
EnforcingWhat it means: Good.
- Why 403?
sudo ausearch -m avc -ts recent | audit2whyOutput:
type=AVC ... comm="nginx" name="index.html" scontext=httpd_t tcontext=user_home_t
 Was caused by: Missing type enforcement
What it means: Wrong label.
- Label a new web folder.
sudo semanage fcontext -a -t httpd_sys_content_t '/srv/www(/.*)?' && sudo restorecon -Rv /srv/wwwOutput:
Relabeled /srv/www/index.html from default_t to httpd_sys_content_tWhat it means: Fixed for good.
- Allow app to call network.
sudo setsebool -P httpd_can_network_connect onOutput:
(no output)What it means: Proxy to backend works.
10. AppArmor (Ubuntu, SUSE)
Why do we need this?
Ubuntu uses AppArmor profiles per program instead of SELinux labels.
What is it?
aa-status lists profiles in enforce or complain mode. Profiles live in /etc/apparmor.d. Denials show in journalctl -k as apparmor="DENIED". aa-complain PROFILE logs without blocking for testing; aa-enforce turns blocking back on. Edit the profile, then apparmor_parser -r FILE.
How to do it (step by step)
- Status.
sudo aa-status | head -4Output:
apparmor module is loaded.
41 profiles are loaded.
37 profiles are in enforce mode.
What it means: On.
- Find denials.
sudo journalctl -k | grep 'apparmor="DENIED"' | tail -2Output:
apparmor="DENIED" operation="open" profile="/usr/sbin/mysqld" name="/data/mysql/"What it means: New data dir.
- Reload a profile.
sudo apparmor_parser -r /etc/apparmor.d/usr.sbin.mysqldOutput:
(no output)What it means: After adding /data/mysql/ rules.
11. auditd: who changed what
Why do we need this?
Compliance (PCI, ISO, banks) and incident review need a record of changes to key files.
What is it?
auditctl -w FILE -p wa -k KEY watches writes and attribute changes. Persist rules in /etc/audit/rules.d/*.rules and load with augenrules --load. ausearch -k KEY finds events; aureport gives summaries. Logs in /var/log/audit/audit.log.
How to do it (step by step)
- Watch sudoers.
sudo auditctl -w /etc/sudoers -p wa -k sudoersOutput:
(no output)What it means: Live rule.
- Who touched it?
sudo ausearch -k sudoers -i | tail -3Output:
type=SYSCALL ... auid=ravi uid=root comm="vim" name="/etc/sudoers"What it means: auid = real login user.
- Persist.
echo '-w /etc/ssh/sshd_config -p wa -k sshcfg' | sudo tee /etc/audit/rules.d/ssh.rules && sudo augenrules --loadOutput:
No rules
enabled 1
What it means: Loaded at boot.
- Summary.
sudo aureport --login --failed | head -5Output:
Failed Login Report
1. 10/25/26 21:02 root 198.51.100.7 ssh no
What it means: Failed logins.
12. Users, sudo and file permissions checks
Why do we need this?
Weak accounts and world-writable files undo all other hardening.
What is it?
Find users with UID 0: awk -F: '$3==0' /etc/passwd. Lock unused accounts with usermod -L. Find SUID files: find / -xdev -perm -4000. Find world-writable: find / -xdev -type f -perm -0002. Check last logins with last and lastb.
How to do it (step by step)
- Extra root?
awk -F: '$3==0' /etc/passwdOutput:
root:x:0:0:root:/root:/bin/bashWhat it means: Only root: good.
- SUID list.
sudo find / -xdev -perm -4000 -type f 2>/dev/null | head -4Output:
/usr/bin/passwd
/usr/bin/sudo
/usr/bin/su
What it means: Compare with a known list.
- Bad logins.
sudo lastb | head -3Output:
admin ssh:notty 198.51.100.7 Sun Oct 25 21:01What it means: Bots.
13. Real examples from many industries
Why do we need this?
The same Linux skill shows up in every kind of company. Seeing it in many places helps you remember it.
What is it?
Each row is a made-up team. It shows who uses this and how.
How to do it (step by step)
| Team and city | How they use it | Command |
|---|---|---|
| Sameer, fintech, Pune | auditd rules for RBI audit | auditctl -w /etc/sudoers -p wa |
| Olivia, SaaS, Toronto | fail2ban on every bastion | fail2ban-client status sshd |
| Ahmed, telecom, Riyadh | nftables sets for blocklists | nft add element |
| Mei, e-commerce, Shanghai | SELinux booleans for nginx proxy | setsebool -P httpd_can_network_connect on |
| Tom, university, Melbourne | ufw on lab servers | ufw allow OpenSSH |
| Neha, hospital, Nashik | AppArmor for MySQL data dir | aa-status |
14. Common errors and how to fix them
Why do we need this?
Everyone hits these errors. Knowing the cause saves hours.
What is it?
Read the exact message first. Then match it to a row below.
How to do it (step by step)
| Error you see | Why it happens | How to fix |
|---|---|---|
ERROR: Could not load logfile ... fail2ban | Wrong backend or log path | Use backend = systemd for journald systems.sudo fail2ban-client -d |
Locked out after ufw enable | SSH not allowed first | Use the cloud console; ufw allow OpenSSH.sudo ufw allow OpenSSH |
firewall-cmd rule gone after reboot | Added without --permanent | Add with --permanent and reload.sudo firewall-cmd --runtime-to-permanent |
nginx 403 with correct permissions | SELinux label wrong | restorecon or semanage fcontext.ls -Z /srv/www |
nginx 502: connect() failed (13: Permission denied) | SELinux blocks network connect | Enable the boolean.sudo setsebool -P httpd_can_network_connect on |
ValueError: Port tcp/8081 already defined | Port already labeled | Use -m to modify.sudo semanage port -m -t http_port_t -p tcp 8081 |
apparmor="DENIED" in logs | Profile does not allow the path | Add the path and reload the profile.sudo aa-complain /usr/sbin/mysqld |
iptables: No chain/target/match by that name | Typo or missing module | Check chain name and case.sudo iptables -L -n |
Permission denied (publickey) after hardening | Passwords off but no key installed | Add key via console, then retry.sudo sshd -T | grep pubkey |
auditctl: Error sending add rule request (Operation not permitted) | Rules locked (-e 2) | Edit rules.d and reboot.sudo auditctl -s |
15. Troubleshooting step by step
Why do we need this?
When something is blocked, ask which layer blocked it.
What is it?
Go top to bottom. Stop at the first step that shows the problem.
How to do it (step by step)
- Is the port open in the host firewall?
sudo firewall-cmd --list-all- Banned by fail2ban?
sudo fail2ban-client status sshd- SELinux denial?
sudo ausearch -m avc -ts recent- AppArmor denial?
sudo journalctl -k | grep DENIED- SSH config?
sudo sshd -T- Cloud security group?
aws ec2 describe-security-groups16. Lab 1: Firewall and fail2ban
Why do we need this?
Open only web ports and ban a brute-force IP.
What is it?
A full hands-on lab. Run every step on a test Linux machine (an EC2 instance, a VM, or WSL).
How to do it (step by step)
- Allow web.
sudo firewall-cmd --permanent --add-service=https && sudo firewall-cmd --reloadOutput:
success- Install fail2ban.
sudo dnf install -y fail2banOutput:
Complete!- Jail.
printf '[sshd]\nenabled = true\nmaxretry = 3\nbantime = 15m\n' | sudo tee /etc/fail2ban/jail.localOutput:
[sshd] ...- Start.
sudo systemctl enable --now fail2banOutput:
Created symlink- Ban test IP.
sudo fail2ban-client set sshd banip 198.51.100.99 && sudo fail2ban-client status sshdOutput:
Banned IP list: 198.51.100.9917. Lab 2: Fix an SELinux denial
Why do we need this?
Serve a site from /srv/site with SELinux enforcing.
What is it?
A full hands-on lab. Run every step on a test Linux machine (an EC2 instance, a VM, or WSL).
How to do it (step by step)
- Make content.
sudo mkdir -p /srv/site && echo hi | sudo tee /srv/site/index.htmlOutput:
hi- Point nginx root to /srv/site and reload.
sudo systemctl reload nginx && curl -s -o /dev/null -w '%{http_code}\n' localhostOutput:
403- Read the denial.
sudo ausearch -m avc -ts recent | audit2whyOutput:
Missing type enforcement- Fix label.
sudo semanage fcontext -a -t httpd_sys_content_t '/srv/site(/.*)?' && sudo restorecon -Rv /srv/siteOutput:
Relabeled- Test.
curl -s localhostOutput:
hiRavindra Bagale's Tip
Before you enable any firewall or change sshd, keep a second SSH session open and test a new login from a third window. If the new login fails, fix it from the open session. This one habit prevents most lock-outs.
Ravindra Bagale's Tip – मराठी
कोणताही firewall enable किंवा sshd बदलण्याआधी दुसरं SSH session उघडं ठेवा आणि तिसऱ्या window मधून नवं login test करा. नवं login fail झालं तर उघड्या session मधून fix करा. ही एक सवय बहुतेक lock-outs टाळते.
Ravindra Bagale's Tip – हिंदी
कोई भी firewall enable करने या sshd बदलने से पहले दूसरा SSH session खुला रखिए और तीसरी window से नया login test कीजिए. नया login fail हो तो खुले session से ठीक कीजिए. यह एक आदत ज़्यादातर lock-outs रोकती है.
18. Frequently asked questions
Q. firewalld or ufw?
Use what the distro ships: firewalld on RHEL, ufw on Ubuntu.
Q. Do I need a host firewall in the cloud?
Yes, as a second layer to security groups.
Q. iptables or nftables?
nftables for new work; read iptables for old.
Q. Can I just disable SELinux?
No; set permissive briefly to debug, then fix.
Q. Does fail2ban replace keys?
No; use keys and fail2ban together.
Q. Change the SSH port?
Reduces noise, not real security.
Q. What is auid in audit logs?
The original login user, even after sudo.
Q. How often to patch?
Security updates weekly or automatic.
19. Interview questions and answers
Beginner level
Q. Check SELinux mode?
getenforce.
Q. Allow HTTPS in ufw?
ufw allow 443/tcp.
Q. Disable root SSH login?
PermitRootLogin no.
Q. What is fail2ban?
Bans IPs after failed logins.
Mid level level
Q. firewalld rule lost after reboot?
Add --permanent then --reload.
Q. nginx 403 on new folder with SELinux?
semanage fcontext + restorecon.
Q. Block one IP with iptables?
iptables -I INPUT -s IP -j DROP.
Q. Watch a file with auditd?
auditctl -w FILE -p wa -k KEY.
Senior level
Q. Harden a fresh internet server: plan?
Patch, sudo user, keys only, firewall 22/80/443, fail2ban, SELinux enforcing, auditd, monitoring.
Q. SELinux vs AppArmor?
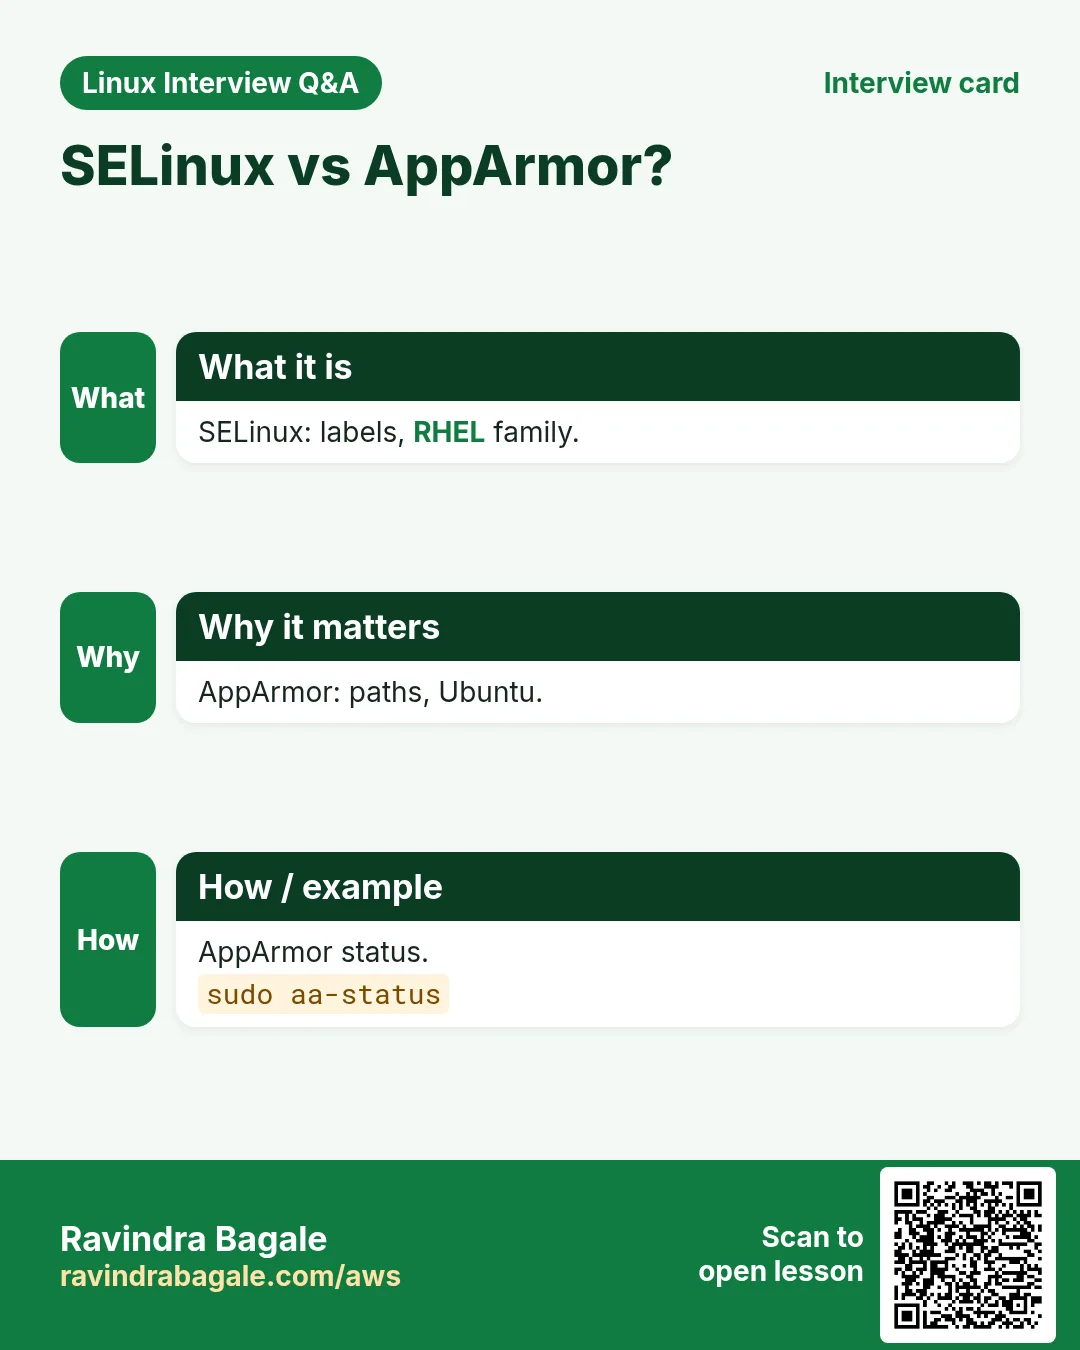
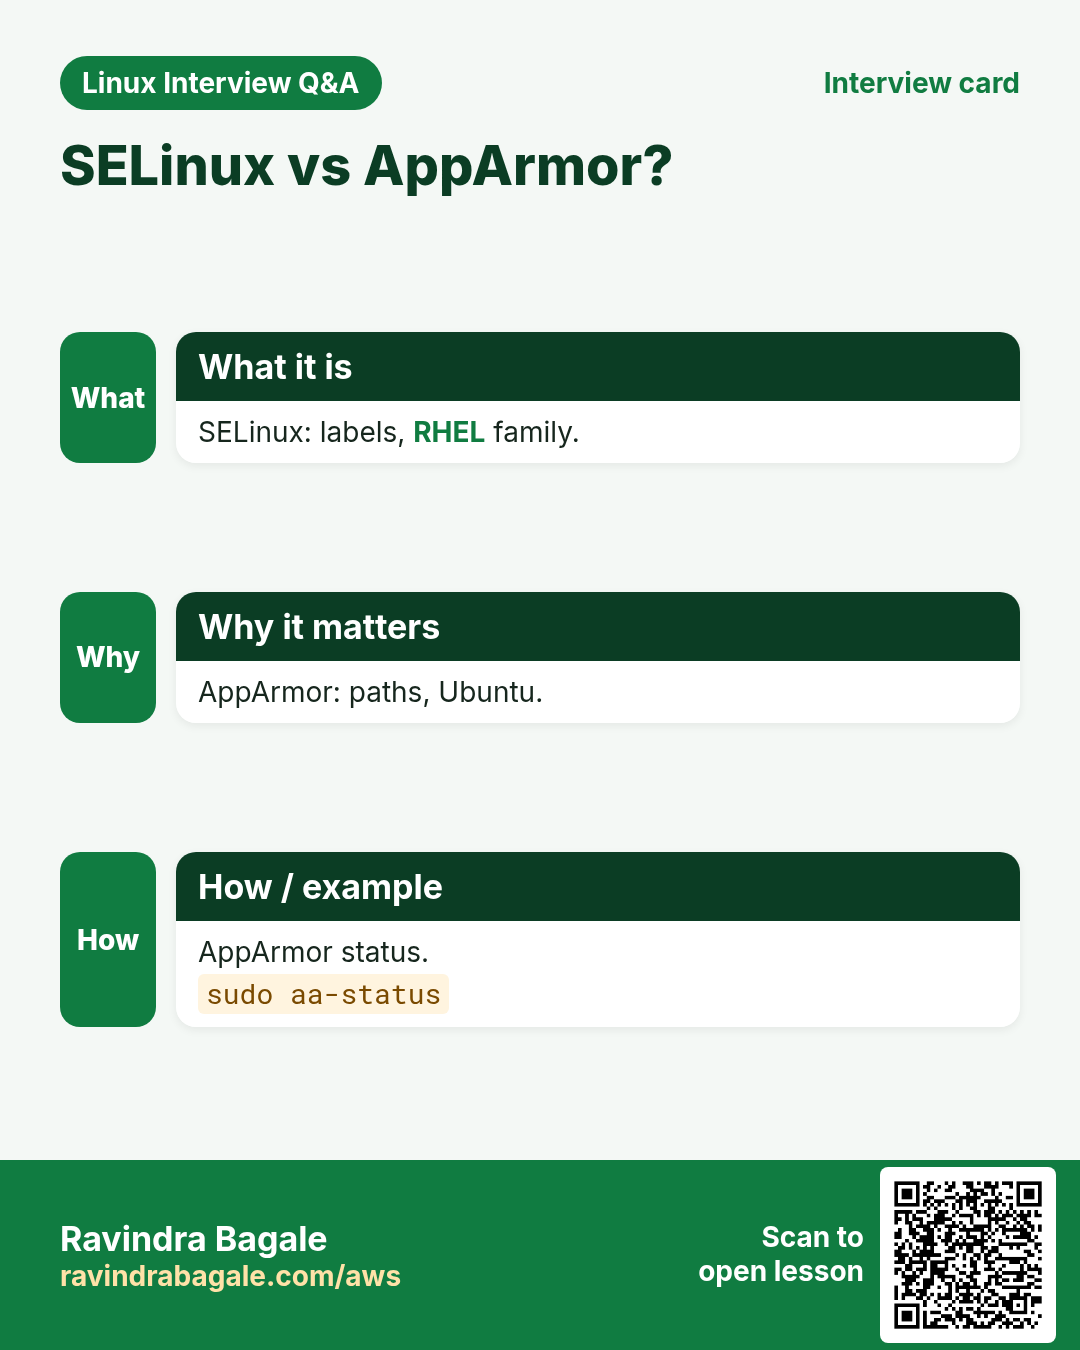
SELinux labels every object; AppArmor uses path profiles per program.
Q. Defense in depth on AWS?
SG, NACL, host firewall, IAM, SELinux, patching, logging.
Q. Prove who edited sshd_config?
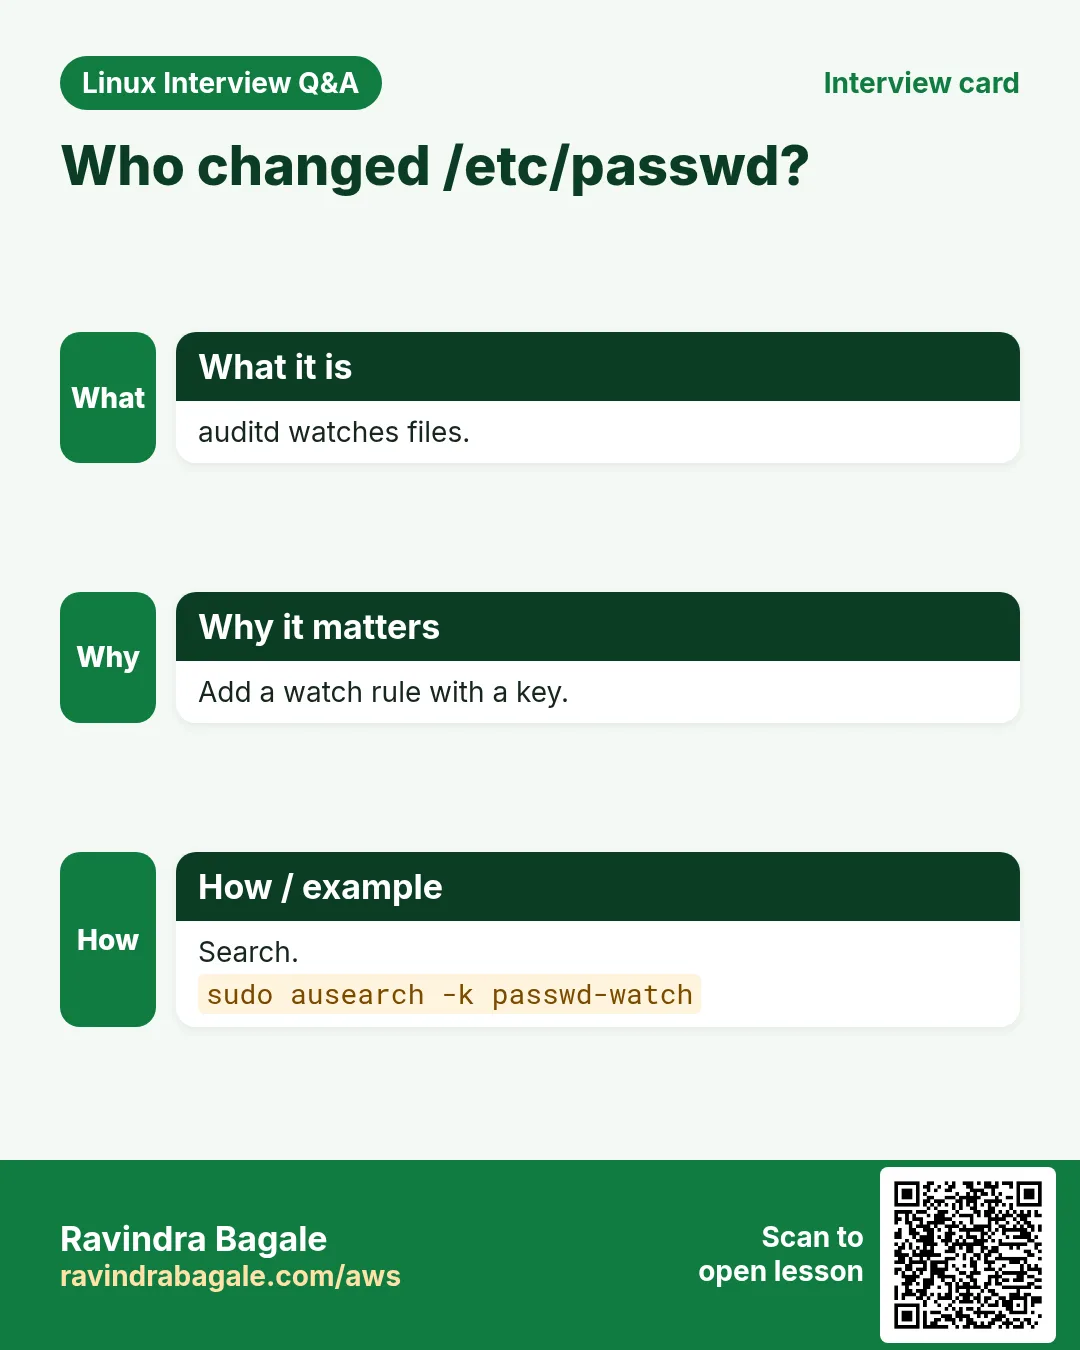
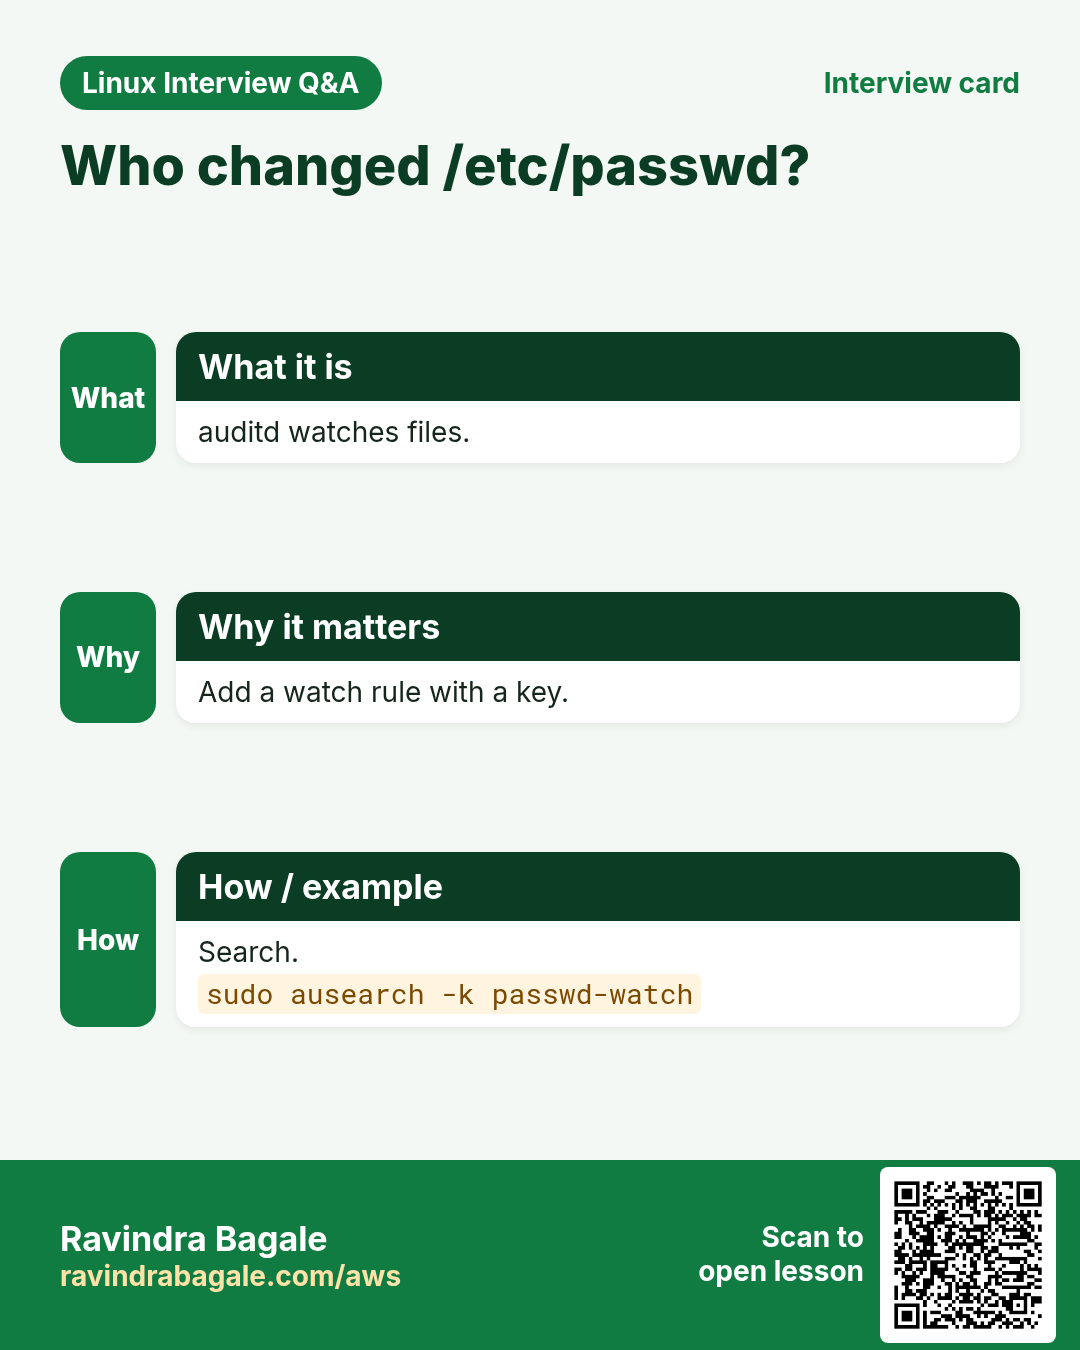
auditd watch key; ausearch -k shows auid and time.
Try at home
- On a test VM, apply the six-step hardening flow and write down every command.
- Add an auditd watch on /etc/passwd, add a user, and find the event with ausearch.
Practice Tasks
Vidarbha Cotton Mills is a textiles business in Nagpur. Ganesh Wankhede looks after its IT and cloud work. They count money in INR and run their AWS resources in the ap-south-1 Region. In the tasks below you do real jobs for them using what this lesson teaches. All names, account IDs, IP addresses and numbers are made up for practice.
0 / 20
Easy Zone rules
Why: Every open door on a BIZ server gets attacked.
What to do: Show all rules of the public zone, naming the zone.
- Find the Linux command that does this job.
- Add the options (like -r or -h) the task needs.
- Add the file names, folders or users in the right order.
- Use sudo if the job changes system files or users. Click Check answer.
Easy Reload firewalld
Why: Every open door on a BIZ server gets attacked.
What to do: Fully reload firewalld, resetting connection state too.
- Find the Linux command that does this job.
- Add the options (like -r or -h) the task needs.
- Add the file names, folders or users in the right order.
- Use sudo if the job changes system files or users. Click Check answer.
Easy Allow HTTP in ufw
Why: Every open door on a BIZ server gets attacked.
What to do: Allow TCP port 80 with ufw.
- Find the Linux command that does this job.
- Add the options (like -r or -h) the task needs.
- Add the file names, folders or users in the right order.
- Use sudo if the job changes system files or users. Click Check answer.
Easy List INPUT
Why: Every open door on a BIZ server gets attacked.
What to do: List INPUT rules numerically with line numbers, verbose.
- Find the Linux command that does this job.
- Add the options (like -r or -h) the task needs.
- Add the file names, folders or users in the right order.
- Use sudo if the job changes system files or users. Click Check answer.
Easy nft ruleset
Why: Every open door on a BIZ server gets attacked.
What to do: Show the whole nftables ruleset.
- Find the Linux command that does this job.
- Add the options (like -r or -h) the task needs.
- Add the file names, folders or users in the right order.
- Use sudo if the job changes system files or users. Click Check answer.
Easy fail2ban overview
Why: Every open door on a BIZ server gets attacked.
What to do: Show fail2ban status of the nginx-http-auth jail.
- Find the Linux command that does this job.
- Add the options (like -r or -h) the task needs.
- Add the file names, folders or users in the right order.
- Use sudo if the job changes system files or users. Click Check answer.
Easy SELinux status
Why: Every open door on a BIZ server gets attacked.
What to do: Show SELinux status plus file and process contexts.
- Find the Linux command that does this job.
- Add the options (like -r or -h) the task needs.
- Add the file names, folders or users in the right order.
- Use sudo if the job changes system files or users. Click Check answer.
Easy Search audit key
Why: Every open door on a BIZ server gets attacked.
What to do: Search audit events with key users, interpreted.
- Find the Linux command that does this job.
- Add the options (like -r or -h) the task needs.
- Add the file names, folders or users in the right order.
- Use sudo if the job changes system files or users. Click Check answer.
Easy Test sshd
Why: Every open door on a BIZ server gets attacked.
What to do: Test the sshd config file /etc/ssh/sshd_config.new.
- Find the Linux command that does this job.
- Add the options (like -r or -h) the task needs.
- Add the file names, folders or users in the right order.
- Use sudo if the job changes system files or users. Click Check answer.
Medium Open 8443
Why: Every open door on a BIZ server gets attacked.
What to do: Permanently open TCP port 8443 in firewalld.
- Find the Linux command that does this job.
- Add the options (like -r or -h) the task needs.
- Add the file names, folders or users in the right order.
- Use sudo if the job changes system files or users. Click Check answer.
Medium Close FTP
Why: Every open door on a BIZ server gets attacked.
What to do: Permanently remove the ftp service.
- Find the Linux command that does this job.
- Add the options (like -r or -h) the task needs.
- Add the file names, folders or users in the right order.
- Use sudo if the job changes system files or users. Click Check answer.
Medium Delete rule 3
Why: Every open door on a BIZ server gets attacked.
What to do: Delete ufw rule number 3.
- Find the Linux command that does this job.
- Add the options (like -r or -h) the task needs.
- Add the file names, folders or users in the right order.
- Use sudo if the job changes system files or users. Click Check answer.
Medium Drop an IP
Why: Every open door on a BIZ server gets attacked.
What to do: Insert a rule at the top dropping 192.0.2.44.
- Find the Linux command that does this job.
- Add the options (like -r or -h) the task needs.
- Add the file names, folders or users in the right order.
- Use sudo if the job changes system files or users. Click Check answer.
Medium Ban an IP
Why: Every open door on a BIZ server gets attacked.
What to do: Ban 192.0.2.55 in the sshd jail.
- Find the Linux command that does this job.
- Add the options (like -r or -h) the task needs.
- Add the file names, folders or users in the right order.
- Use sudo if the job changes system files or users. Click Check answer.
Medium Allow nginx DB
Why: Every open door on a BIZ server gets attacked.
What to do: Permanently let httpd connect to databases (httpd_can_network_connect_db).
- Find the Linux command that does this job.
- Add the options (like -r or -h) the task needs.
- Add the file names, folders or users in the right order.
- Use sudo if the job changes system files or users. Click Check answer.
Medium Relabel /var/www
Why: Every open door on a BIZ server gets attacked.
What to do: Restore SELinux labels recursively on /var/www/html, verbose.
- Find the Linux command that does this job.
- Add the options (like -r or -h) the task needs.
- Add the file names, folders or users in the right order.
- Use sudo if the job changes system files or users. Click Check answer.
Medium Watch passwd
Why: Every open door on a BIZ server gets attacked.
What to do: Add an audit watch on /etc/passwd for writes and attributes, key users.
- Find the Linux command that does this job.
- Add the options (like -r or -h) the task needs.
- Add the file names, folders or users in the right order.
- Use sudo if the job changes system files or users. Click Check answer.
Hard Redis from app
Why: Every open door on a BIZ server gets attacked.
What to do: Allow 10.0.2.20 to reach TCP port 6379 only.
- Find the Linux command that does this job.
- Add the options (like -r or -h) the task needs.
- Add the file names, folders or users in the right order.
- Use sudo if the job changes system files or users. Click Check answer.
Hard Delete rule 2
Why: Every open door on a BIZ server gets attacked.
What to do: Delete INPUT rule number 2.
- Find the Linux command that does this job.
- Add the options (like -r or -h) the task needs.
- Add the file names, folders or users in the right order.
- Use sudo if the job changes system files or users. Click Check answer.
Hard Label port 8090
Why: Every open door on a BIZ server gets attacked.
What to do: Allow httpd to use TCP 8090 via SELinux port type http_port_t.
- Find the Linux command that does this job.
- Add the options (like -r or -h) the task needs.
- Add the file names, folders or users in the right order.
- Use sudo if the job changes system files or users. Click Check answer.
20. Related chapters
- Linux Ops Refresh for DevOps
- Bash Scripting for Automation
- Linux grep and find Commands with Examples
- How to Set Up Passwordless SSH Between Linux Servers
In short
- Patch and remove unused services first.
- firewalld/ufw: allow only what you need; --permanent.
- iptables first match wins; nftables is the modern tool.
- SSH: keys only, no root; fail2ban for brute force.
- SELinux/AppArmor: fix labels and profiles, never disable.
- auditd records who changed key files.
Revision, comparison and interview cards
Revise this lesson in a few minutes. Save the cards on your phone or download them as PNG files. The QR code on each card opens this lesson.
More cards: Ravi Sir's Cards.