Ravi Sir's Cards › AWS
Secrets Manager + KMS
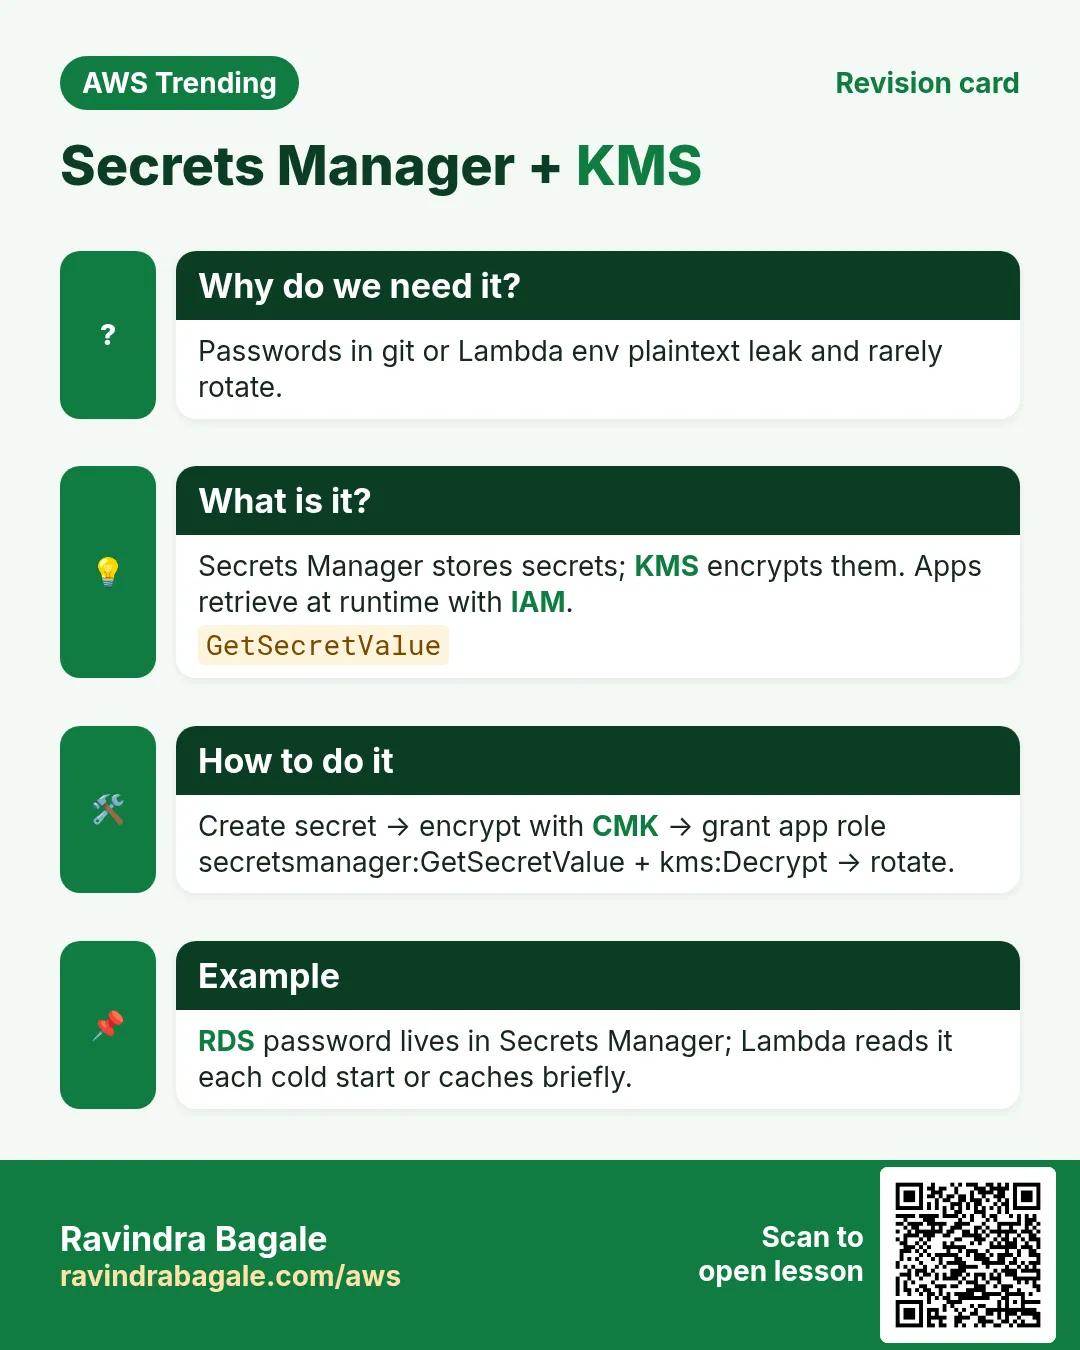
This revision card explains Secrets Manager + KMS. It starts from the need that passwords in git or Lambda env plaintext leak and rarely rotate. It describes secrets Manager stores secrets; KMS encrypts them. Apps retrieve at runtime with IAM. The how-to section covers how to create secret , then encrypt with CMK , then grant app role secretsmanager:GetSecretValue + kms:Decrypt , then rotate. An example on the card is RDS password lives in Secrets Manager; Lambda reads it each cold start or caches briefly.
Read card text
What this card says
Why do we need it?
Passwords in git or Lambda env plaintext leak and rarely rotate.
What is it?
Secrets Manager stores secrets; KMS encrypts them. Apps retrieve at runtime with IAM.
GetSecretValue
How to do it
Create secret → encrypt with CMK → grant app role secretsmanager:GetSecretValue + kms:Decrypt → rotate.
Example
RDS password lives in Secrets Manager; Lambda reads it each cold start or caches briefly.