Ravi Sir's Cards › AWS
HTTPS and OAC
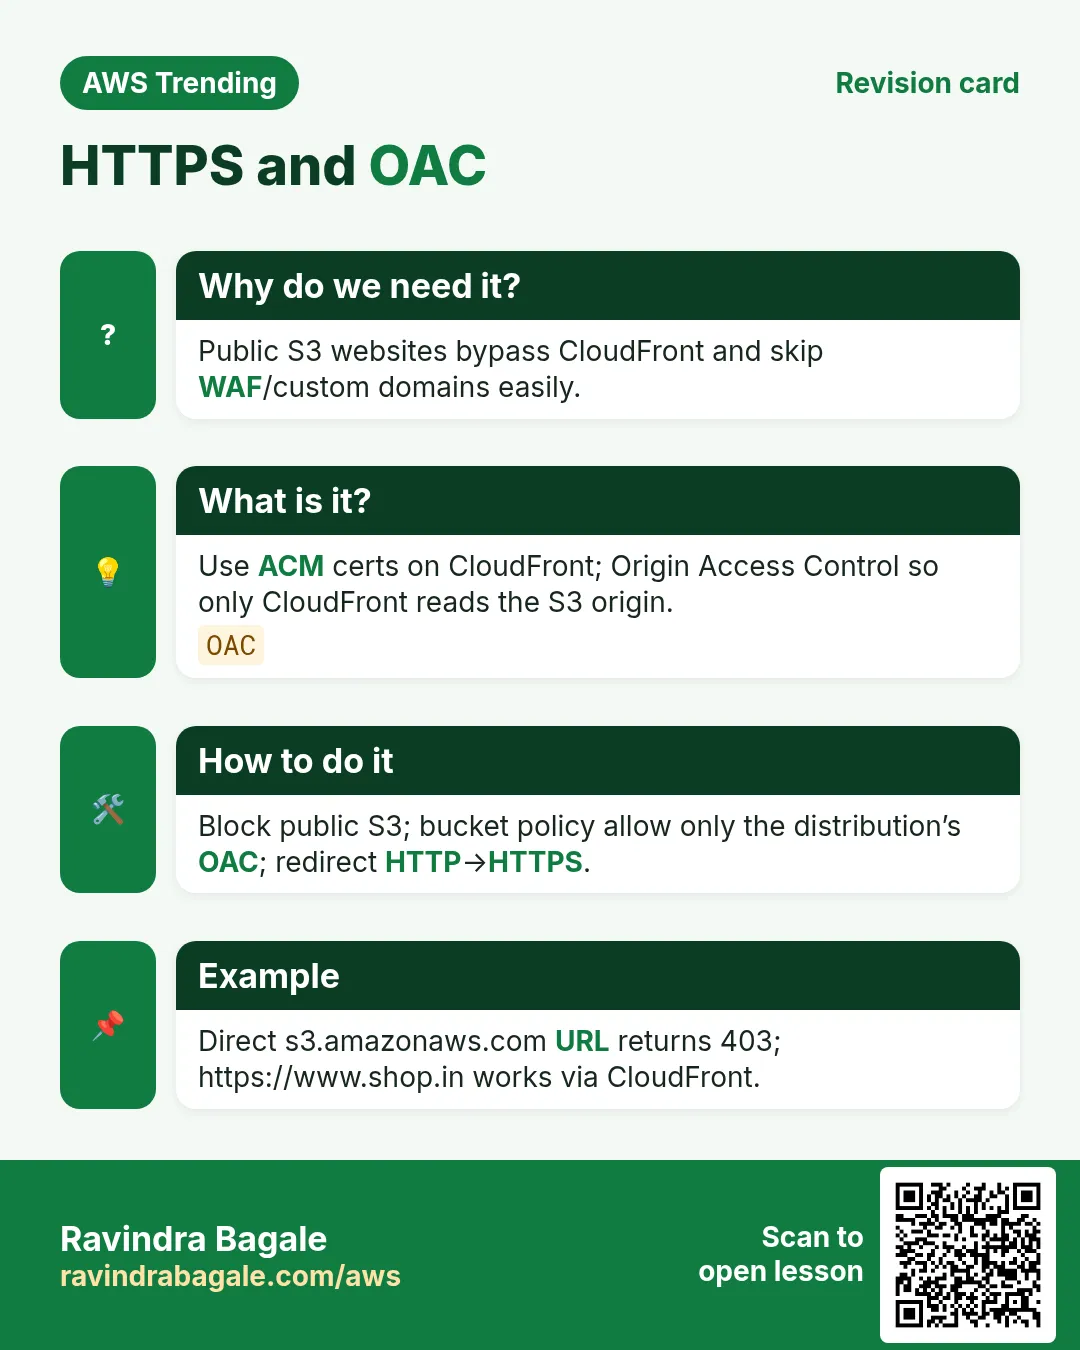
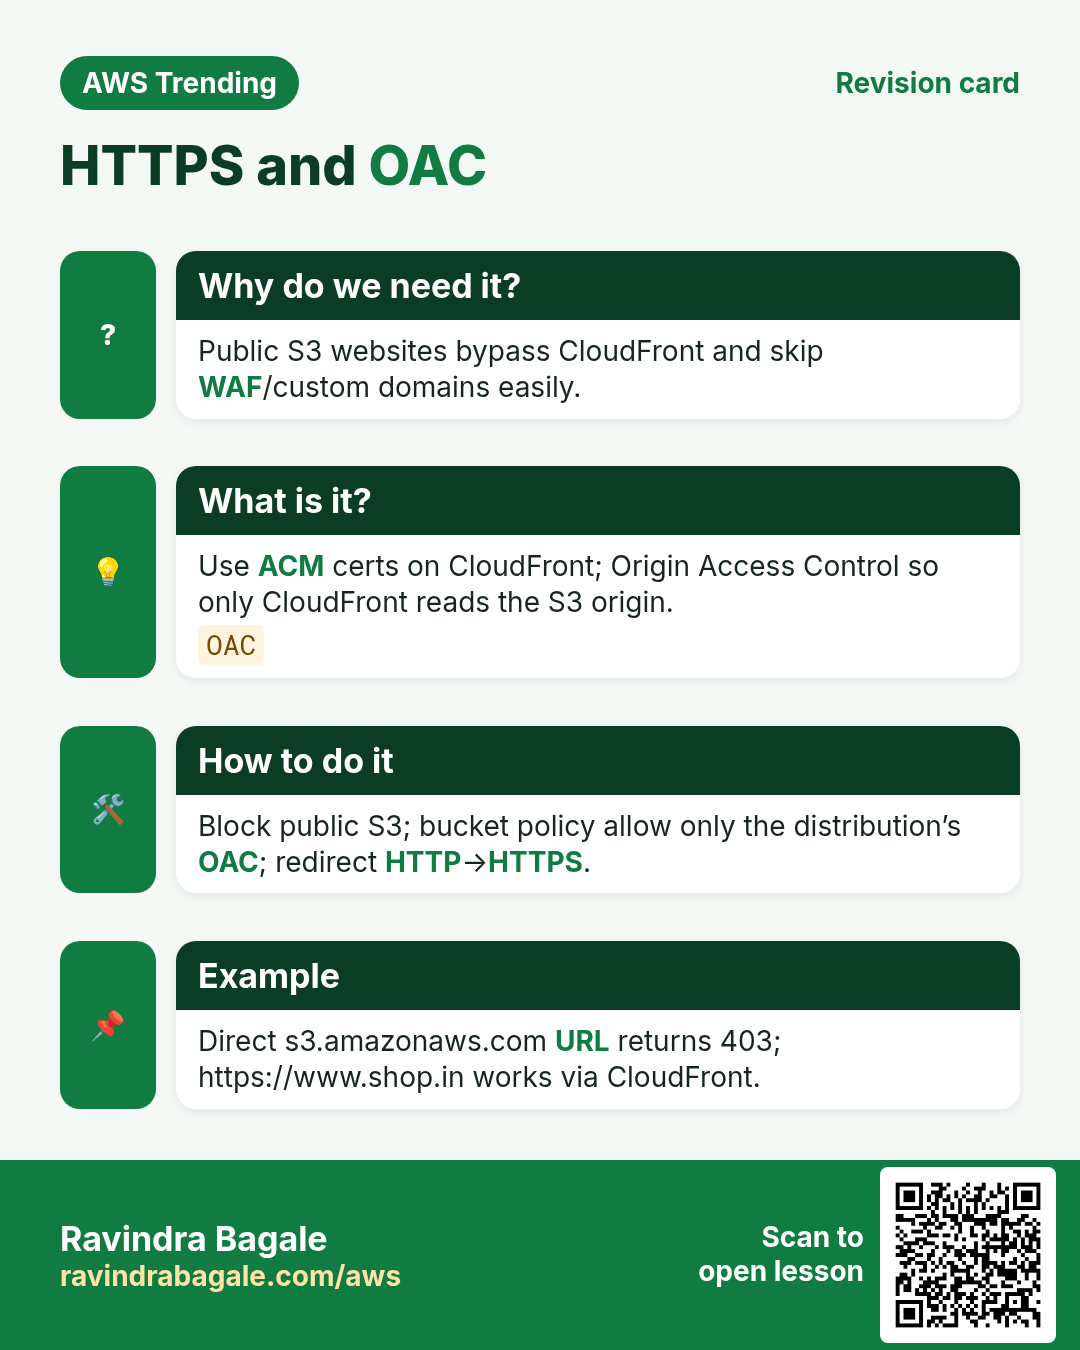
This revision card explains HTTPS and OAC. It starts from the need that public S3 websites bypass CloudFront and skip WAF/custom domains easily. It describes use ACM certs on CloudFront; Origin Access Control so only CloudFront reads the S3 origin. The how-to section notes block public S3; bucket policy allow only the distribution’s OAC; redirect HTTP, then HTTPS. An example on the card is direct s3.amazonaws.com URL returns 403; https://www.shop.in works via CloudFront.
Read card text
What this card says
Why do we need it?
Public S3 websites bypass CloudFront and skip WAF/custom domains easily.
What is it?
Use ACM certs on CloudFront; Origin Access Control so only CloudFront reads the S3 origin.
OAC
How to do it
Block public S3; bucket policy allow only the distribution’s OAC; redirect HTTP→HTTPS.
Example
Direct s3.amazonaws.com URL returns 403; https://www.shop.in works via CloudFront.