Ravi Sir's Cards › AWS
Security group for cache
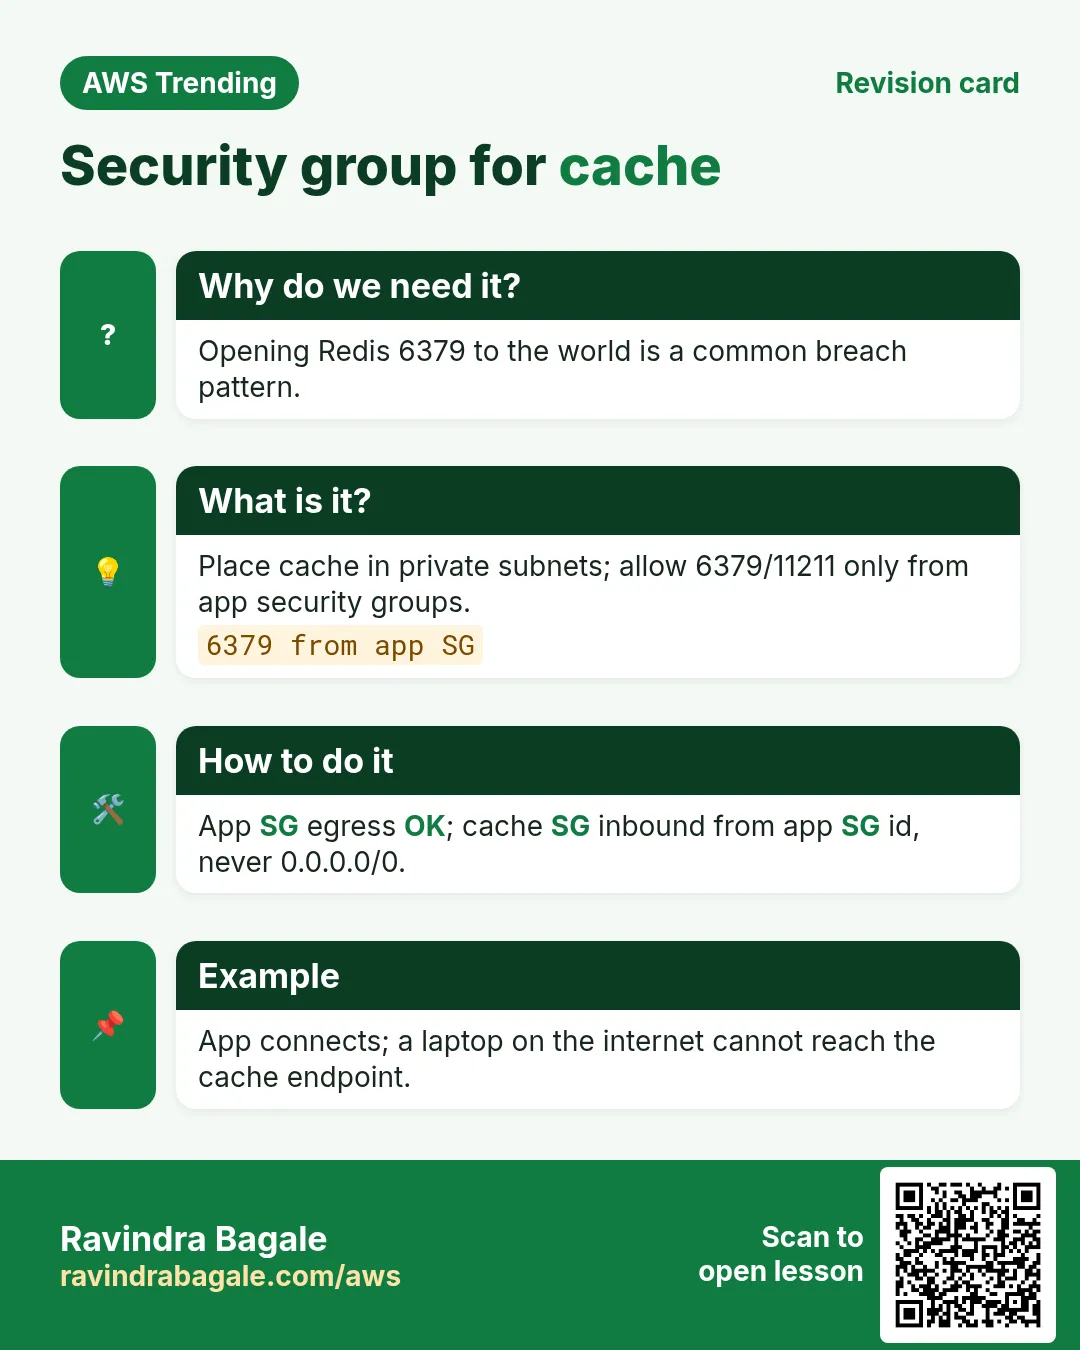
This revision card explains Security group for cache. It starts from the need that opening Redis 6379 to the world is a common breach pattern. It describes place cache in private subnets; allow 6379/11211 only from app security groups. The how-to section notes app SG egress OK; cache SG inbound from app SG id, never 0.0.0.0/0. An example on the card is app connects; a laptop on the internet cannot reach the cache endpoint.
Read card text
What this card says
Why do we need it?
Opening Redis 6379 to the world is a common breach pattern.
What is it?
Place cache in private subnets; allow 6379/11211 only from app security groups.
6379 from app SG
How to do it
App SG egress OK; cache SG inbound from app SG id, never 0.0.0.0/0.
Example
App connects; a laptop on the internet cannot reach the cache endpoint.