Ravi Sir's Cards › AWS
PrincipalOrgID fence
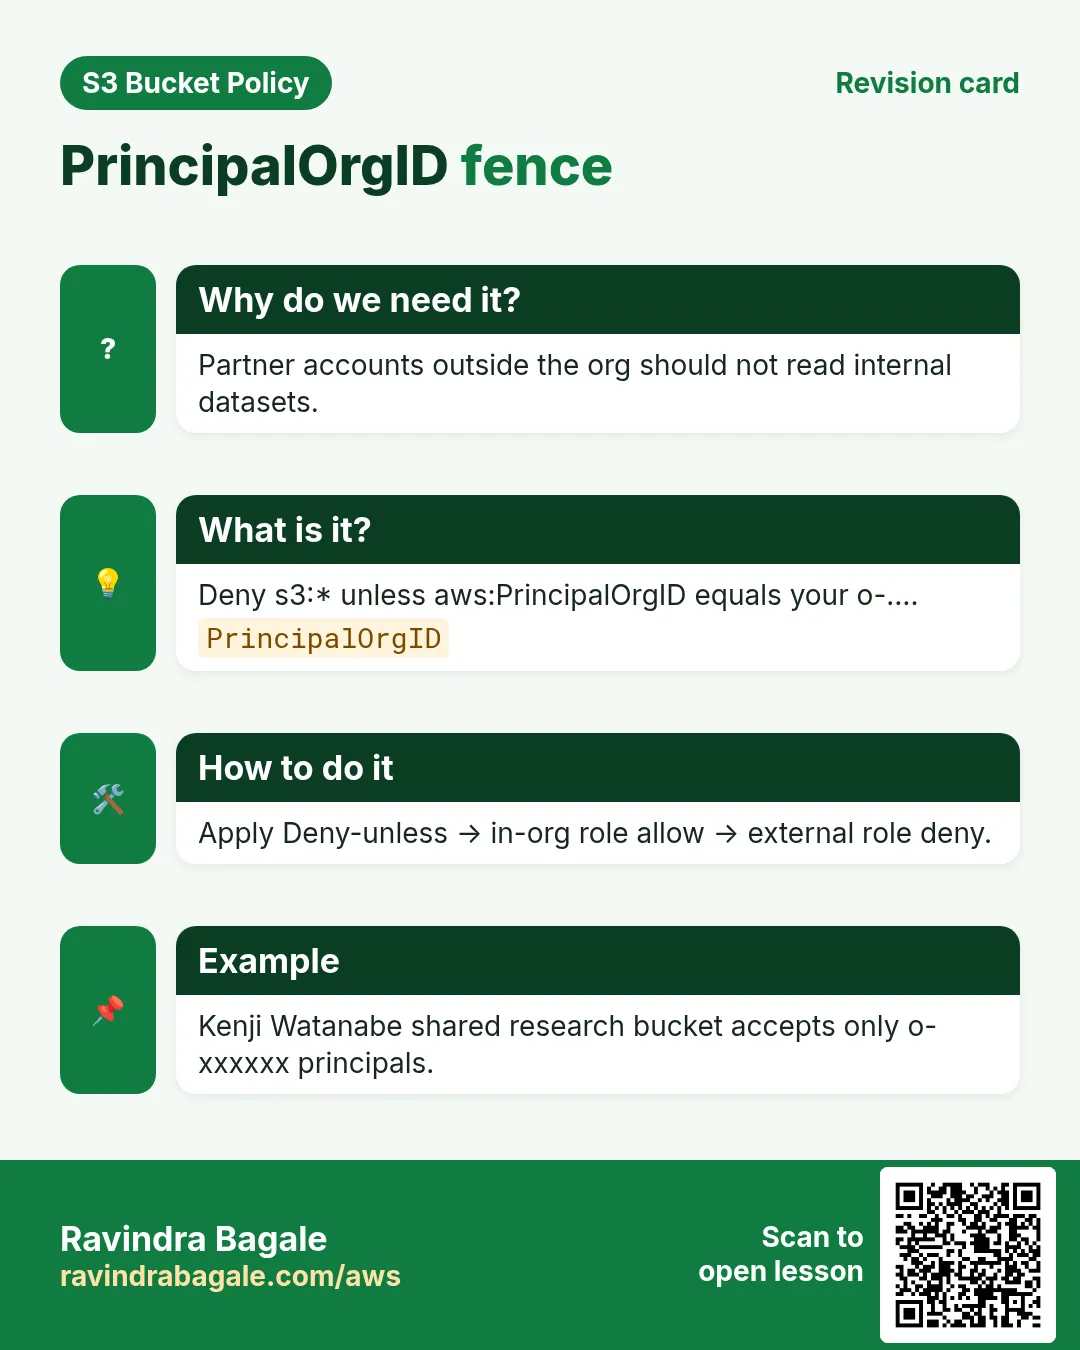
This revision card explains PrincipalOrgID fence. It starts from the need that partner accounts outside the org should not read internal datasets. It describes deny s3 — * unless aws:PrincipalOrgID equals your o-…. The how-to section notes apply Deny-unless , then in-org role allow , then external role deny. An example on the card is kenji Watanabe shared research bucket accepts only o-xxxxxx principals.
Read card text
What this card says
Why do we need it?
Partner accounts outside the org should not read internal datasets.
What is it?
Deny s3:* unless aws:PrincipalOrgID equals your o-….
PrincipalOrgID
How to do it
Apply Deny-unless → in-org role allow → external role deny.
Example
Kenji Watanabe shared research bucket accepts only o-xxxxxx principals.