Ravi Sir's Cards › AWS
Office SourceIp fence
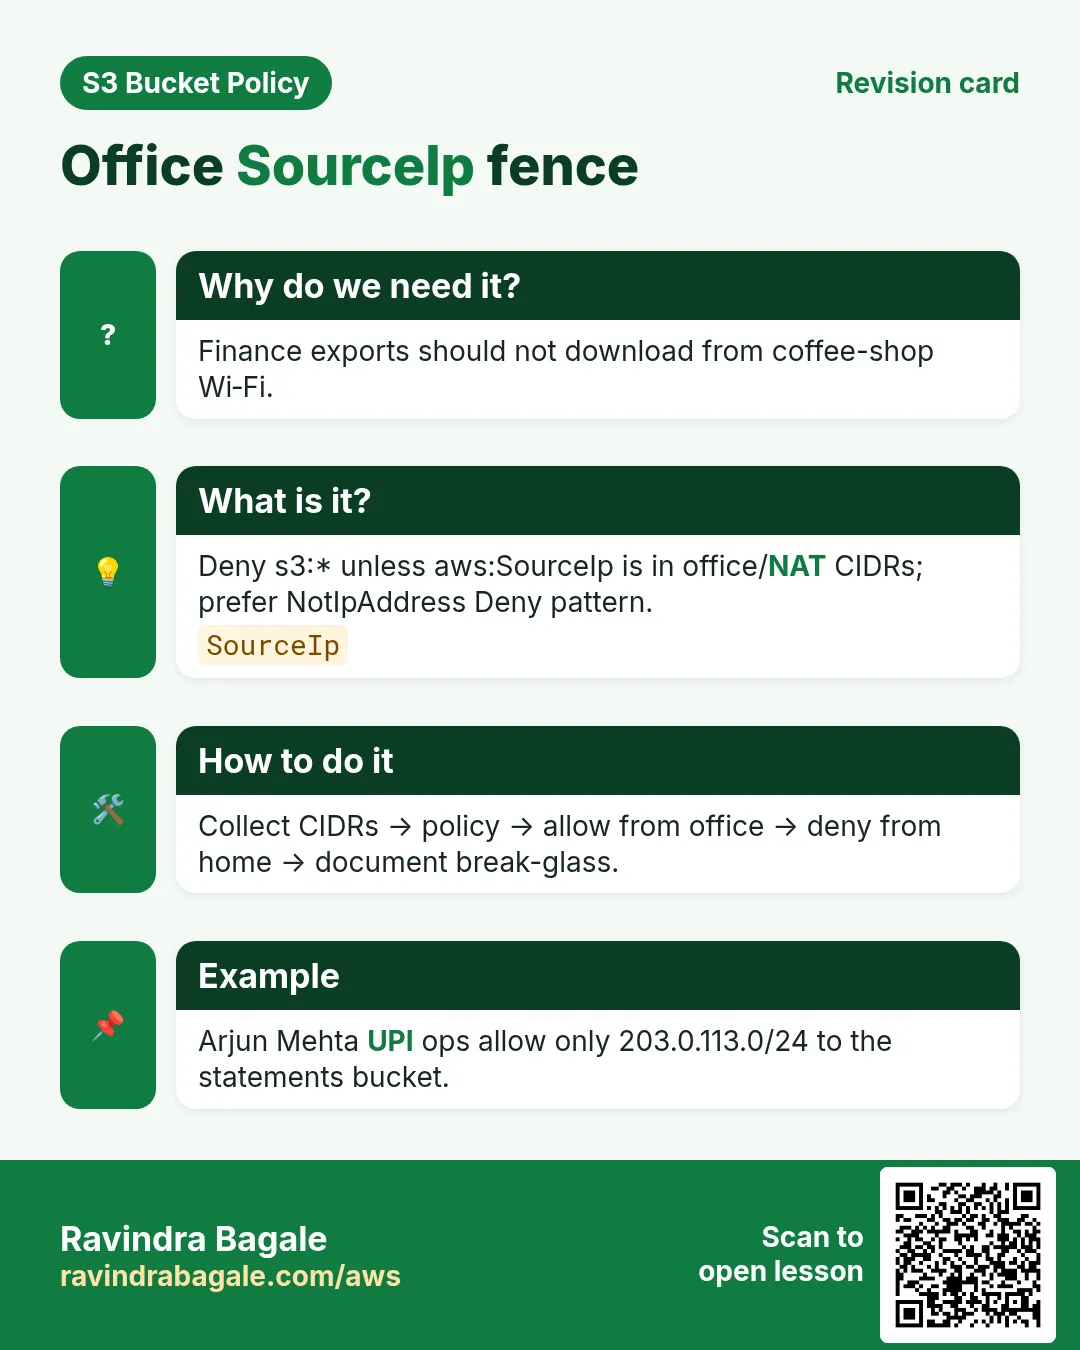
This revision card explains Office SourceIp fence. It starts from the need that finance exports should not download from coffee-shop Wi‑Fi. It describes deny s3 — * unless aws:SourceIp is in office/NAT CIDRs; prefer NotIpAddress Deny pattern. The how-to section notes collect CIDRs , then policy , then allow from office , then deny from home , then document break-glass. An example on the card is arjun Mehta UPI ops allow only 203.0.113.0/24 to the statements bucket.
Read card text
What this card says
Why do we need it?
Finance exports should not download from coffee-shop Wi‑Fi.
What is it?
Deny s3:* unless aws:SourceIp is in office/NAT CIDRs; prefer NotIpAddress Deny pattern.
SourceIp
How to do it
Collect CIDRs → policy → allow from office → deny from home → document break-glass.
Example
Arjun Mehta UPI ops allow only 203.0.113.0/24 to the statements bucket.