Ravi Sir's Cards › AWS
CloudFront OAC only
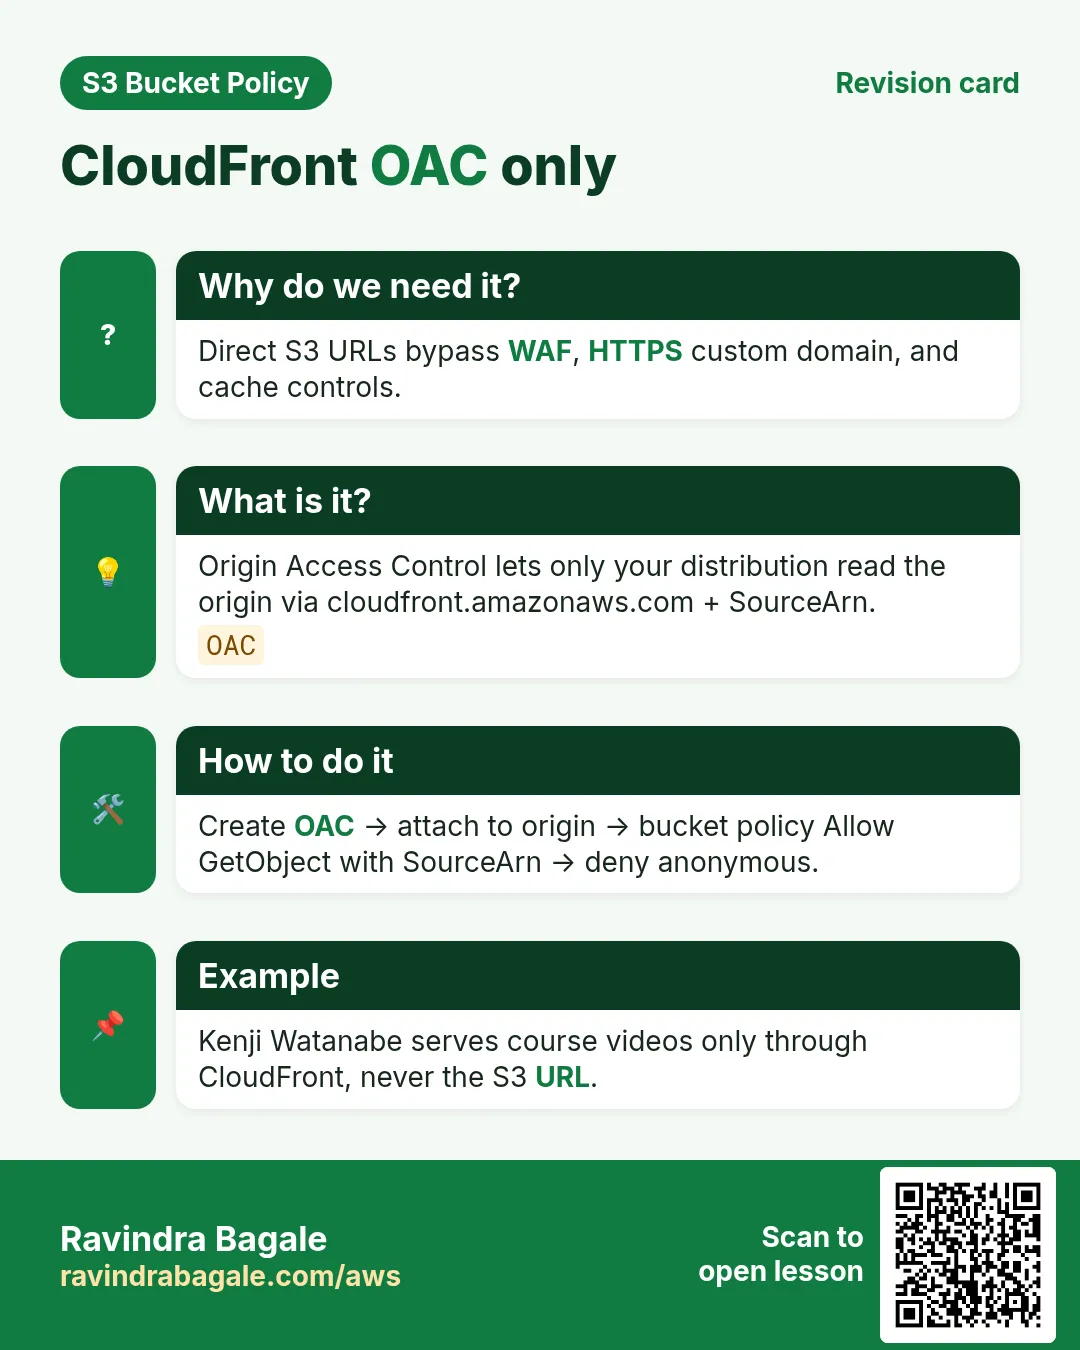
This revision card explains CloudFront OAC only. It starts from the need that direct S3 URLs bypass WAF, HTTPS custom domain, and cache controls. It describes origin Access Control lets only your distribution read the origin via cloudfront.amazonaws.com + SourceArn. The how-to section covers how to create OAC , then attach to origin , then bucket policy Allow GetObject with SourceArn , then deny anonymous. An example on the card is kenji Watanabe serves course videos only through CloudFront, never the S3 URL.
Read card text
What this card says
Why do we need it?
Direct S3 URLs bypass WAF, HTTPS custom domain, and cache controls.
What is it?
Origin Access Control lets only your distribution read the origin via cloudfront.amazonaws.com + SourceArn.
OAC
How to do it
Create OAC → attach to origin → bucket policy Allow GetObject with SourceArn → deny anonymous.
Example
Kenji Watanabe serves course videos only through CloudFront, never the S3 URL.