Ravi Sir's Cards › AWS
Lab: role with tight trust
What is a VPC: your own private network inside one AWS Region, example ThreeTierVpc 10.0.0.0/16.
Read card text
What this card says
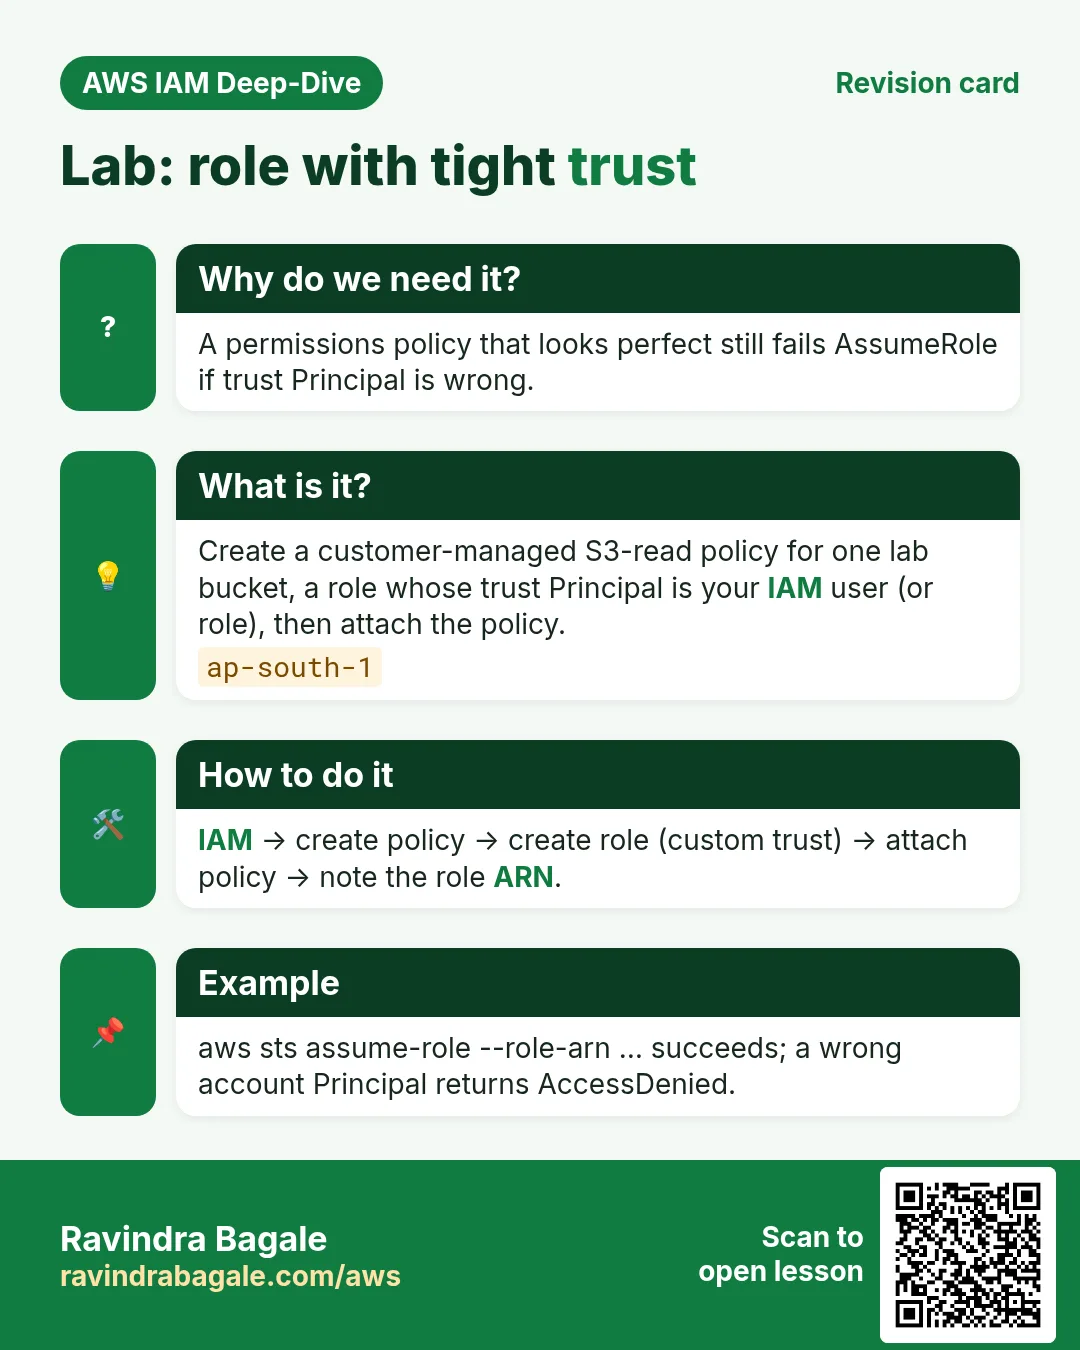
Why do we need it?
A permissions policy that looks perfect still fails AssumeRole if trust Principal is wrong.
What is it?
Create a customer-managed S3-read policy for one lab bucket, a role whose trust Principal is your IAM user (or role), then attach the policy.
ap-south-1
How to do it
IAM → create policy → create role (custom trust) → attach policy → note the role ARN.
Example
aws sts assume-role --role-arn … succeeds; a wrong account Principal returns AccessDenied.