Ravi Sir's Cards › AWS
Trust vs permissions policy
What is a VPC: your own private network inside one AWS Region, example ThreeTierVpc 10.0.0.0/16.
Read card text
What this card says
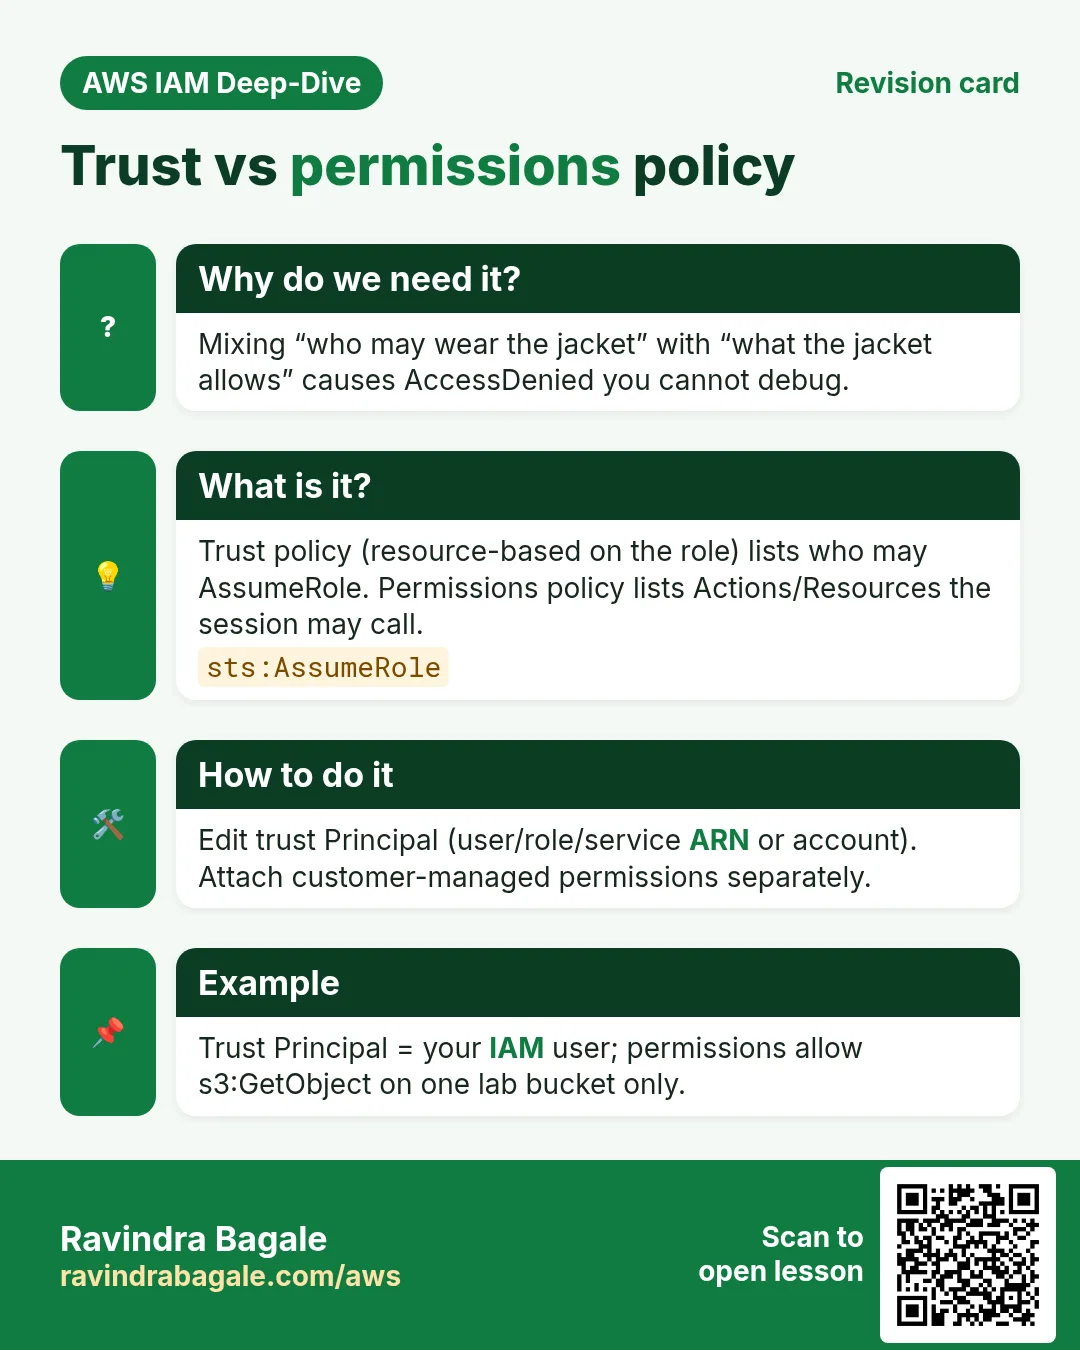
Why do we need it?
Mixing “who may wear the jacket” with “what the jacket allows” causes AccessDenied you cannot debug.
What is it?
Trust policy (resource-based on the role) lists who may AssumeRole. Permissions policy lists Actions/Resources the session may call.
sts:AssumeRole
How to do it
Edit trust Principal (user/role/service ARN or account). Attach customer-managed permissions separately.
Example
Trust Principal = your IAM user; permissions allow s3:GetObject on one lab bucket only.