Ravi Sir's Cards › AWS
Why allow-in-VPC still fails?
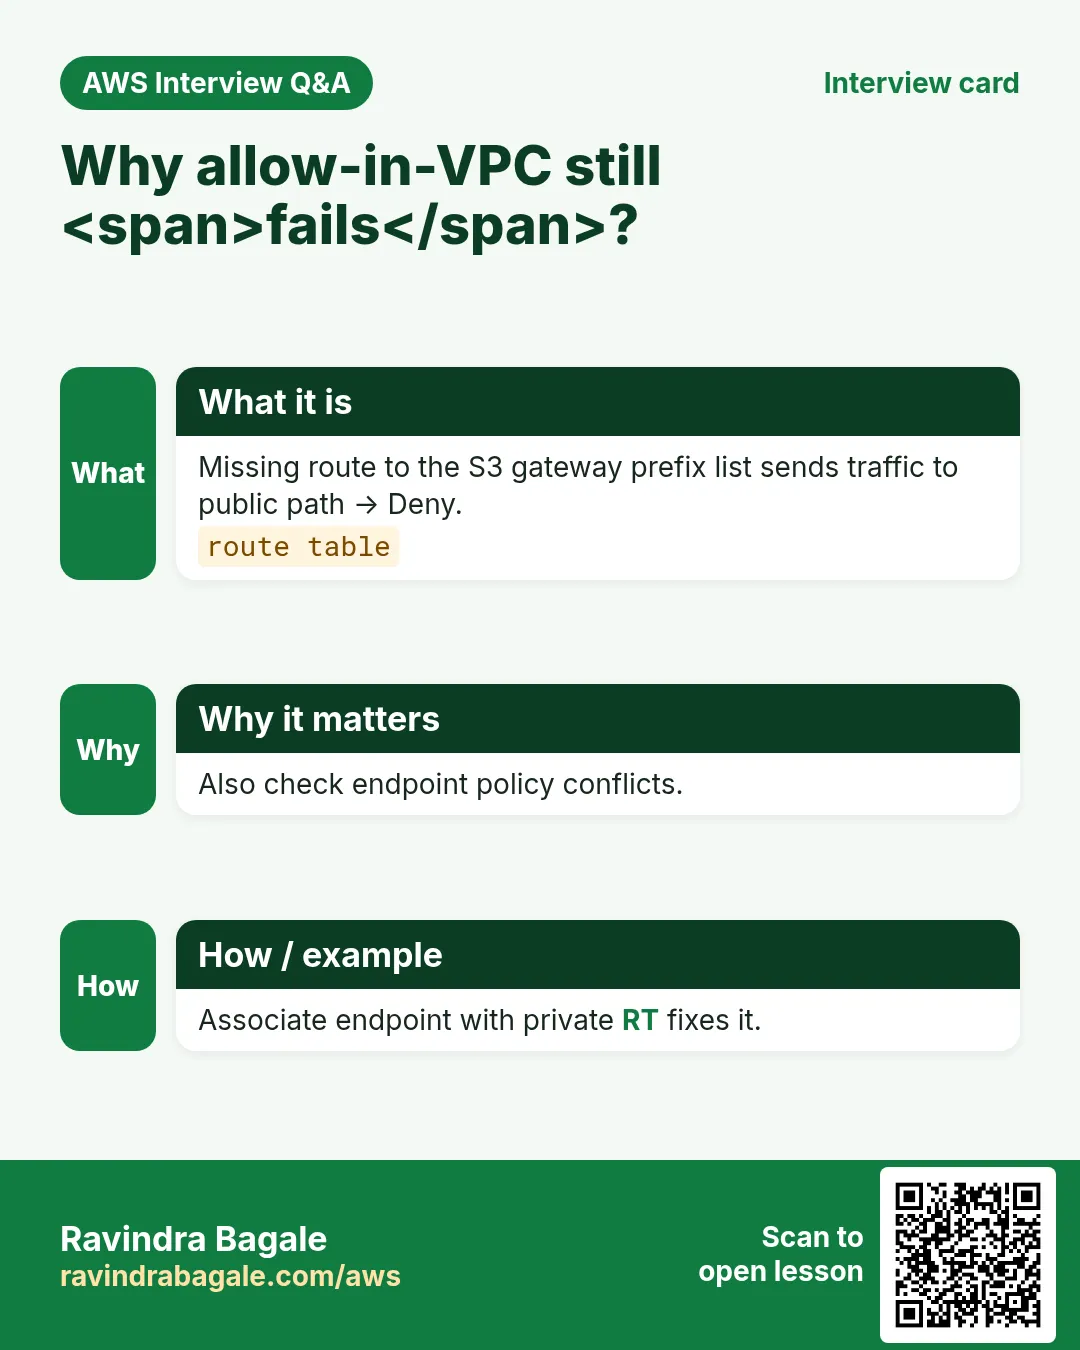
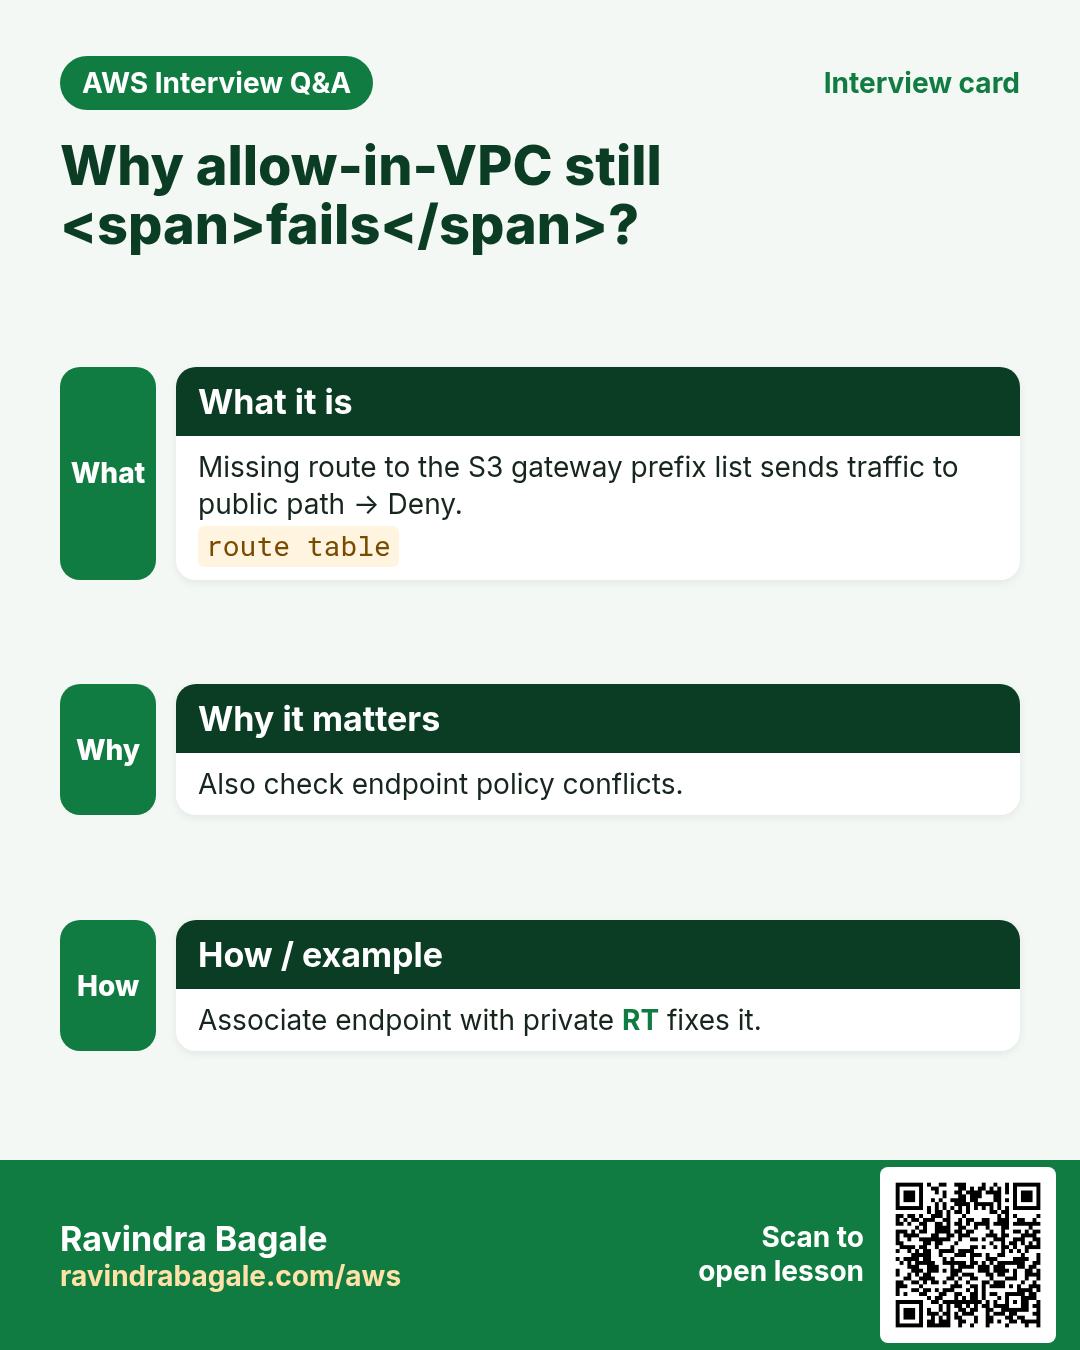
This interview card answers: Why allow-in-VPC still fails? Missing route to the S3 gateway prefix list sends traffic to public path , then Deny. Also check endpoint policy conflicts. Associate endpoint with private RT fixes it.
Read card text
What this card says
What it is
Missing route to the S3 gateway prefix list sends traffic to public path → Deny.
route table
Why it matters
Also check endpoint policy conflicts.
How / example
Associate endpoint with private RT fixes it.