Ravindra BagaleCourses & study guides मराठी

Ravi Sir's Cards › DevOps

Chapter 29: Scan Pipeline in Jenkins: Cards

मराठी cards · Open the chapter

Revision cards
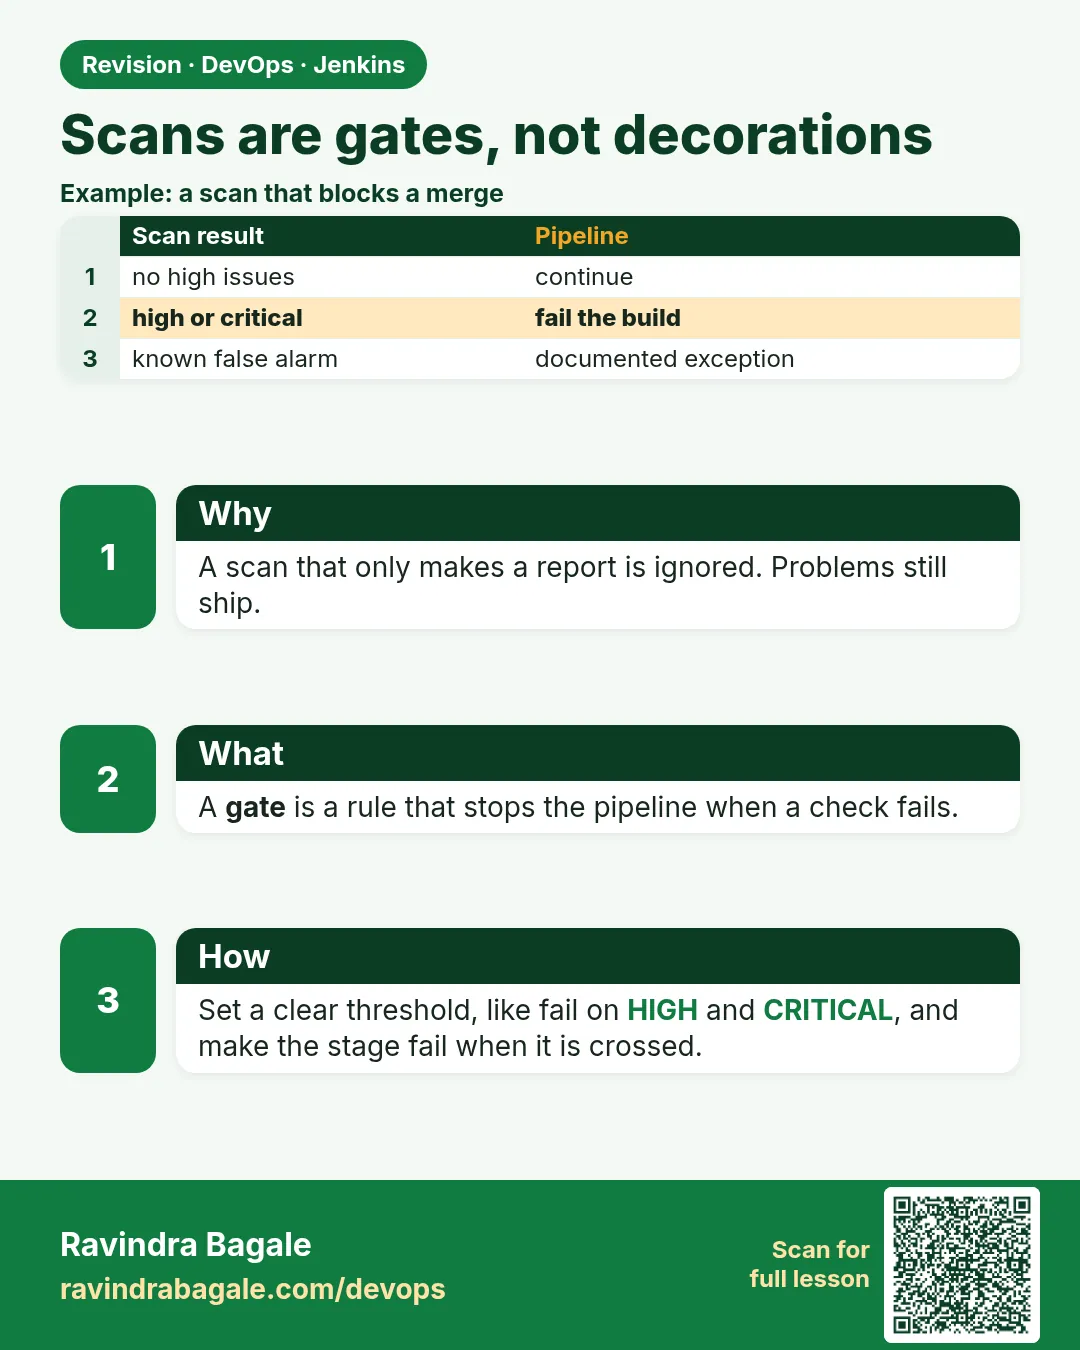
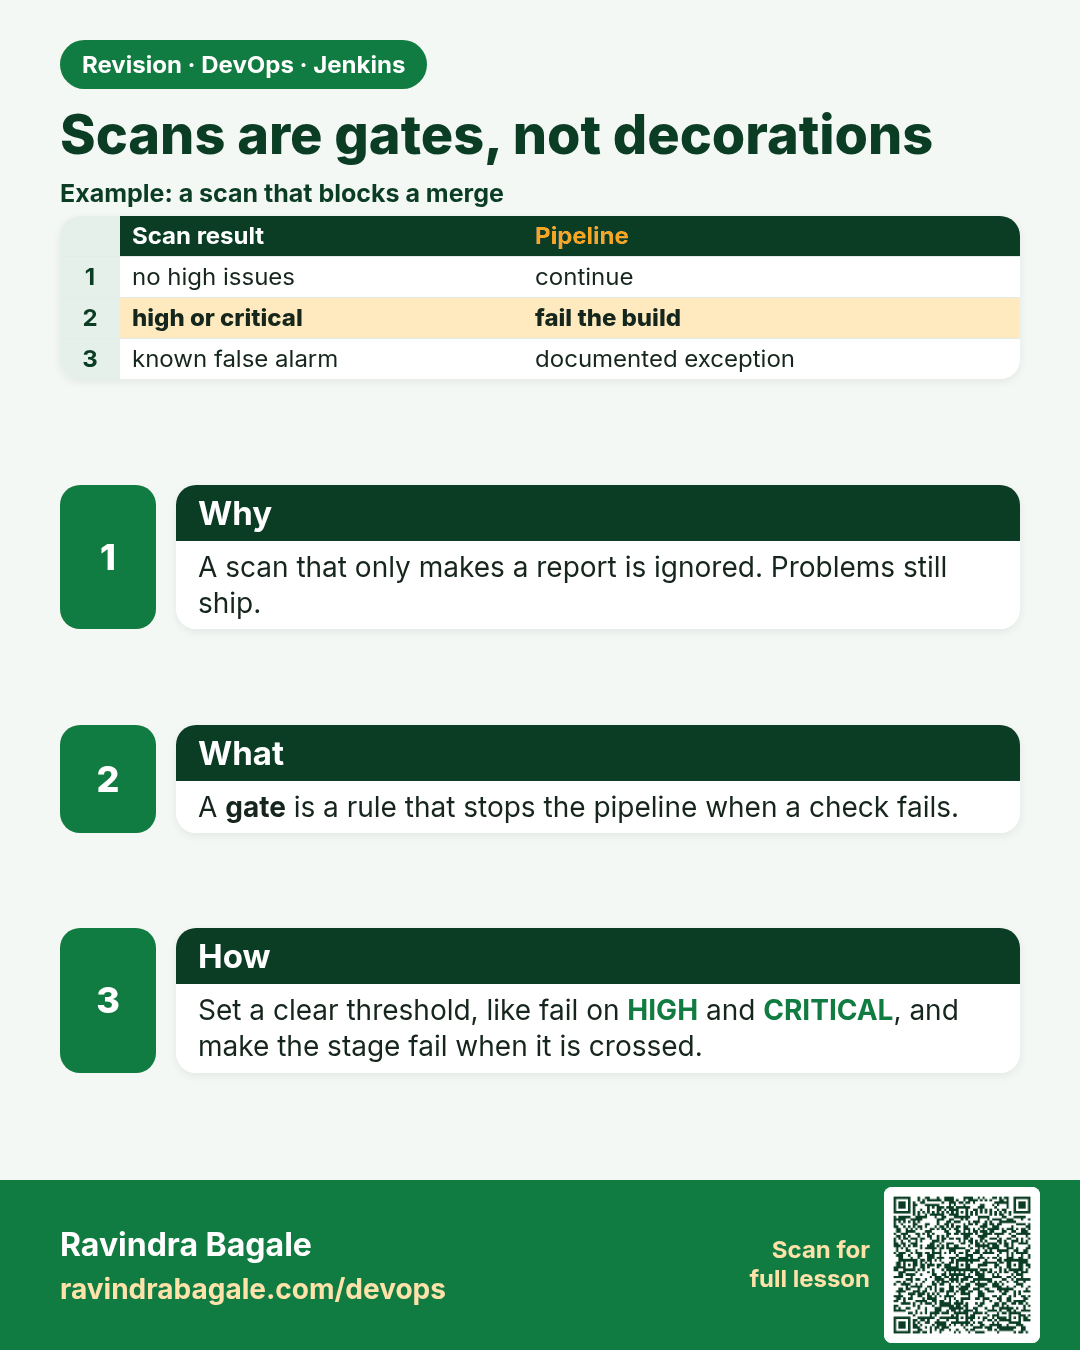
Scans are gates, not decorations. A scan that only makes a report is ignored. Problems still ship.
Revision card 1 of 11: Scans are gates, not decorations · Download PNG · Open card page

Lesson: 29.1 Scans are gates, not decorations
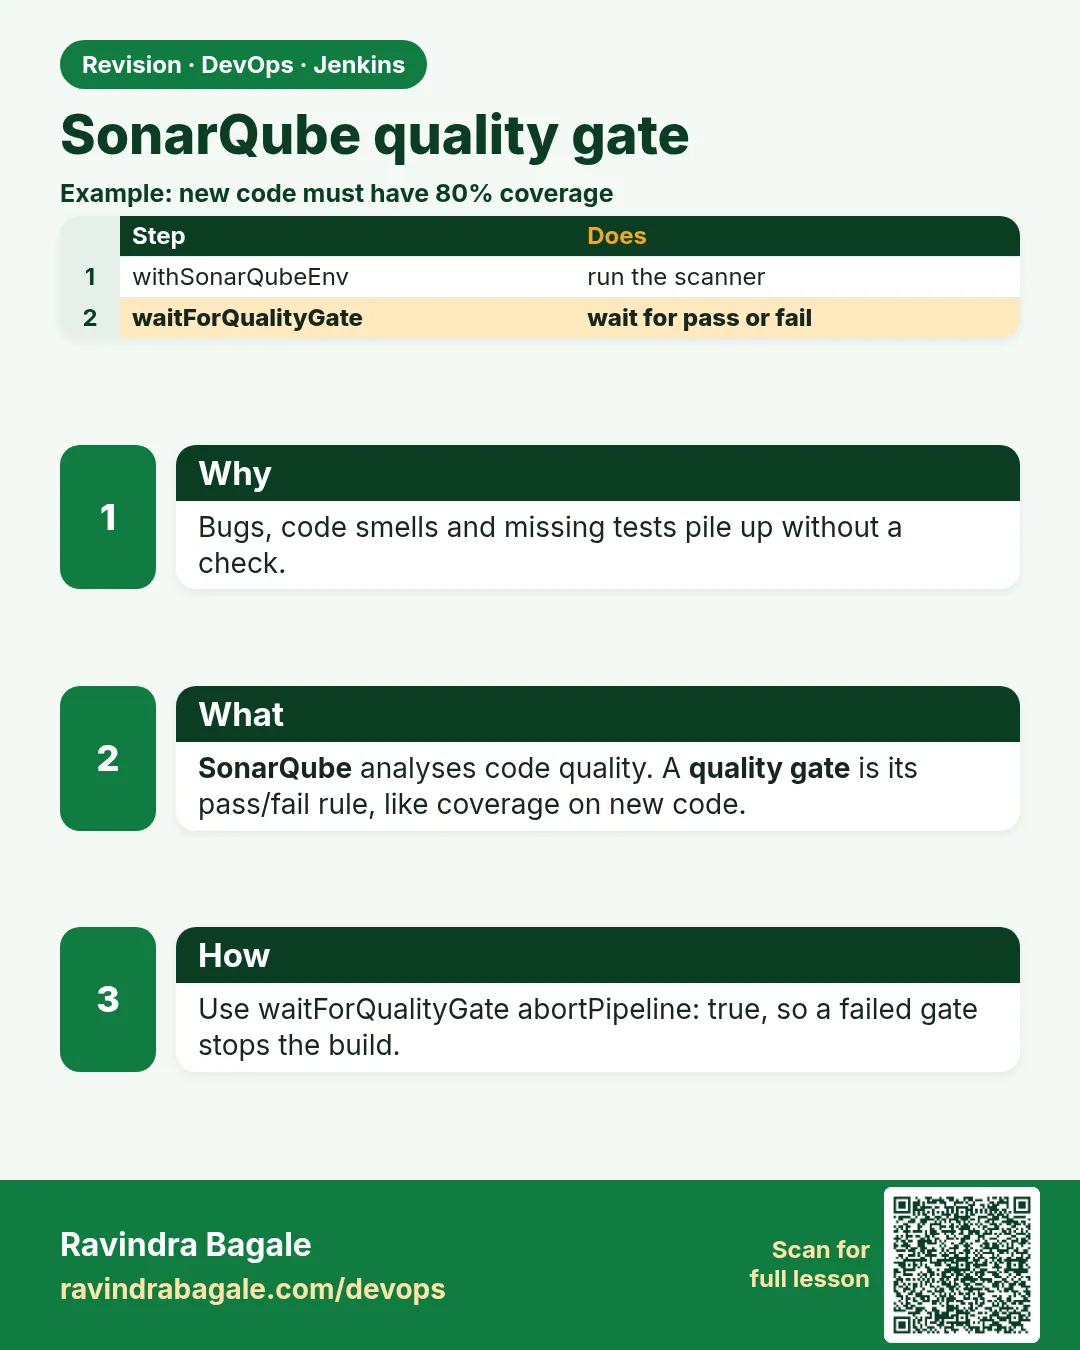
SonarQube quality gate. Bugs, code smells and missing tests pile up without a check.
Revision card 2 of 11: SonarQube quality gate · Download PNG · Open card page

Lesson: 29.2 SonarQube quality gate

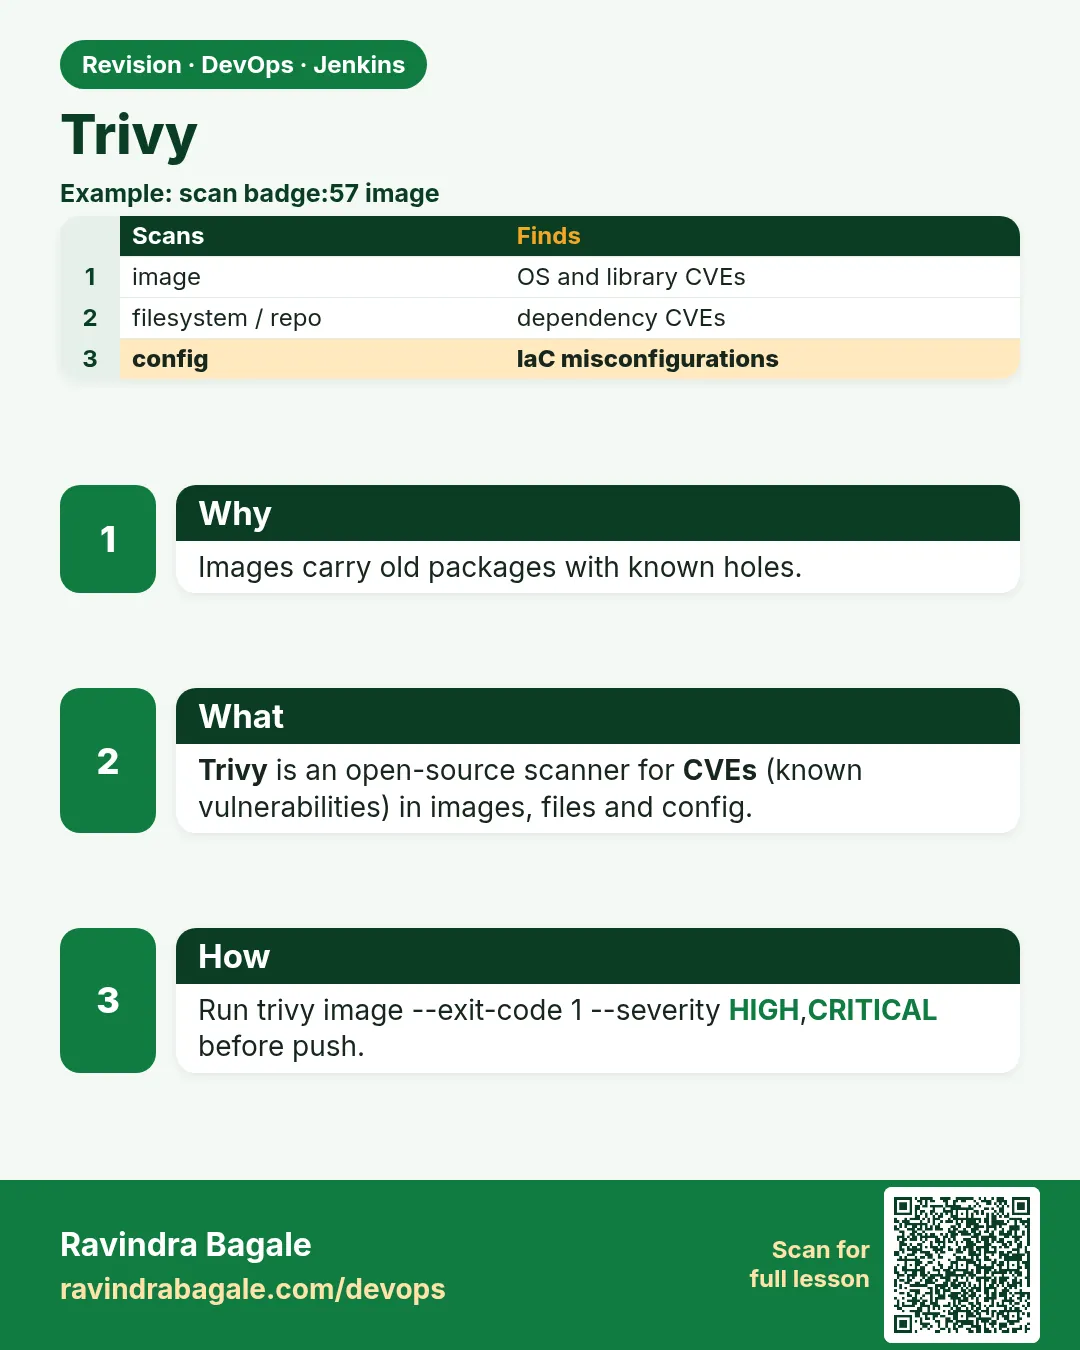
Trivy. Images carry old packages with known holes.
Revision card 3 of 11: Trivy · Download PNG · Open card page

Lesson: 29.3 Trivy

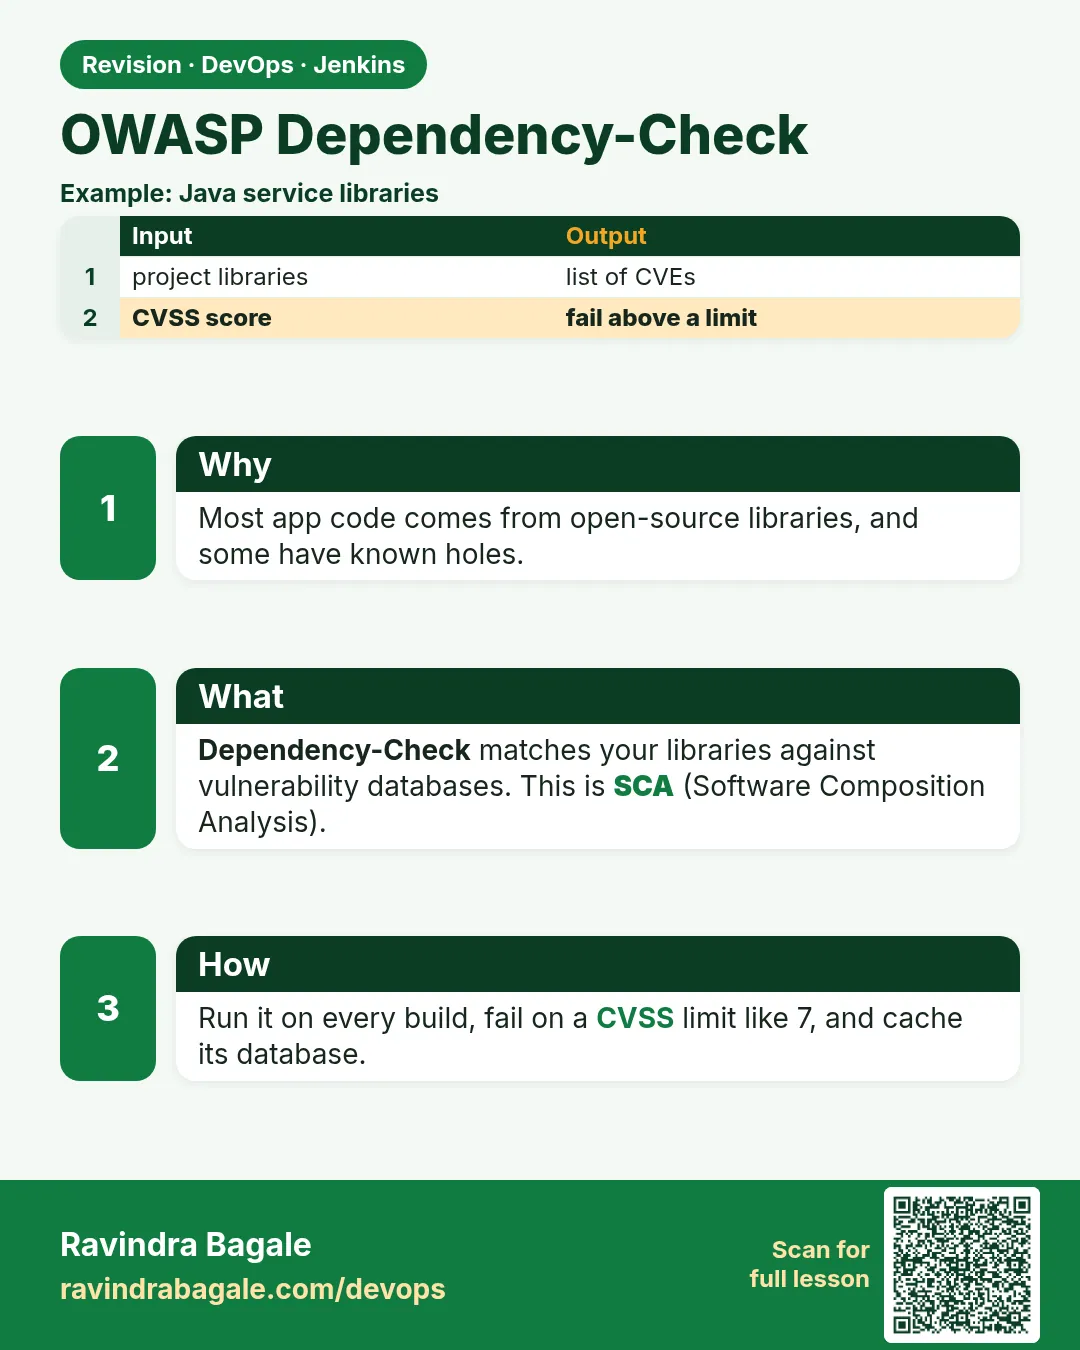
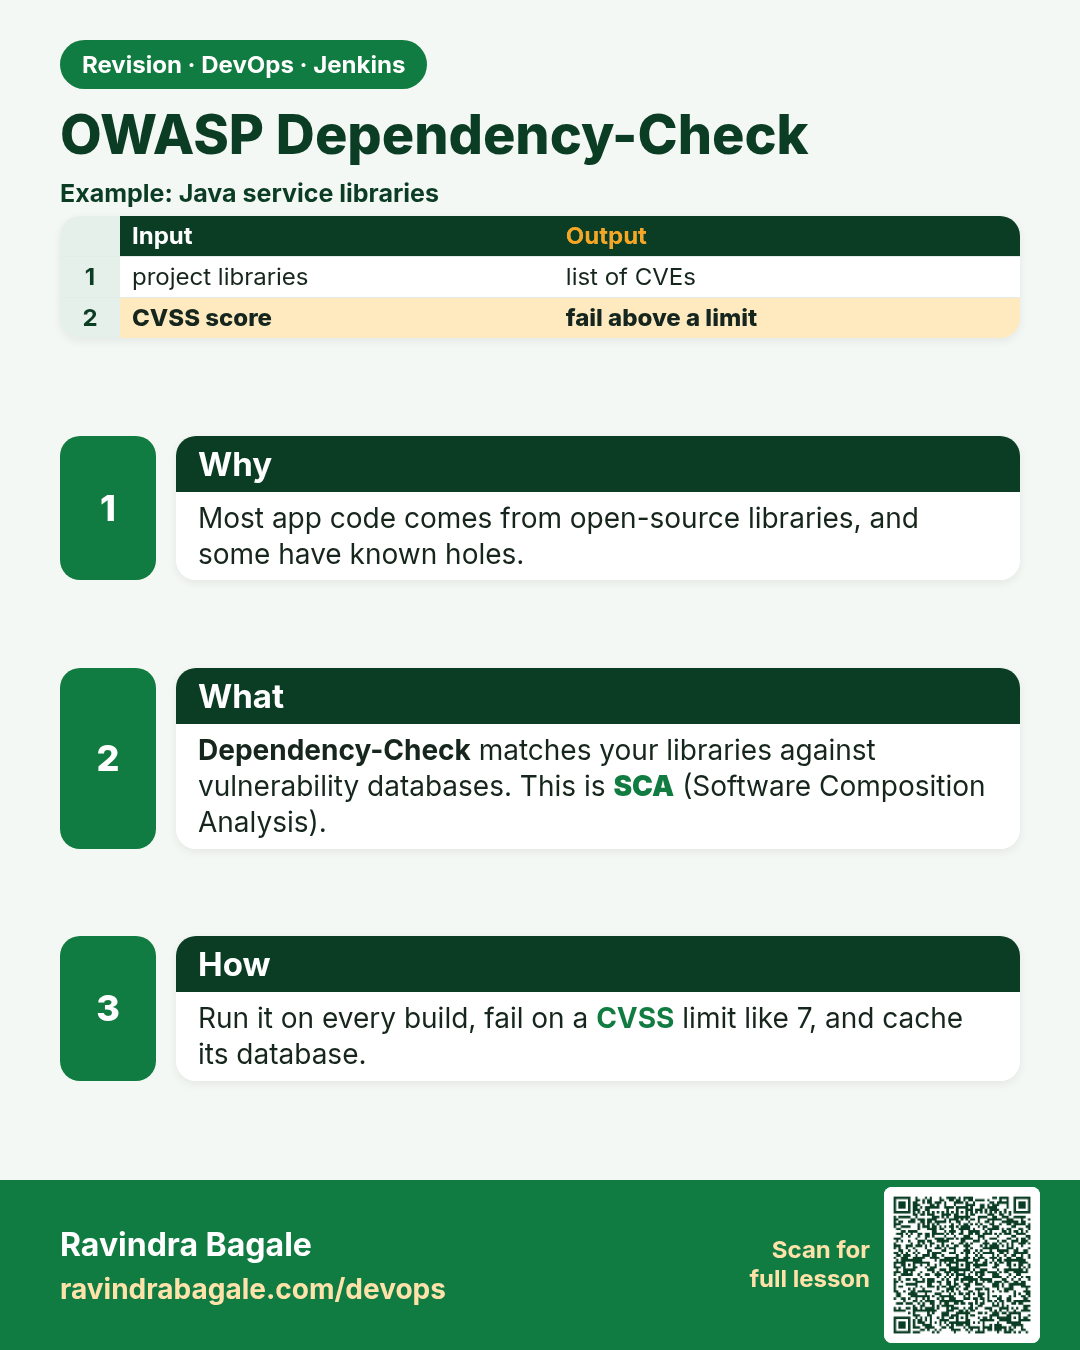
OWASP Dependency-Check. Most app code comes from open-source libraries, and some have known holes.
Revision card 4 of 11: OWASP Dependency-Check · Download PNG · Open card page

Lesson: 29.4 OWASP Dependency-Check

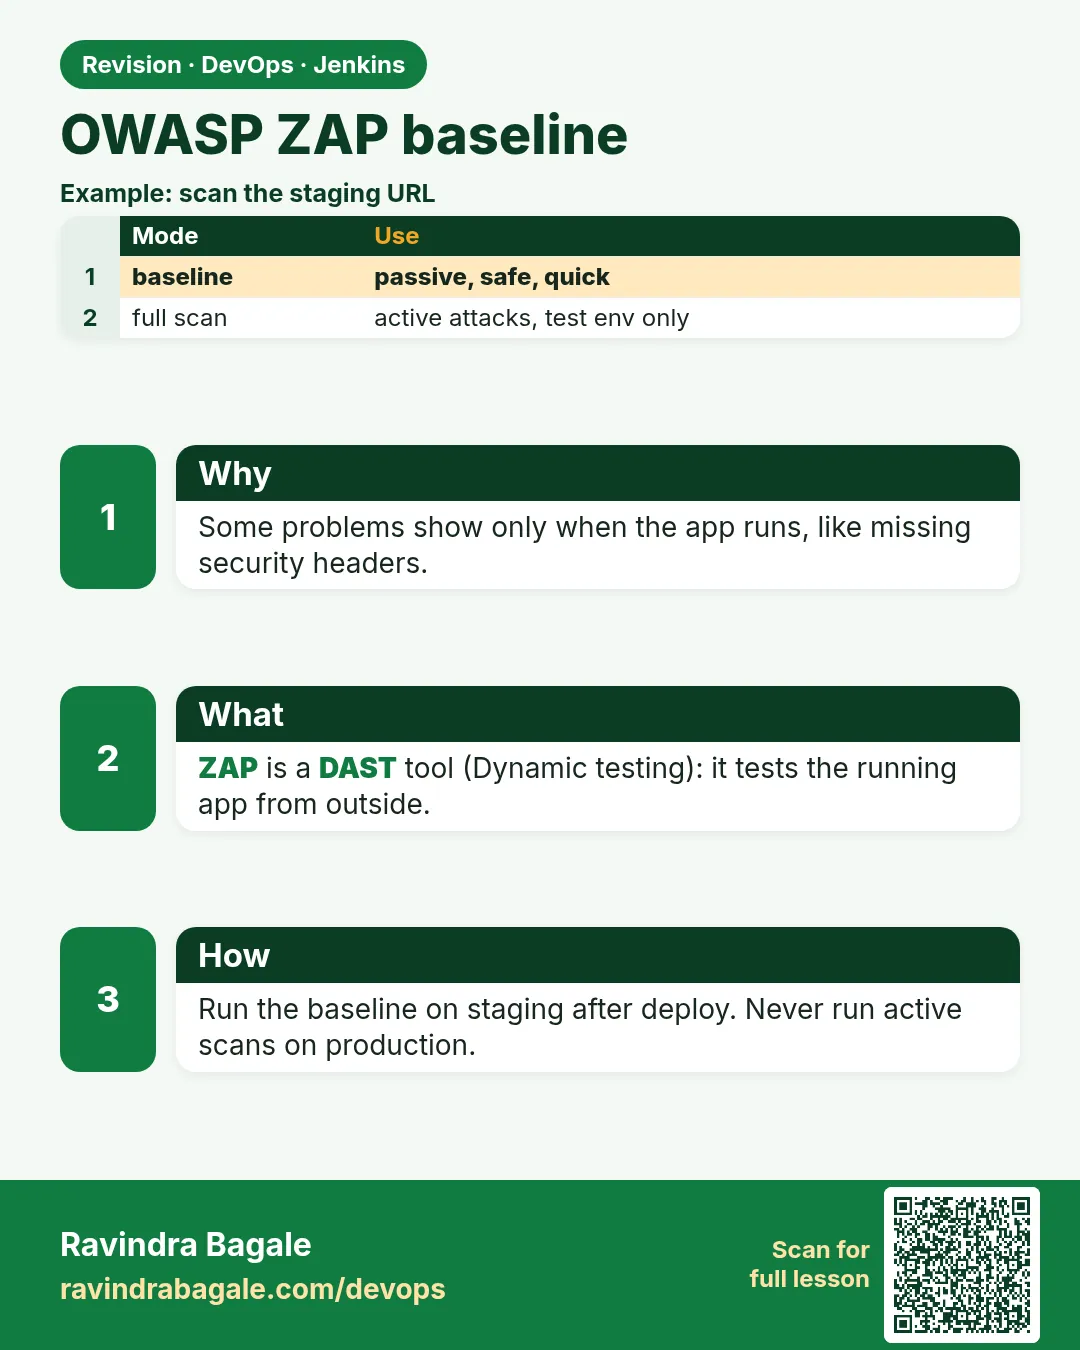
OWASP ZAP baseline. Some problems show only when the app runs, like missing security headers.
Revision card 5 of 11: OWASP ZAP baseline · Download PNG · Open card page

Lesson: 29.5 ZAP baseline

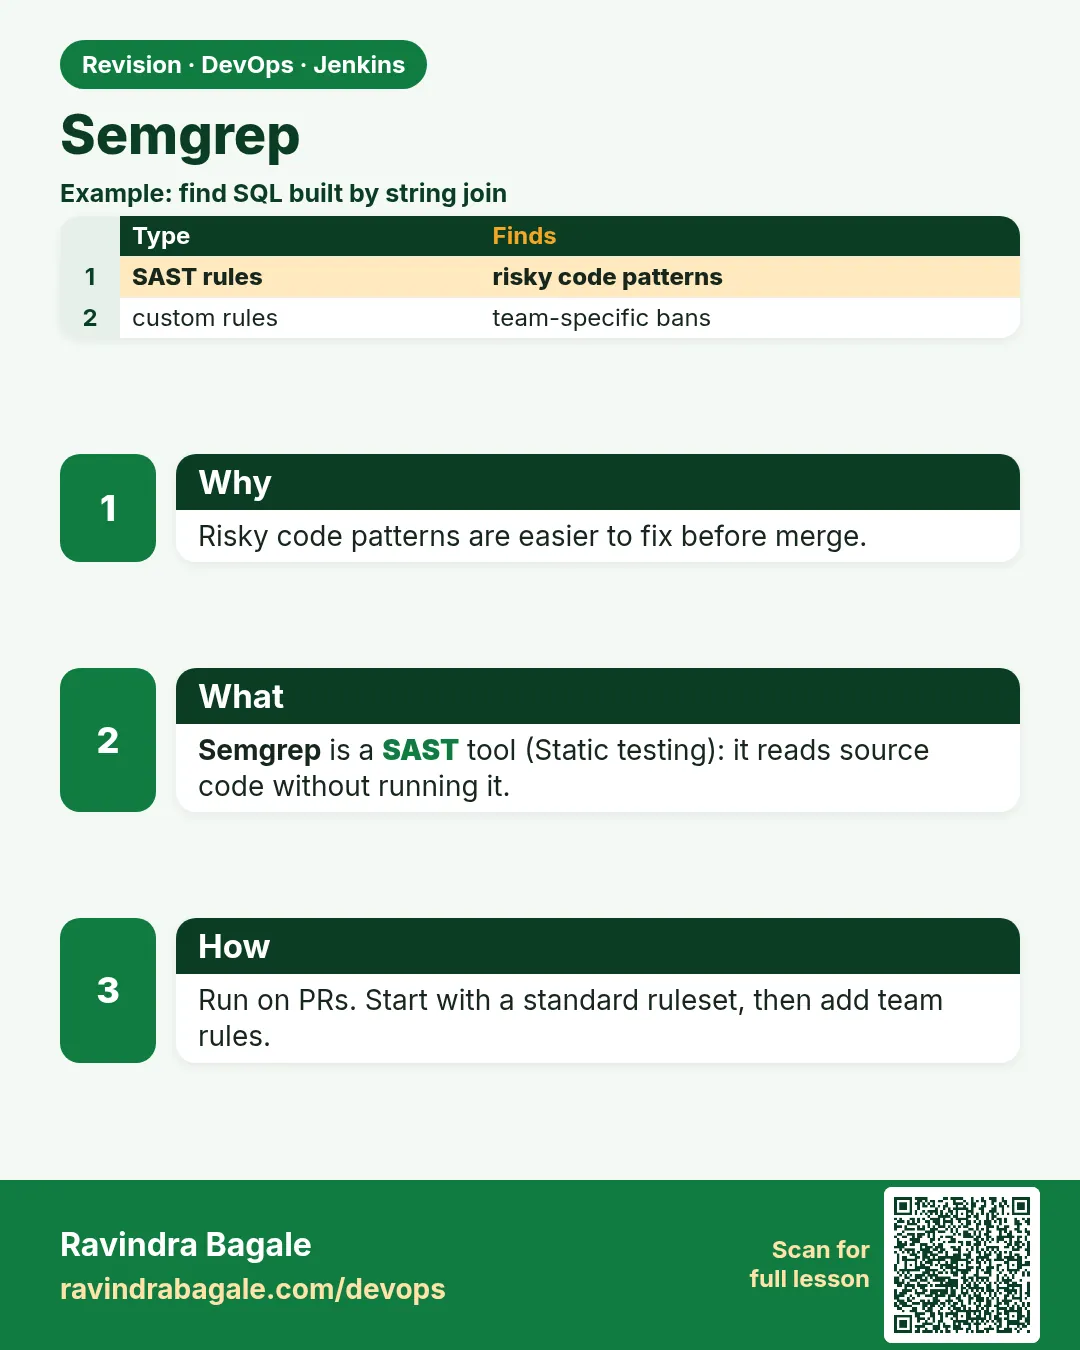
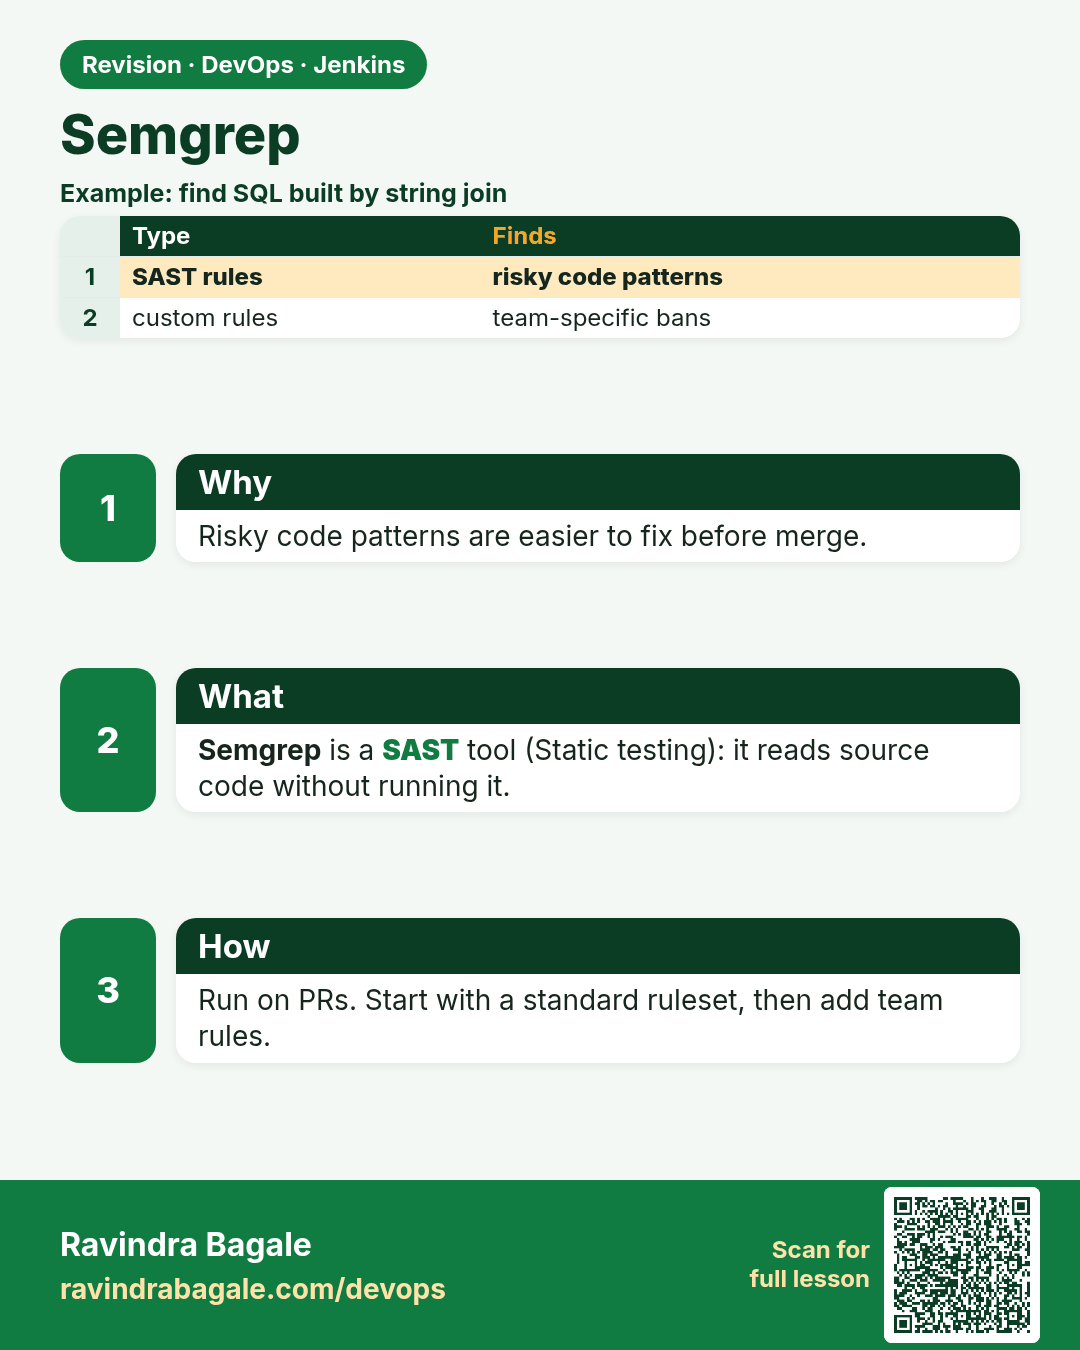
Semgrep. Risky code patterns are easier to fix before merge.
Revision card 6 of 11: Semgrep · Download PNG · Open card page

Lesson: 29.6 Semgrep

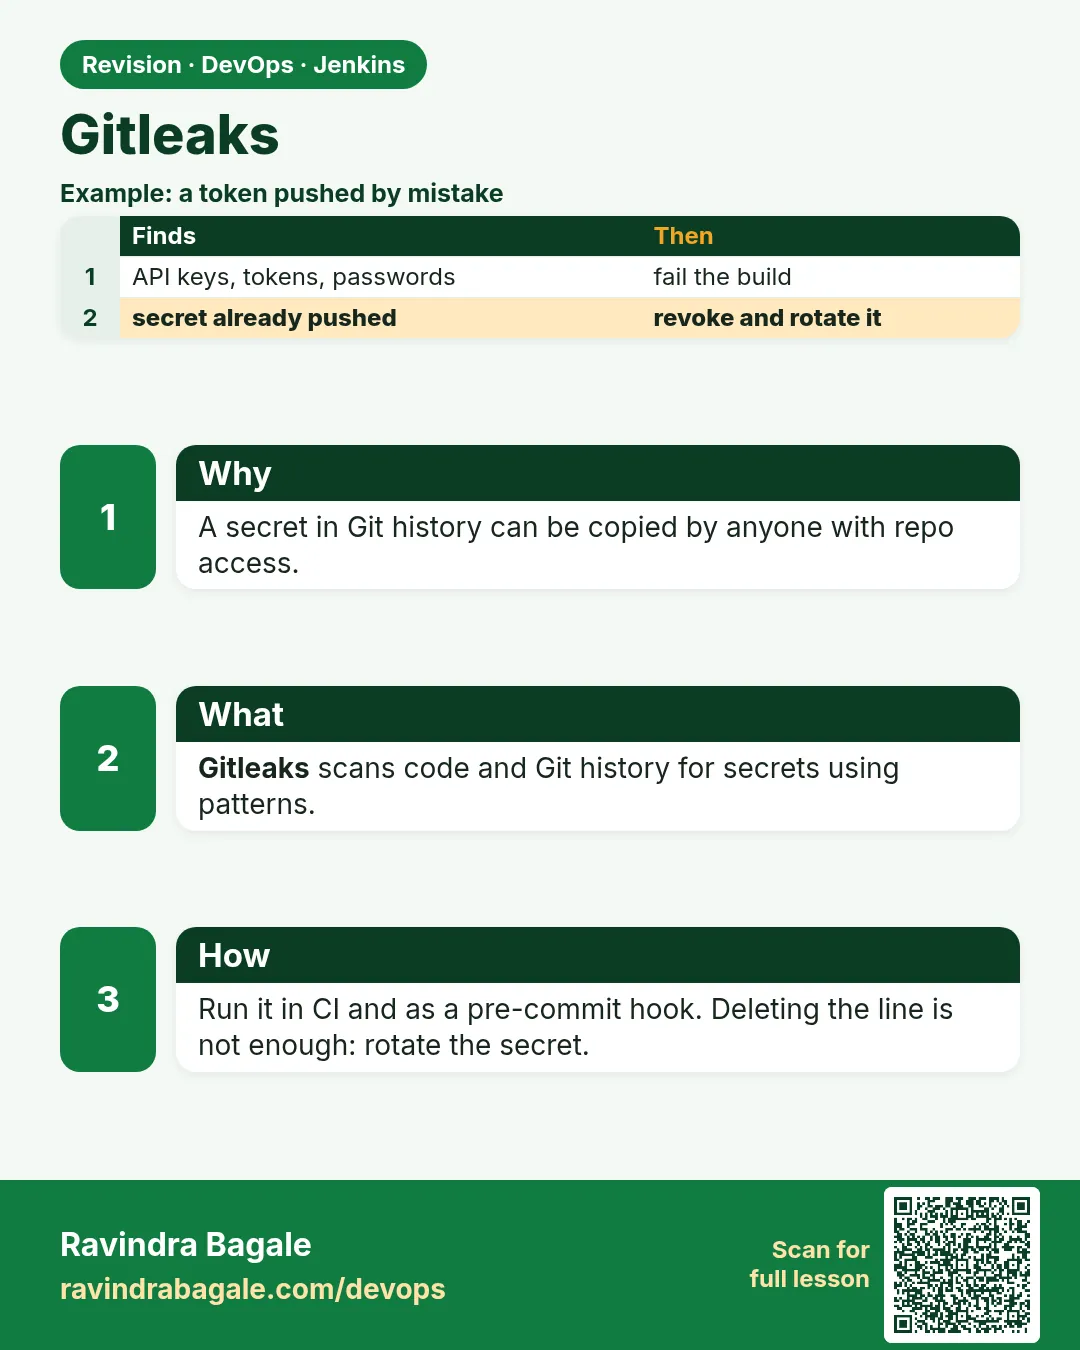
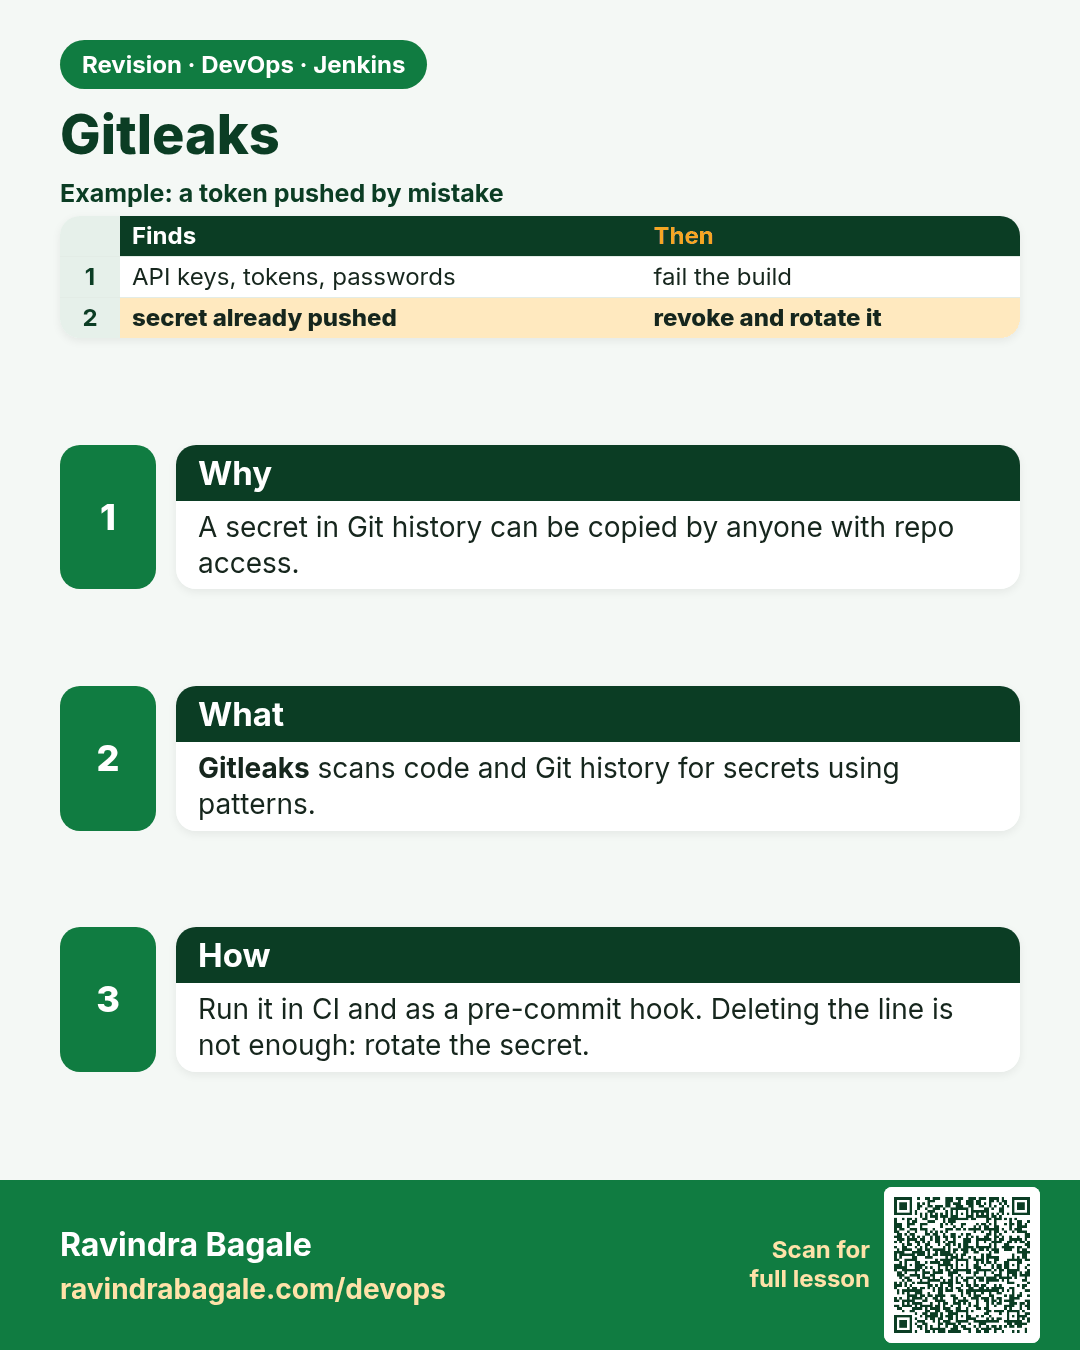
Gitleaks. A secret in Git history can be copied by anyone with repo access.
Revision card 7 of 11: Gitleaks · Download PNG · Open card page

Lesson: 29.7 Gitleaks

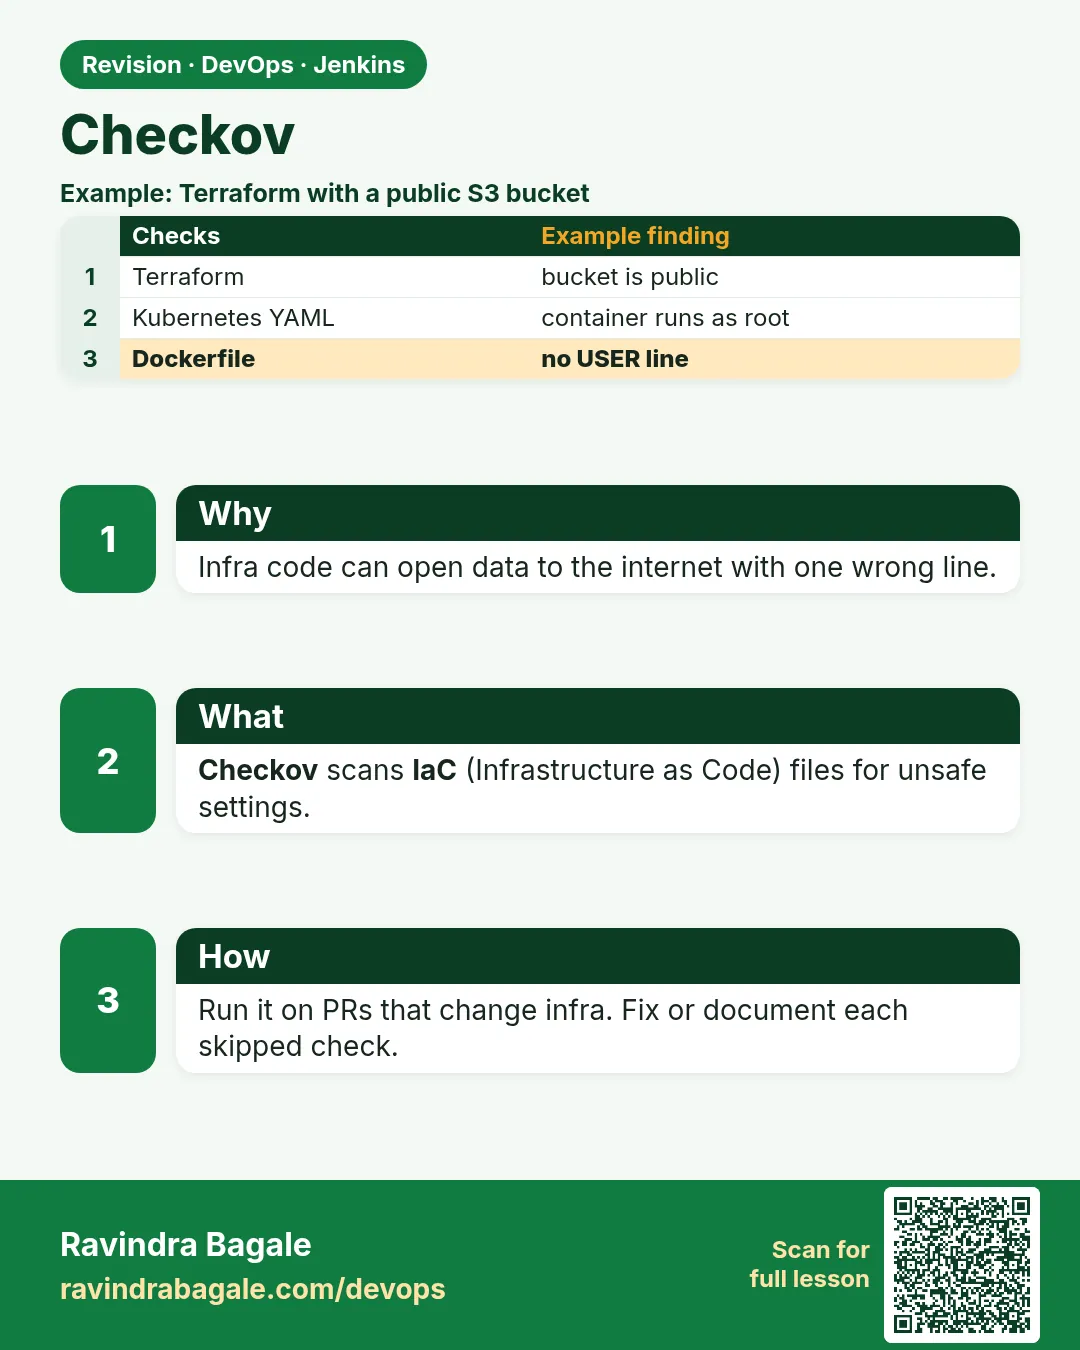
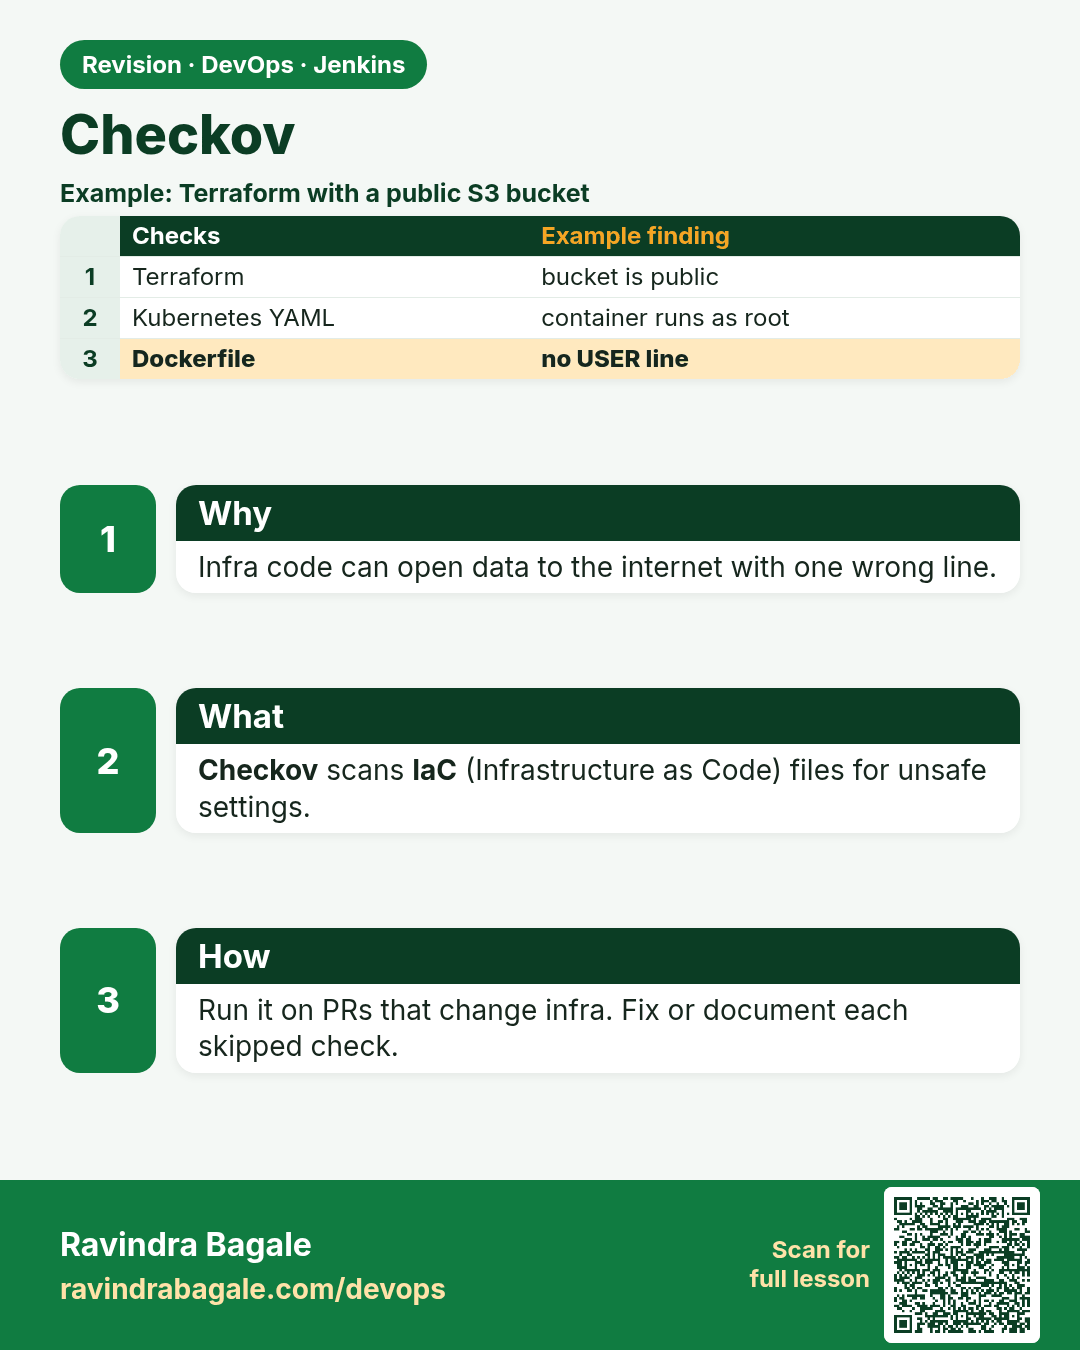
Checkov. Infra code can open data to the internet with one wrong line.
Revision card 8 of 11: Checkov · Download PNG · Open card page

Lesson: 29.8 Checkov

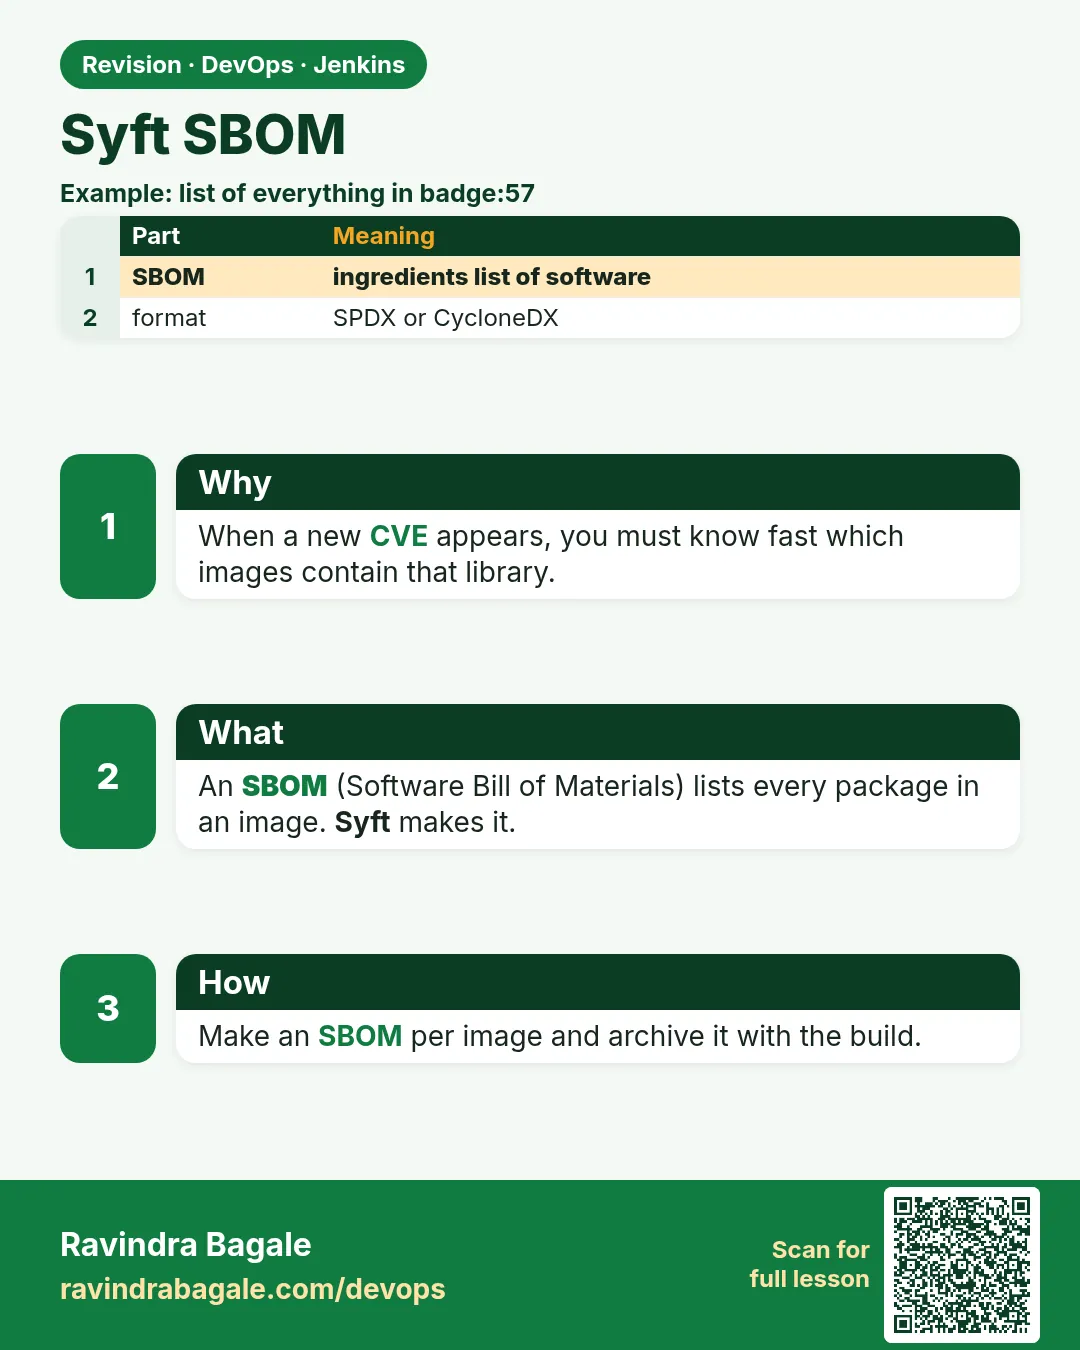
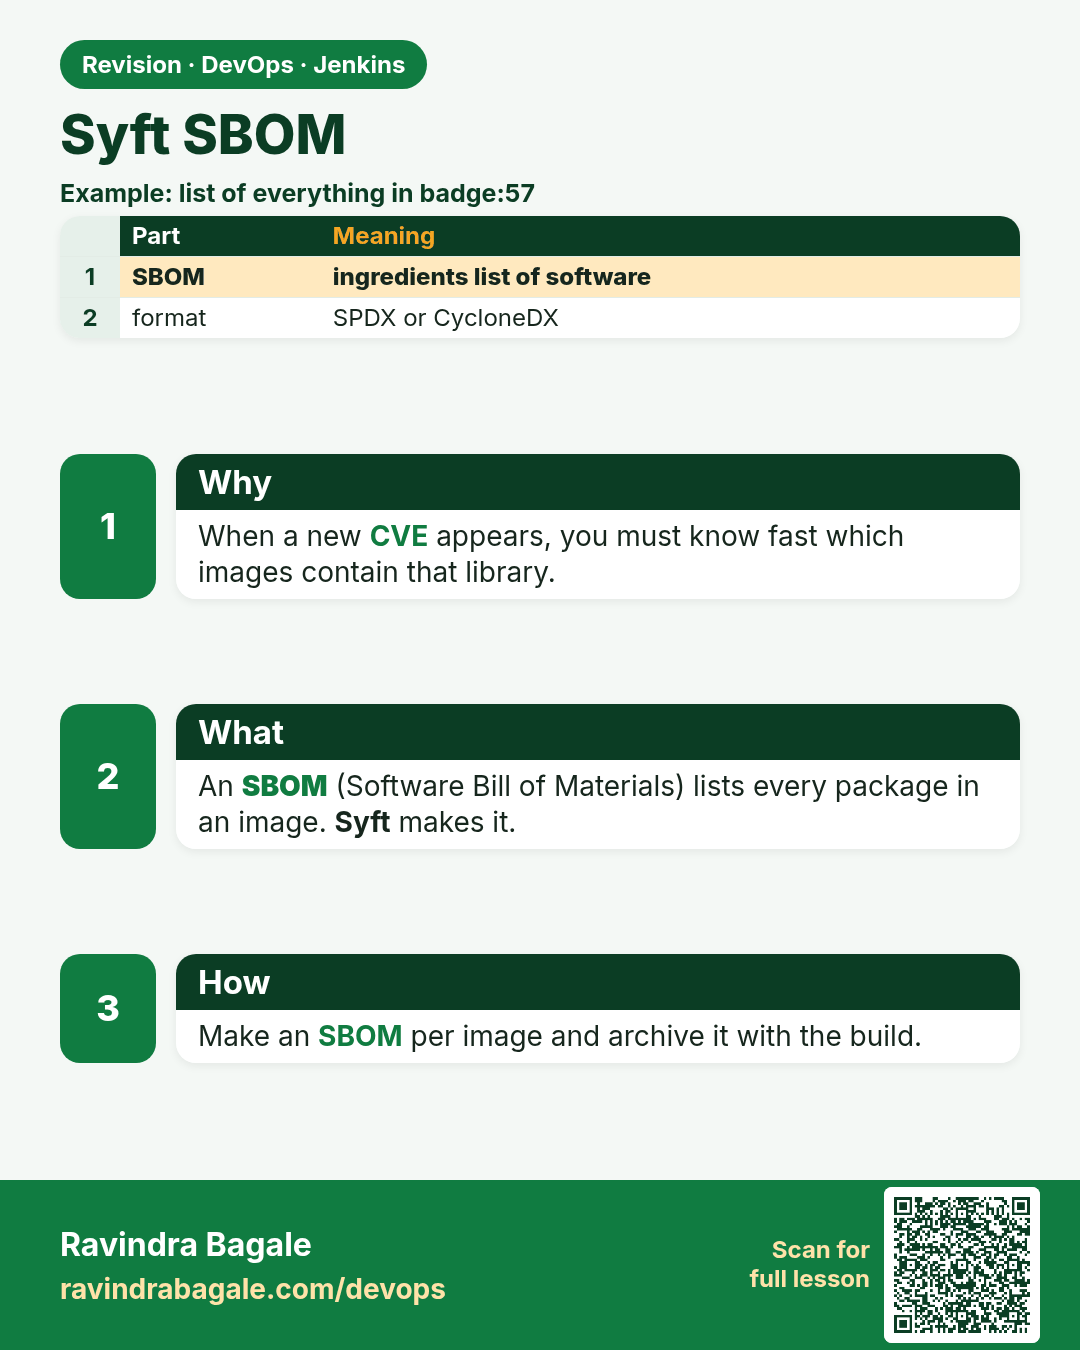
Syft SBOM. When a new CVE appears, you must know fast which images contain that library.
Revision card 9 of 11: Syft SBOM · Download PNG · Open card page

Lesson: 29.9 Syft SBOM

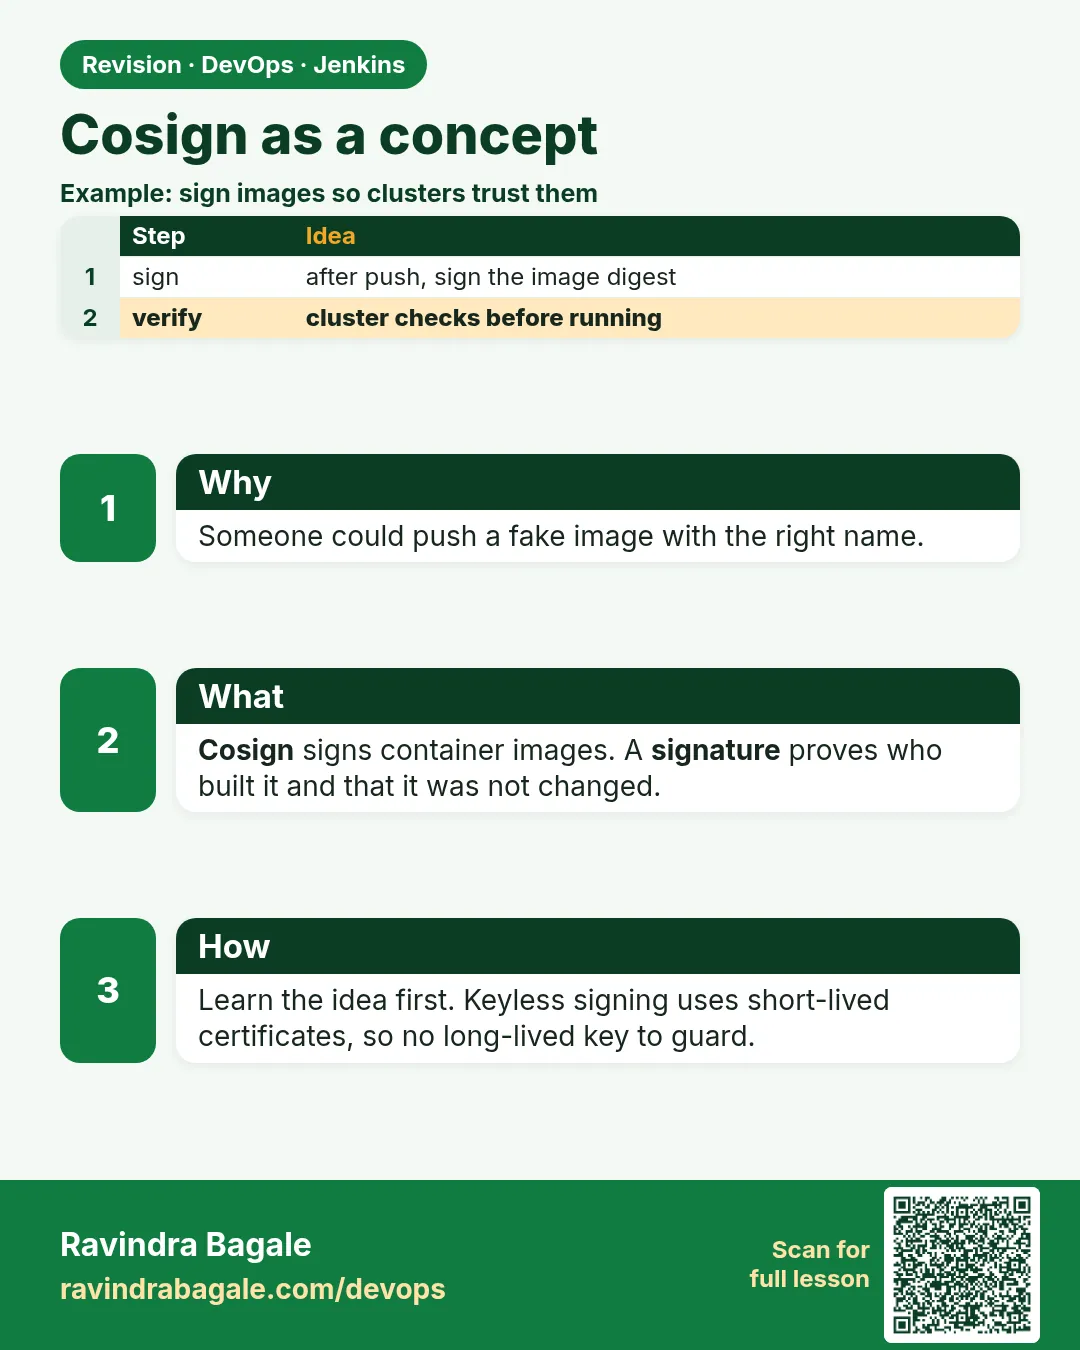
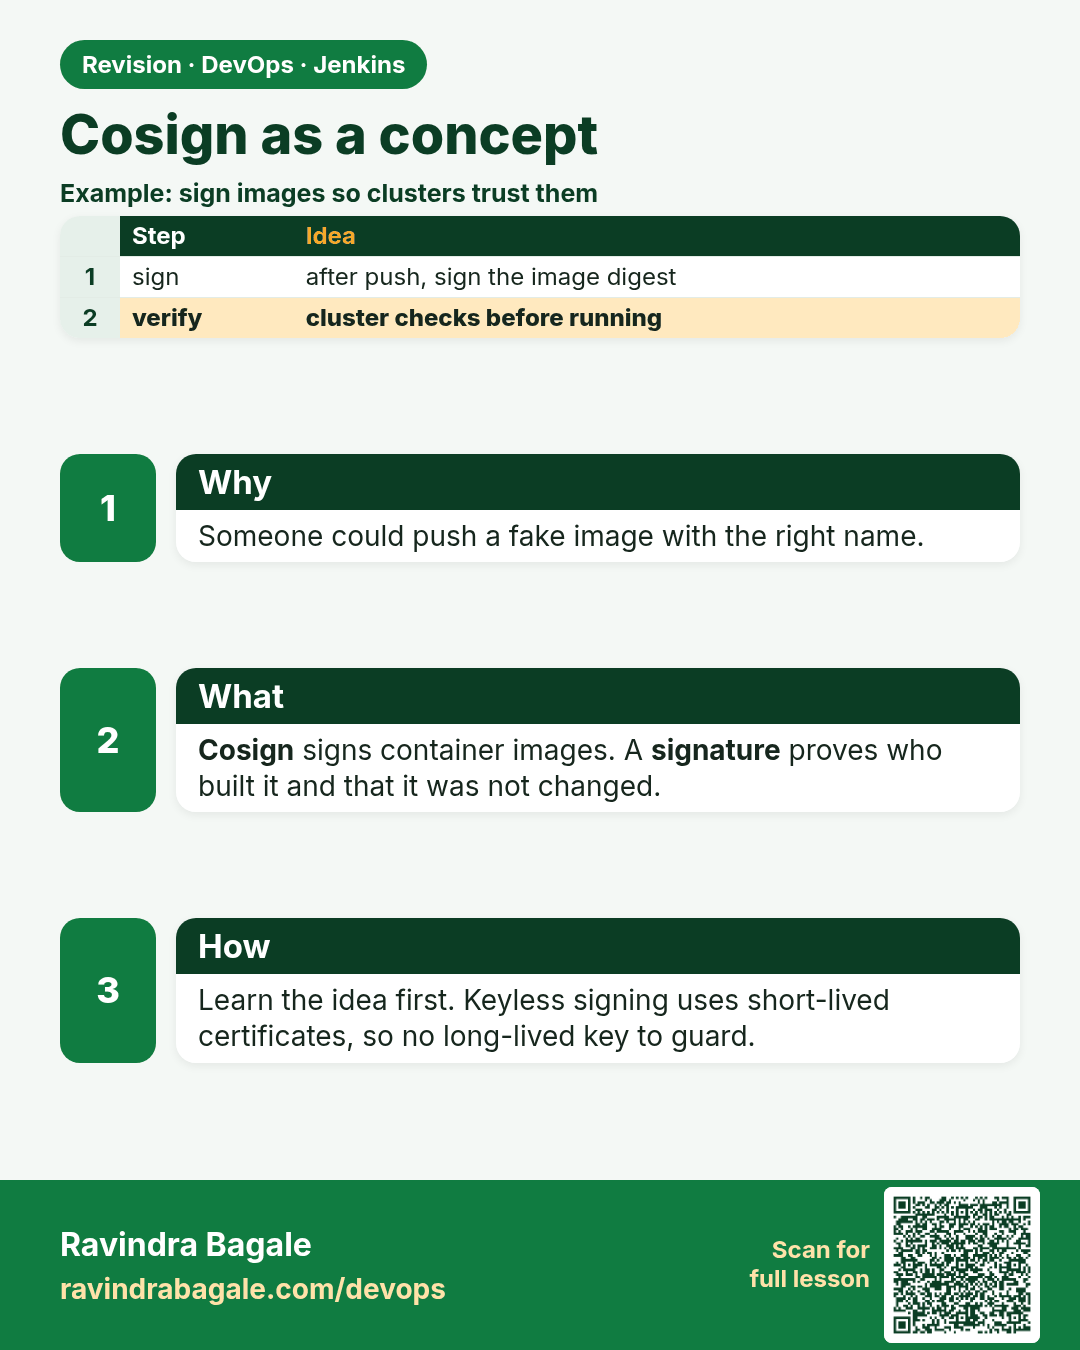
Cosign as a concept. Someone could push a fake image with the right name.
Revision card 10 of 11: Cosign as a concept · Download PNG · Open card page

Lesson: 29.10 Cosign, as a concept, with no keys

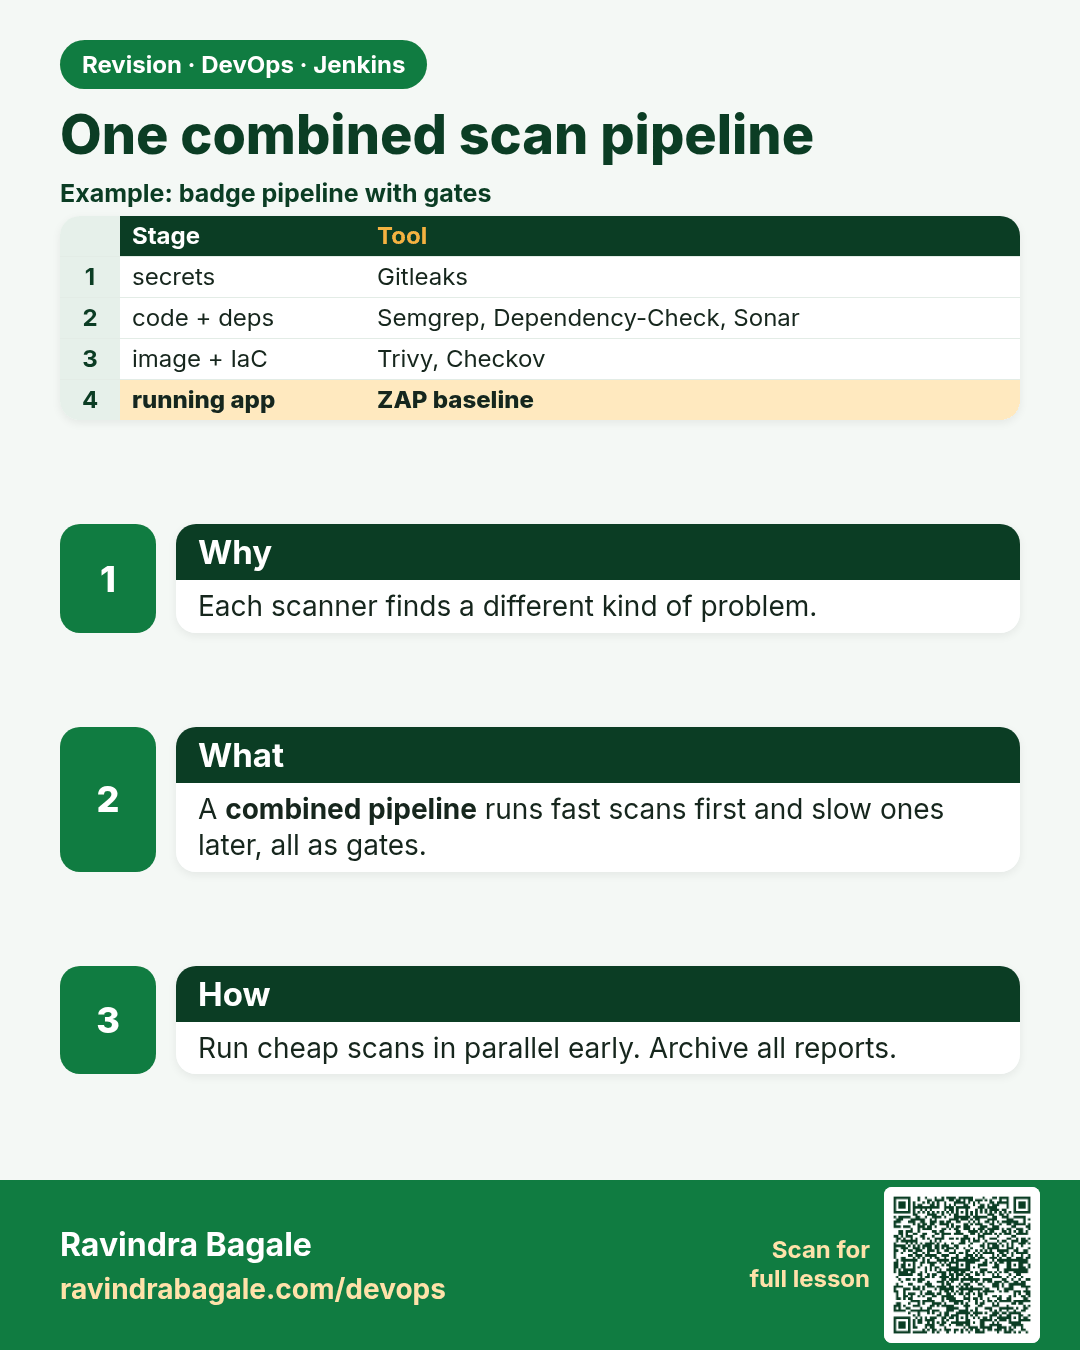
One combined scan pipeline. Each scanner finds a different kind of problem.
Revision card 11 of 11: One combined scan pipeline · Download PNG · Open card page

Lesson: 29.11 One combined pipeline

Interview cards

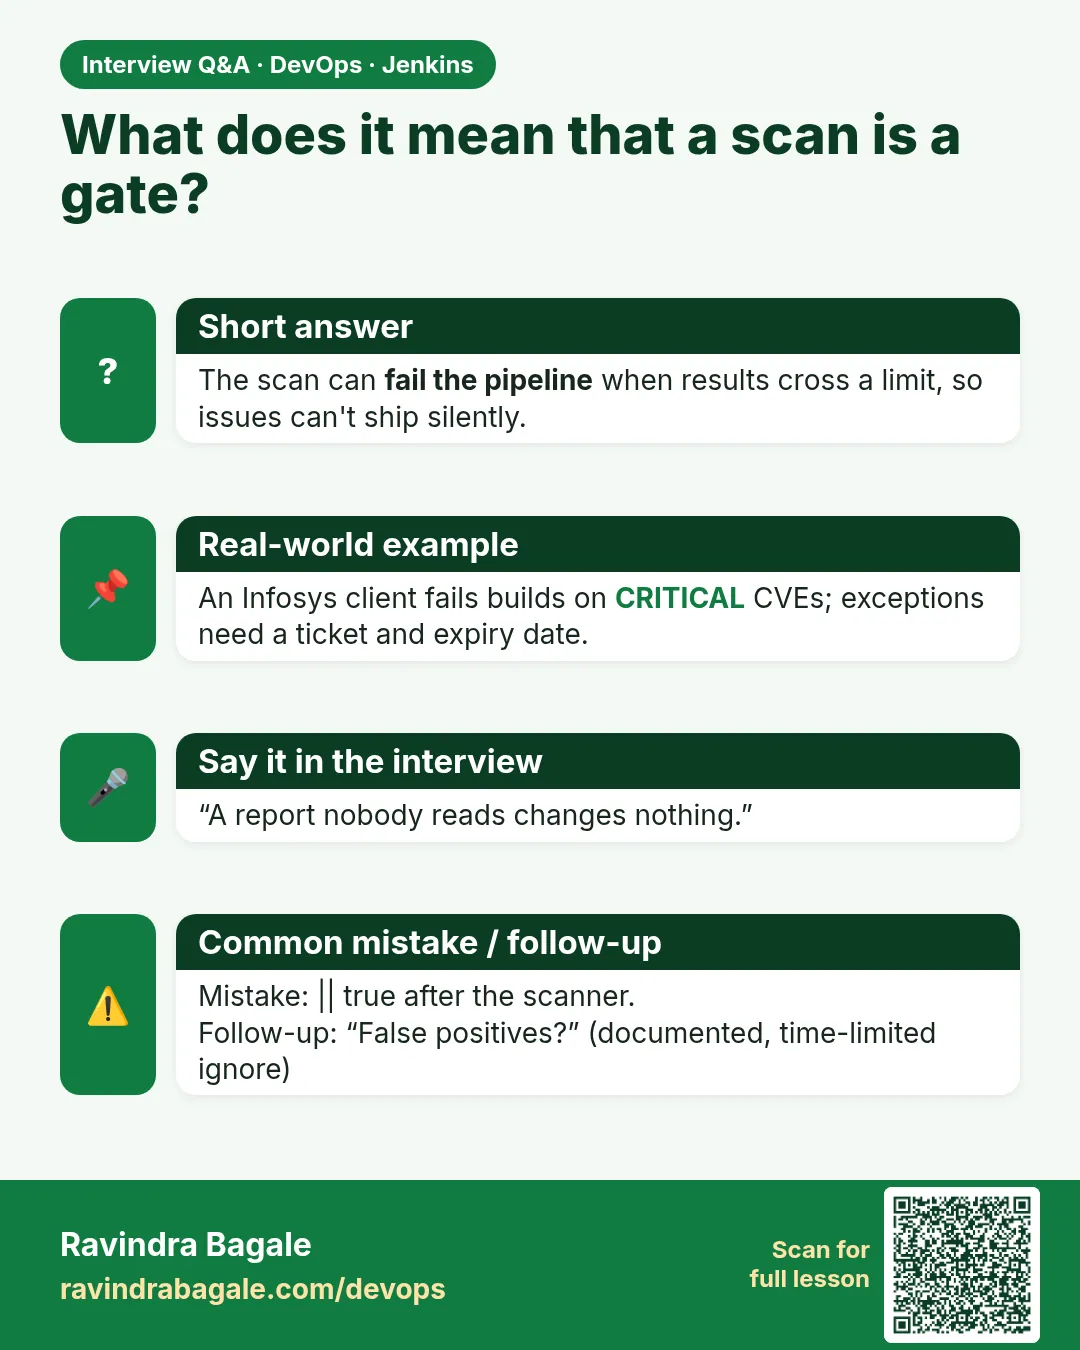
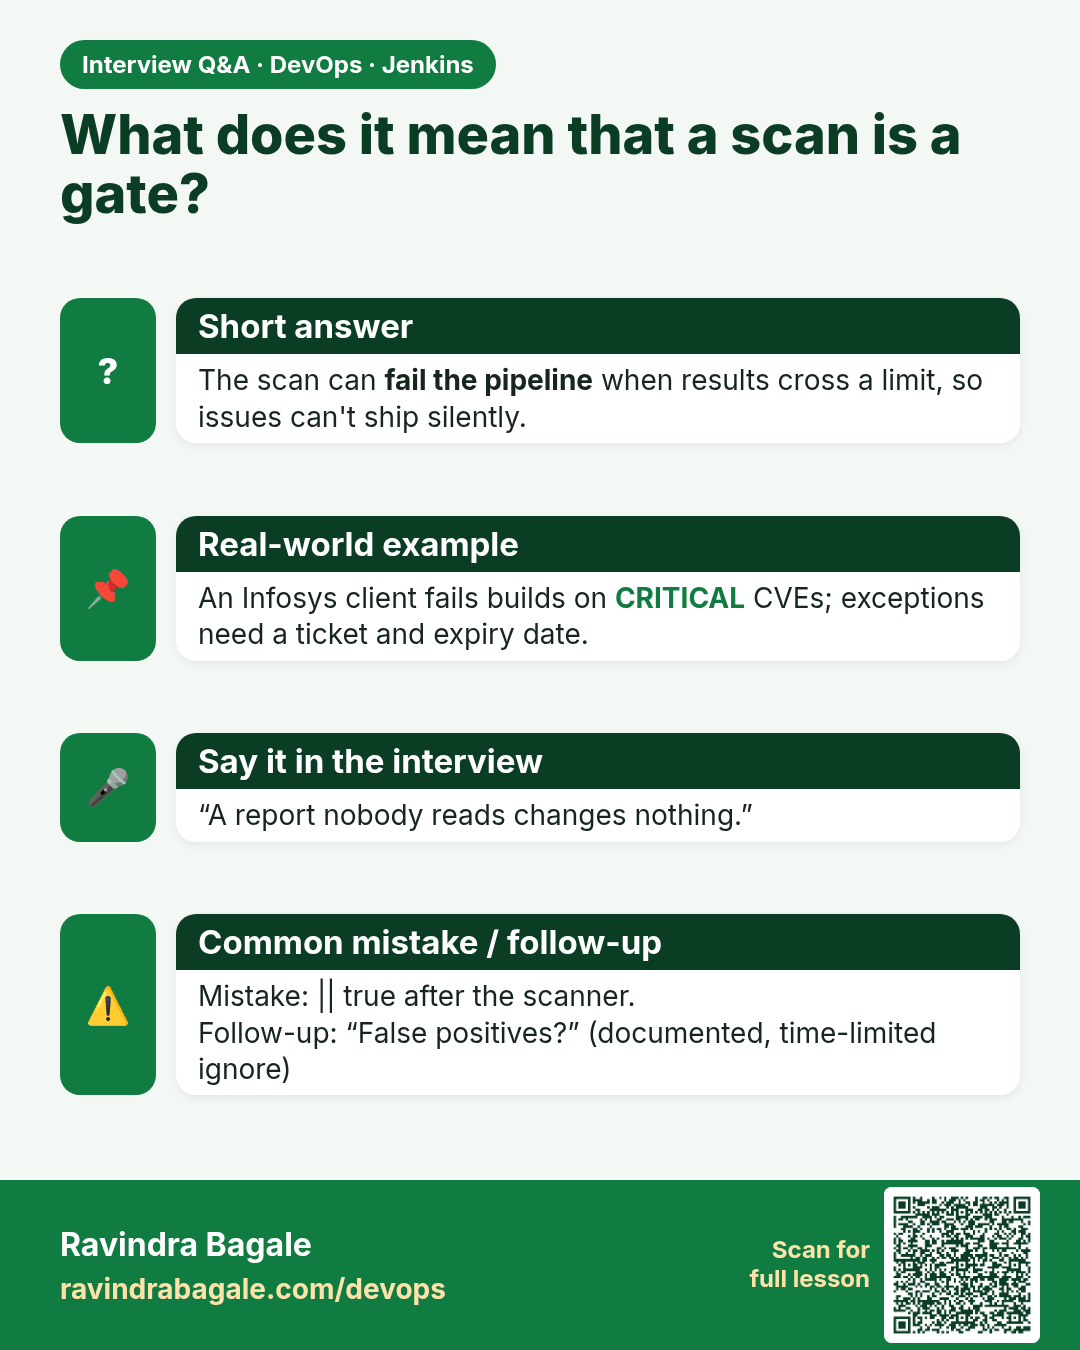
What does it mean that a scan is a gate? The scan can fail the pipeline when results cross a limit, so issues can't ship silently.
Interview card 1 of 11: What does it mean that a scan is a gate? · Download PNG · Open card page

Lesson: 29.1 Scans are gates, not decorations
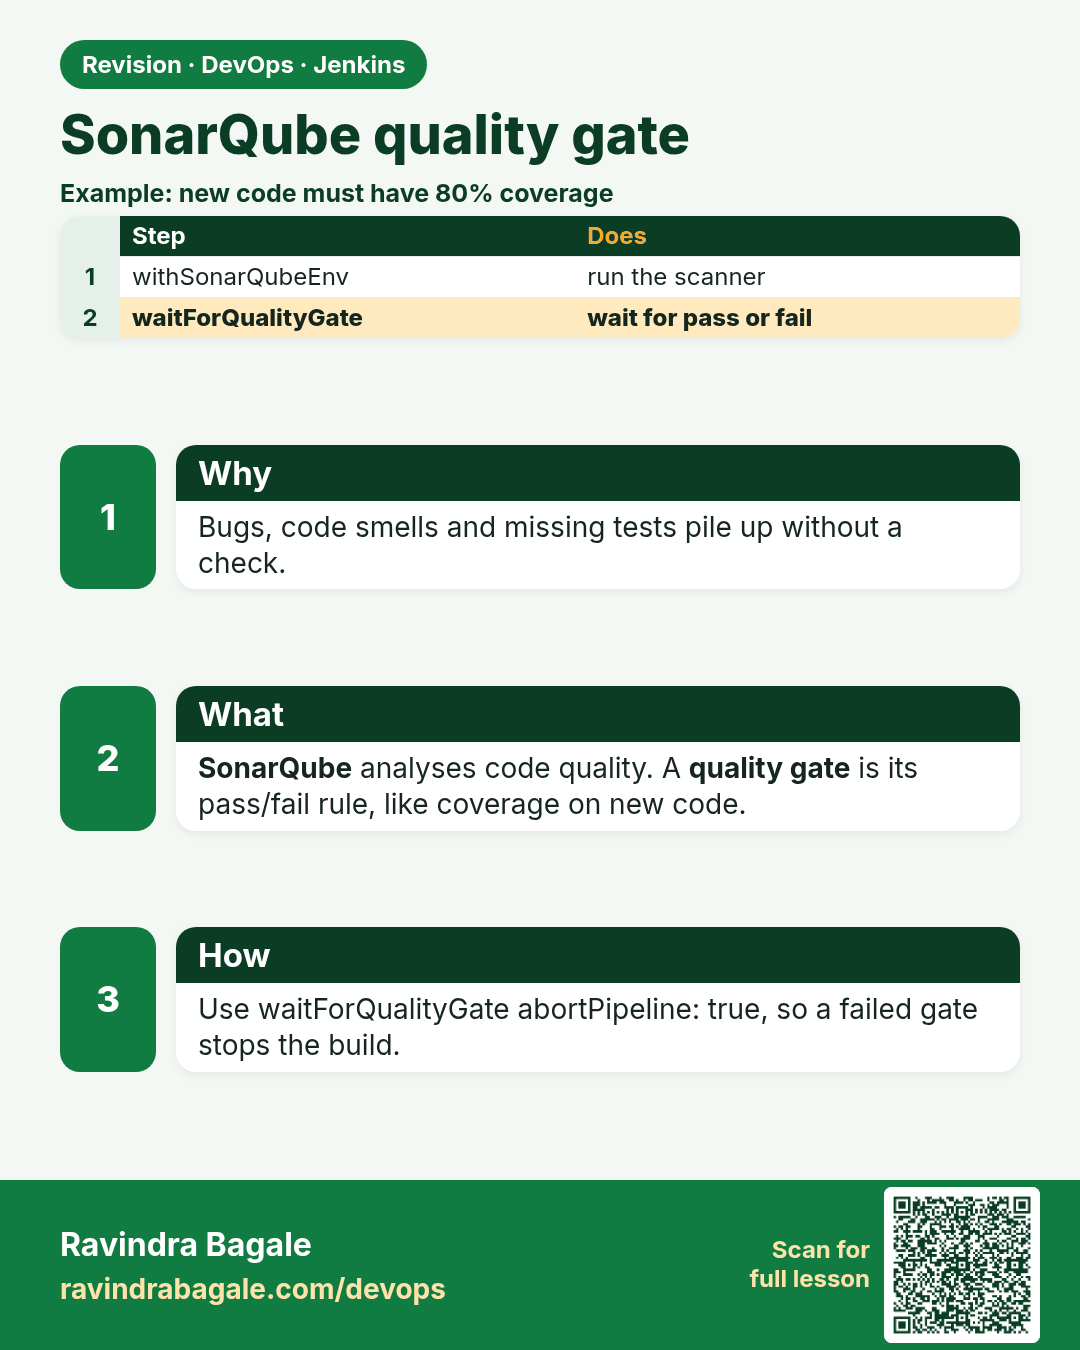
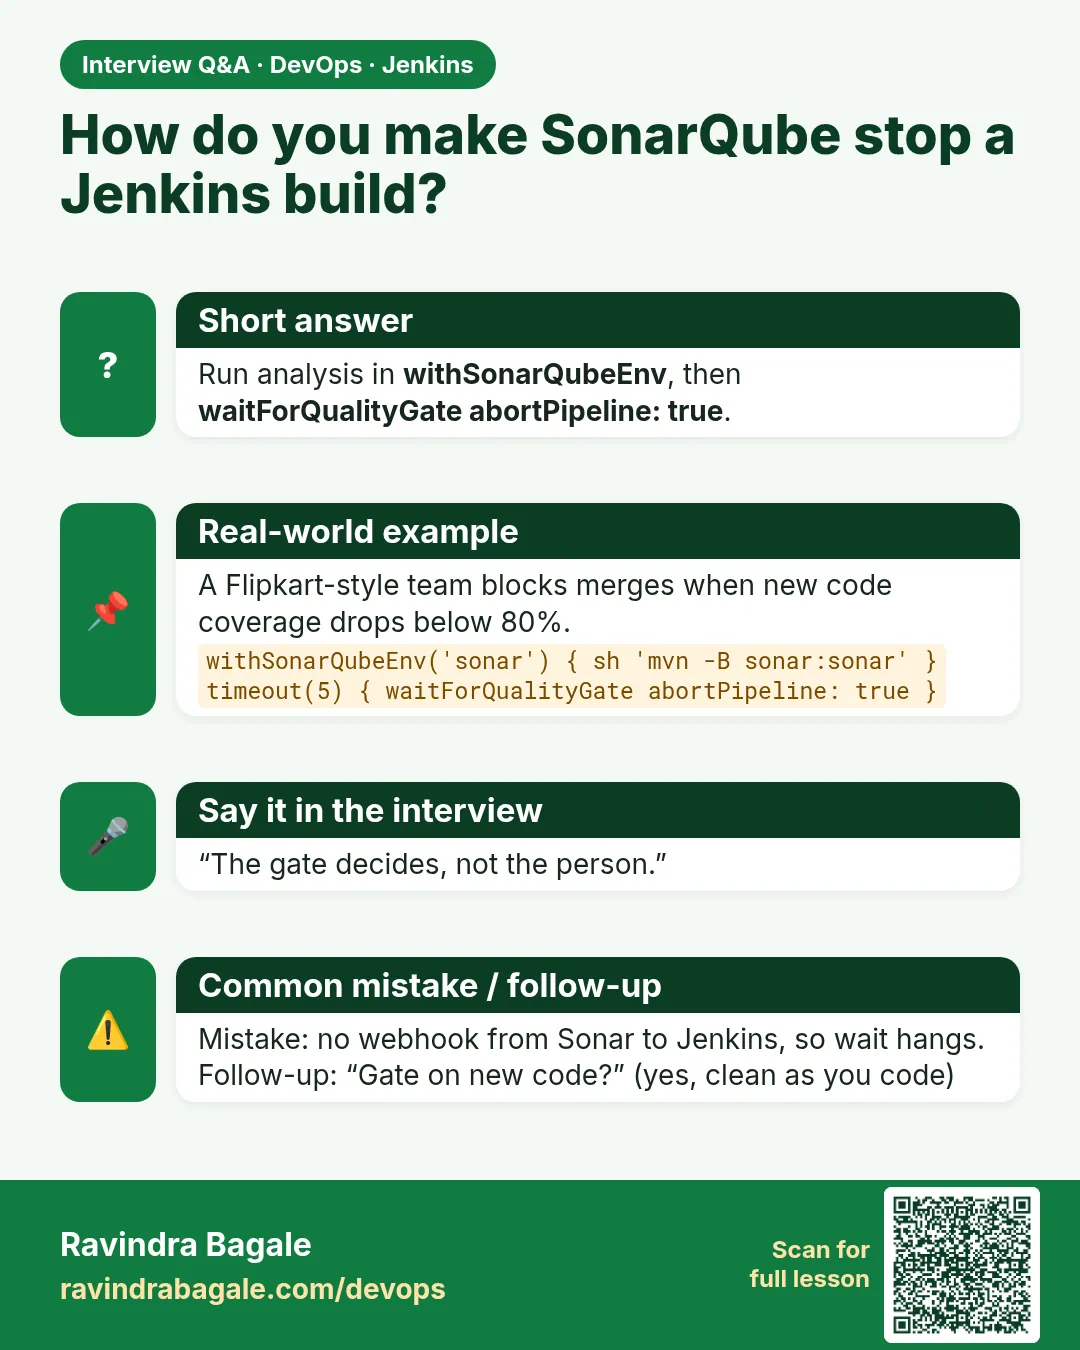
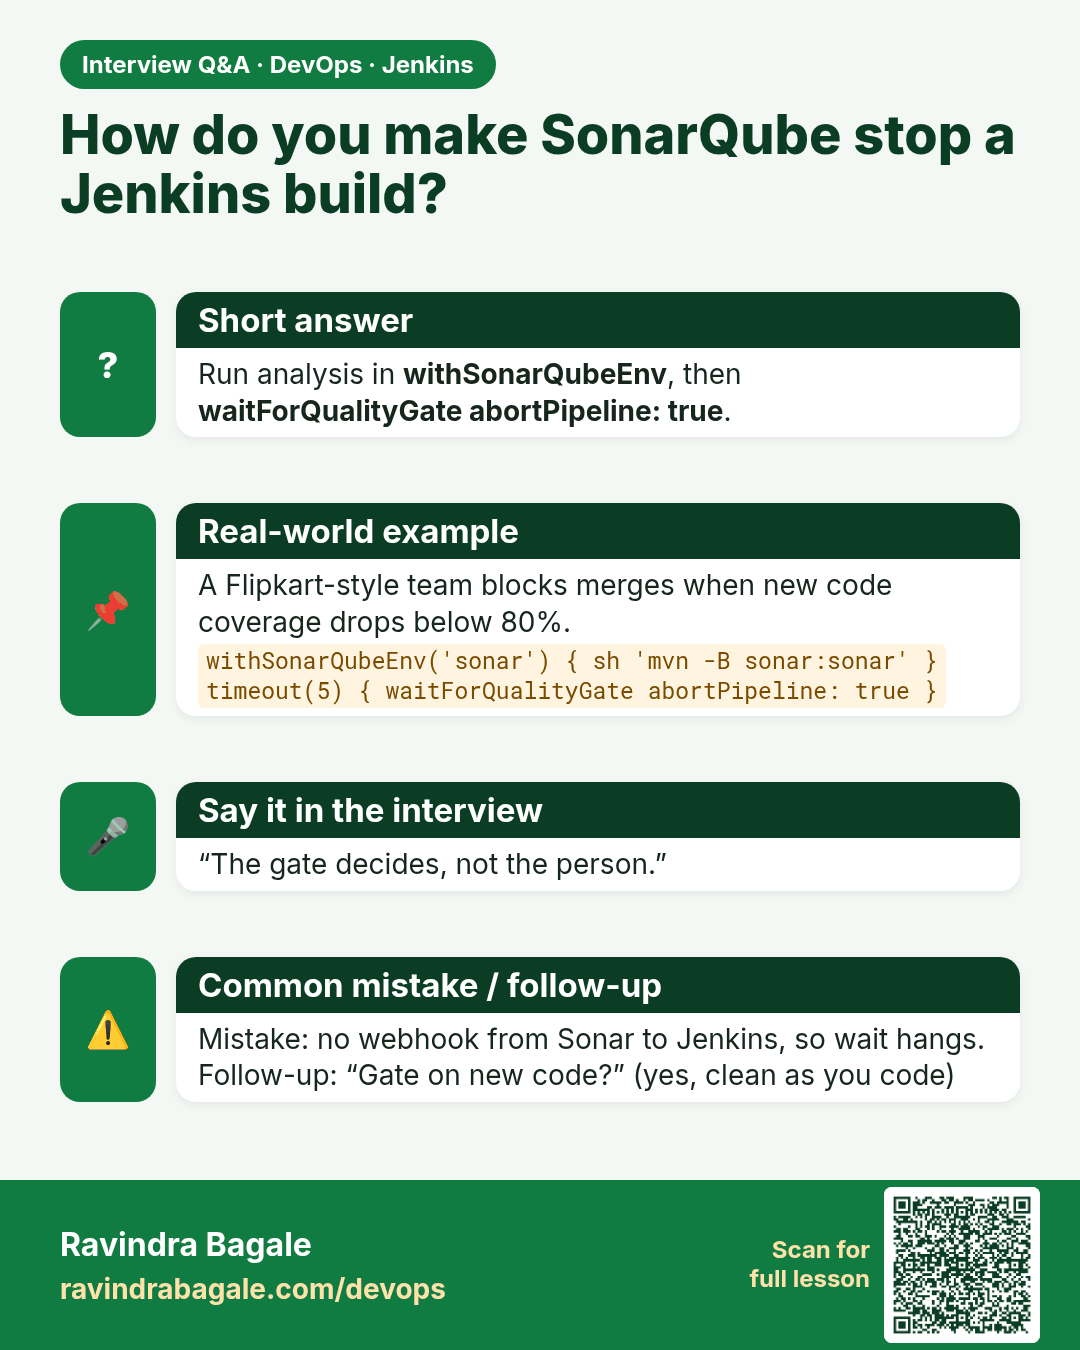
How do you make SonarQube stop a Jenkins build? Run analysis in withSonarQubeEnv, then waitForQualityGate abortPipeline: true.
Interview card 2 of 11: How do you make SonarQube stop a Jenkins build? · Download PNG · Open card page

Lesson: 29.2 SonarQube quality gate
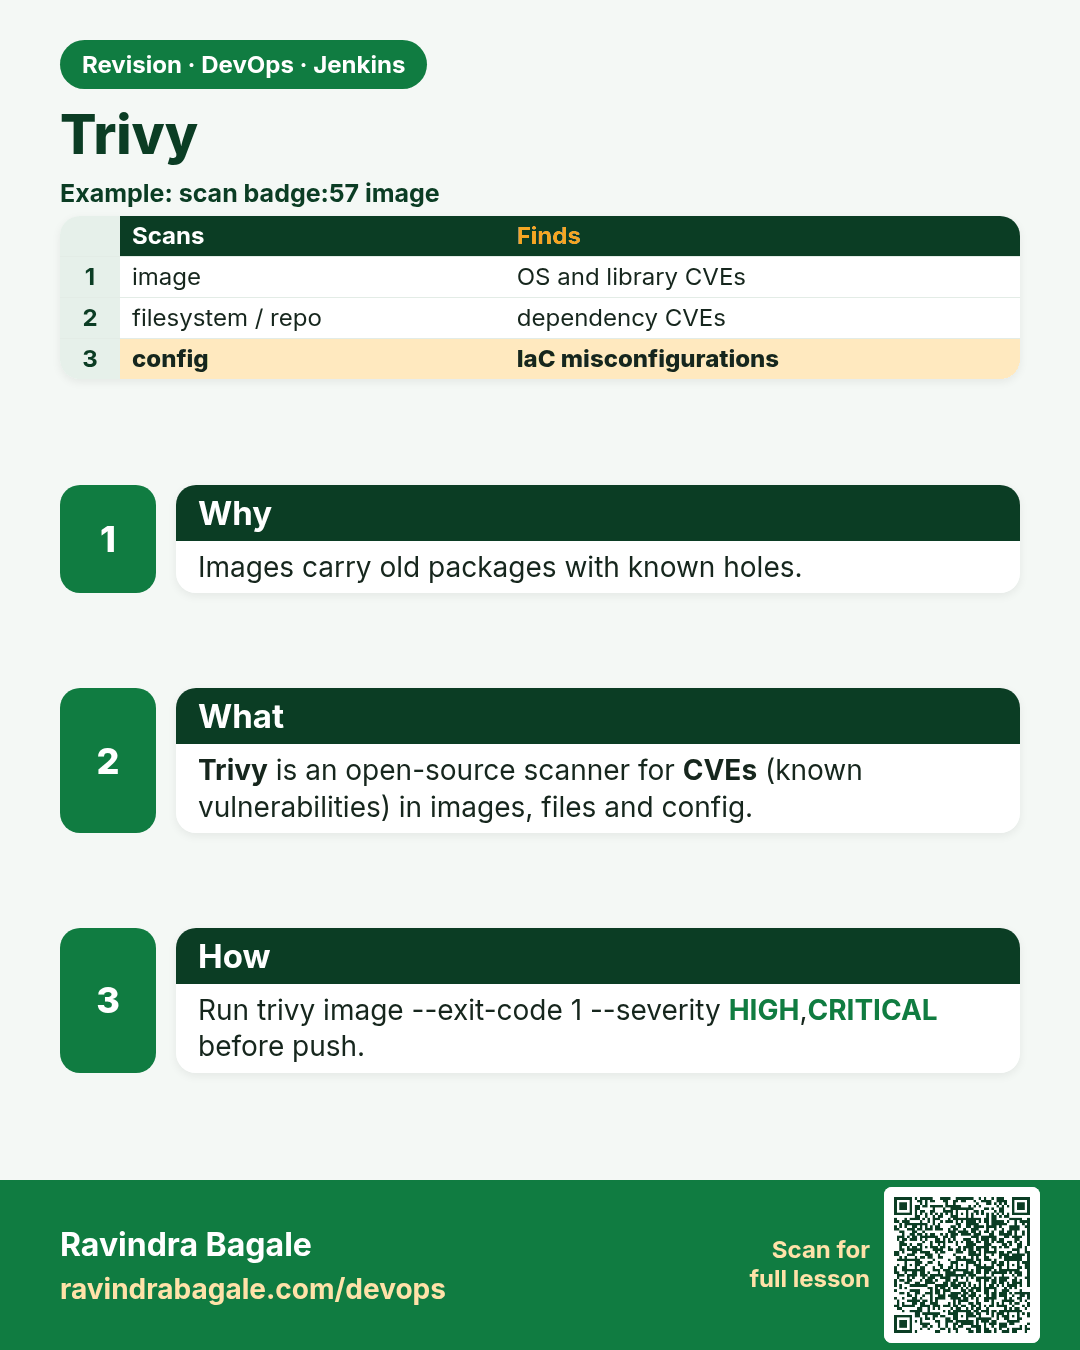
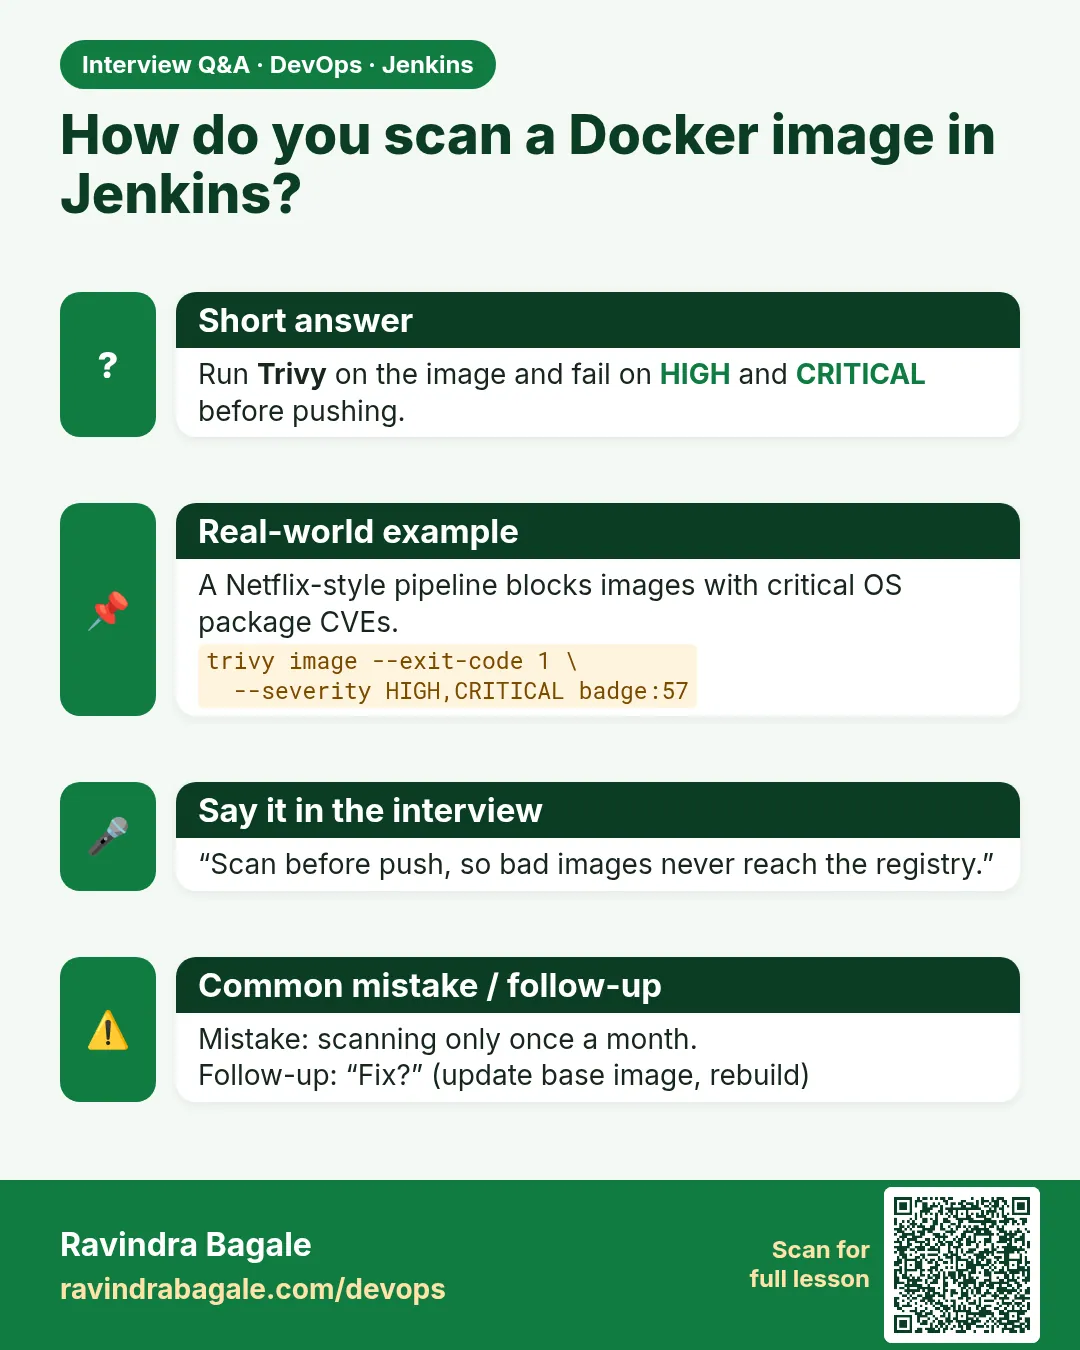
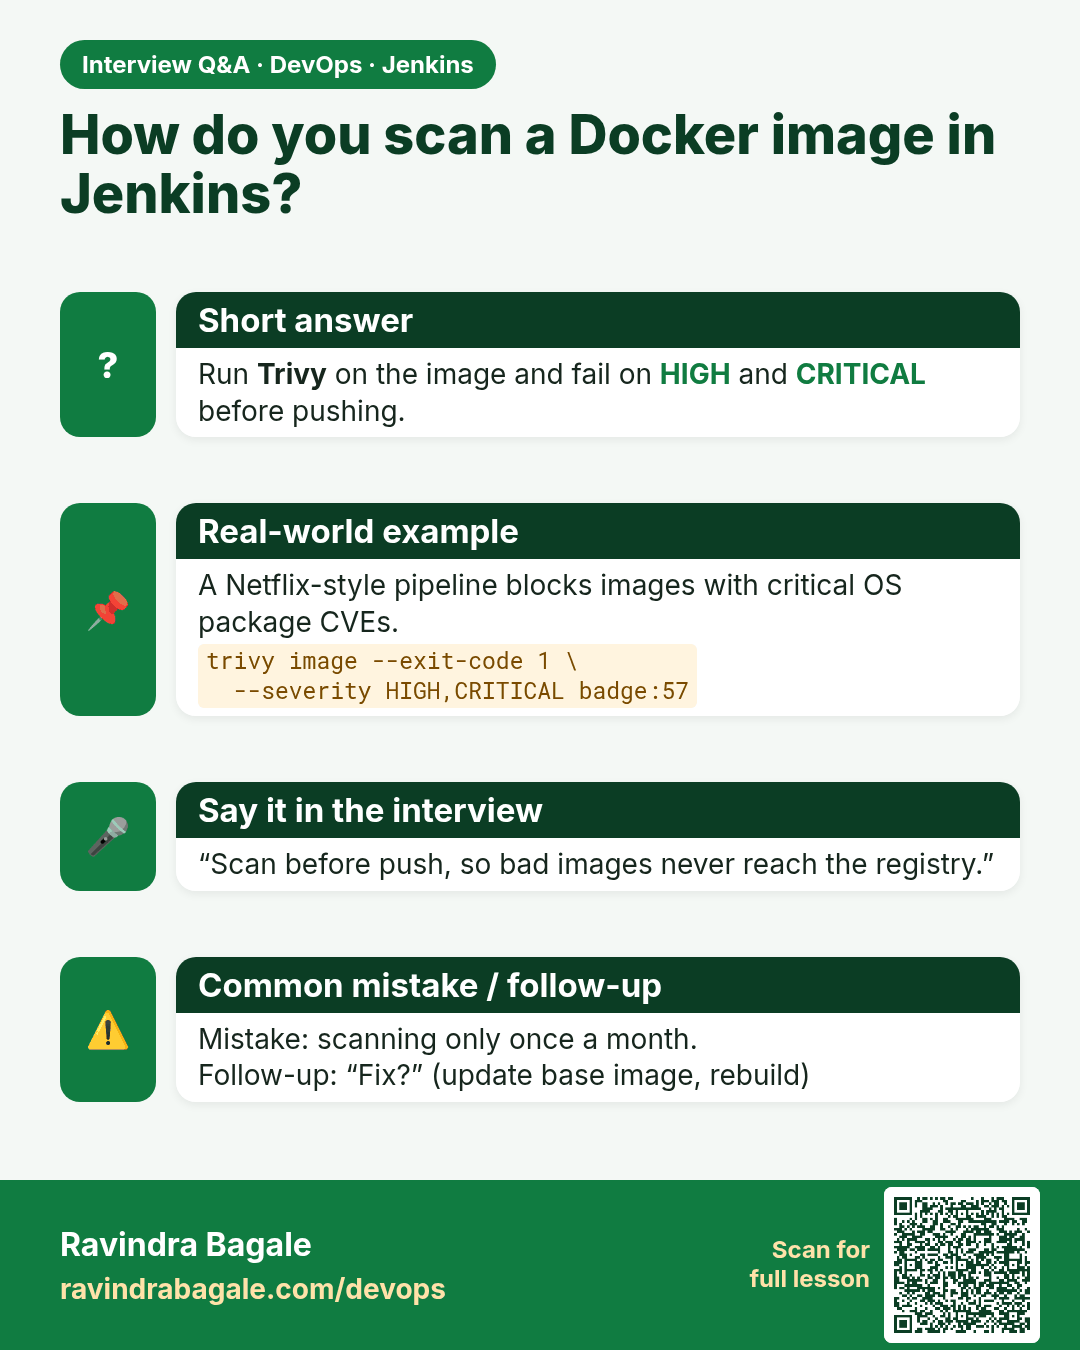
How do you scan a Docker image in Jenkins? Run Trivy on the image and fail on HIGH and CRITICAL before pushing.
Interview card 3 of 11: How do you scan a Docker image in Jenkins? · Download PNG · Open card page

Lesson: 29.3 Trivy

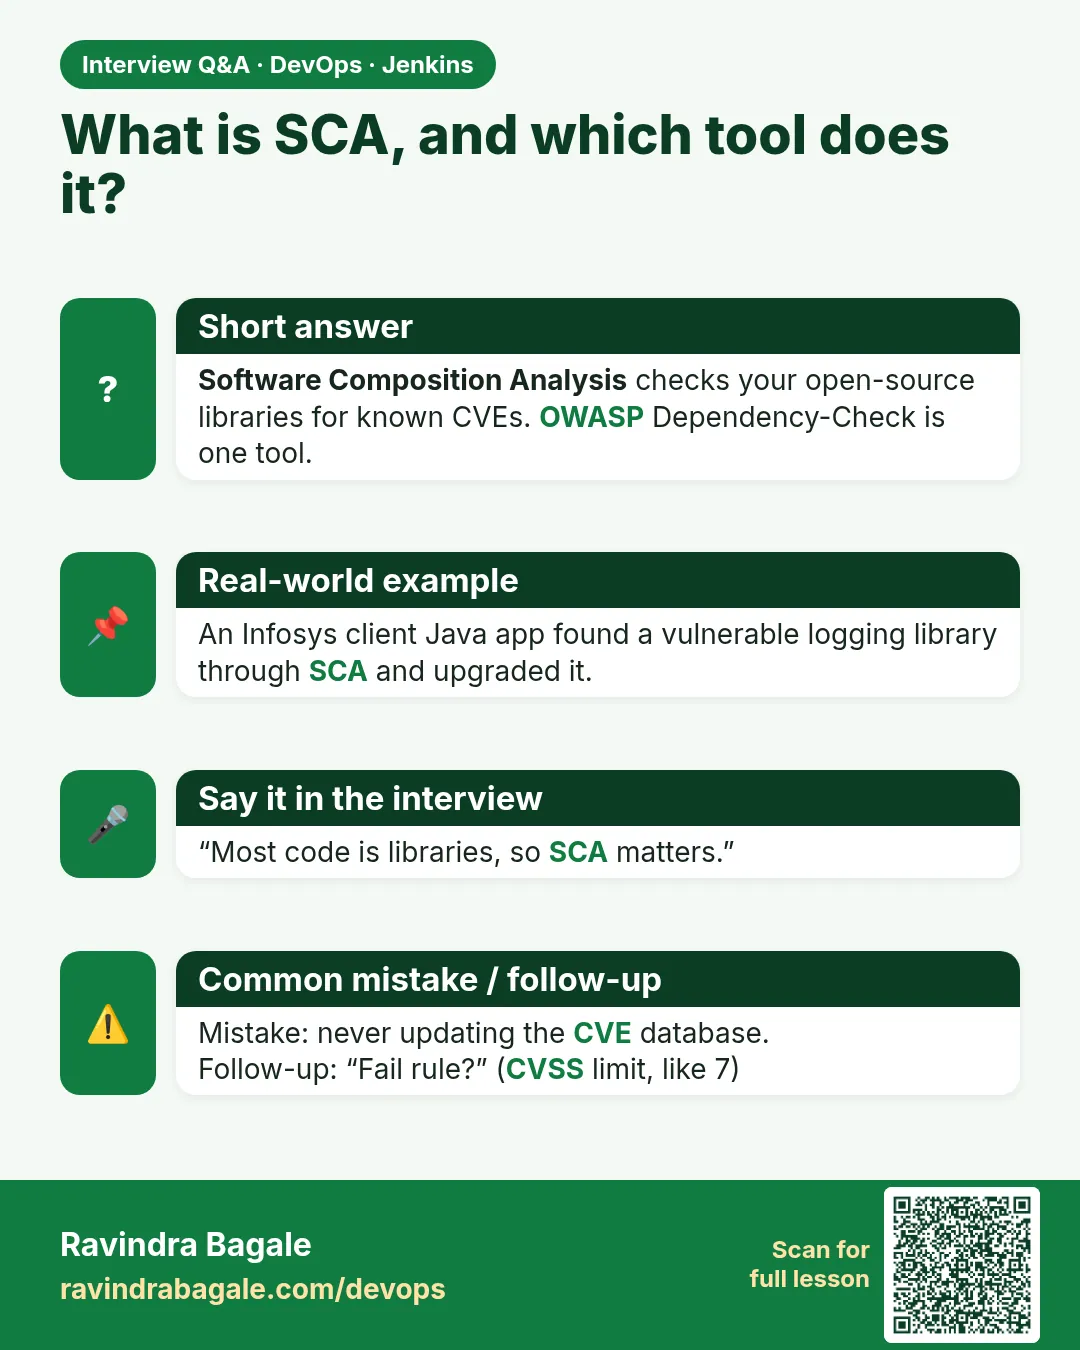
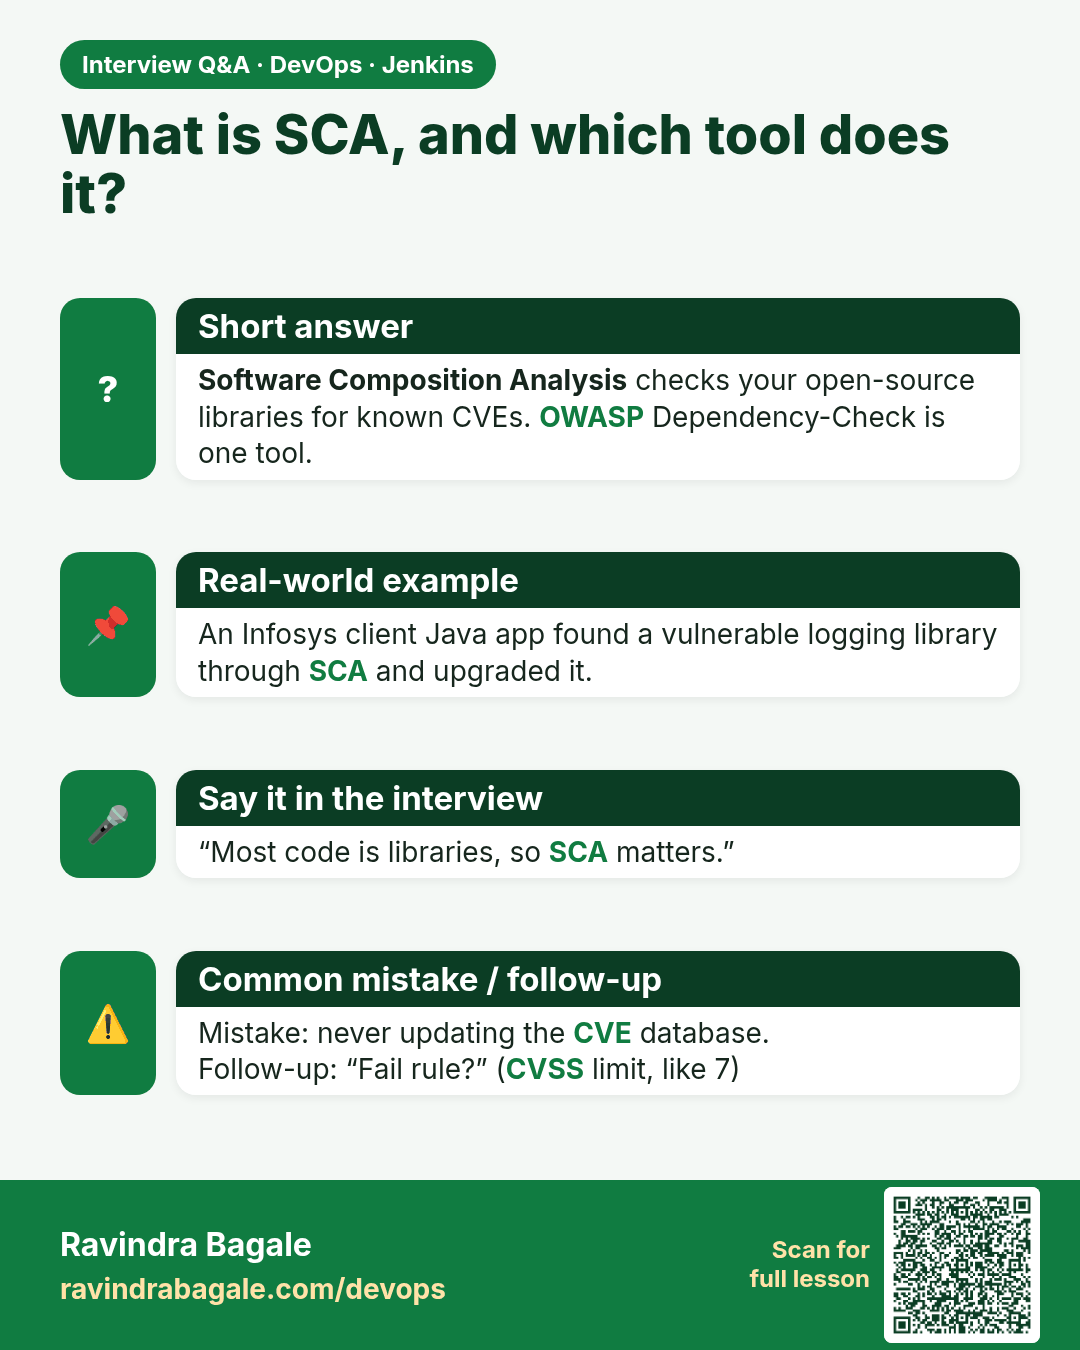
What is SCA, and which tool does it? Software Composition Analysis checks your open-source libraries for known CVEs. OWASP Dependency-Check is one tool.
Interview card 4 of 11: What is SCA, and which tool does it? · Download PNG · Open card page

Lesson: 29.4 OWASP Dependency-Check
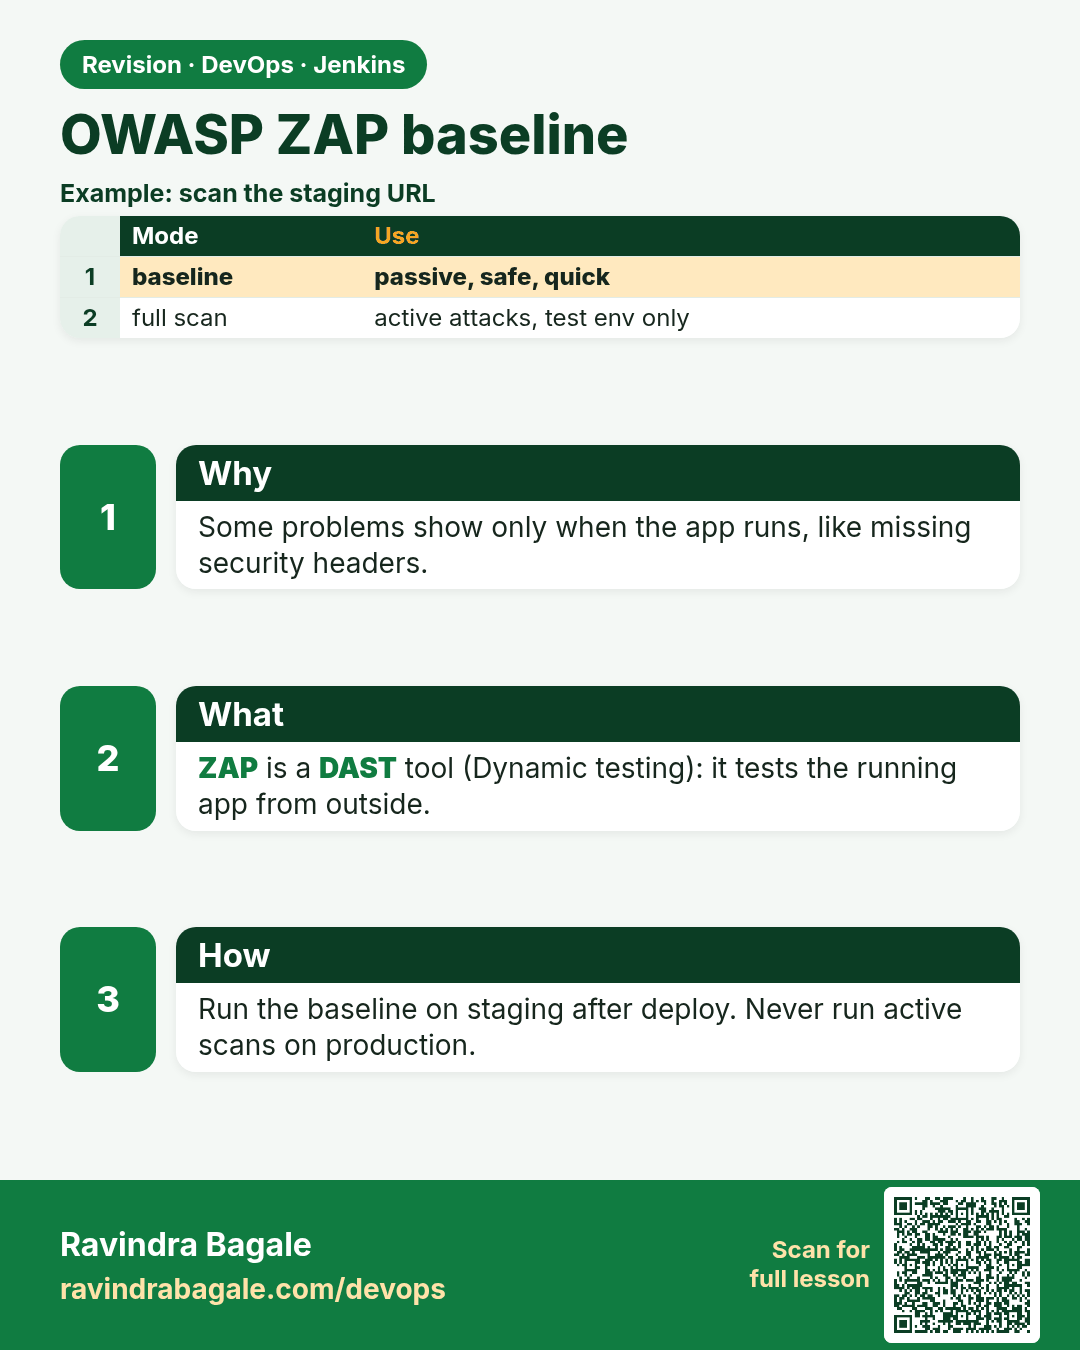
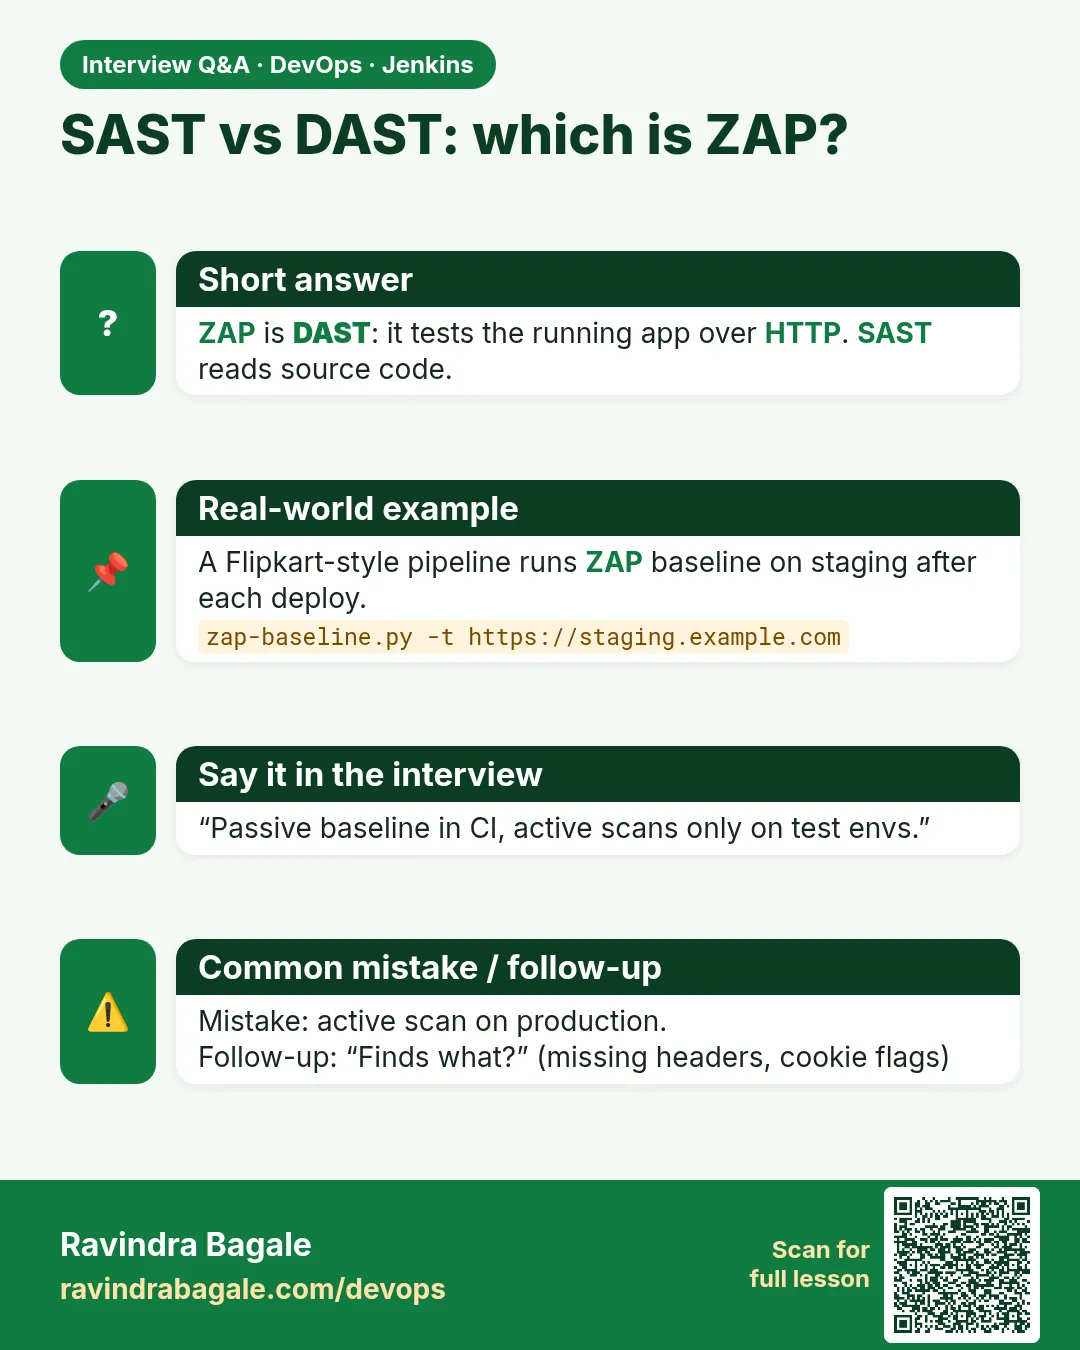
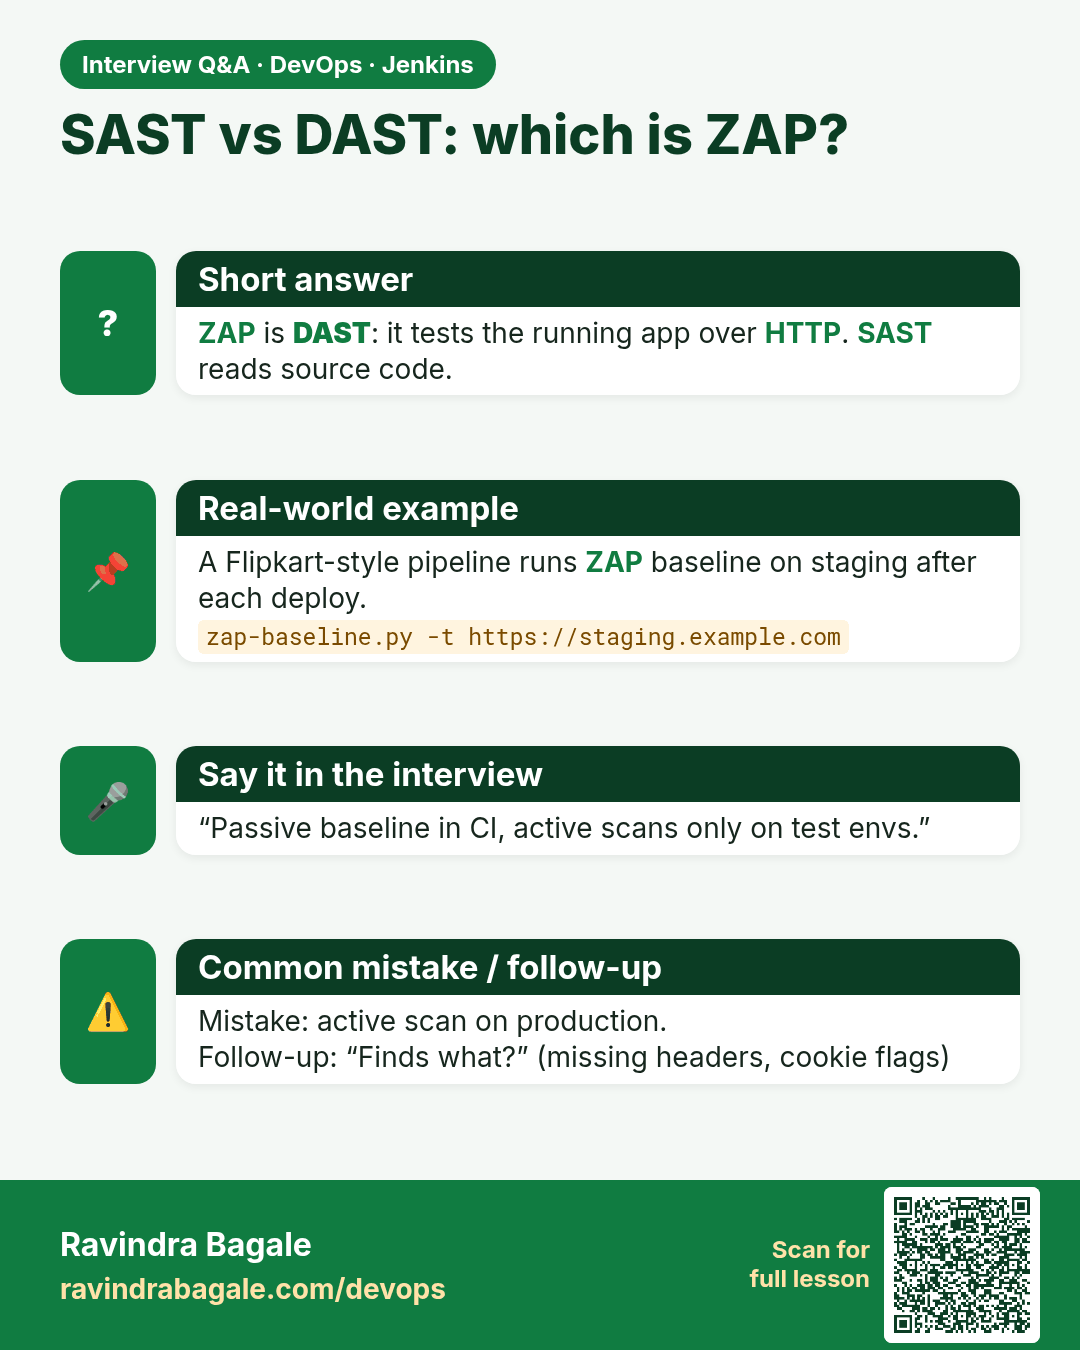
SAST vs DAST: which is ZAP? ZAP is DAST: it tests the running app over HTTP. SAST reads source code.
Interview card 5 of 11: SAST vs DAST: which is ZAP? · Download PNG · Open card page

Lesson: 29.5 ZAP baseline

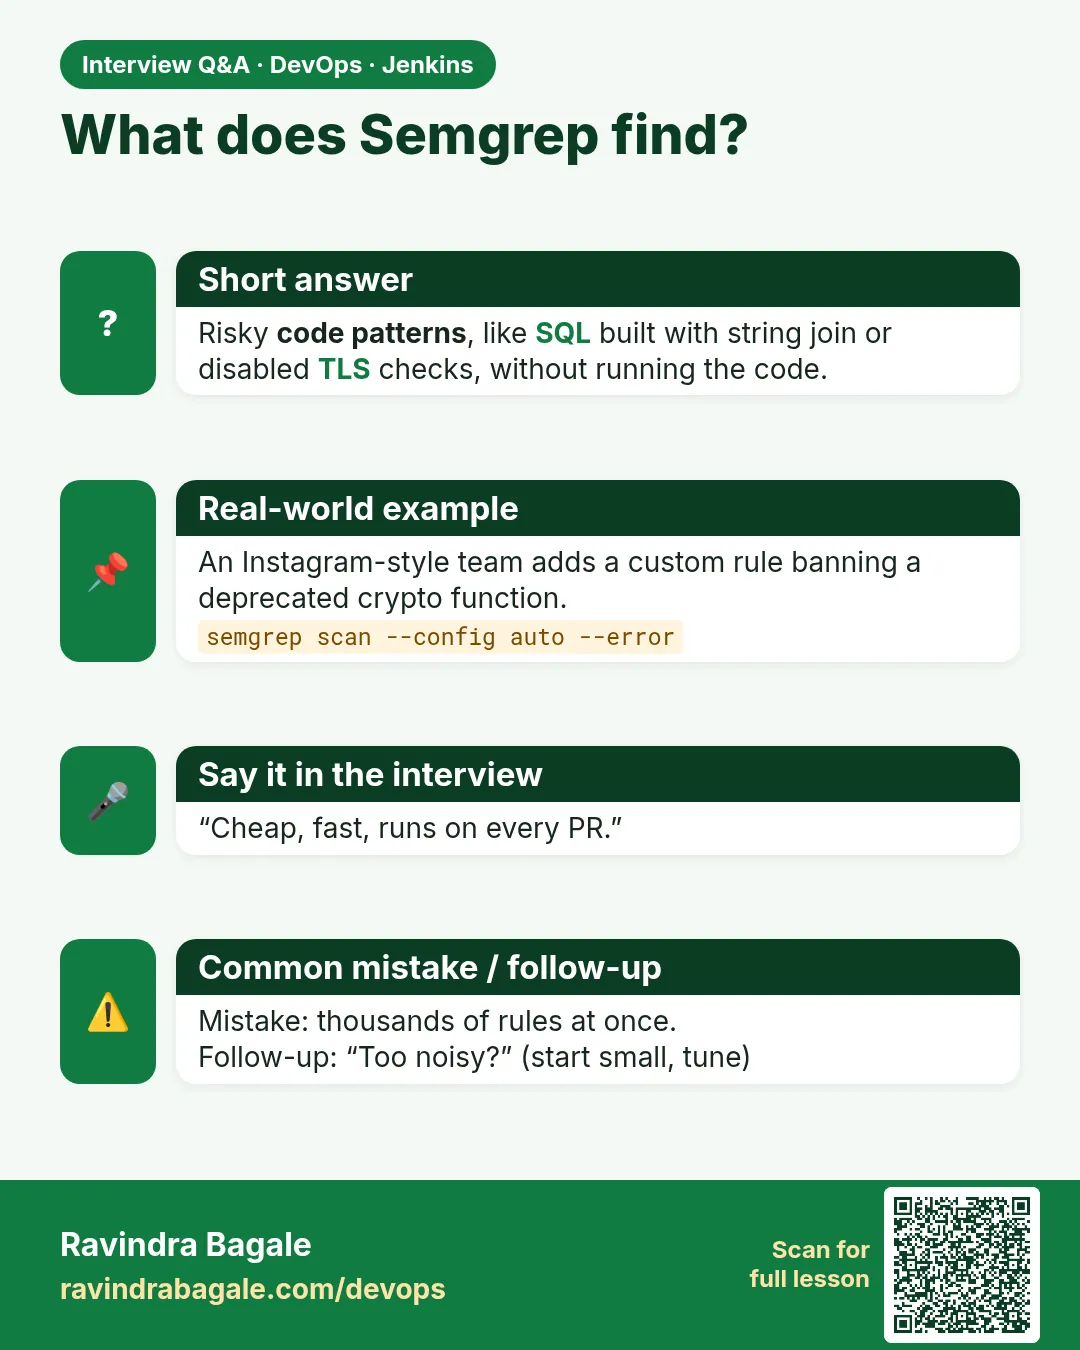
What does Semgrep find? Risky code patterns, like SQL built with string join or disabled TLS checks, without running the code.
Interview card 6 of 11: What does Semgrep find? · Download PNG · Open card page

Lesson: 29.6 Semgrep

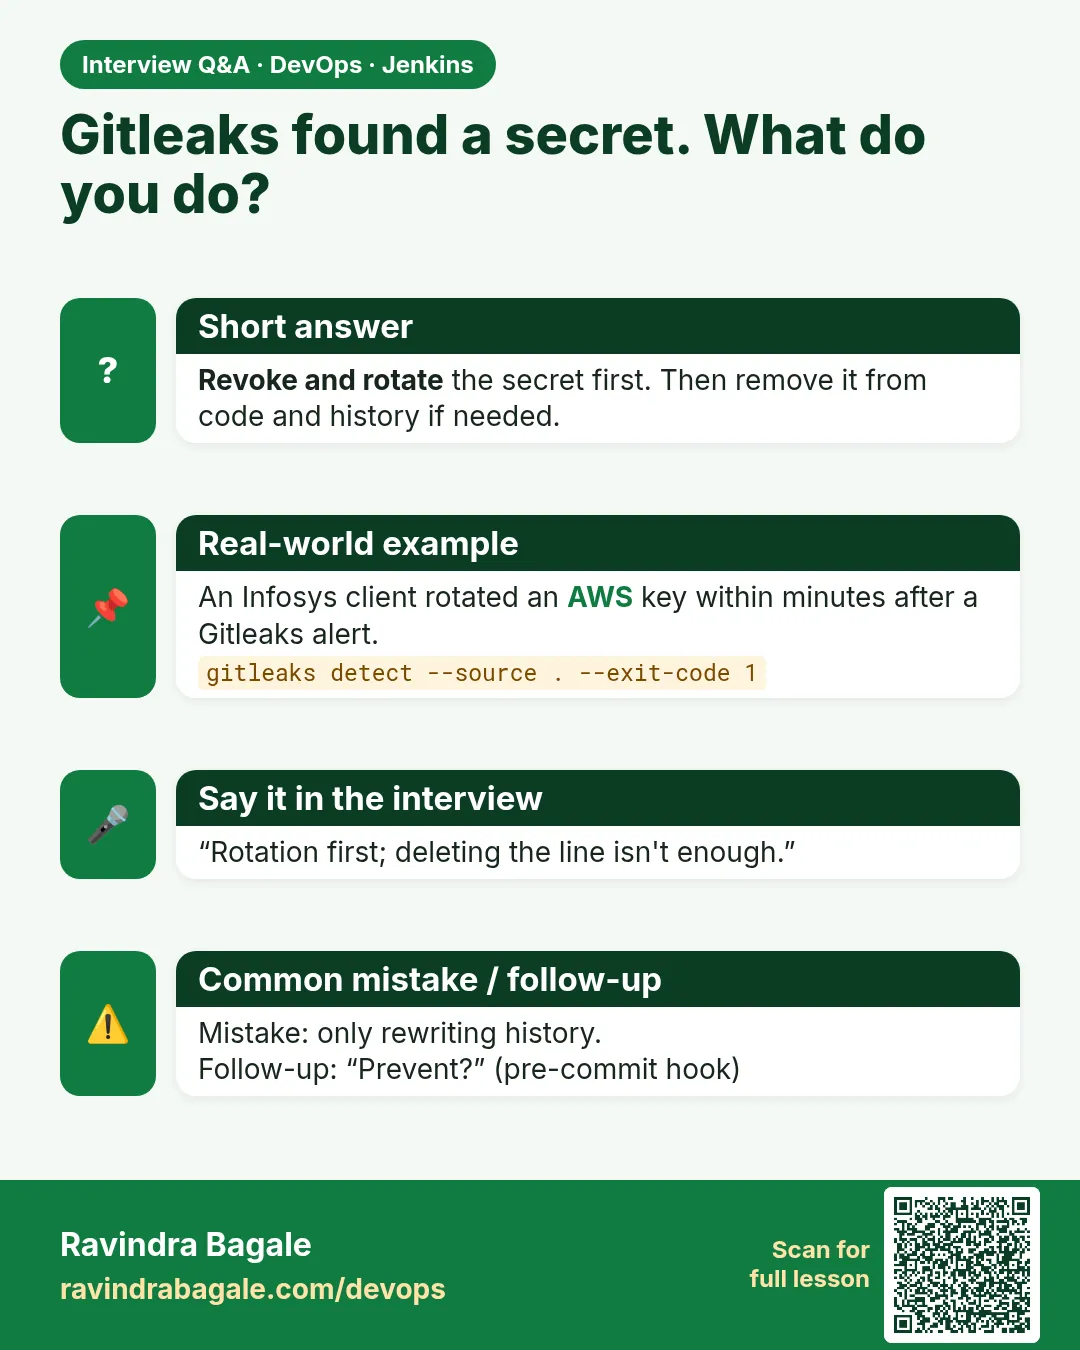
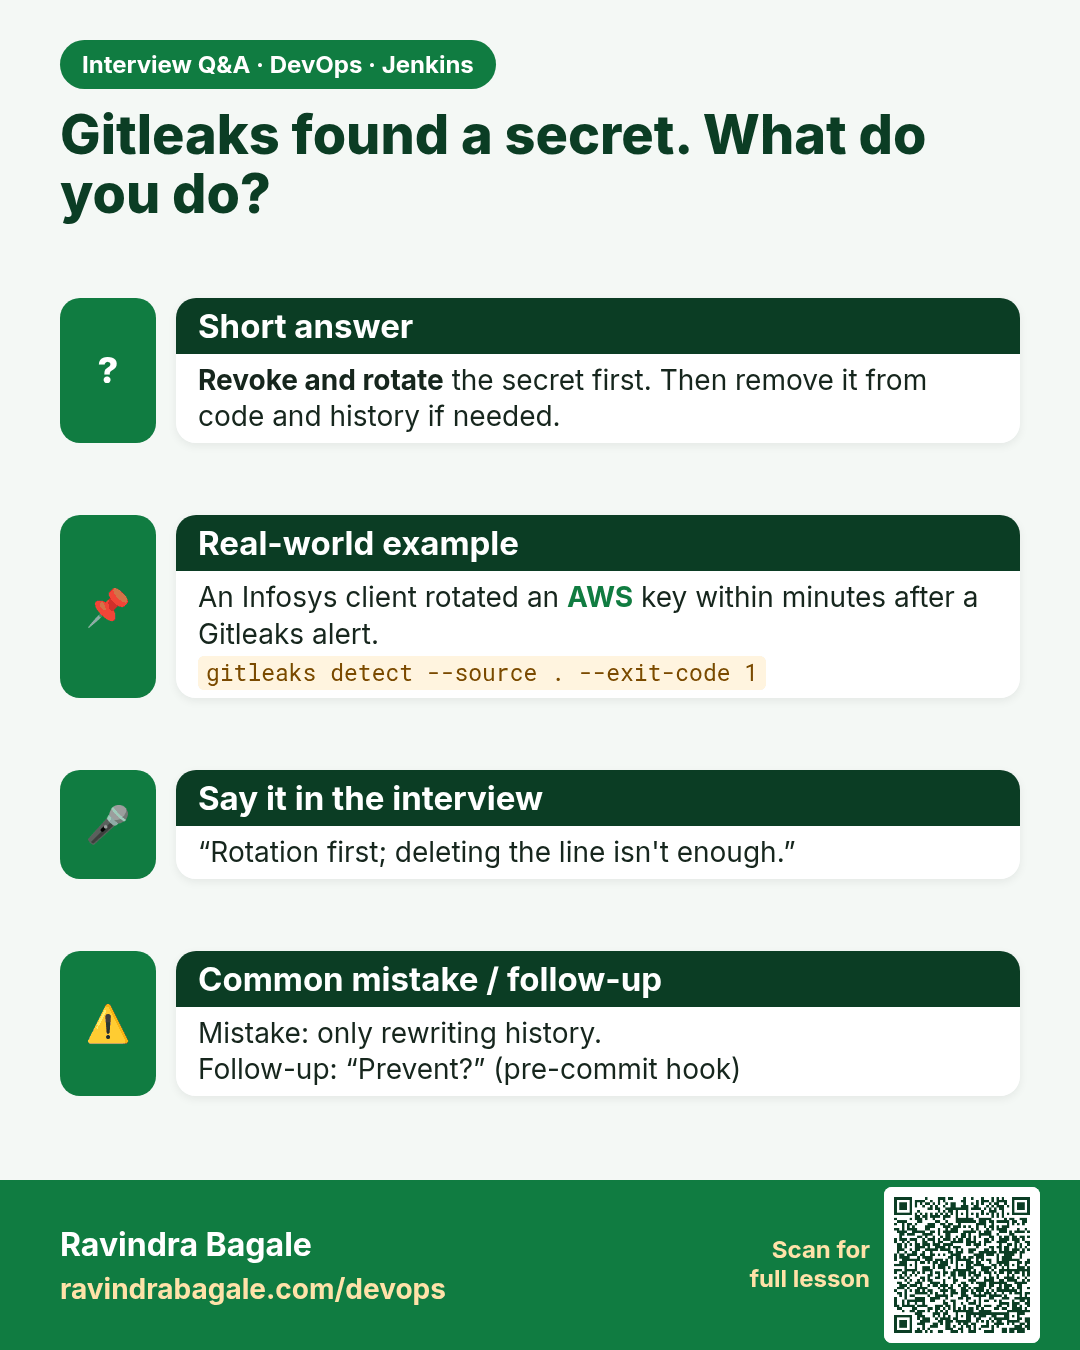
Gitleaks found a secret. What do you do? Revoke and rotate the secret first. Then remove it from code and history if needed.
Interview card 7 of 11: Gitleaks found a secret. What do you do? · Download PNG · Open card page

Lesson: 29.7 Gitleaks

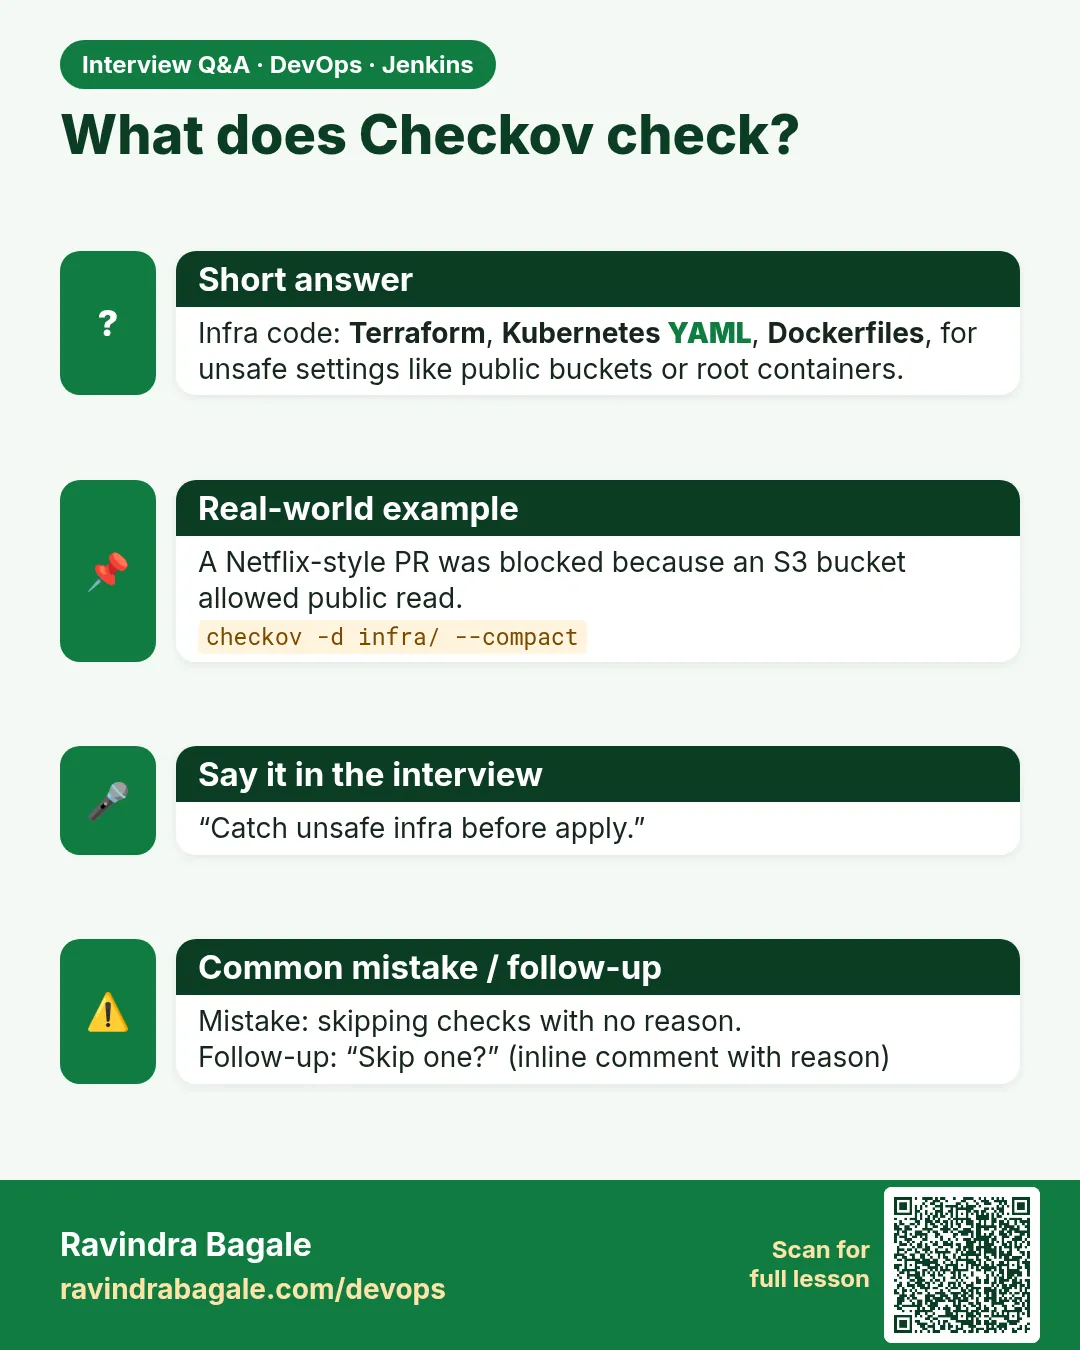
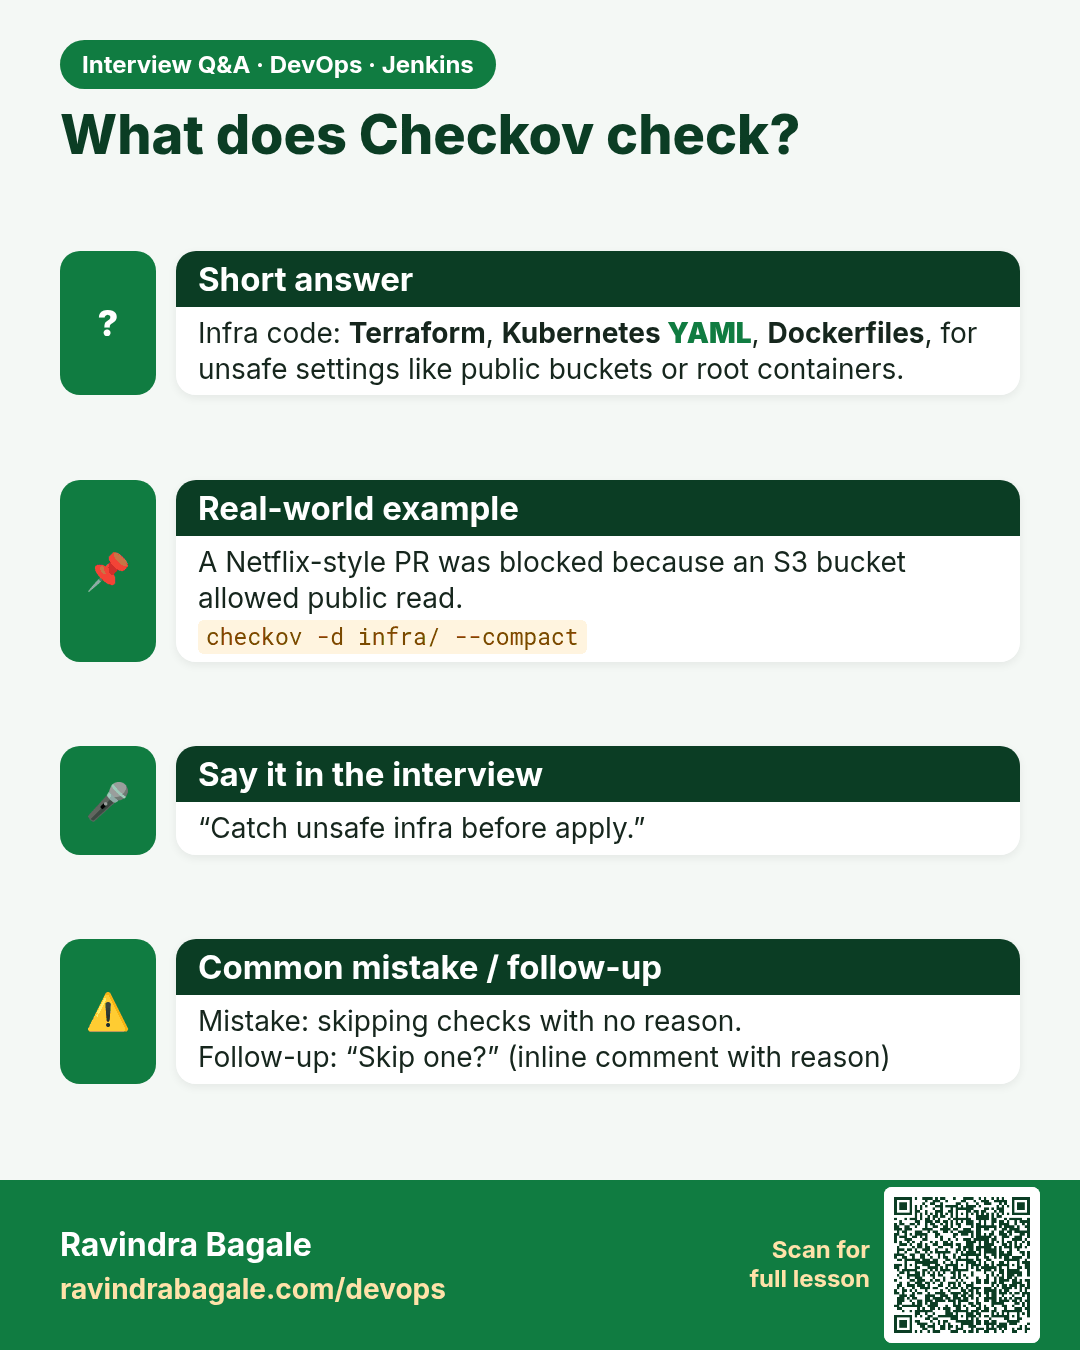
What does Checkov check? Infra code: Terraform, Kubernetes YAML, Dockerfiles, for unsafe settings like public buckets or root containers.
Interview card 8 of 11: What does Checkov check? · Download PNG · Open card page

Lesson: 29.8 Checkov

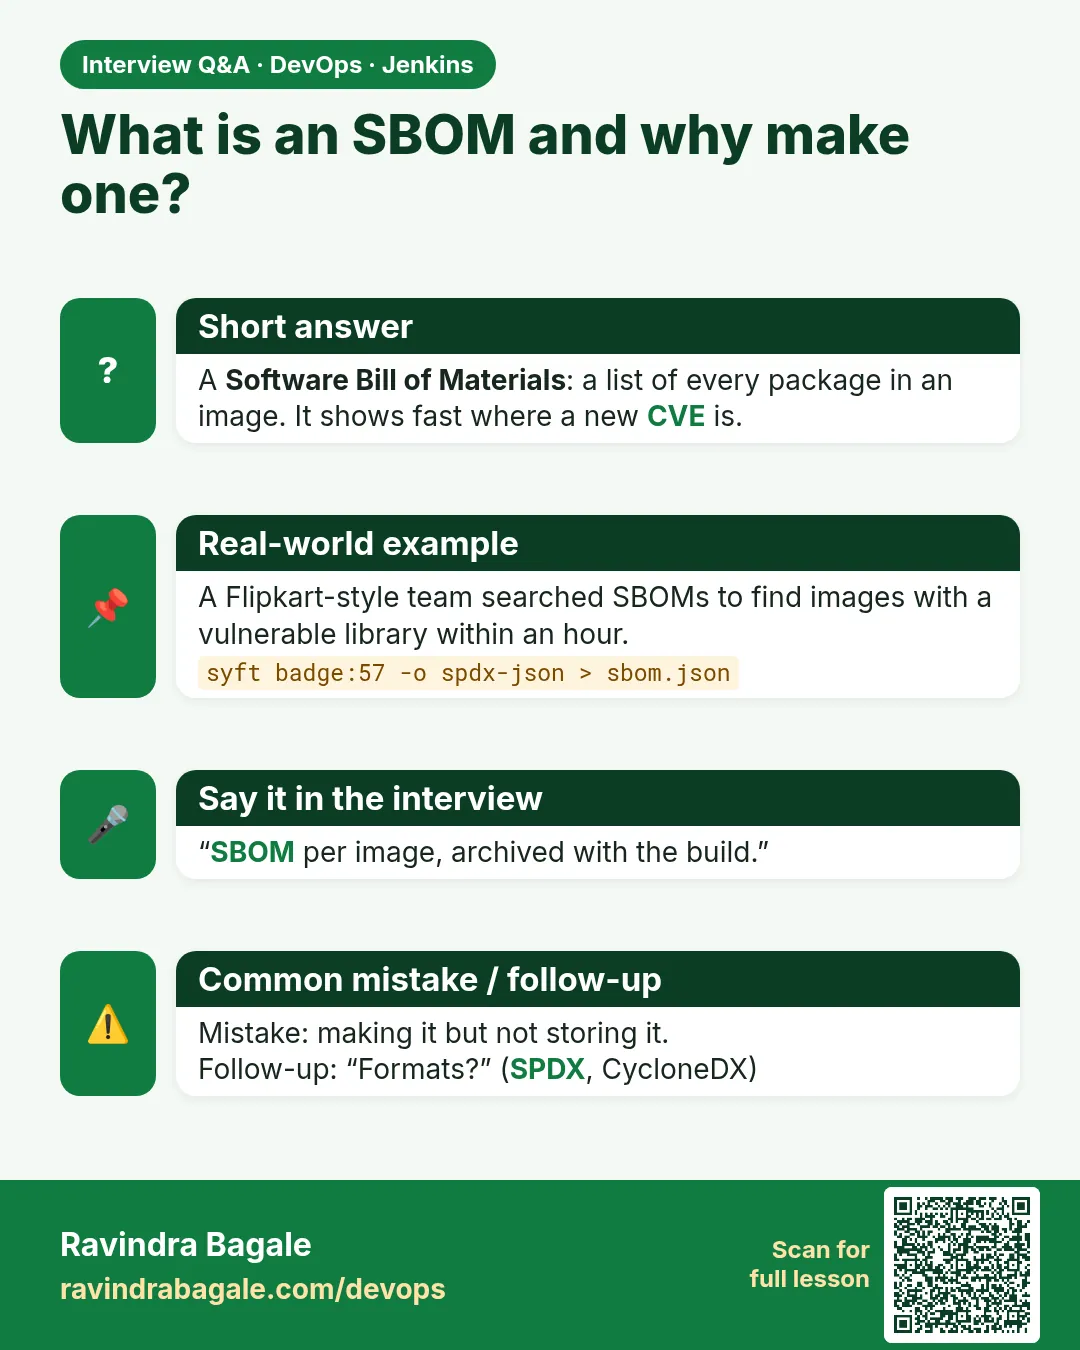
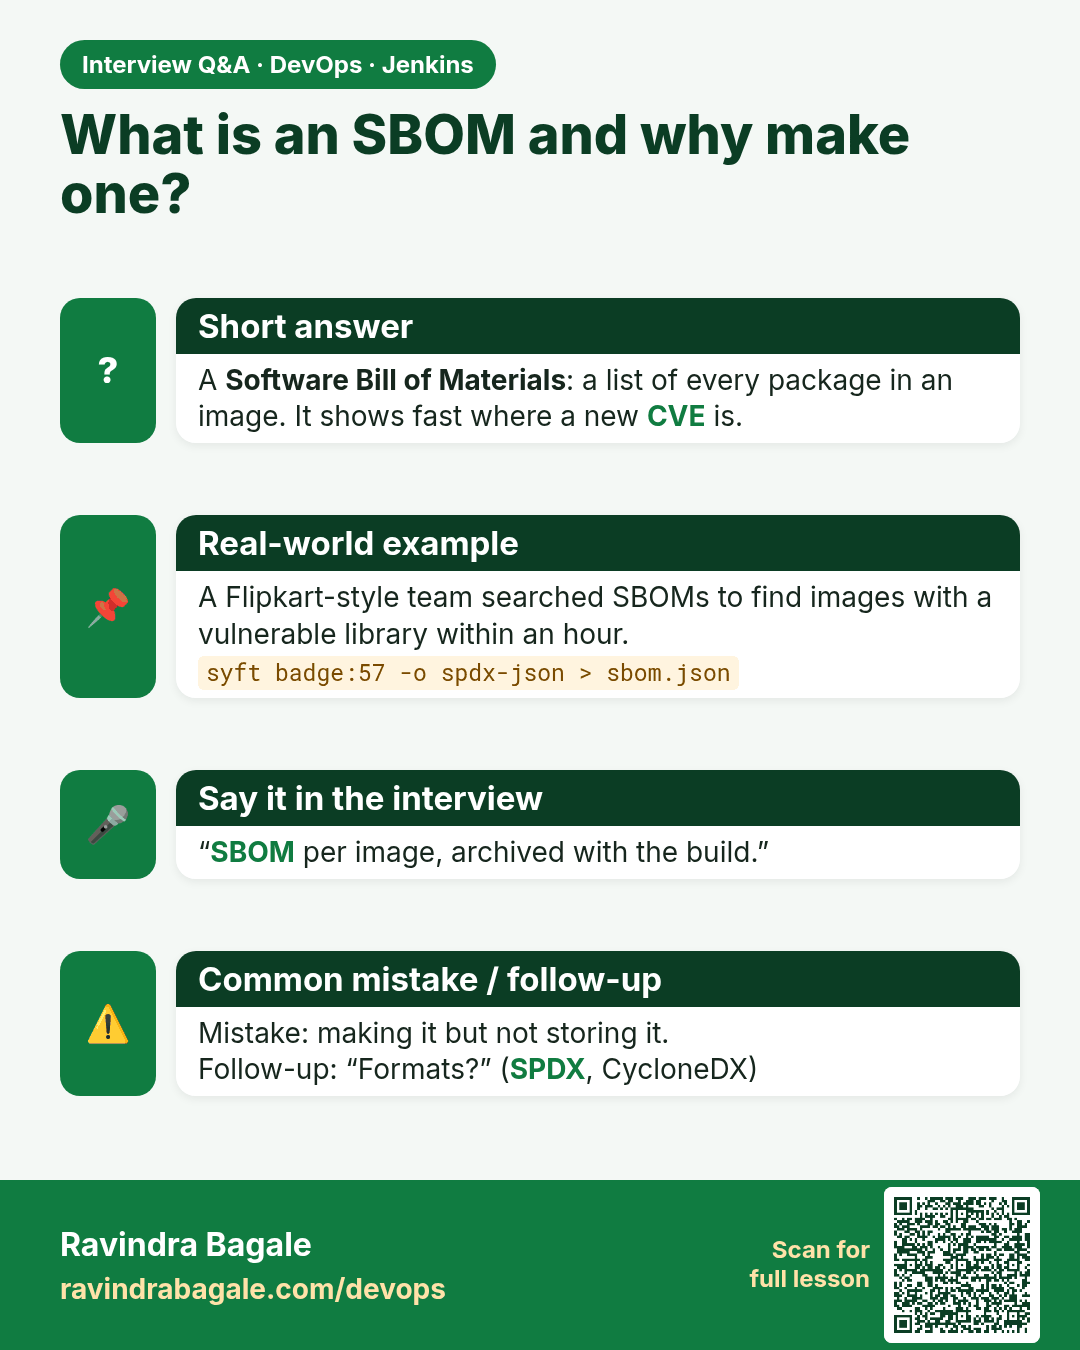
What is an SBOM and why make one? A Software Bill of Materials: a list of every package in an image. It shows fast where a new CVE is.
Interview card 9 of 11: What is an SBOM and why make one? · Download PNG · Open card page

Lesson: 29.9 Syft SBOM

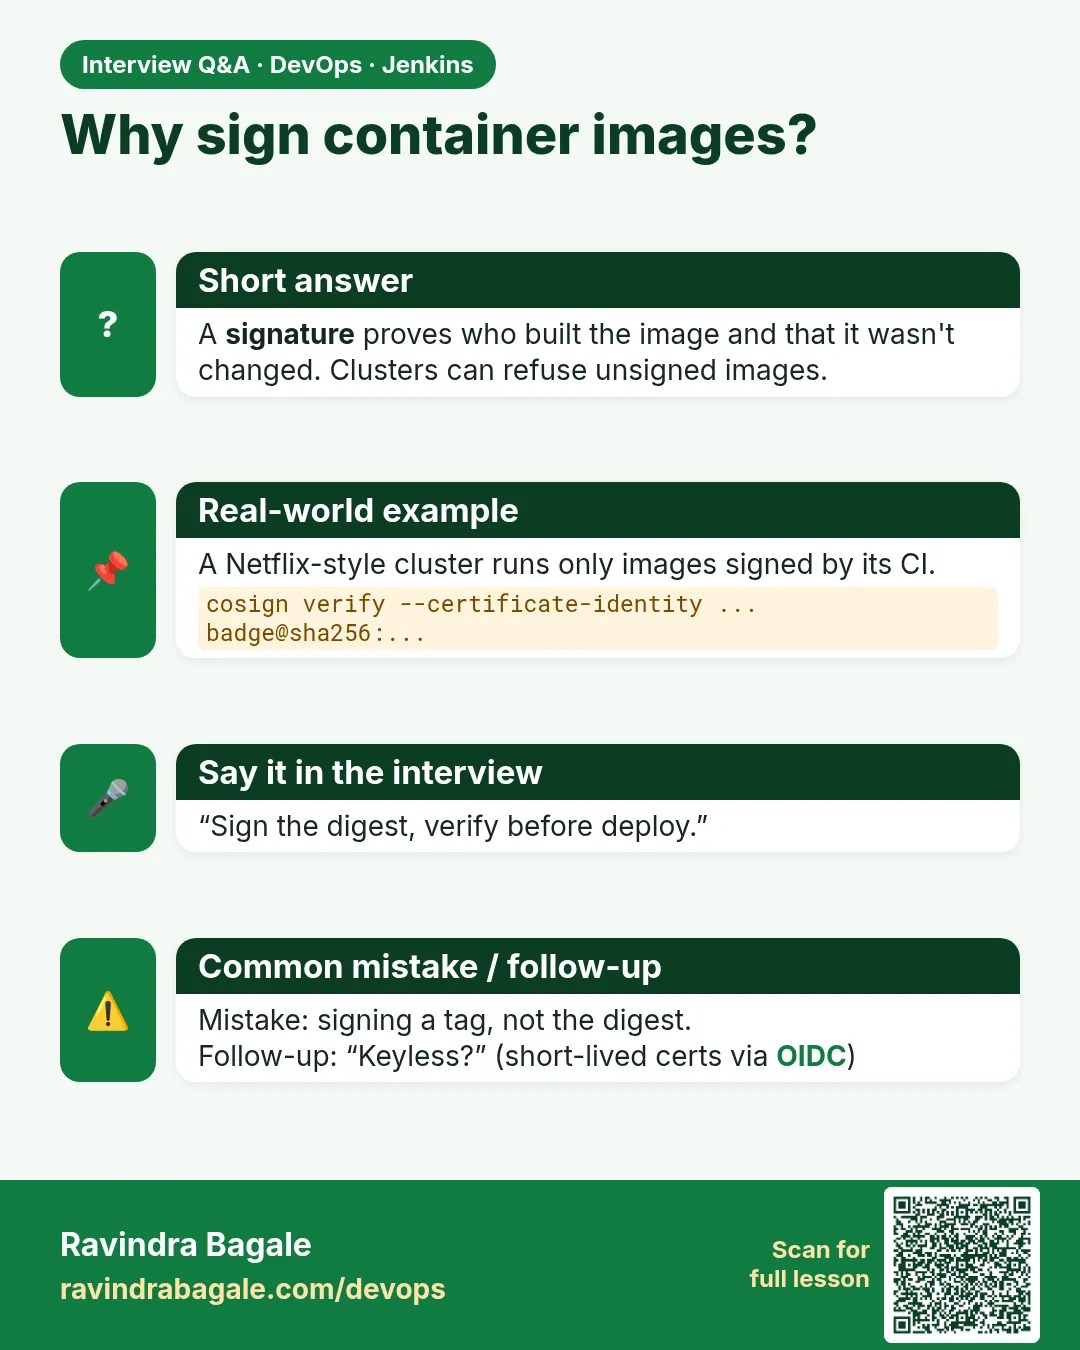
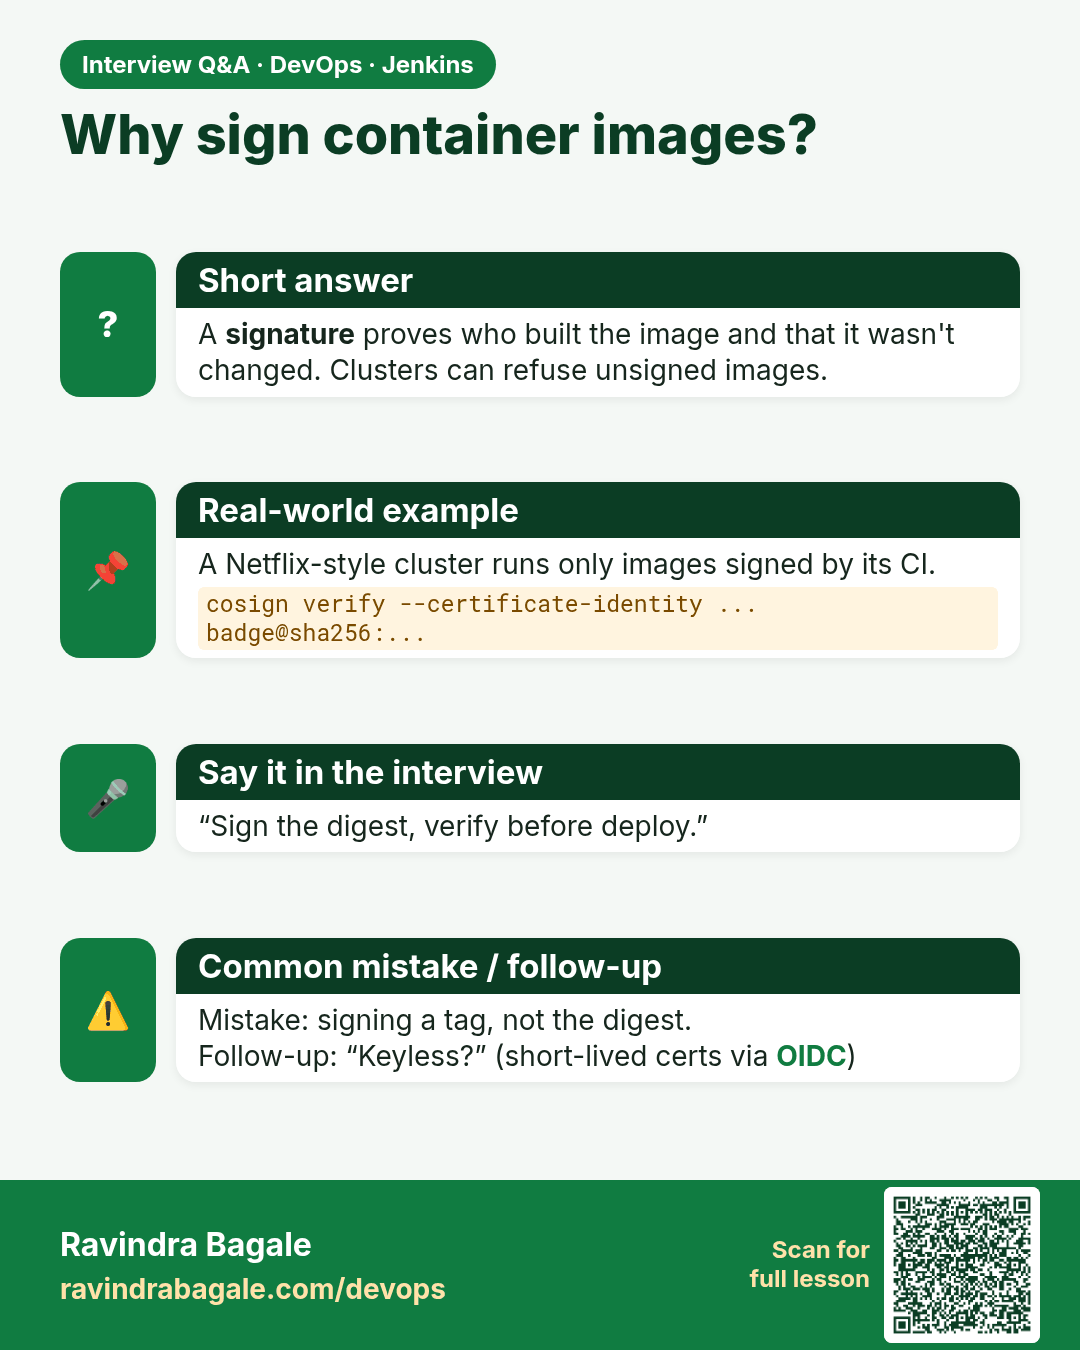
Why sign container images? A signature proves who built the image and that it wasn't changed. Clusters can refuse unsigned images.
Interview card 10 of 11: Why sign container images? · Download PNG · Open card page

Lesson: 29.10 Cosign, as a concept, with no keys
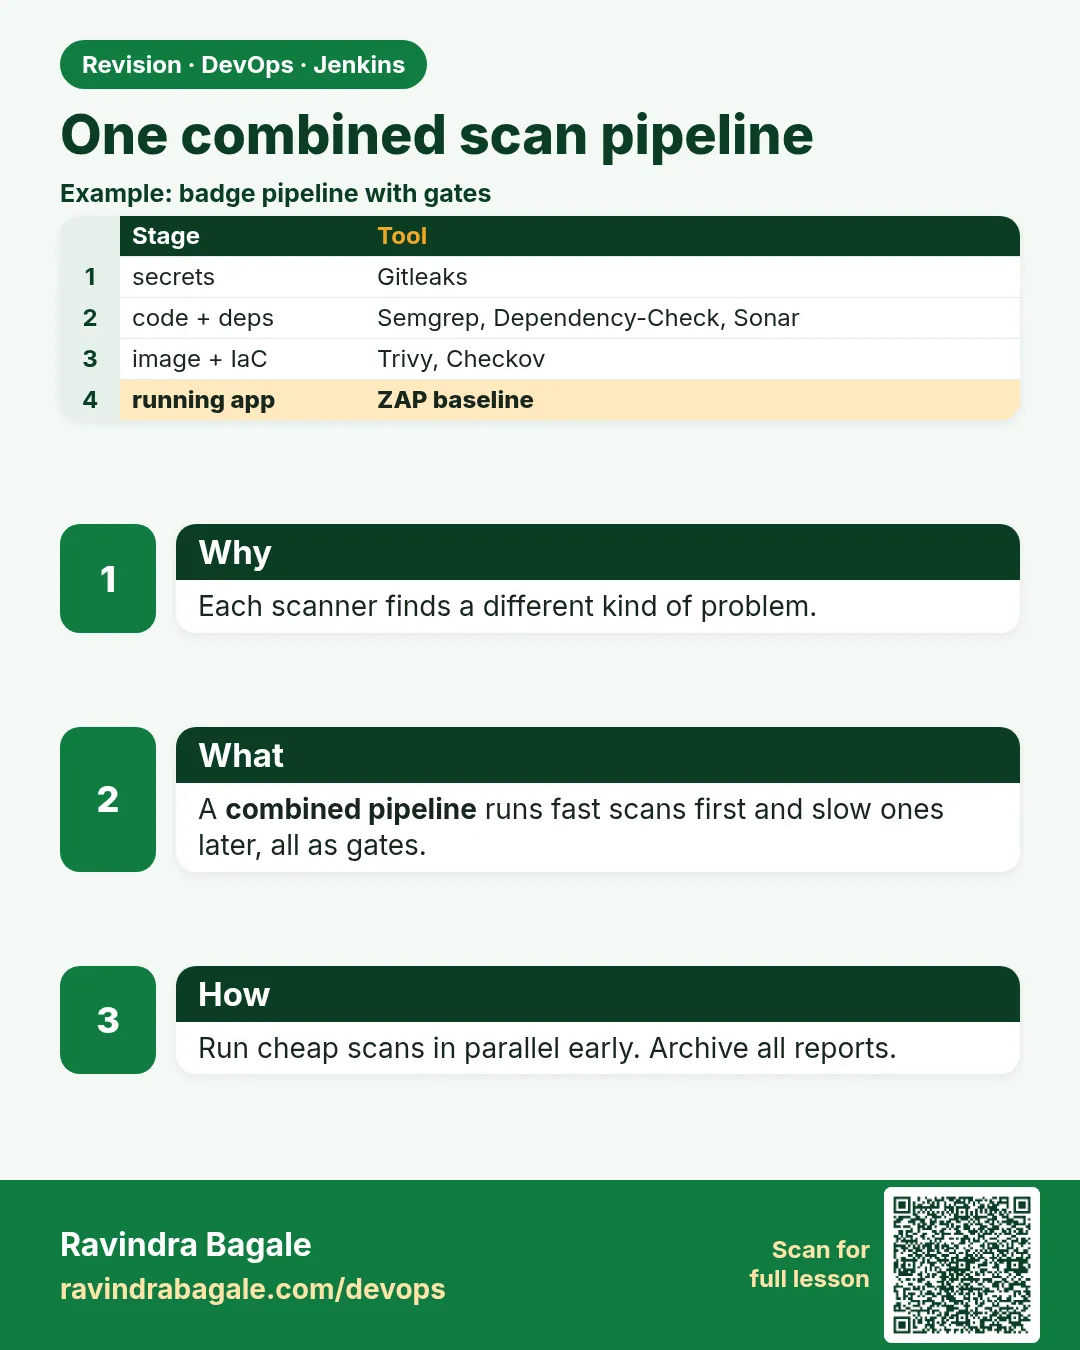
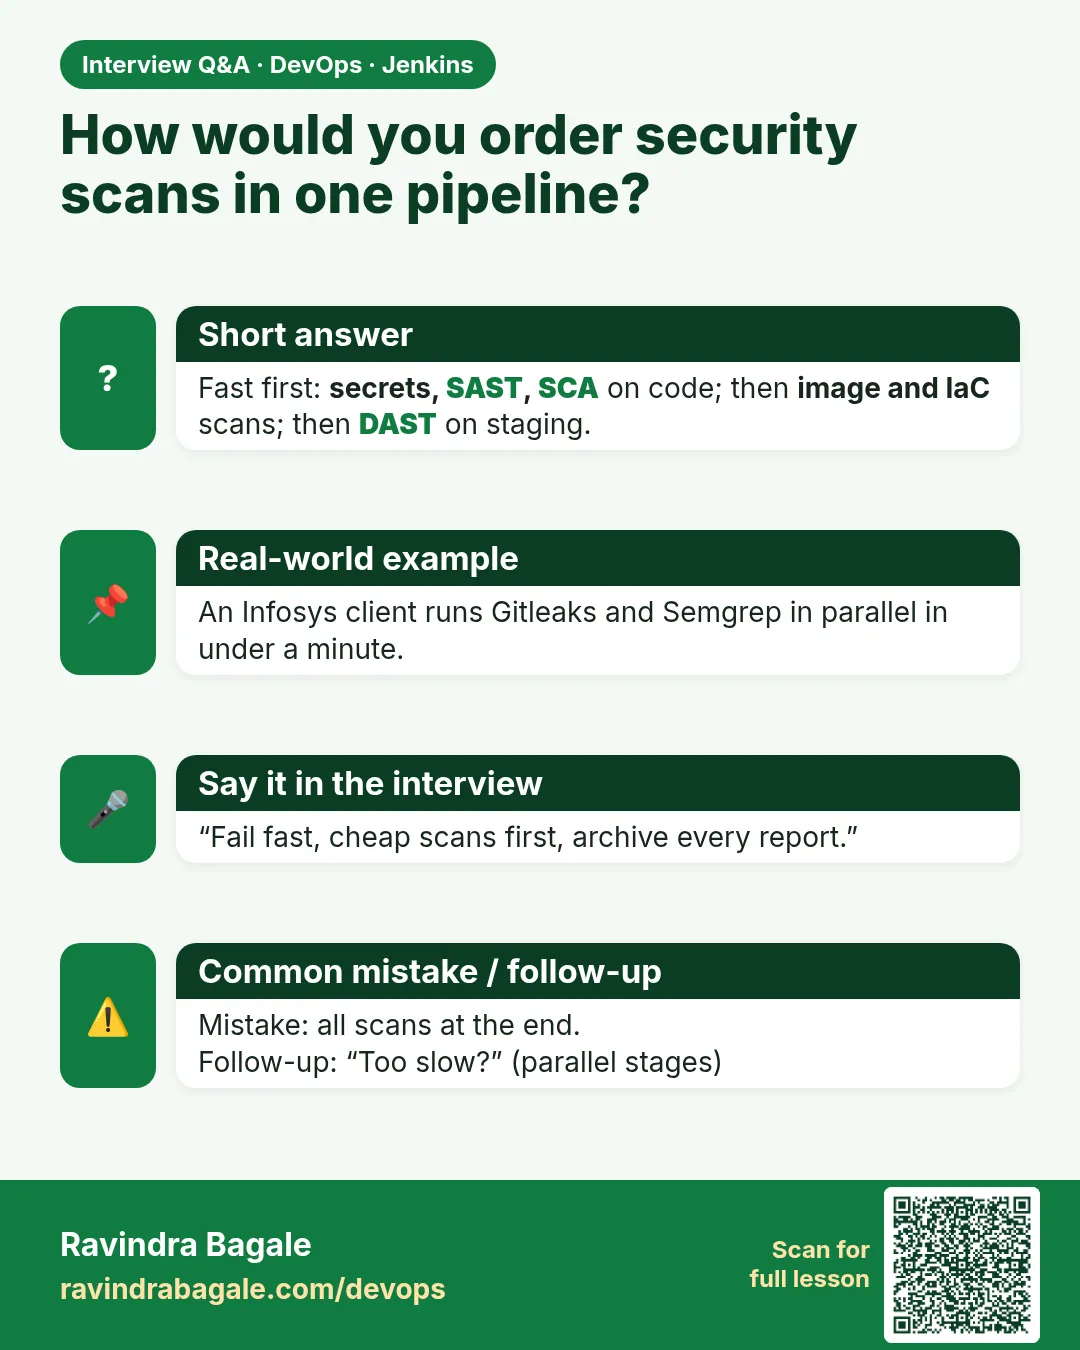
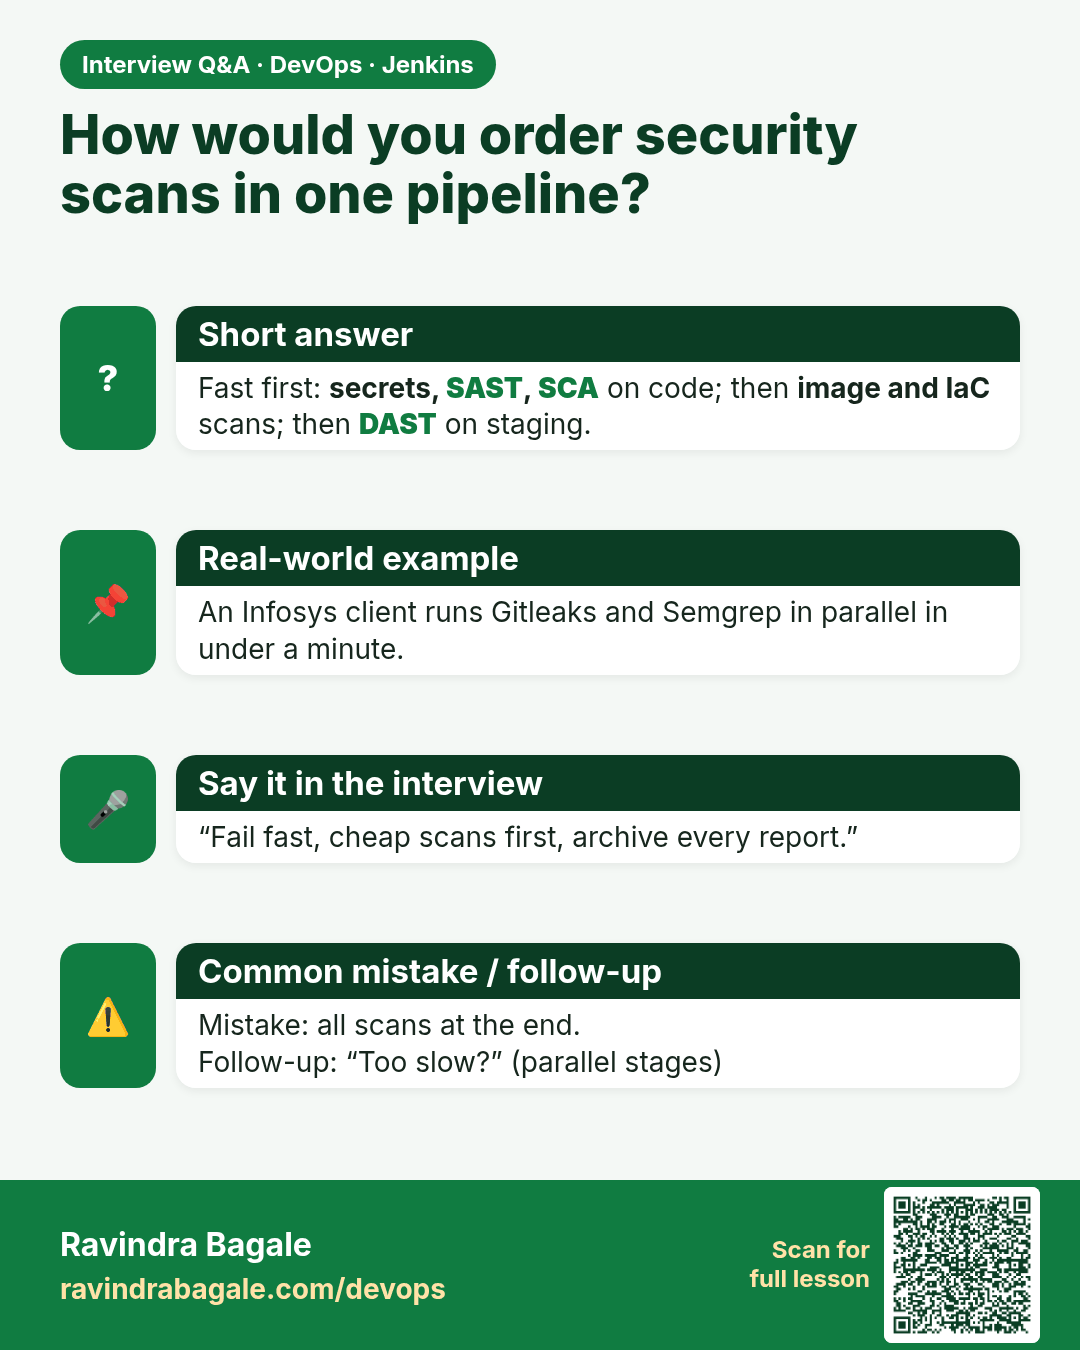
How would you order security scans in one pipeline? Fast first: secrets, SAST, SCA on code; then image and IaC scans; then DAST on staging.
Interview card 11 of 11: How would you order security scans in one pipeline? · Download PNG · Open card page

Lesson: 29.11 One combined pipeline

Comparison cards

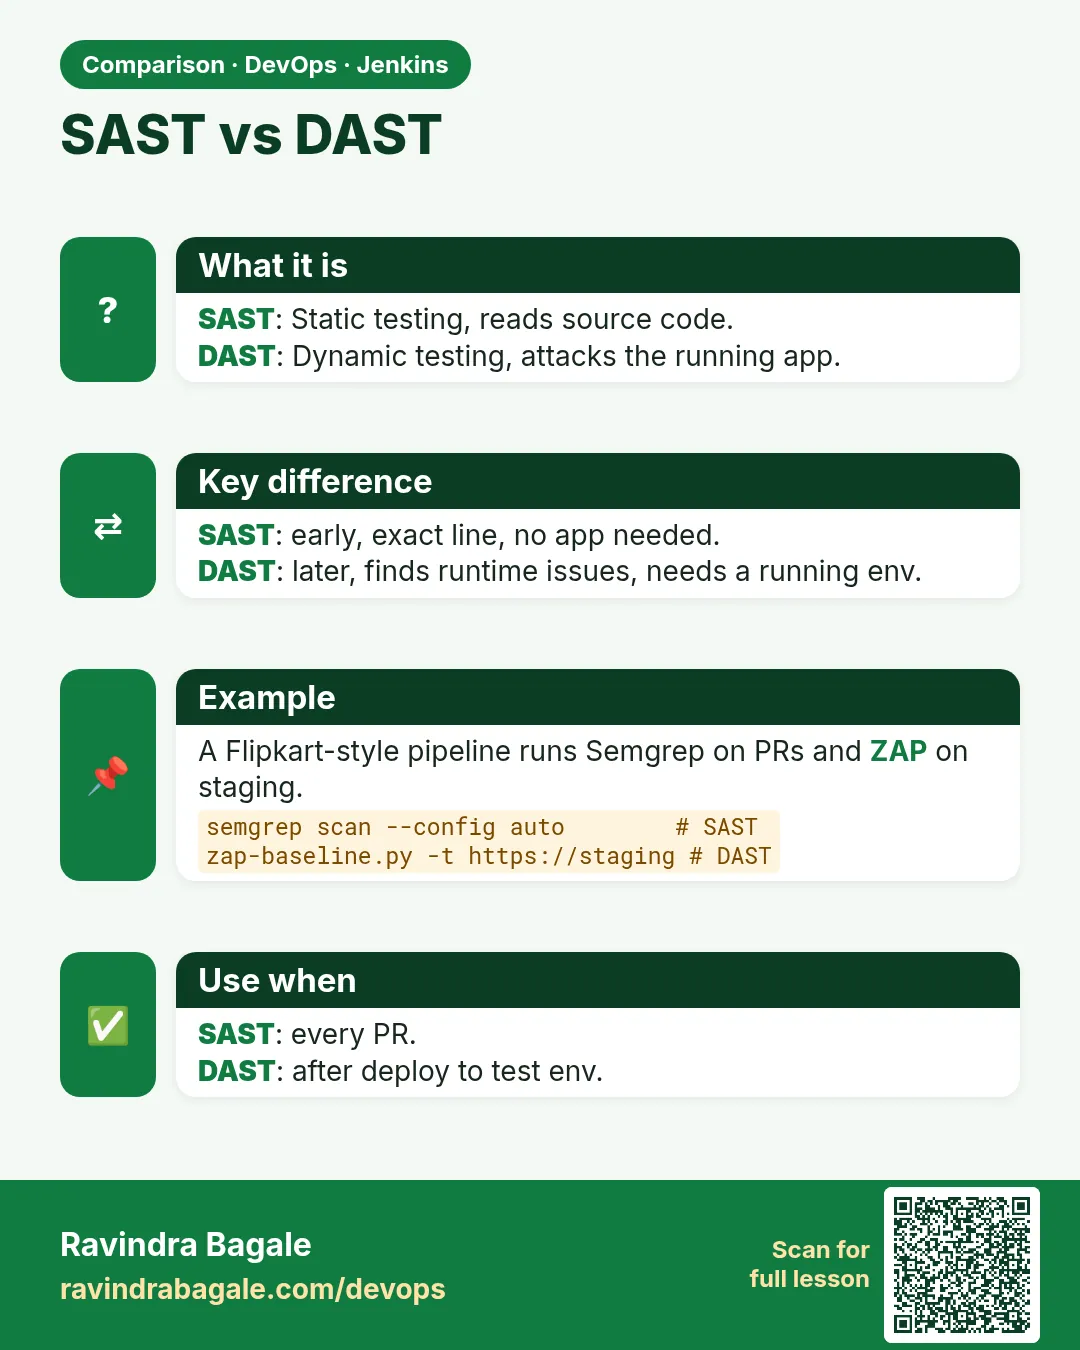
SAST vs DAST. SAST: Static testing, reads source code.DAST: Dynamic testing, attacks the running app.
Comparison card 1 of 3: SAST vs DAST · Download PNG · Open card page

Lesson: 29.6 Semgrep

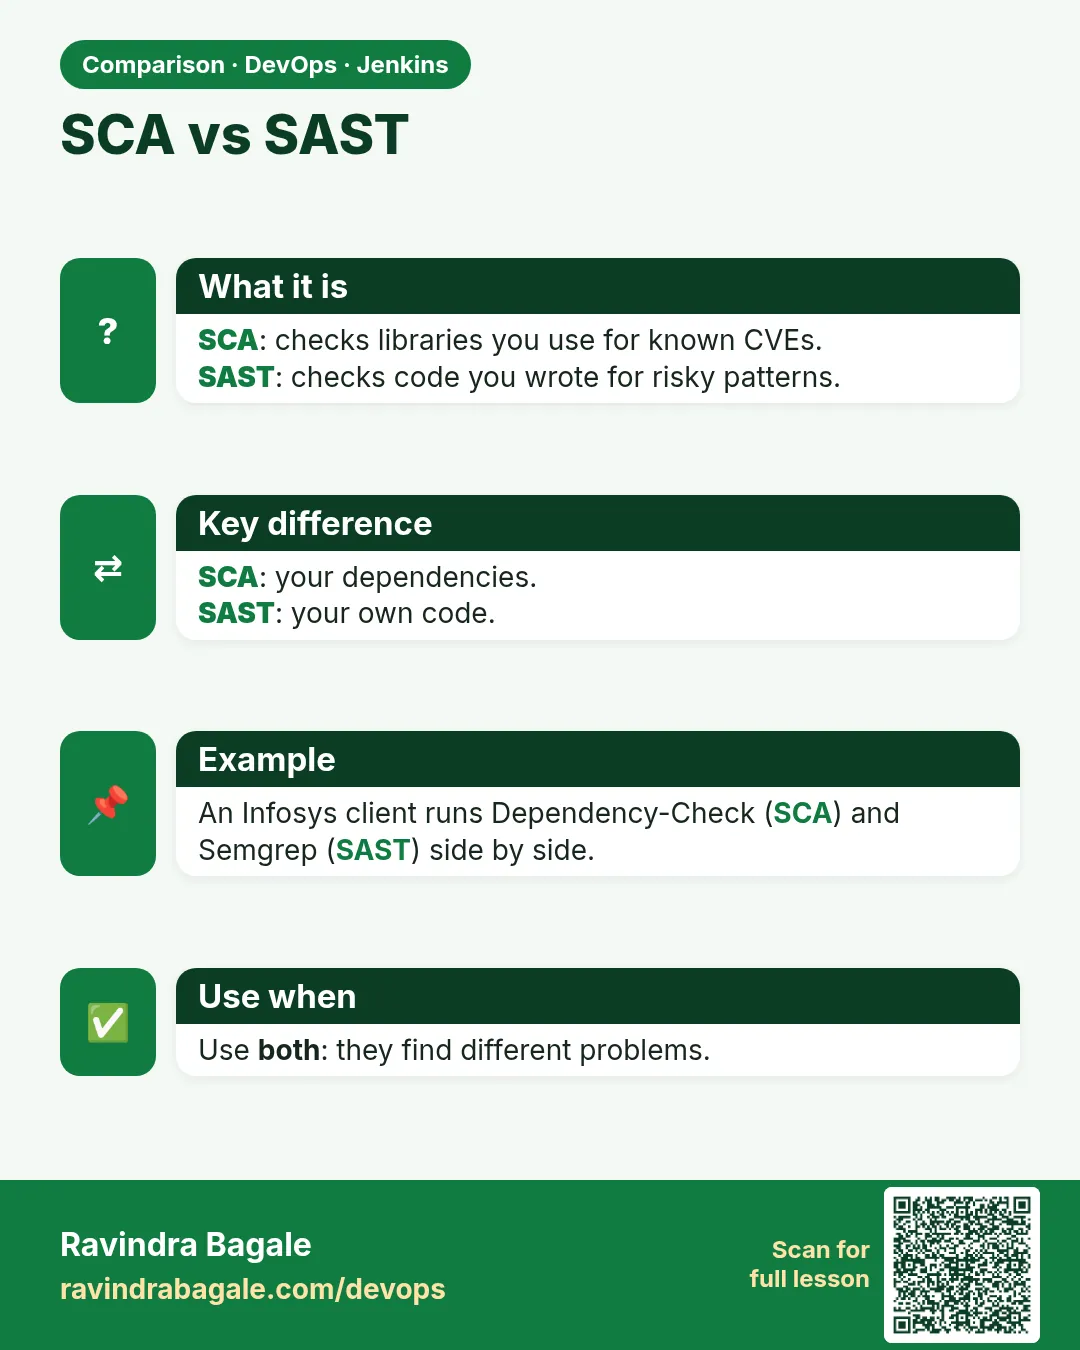
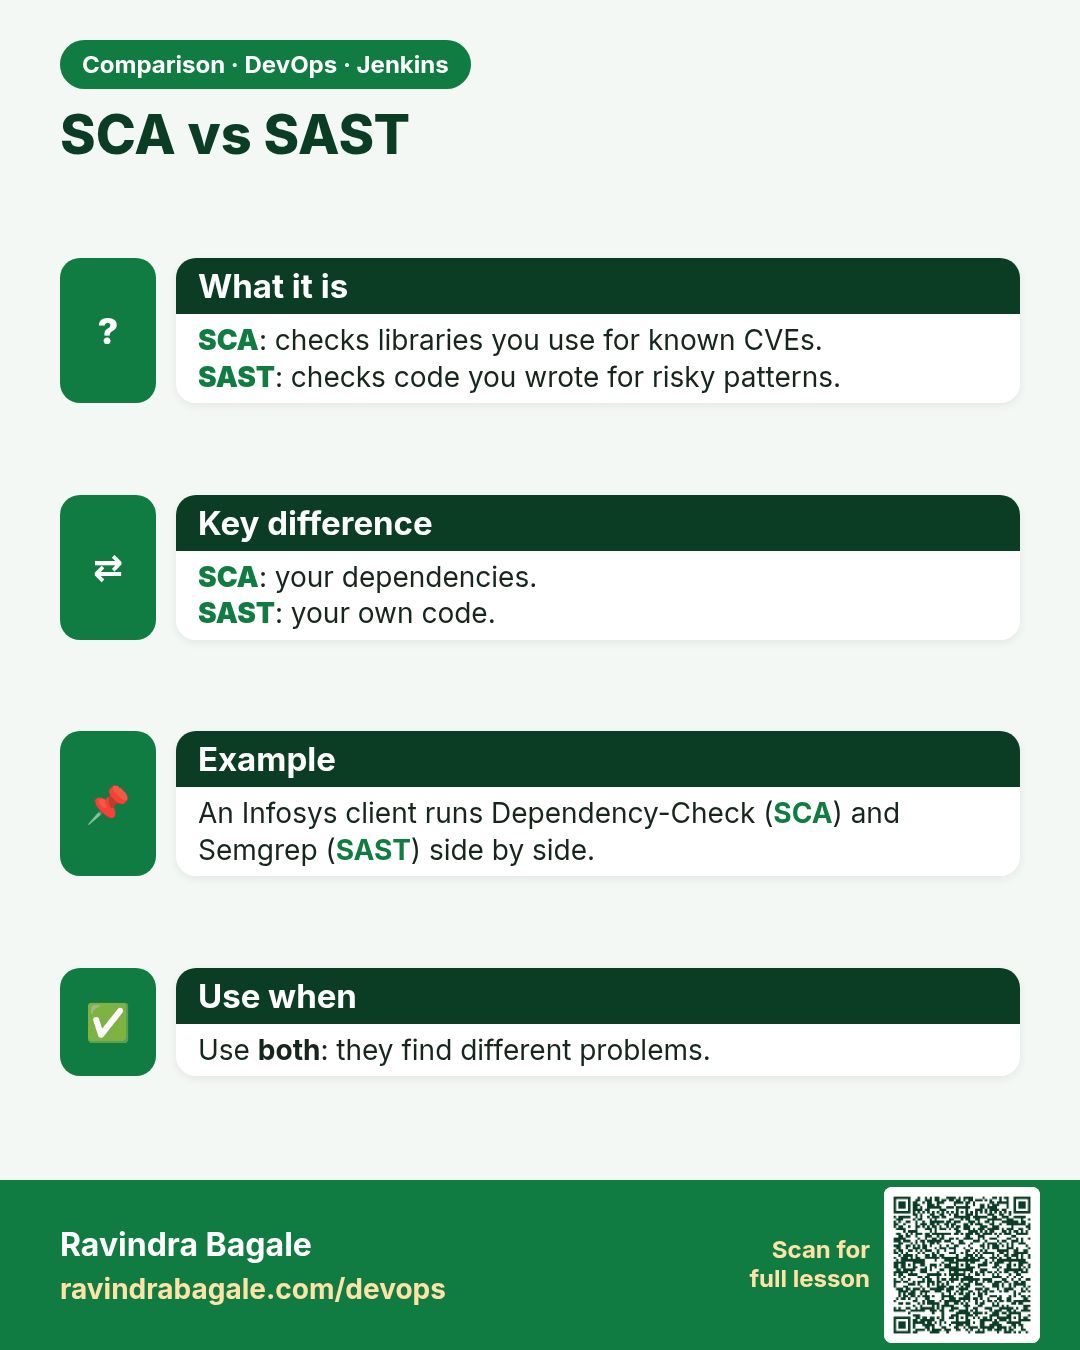
SCA vs SAST. SCA: checks libraries you use for known CVEs.SAST: checks code you wrote for risky patterns.
Comparison card 2 of 3: SCA vs SAST · Download PNG · Open card page

Lesson: 29.4 OWASP Dependency-Check
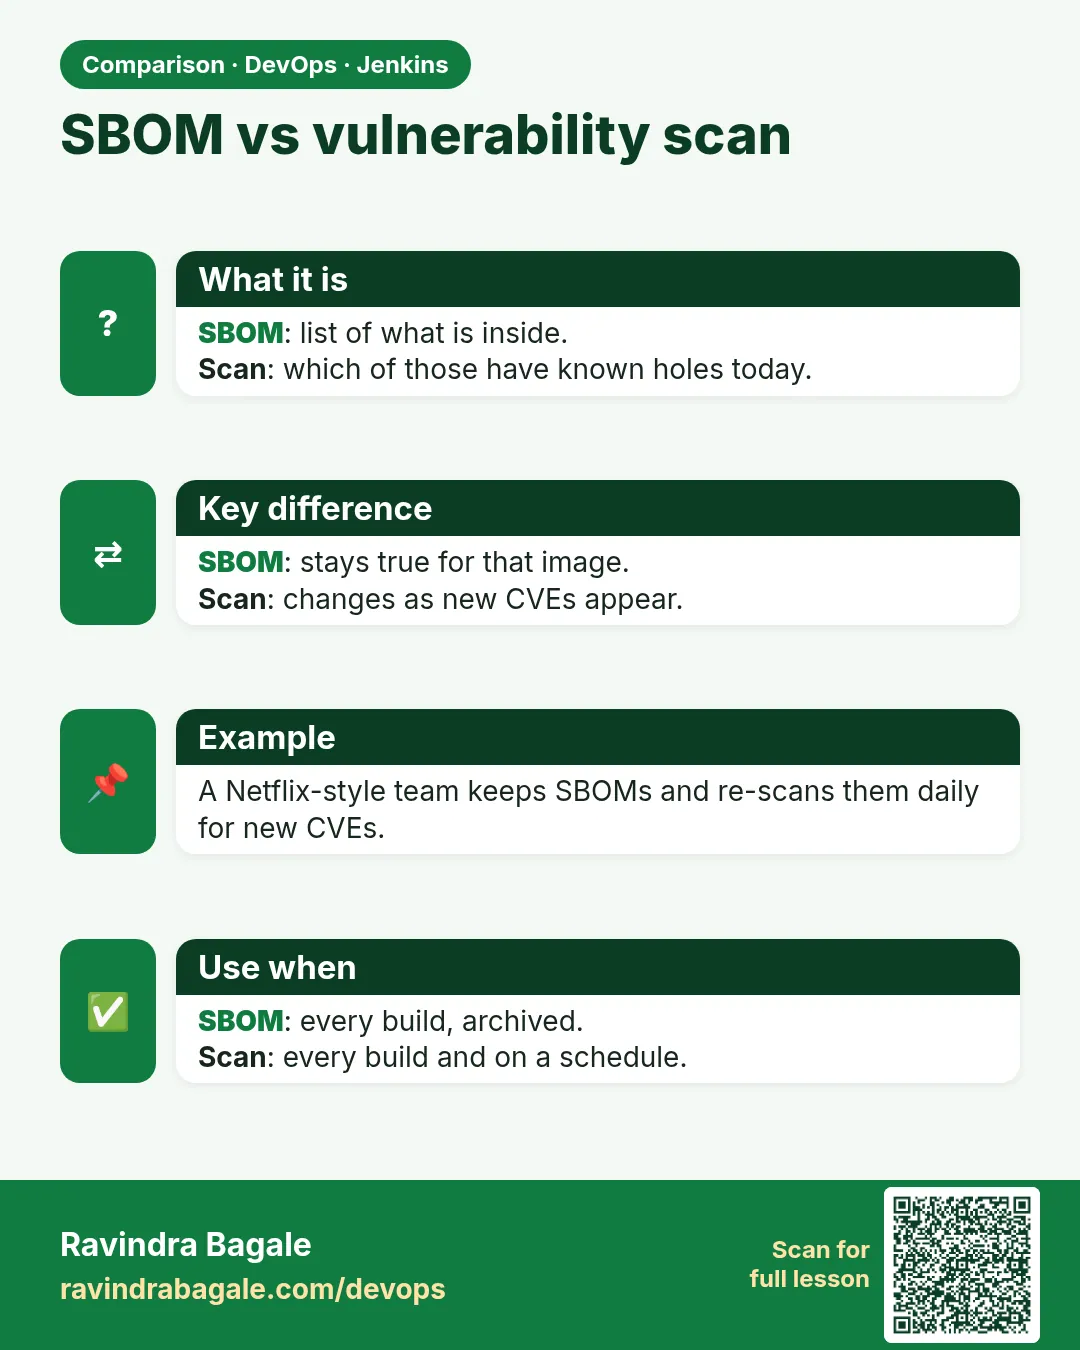
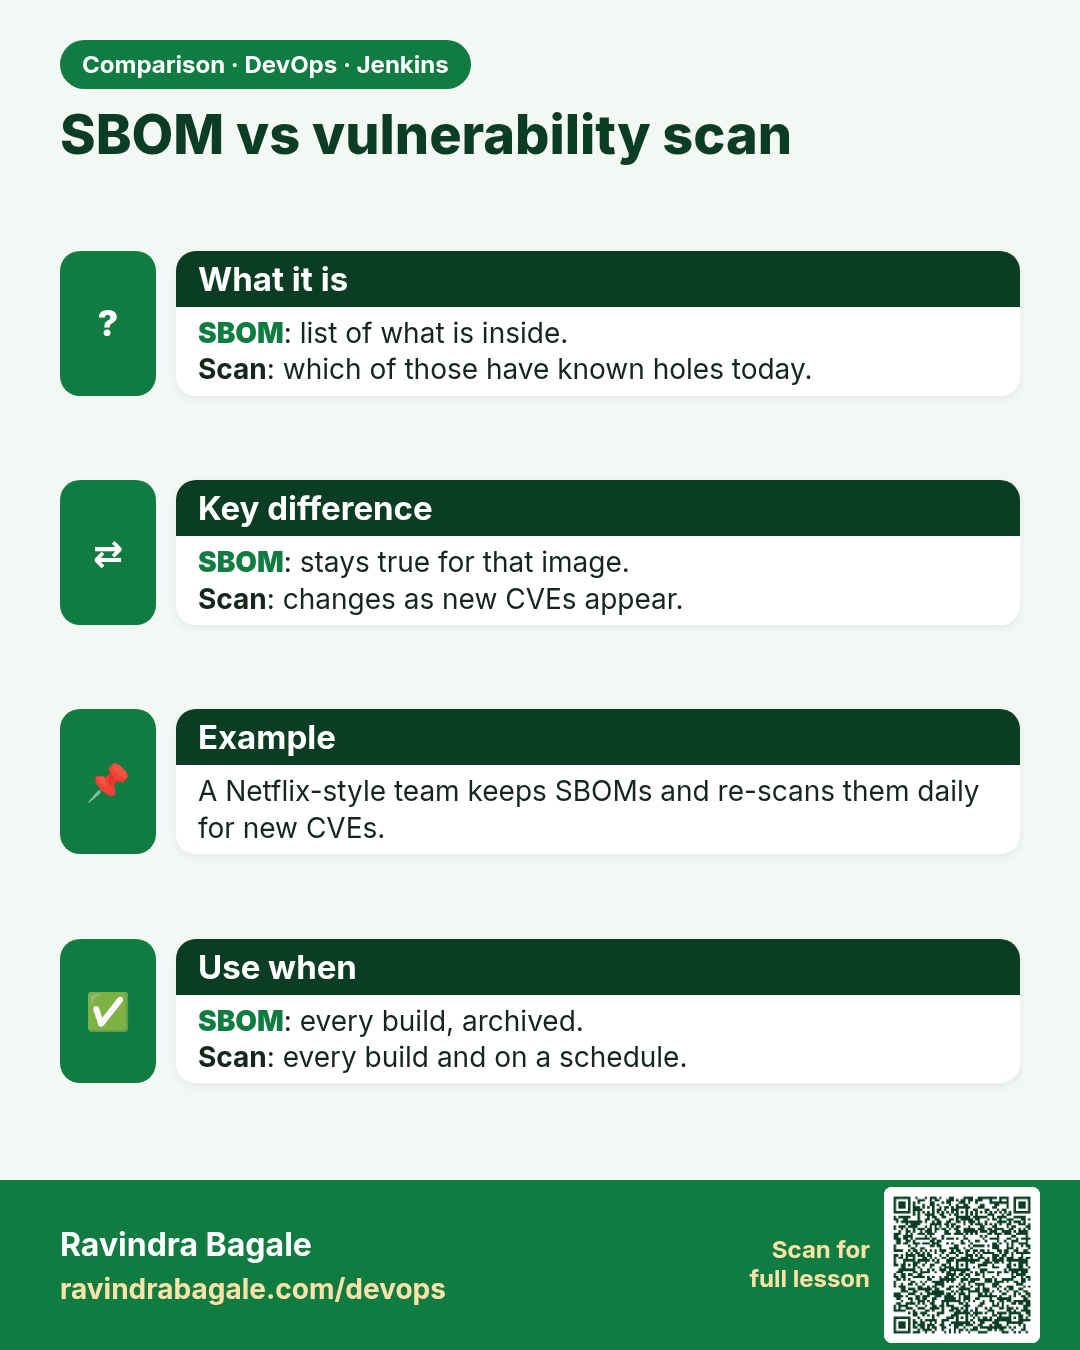
SBOM vs vulnerability scan. SBOM: list of what is inside.Scan: which of those have known holes today.
Comparison card 3 of 3: SBOM vs vulnerability scan · Download PNG · Open card page

Lesson: 29.9 Syft SBOM