Ravindra BagaleCourses & study guides मराठी

Ravi Sir's Cards › DevOps

Chapter 26: Jenkins Security, RBAC and Hardening: Cards

मराठी cards · Open the chapter

Revision cards
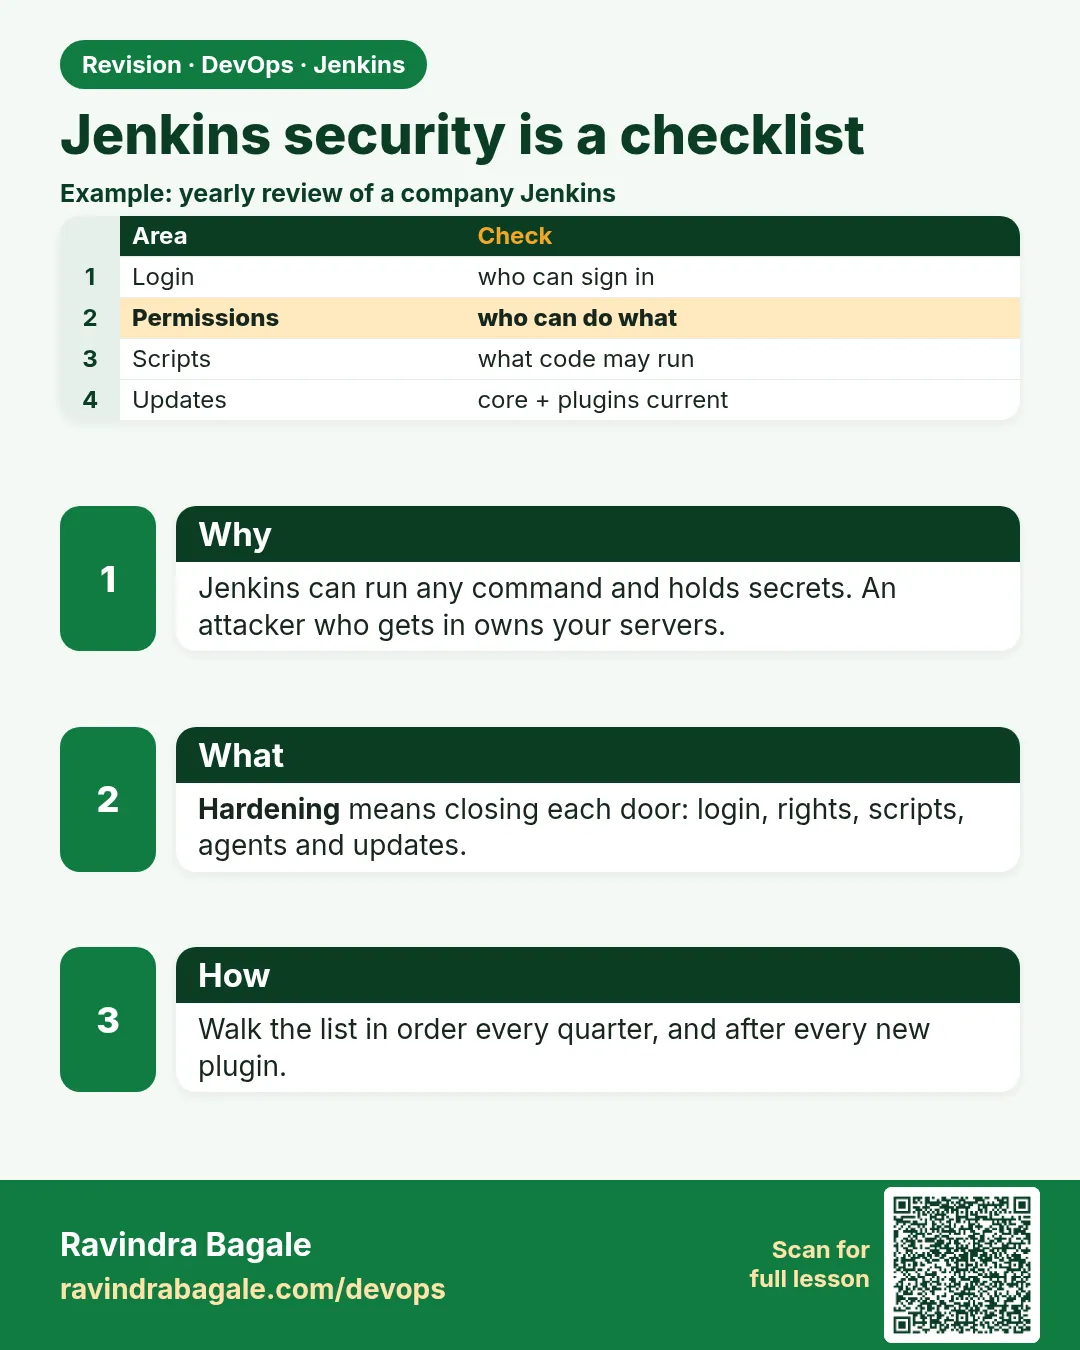
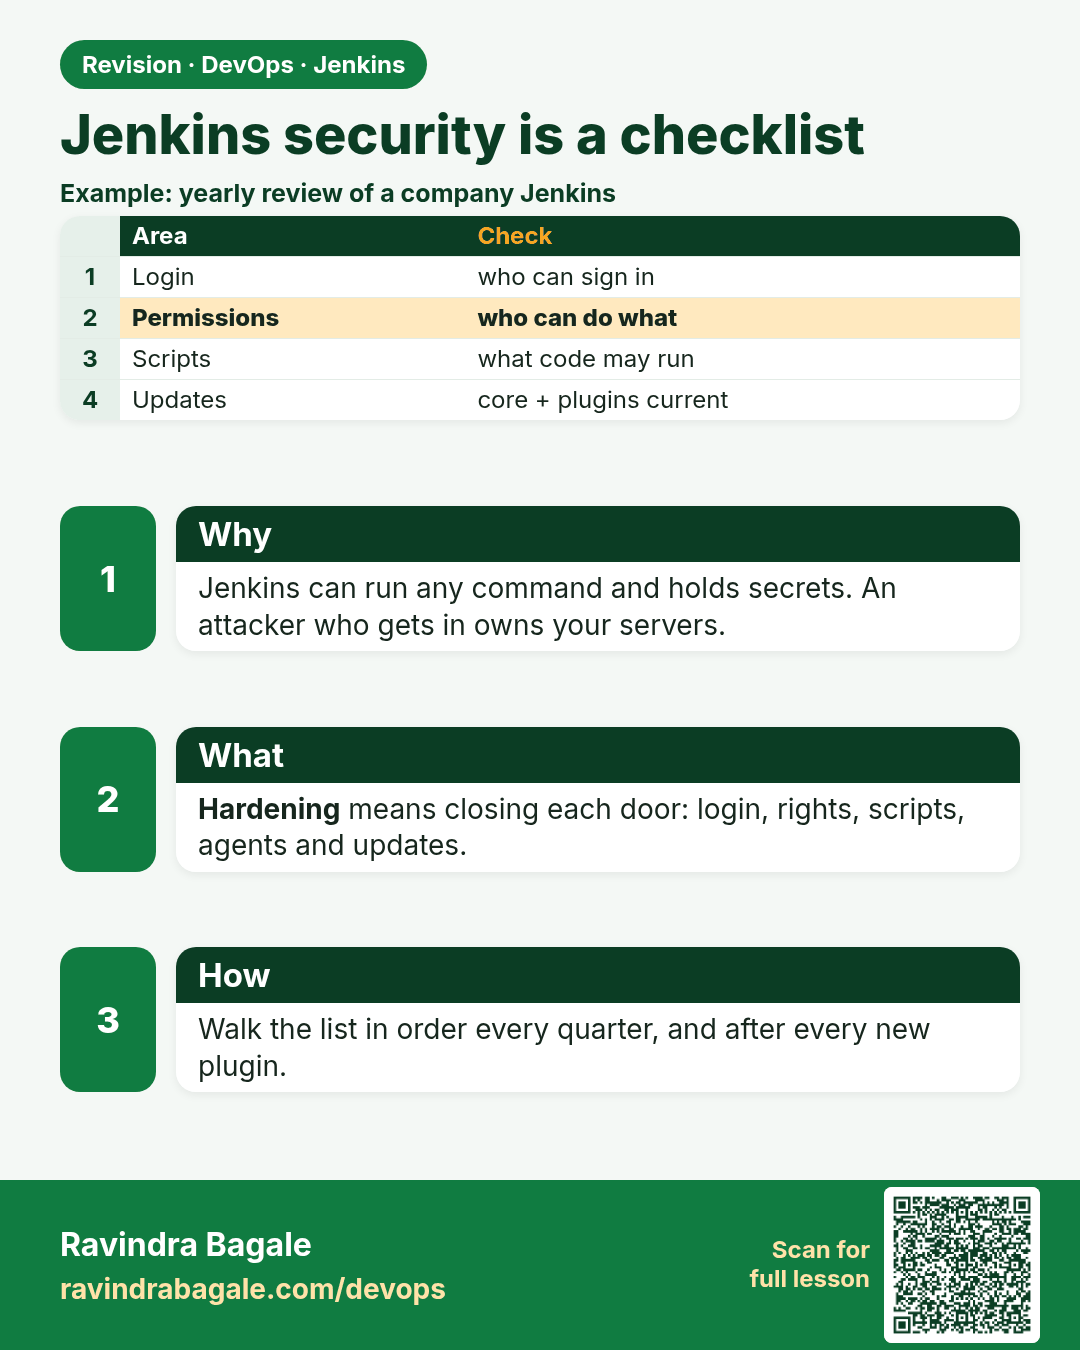
Jenkins security is a checklist. Jenkins can run any command and holds secrets. An attacker who gets in owns your servers.
Revision card 1 of 7: Jenkins security is a checklist · Download PNG · Open card page

Lesson: 26.1 Why this chapter is a checklist
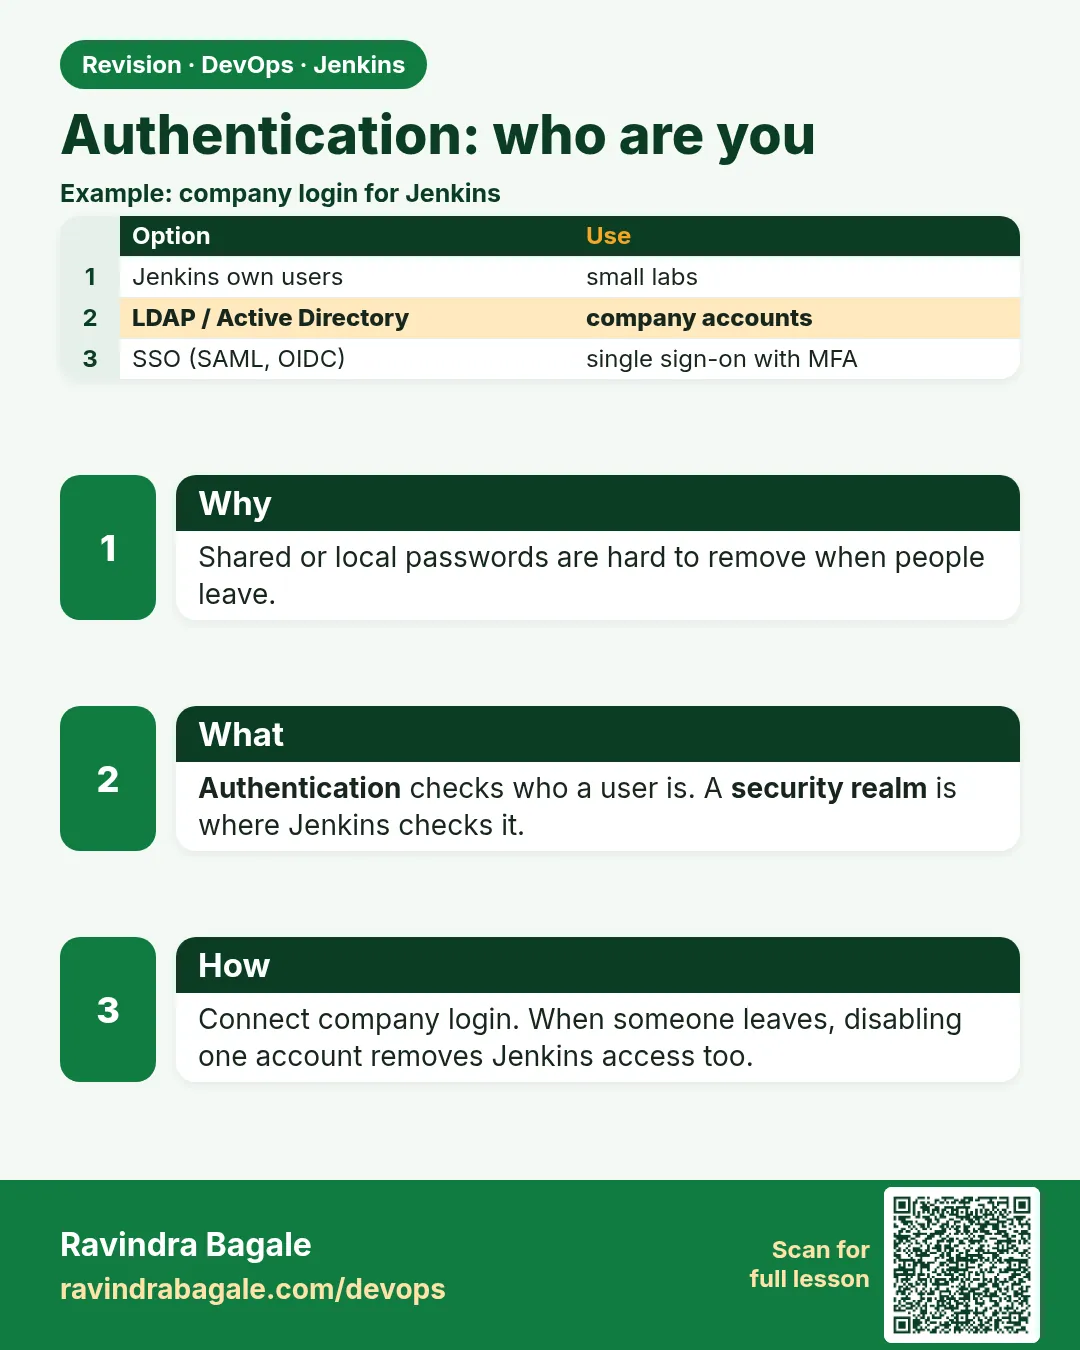
Authentication: who are you. Shared or local passwords are hard to remove when people leave.
Revision card 2 of 7: Authentication: who are you · Download PNG · Open card page

Lesson: 26.2 Authentication

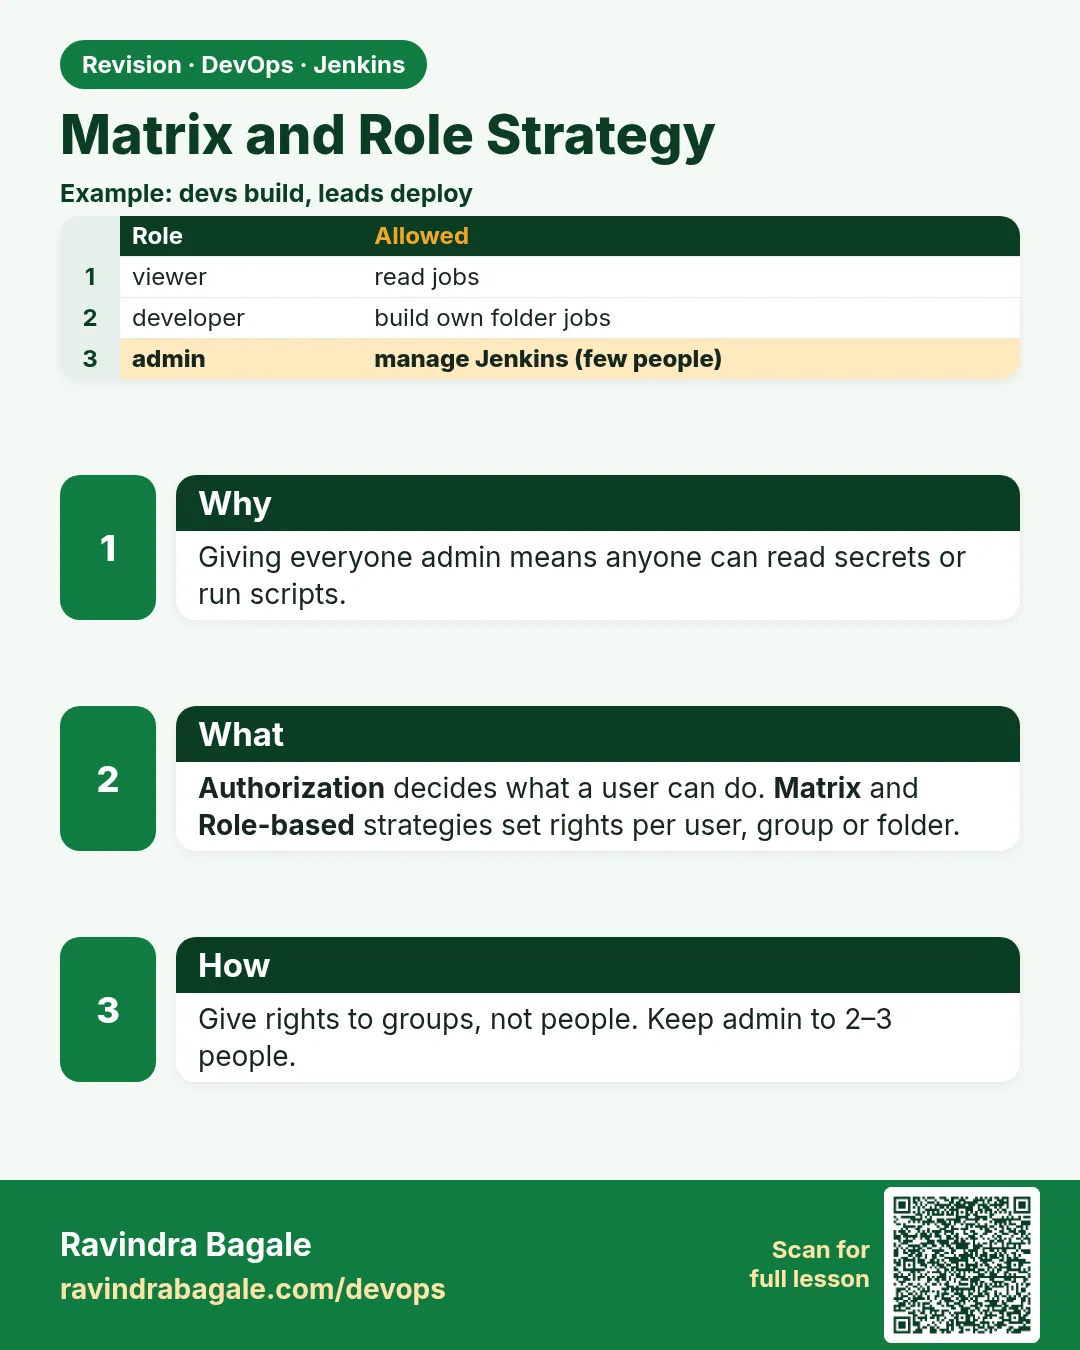
Matrix and Role Strategy. Giving everyone admin means anyone can read secrets or run scripts.
Revision card 3 of 7: Matrix and Role Strategy · Download PNG · Open card page

Lesson: 26.3 Matrix and role strategy

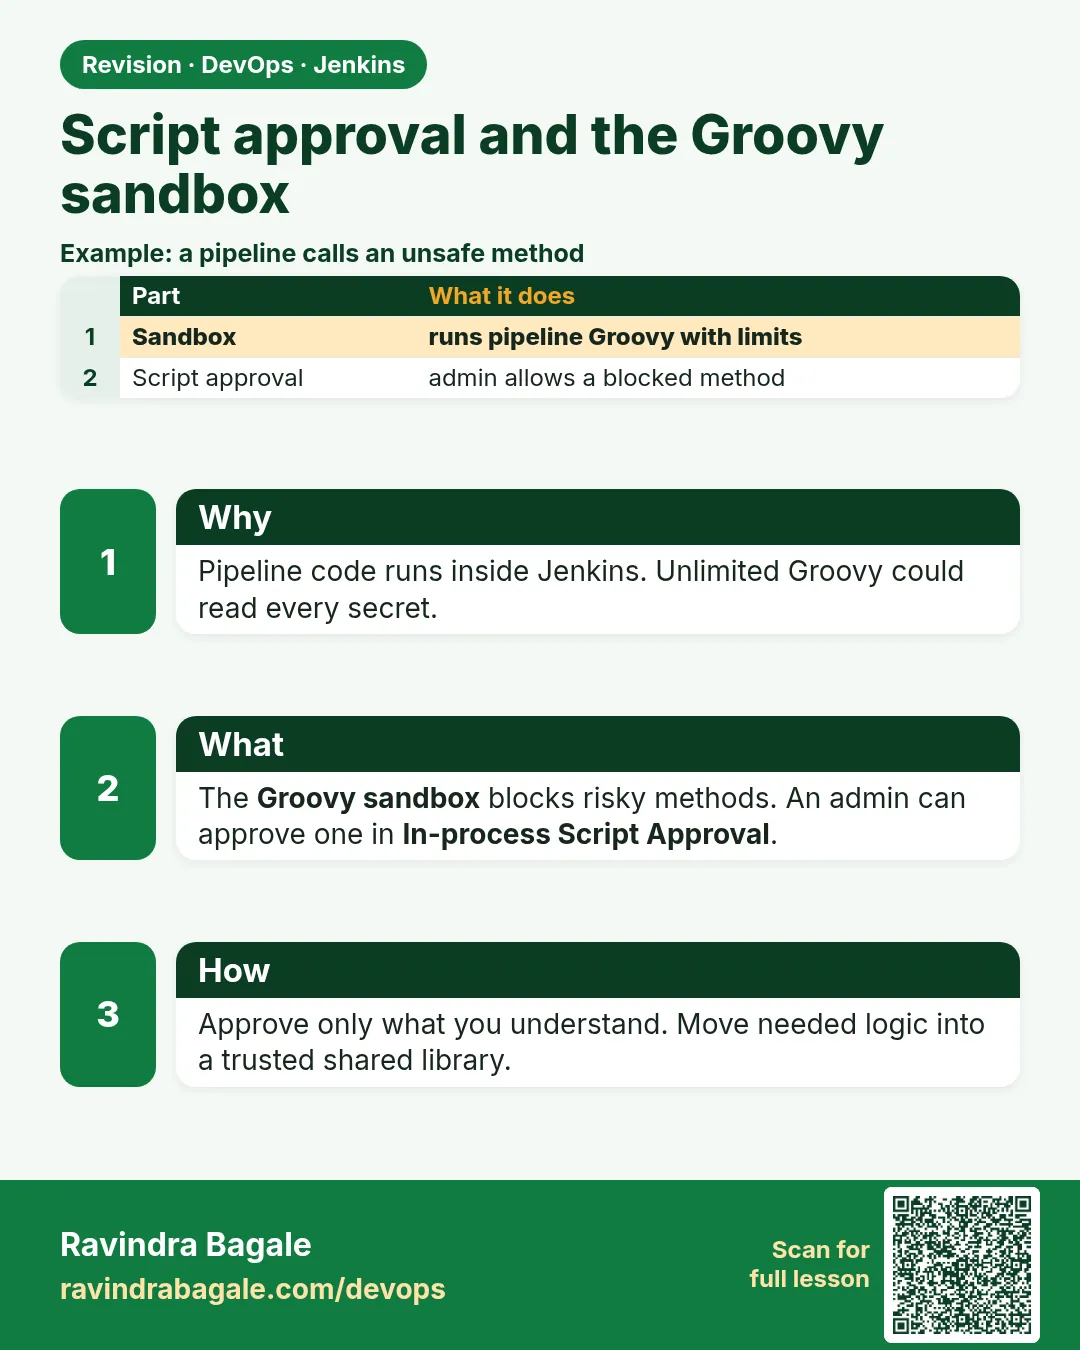
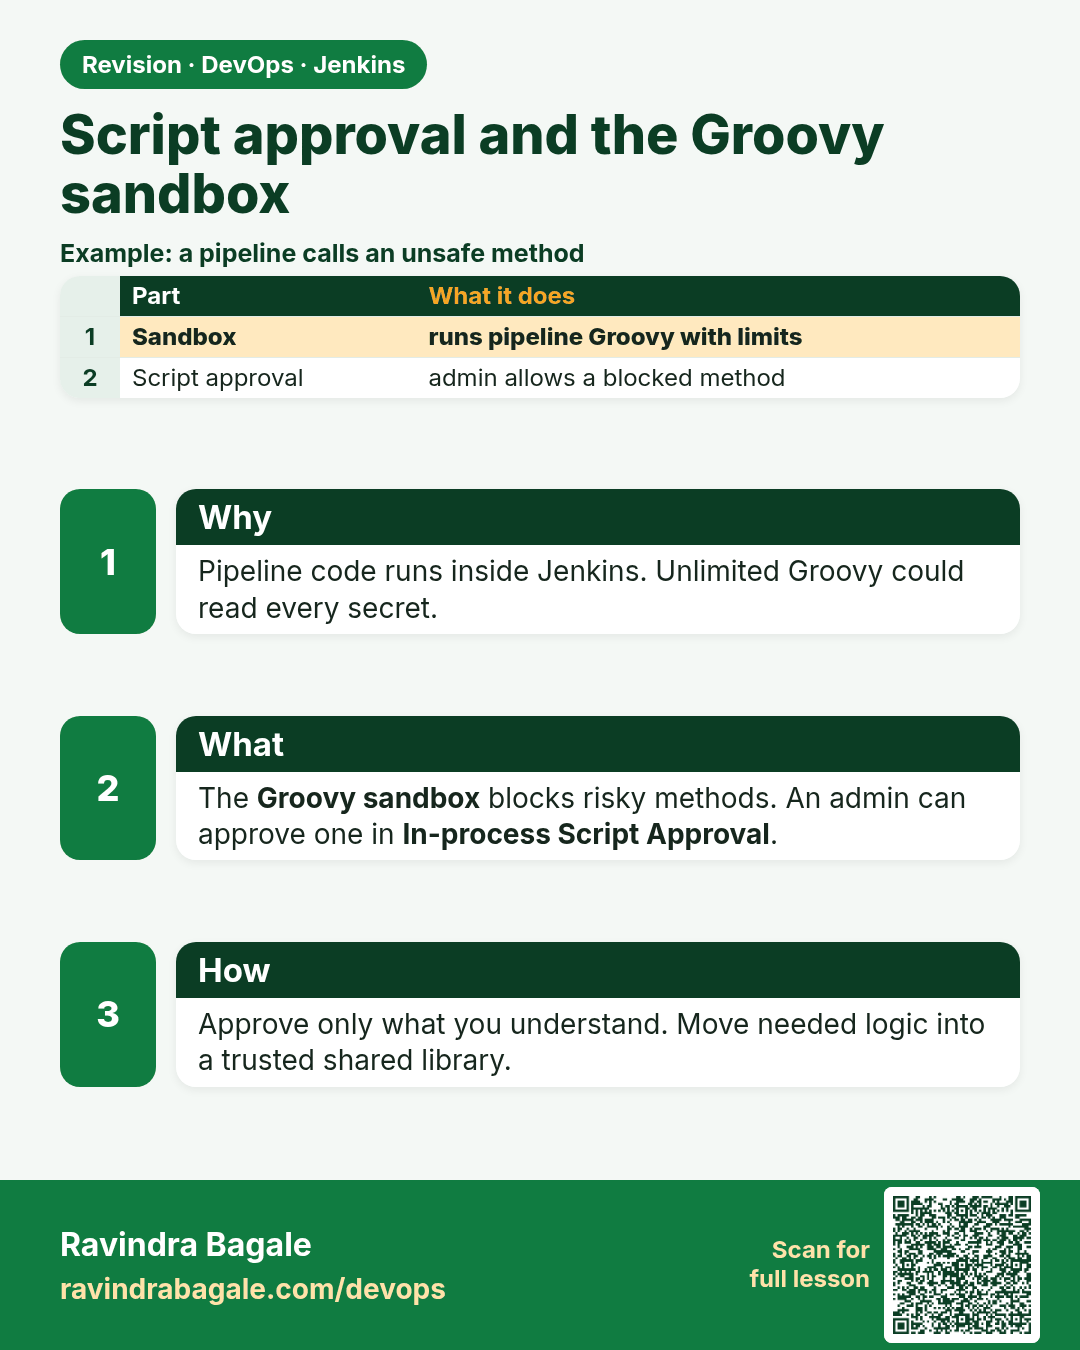
Script approval and the Groovy sandbox. Pipeline code runs inside Jenkins. Unlimited Groovy could read every secret.
Revision card 4 of 7: Script approval and the Groovy sandbox · Download PNG · Open card page

Lesson: 26.4 Script approval and the Groovy sandbox

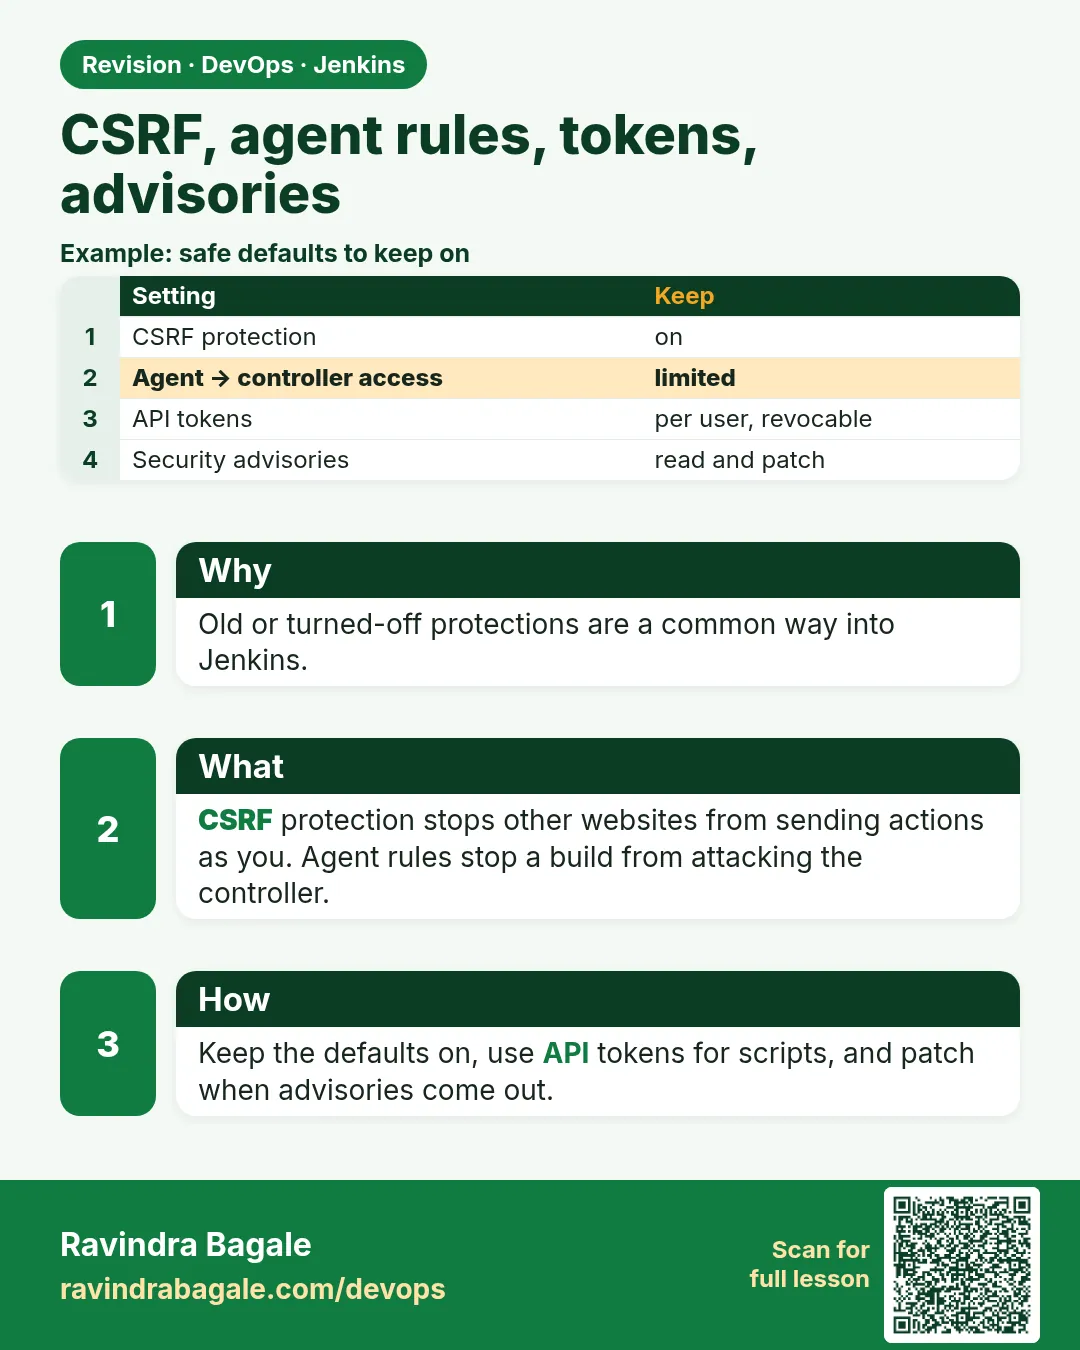
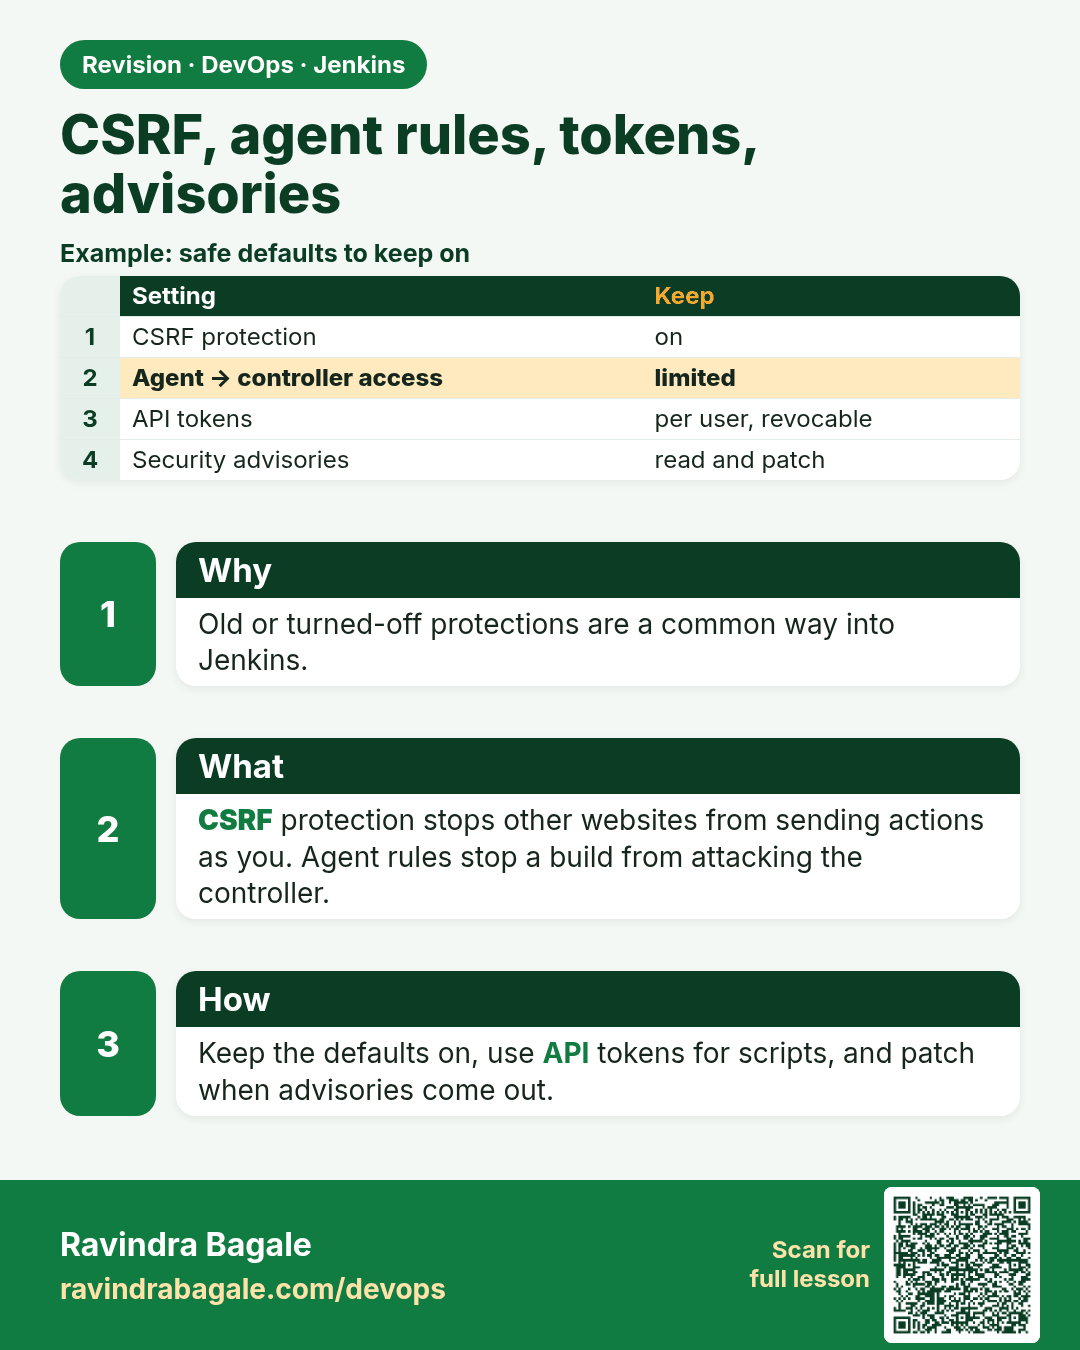
CSRF, agent rules, tokens, advisories. Old or turned-off protections are a common way into Jenkins.
Revision card 5 of 7: CSRF, agent rules, tokens, advisories · Download PNG · Open card page

Lesson: 26.5 CSRF, agents, tokens, advisories

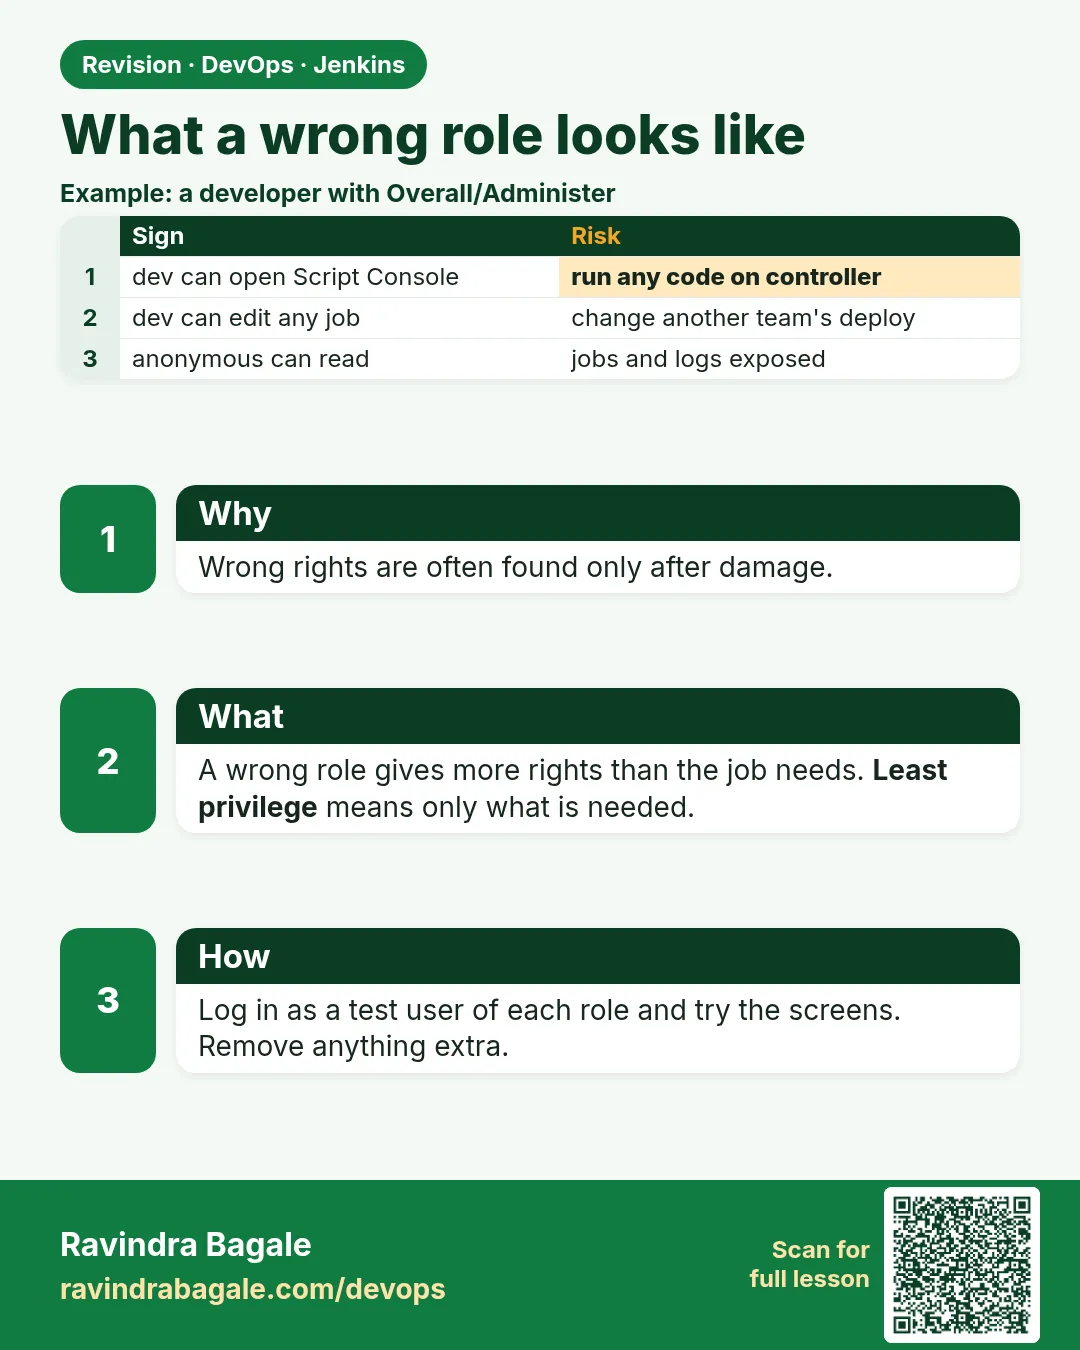
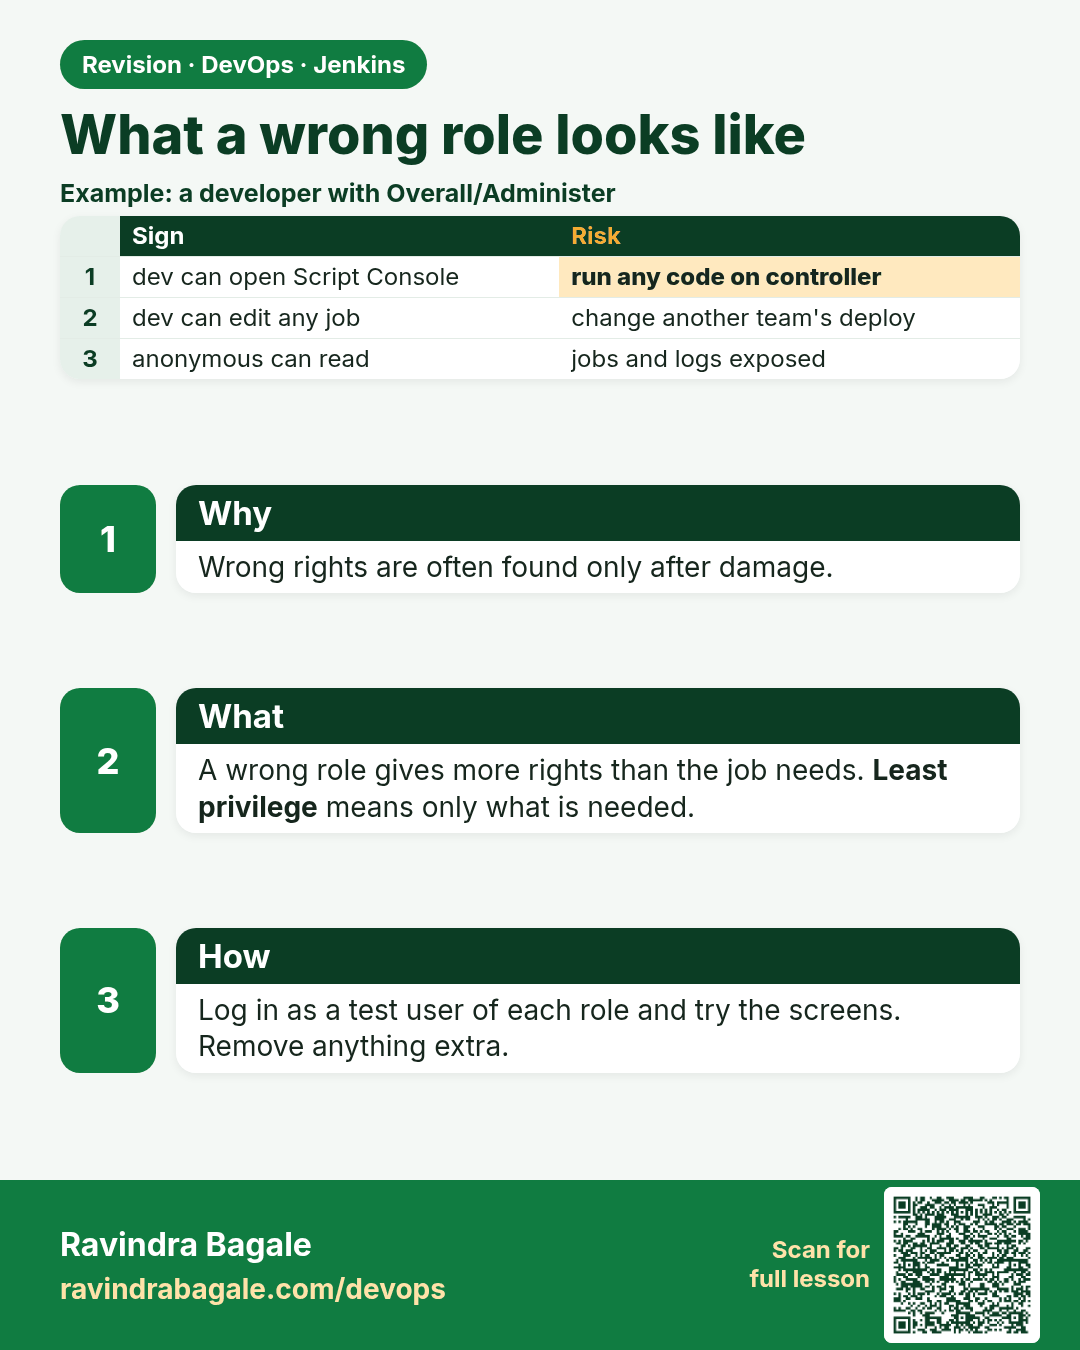
What a wrong role looks like. Wrong rights are often found only after damage.
Revision card 6 of 7: What a wrong role looks like · Download PNG · Open card page

Lesson: 26.6 What a wrong role looks like

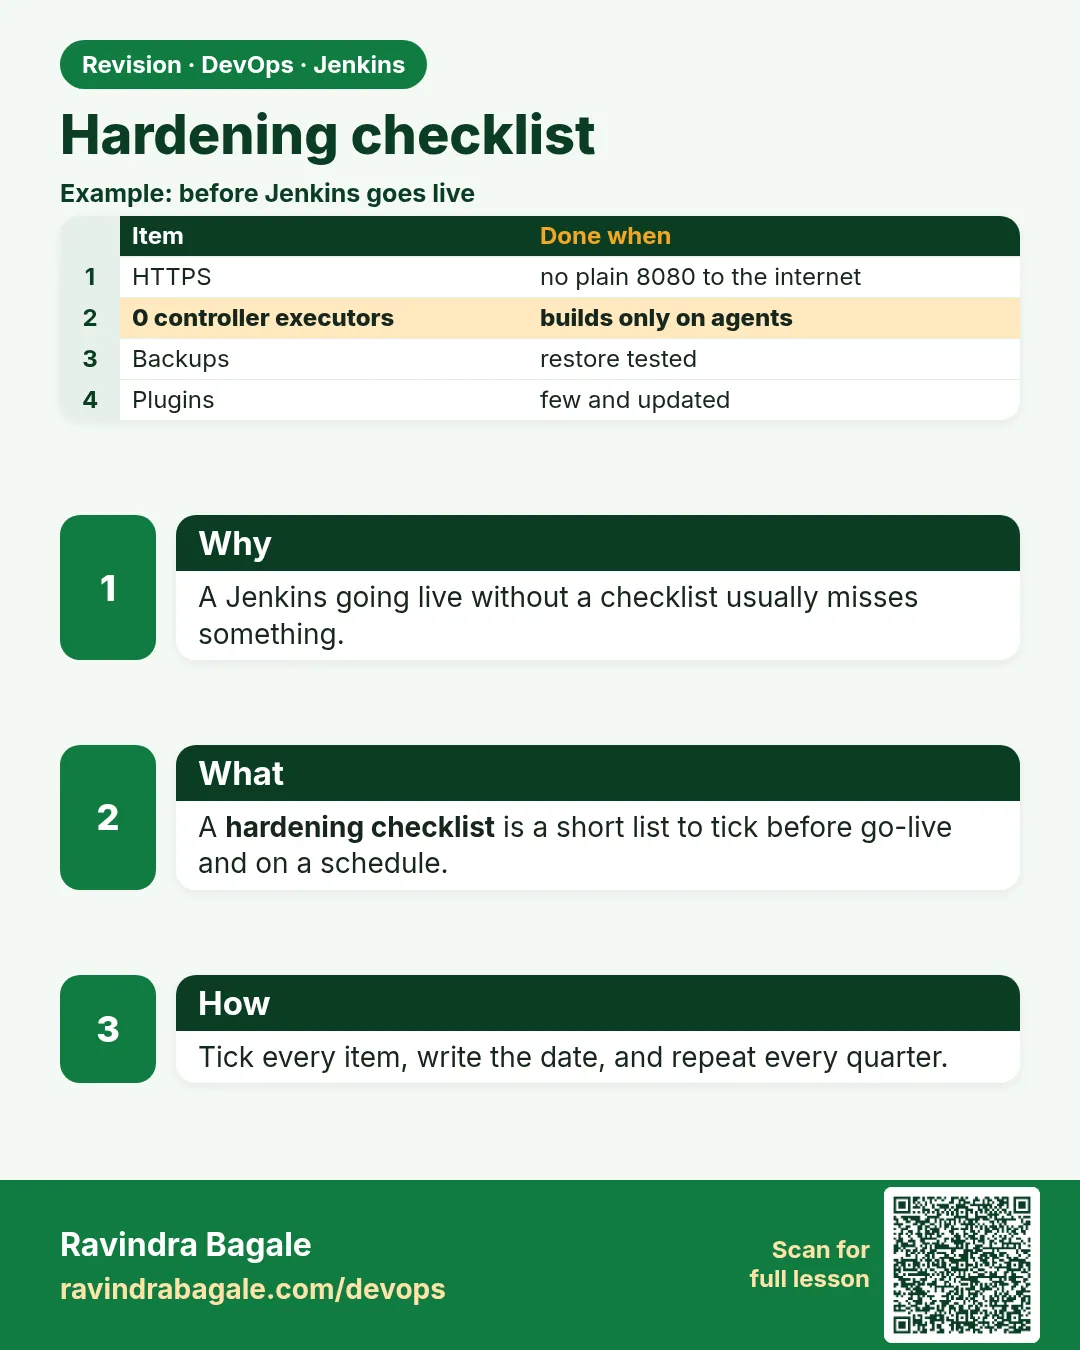
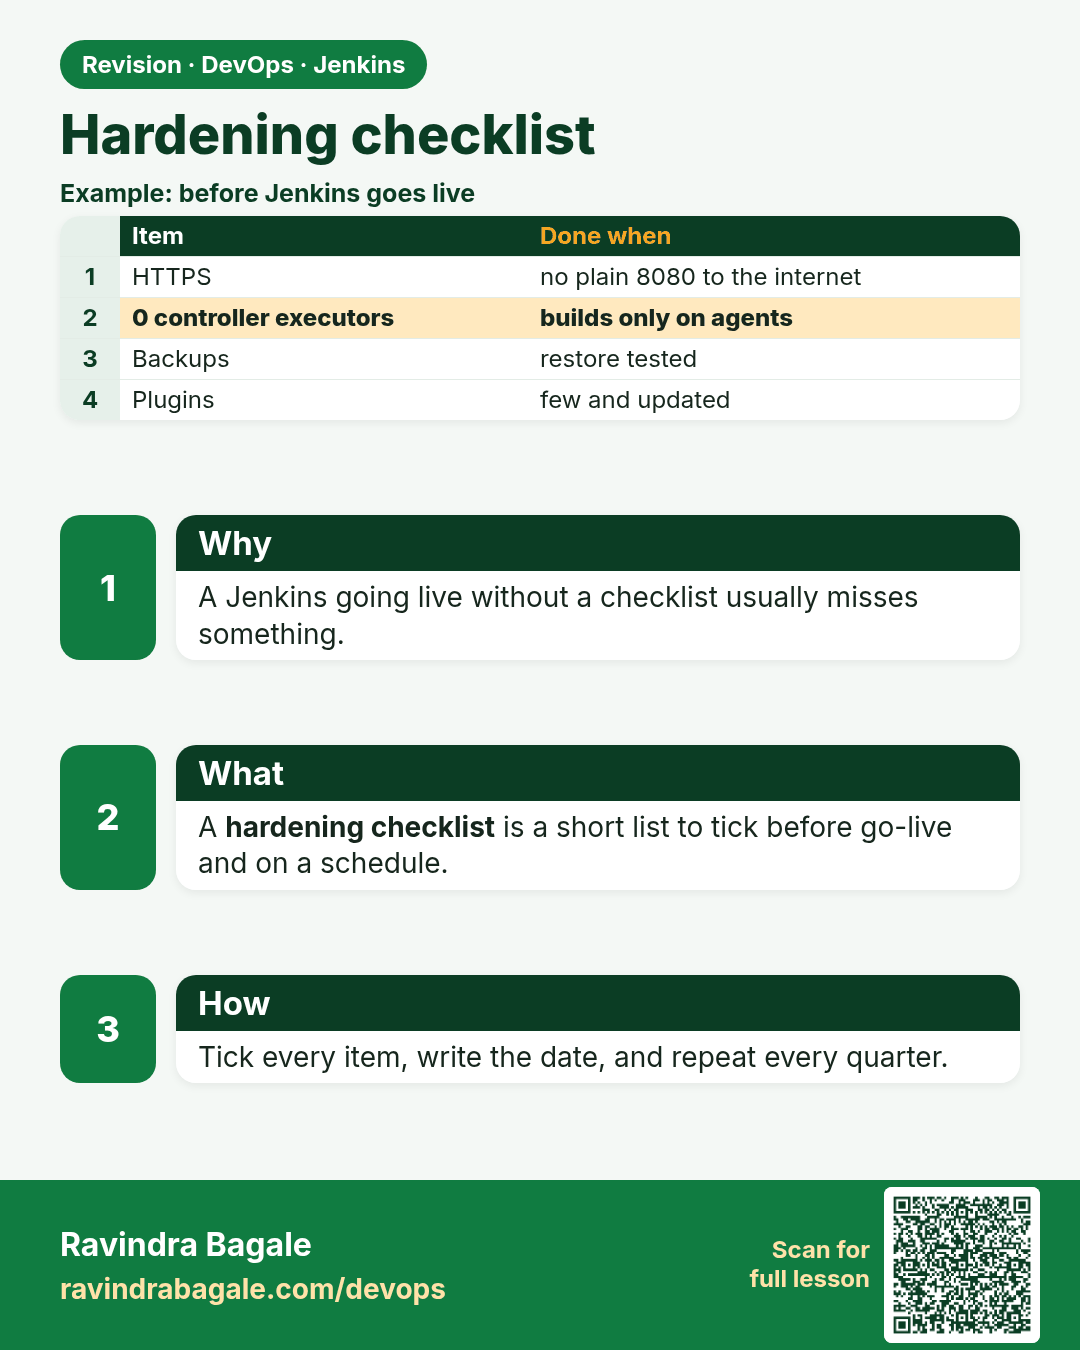
Hardening checklist. A Jenkins going live without a checklist usually misses something.
Revision card 7 of 7: Hardening checklist · Download PNG · Open card page

Lesson: 26.7 Hardening checklist

Interview cards

Why is Jenkins a big security risk? It can run commands on agents and holds credentials for Git, cloud and registries. Getting in means getting those.
Interview card 1 of 7: Why is Jenkins a big security risk? · Download PNG · Open card page

Lesson: 26.1 Why this chapter is a checklist
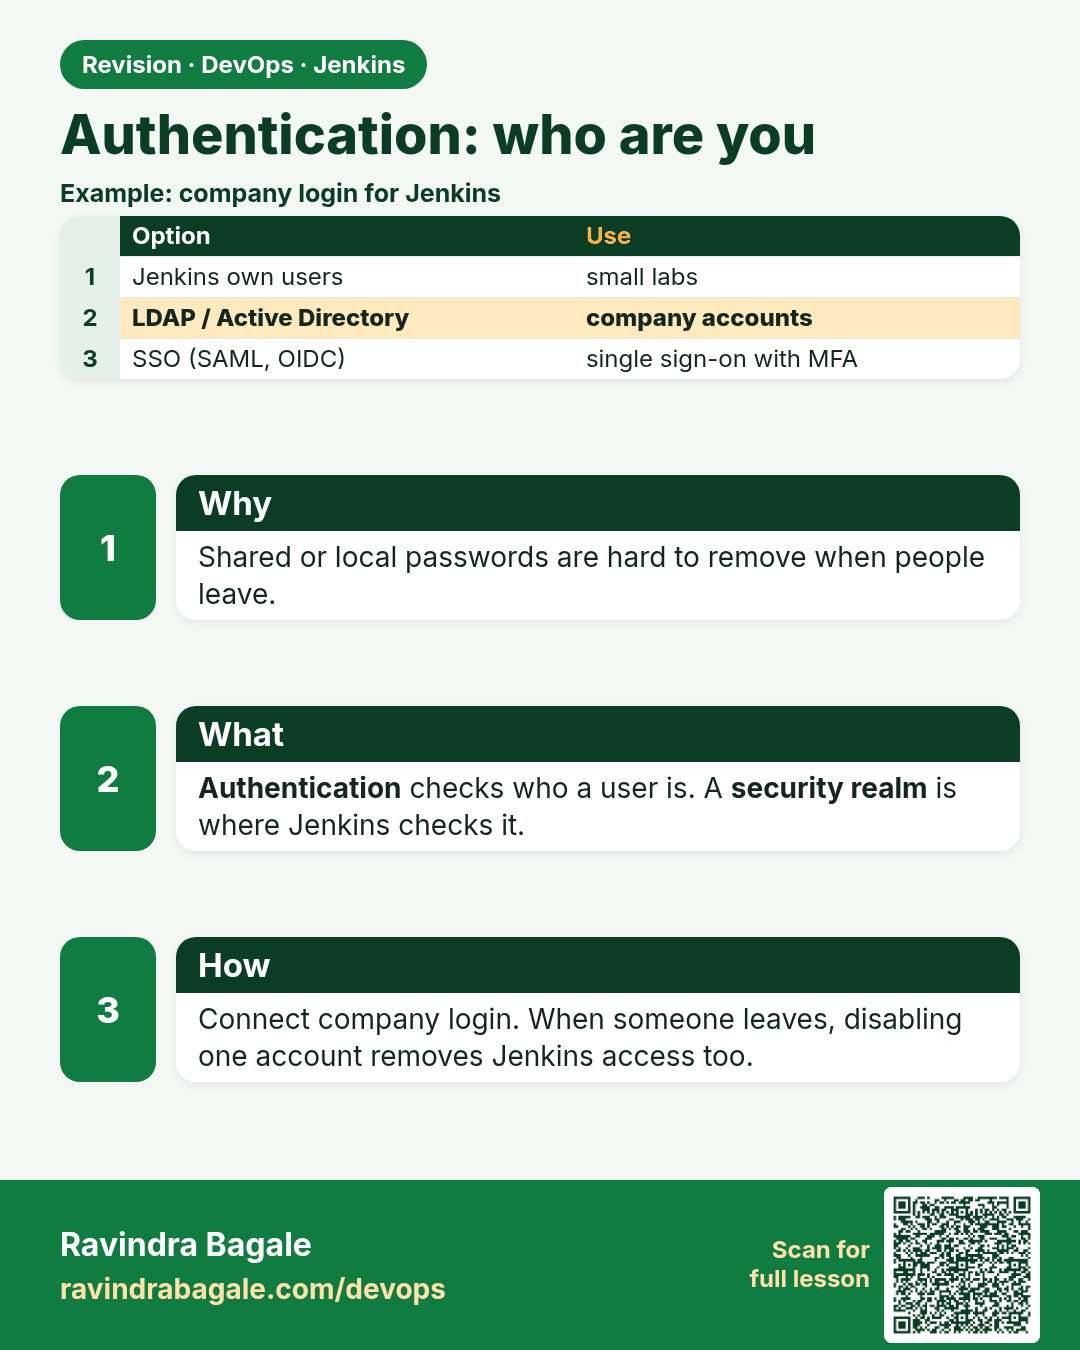
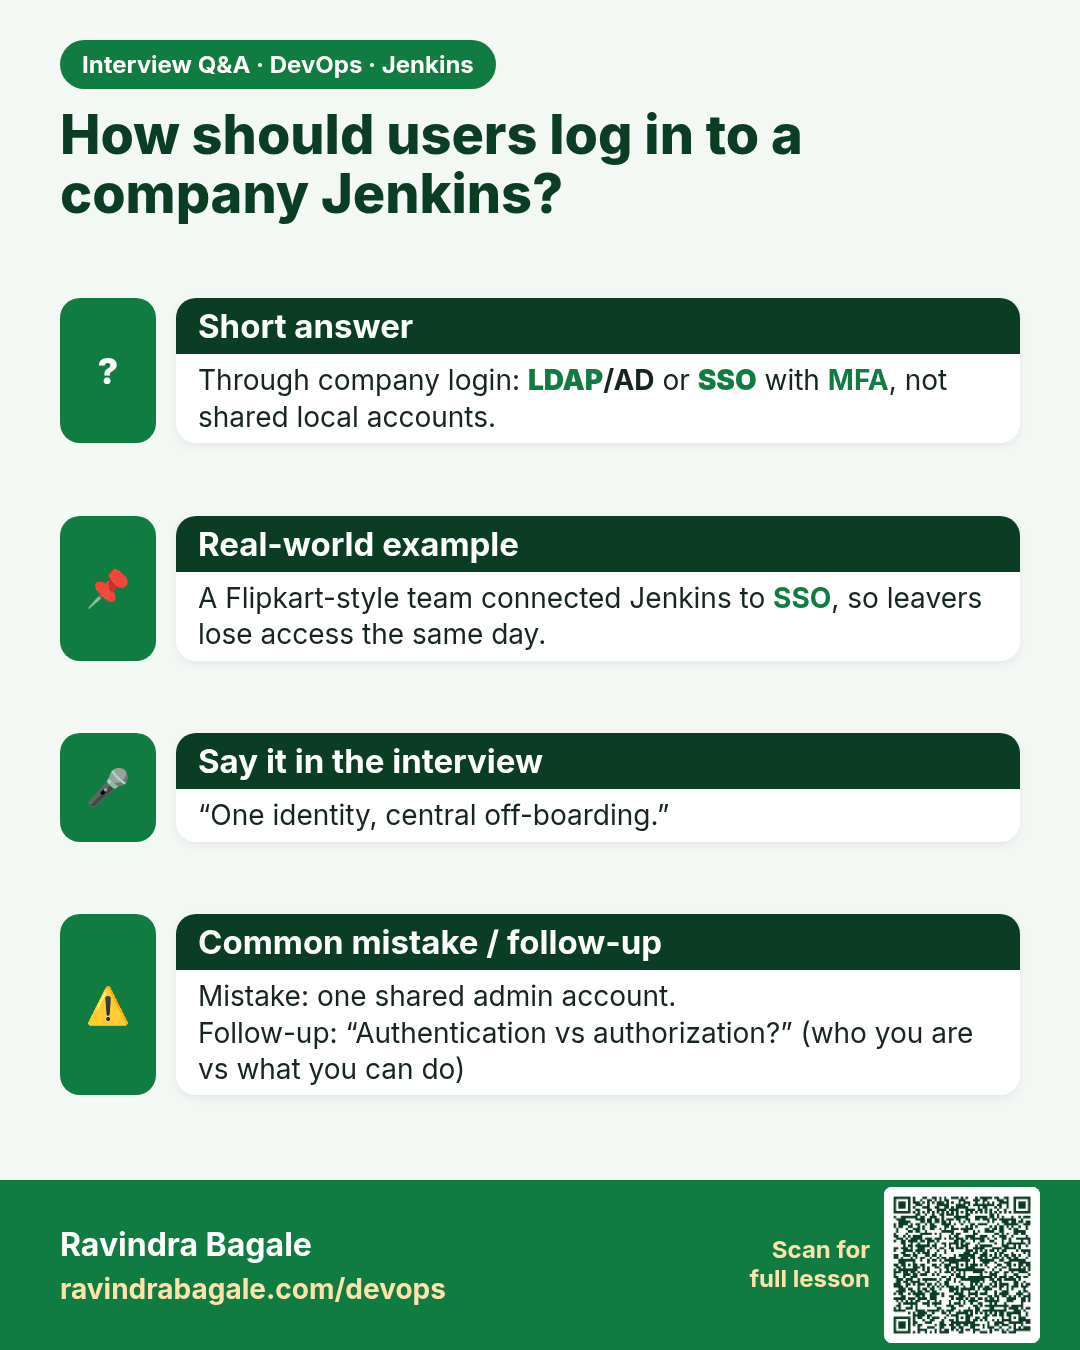
How should users log in to a company Jenkins? Through company login: LDAP/AD or SSO with MFA, not shared local accounts.
Interview card 2 of 7: How should users log in to a company Jenkins? · Download PNG · Open card page

Lesson: 26.2 Authentication

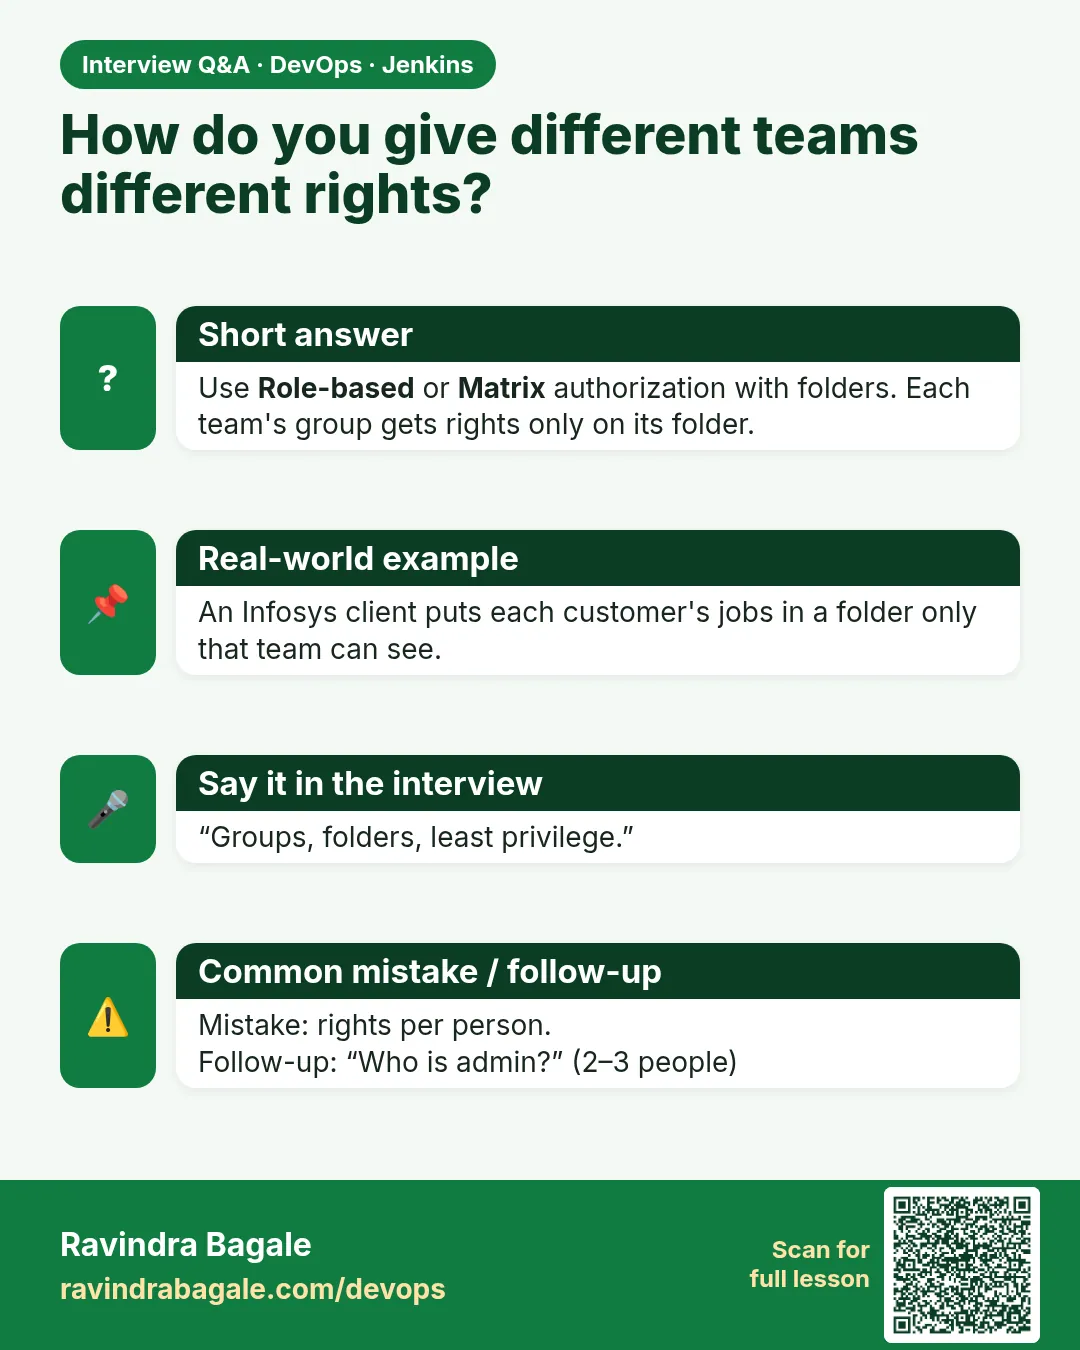
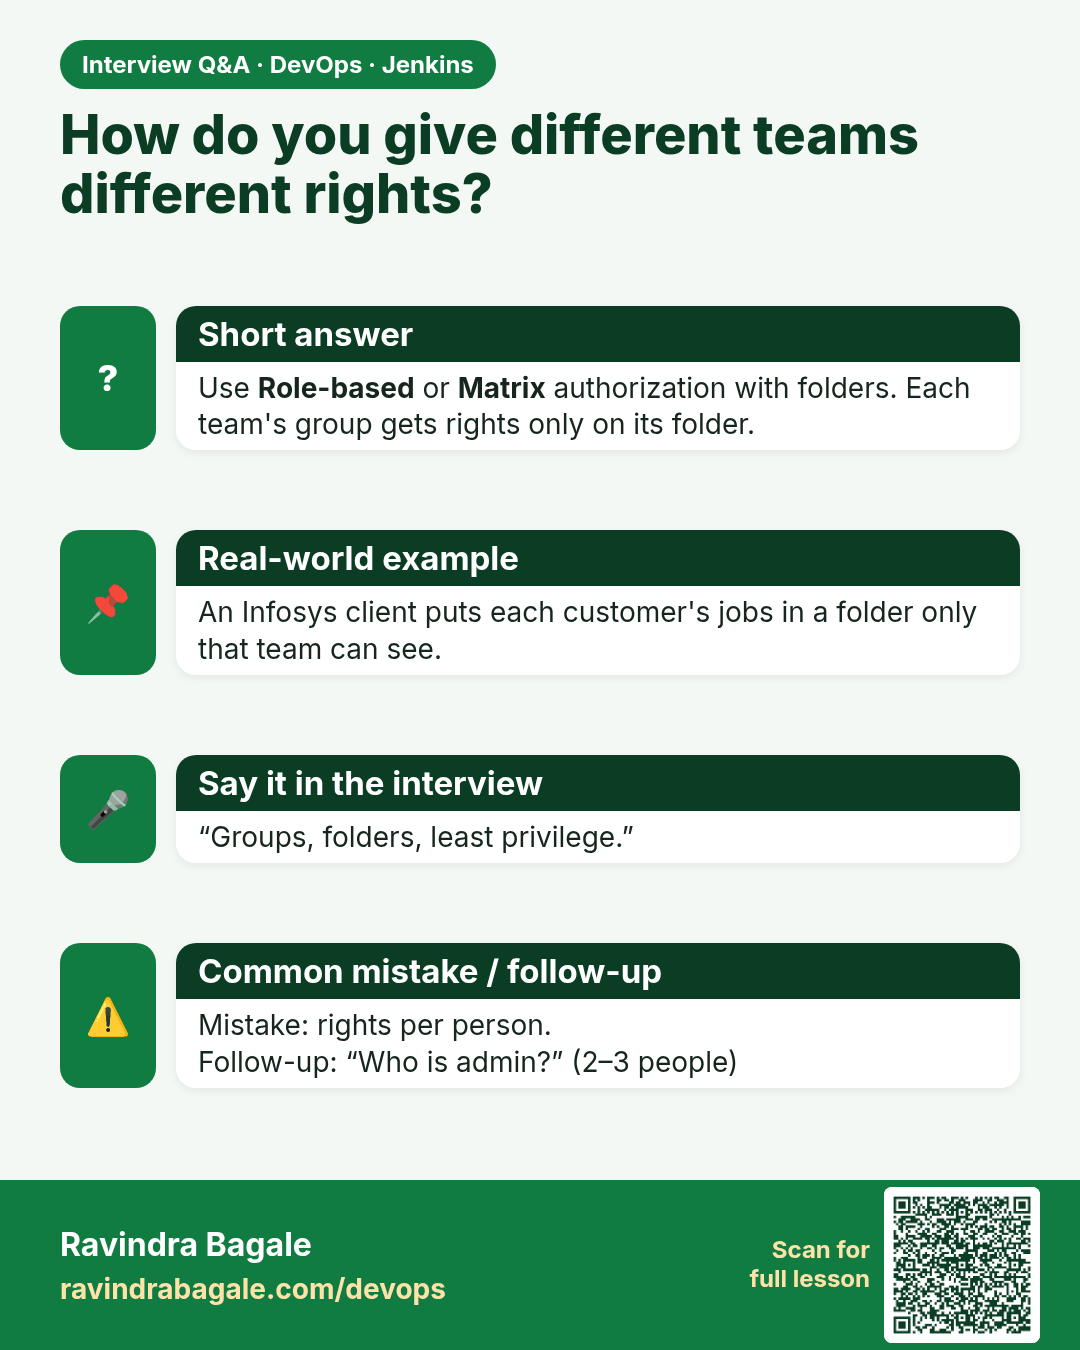
How do you give different teams different rights? Use Role-based or Matrix authorization with folders. Each team's group gets rights only on its folder.
Interview card 3 of 7: How do you give different teams different rights? · Download PNG · Open card page

Lesson: 26.3 Matrix and role strategy
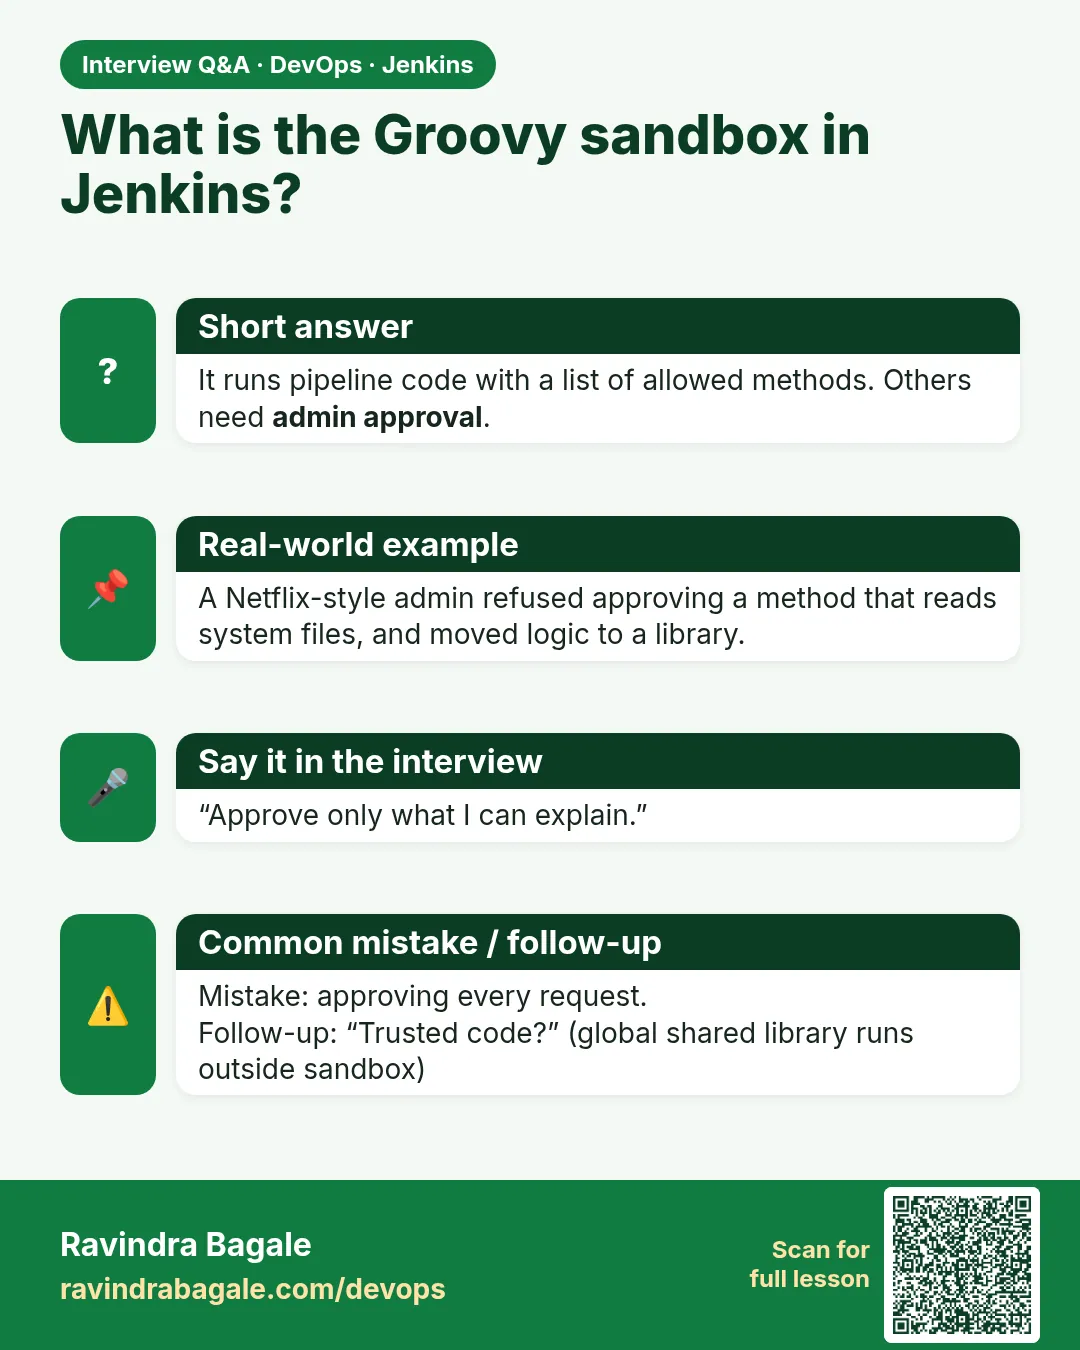
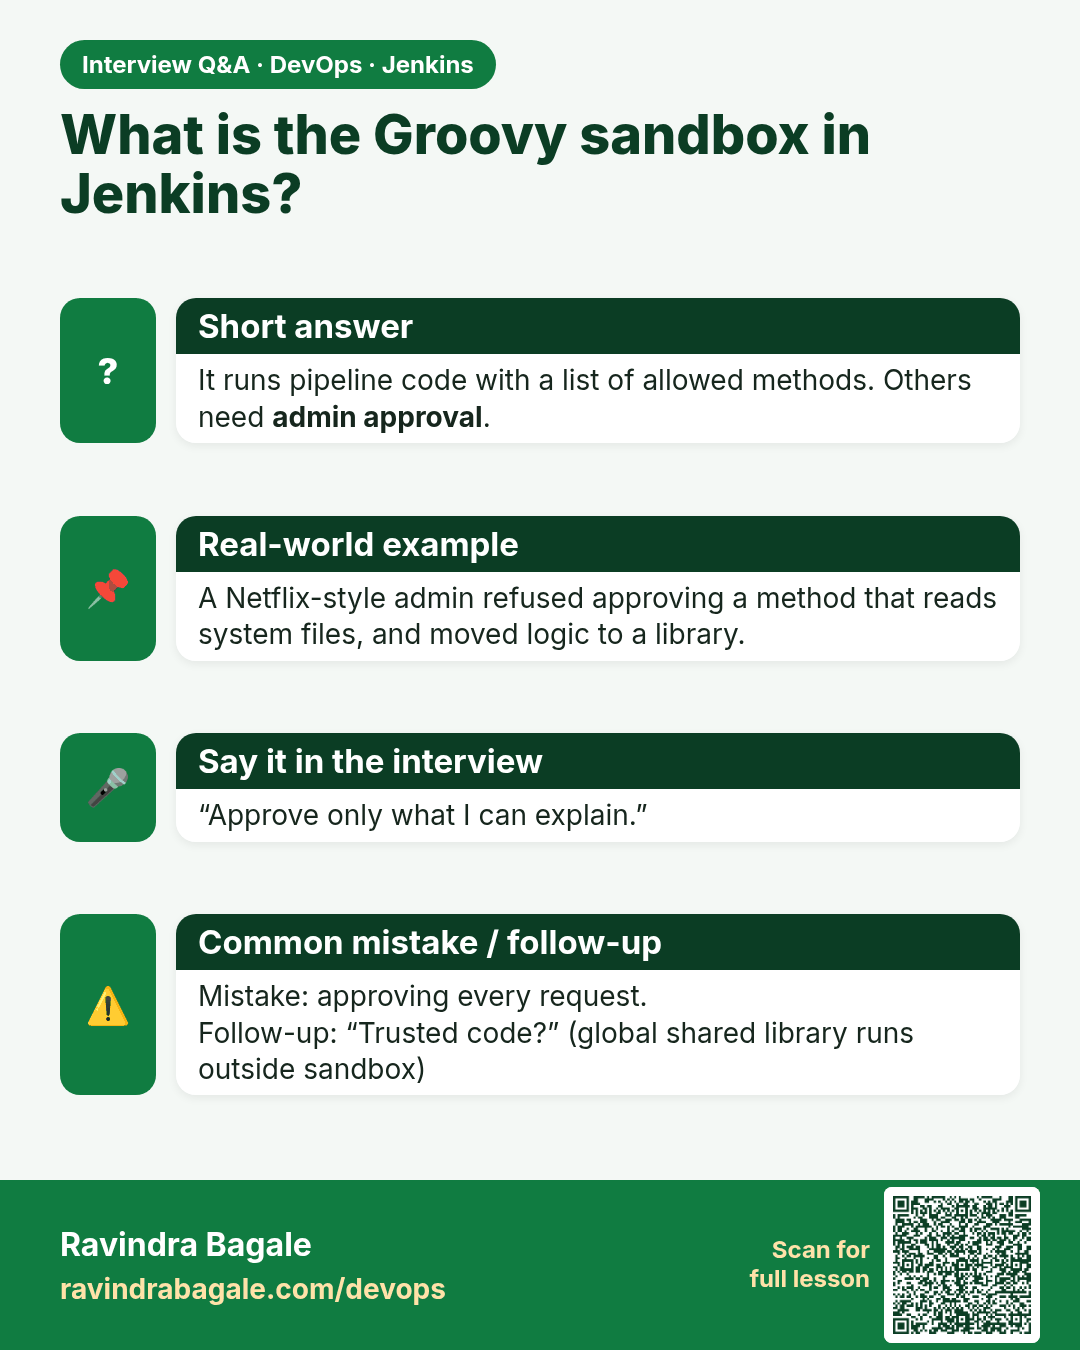
What is the Groovy sandbox in Jenkins? It runs pipeline code with a list of allowed methods. Others need admin approval.
Interview card 4 of 7: What is the Groovy sandbox in Jenkins? · Download PNG · Open card page

Lesson: 26.4 Script approval and the Groovy sandbox

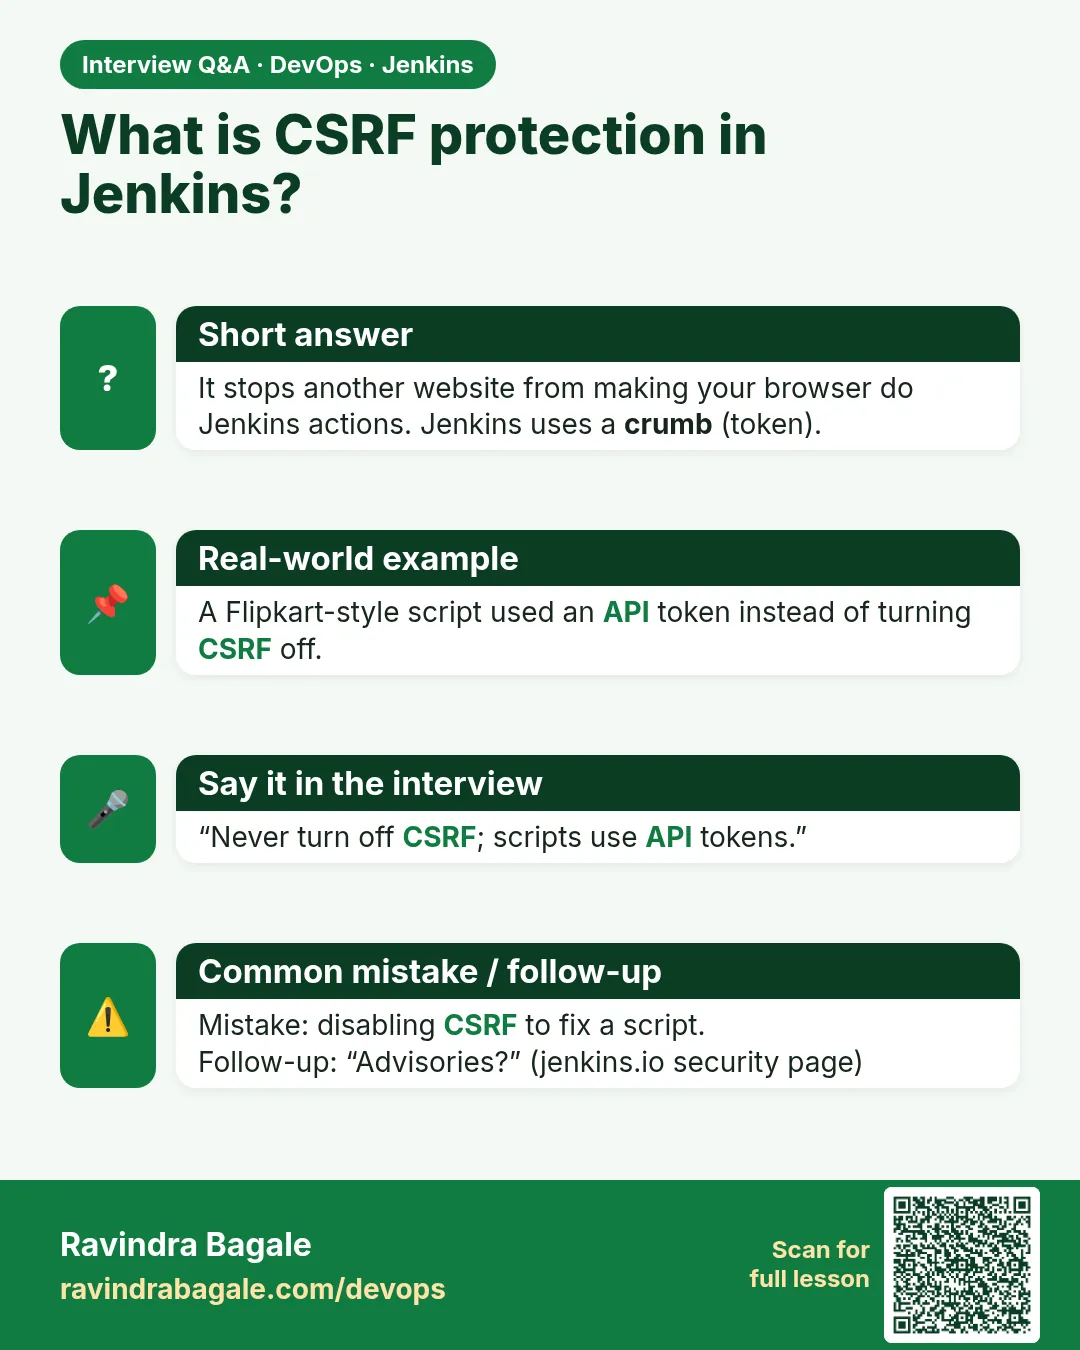
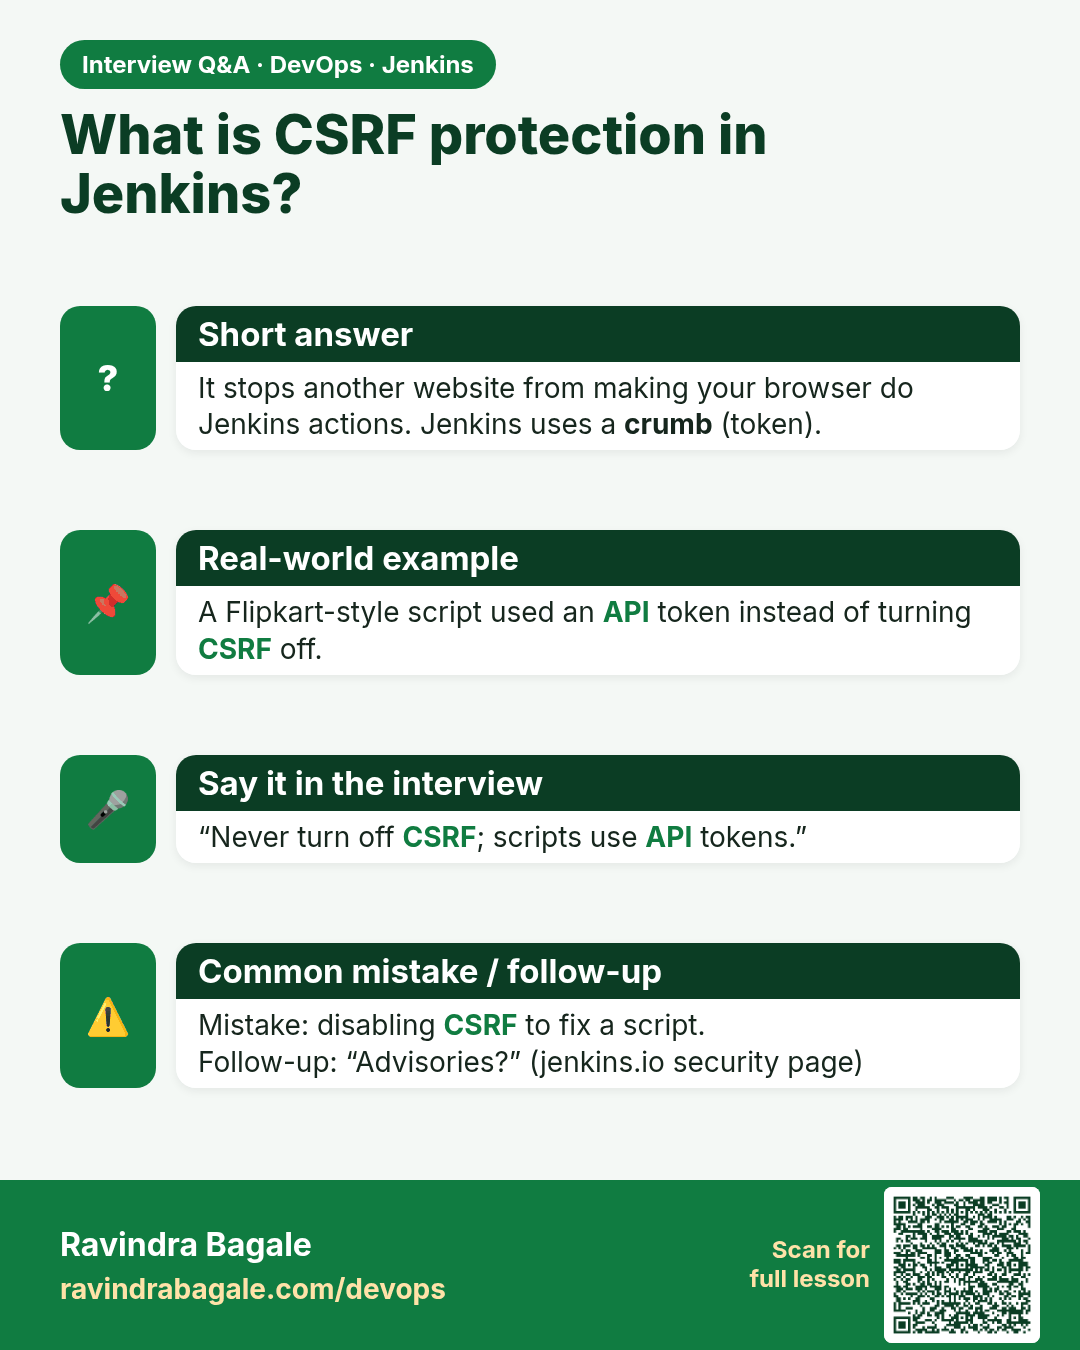
What is CSRF protection in Jenkins? It stops another website from making your browser do Jenkins actions. Jenkins uses a crumb (token).
Interview card 5 of 7: What is CSRF protection in Jenkins? · Download PNG · Open card page

Lesson: 26.5 CSRF, agents, tokens, advisories

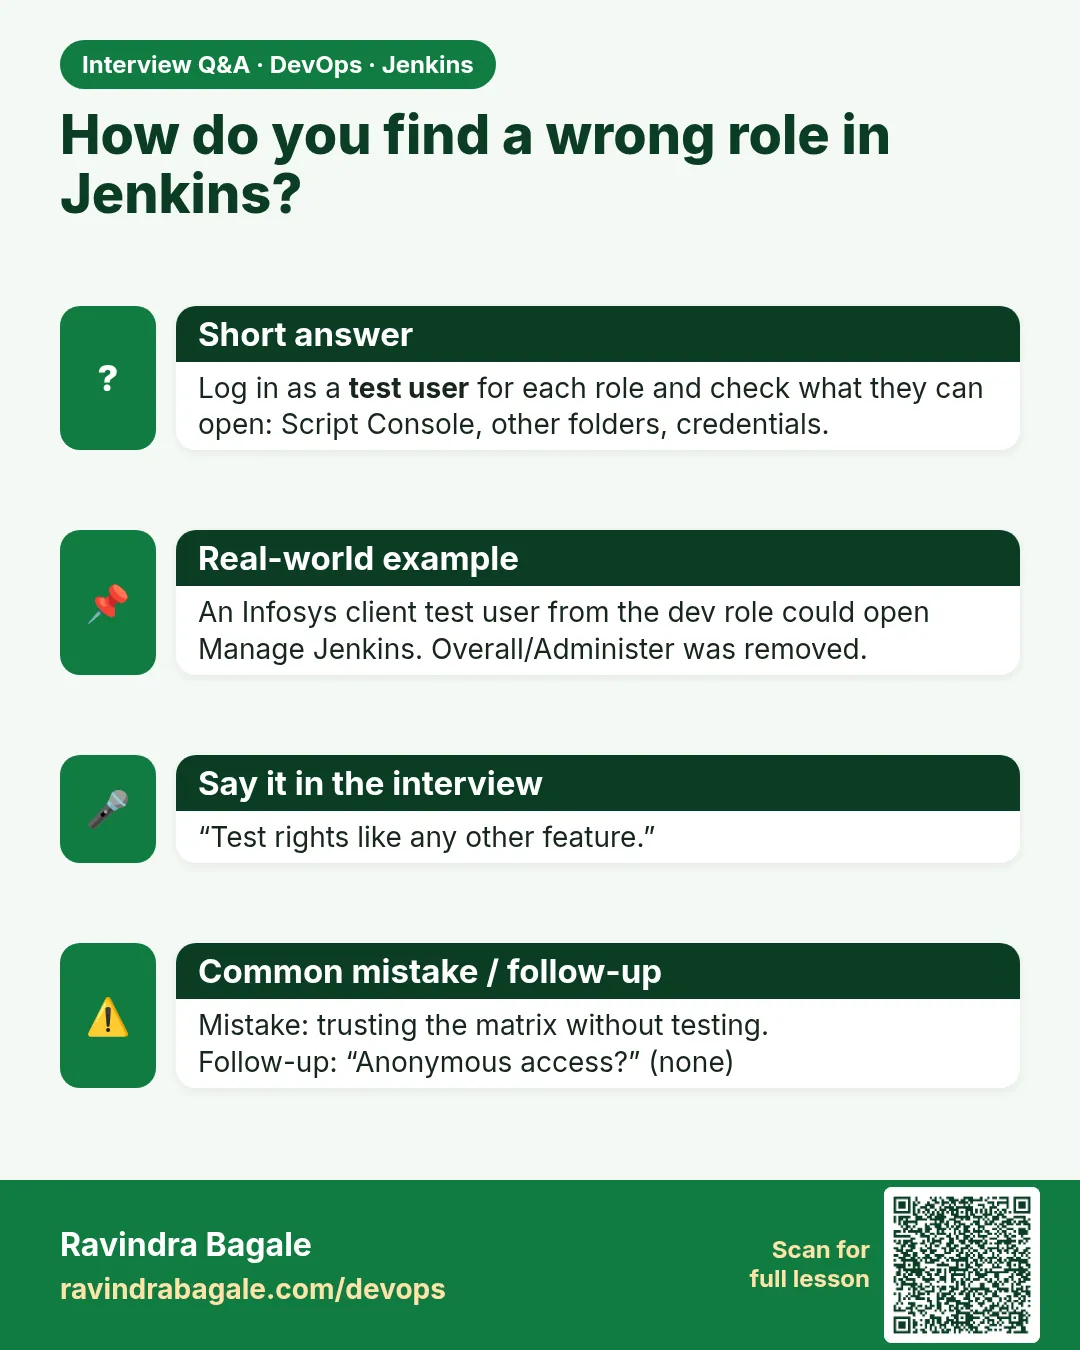
How do you find a wrong role in Jenkins? Log in as a test user for each role and check what they can open: Script Console, other folders, credentials.
Interview card 6 of 7: How do you find a wrong role in Jenkins? · Download PNG · Open card page

Lesson: 26.6 What a wrong role looks like

Give a short Jenkins hardening checklist. HTTPS, company login, least rights, CSRF on, 0 controller executors, few updated plugins, tested backups.
Interview card 7 of 7: Give a short Jenkins hardening checklist. · Download PNG · Open card page

Lesson: 26.7 Hardening checklist

Comparison cards

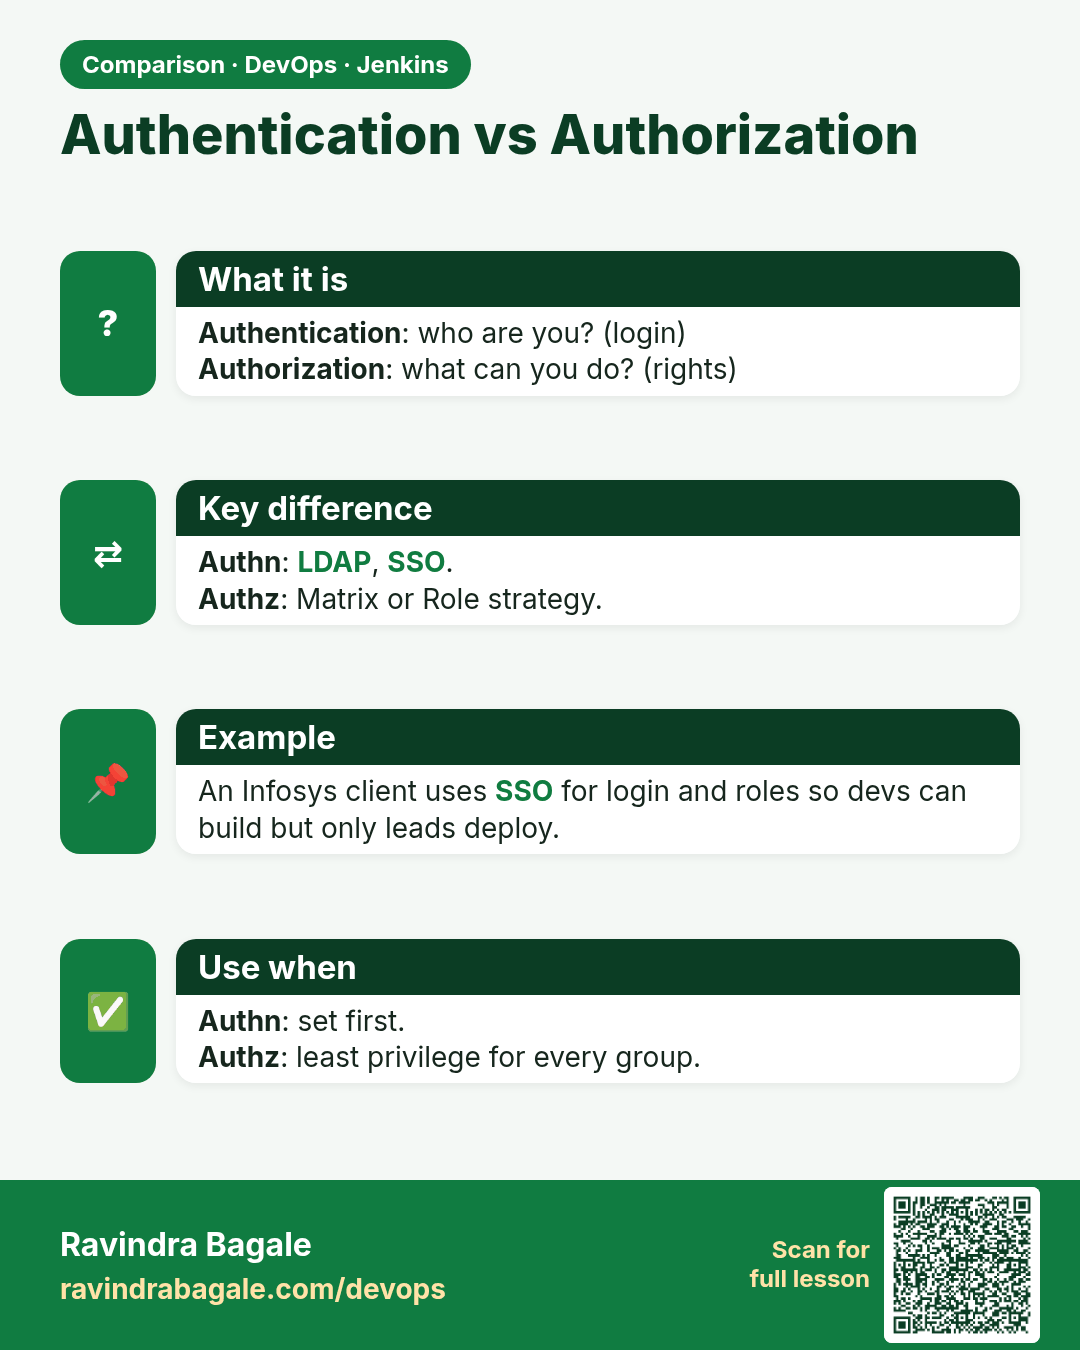
Authentication vs Authorization. Authentication: who are you? (login)Authorization: what can you do? (rights)
Comparison card 1 of 3: Authentication vs Authorization · Download PNG · Open card page

Lesson: 26.2 Authentication

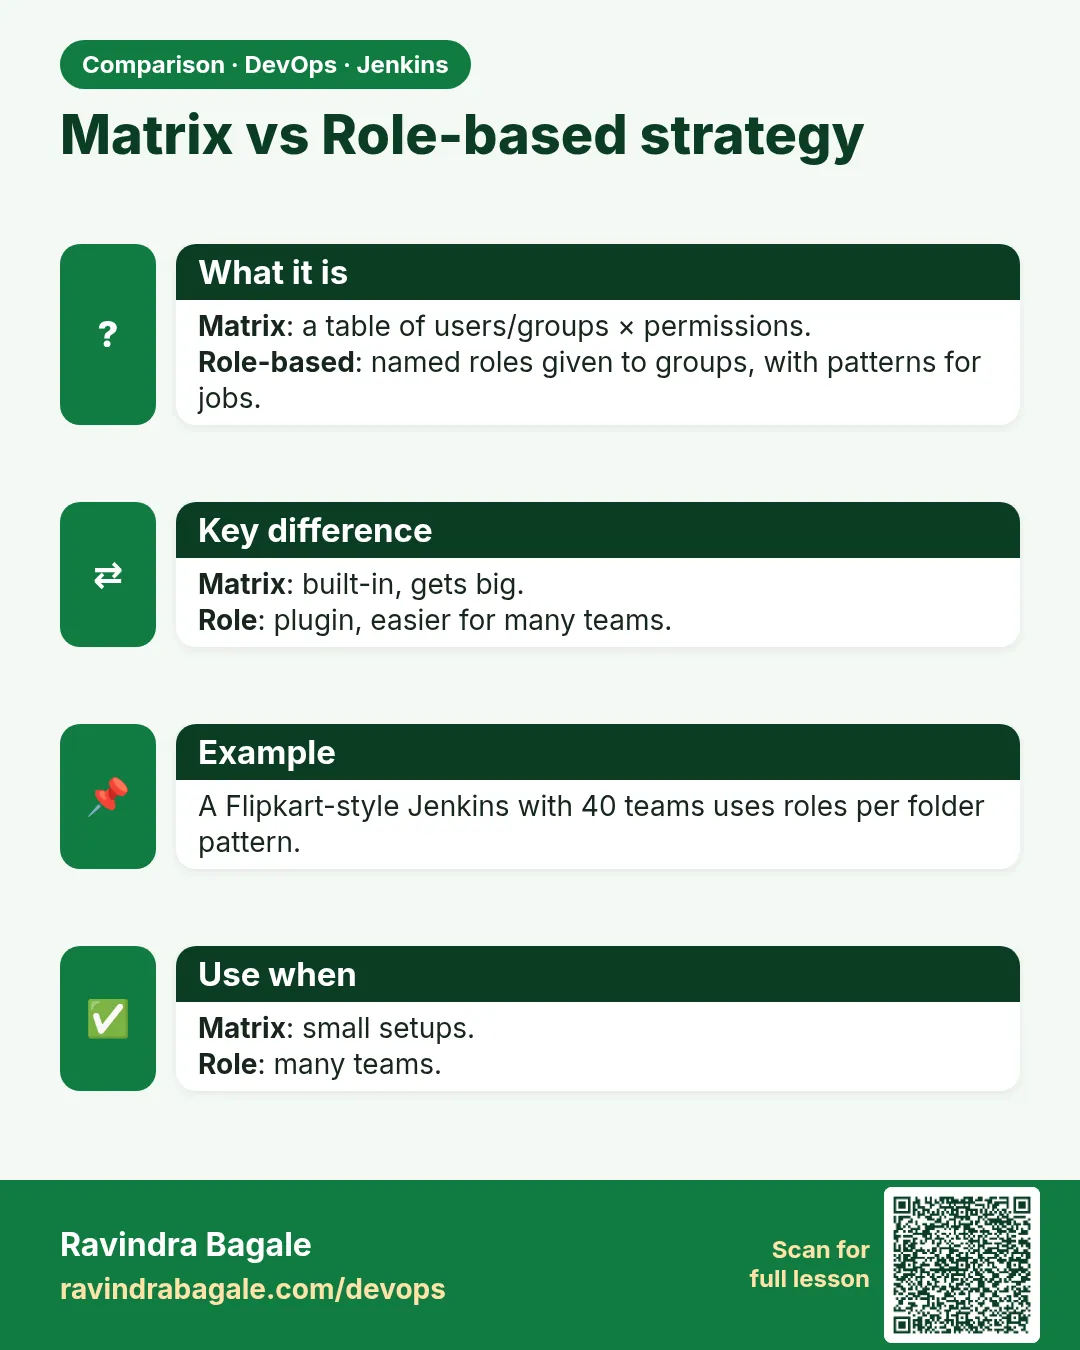
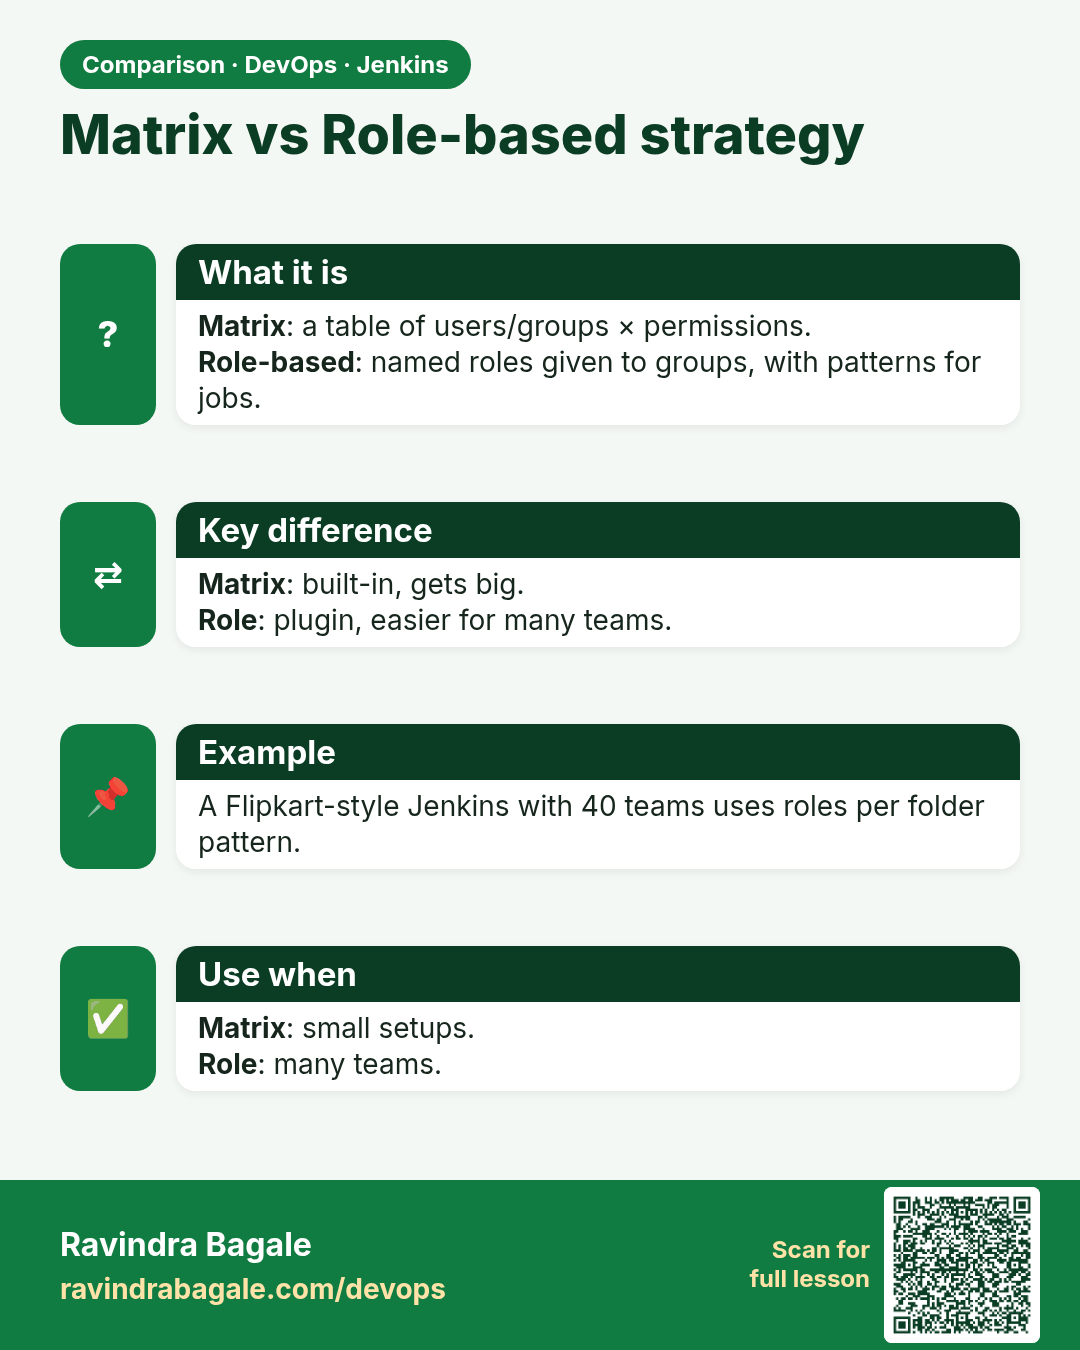
Matrix vs Role-based strategy. Matrix: a table of users/groups × permissions.Role-based: named roles given to groups, with patterns for jobs.
Comparison card 2 of 3: Matrix vs Role-based strategy · Download PNG · Open card page

Lesson: 26.3 Matrix and role strategy
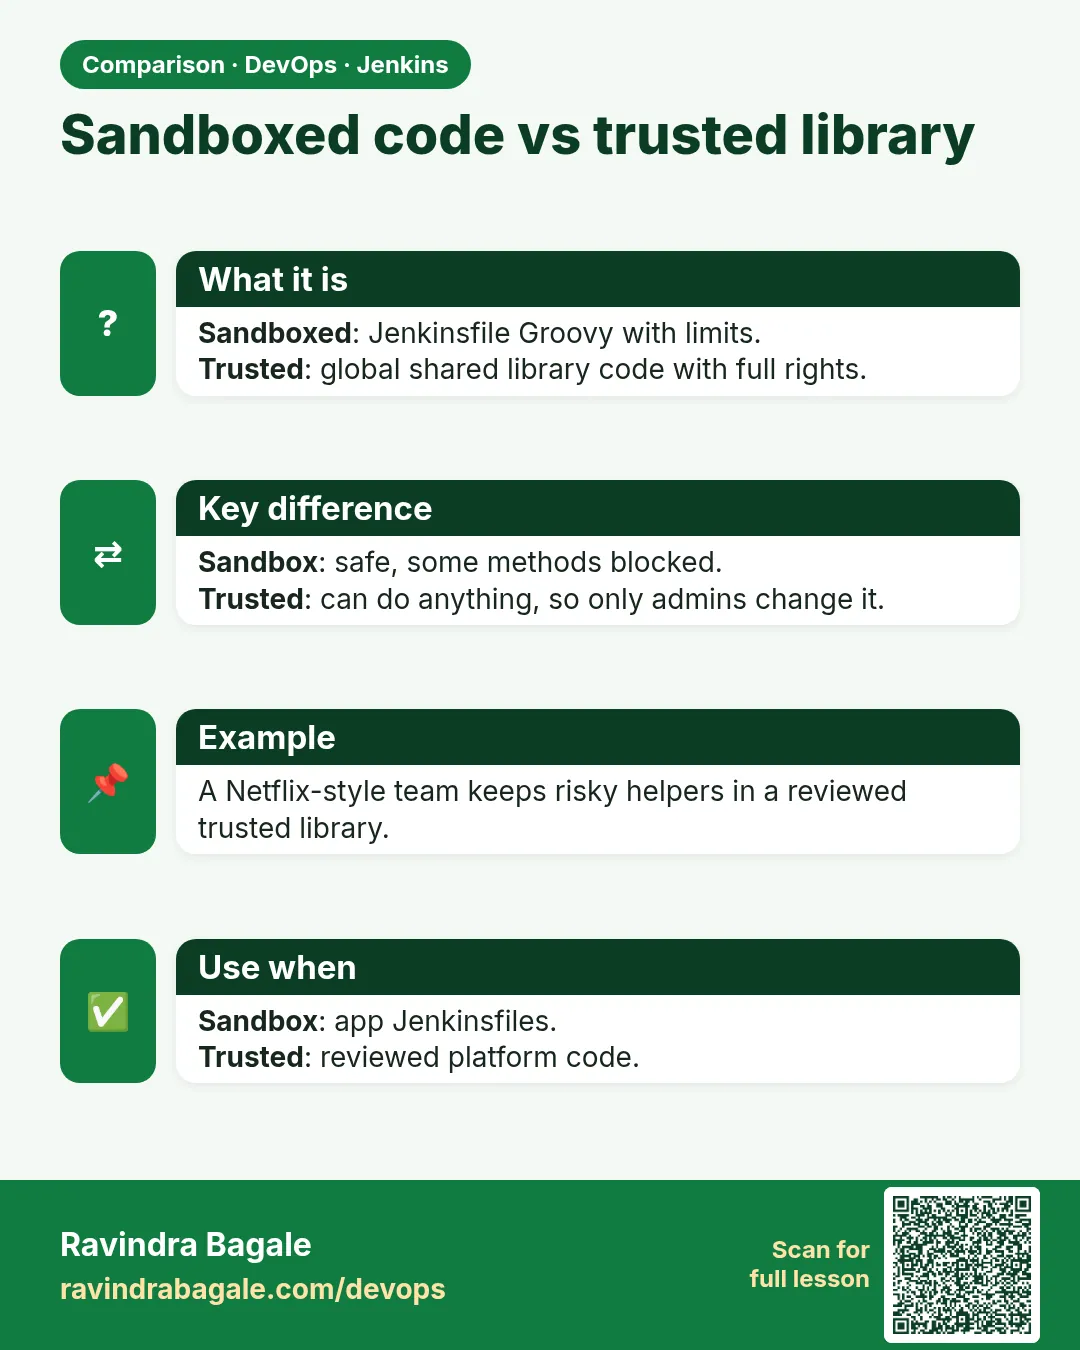
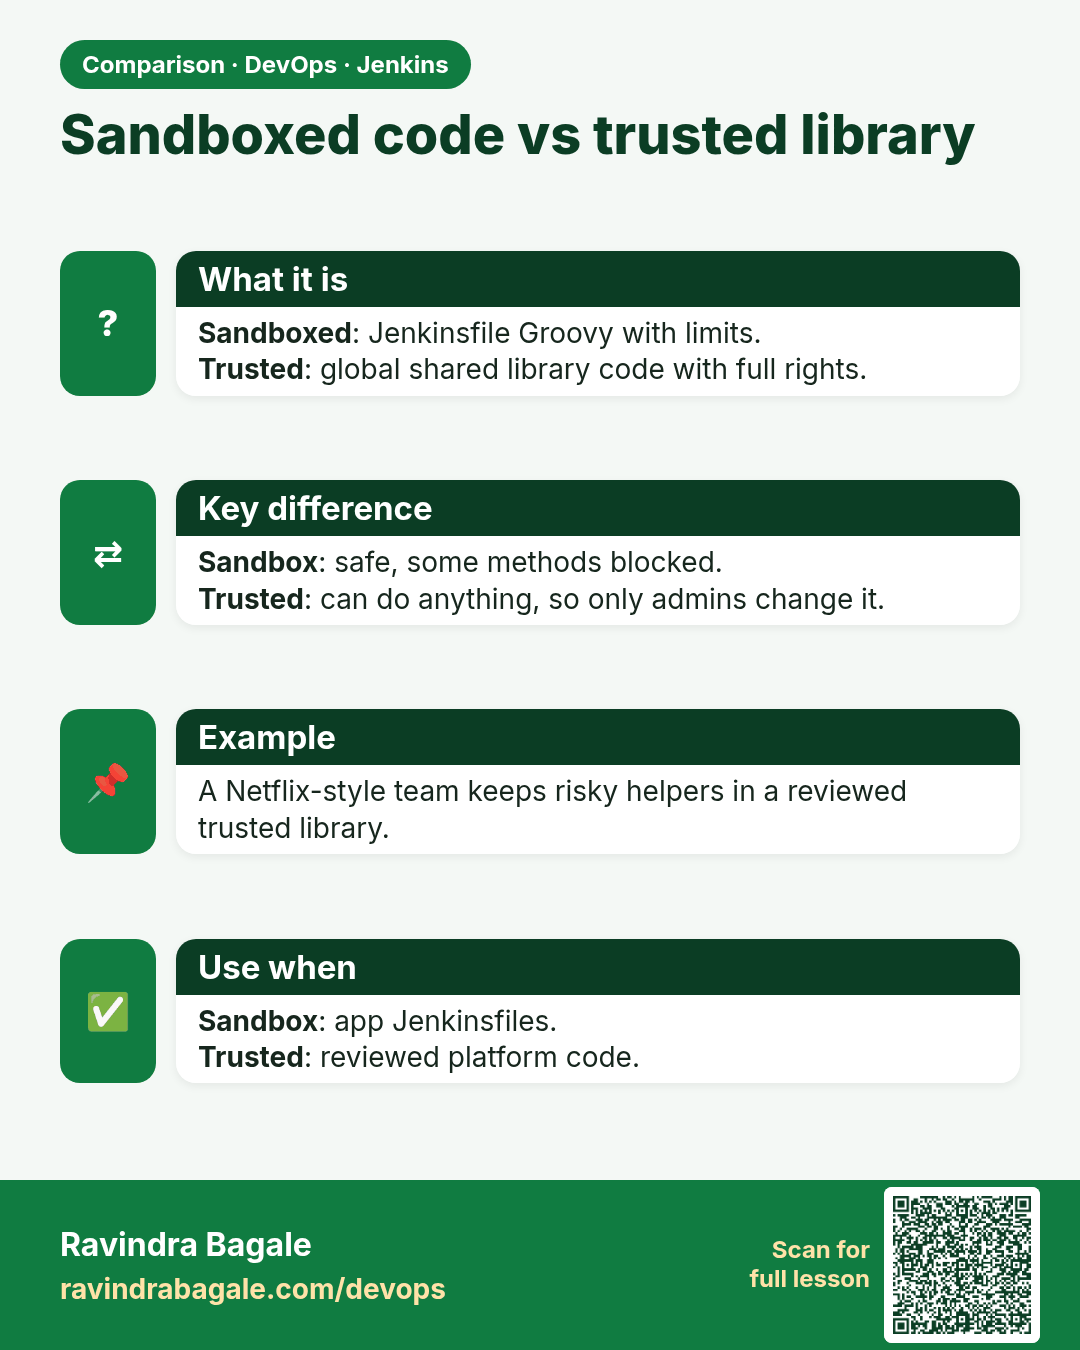
Sandboxed code vs trusted library. Sandboxed: Jenkinsfile Groovy with limits.Trusted: global shared library code with full rights.
Comparison card 3 of 3: Sandboxed code vs trusted library · Download PNG · Open card page

Lesson: 26.4 Script approval and the Groovy sandbox