Ravi Sir's Cards › DevOps
Chapter 40: Terraform Real AWS Labs VPC EC2 nginx S3 and IAM Role: मराठी Cards
English cards · Chapter उघडा
उजळणी (Revision) cards
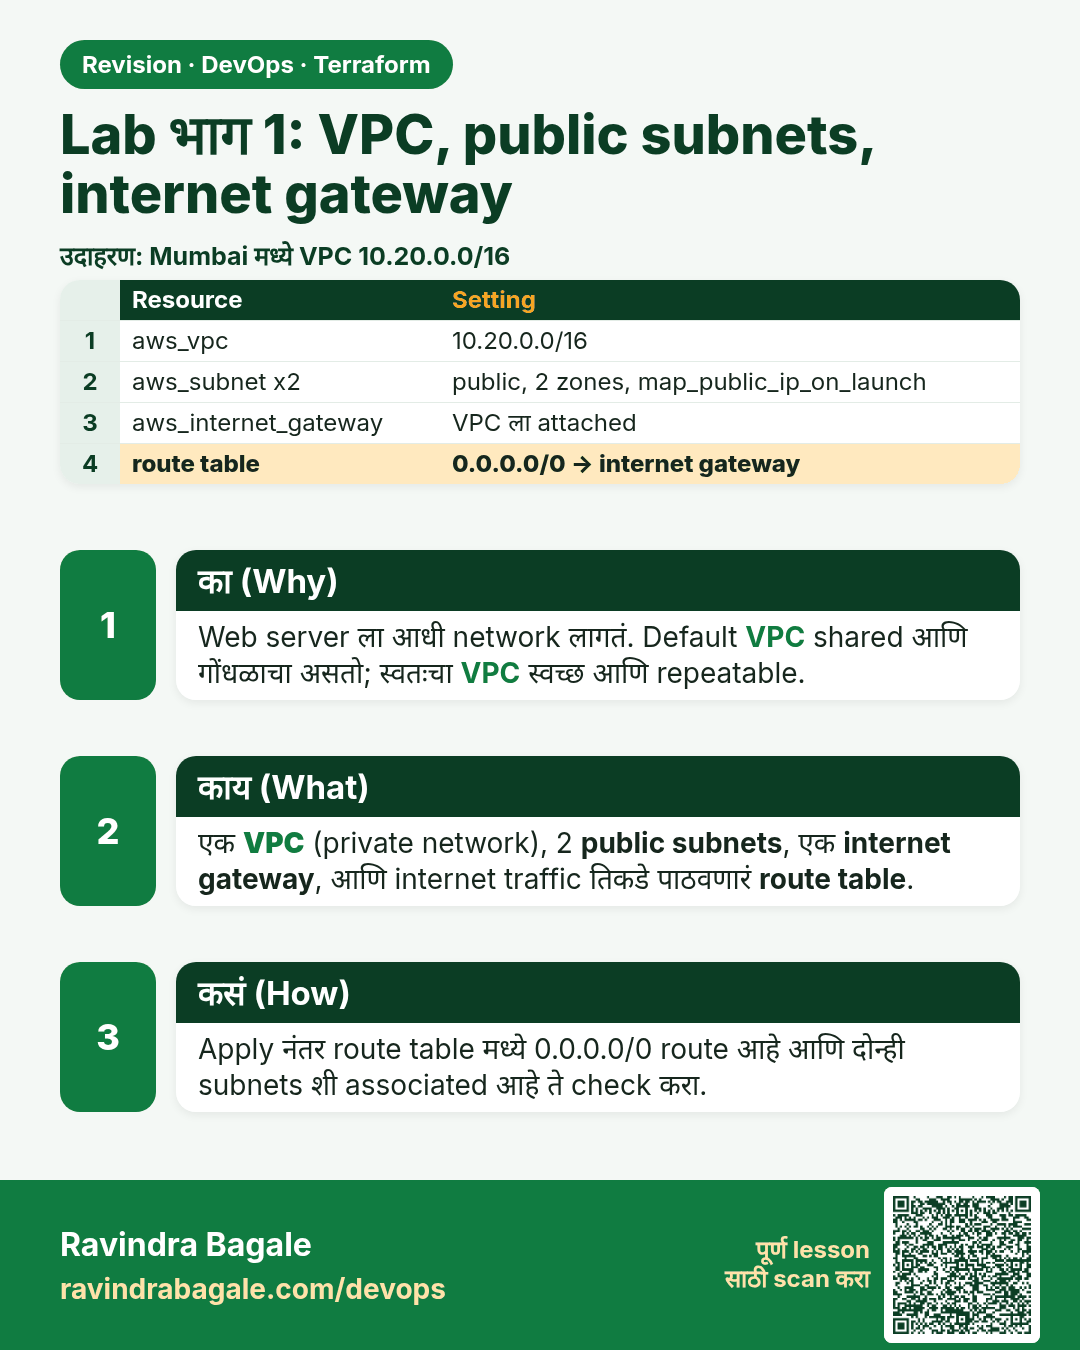
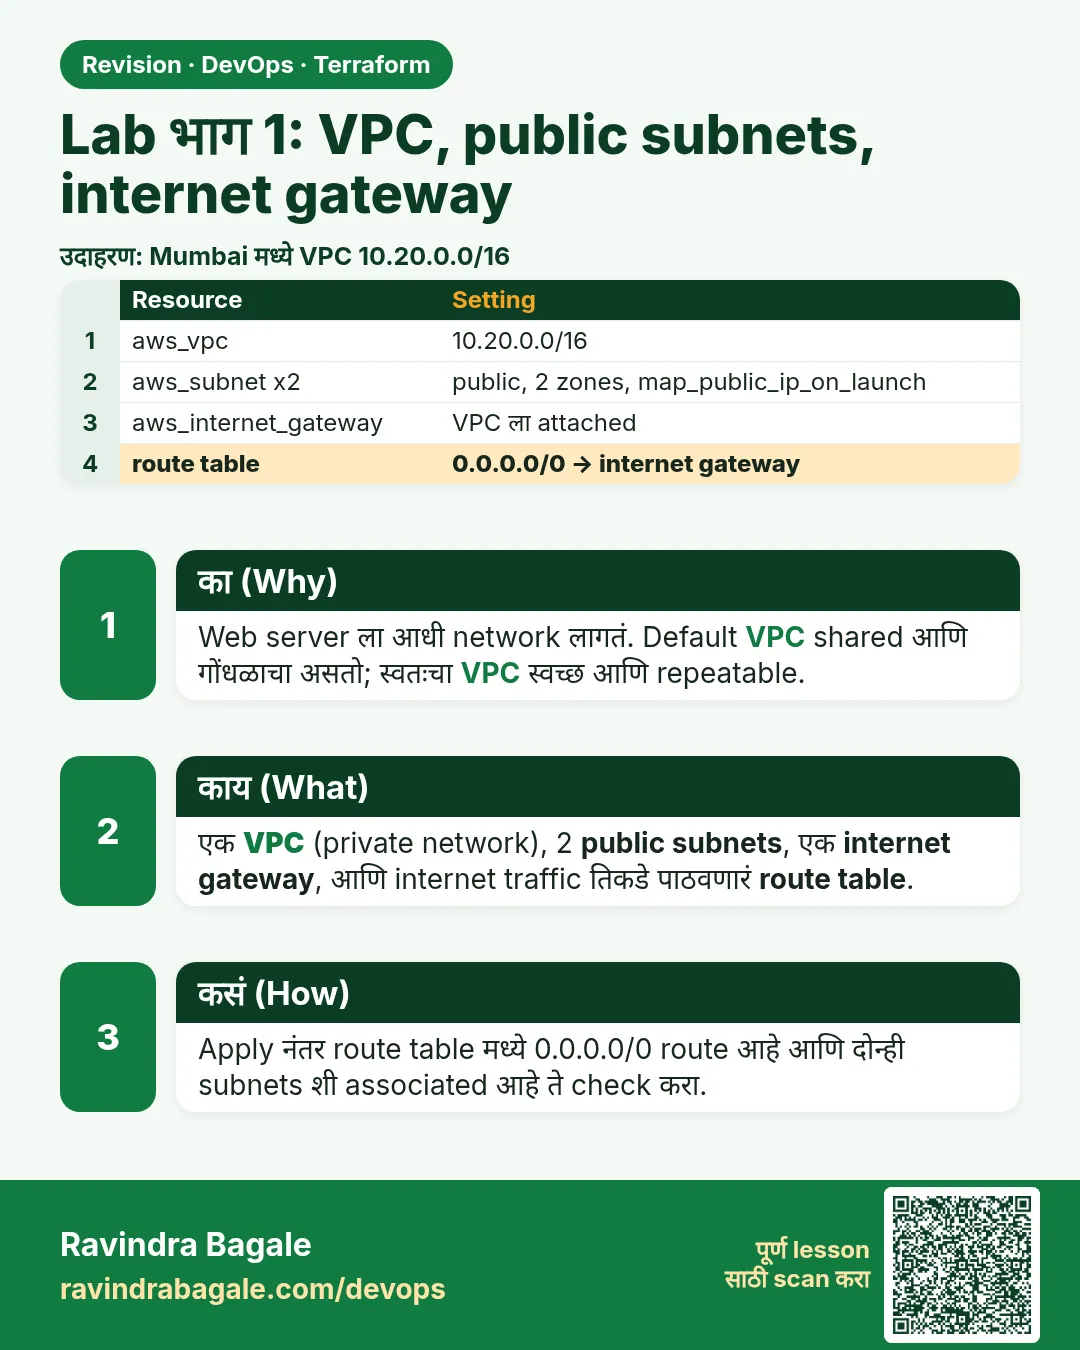 उजळणी (Revision) card 1 of 5: Lab भाग 1: VPC, public subnets, internet gateway · PNG download करा · Card page उघडा
Lesson: 40.1 Lab part 1 — VPC, public subnets, internet gateway and routes
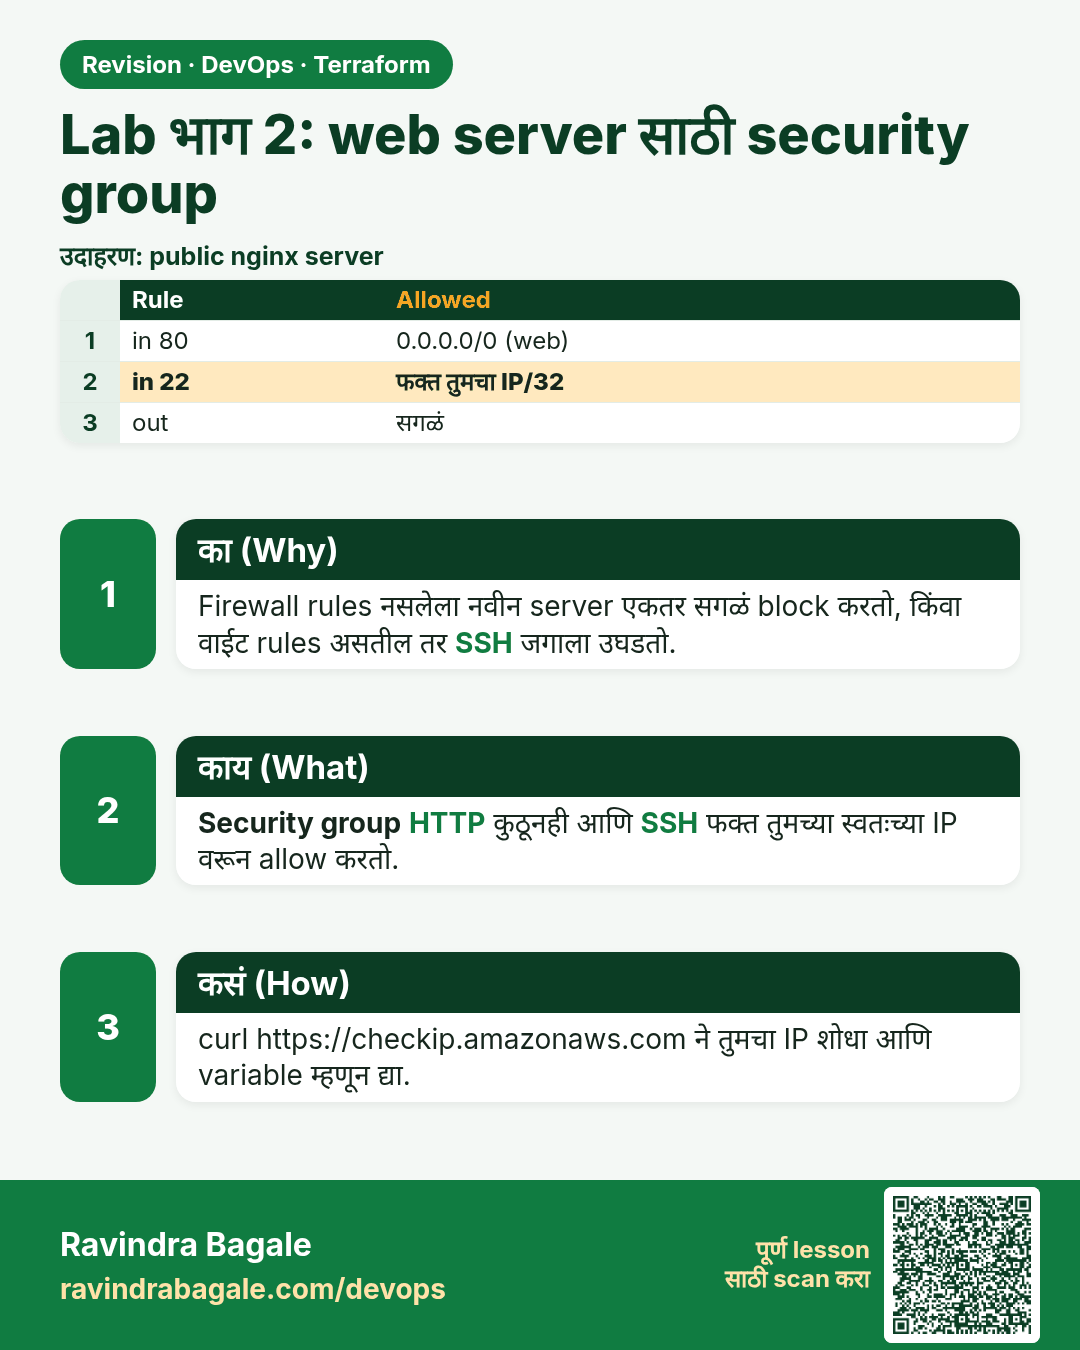
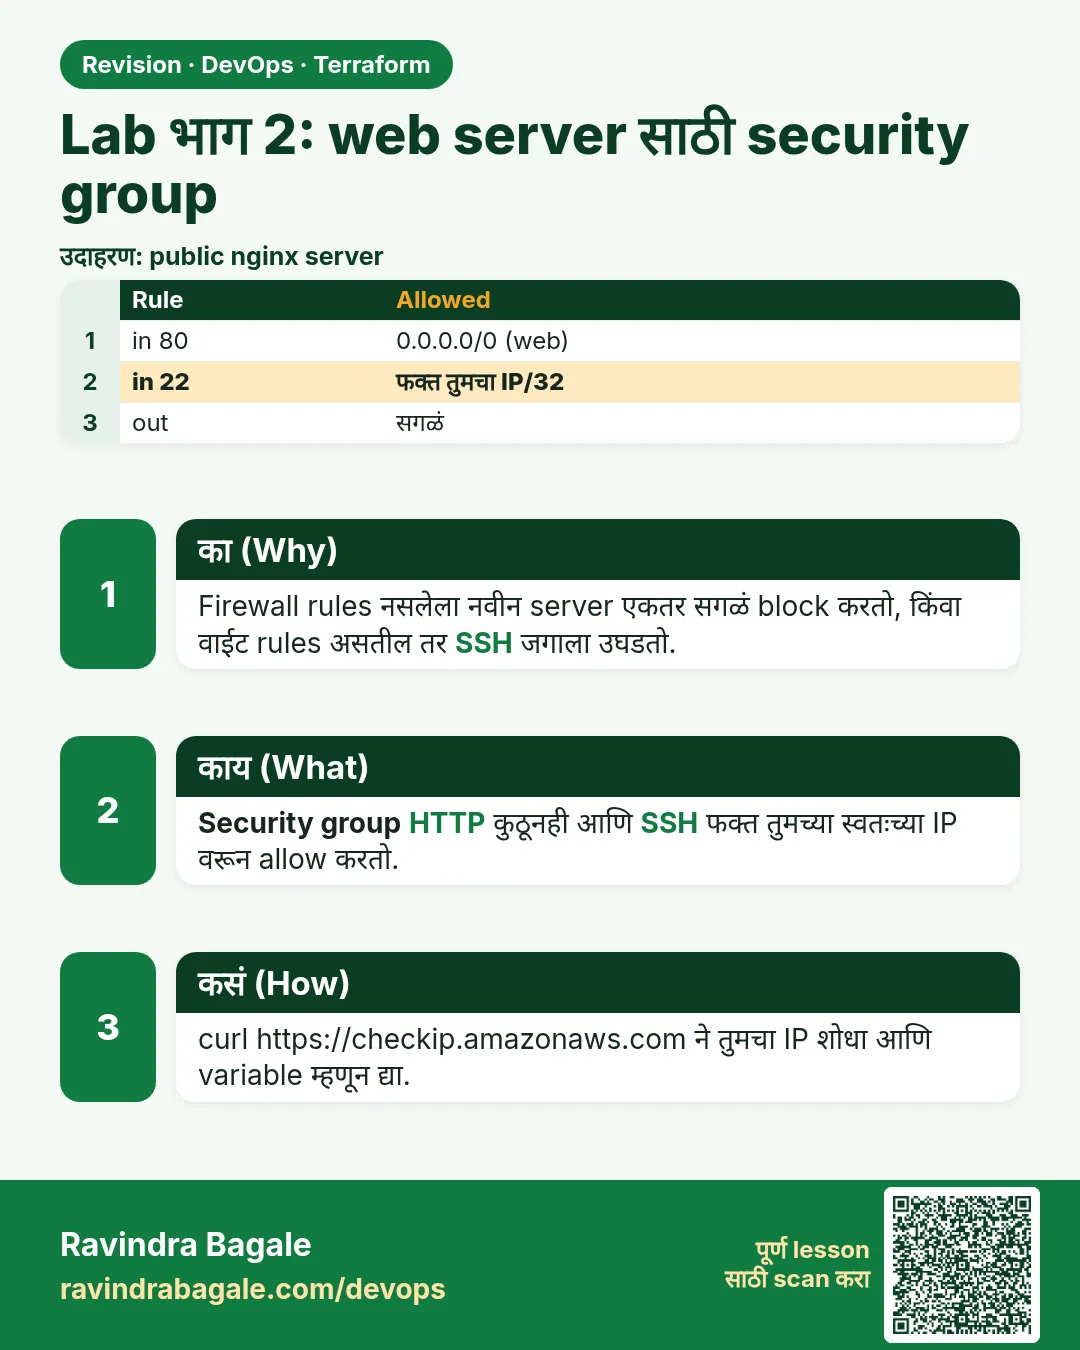 उजळणी (Revision) card 2 of 5: Lab भाग 2: web server साठी security group · PNG download करा · Card page उघडा
Lesson: 40.2 Lab part 2 — security group for the web server
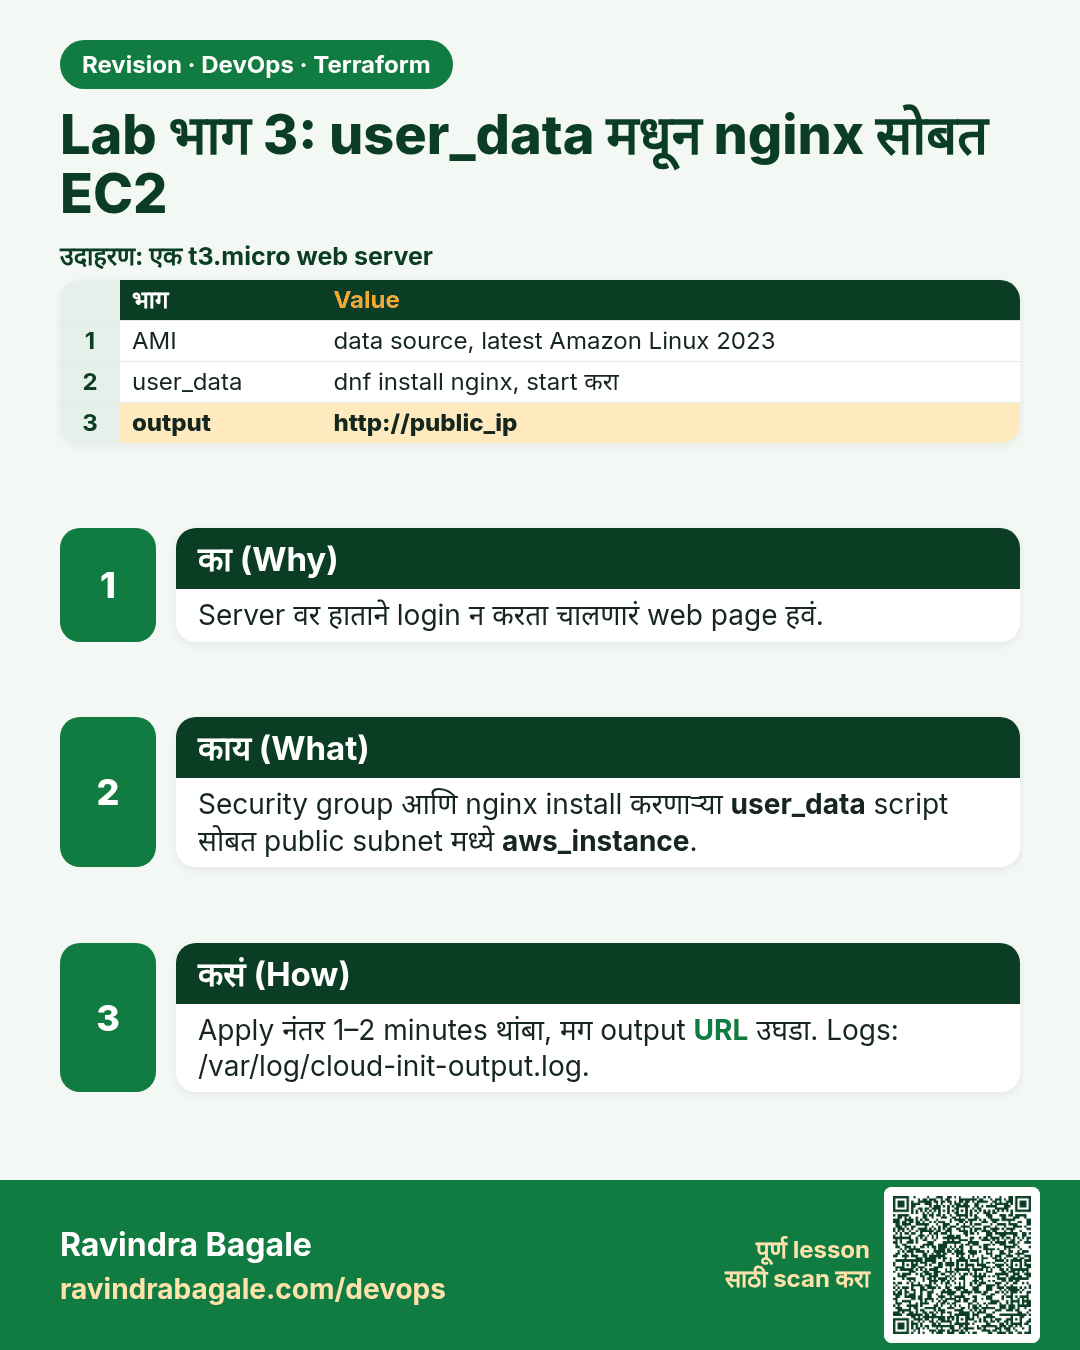
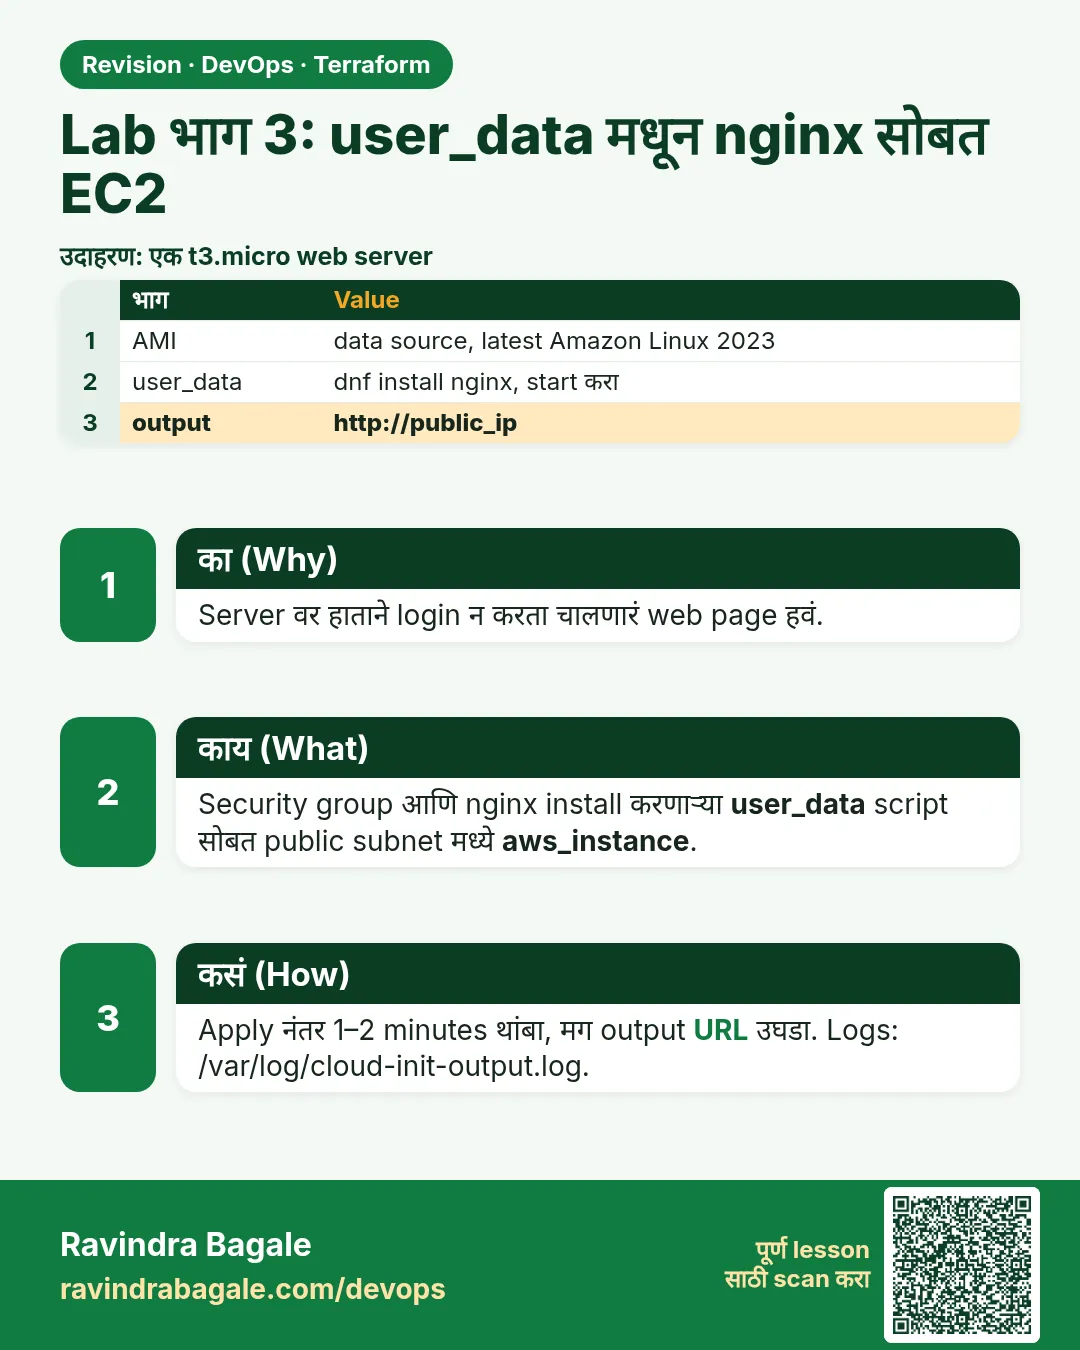 उजळणी (Revision) card 3 of 5: Lab भाग 3: user_data मधून nginx सोबत EC2 · PNG download करा · Card page उघडा
Lesson: 40.3 Lab part 3 — EC2 with nginx from user_data
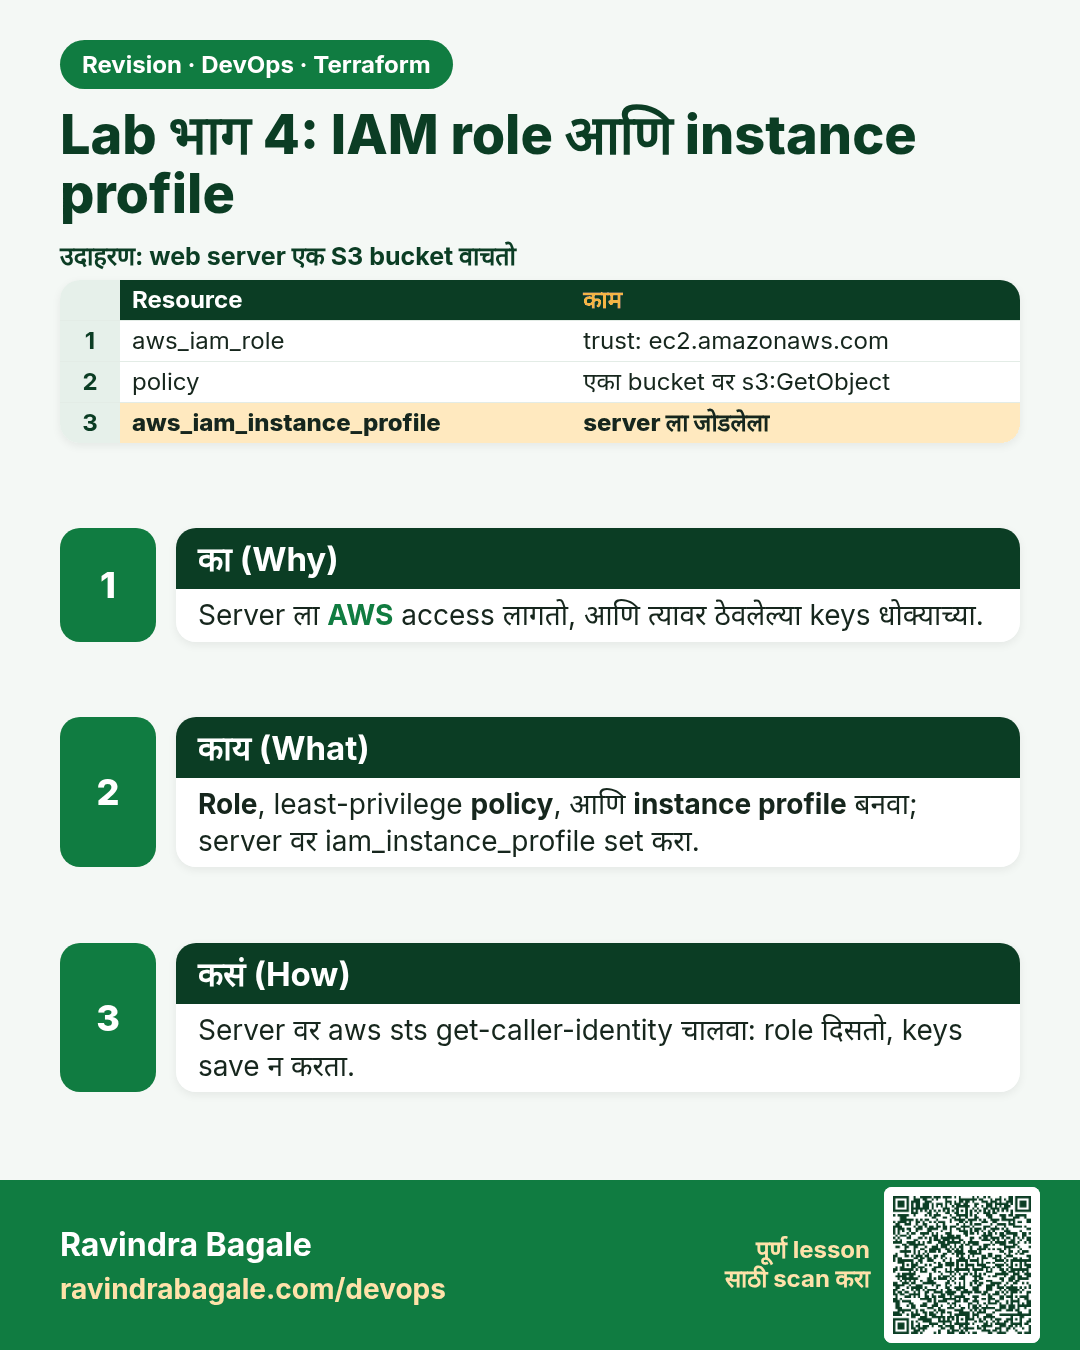
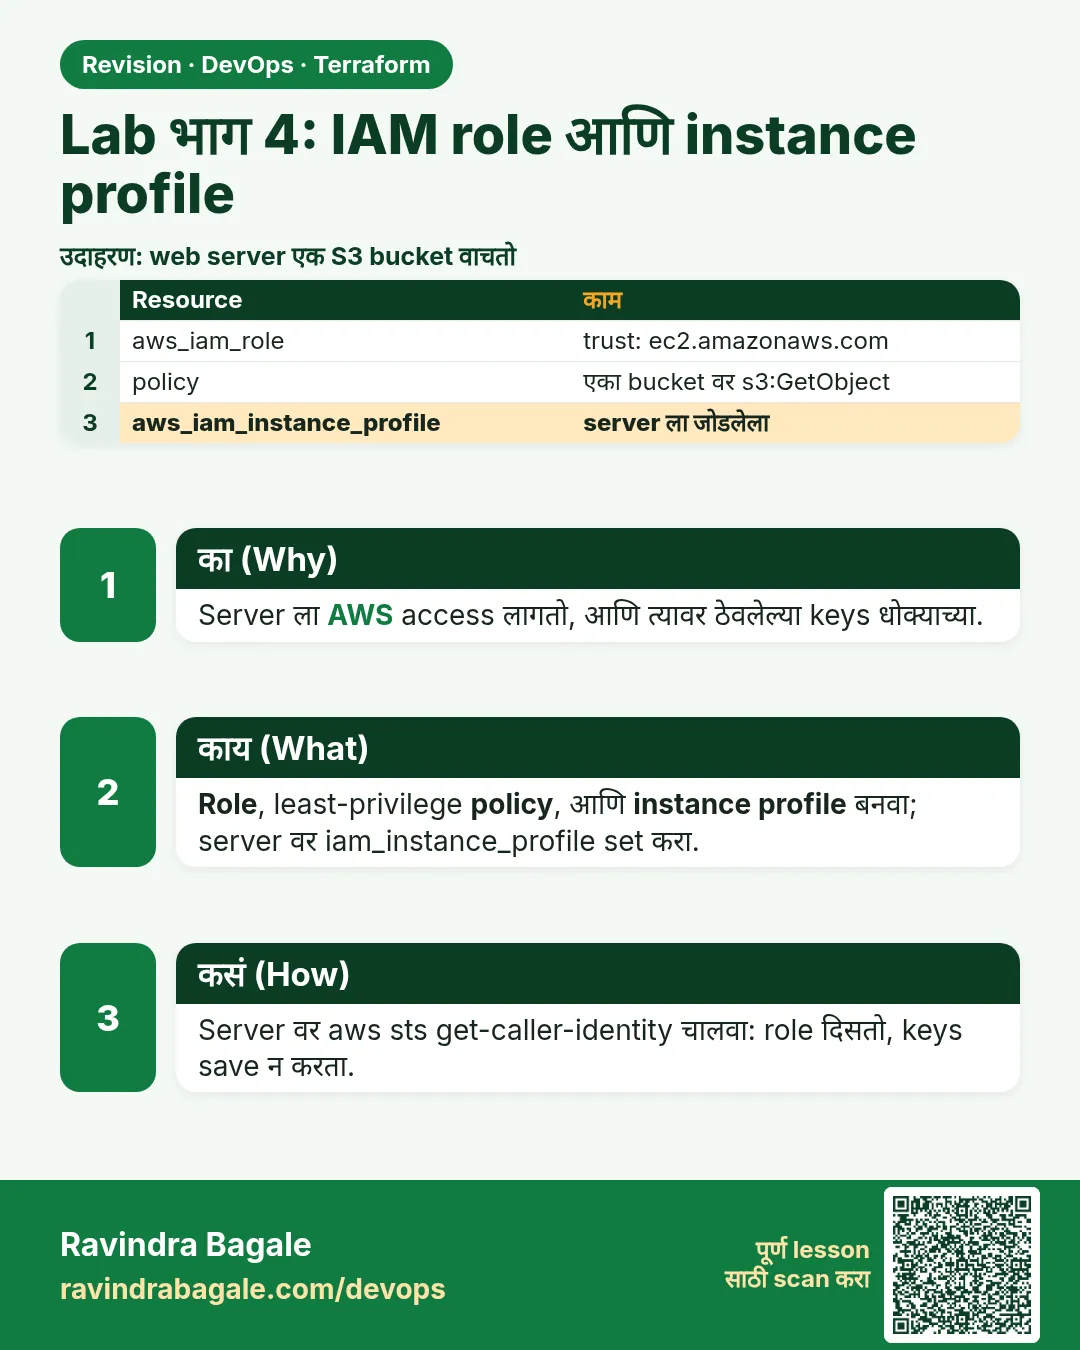 उजळणी (Revision) card 4 of 5: Lab भाग 4: IAM role आणि instance profile · PNG download करा · Card page उघडा
Lesson: 40.4 Lab part 4 — IAM role and instance profile
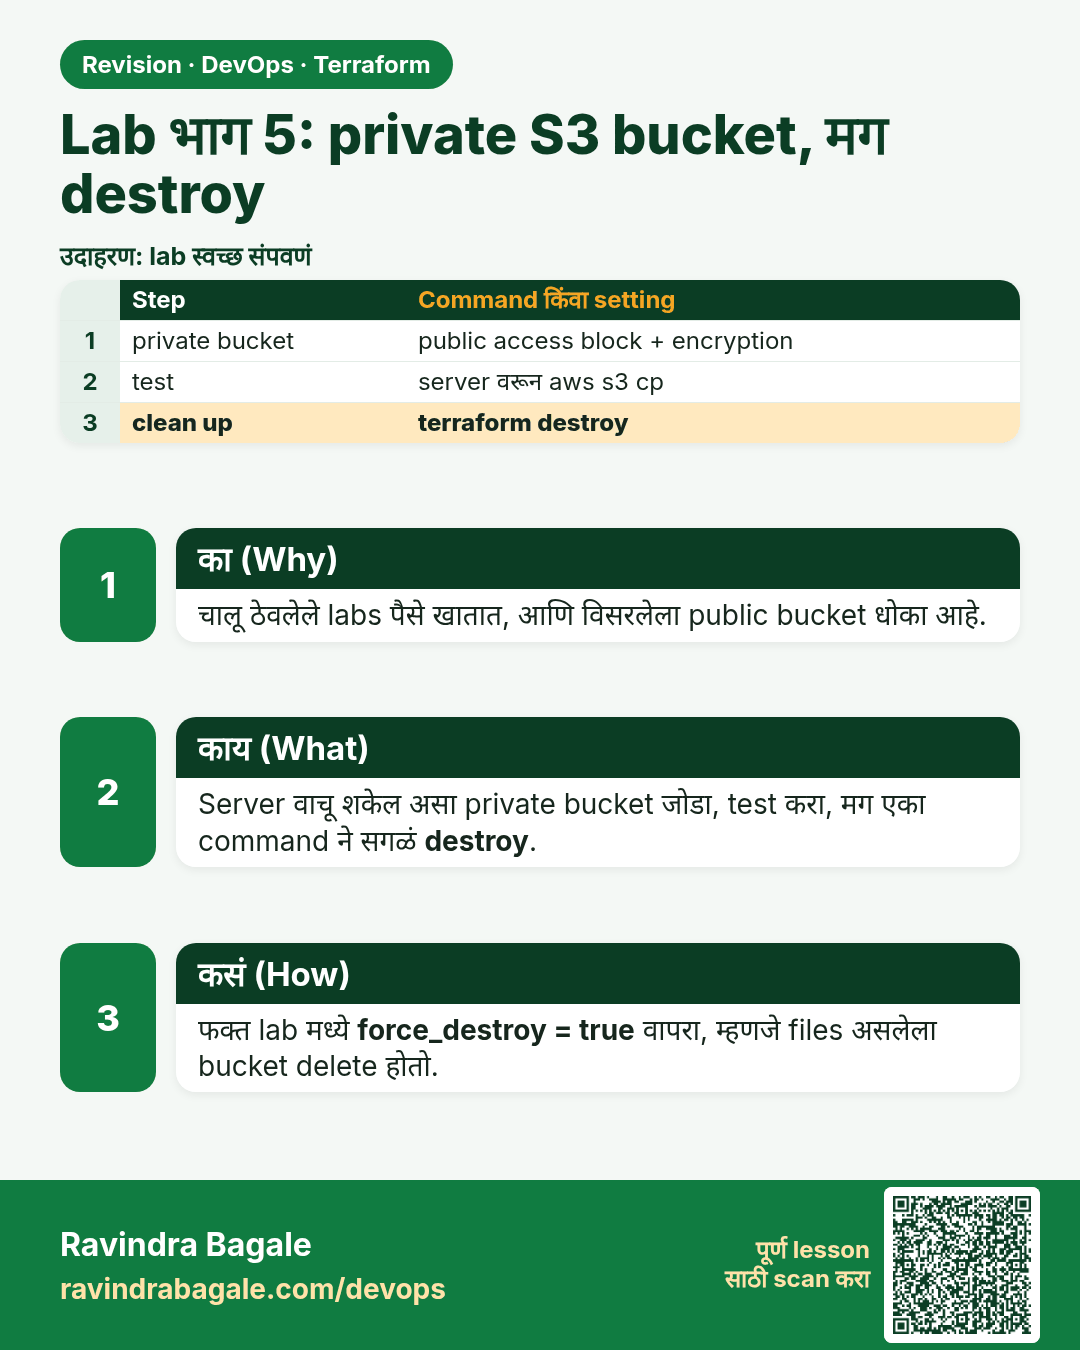
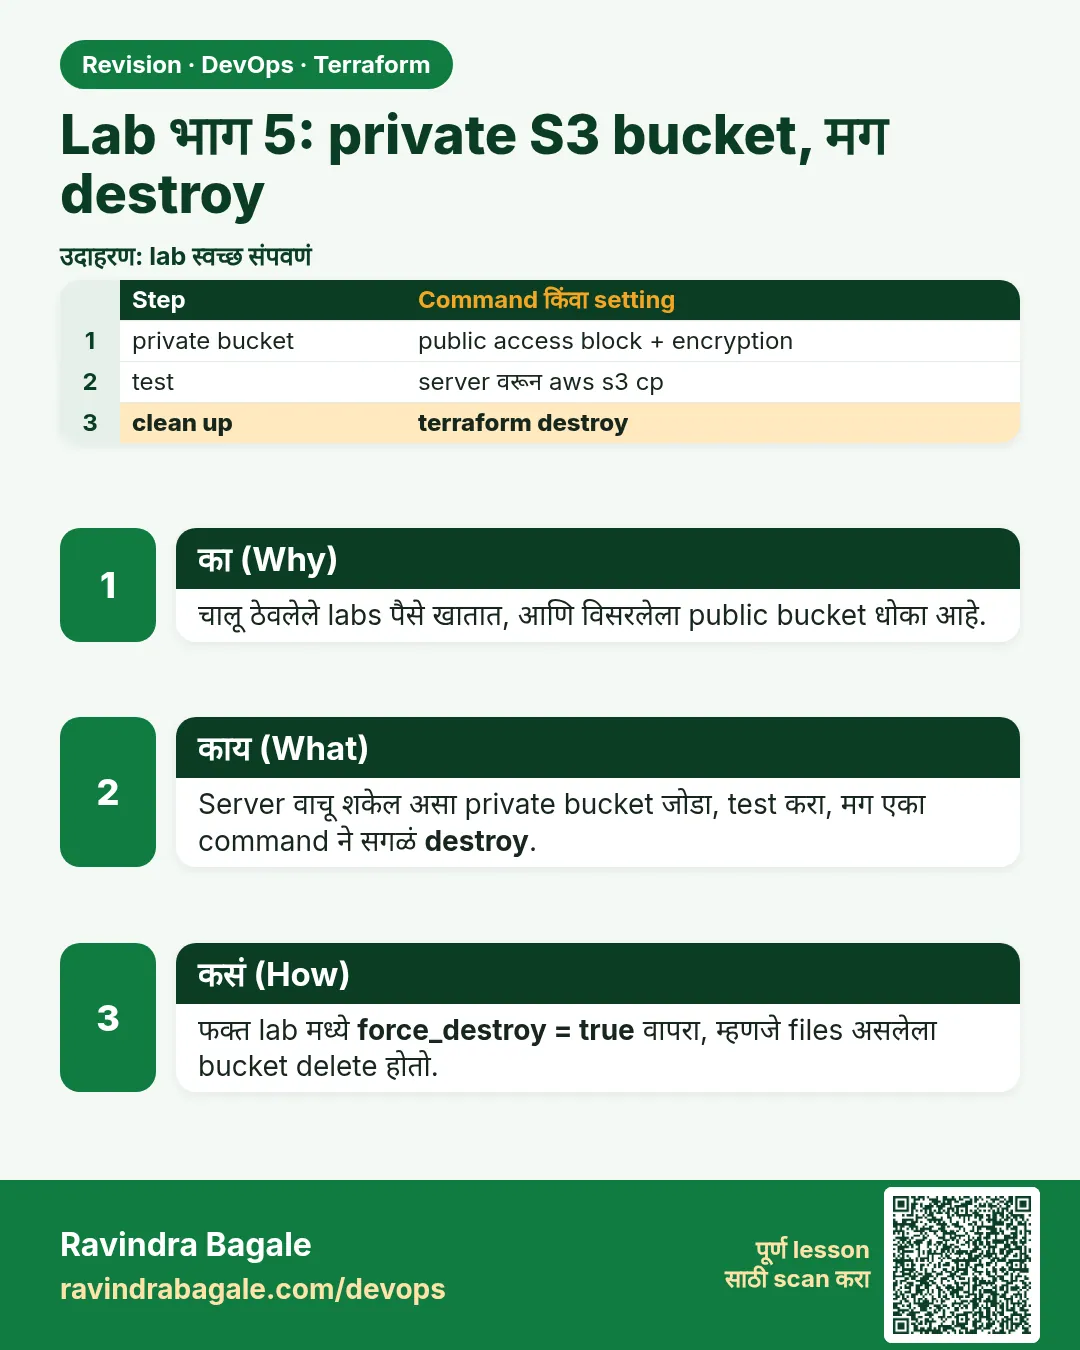 उजळणी (Revision) card 5 of 5: Lab भाग 5: private S3 bucket, मग destroy · PNG download करा · Card page उघडा
Lesson: 40.5 Lab part 5 — a private S3 bucket, then destroy everything
मुलाखत (Interview) cards
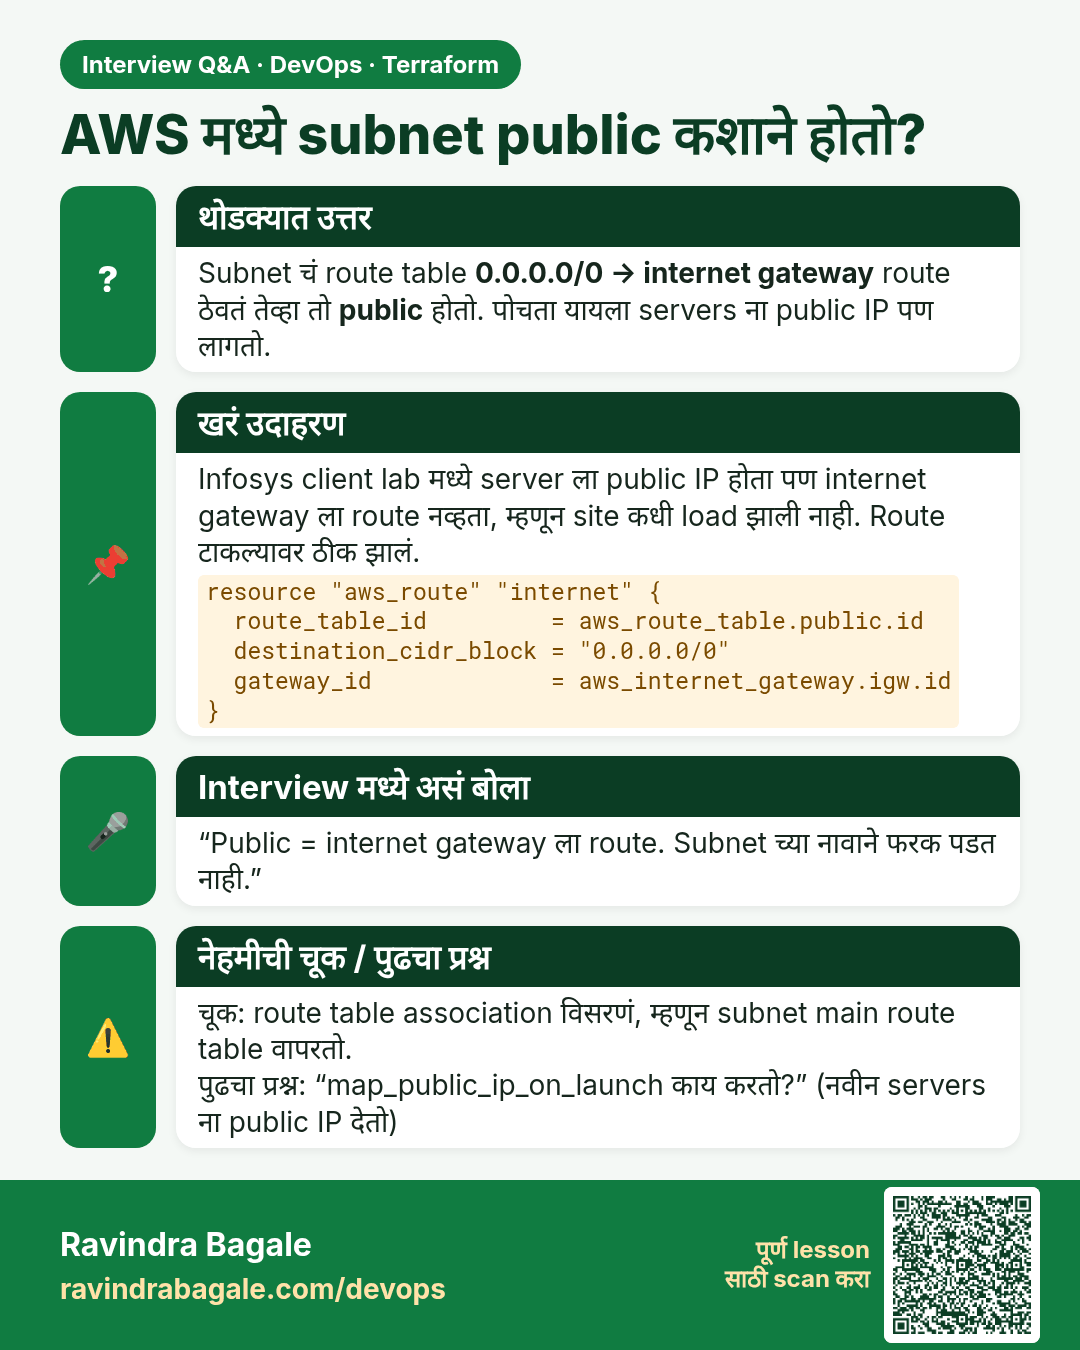
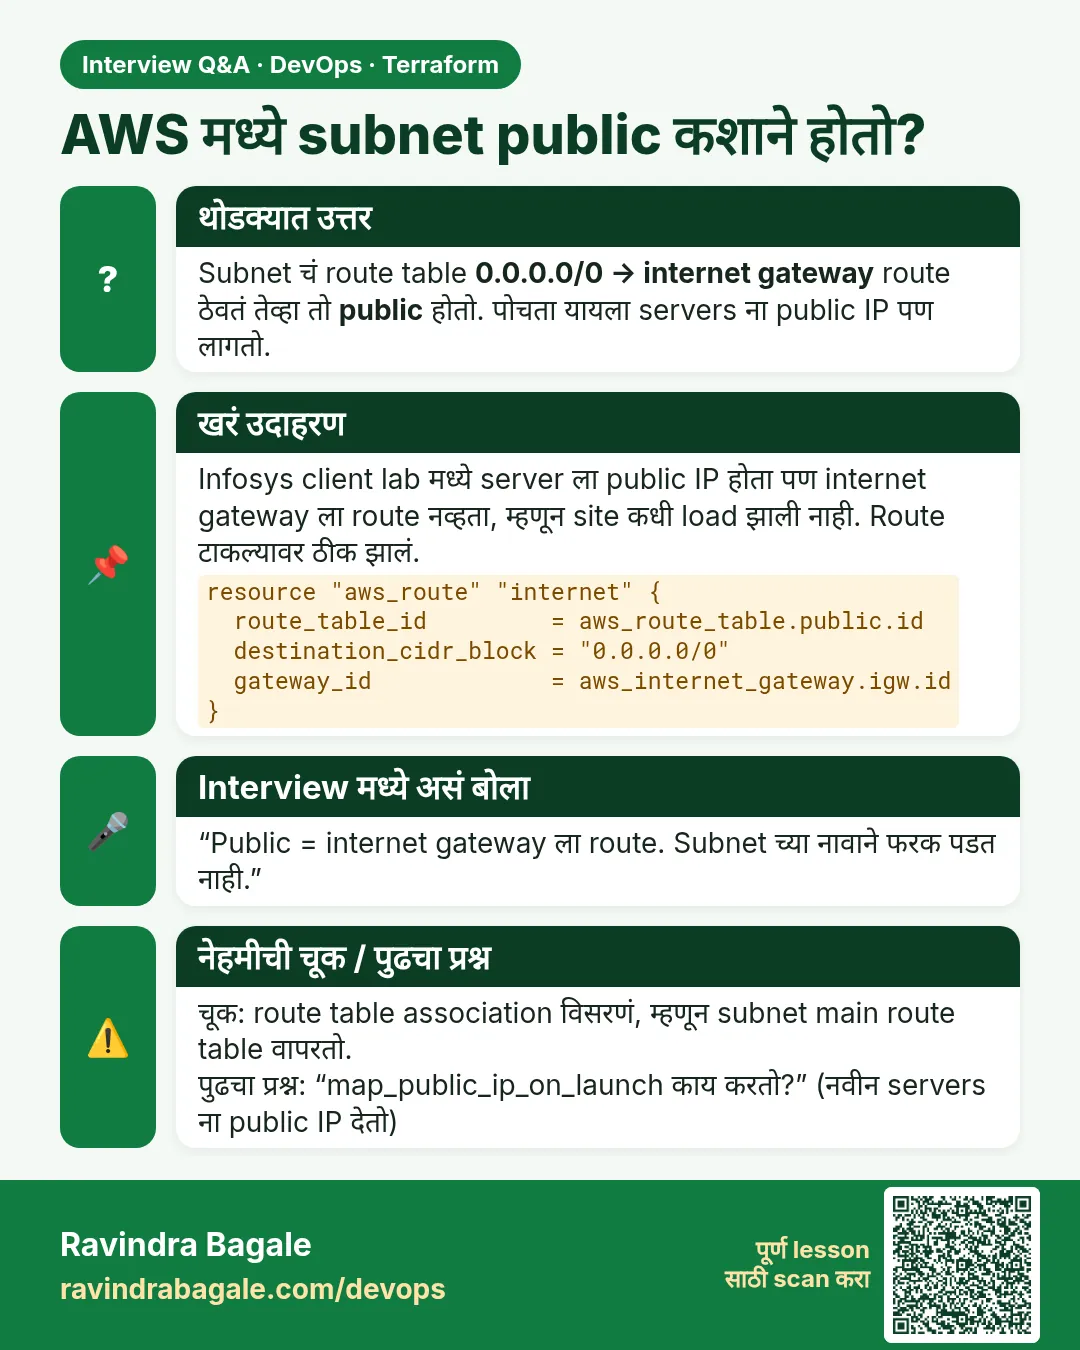 मुलाखत (Interview) card 1 of 5: AWS मध्ये subnet public कशाने होतो? · PNG download करा · Card page उघडा
Lesson: 40.1 Lab part 1 — VPC, public subnets, internet gateway and routes
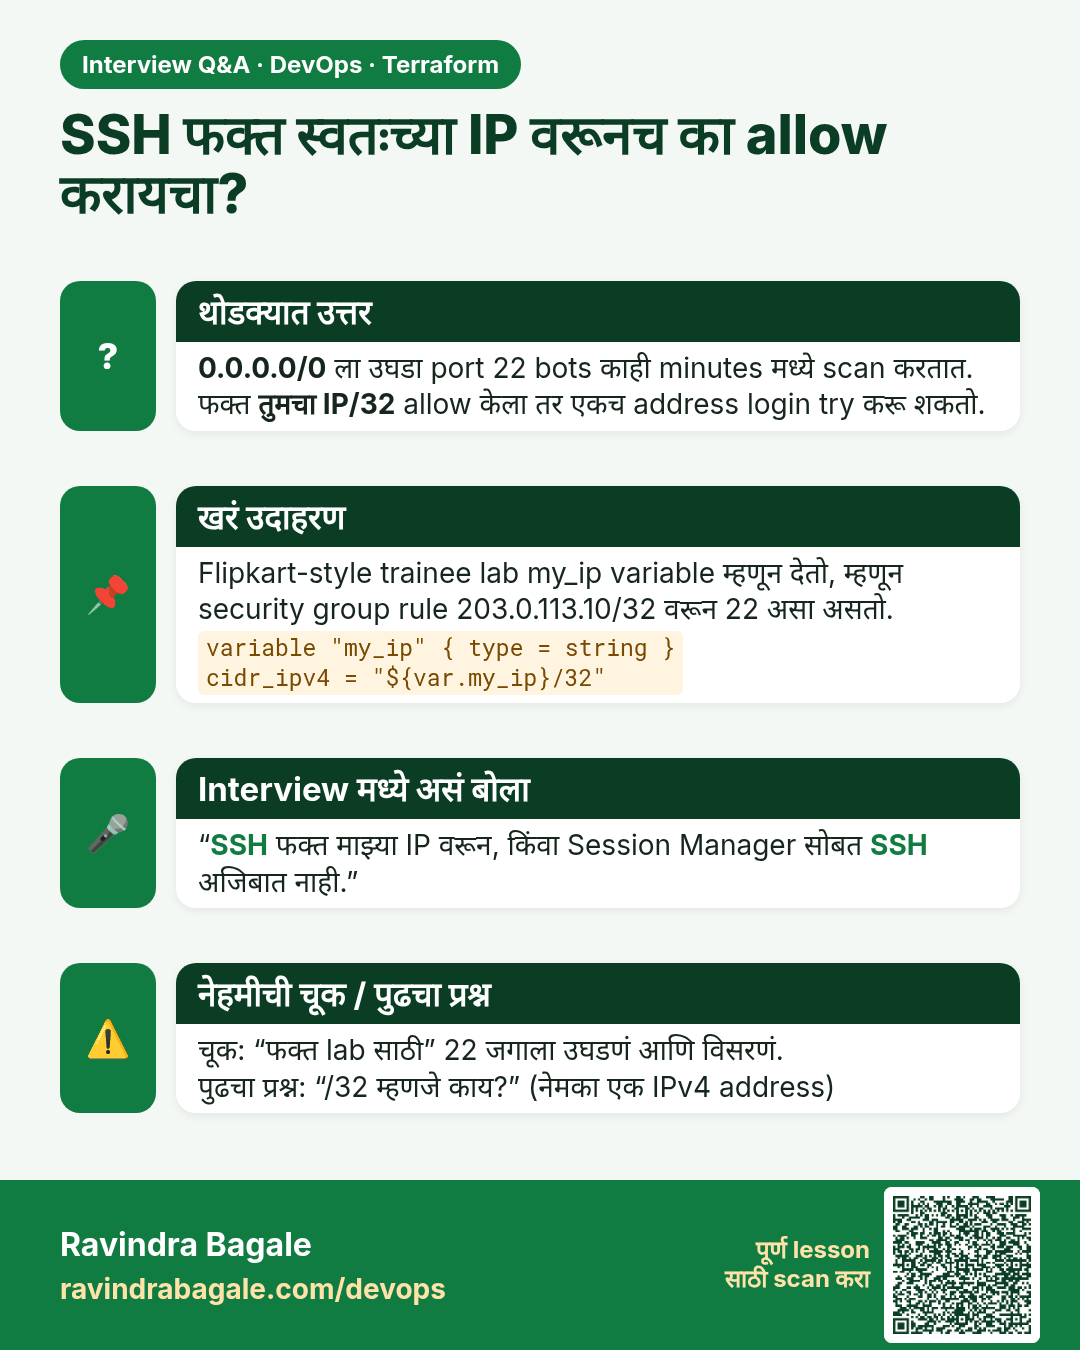
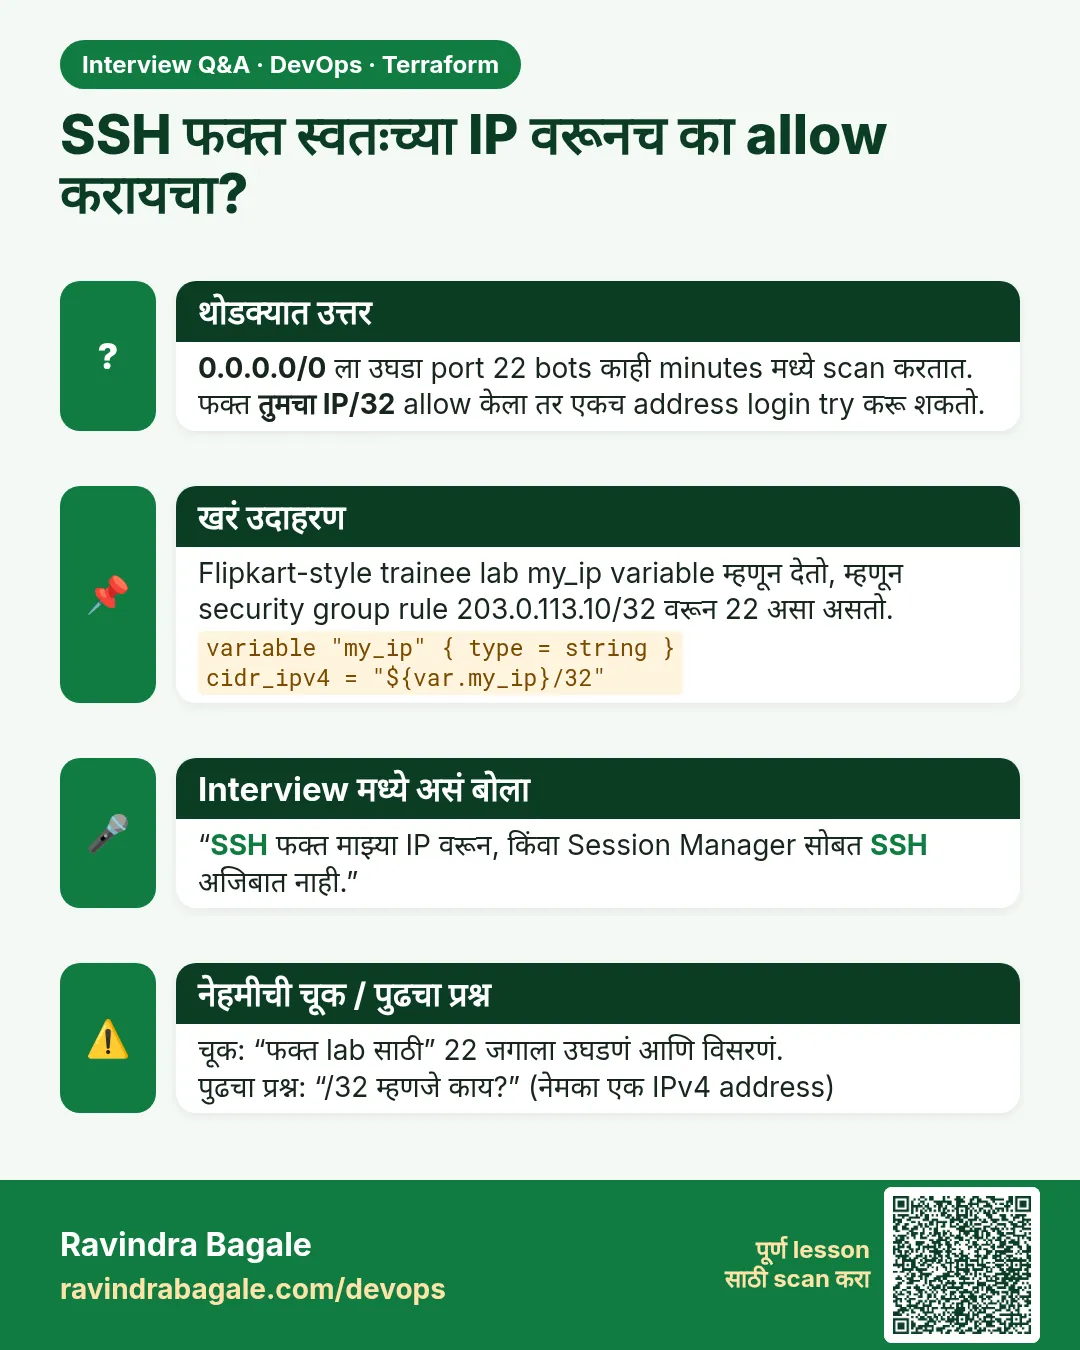 मुलाखत (Interview) card 2 of 5: SSH फक्त स्वतःच्या IP वरूनच का allow करायचा? · PNG download करा · Card page उघडा
Lesson: 40.2 Lab part 2 — security group for the web server
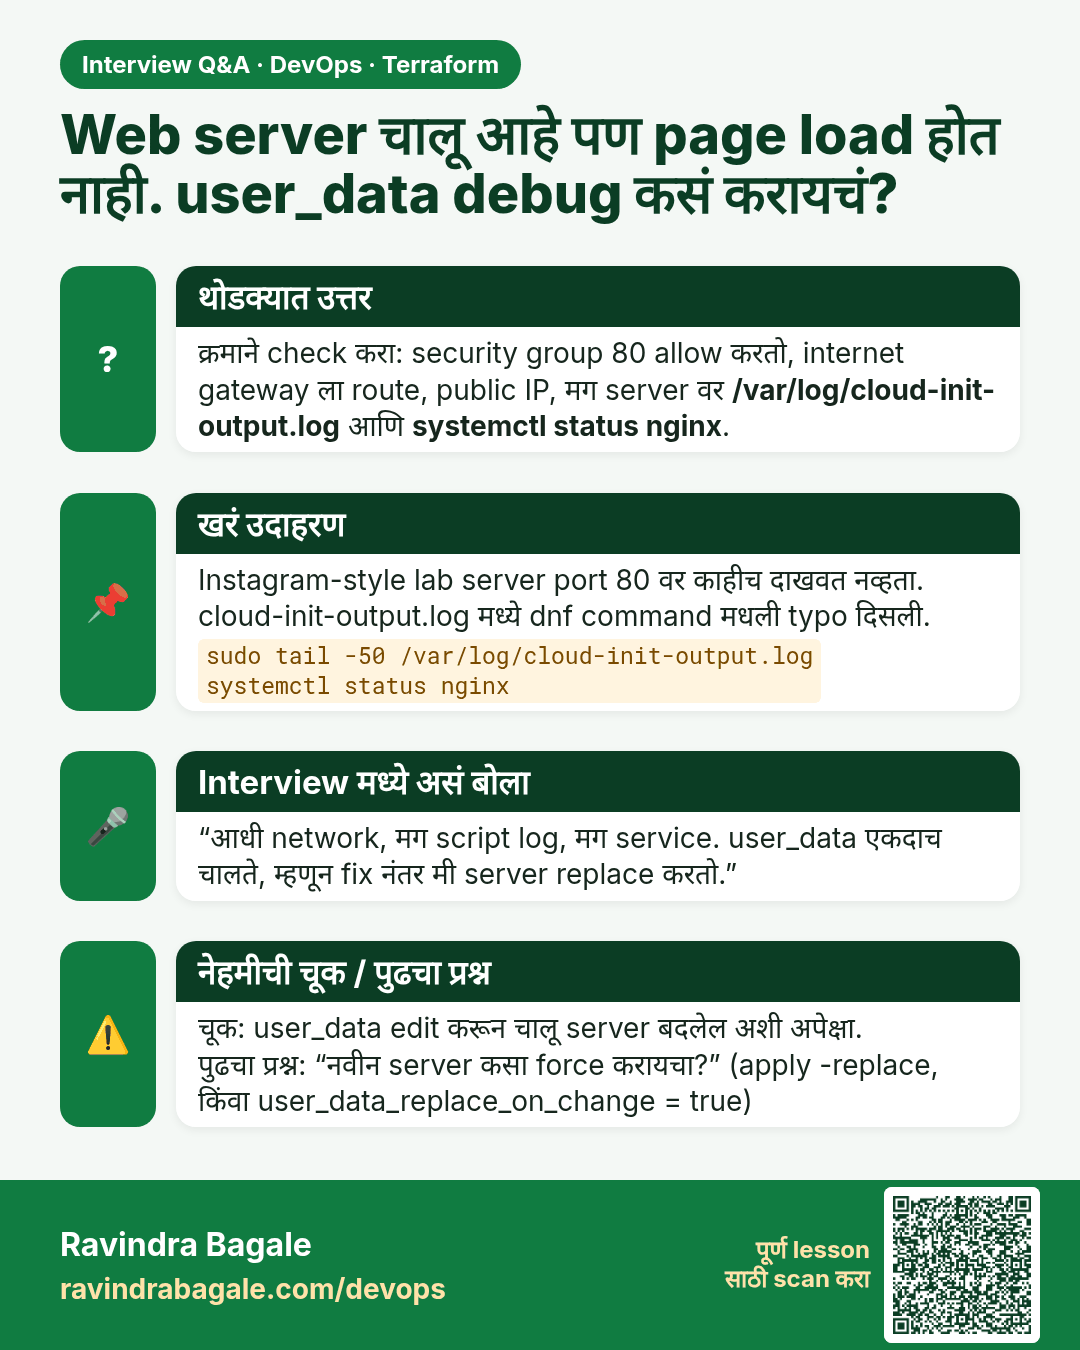
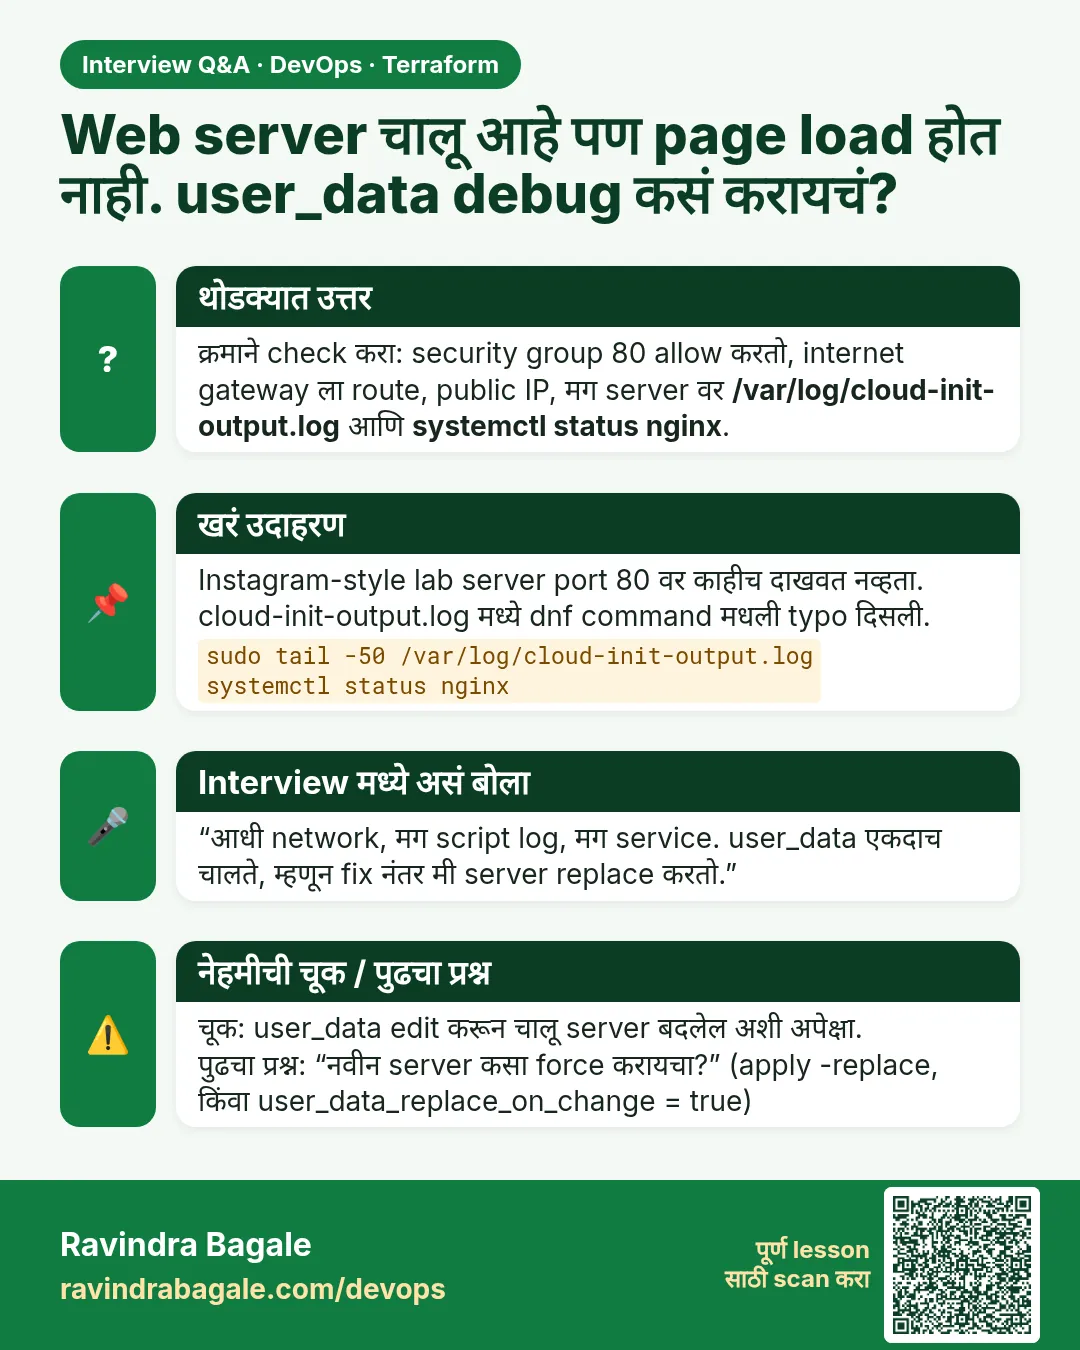 मुलाखत (Interview) card 3 of 5: Web server चालू आहे पण page load होत नाही. user_data debug कसं करायचं? · PNG download करा · Card page उघडा
Lesson: 40.3 Lab part 3 — EC2 with nginx from user_data
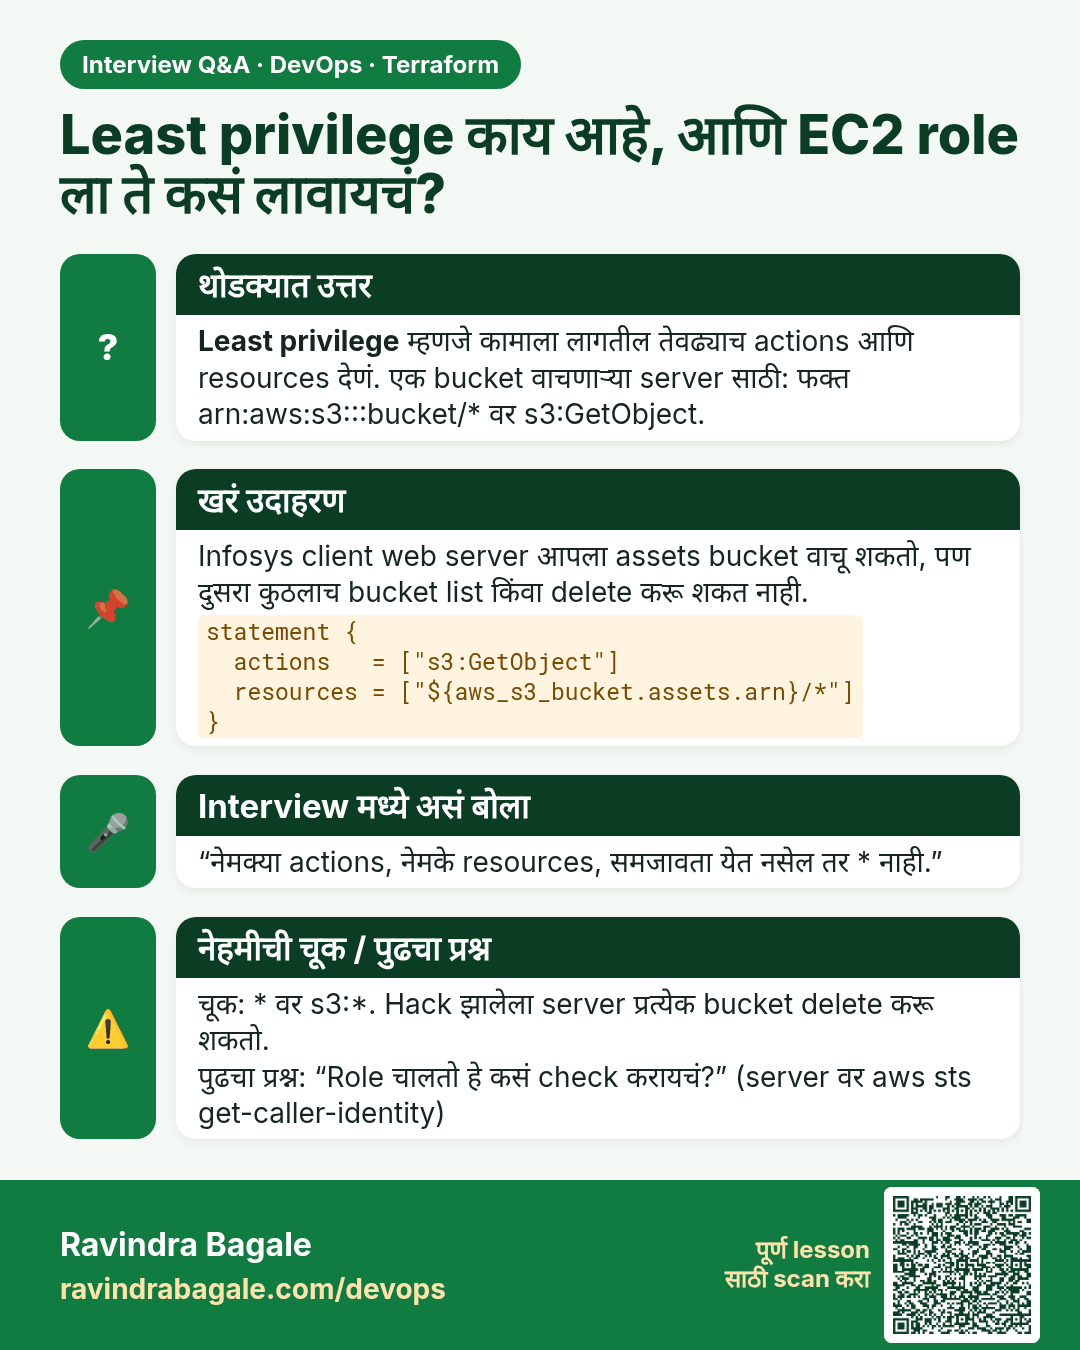
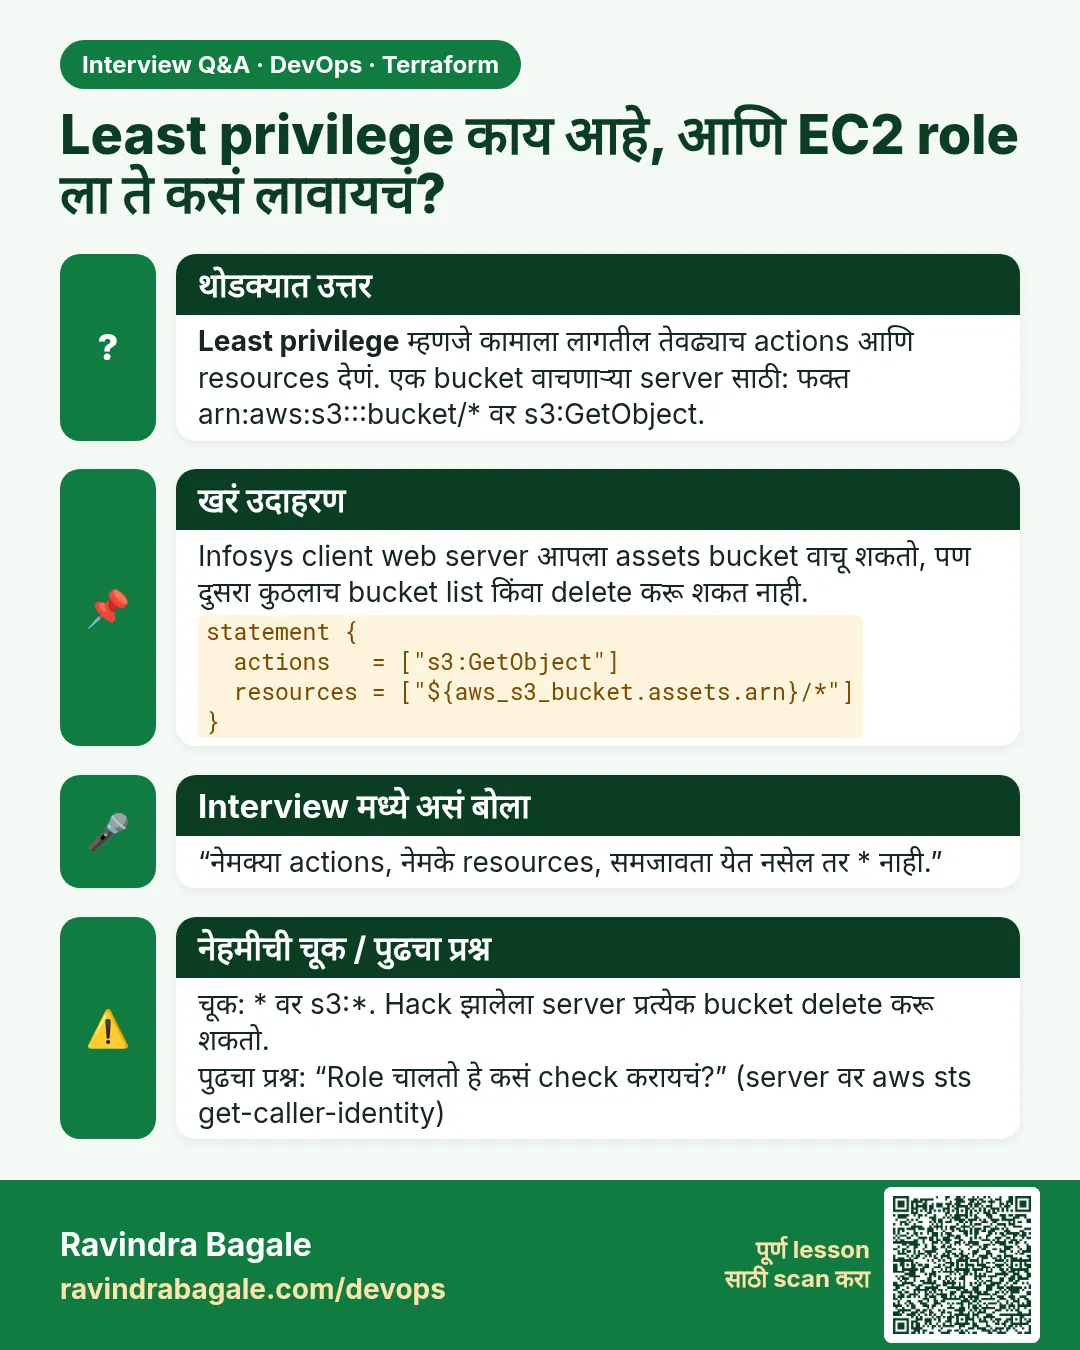 मुलाखत (Interview) card 4 of 5: Least privilege काय आहे, आणि EC2 role ला ते कसं लावायचं? · PNG download करा · Card page उघडा
Lesson: 40.4 Lab part 4 — IAM role and instance profile
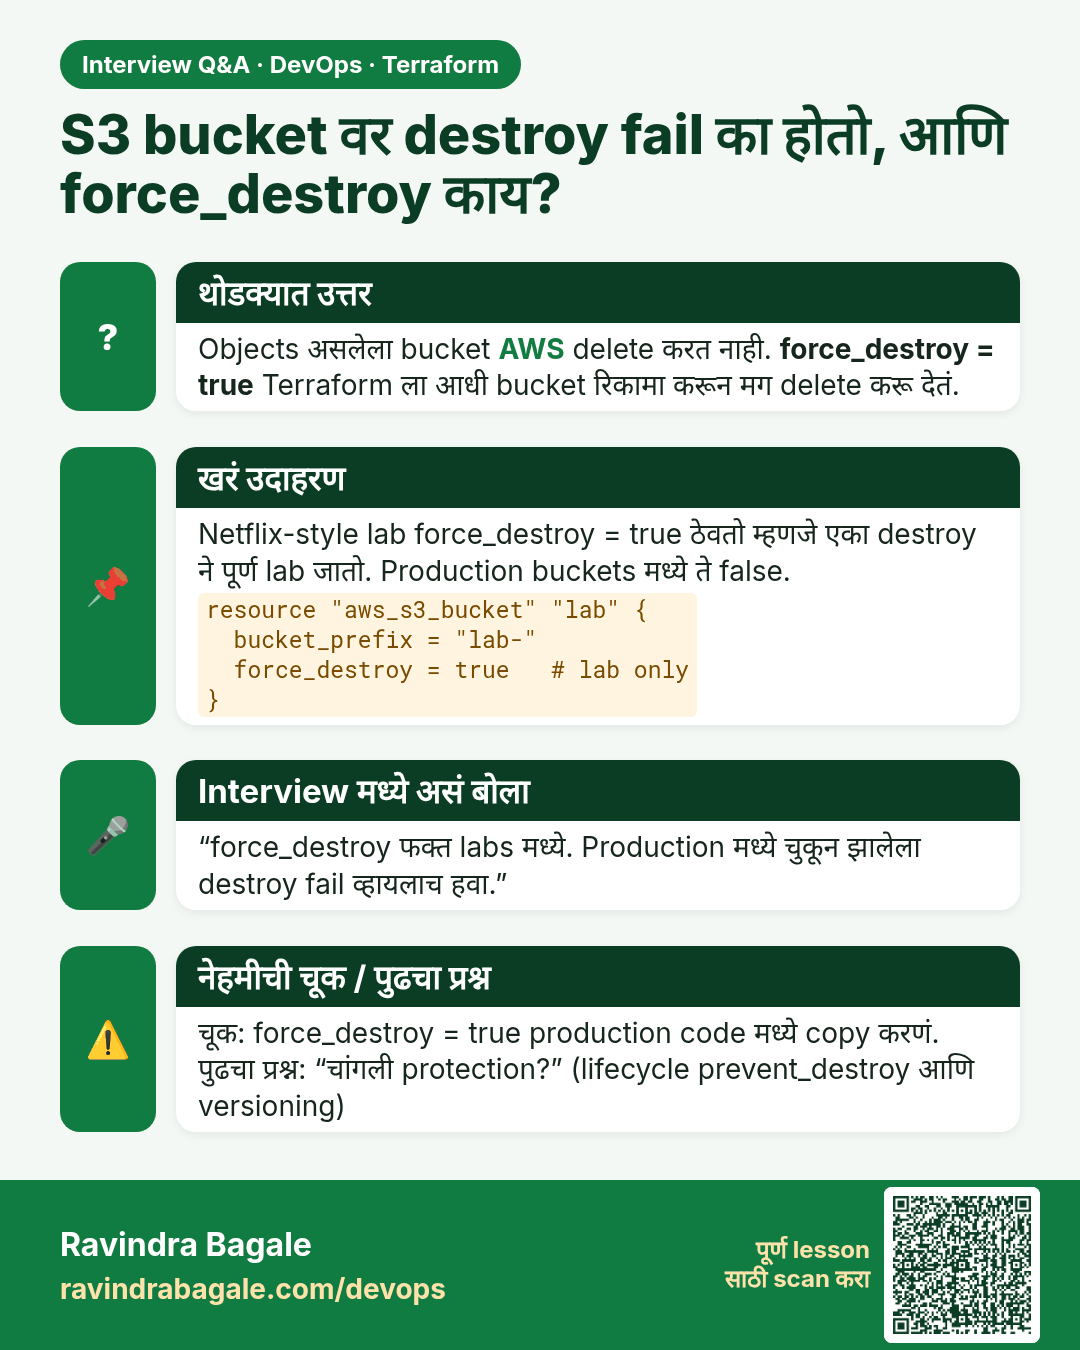
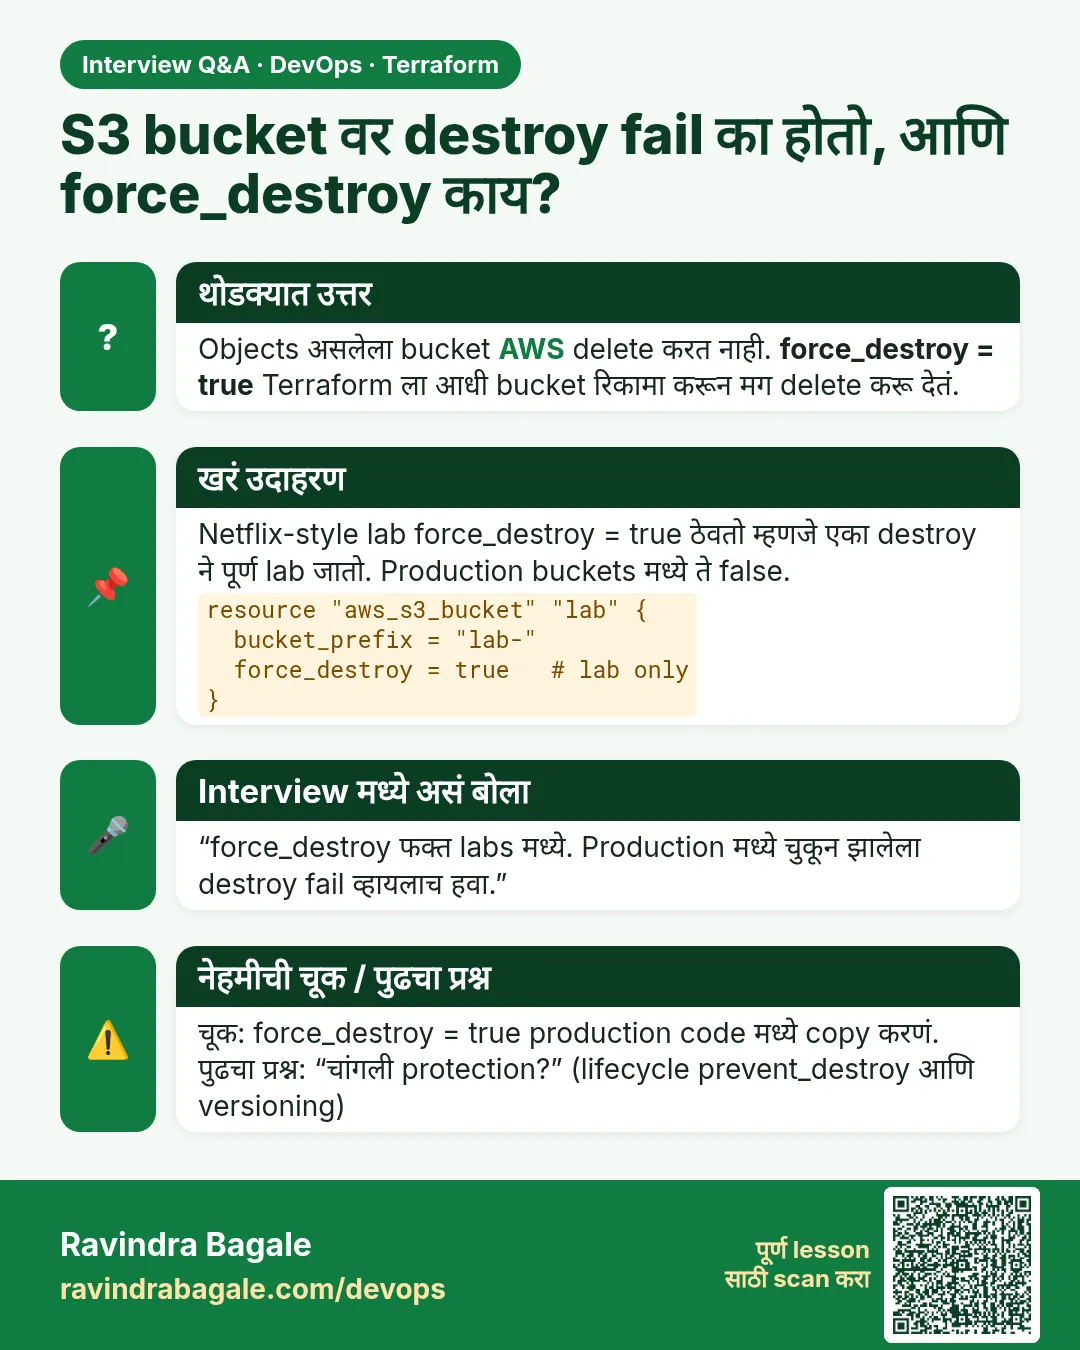 मुलाखत (Interview) card 5 of 5: S3 bucket वर destroy fail का होतो, आणि force_destroy काय? · PNG download करा · Card page उघडा
Lesson: 40.5 Lab part 5 — a private S3 bucket, then destroy everything
तुलना (Comparison) cards
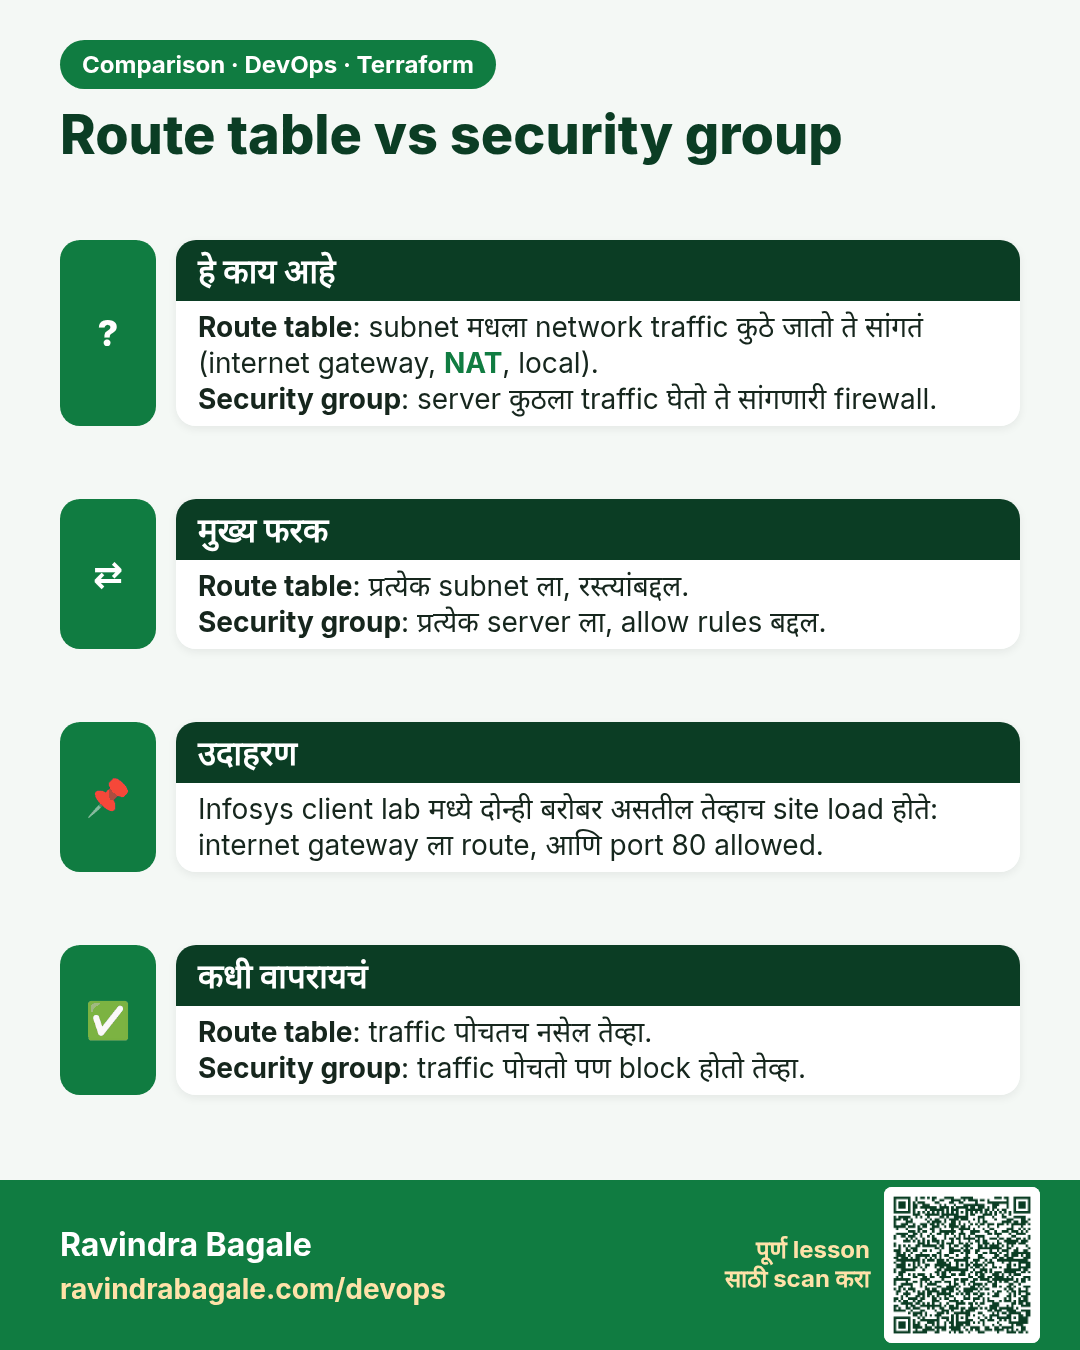
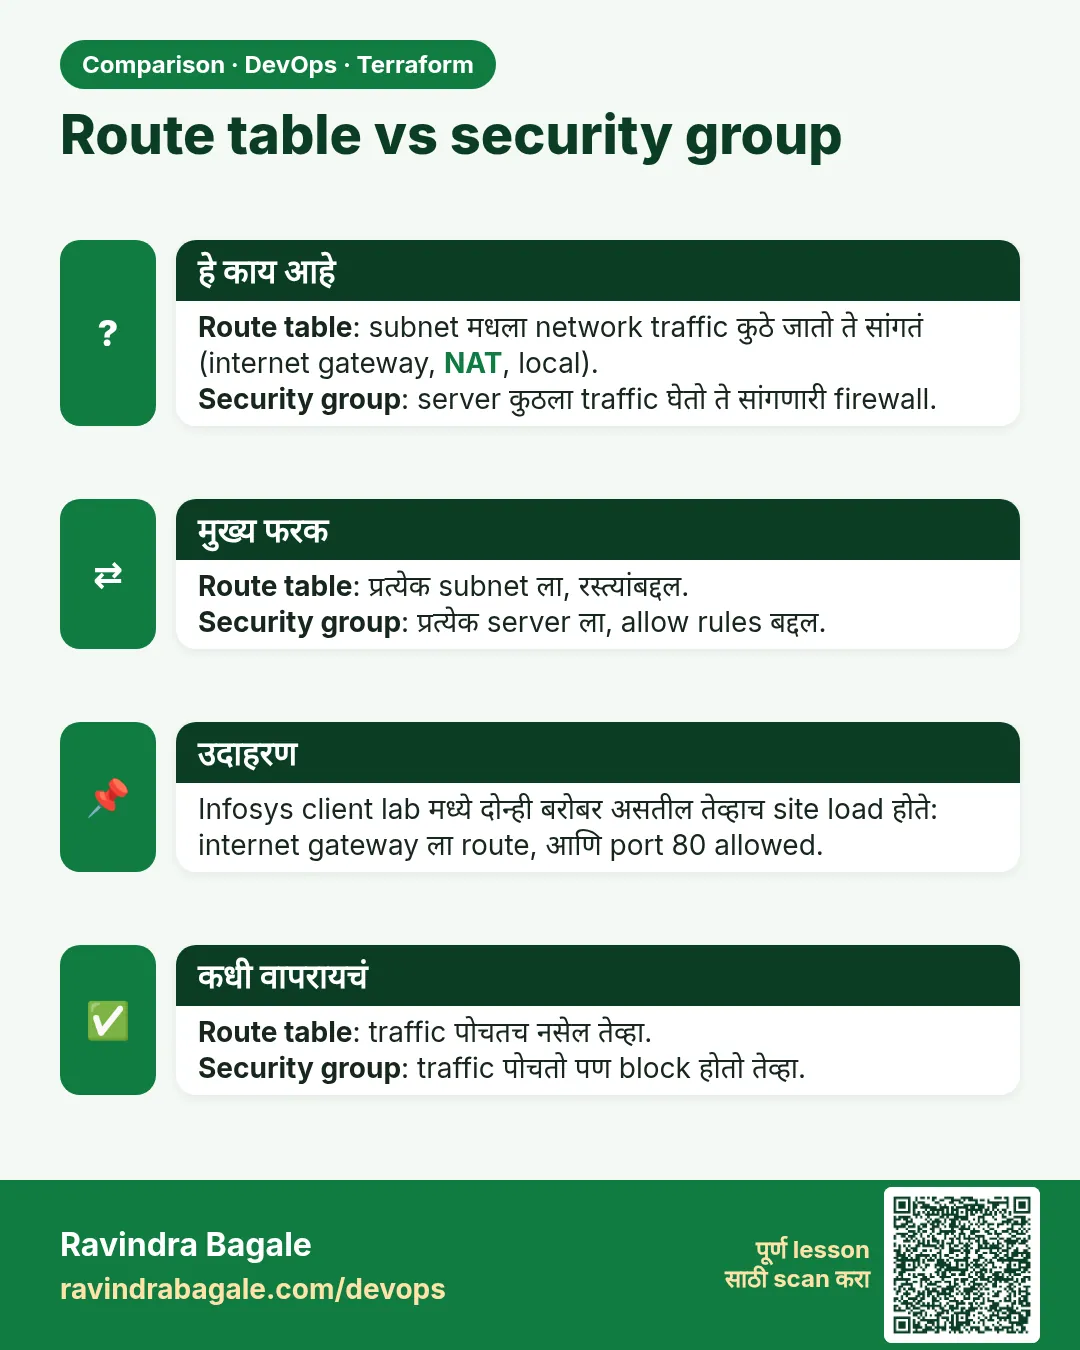 तुलना (Comparison) card 1 of 3: Route table vs security group · PNG download करा · Card page उघडा
Lesson: Chapter 40: Terraform Real AWS Labs VPC EC2 nginx S3 and IAM Role
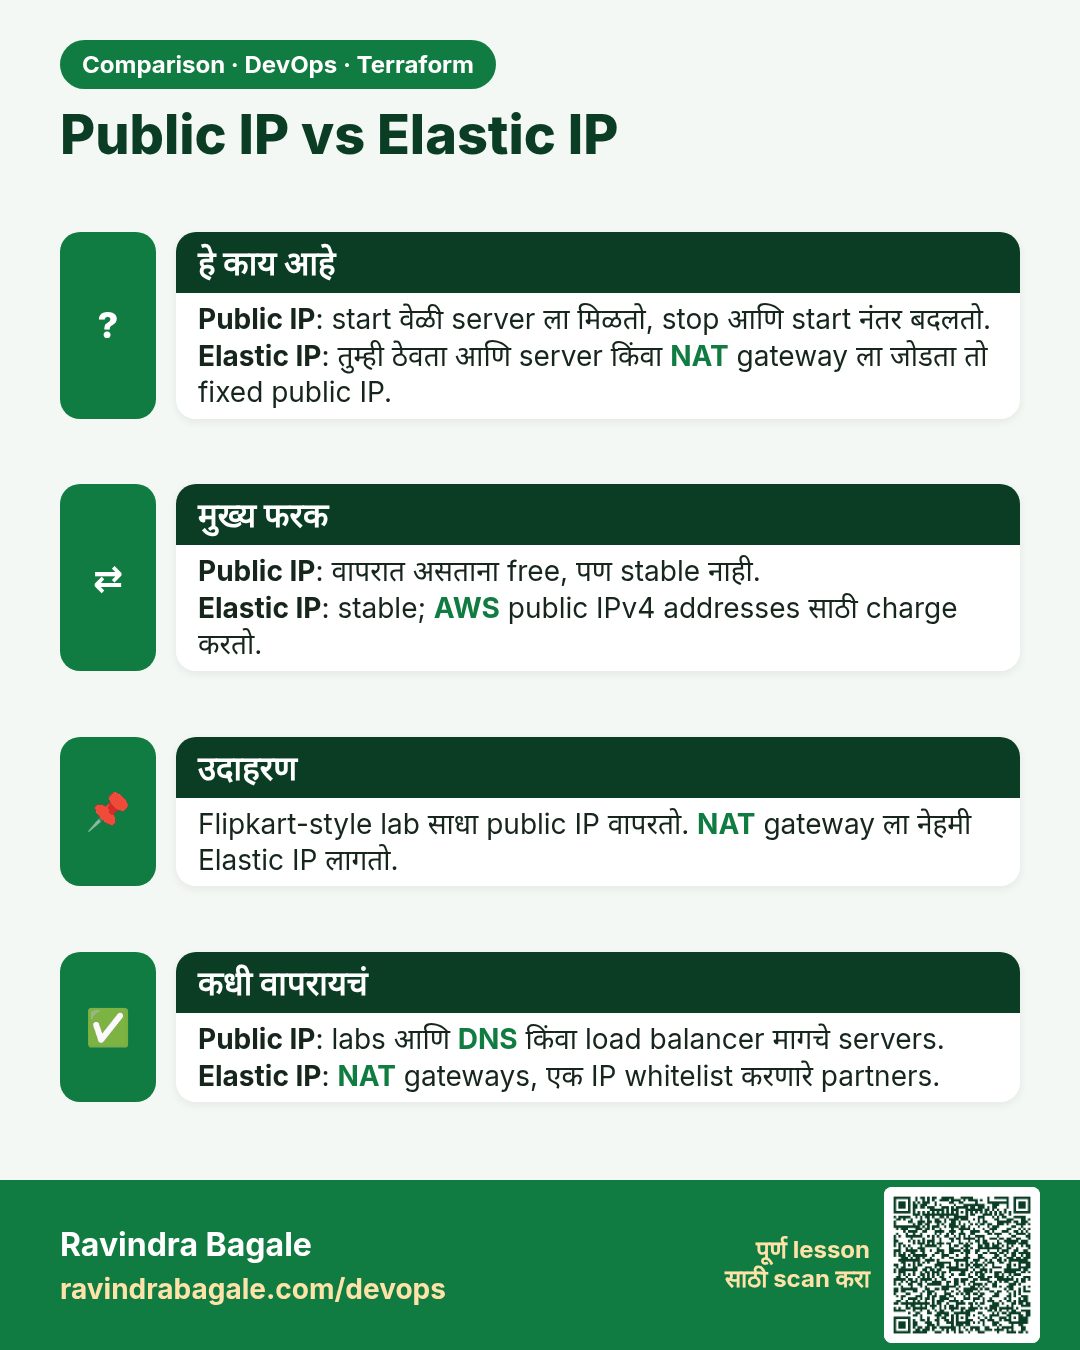
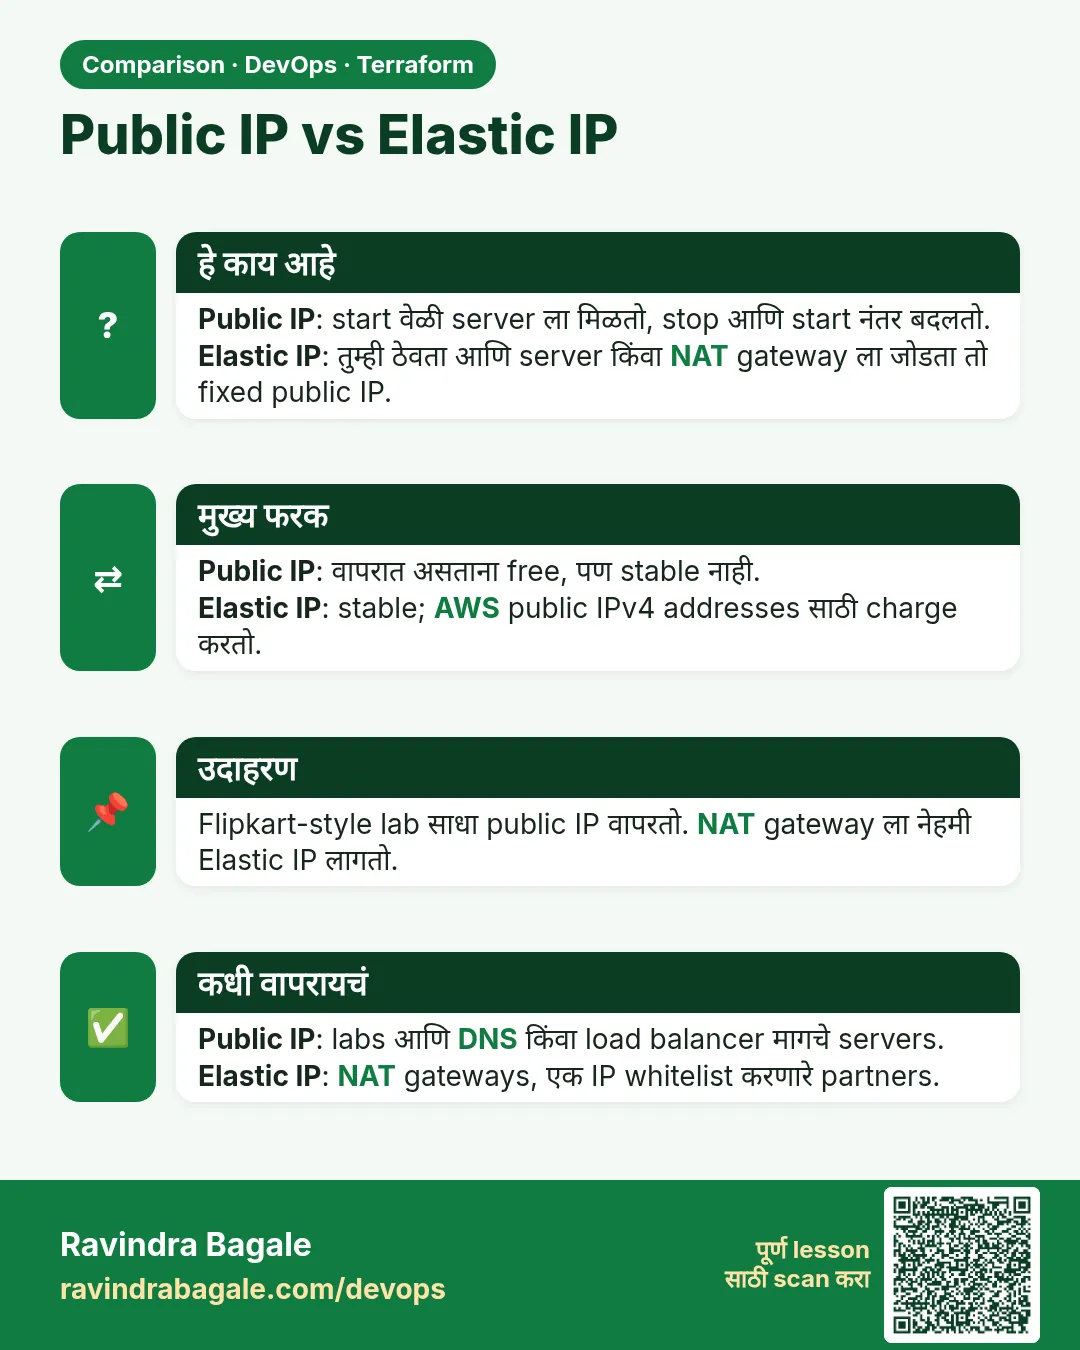 तुलना (Comparison) card 2 of 3: Public IP vs Elastic IP · PNG download करा · Card page उघडा
Lesson: Chapter 40: Terraform Real AWS Labs VPC EC2 nginx S3 and IAM Role
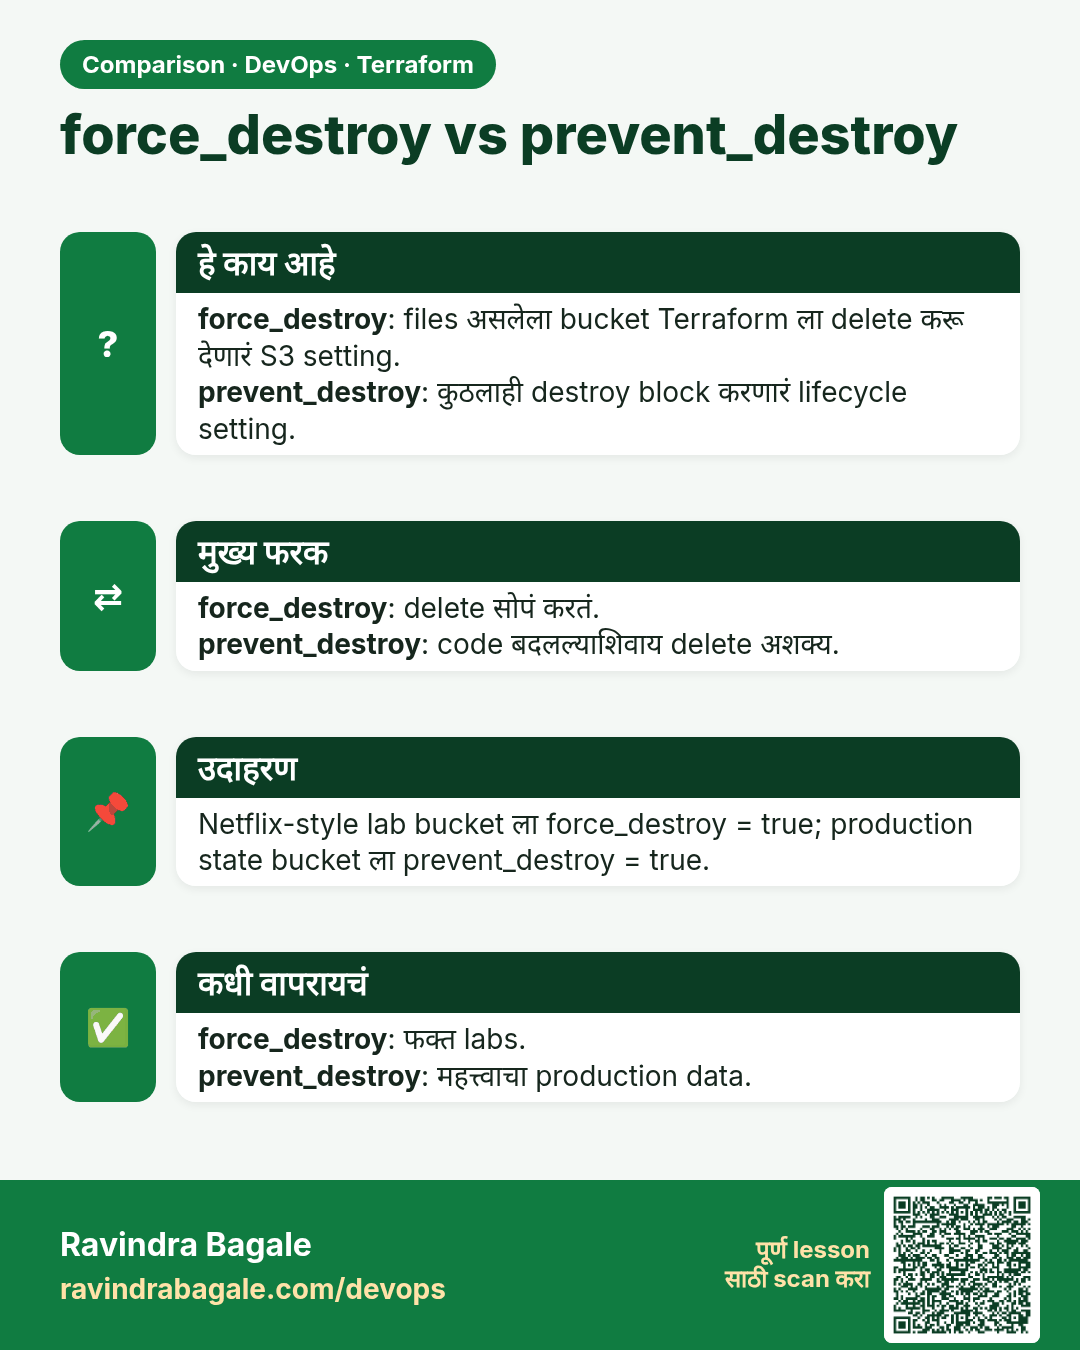
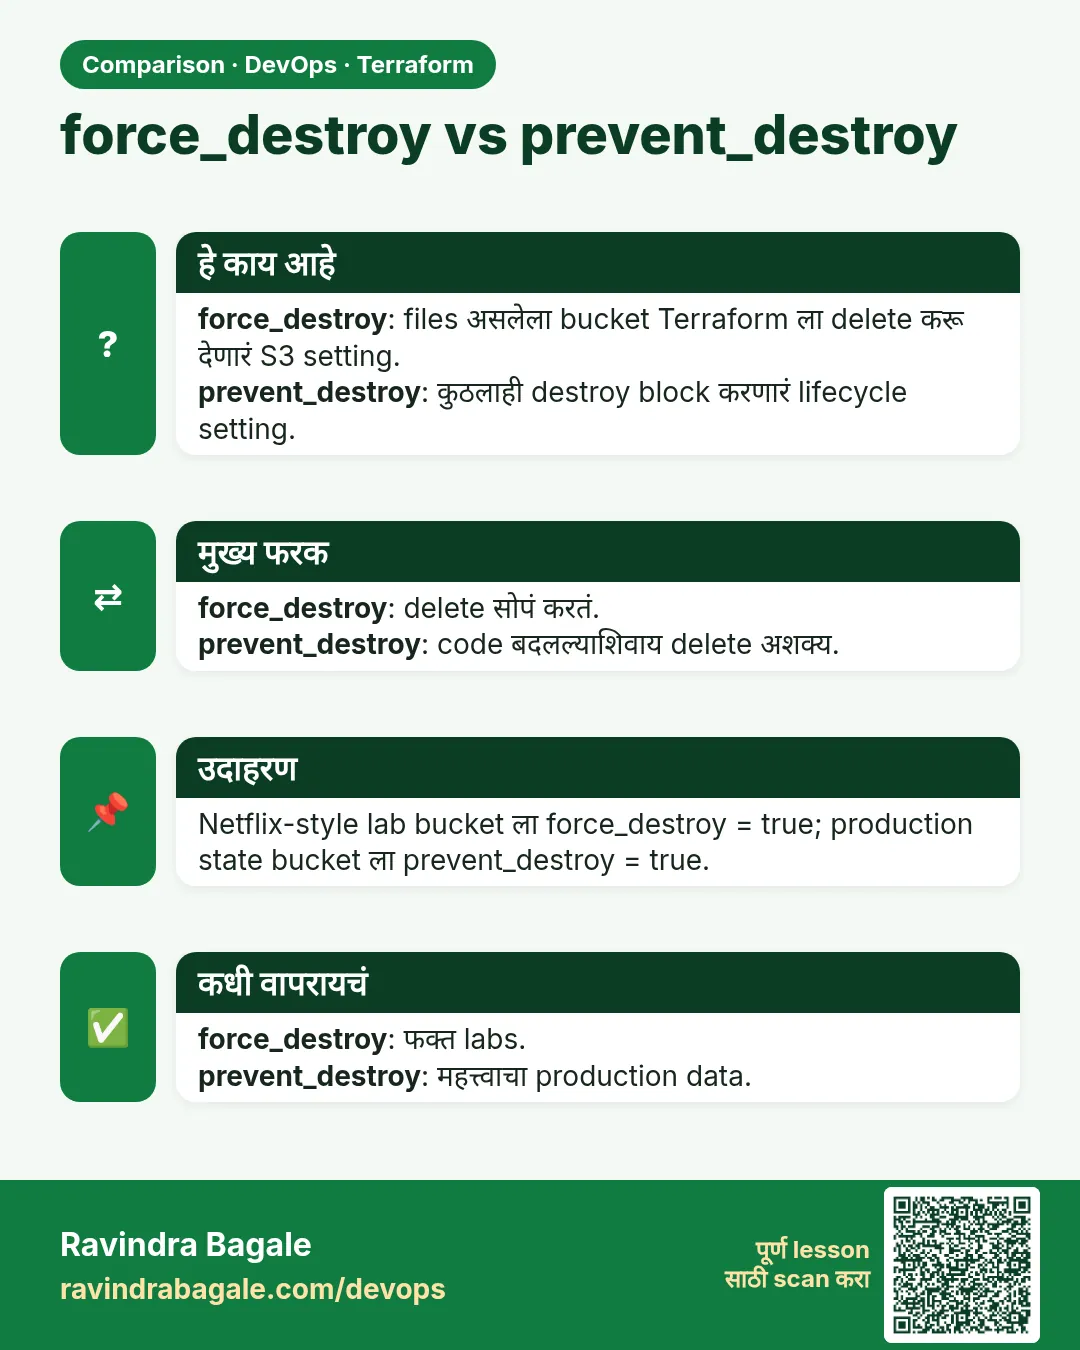 तुलना (Comparison) card 3 of 3: force_destroy vs prevent_destroy · PNG download करा · Card page उघडा
Lesson: Chapter 40: Terraform Real AWS Labs VPC EC2 nginx S3 and IAM Role