Ravi Sir's Cards › DevOps
Chapter 40: Terraform Real AWS Labs VPC EC2 nginx S3 and IAM Role: Cards
मराठी cards · Open the chapter
Revision cards
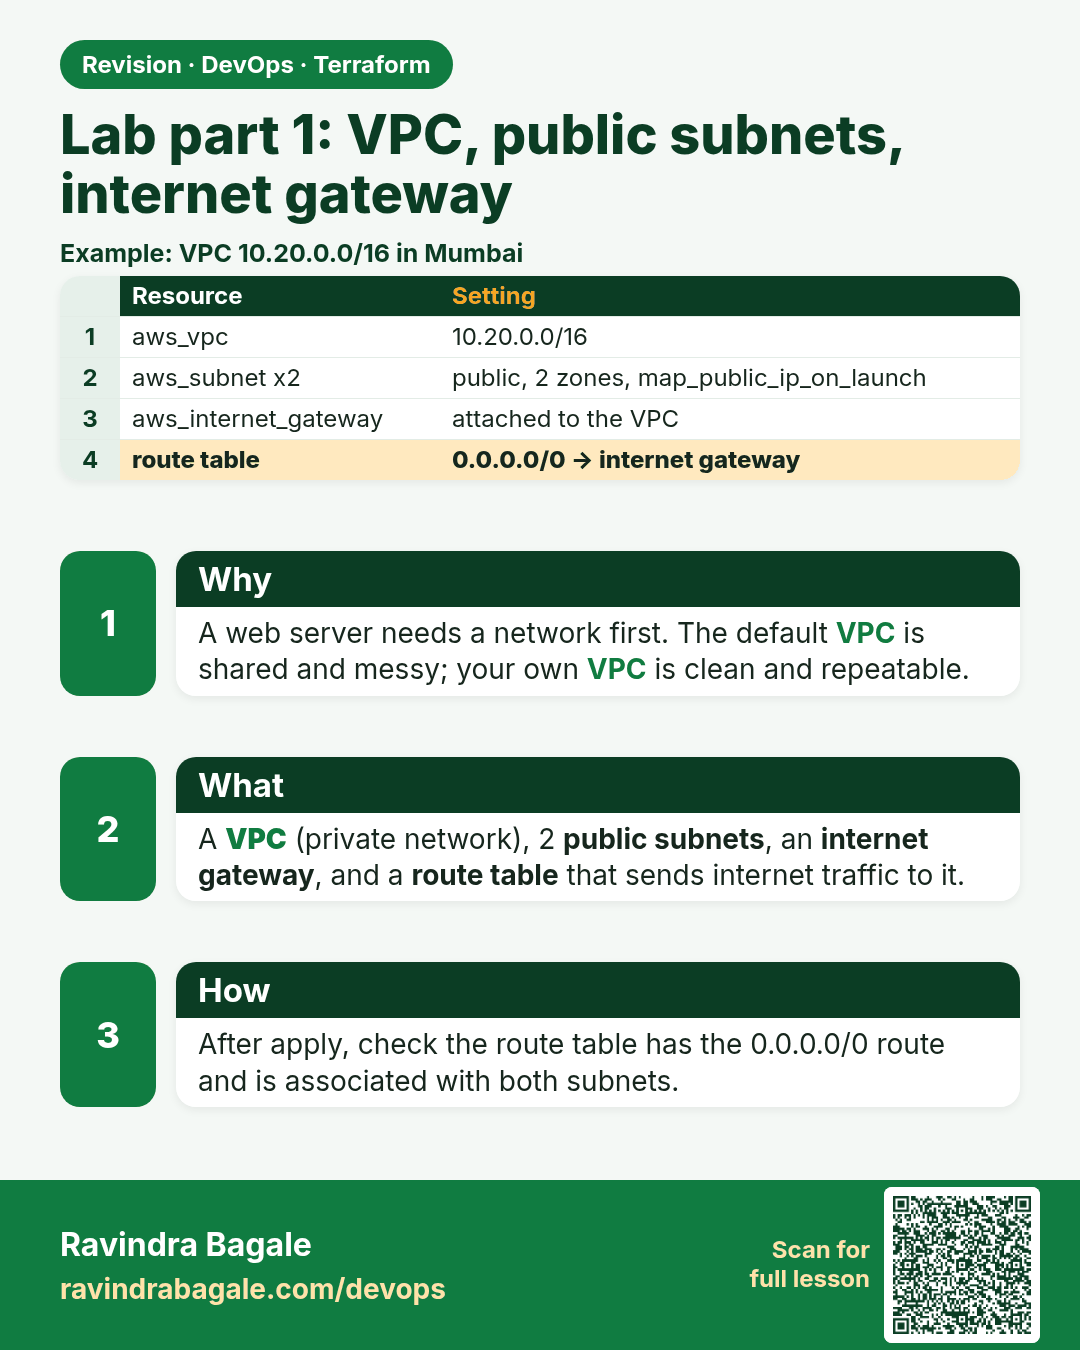
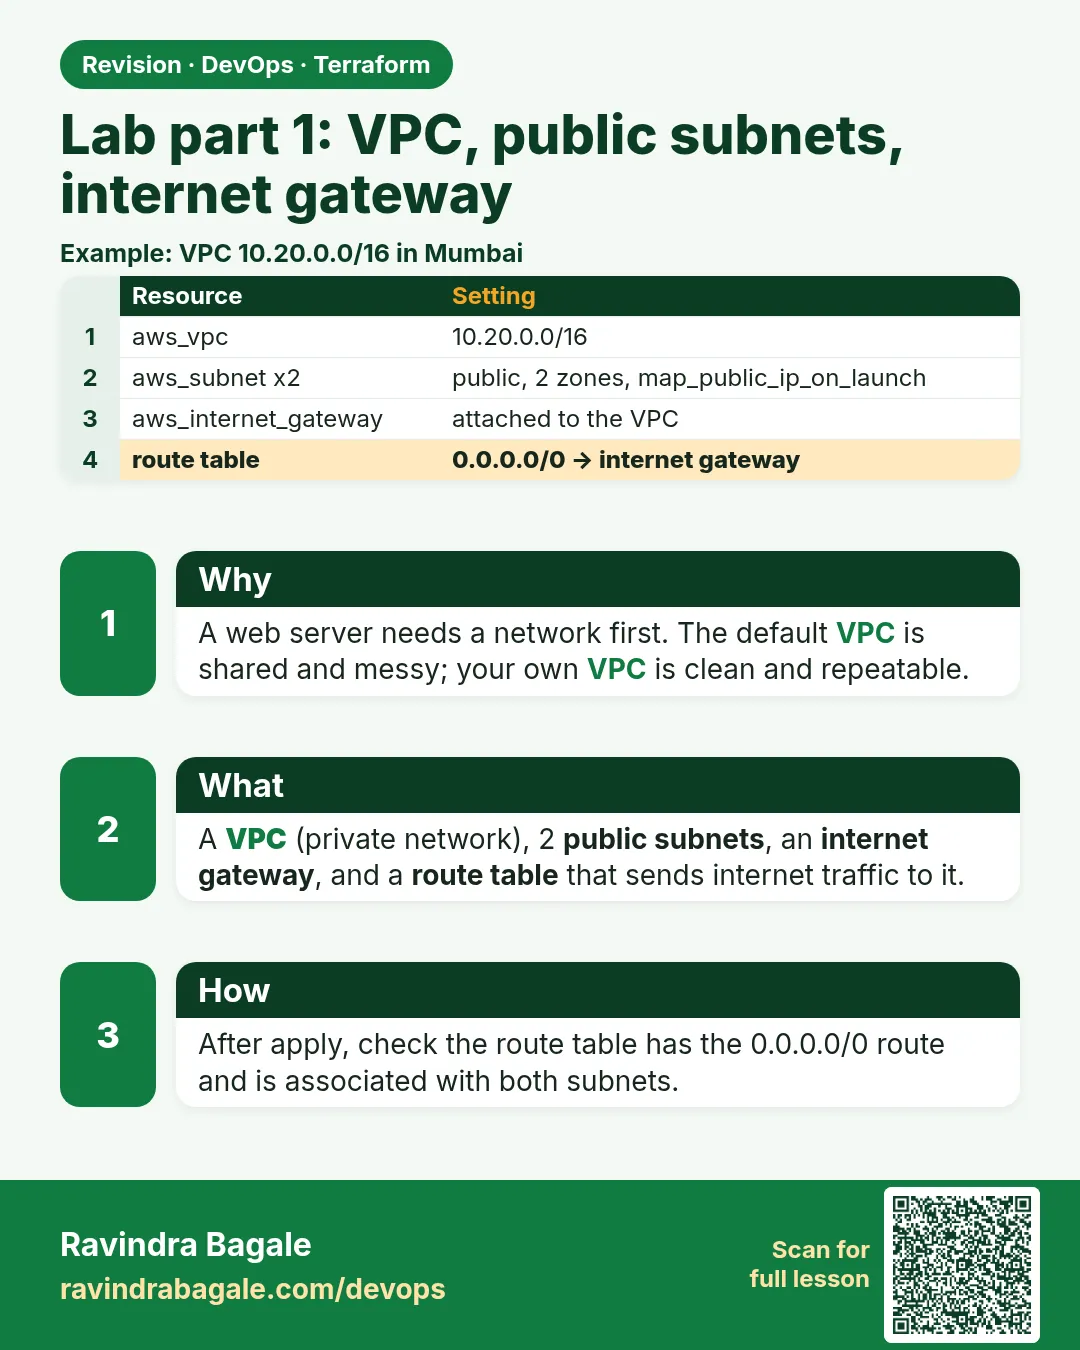 Revision card 1 of 5: Lab part 1: VPC, public subnets, internet gateway · Download PNG · Open card page
Lesson: 40.1 Lab part 1 — VPC, public subnets, internet gateway and routes
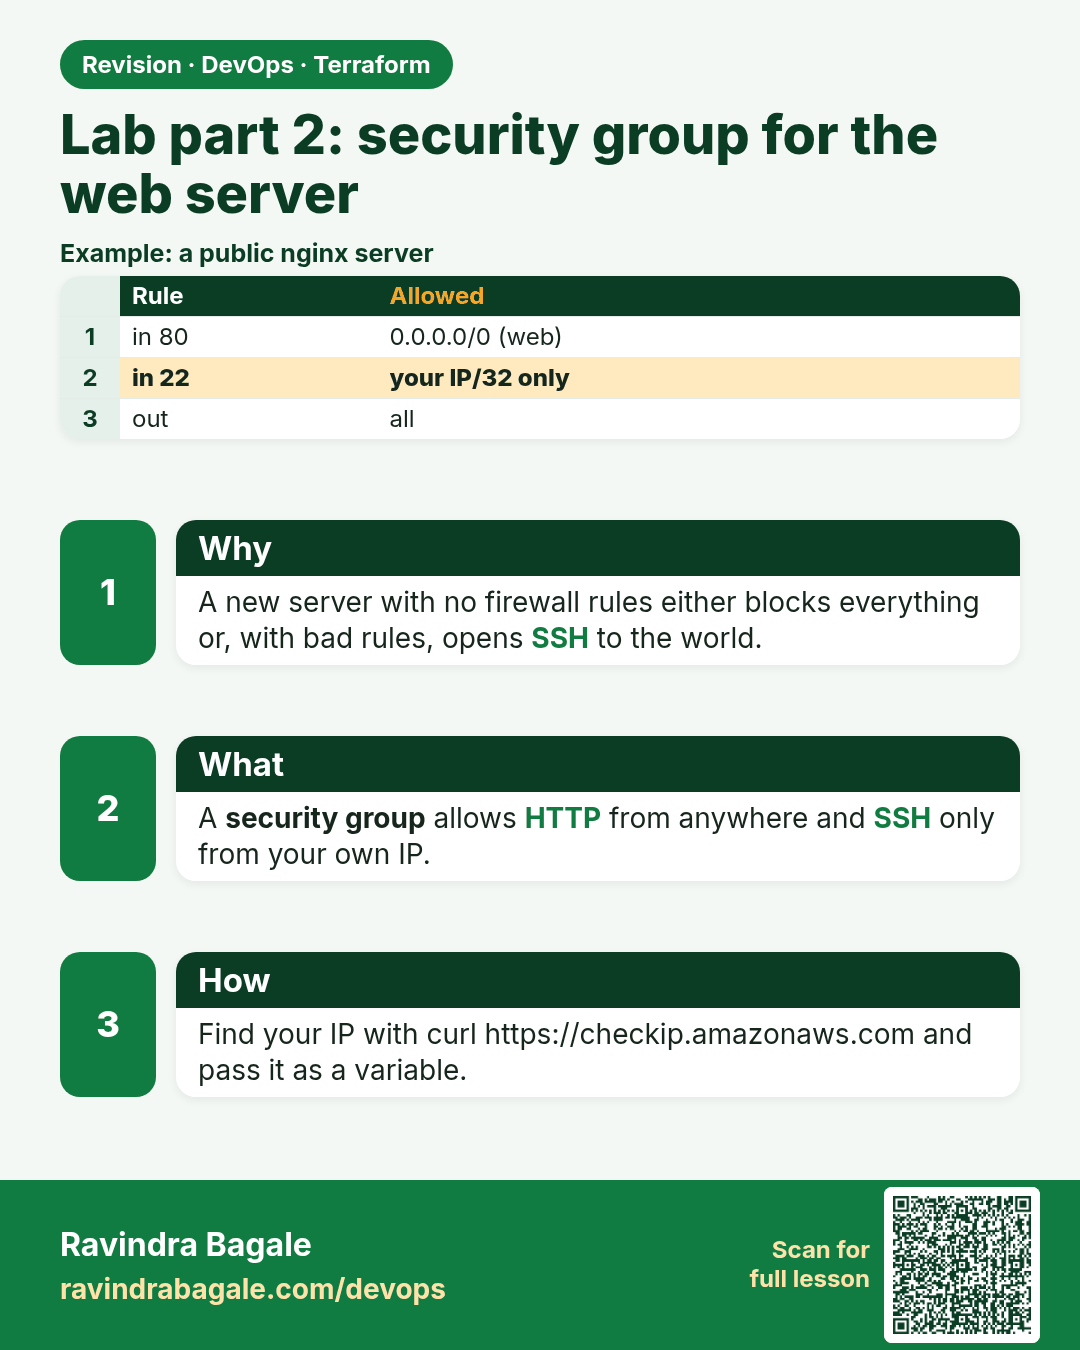
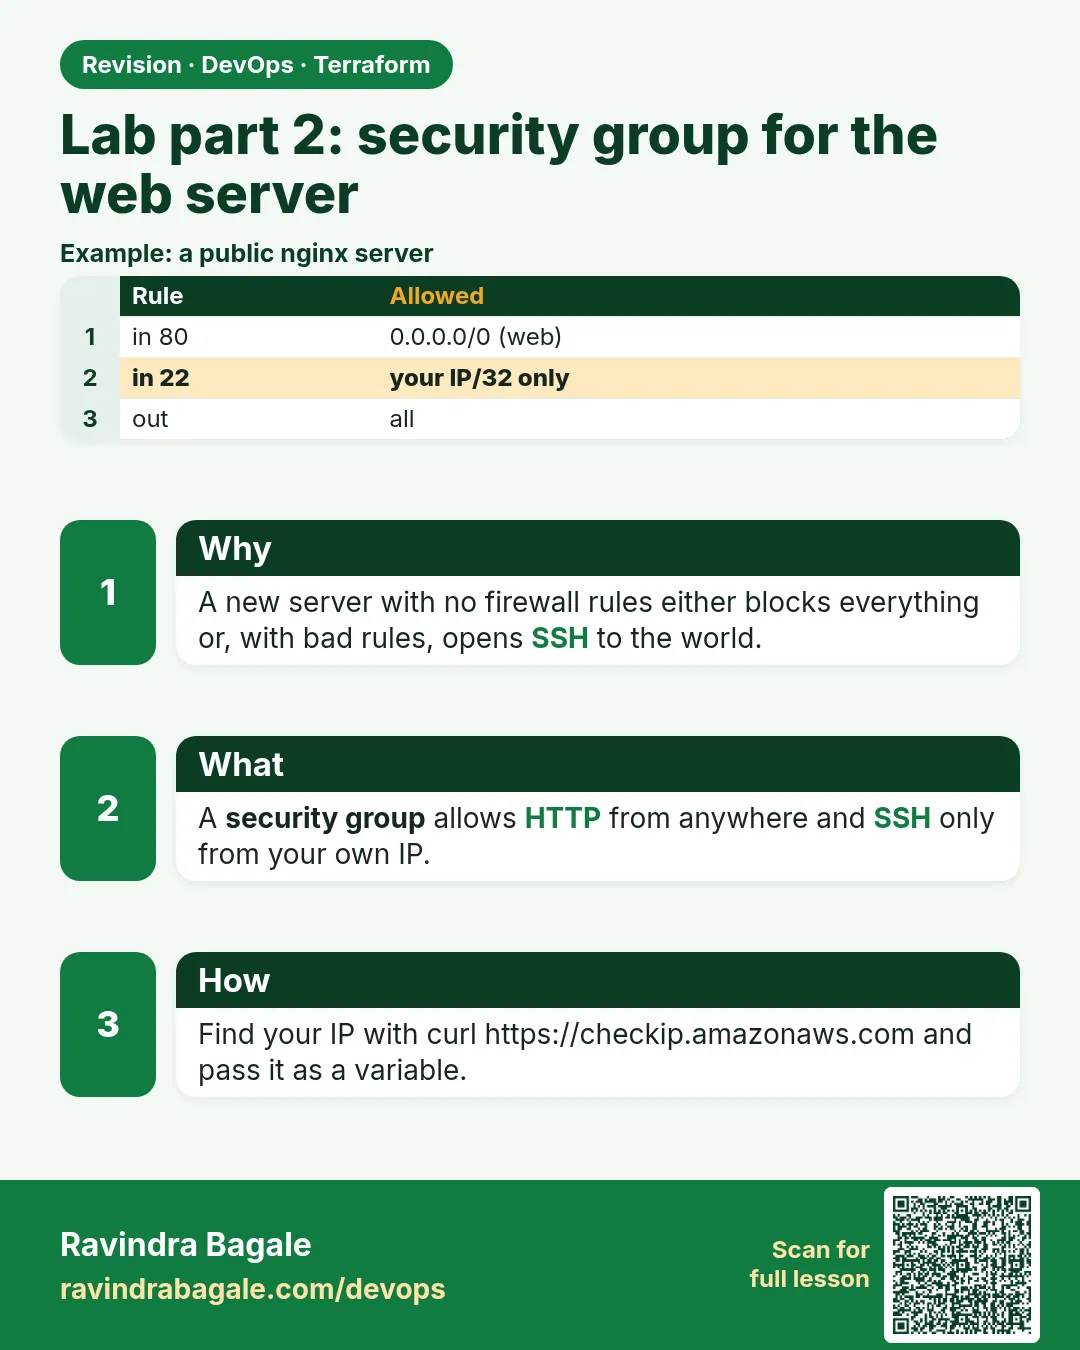 Revision card 2 of 5: Lab part 2: security group for the web server · Download PNG · Open card page
Lesson: 40.2 Lab part 2 — security group for the web server
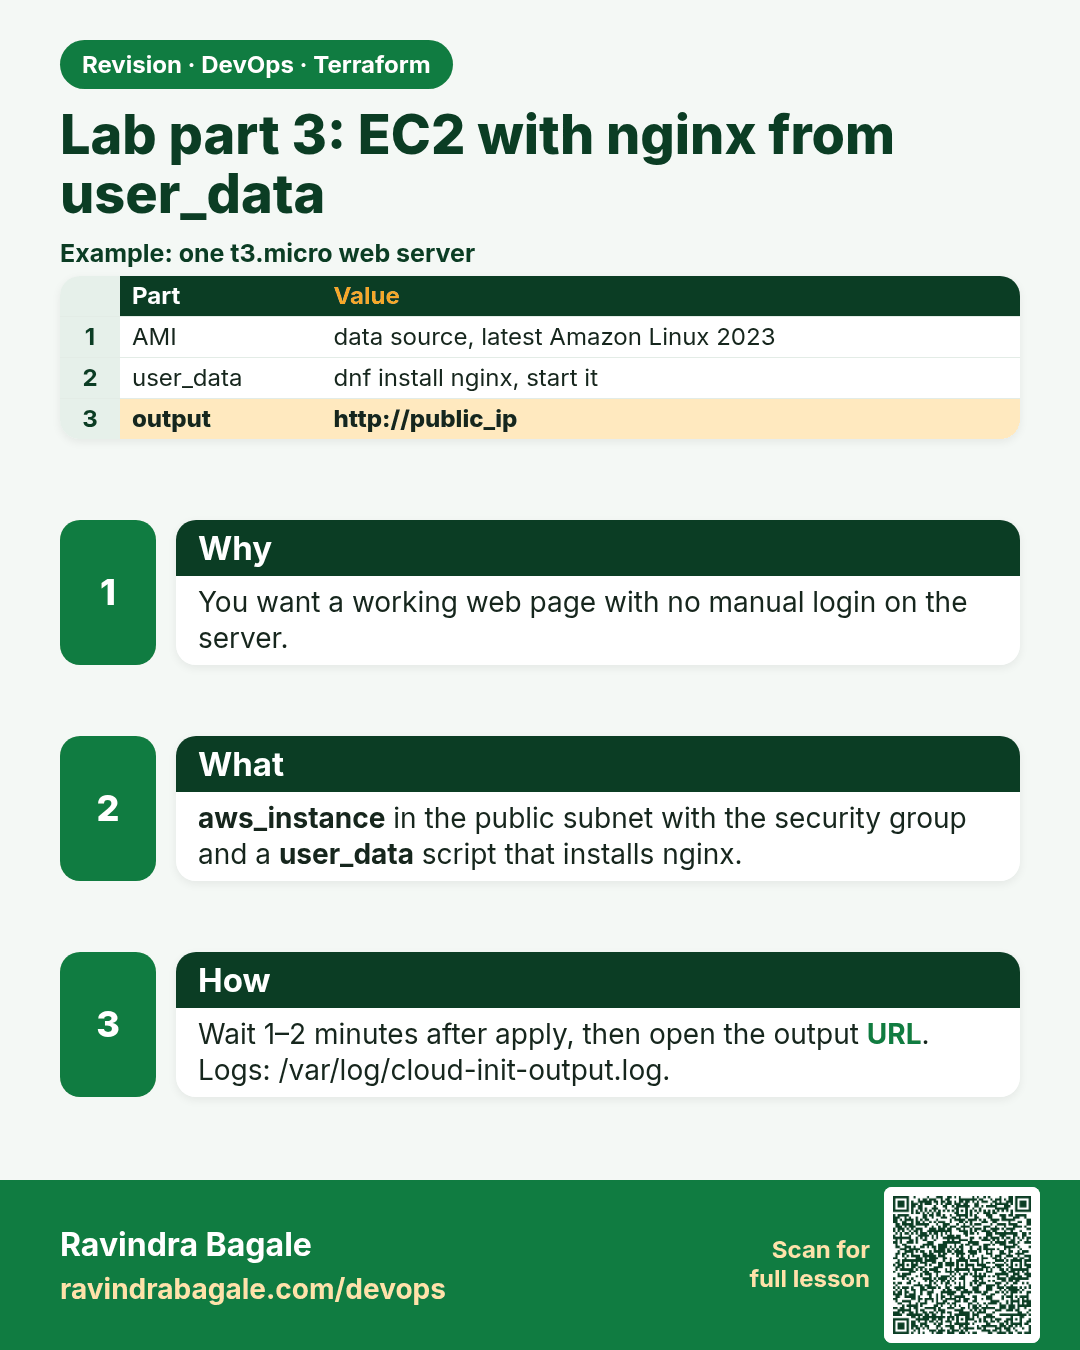
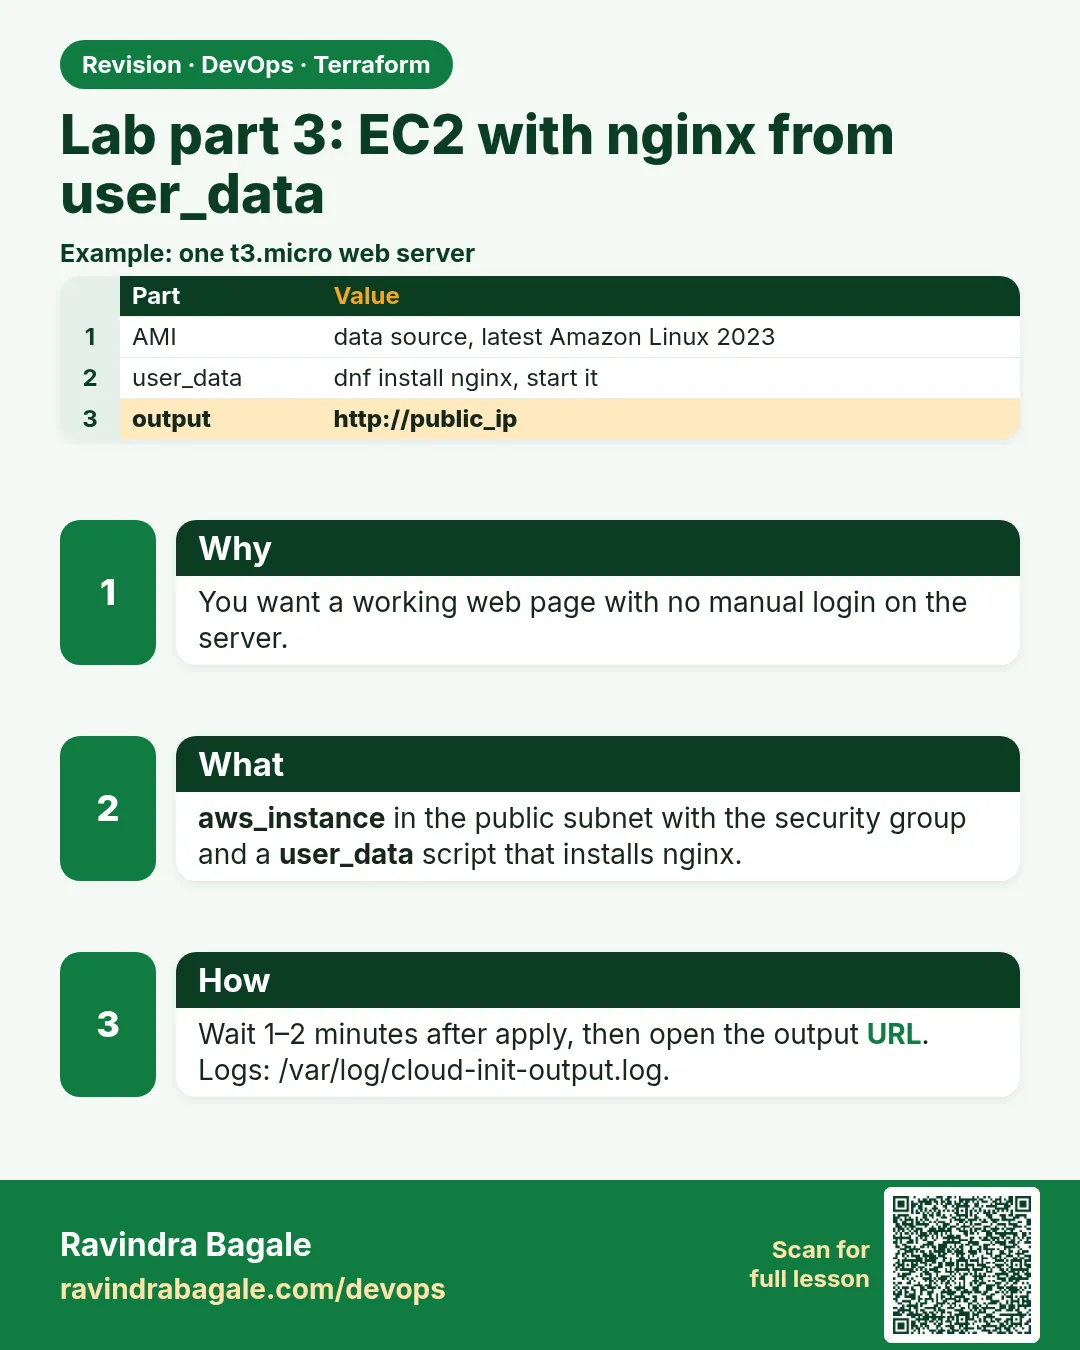 Revision card 3 of 5: Lab part 3: EC2 with nginx from user_data · Download PNG · Open card page
Lesson: 40.3 Lab part 3 — EC2 with nginx from user_data
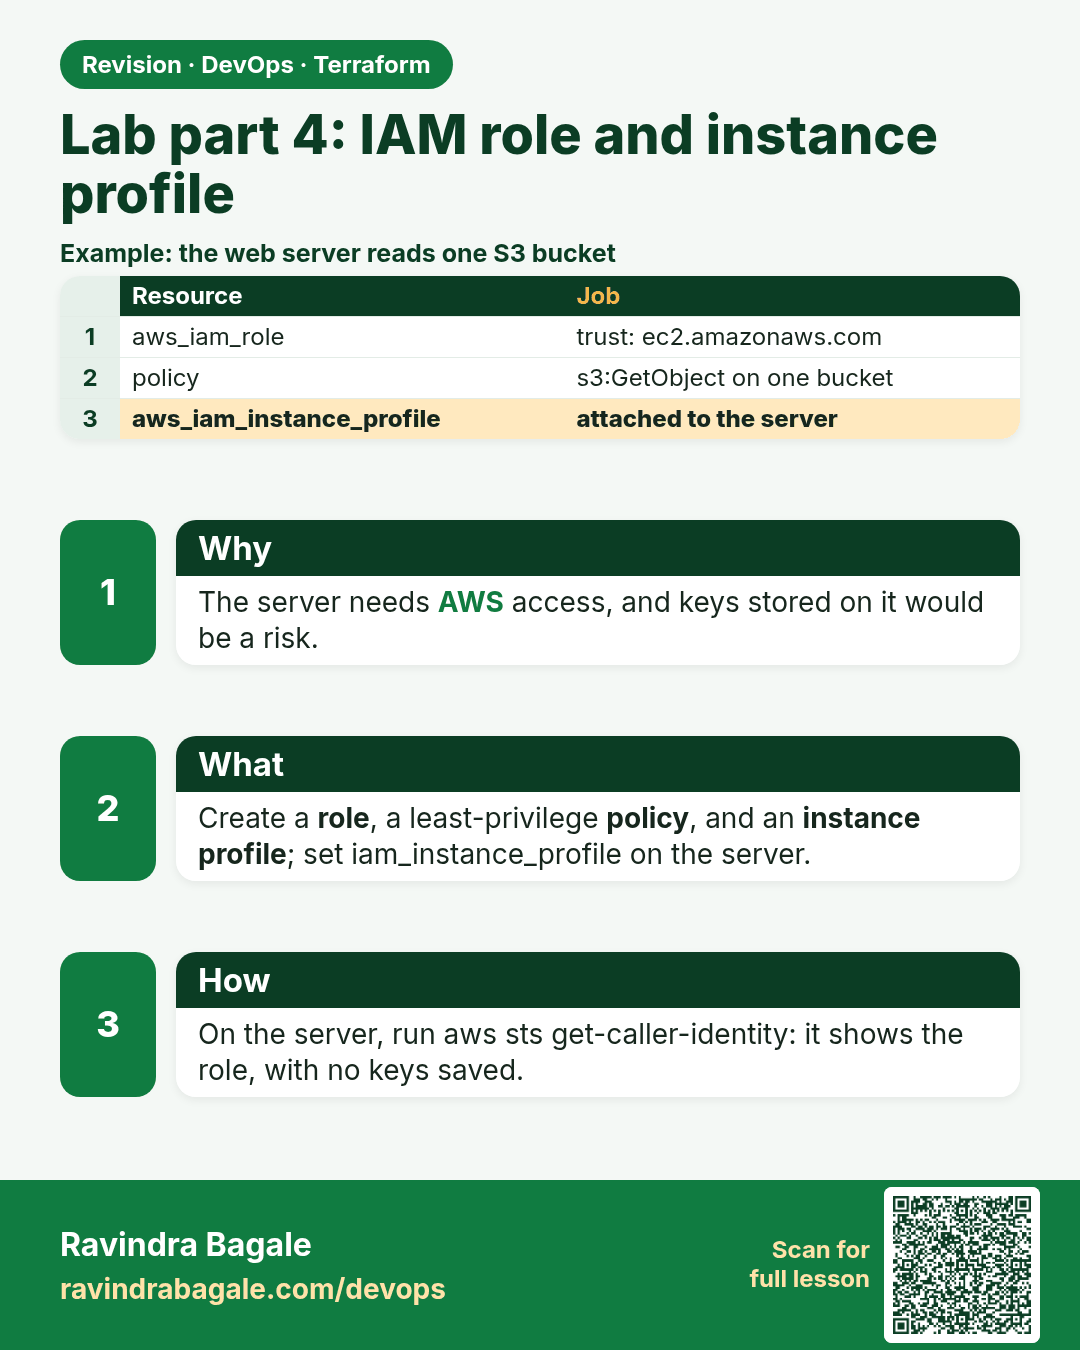
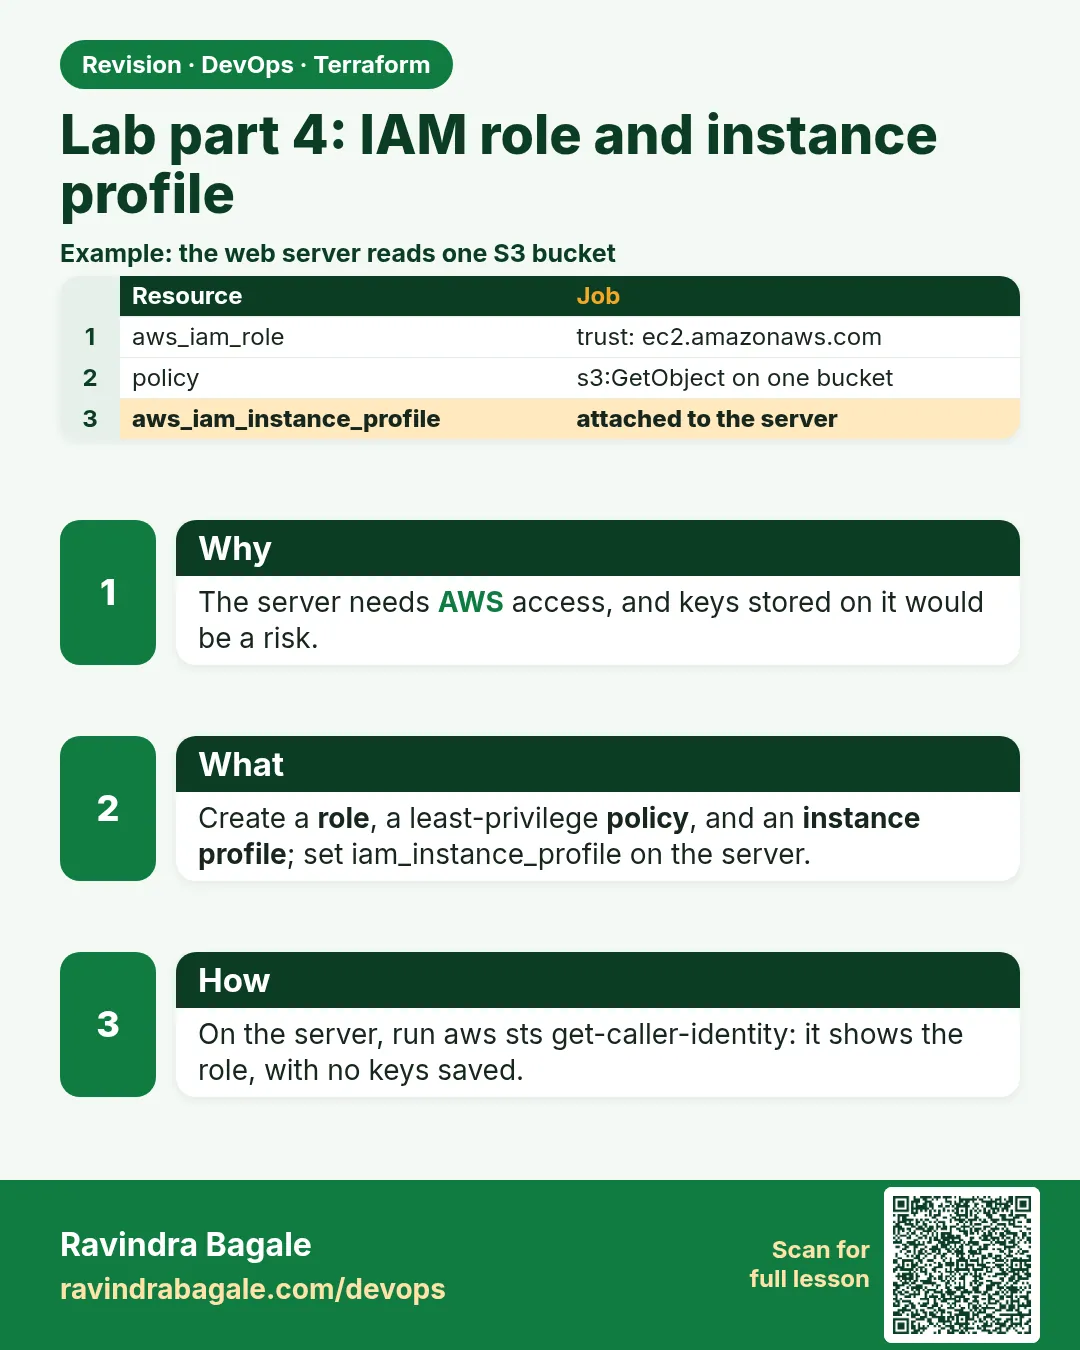 Revision card 4 of 5: Lab part 4: IAM role and instance profile · Download PNG · Open card page
Lesson: 40.4 Lab part 4 — IAM role and instance profile
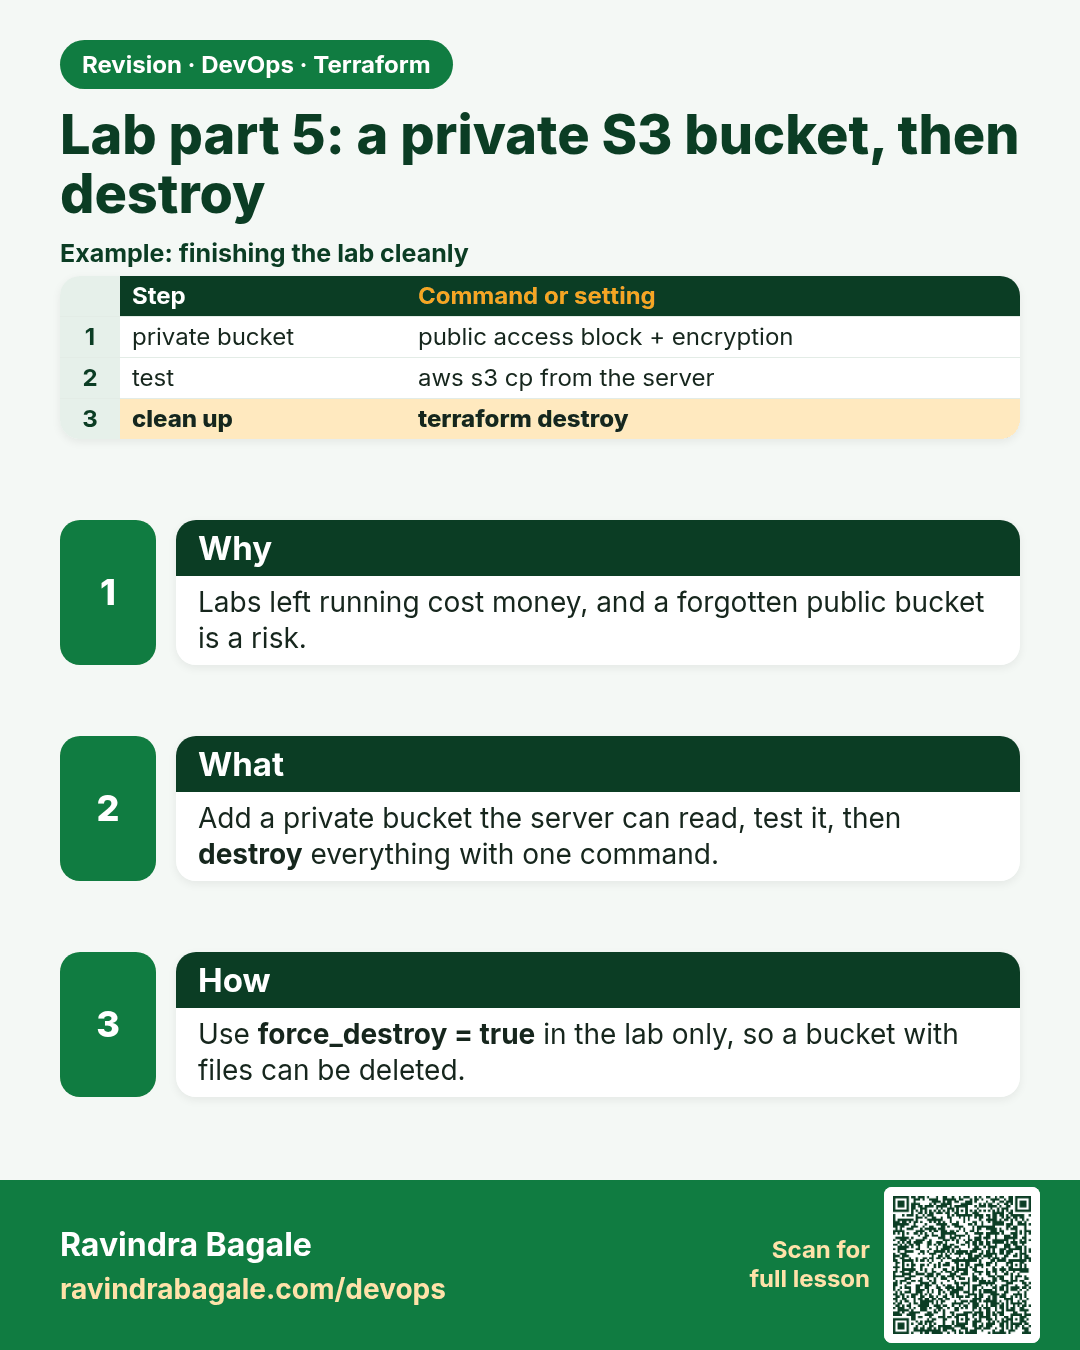
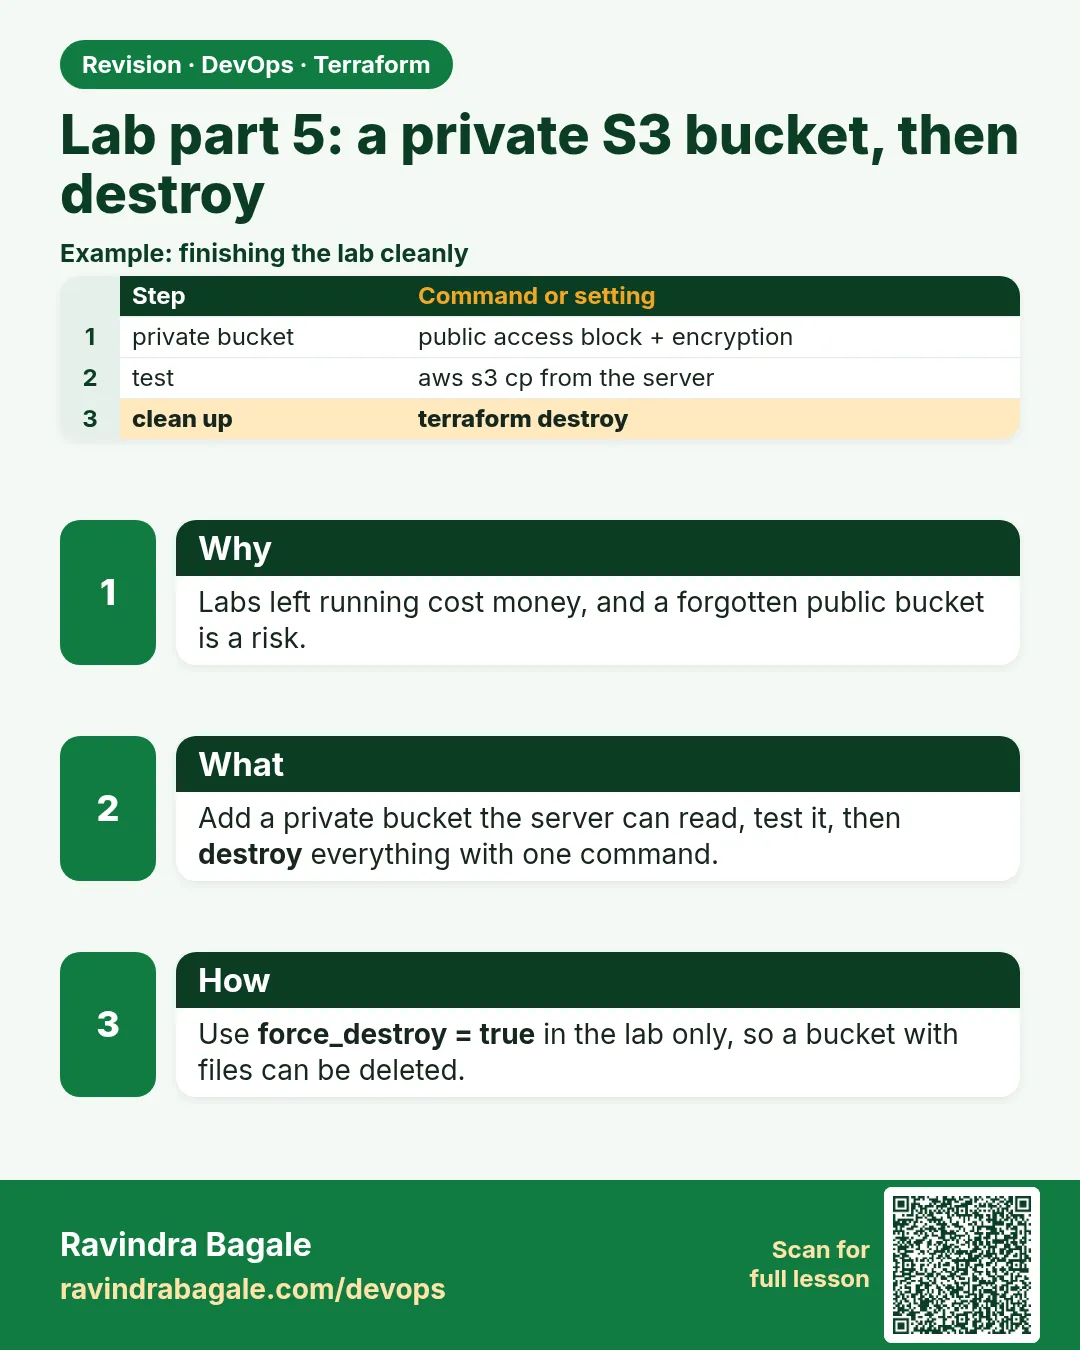 Revision card 5 of 5: Lab part 5: a private S3 bucket, then destroy · Download PNG · Open card page
Lesson: 40.5 Lab part 5 — a private S3 bucket, then destroy everything
Interview cards
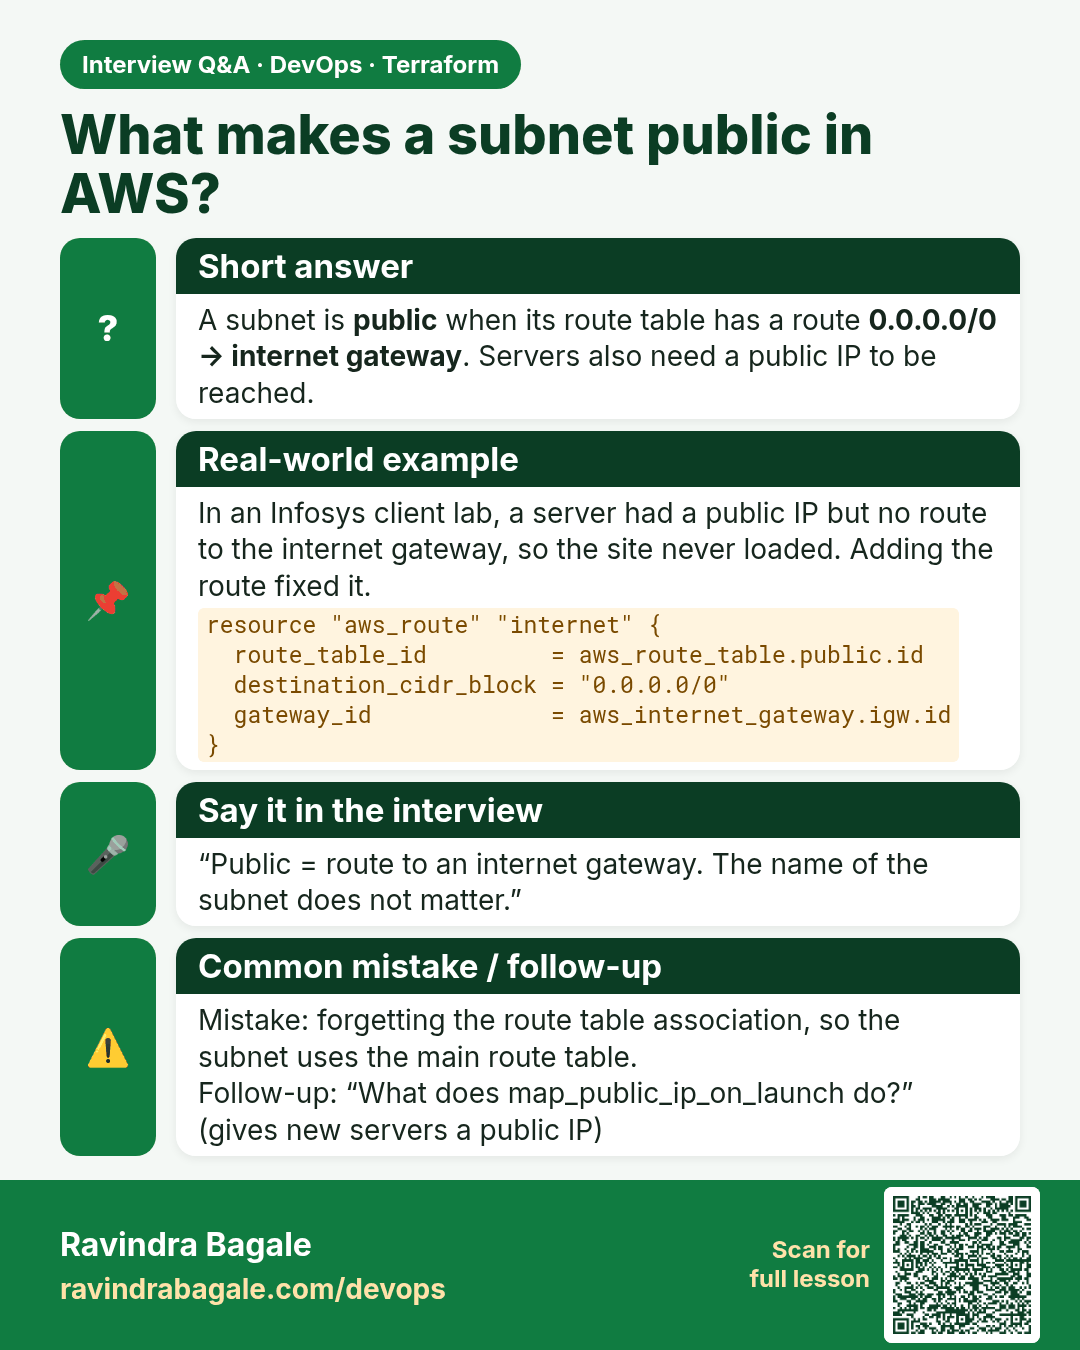
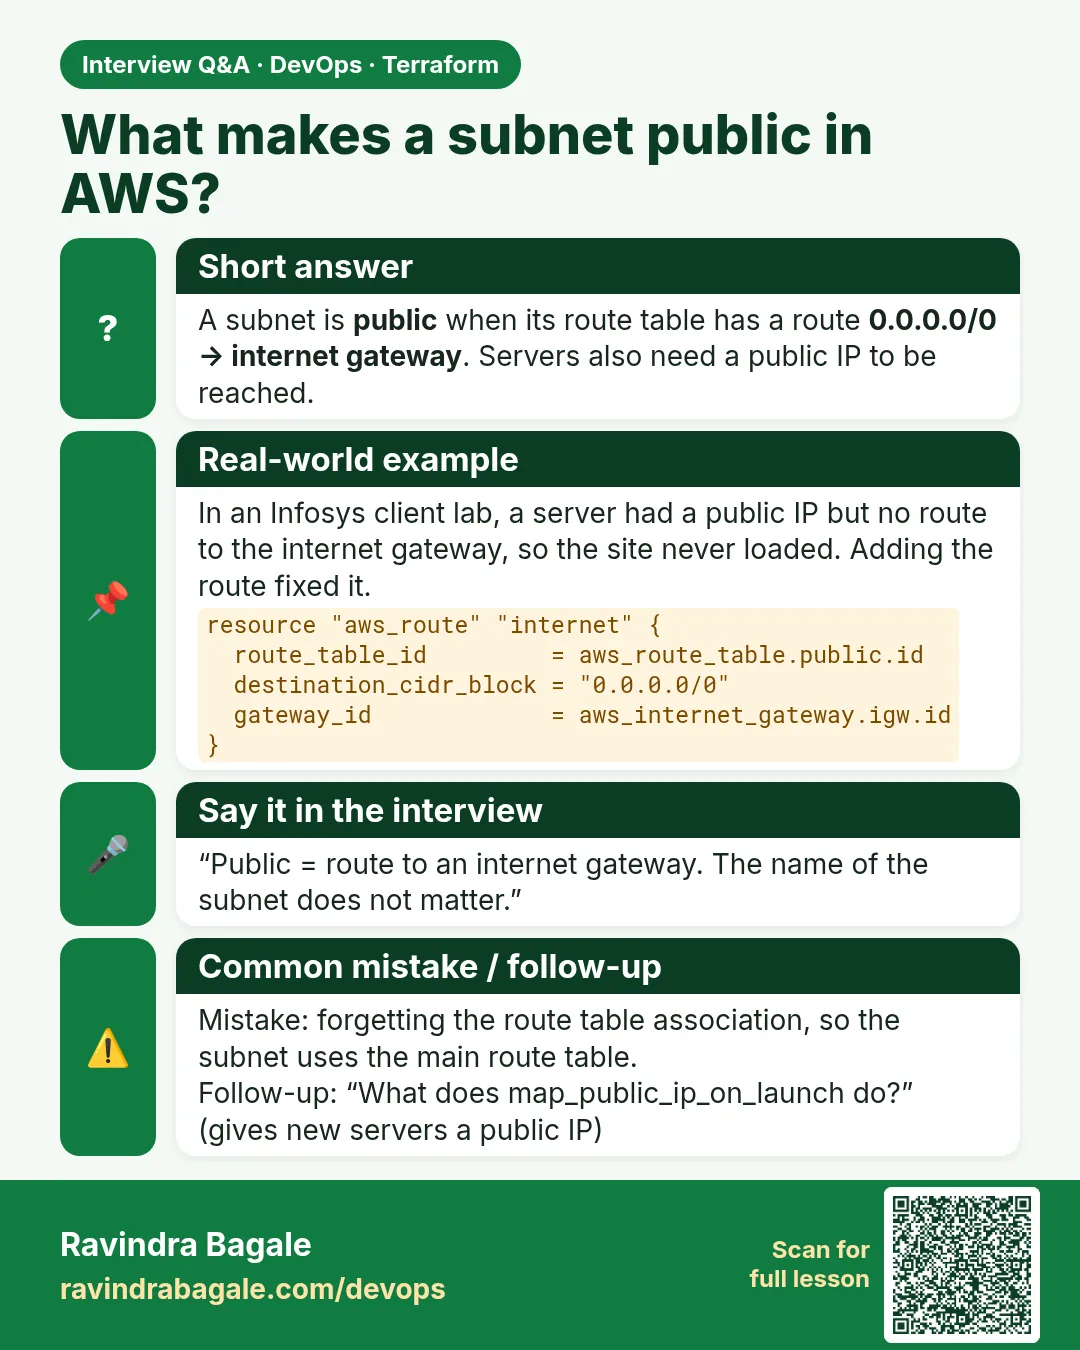 Interview card 1 of 5: What makes a subnet public in AWS? · Download PNG · Open card page
Lesson: 40.1 Lab part 1 — VPC, public subnets, internet gateway and routes
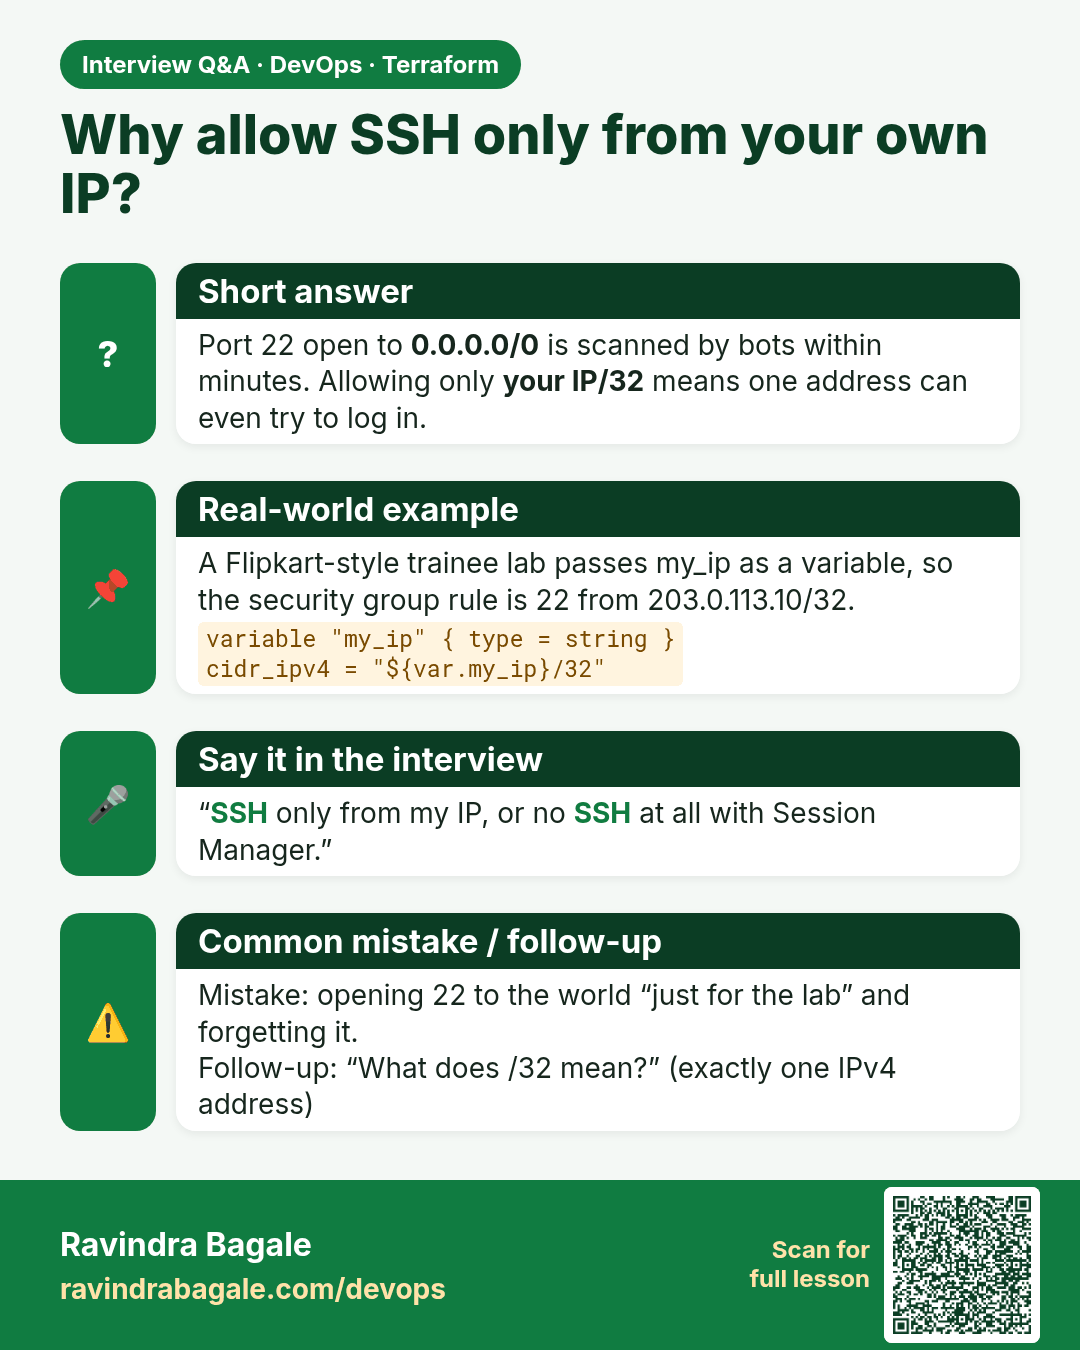
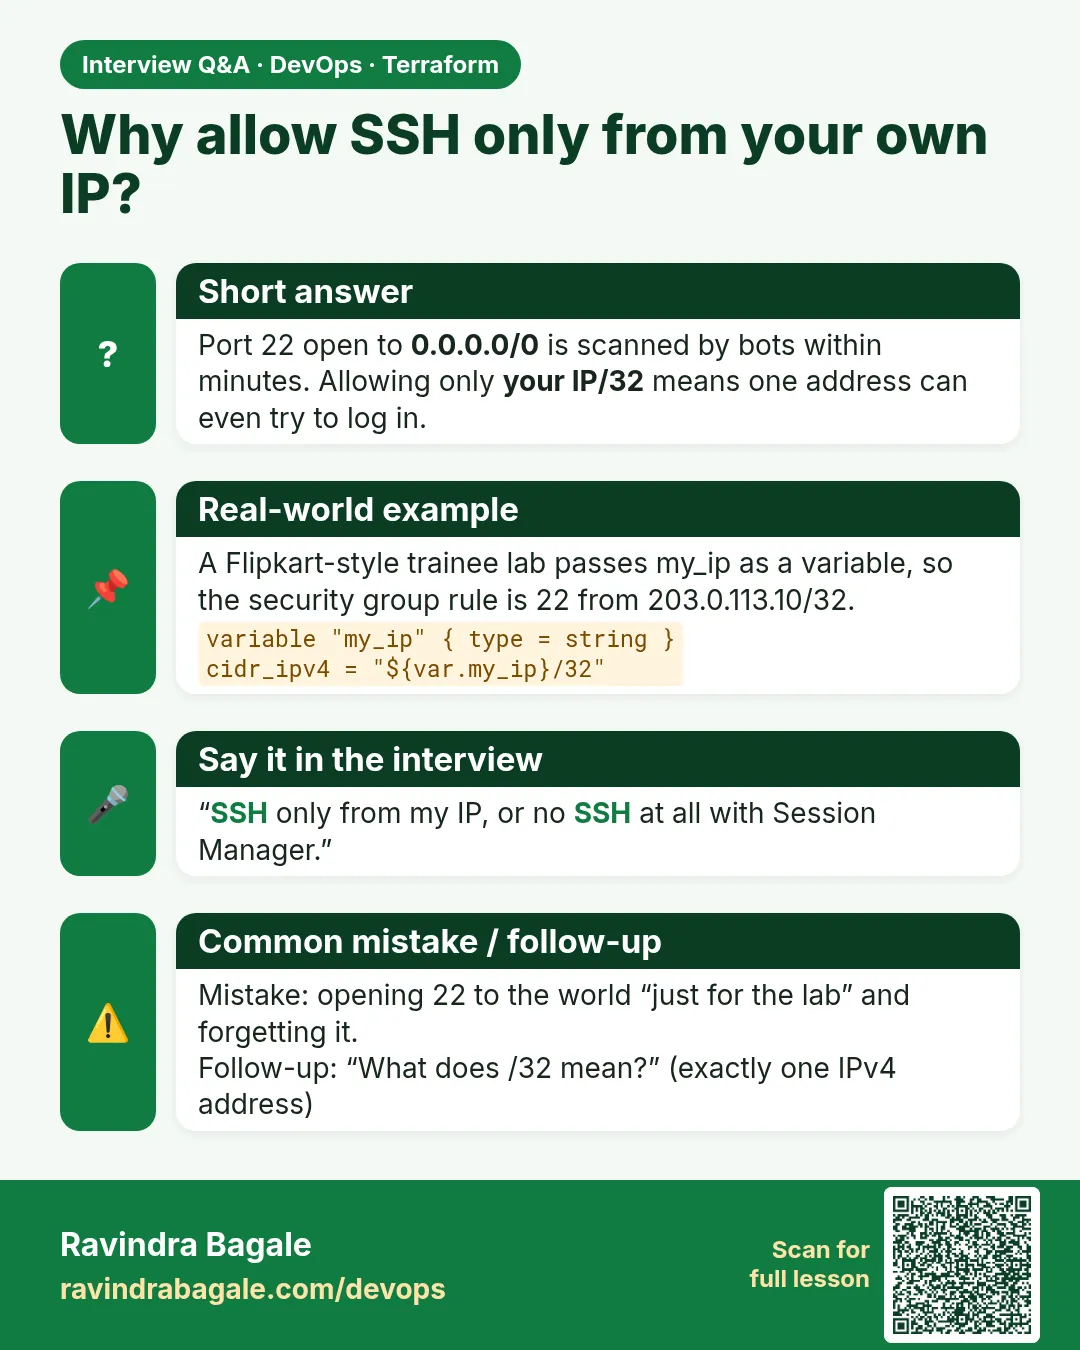 Interview card 2 of 5: Why allow SSH only from your own IP? · Download PNG · Open card page
Lesson: 40.2 Lab part 2 — security group for the web server
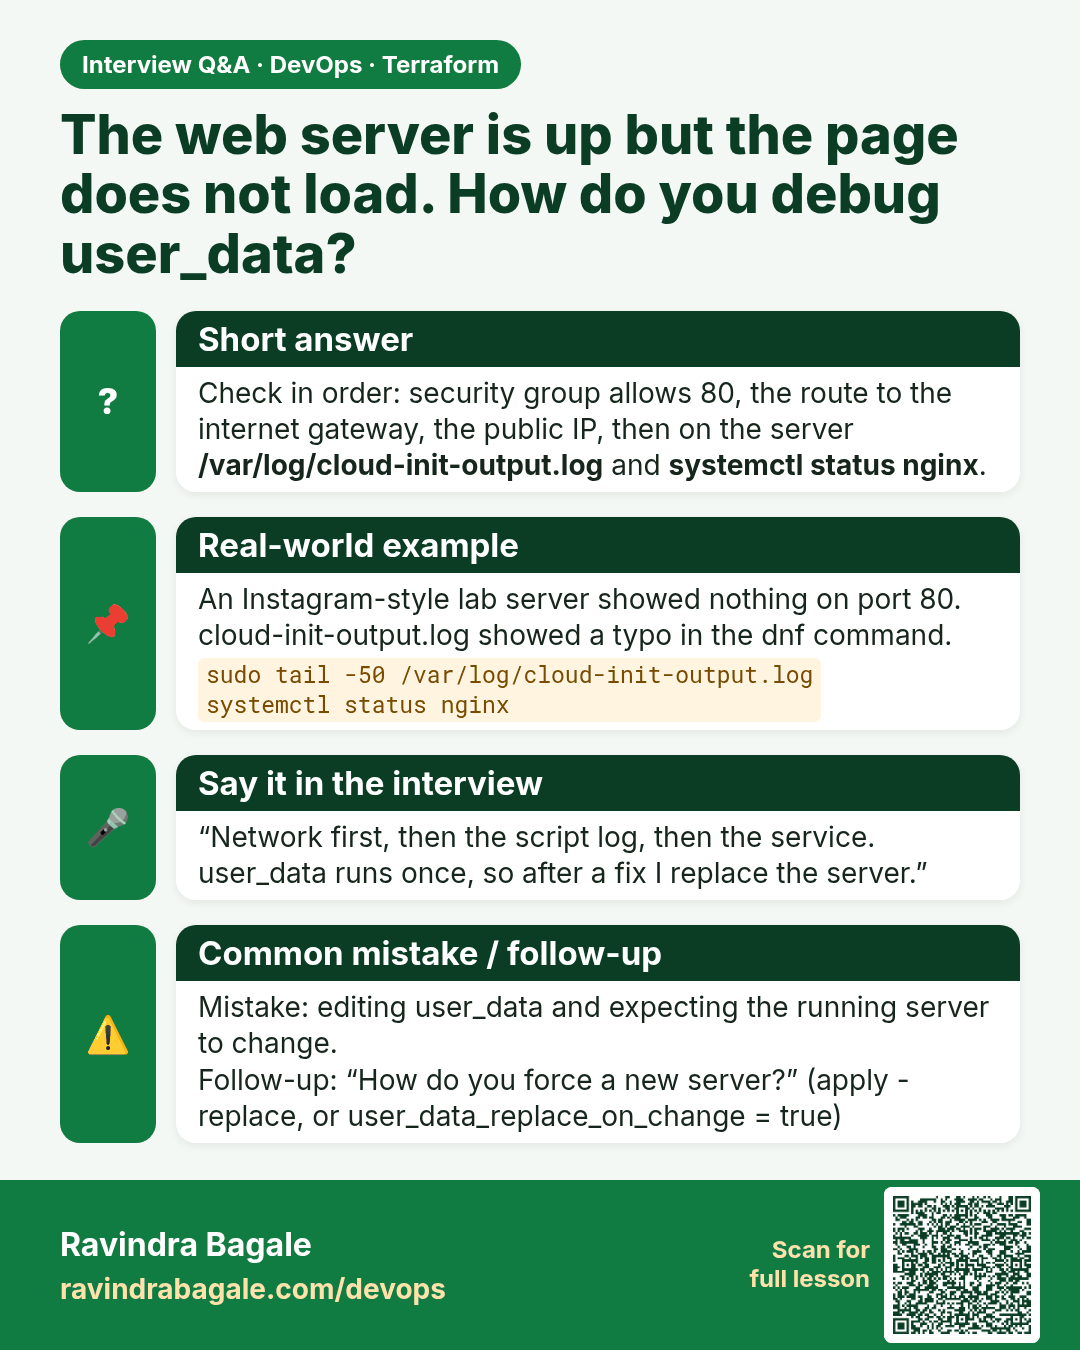
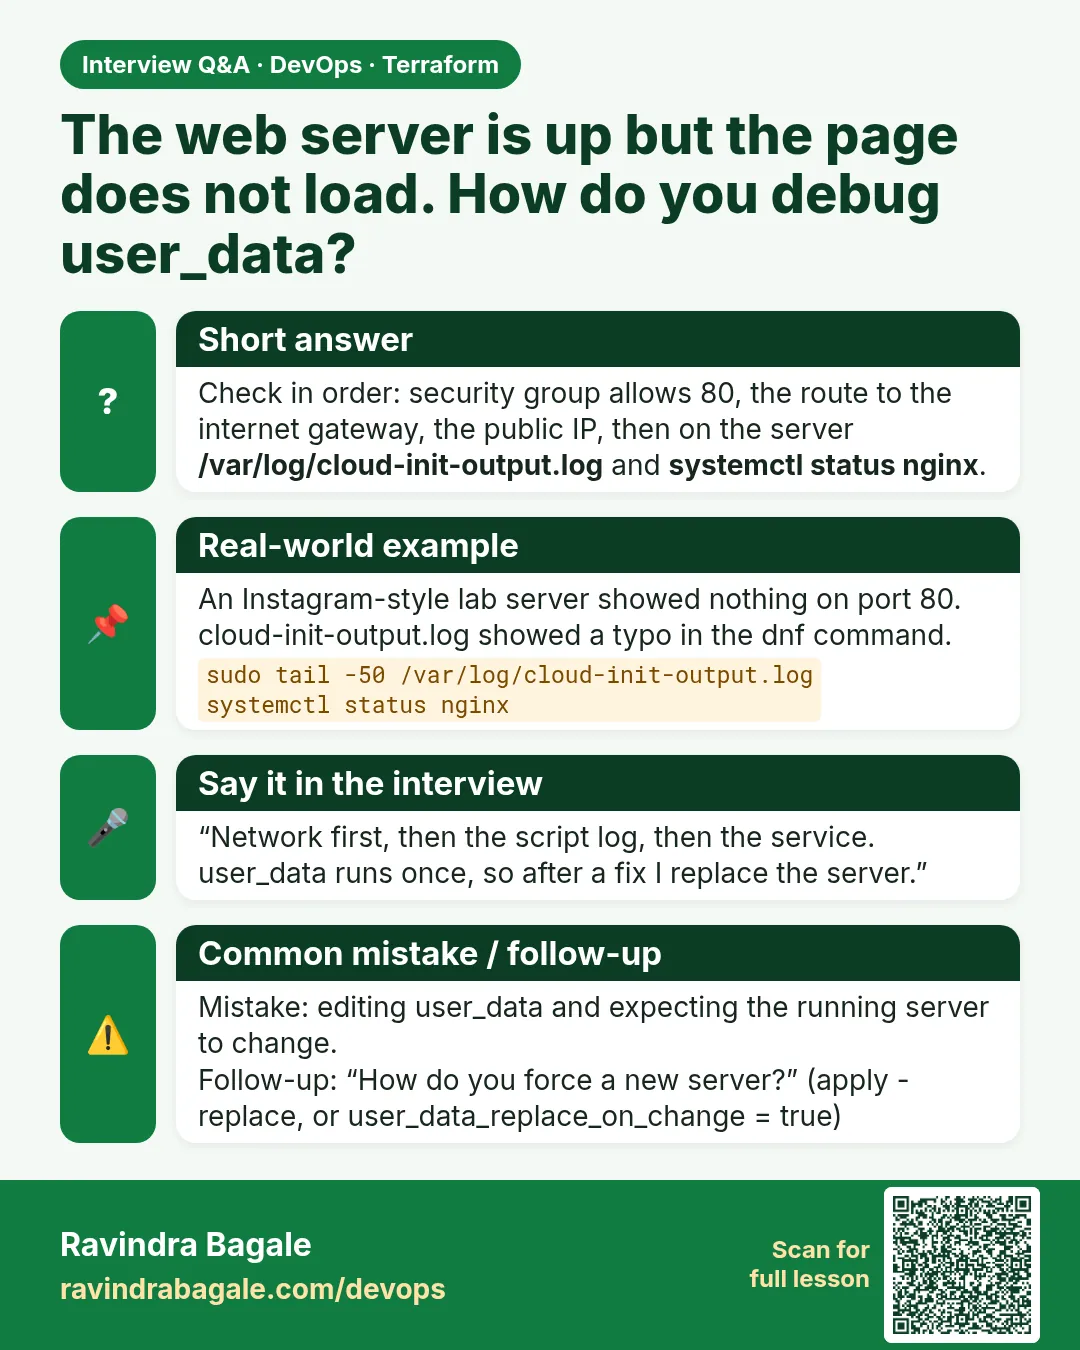 Interview card 3 of 5: The web server is up but the page does not load. How do you debug user_data? · Download PNG · Open card page
Lesson: 40.3 Lab part 3 — EC2 with nginx from user_data
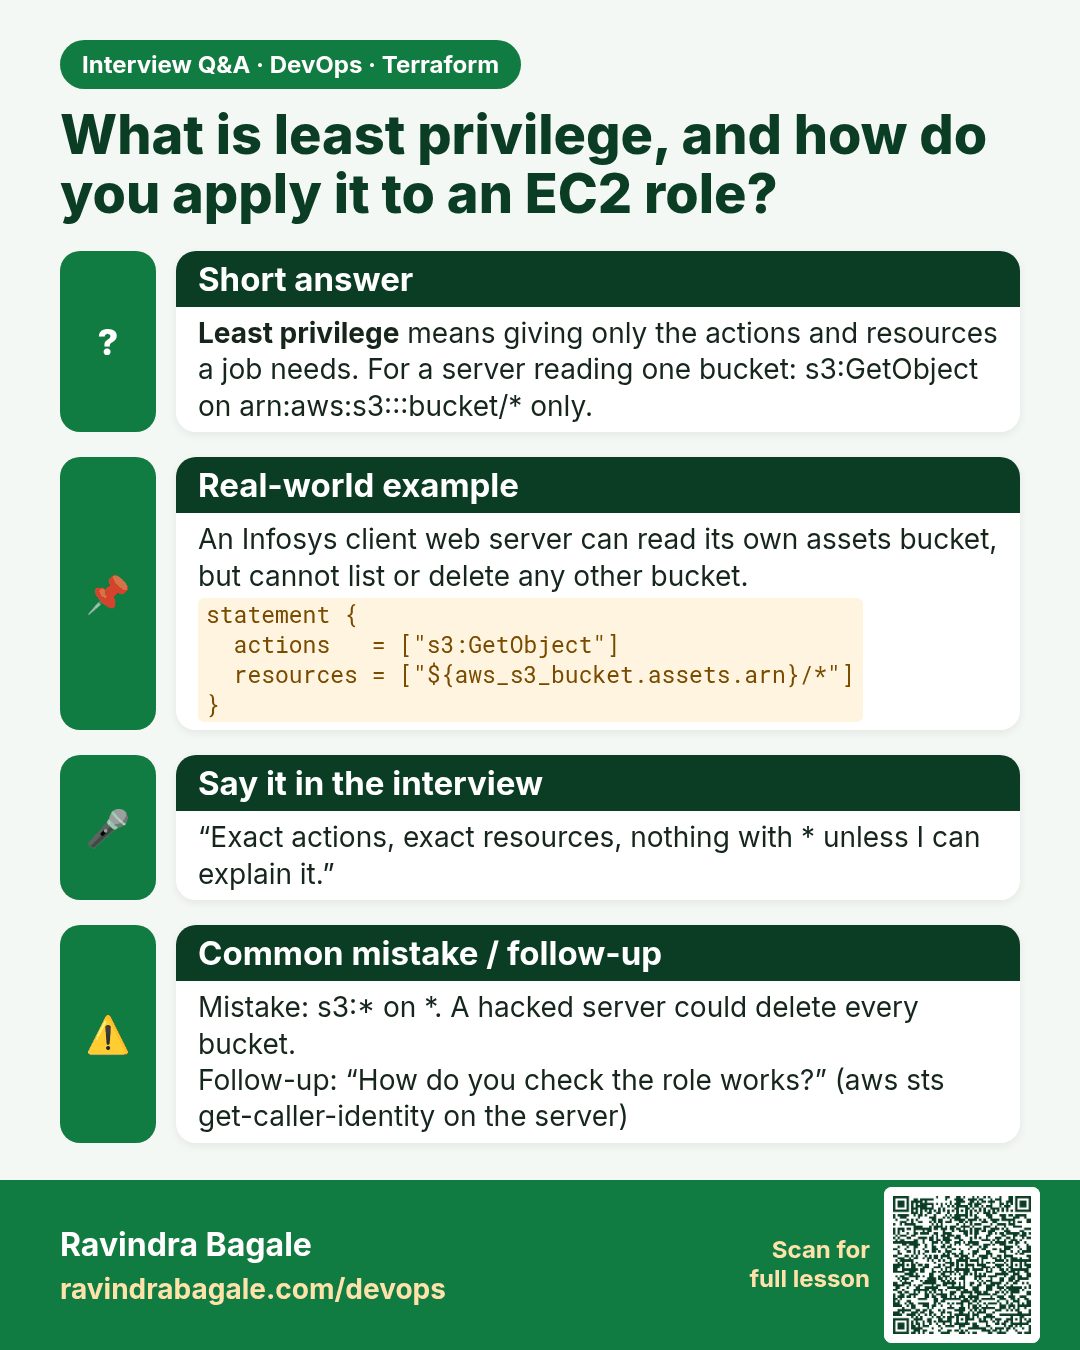
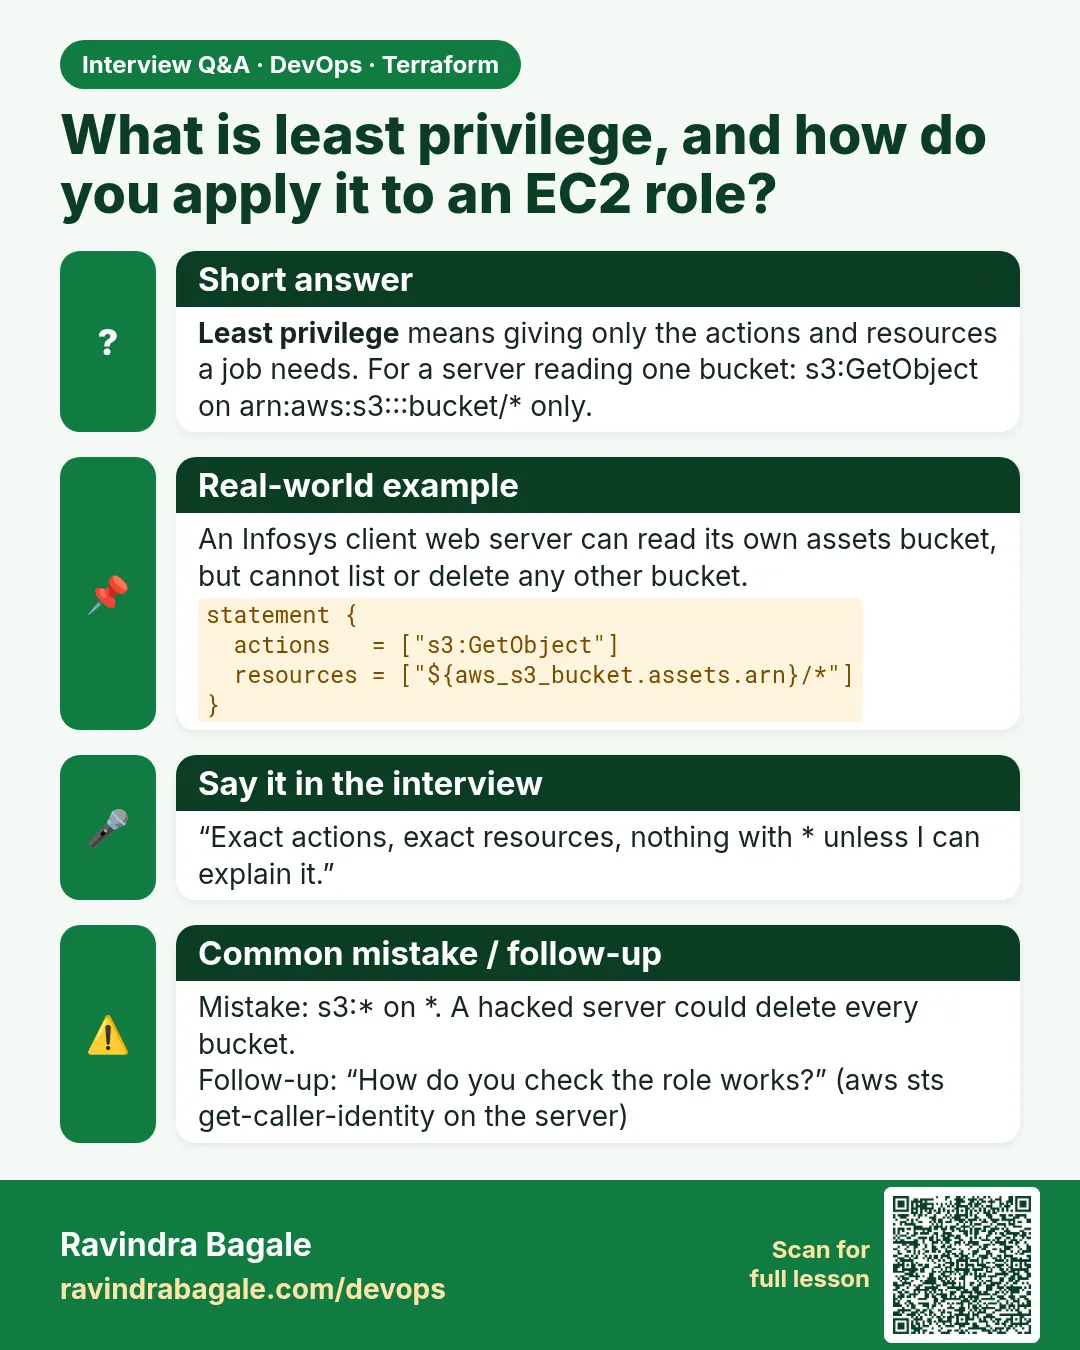 Interview card 4 of 5: What is least privilege, and how do you apply it to an EC2 role? · Download PNG · Open card page
Lesson: 40.4 Lab part 4 — IAM role and instance profile
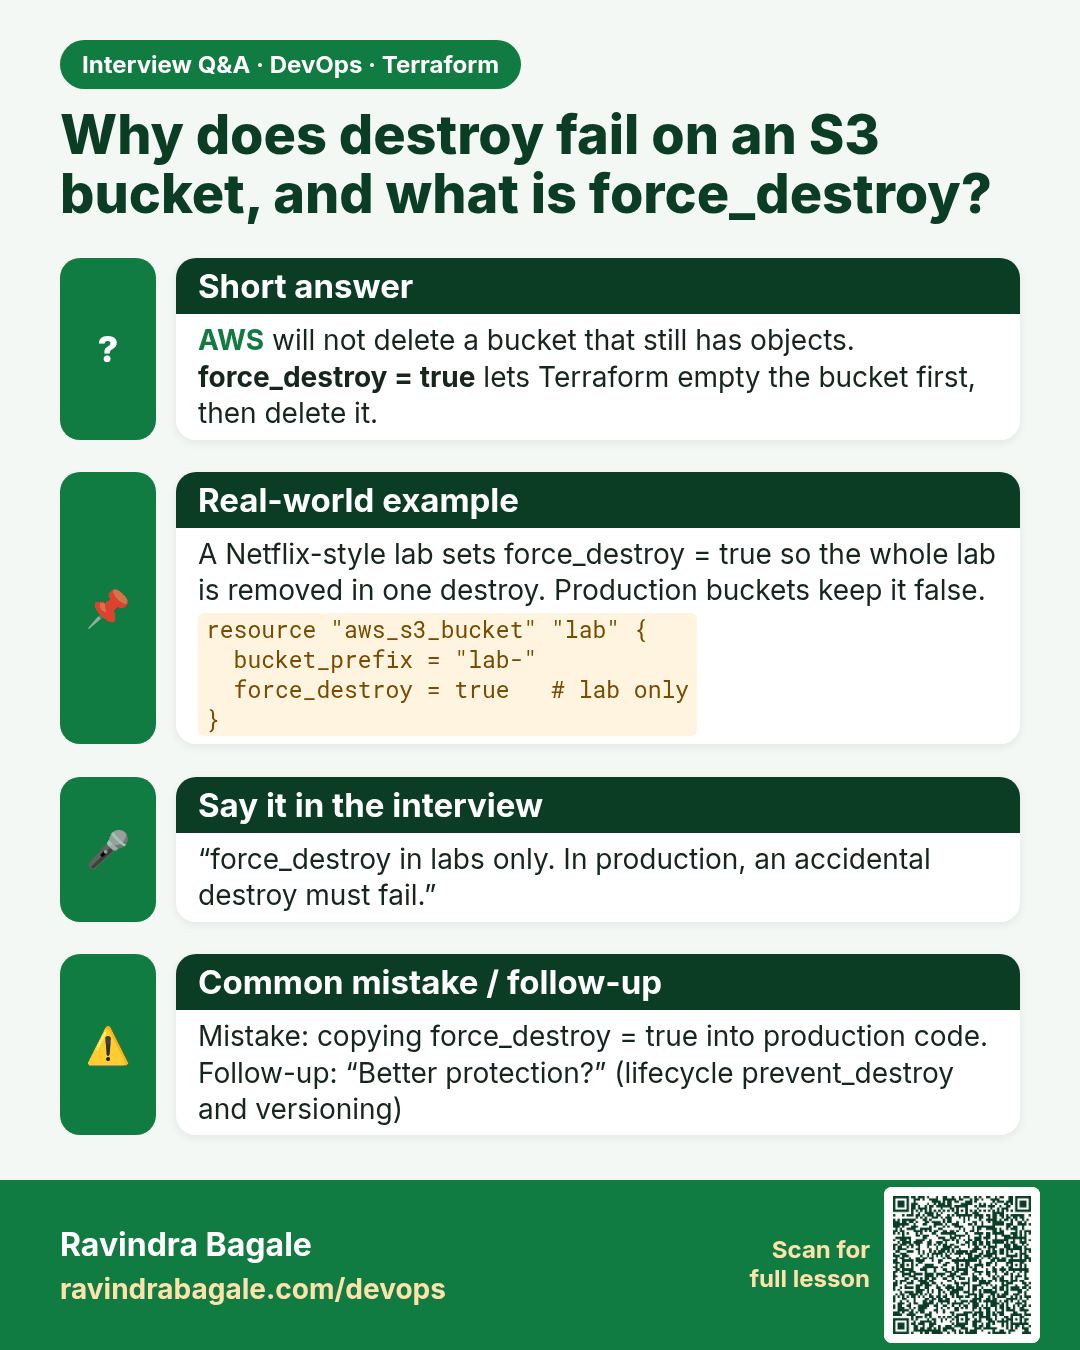
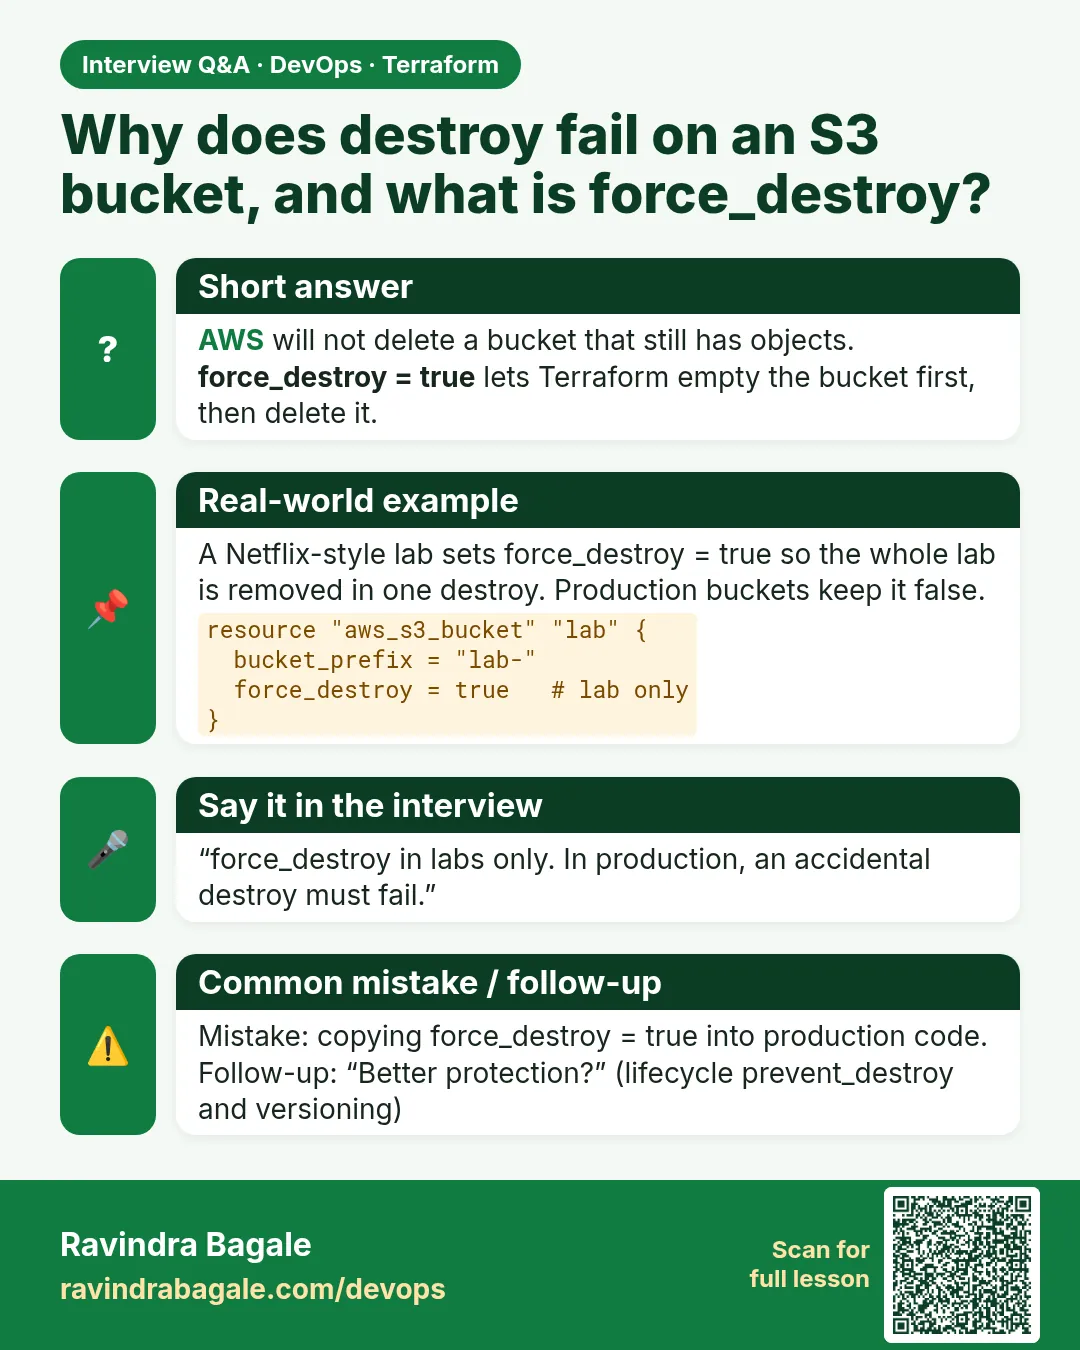 Interview card 5 of 5: Why does destroy fail on an S3 bucket, and what is force_destroy? · Download PNG · Open card page
Lesson: 40.5 Lab part 5 — a private S3 bucket, then destroy everything
Comparison cards
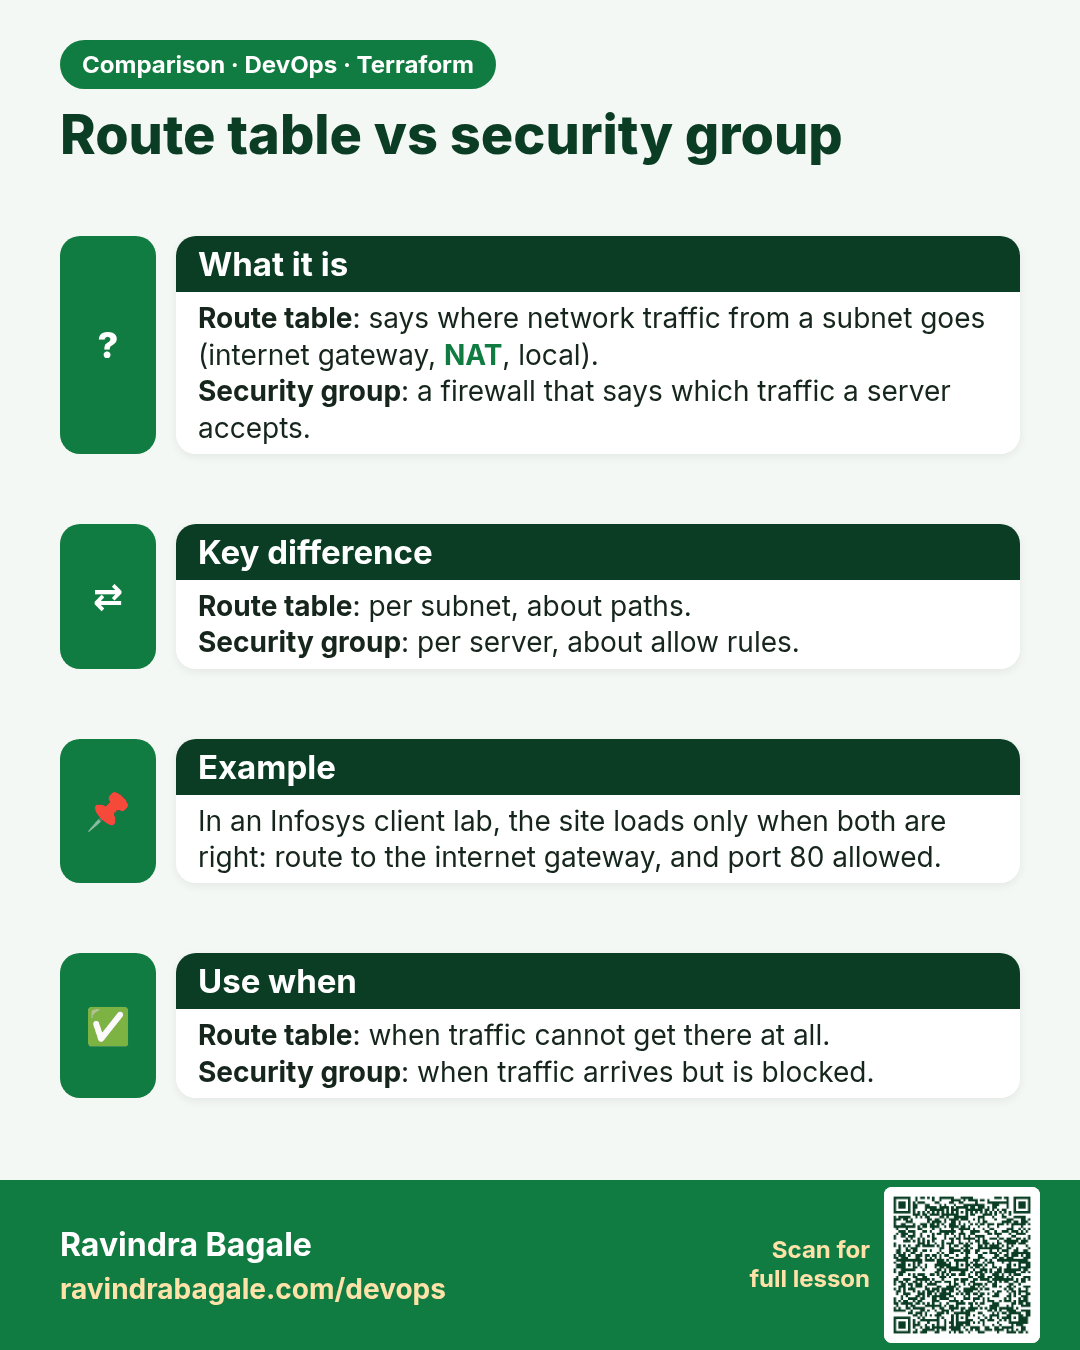
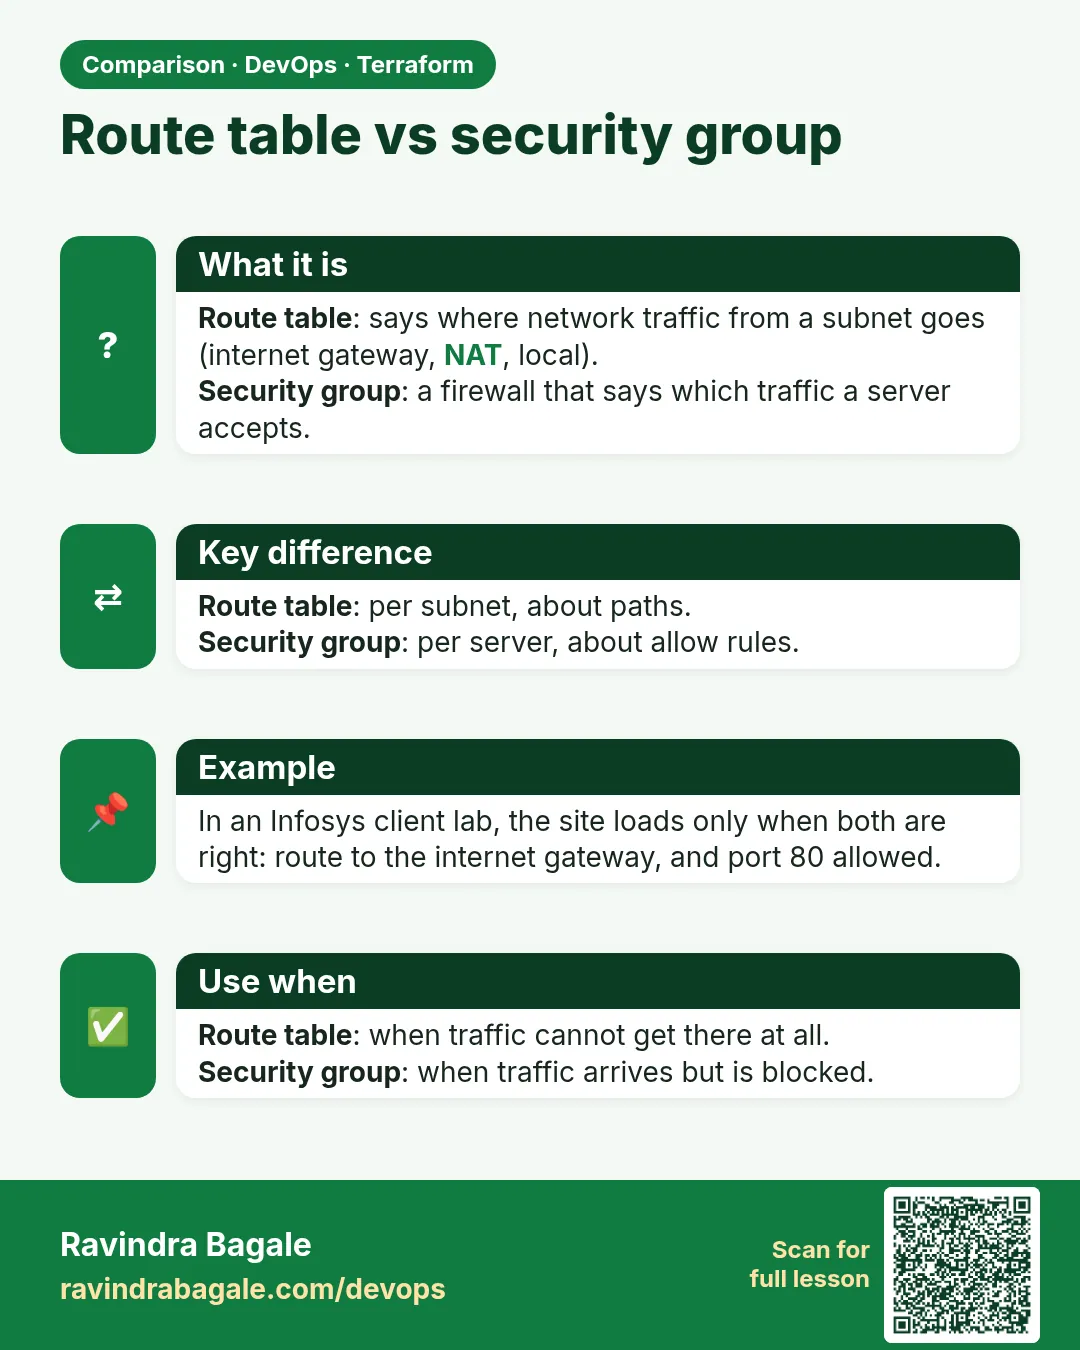 Comparison card 1 of 3: Route table vs security group · Download PNG · Open card page
Lesson: Chapter 40: Terraform Real AWS Labs VPC EC2 nginx S3 and IAM Role
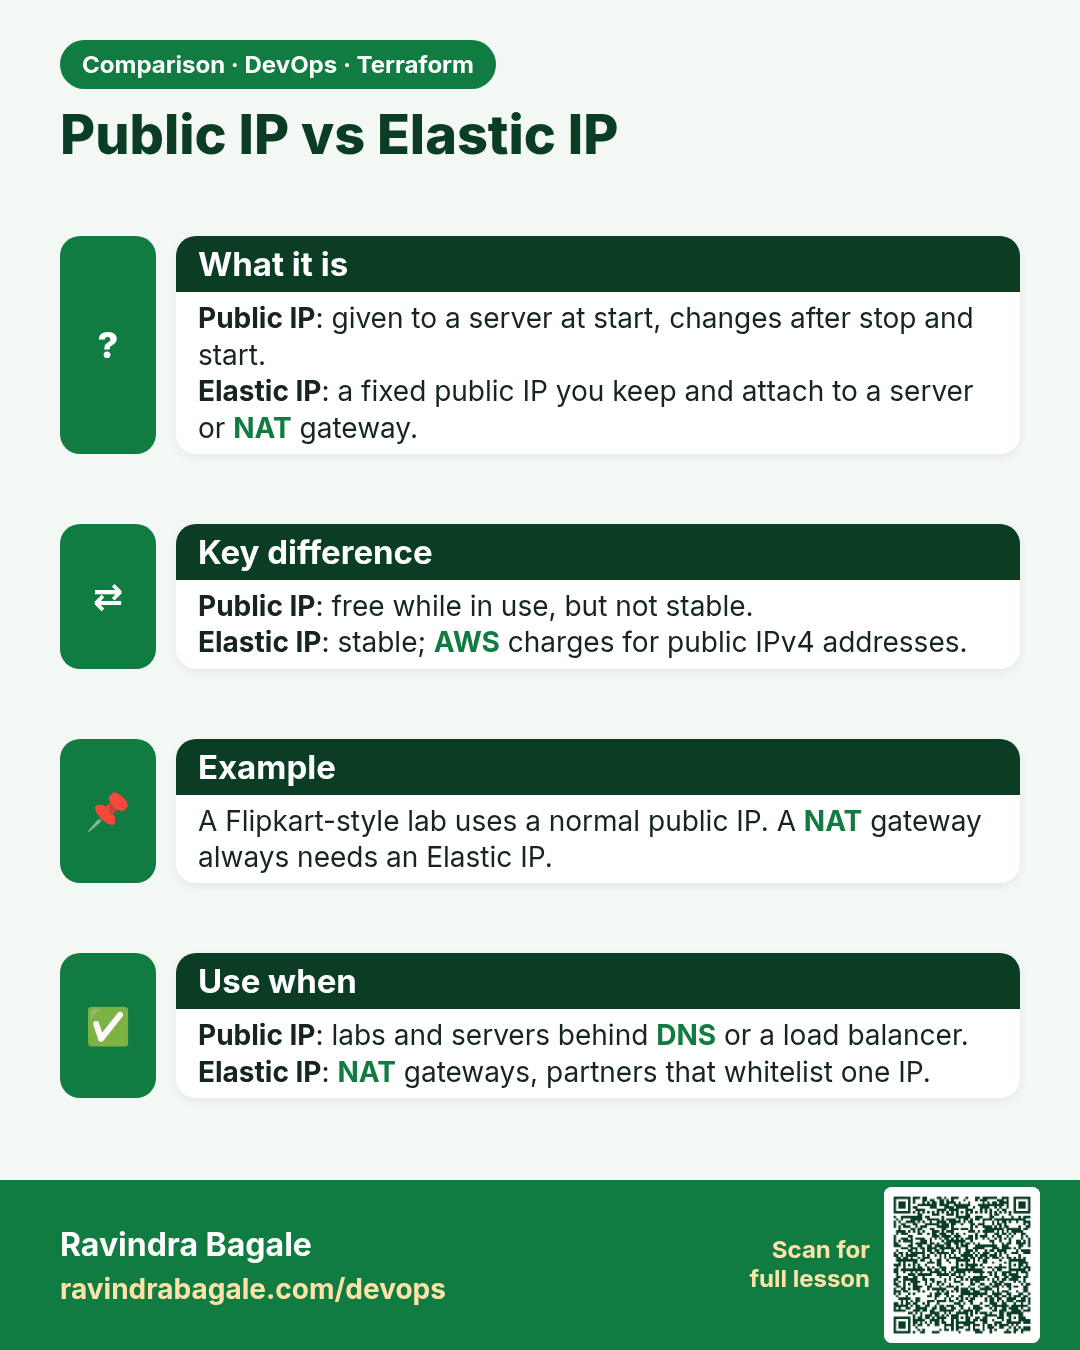
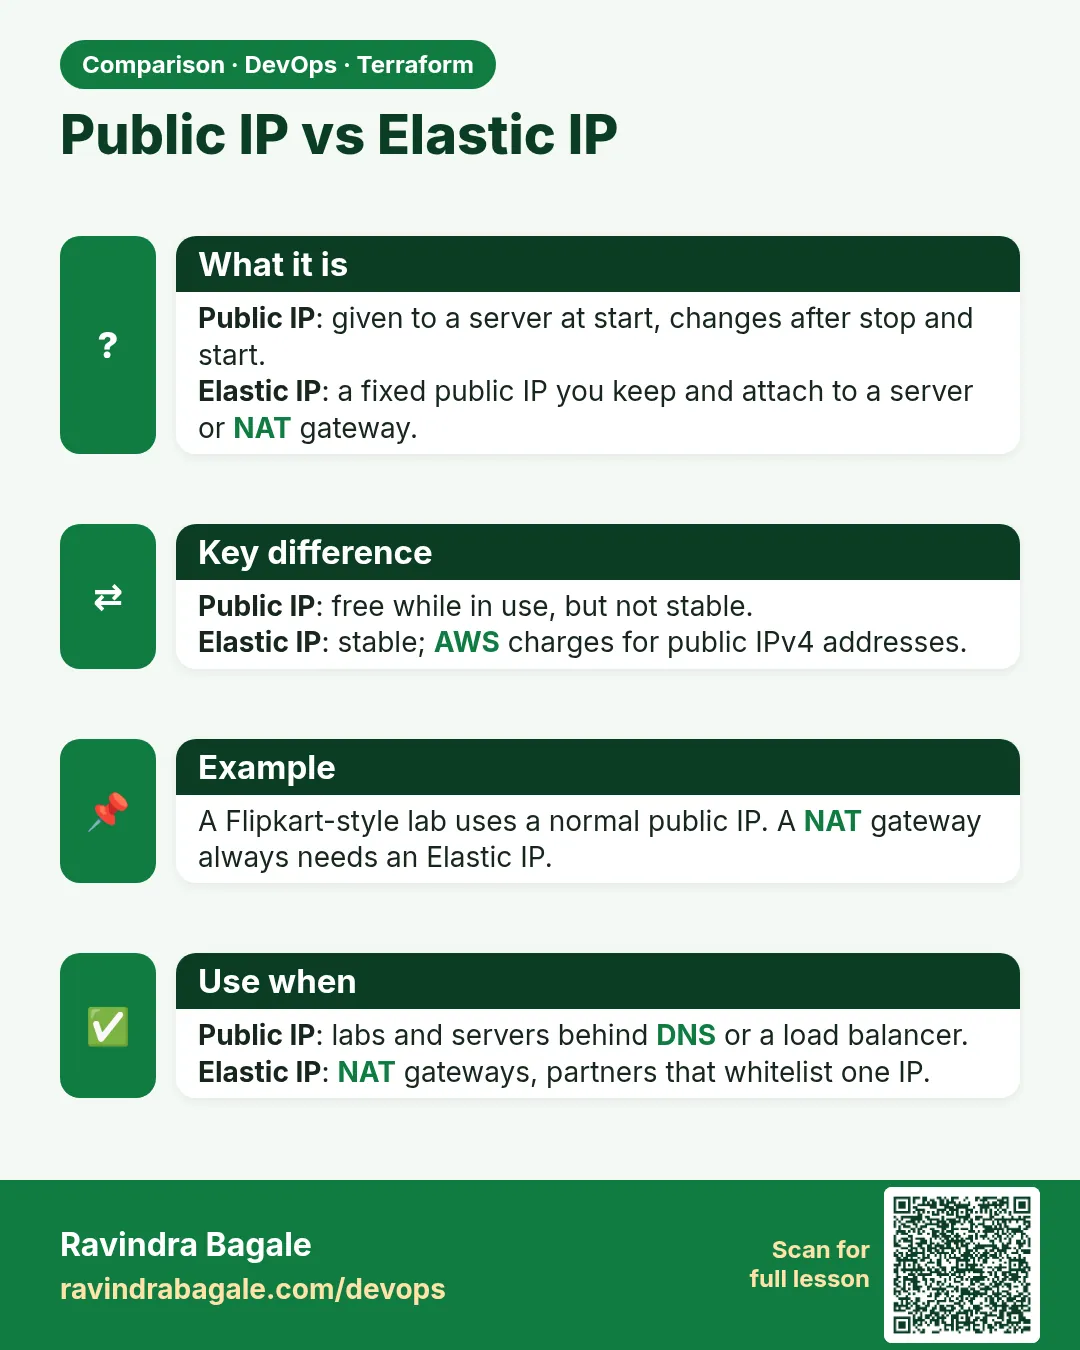 Comparison card 2 of 3: Public IP vs Elastic IP · Download PNG · Open card page
Lesson: Chapter 40: Terraform Real AWS Labs VPC EC2 nginx S3 and IAM Role
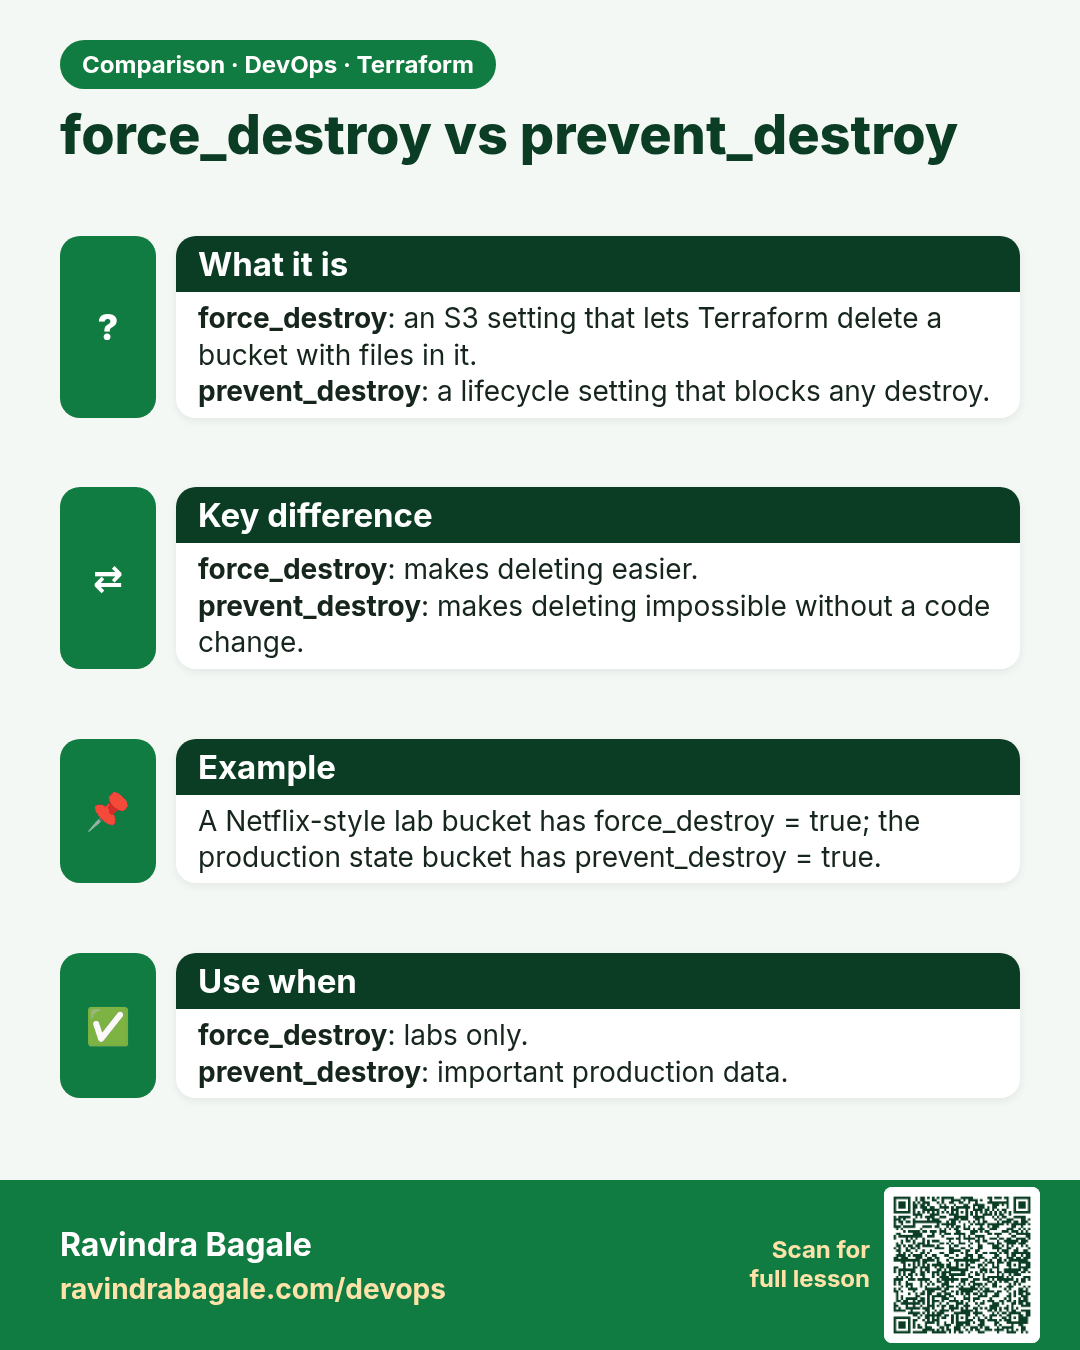
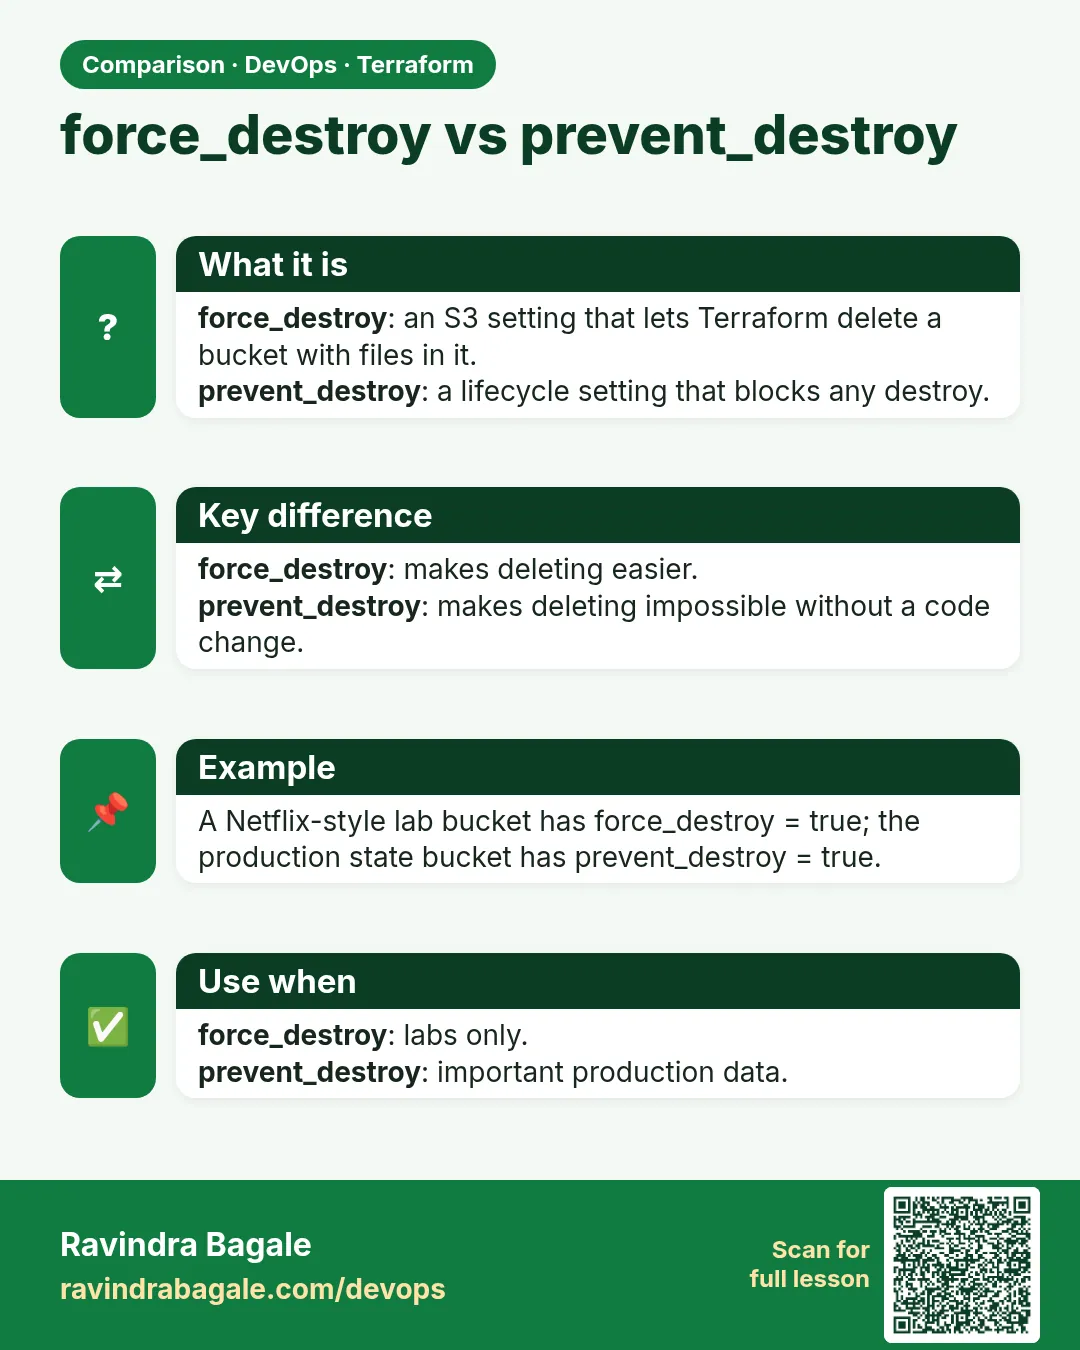 Comparison card 3 of 3: force_destroy vs prevent_destroy · Download PNG · Open card page
Lesson: Chapter 40: Terraform Real AWS Labs VPC EC2 nginx S3 and IAM Role