Ravindra BagaleCourses & study guides मराठी

Ravi Sir's Cards › DevOps

Chapter 46: Terraform 3-Tier Architecture Multi-AZ with ALBs Auto Scaling Bastion NAT and RDS: Cards

मराठी cards · Open the chapter

Revision cards
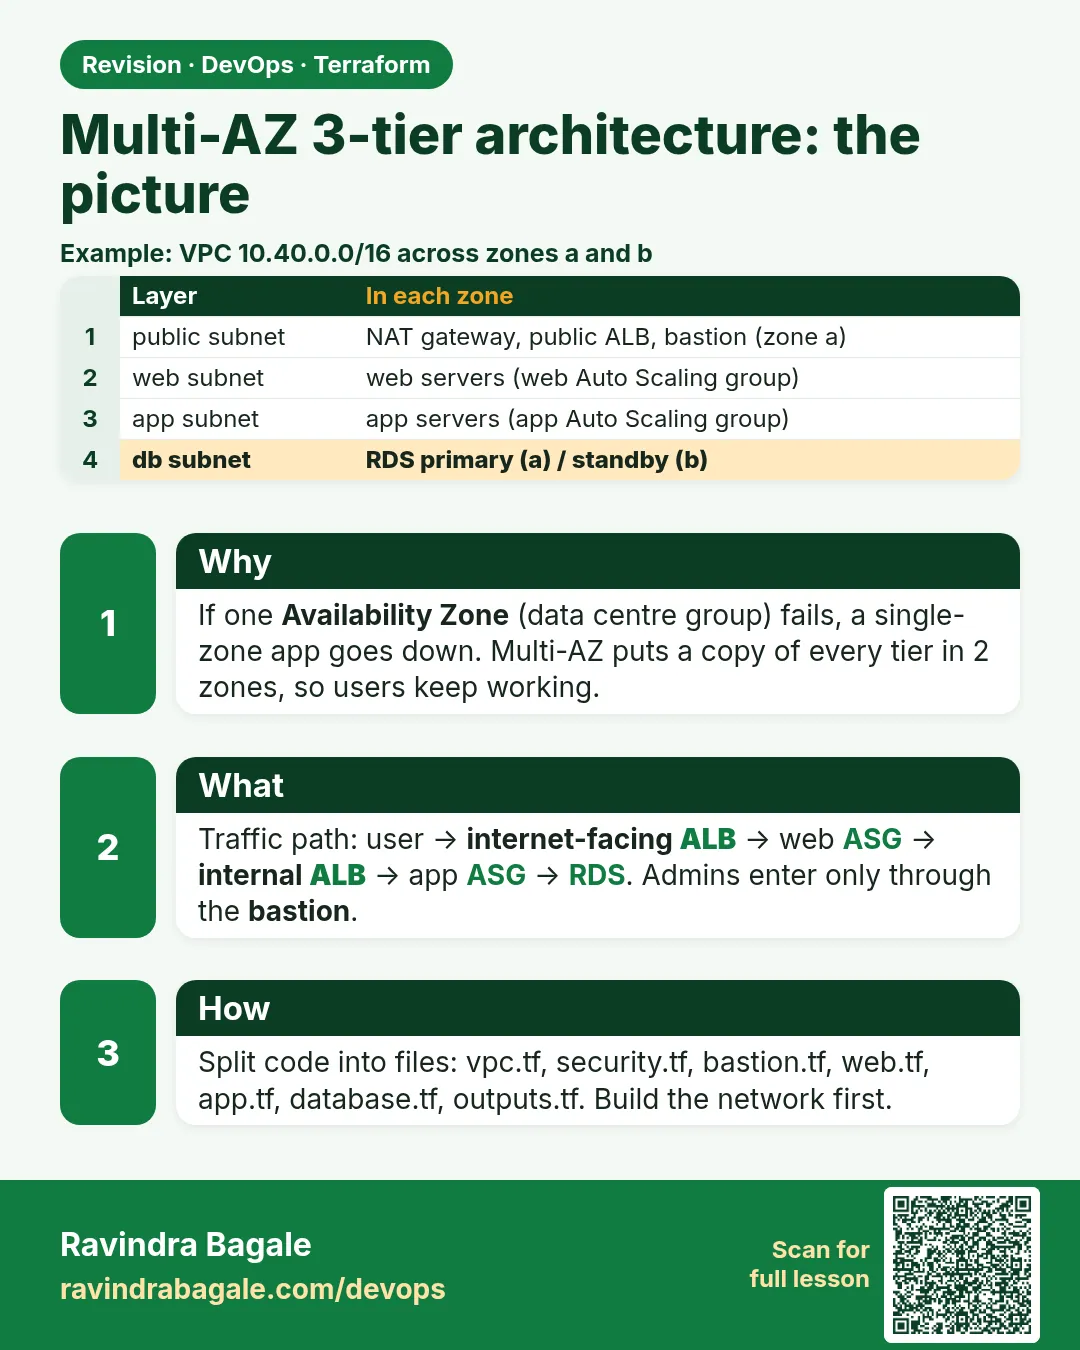
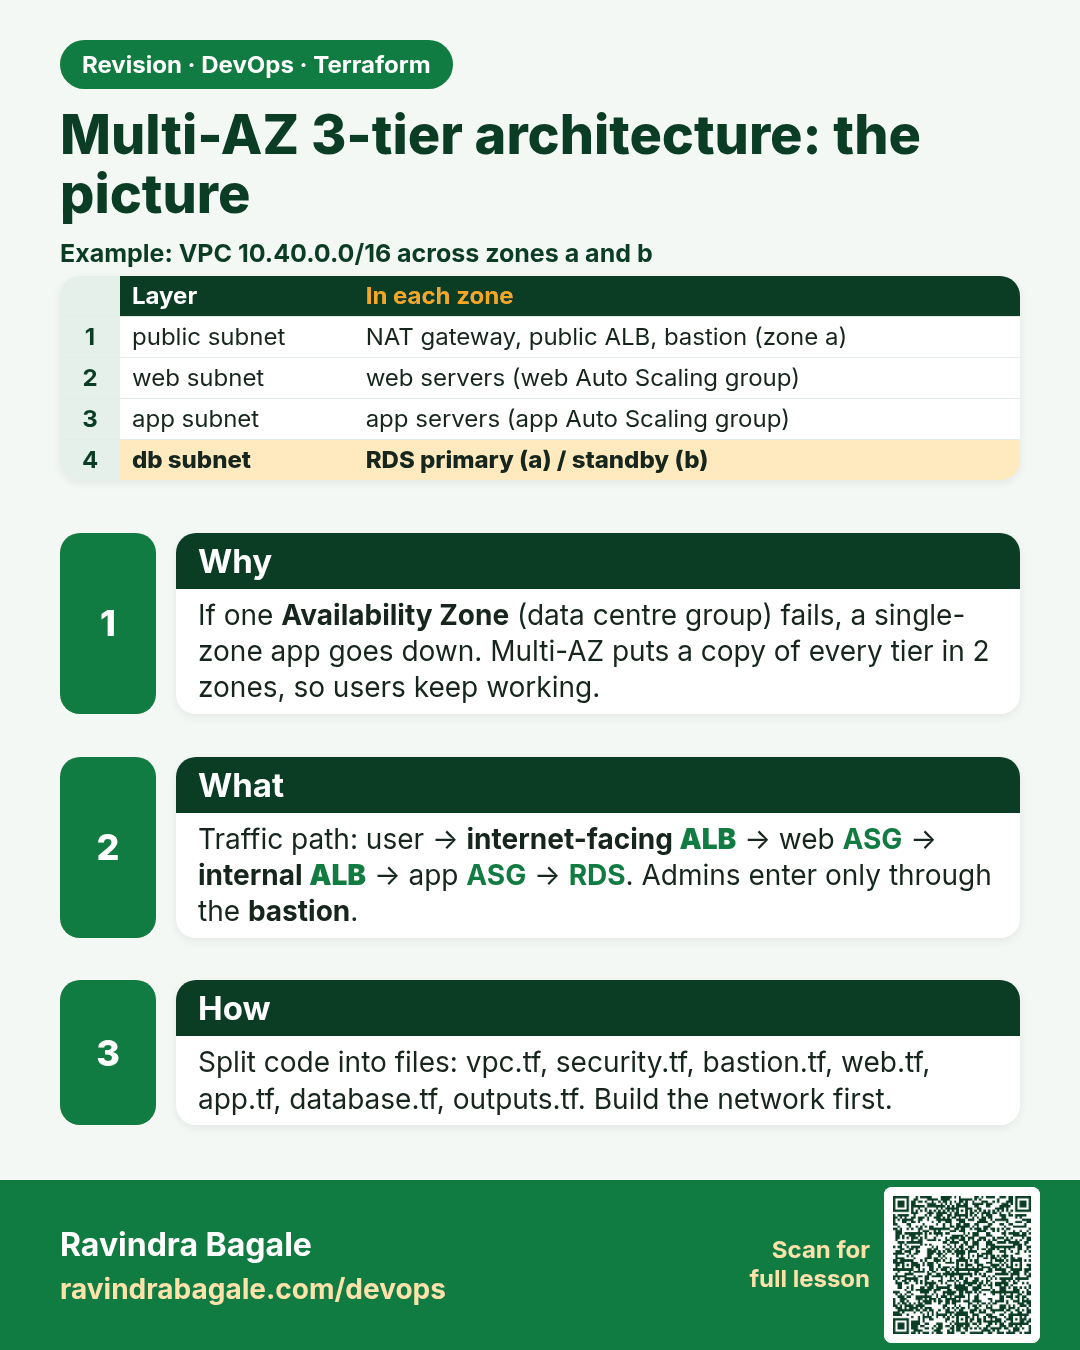
Multi-AZ 3-tier architecture: the picture. If one Availability Zone (data centre group) fails, a single-zone app goes down. Multi-AZ puts a copy of every tier in 2 zones, so users keep working.
Revision card 1 of 8: Multi-AZ 3-tier architecture: the picture · Download PNG · Open card page

Lesson: 46.1 Multi-AZ 3-tier architecture: the picture and the file layout
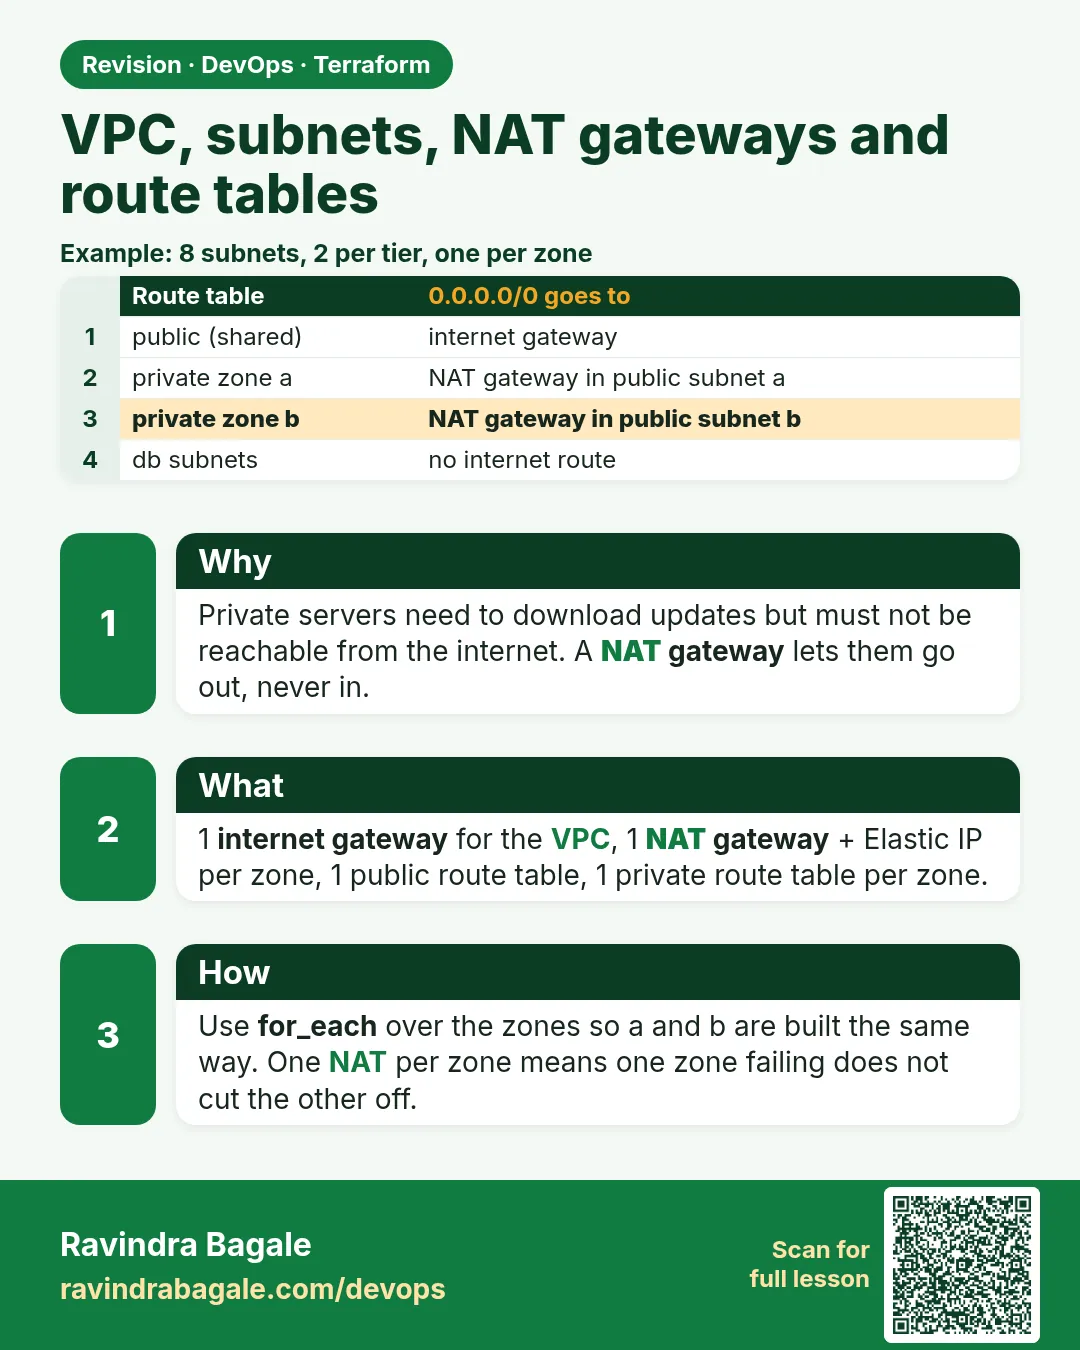
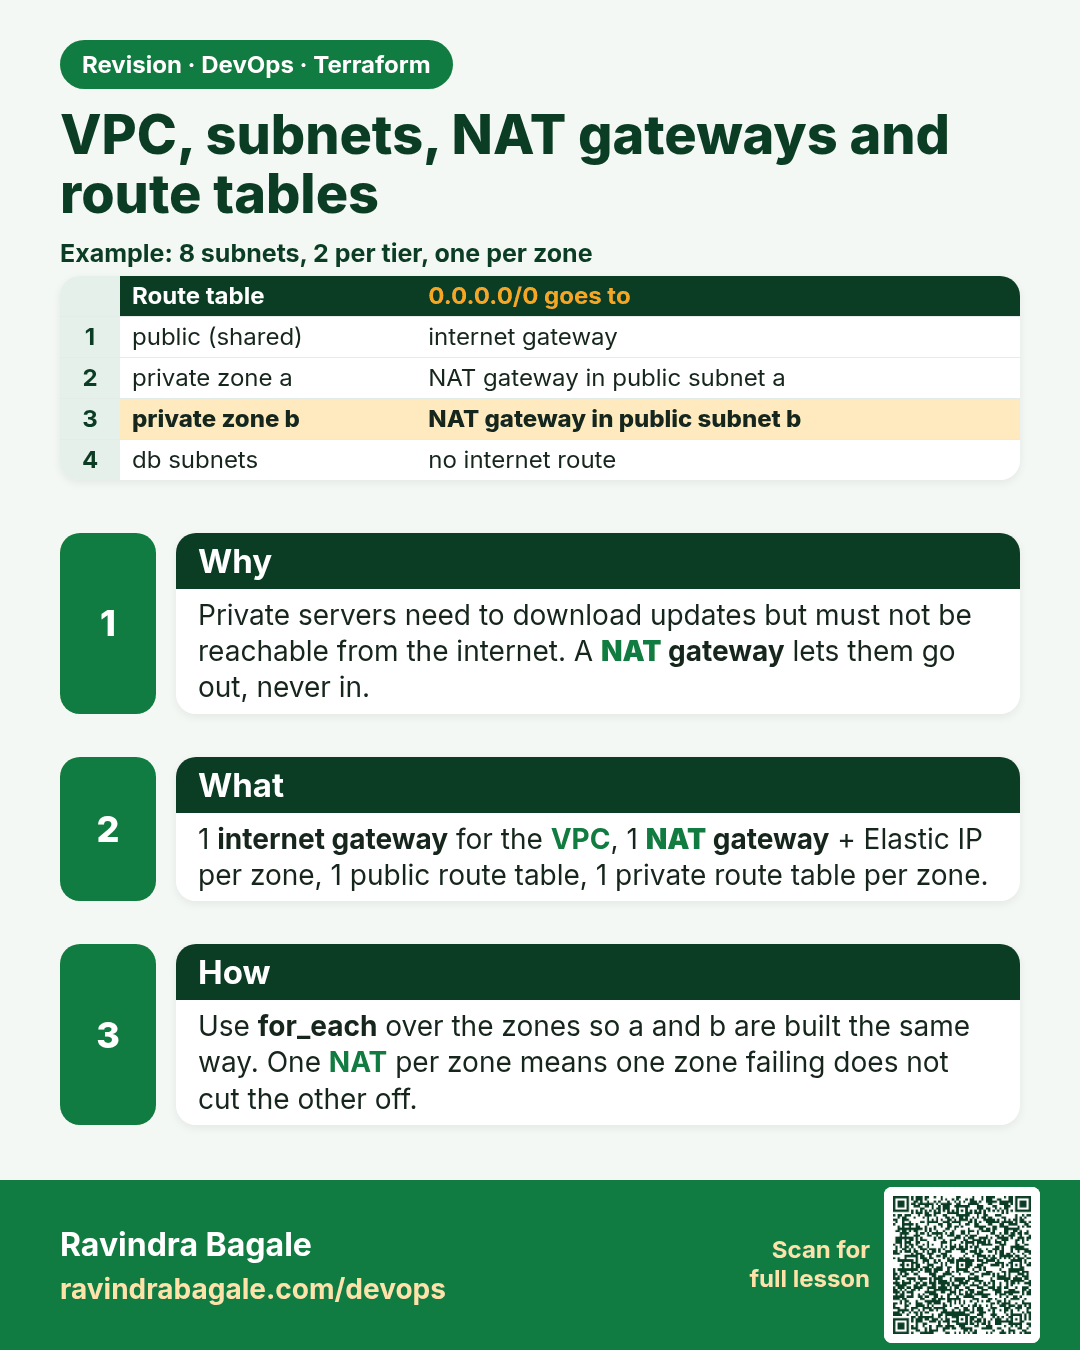
VPC, subnets, NAT gateways and route tables. Private servers need to download updates but must not be reachable from the internet. A NAT gateway lets them go out, never in.
Revision card 2 of 8: VPC, subnets, NAT gateways and route tables · Download PNG · Open card page

Lesson: 46.2 VPC, public and private subnets, internet gateway, NAT gateways and route tables
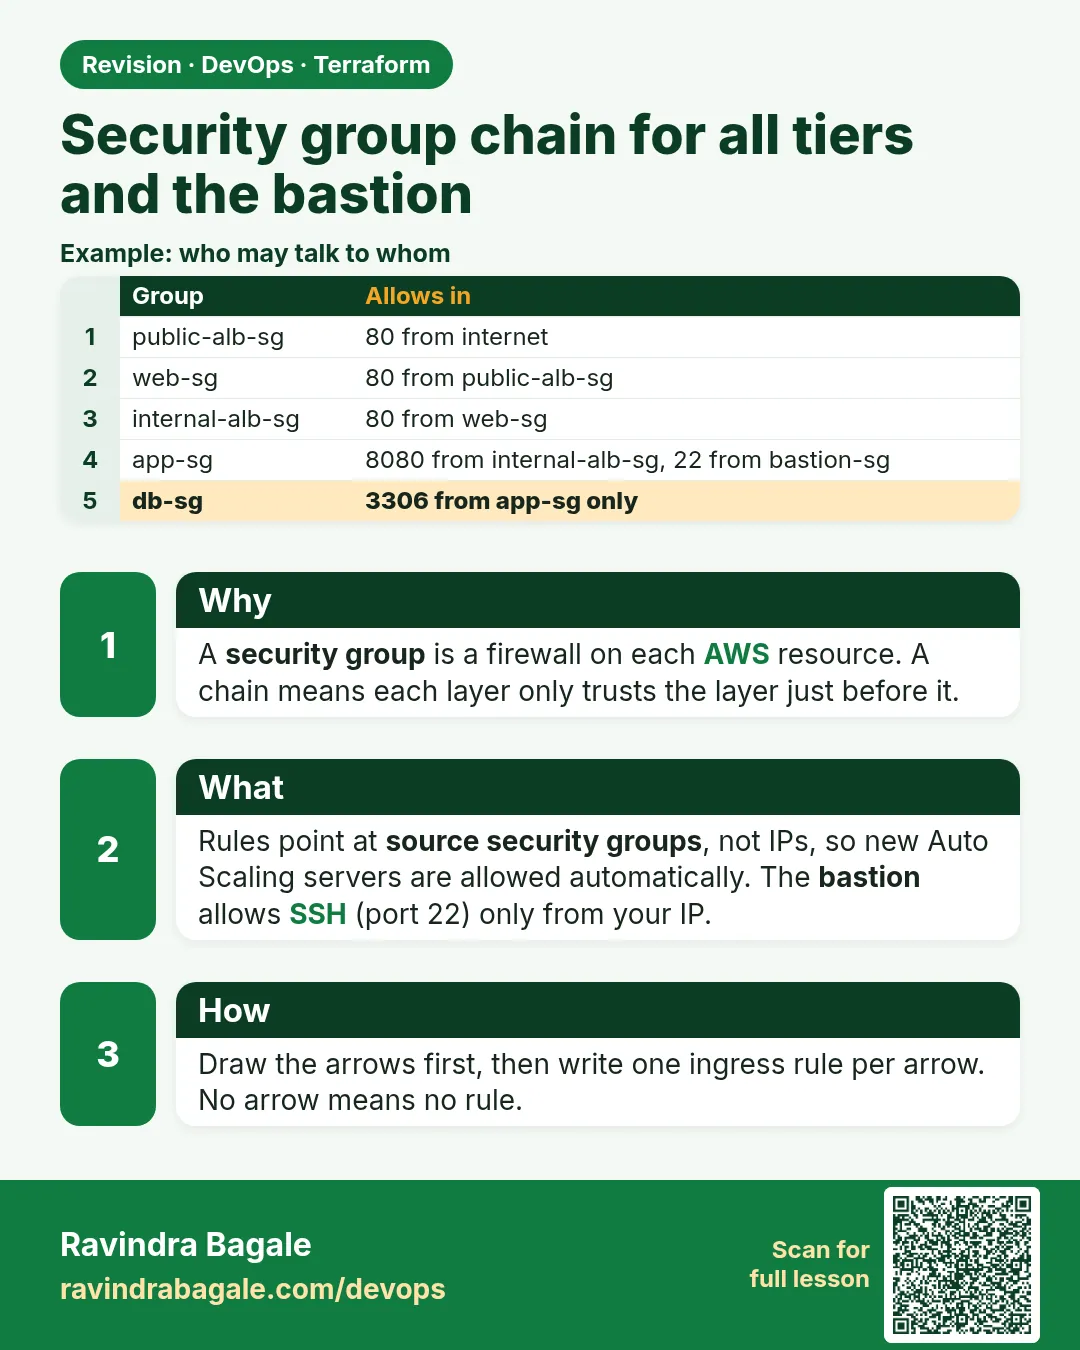
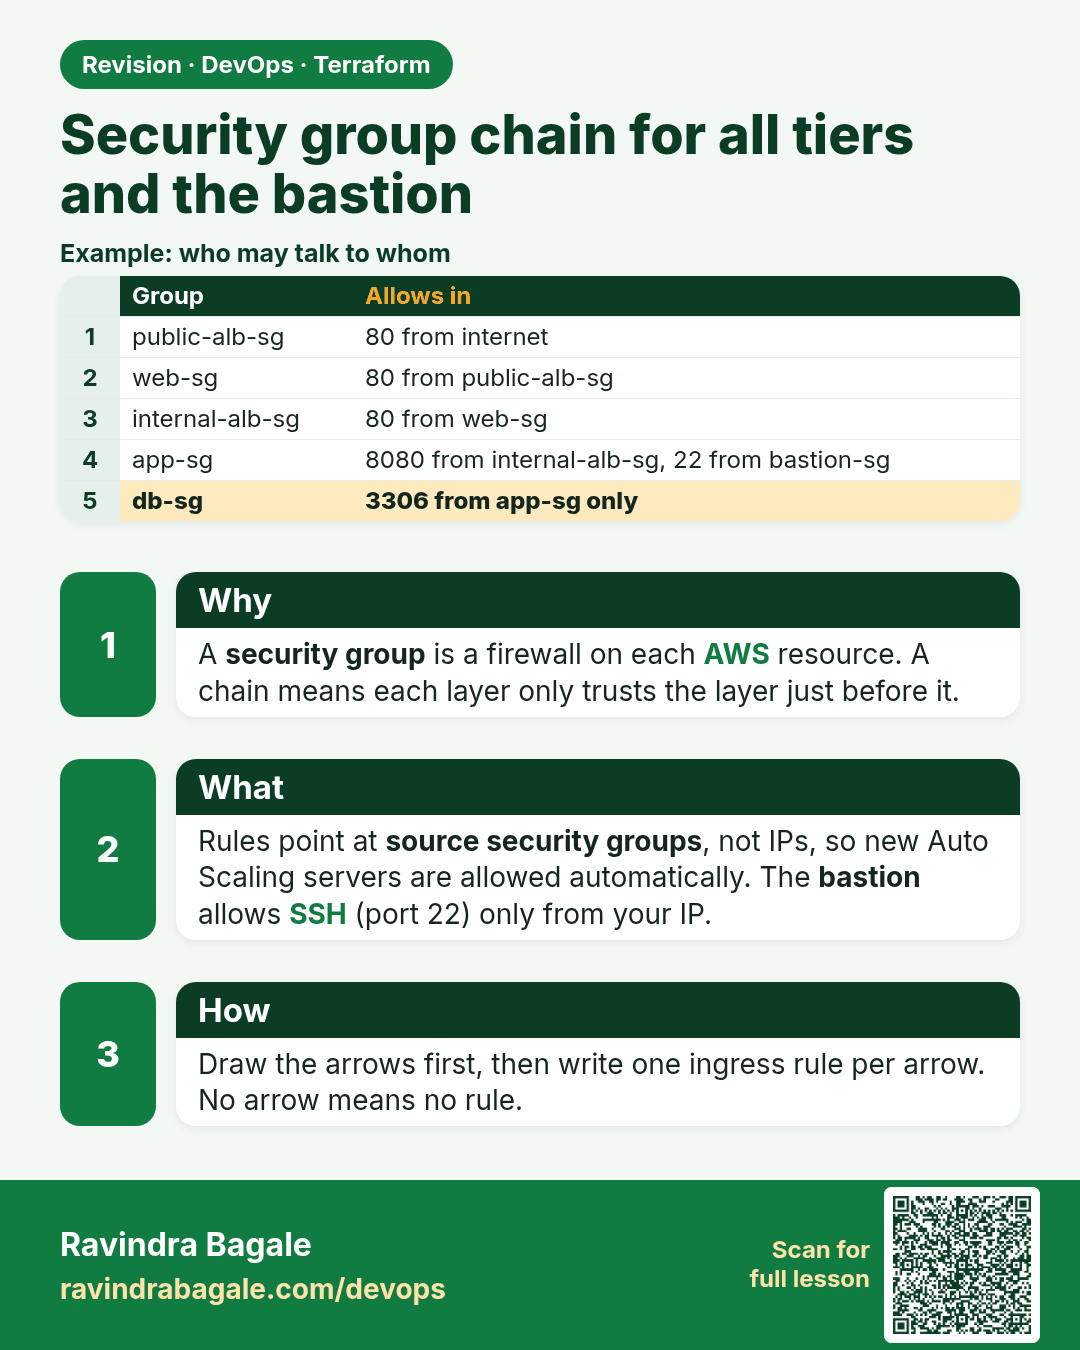
Security group chain for all tiers and the bastion. A security group is a firewall on each AWS resource. A chain means each layer only trusts the layer just before it.
Revision card 3 of 8: Security group chain for all tiers and the bastion · Download PNG · Open card page

Lesson: 46.3 Security group chain for all tiers and the bastion
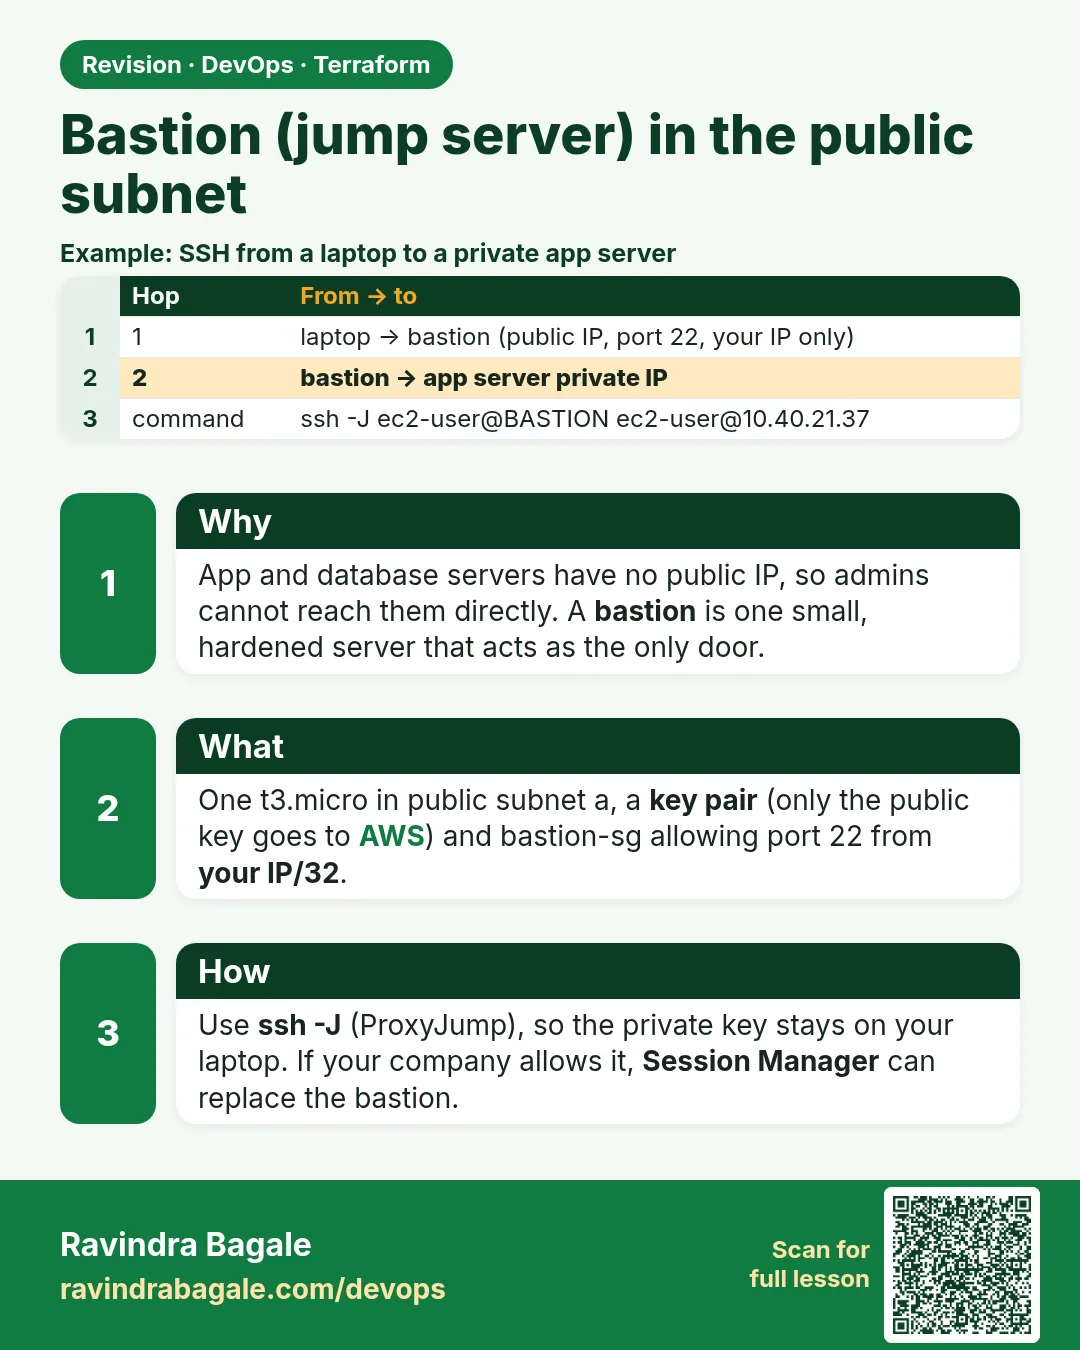
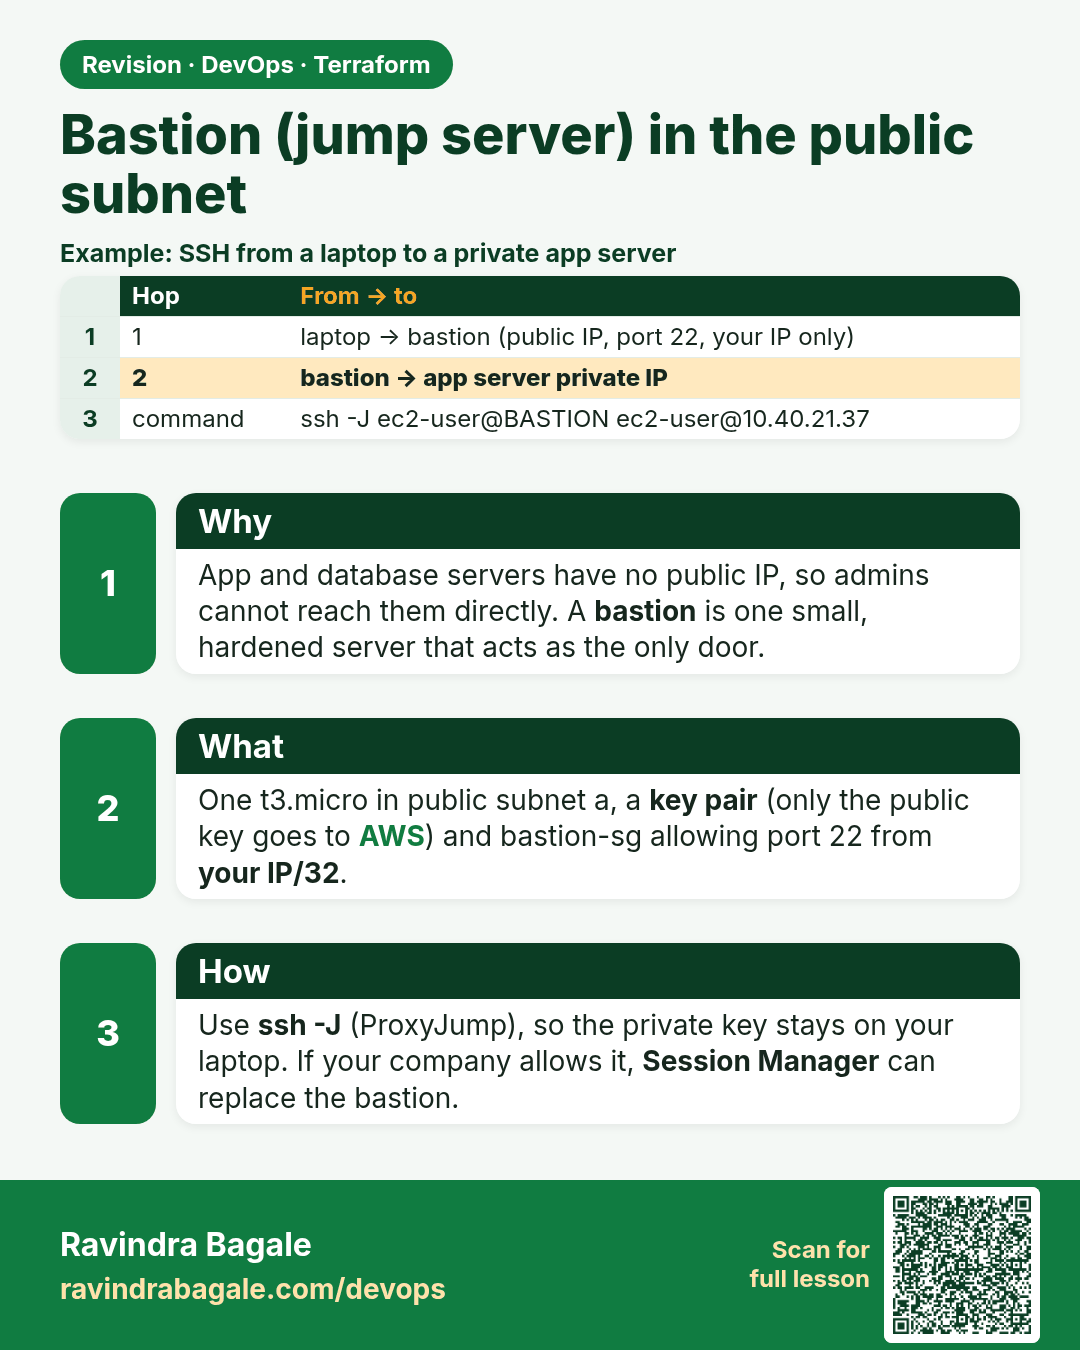
Bastion (jump server) in the public subnet. App and database servers have no public IP, so admins cannot reach them directly. A bastion is one small, hardened server that acts as the only door.
Revision card 4 of 8: Bastion (jump server) in the public subnet · Download PNG · Open card page

Lesson: 46.4 Bastion jump server in the public subnet
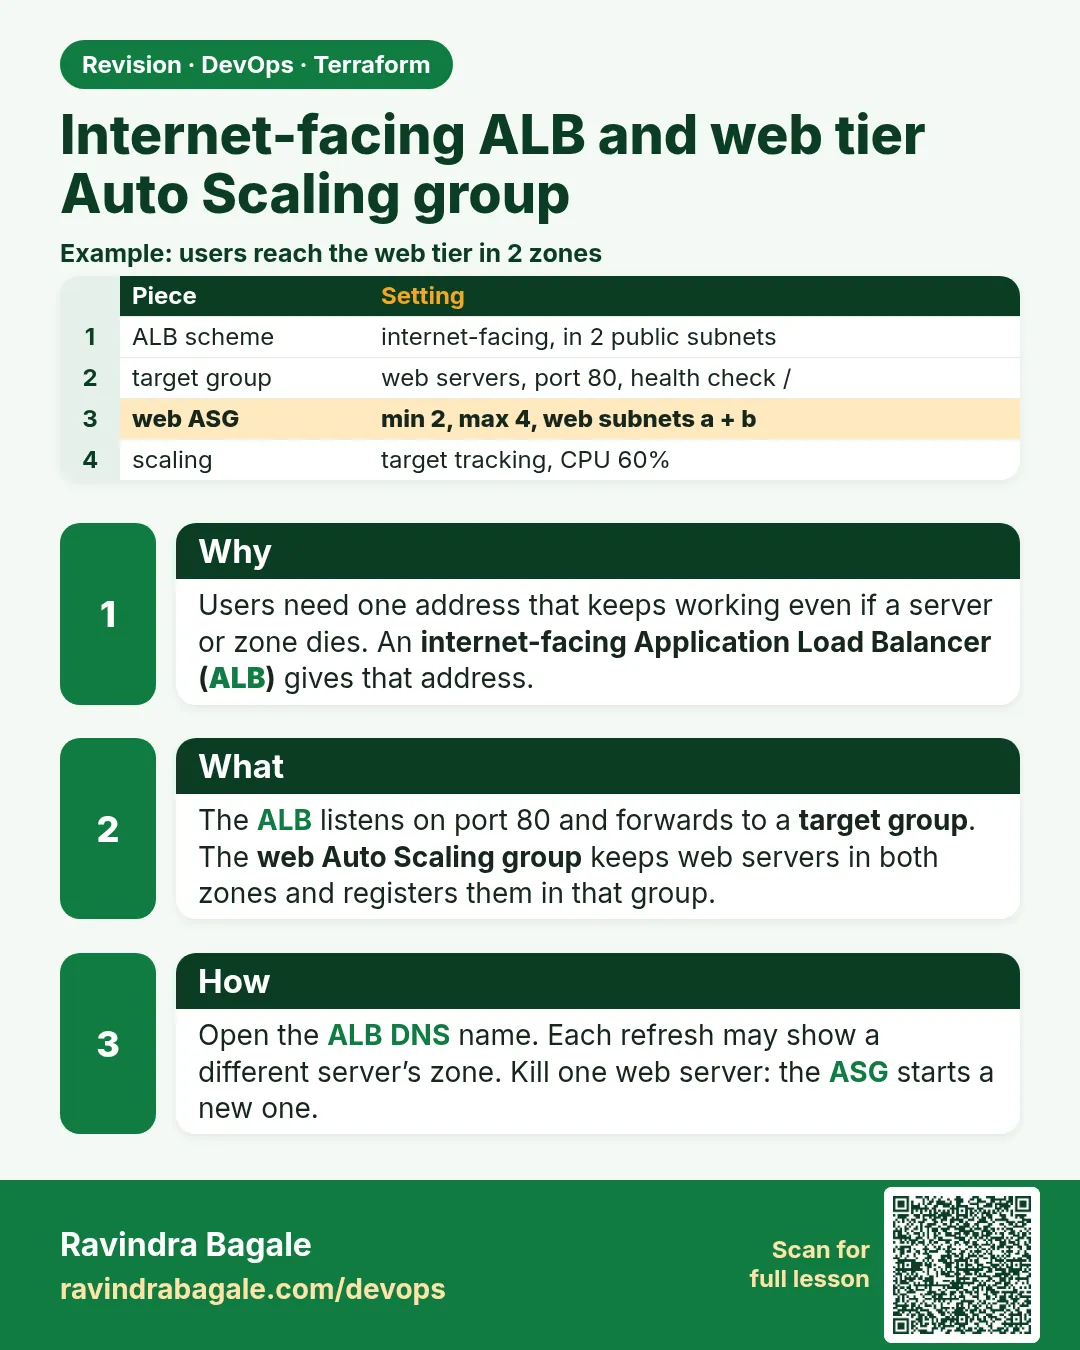
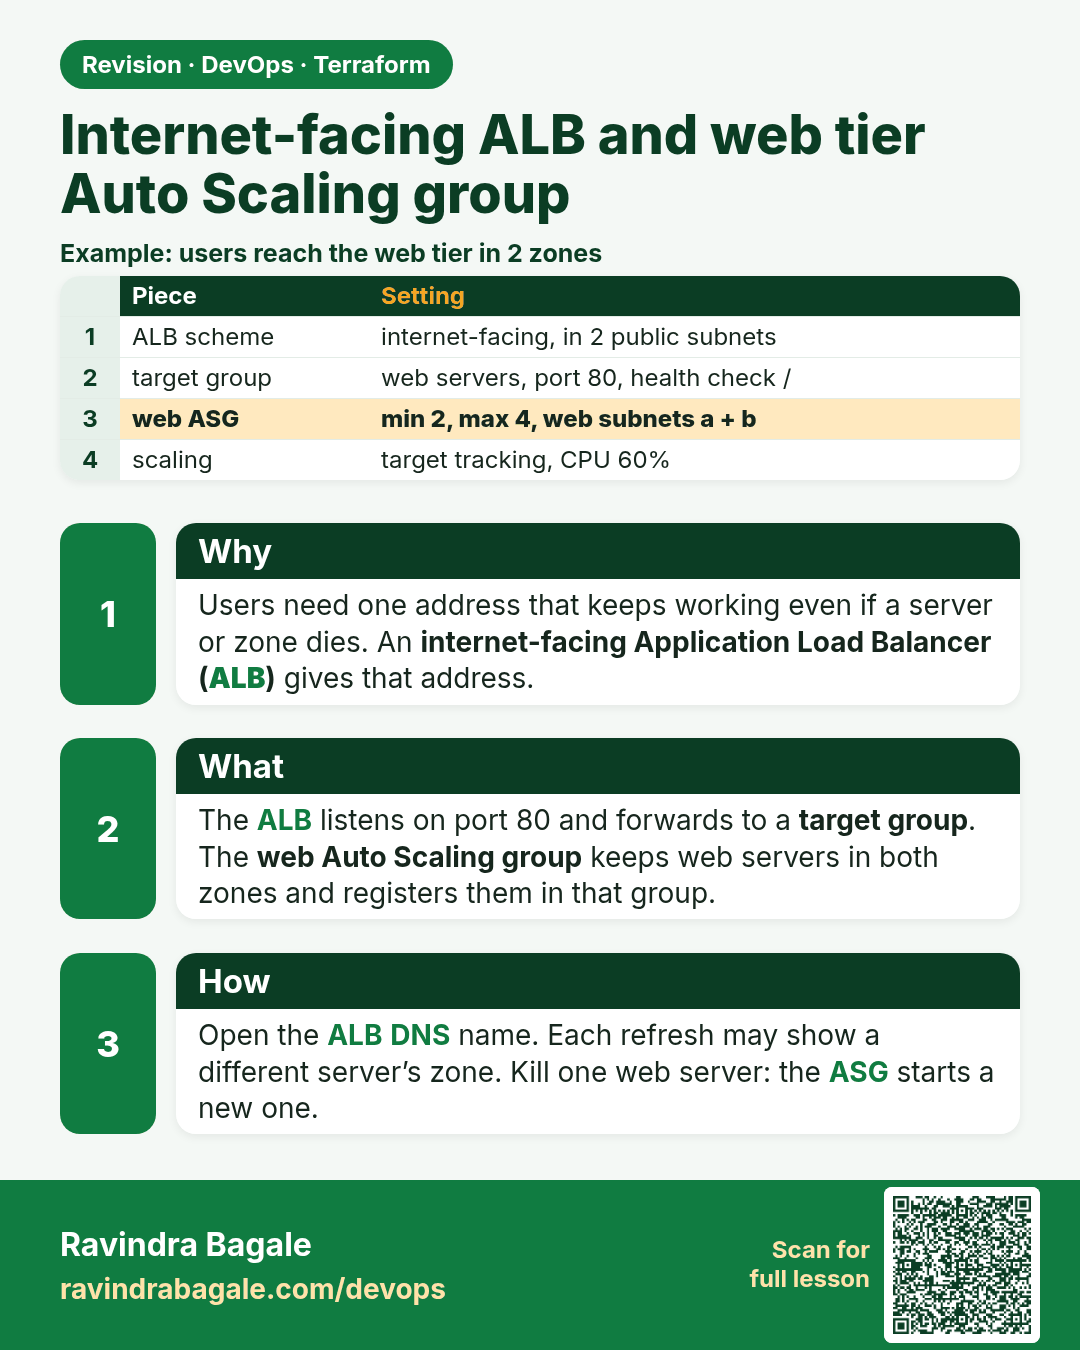
Internet-facing ALB and web tier Auto Scaling group. Users need one address that keeps working even if a server or zone dies. An internet-facing Application Load Balancer (ALB) gives that address.
Revision card 5 of 8: Internet-facing ALB and web tier Auto Scaling group · Download PNG · Open card page

Lesson: 46.5 Internet-facing ALB and web tier Auto Scaling group
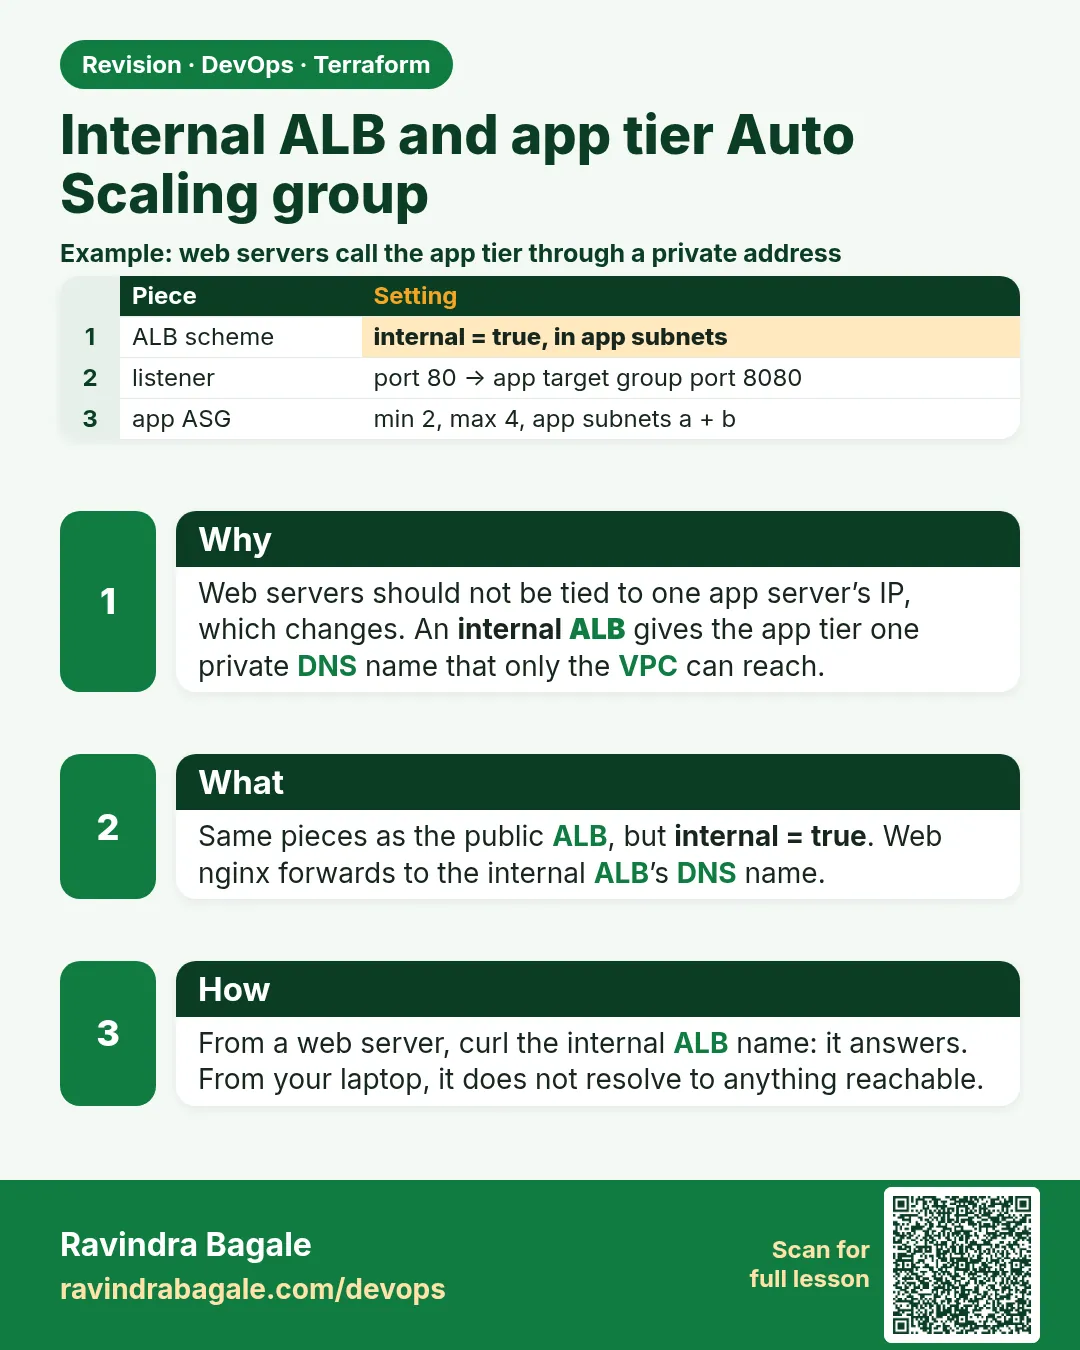
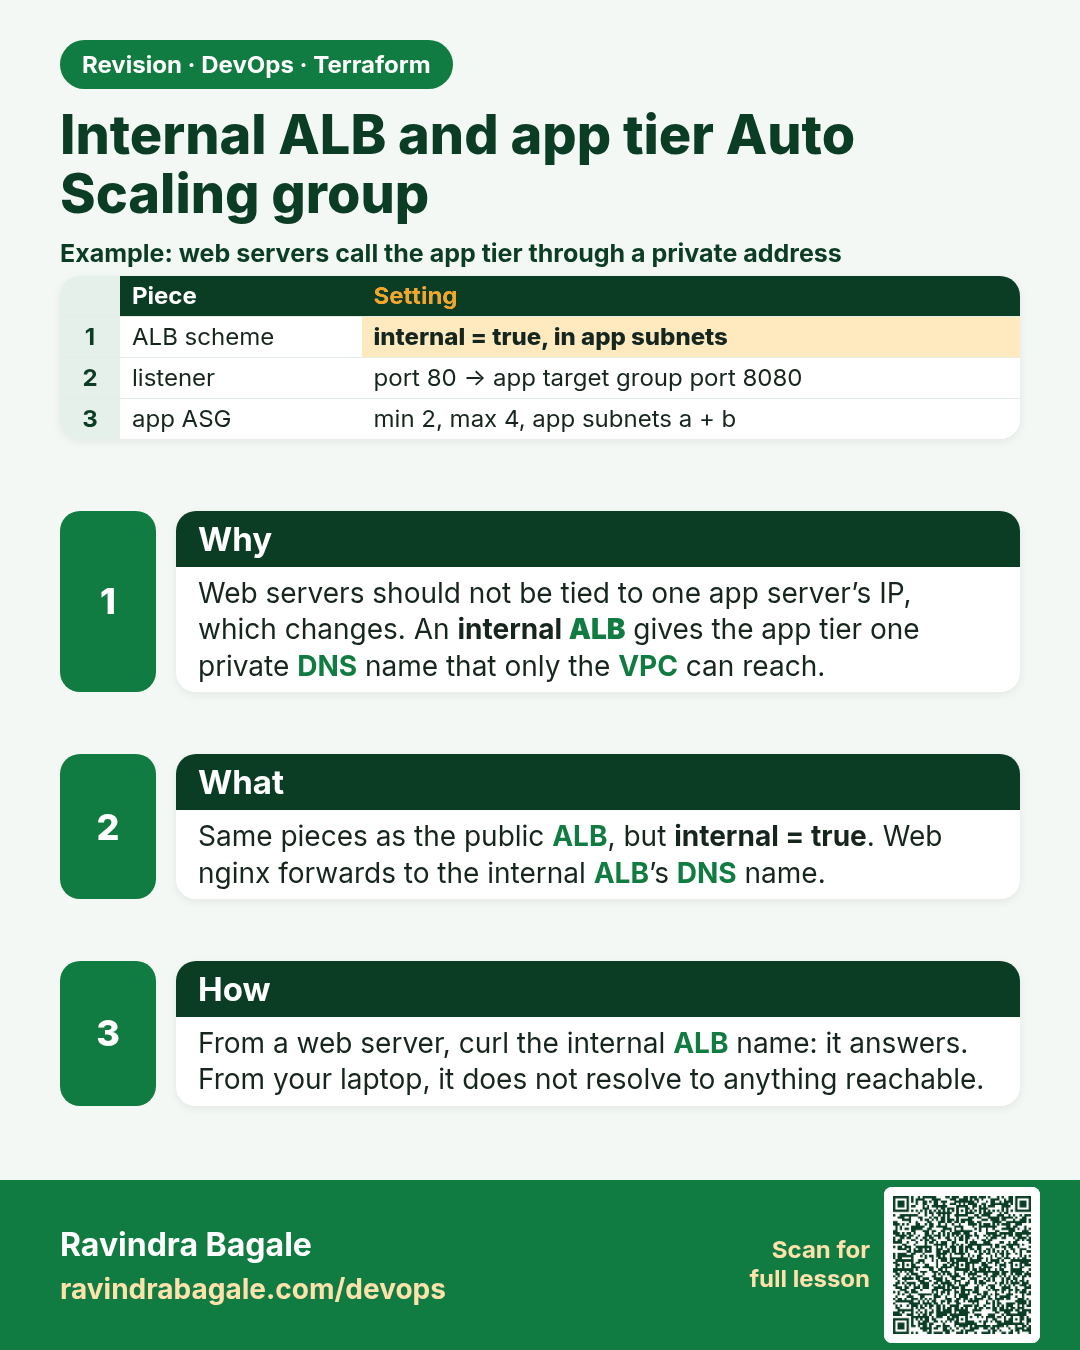
Internal ALB and app tier Auto Scaling group. Web servers should not be tied to one app server’s IP, which changes. An internal ALB gives the app tier one private DNS name that only the VPC can reach.
Revision card 6 of 8: Internal ALB and app tier Auto Scaling group · Download PNG · Open card page

Lesson: 46.6 Internal ALB and app tier Auto Scaling group
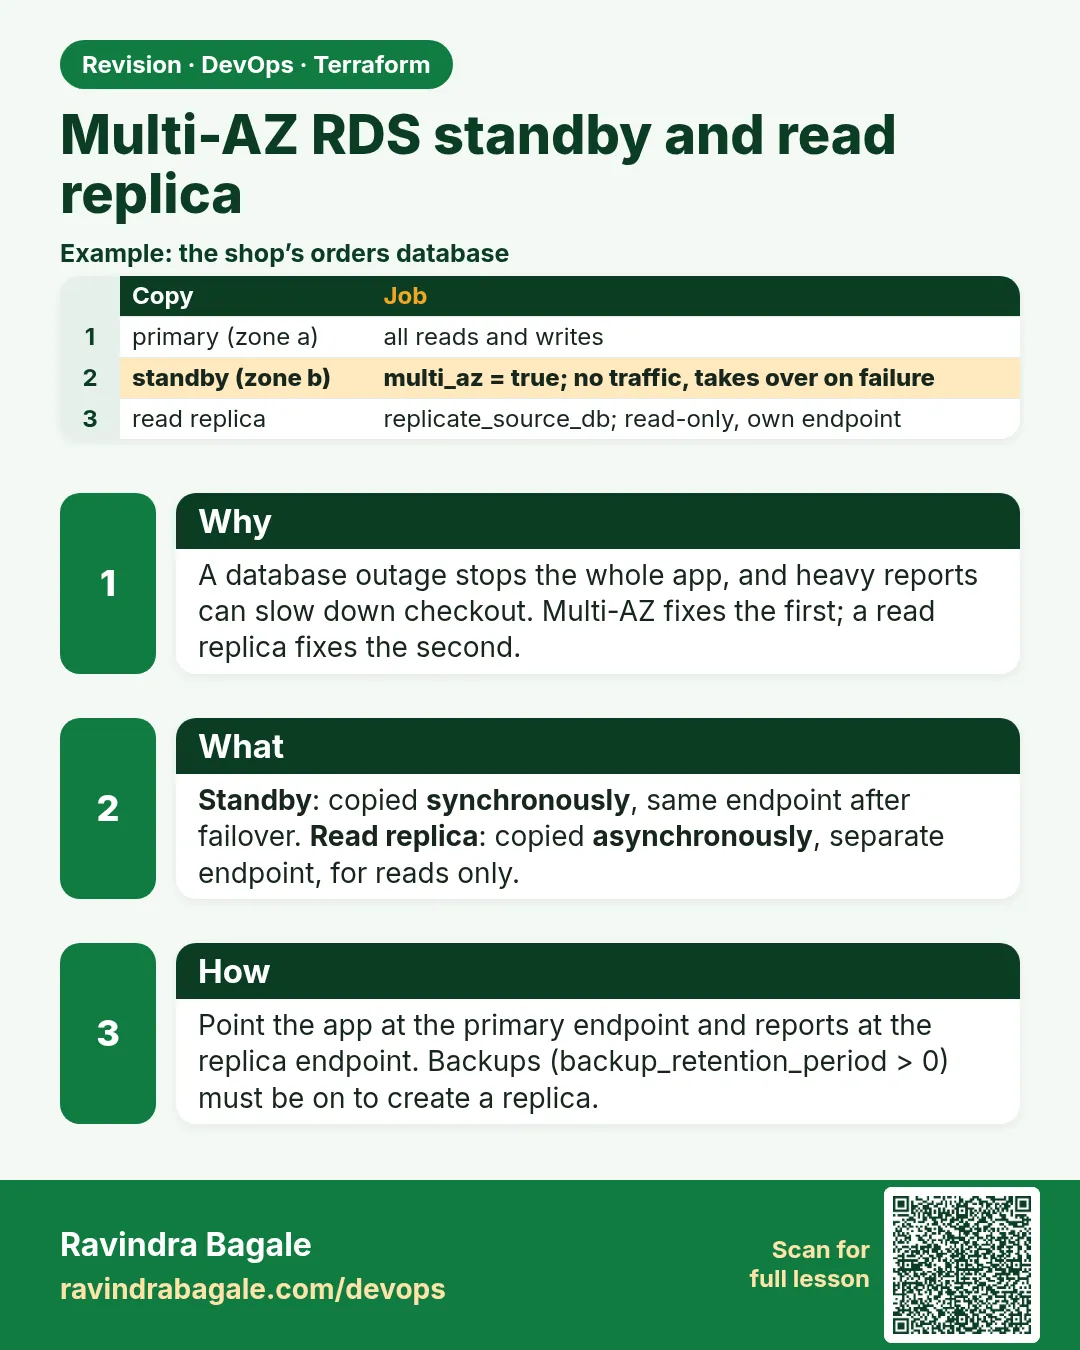
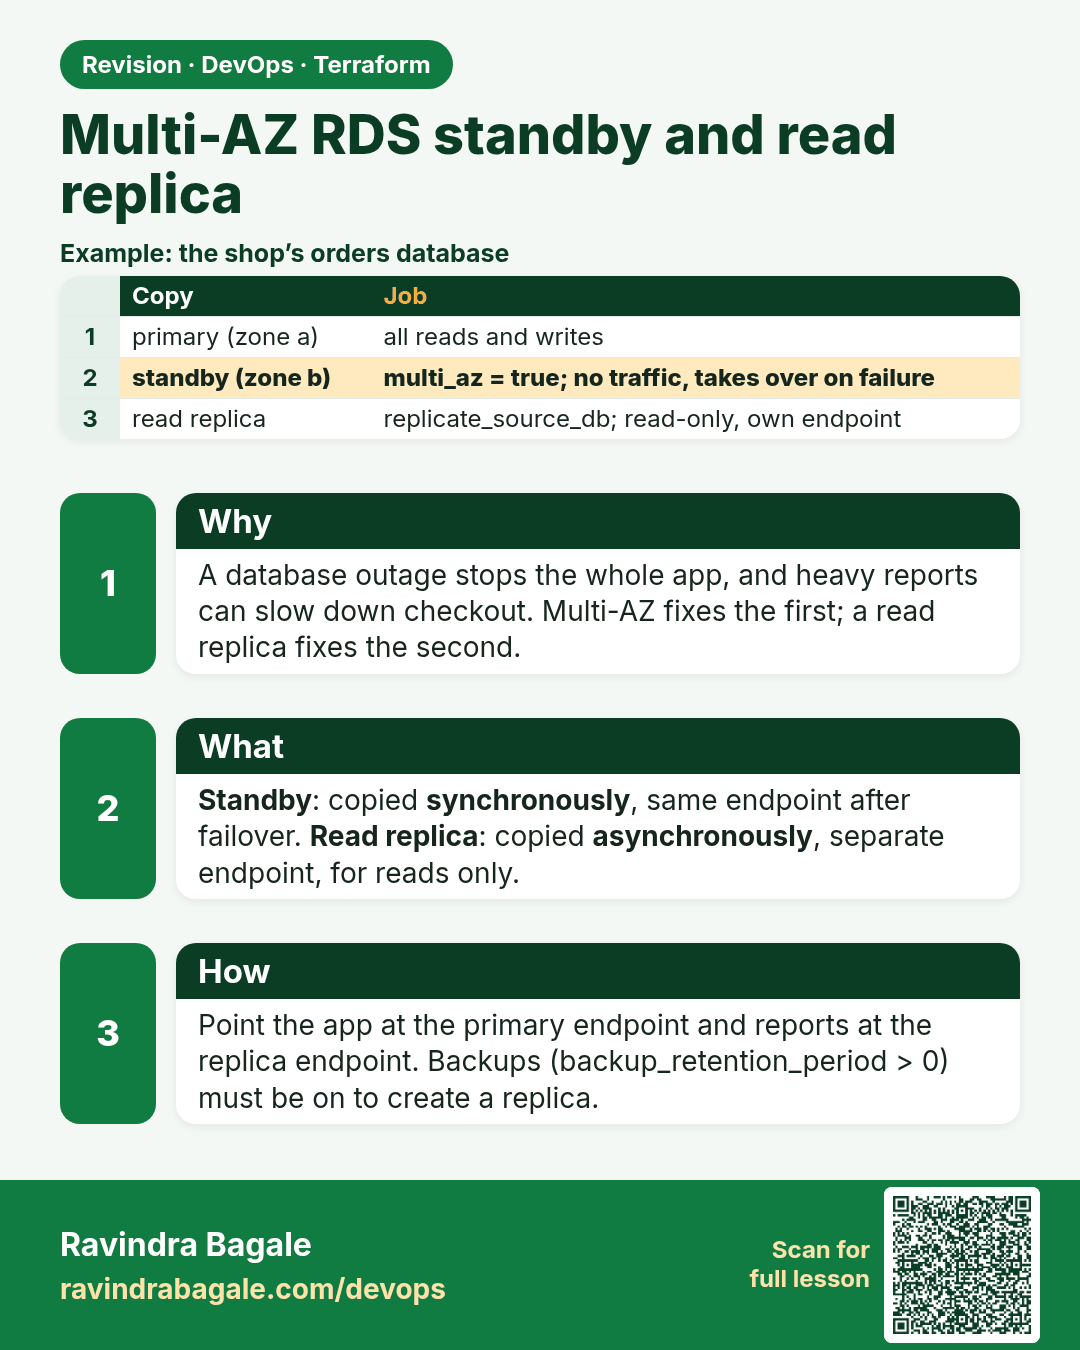
Multi-AZ RDS standby and read replica. A database outage stops the whole app, and heavy reports can slow down checkout. Multi-AZ fixes the first; a read replica fixes the second.
Revision card 7 of 8: Multi-AZ RDS standby and read replica · Download PNG · Open card page

Lesson: 46.7 DB subnet group, Multi-AZ RDS standby and read replica
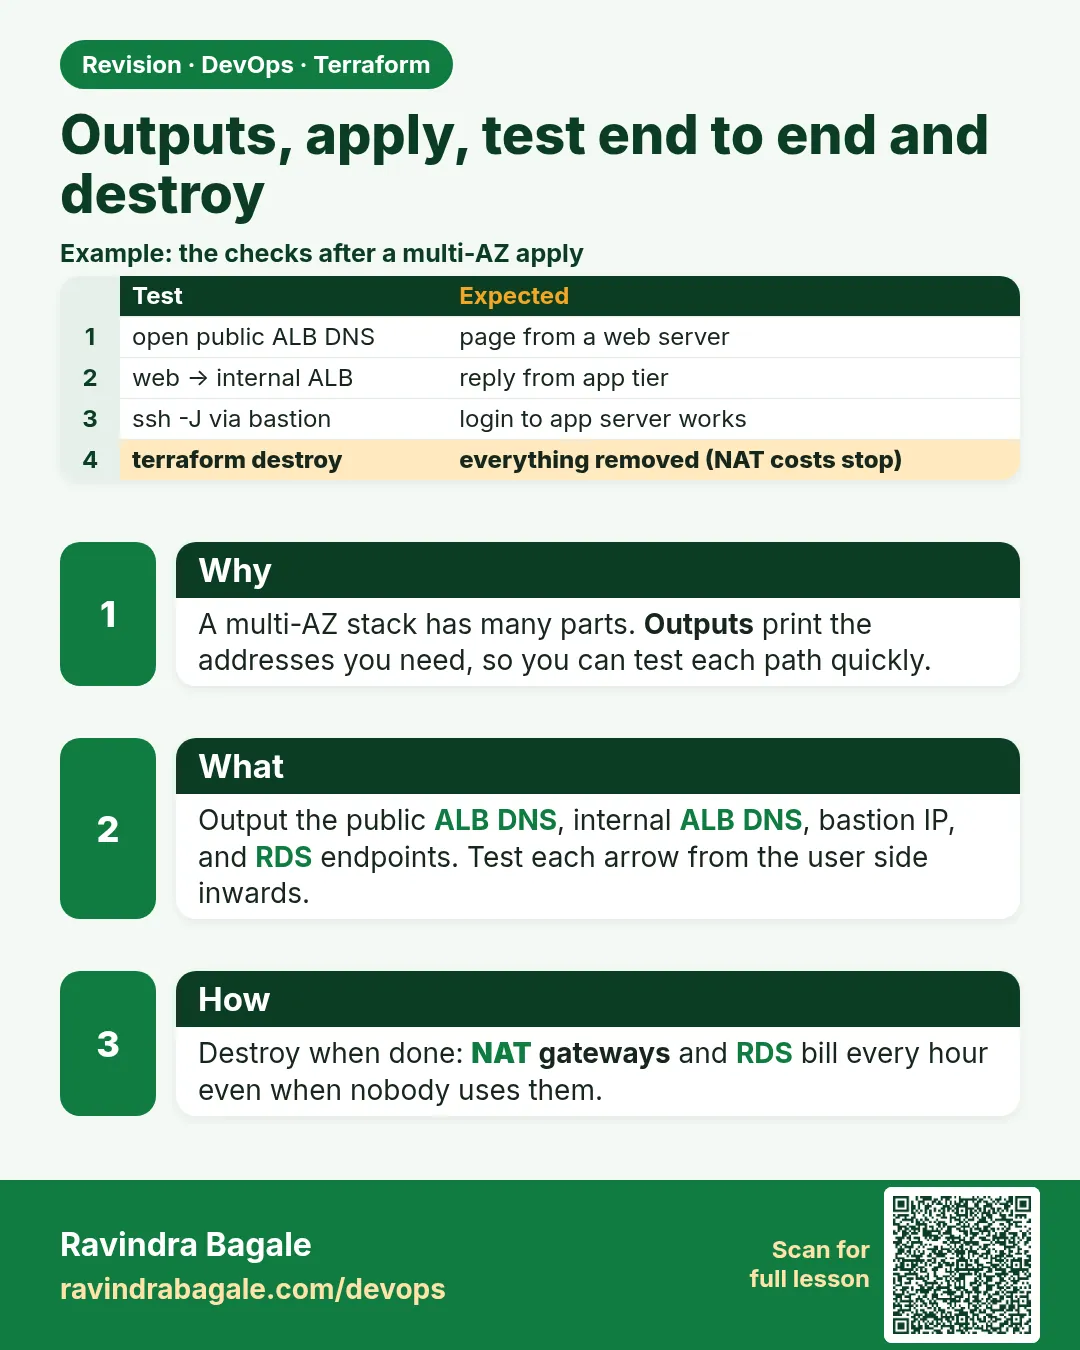
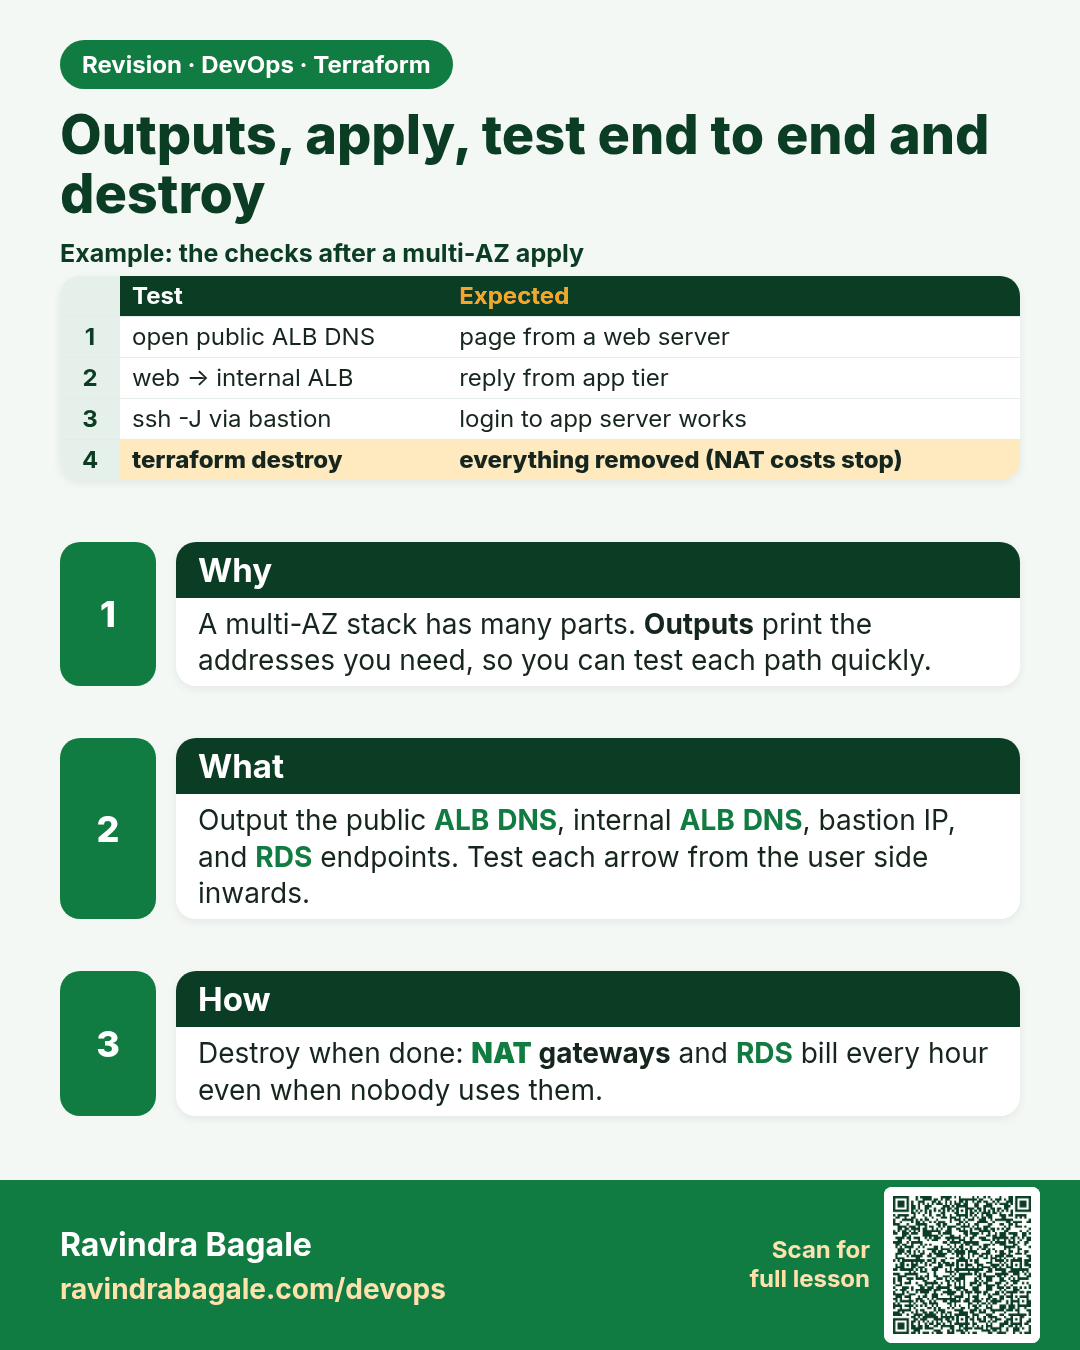
Outputs, apply, test end to end and destroy. A multi-AZ stack has many parts. Outputs print the addresses you need, so you can test each path quickly.
Revision card 8 of 8: Outputs, apply, test end to end and destroy · Download PNG · Open card page

Lesson: 46.8 Outputs, apply, test end to end and destroy

Interview cards
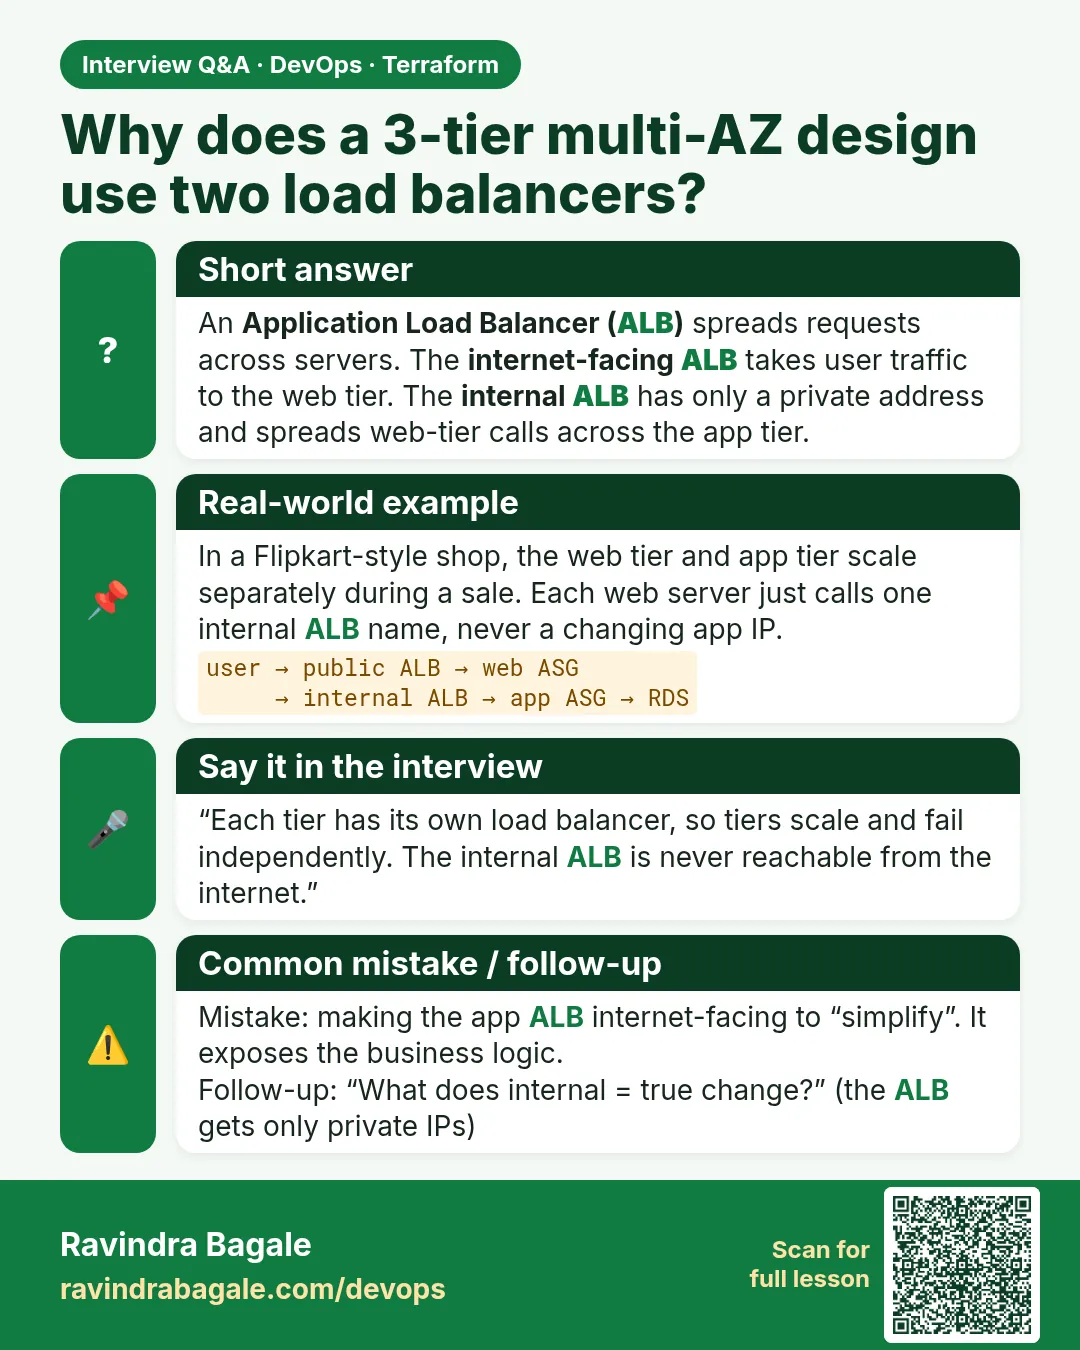
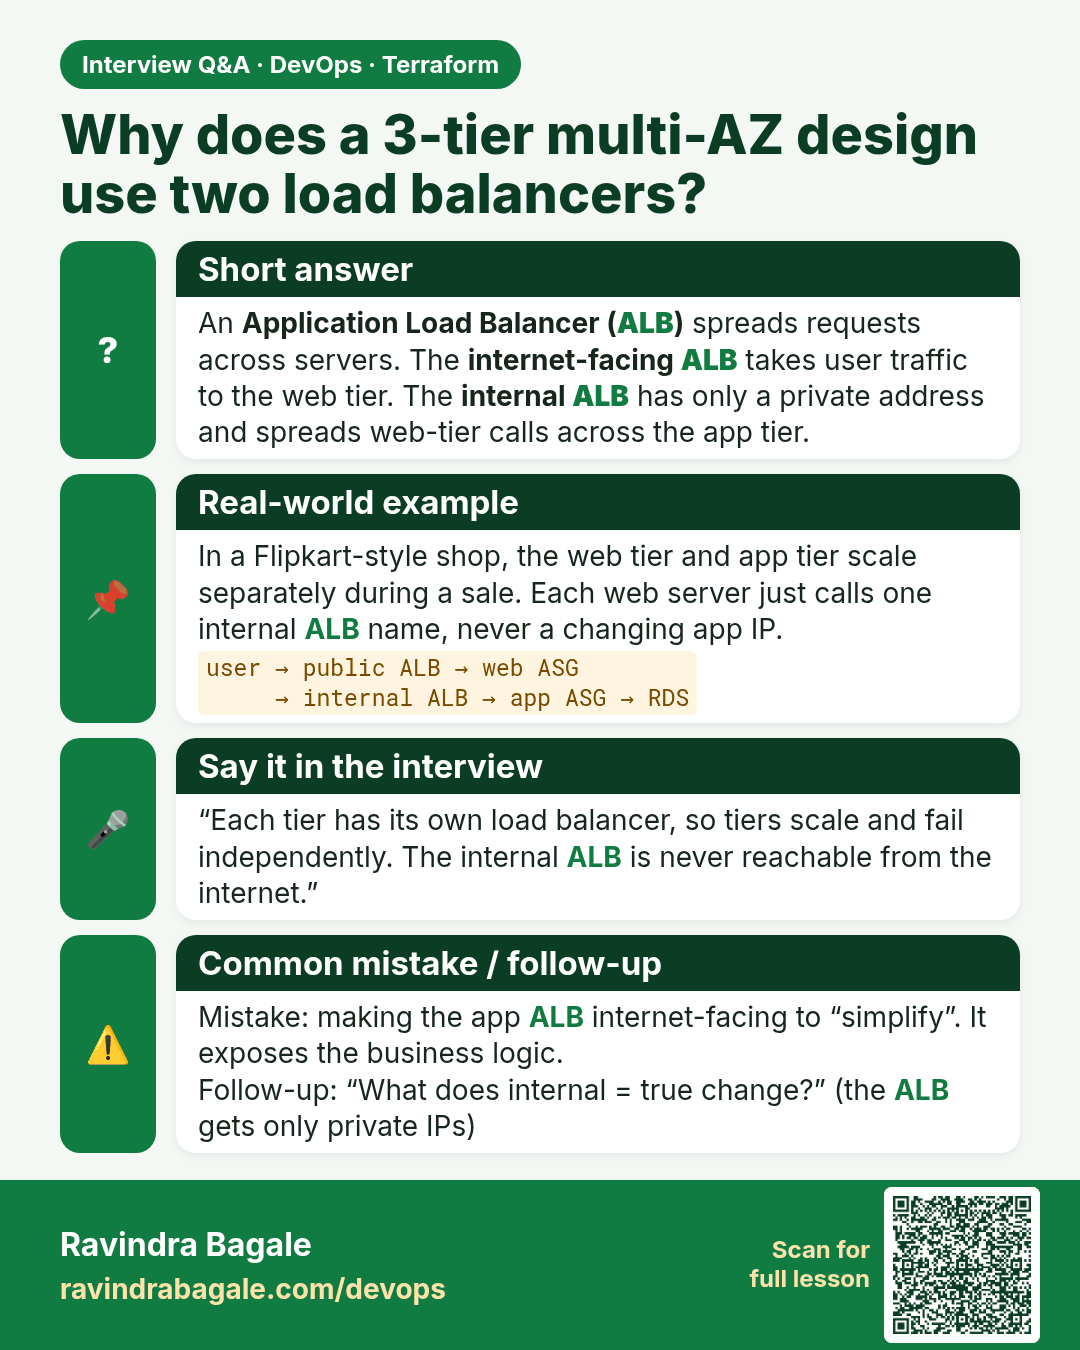
Why does a 3-tier multi-AZ design use two load balancers? An Application Load Balancer (ALB) spreads requests across servers. The internet-facing ALB takes user traffic to the web tier. The internal ALB has only a private address and spreads web-tier calls across the app tier.
Interview card 1 of 8: Why does a 3-tier multi-AZ design use two load balancers? · Download PNG · Open card page

Lesson: 46.1 Multi-AZ 3-tier architecture: the picture and the file layout
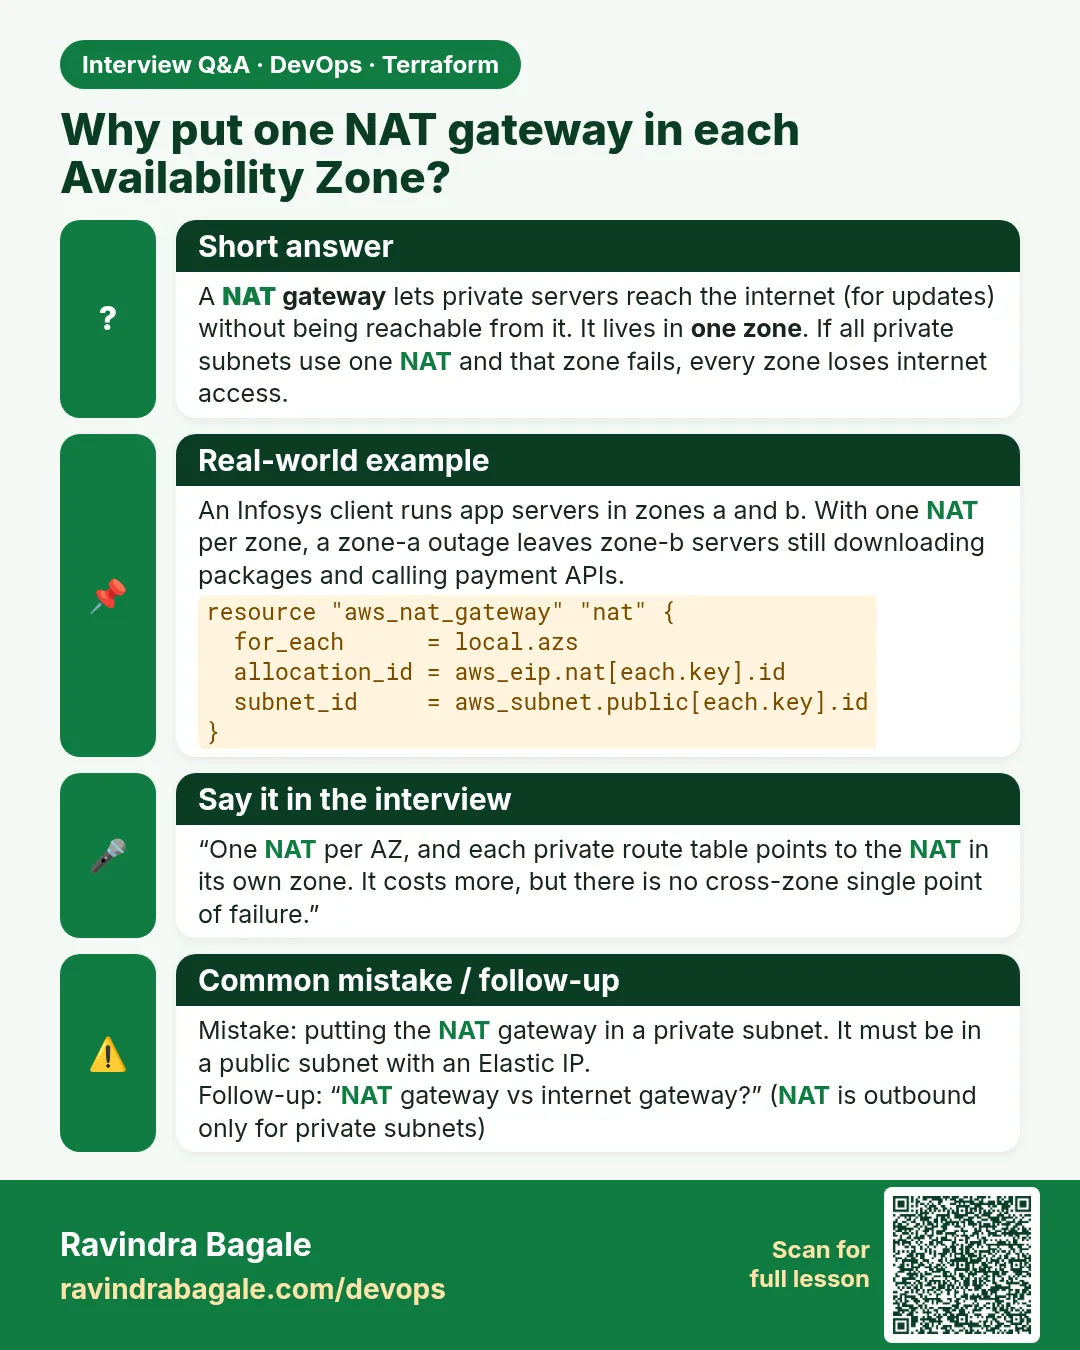
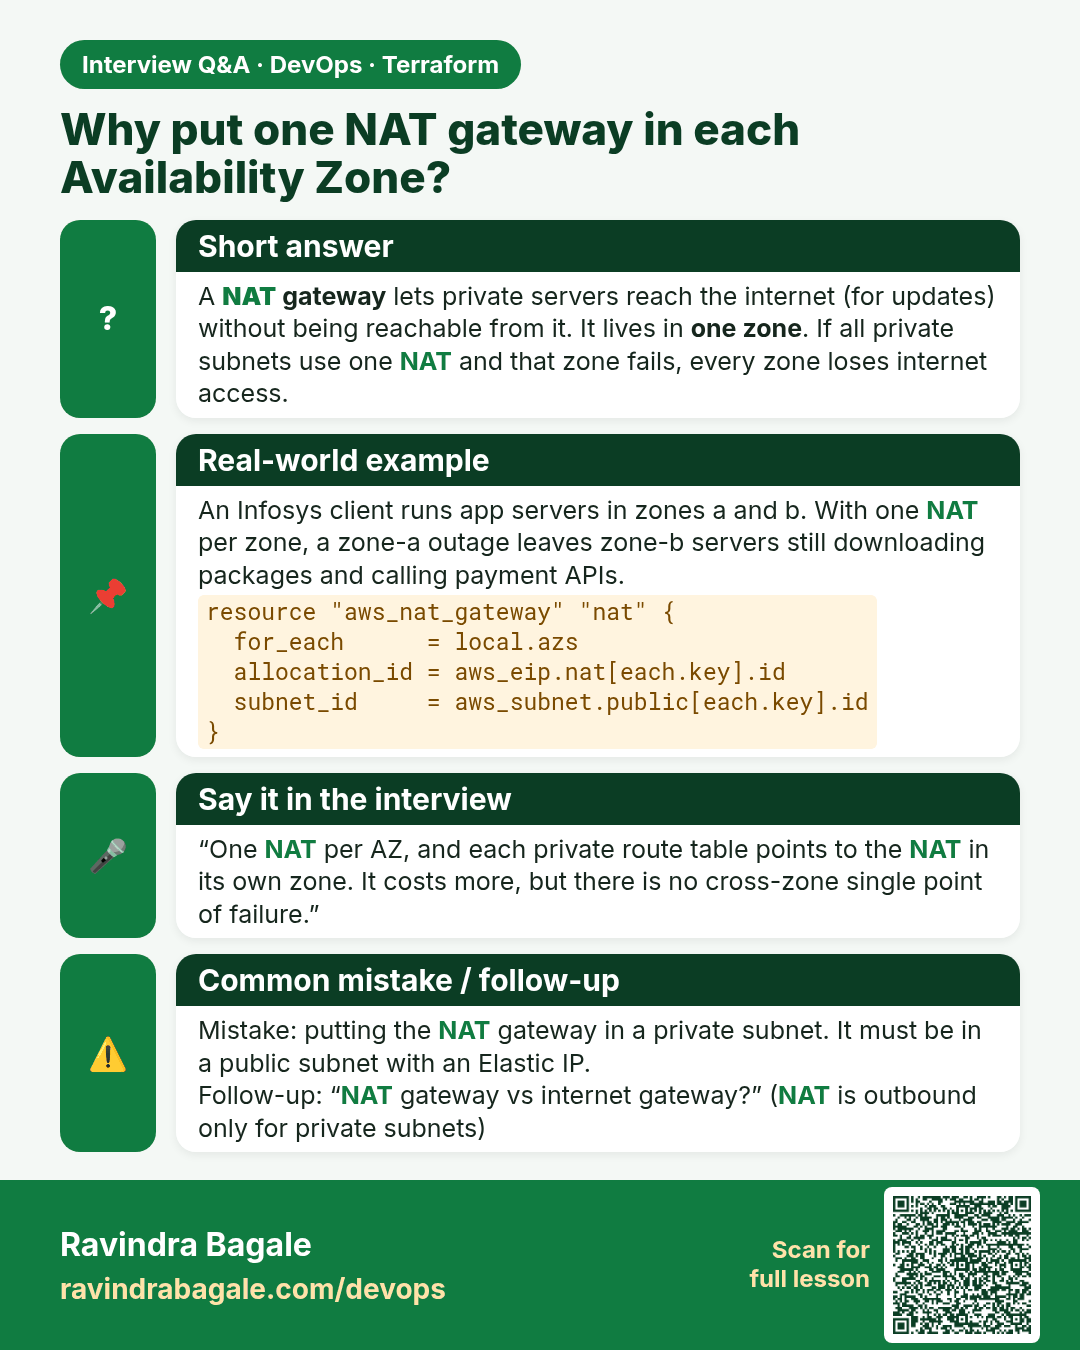
Why put one NAT gateway in each Availability Zone? A NAT gateway lets private servers reach the internet (for updates) without being reachable from it. It lives in one zone. If all private subnets use one NAT and that zone fails, every zone loses internet access.
Interview card 2 of 8: Why put one NAT gateway in each Availability Zone? · Download PNG · Open card page

Lesson: 46.2 VPC, public and private subnets, internet gateway, NAT gateways and route tables
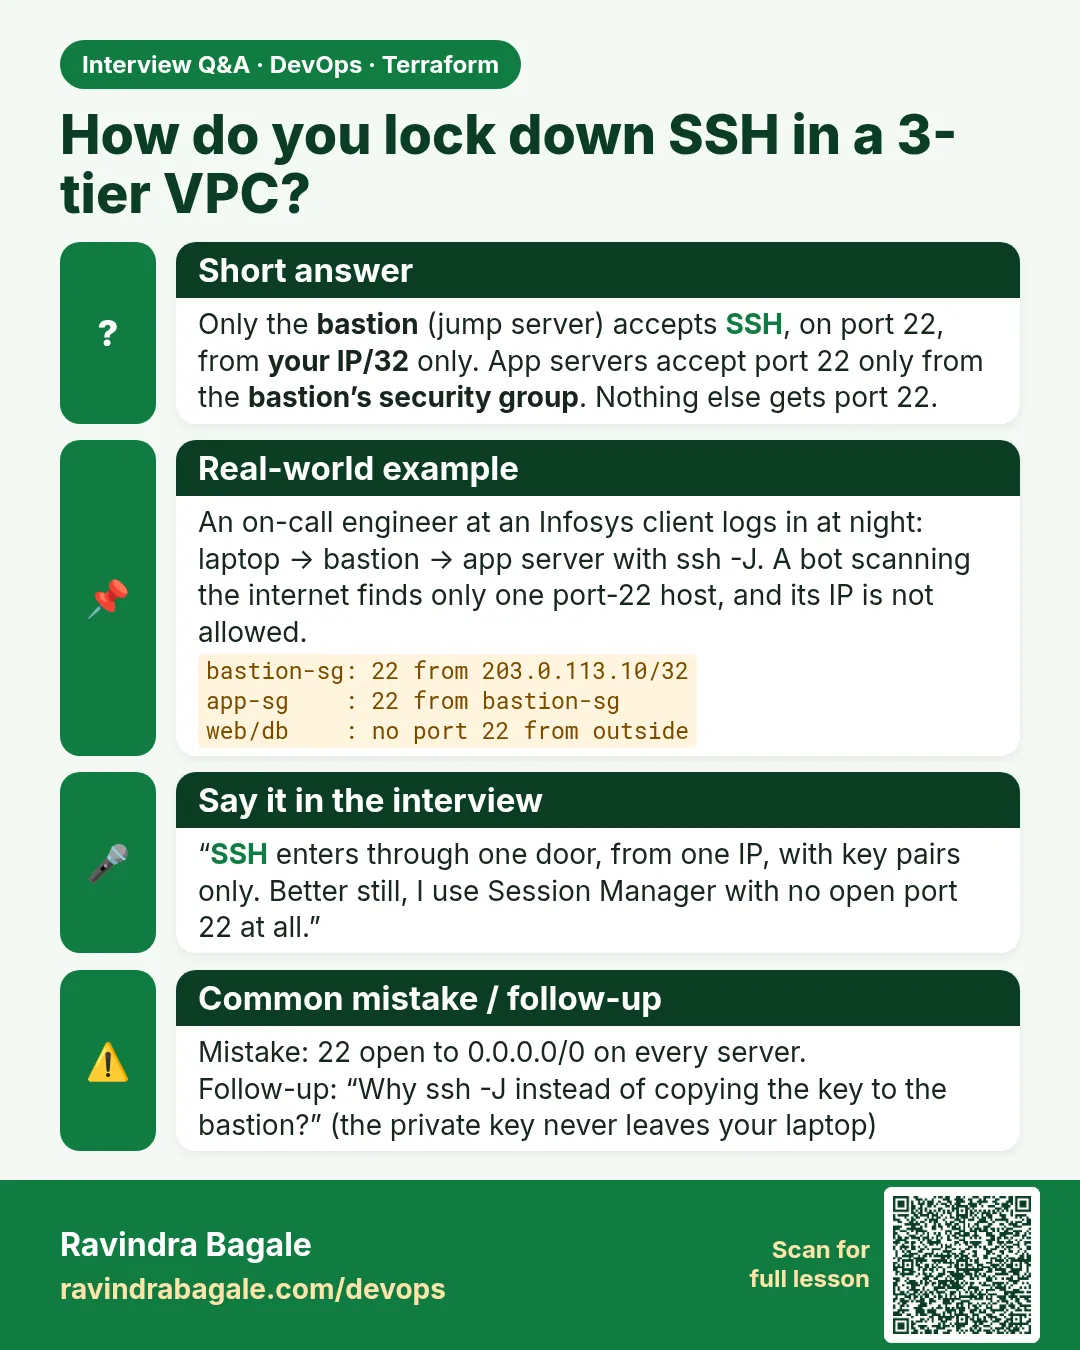
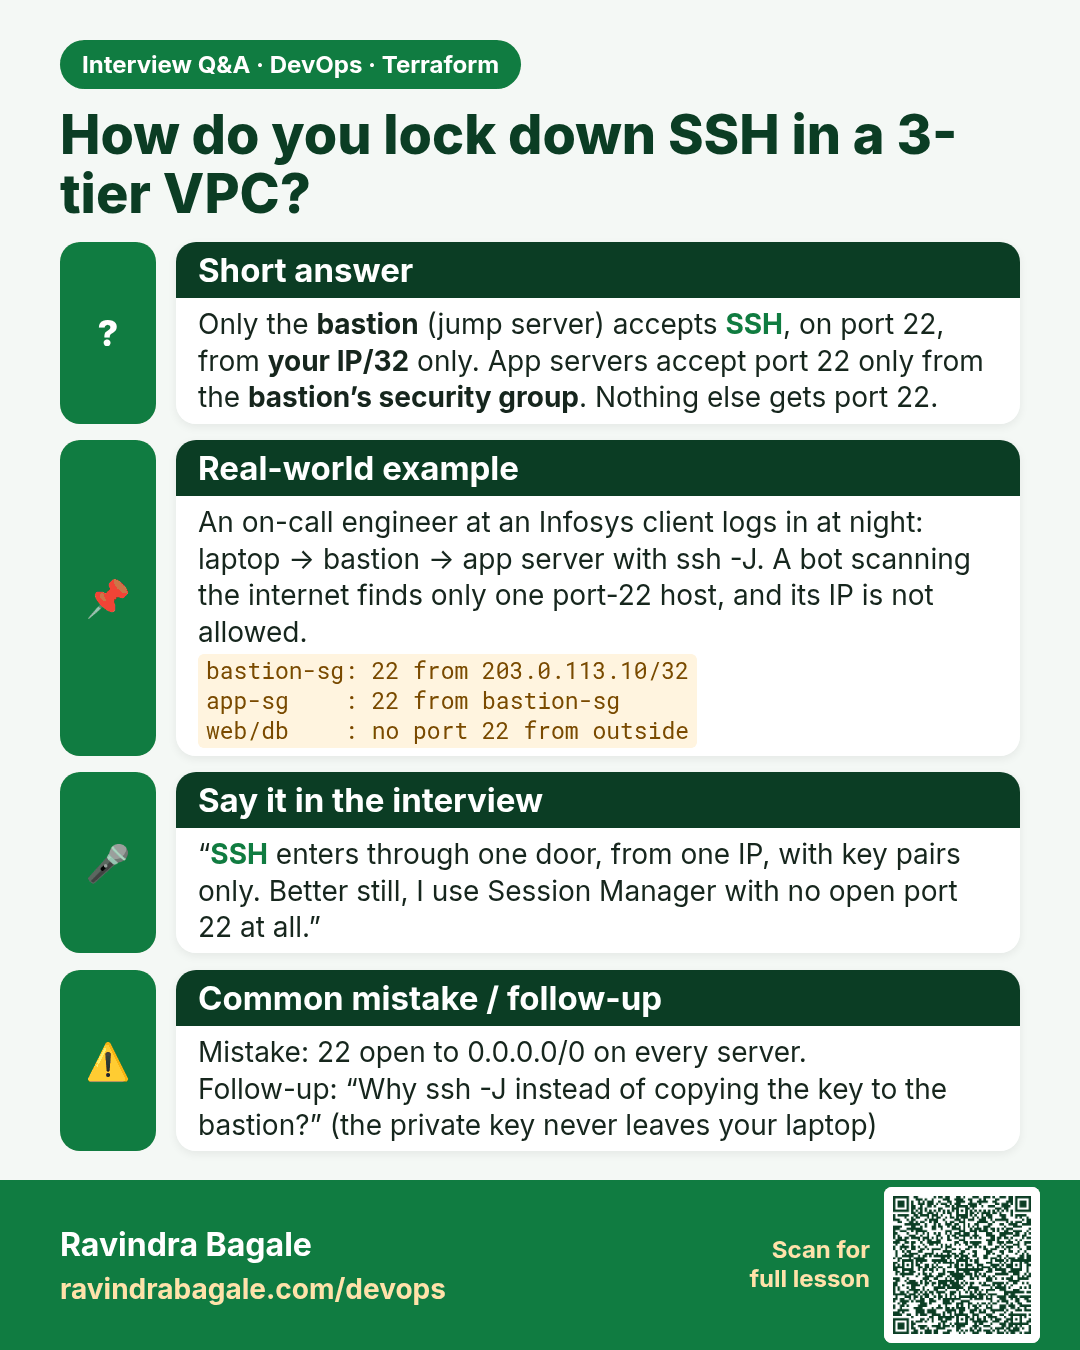
How do you lock down SSH in a 3-tier VPC? Only the bastion (jump server) accepts SSH, on port 22, from your IP/32 only. App servers accept port 22 only from the bastion’s security group. Nothing else gets port 22.
Interview card 3 of 8: How do you lock down SSH in a 3-tier VPC? · Download PNG · Open card page

Lesson: 46.3 Security group chain for all tiers and the bastion
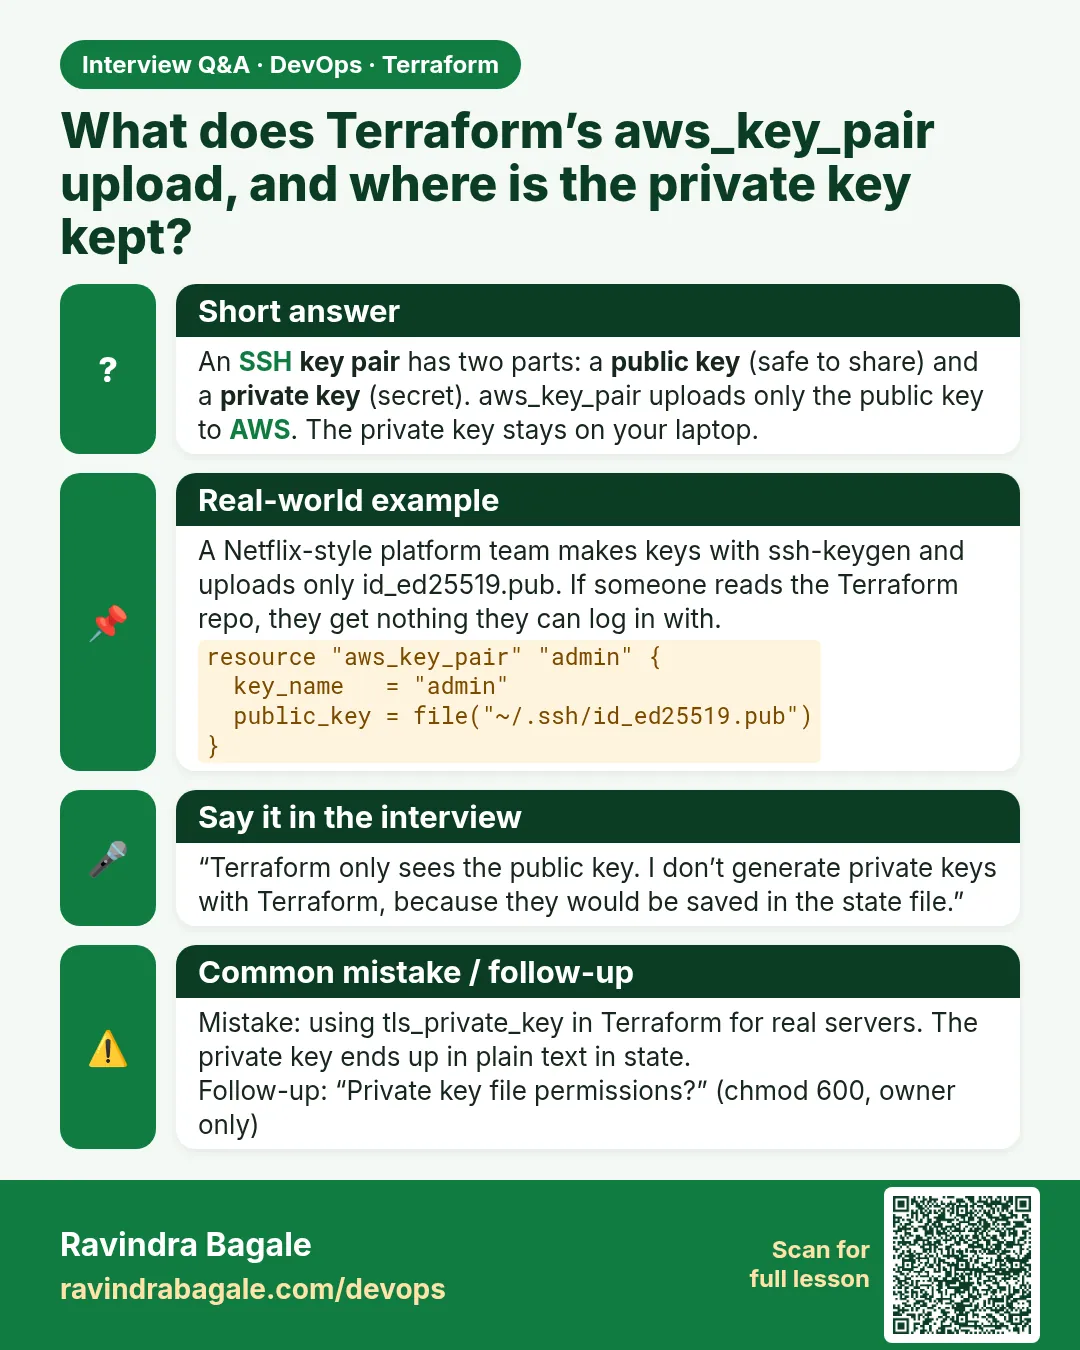
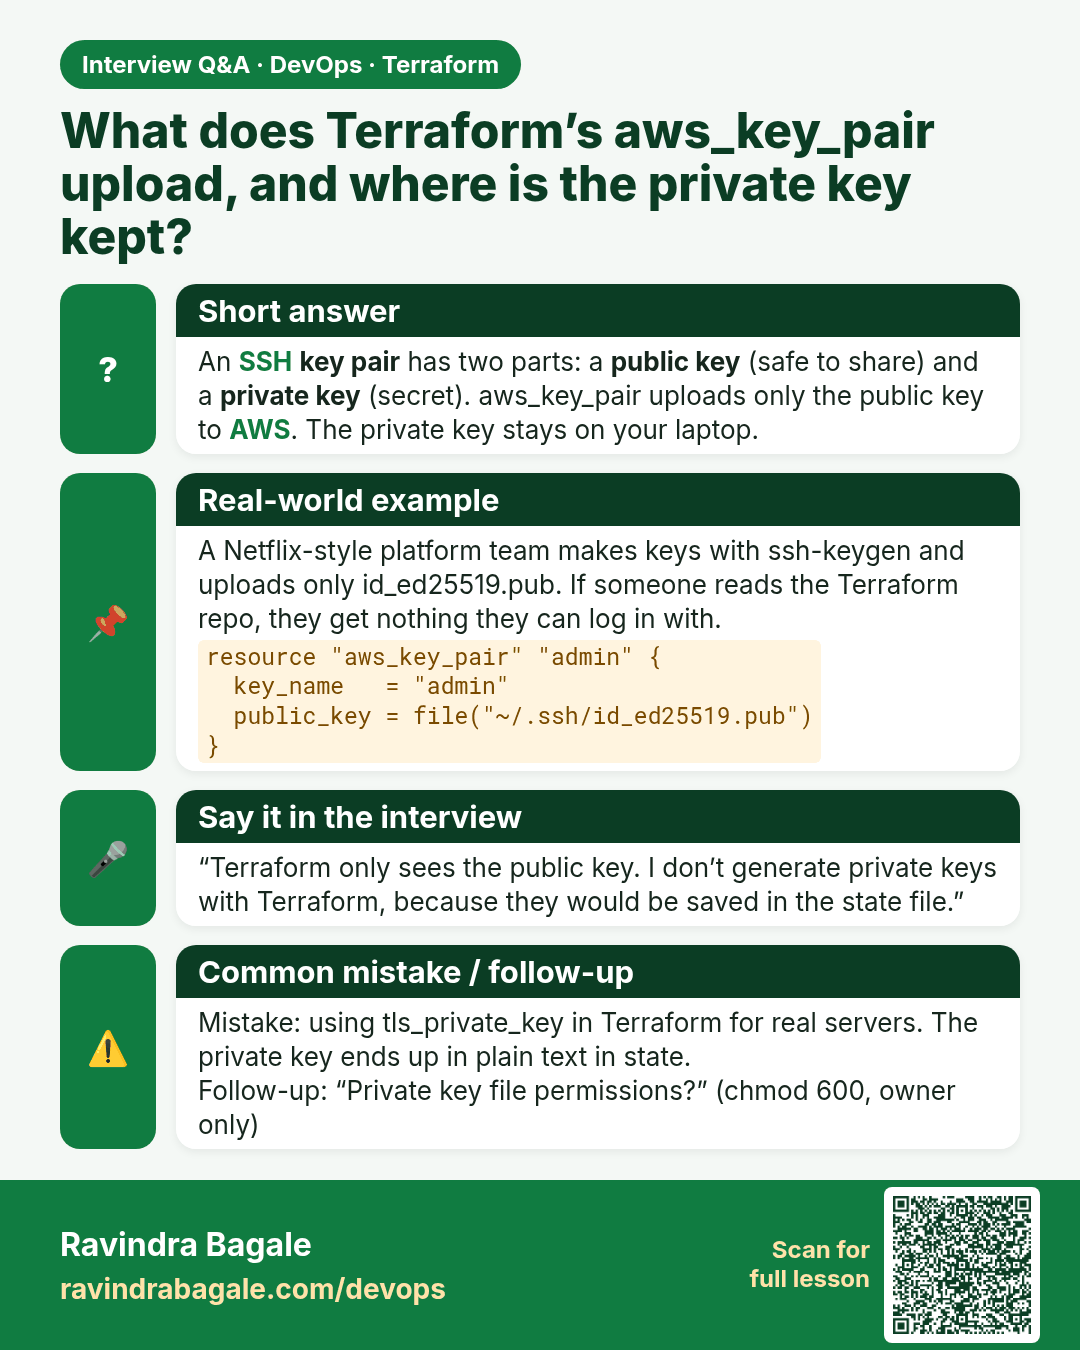
What does Terraform’s aws_key_pair upload, and where is the private key kept? An SSH key pair has two parts: a public key (safe to share) and a private key (secret). aws_key_pair uploads only the public key to AWS. The private key stays on your laptop.
Interview card 4 of 8: What does Terraform’s aws_key_pair upload, and where is the private key kept? · Download PNG · Open card page

Lesson: 46.4 Bastion jump server in the public subnet
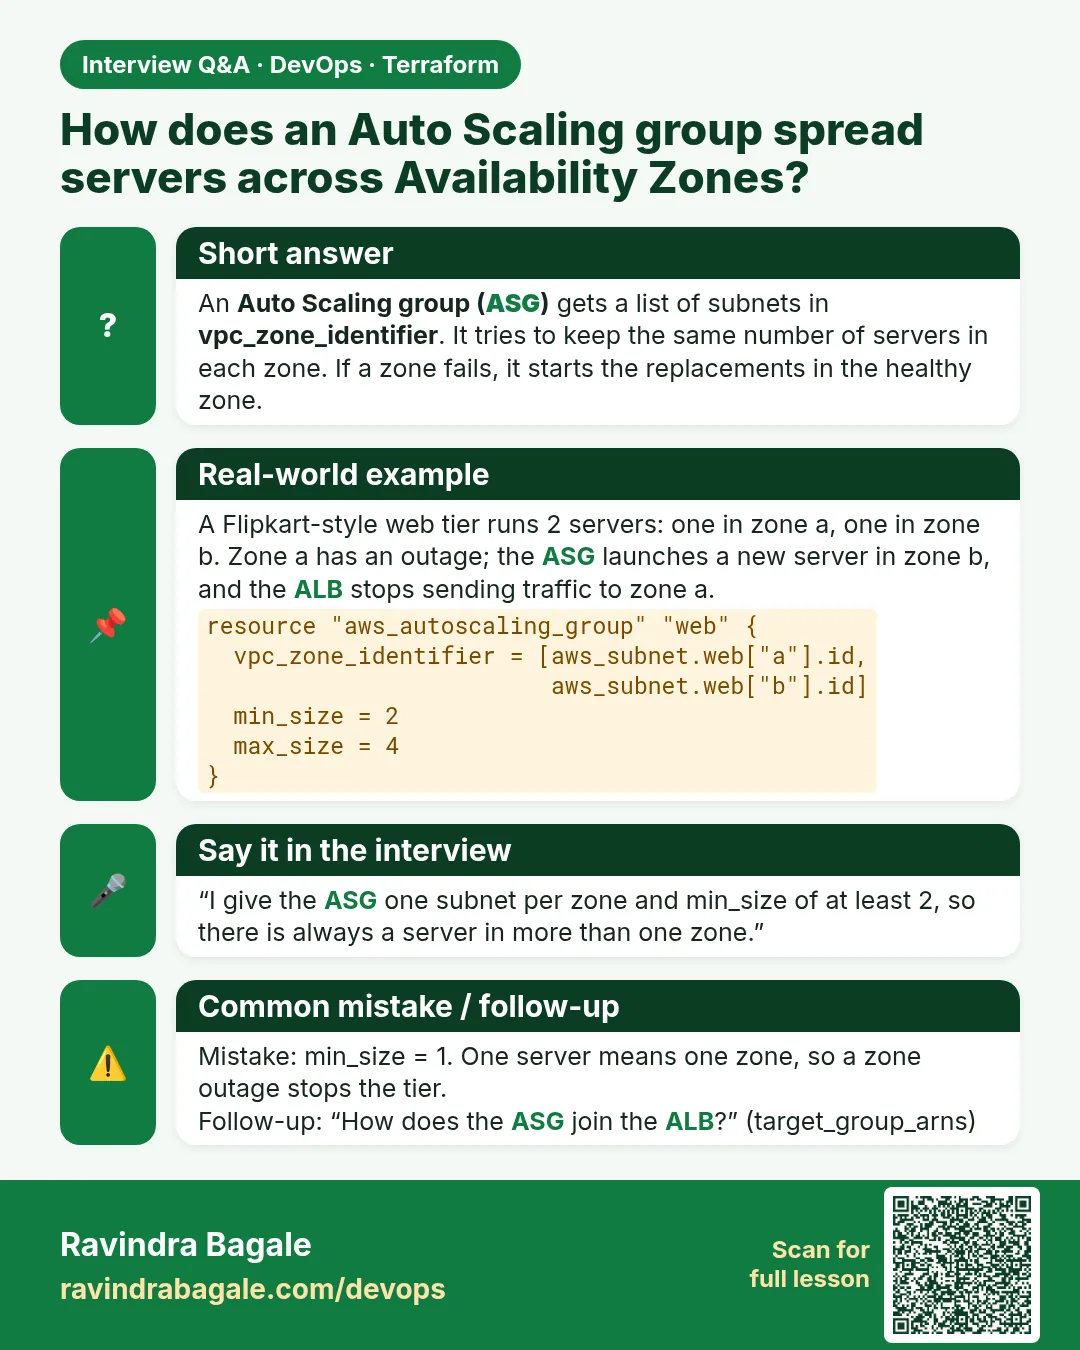
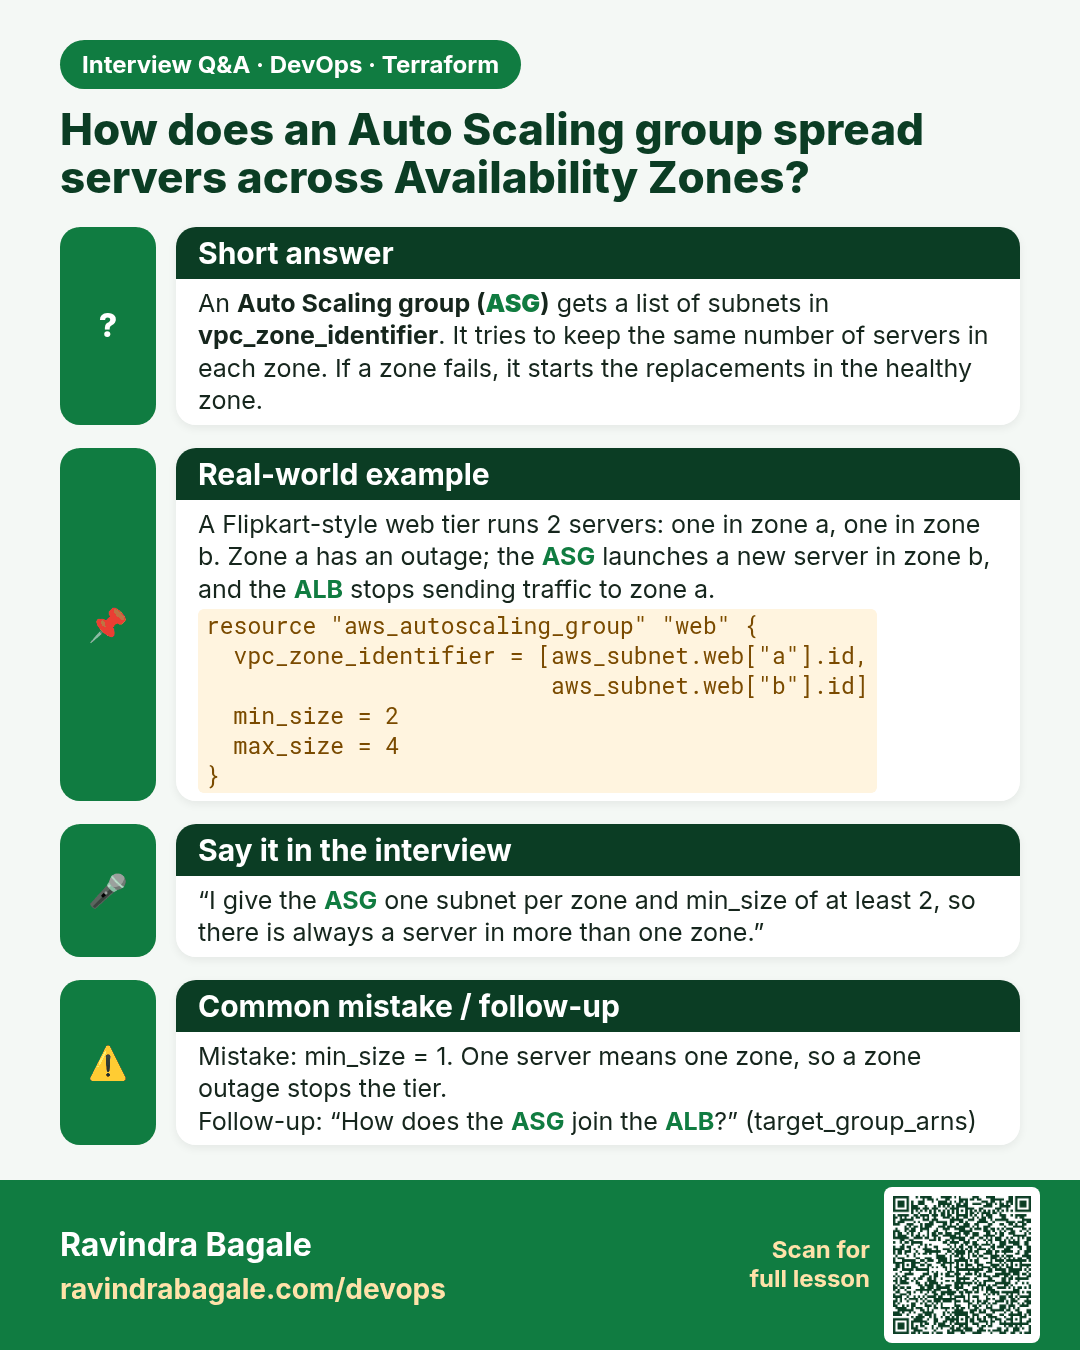
How does an Auto Scaling group spread servers across Availability Zones? An Auto Scaling group (ASG) gets a list of subnets in vpc_zone_identifier. It tries to keep the same number of servers in each zone. If a zone fails, it starts the replacements in the healthy zone.
Interview card 5 of 8: How does an Auto Scaling group spread servers across Availability Zones? · Download PNG · Open card page

Lesson: 46.5 Internet-facing ALB and web tier Auto Scaling group
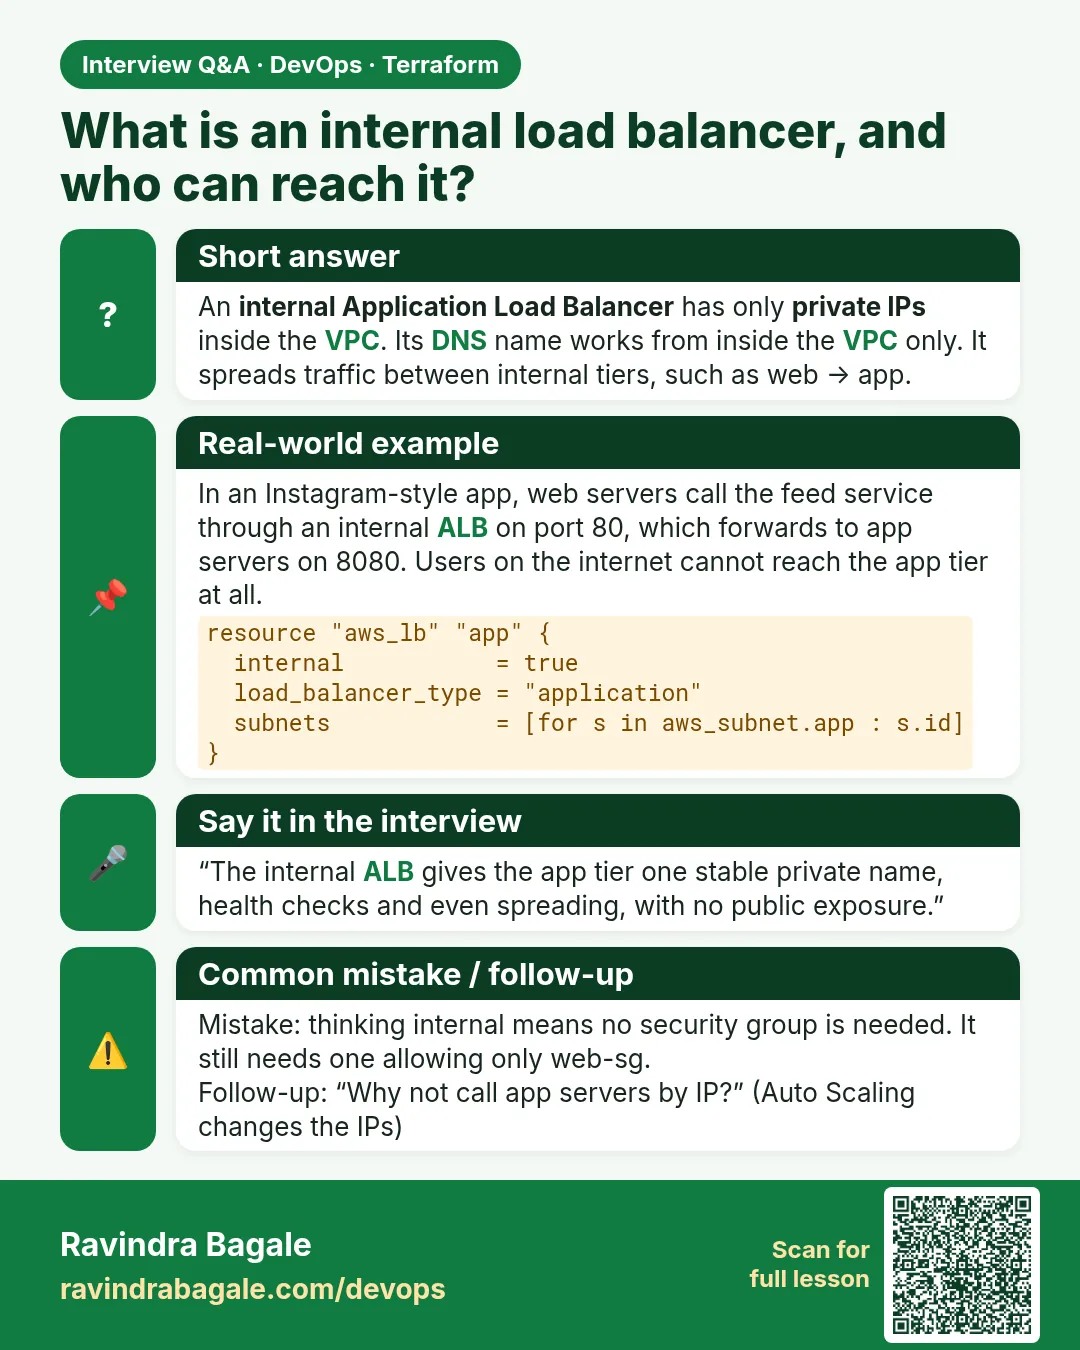
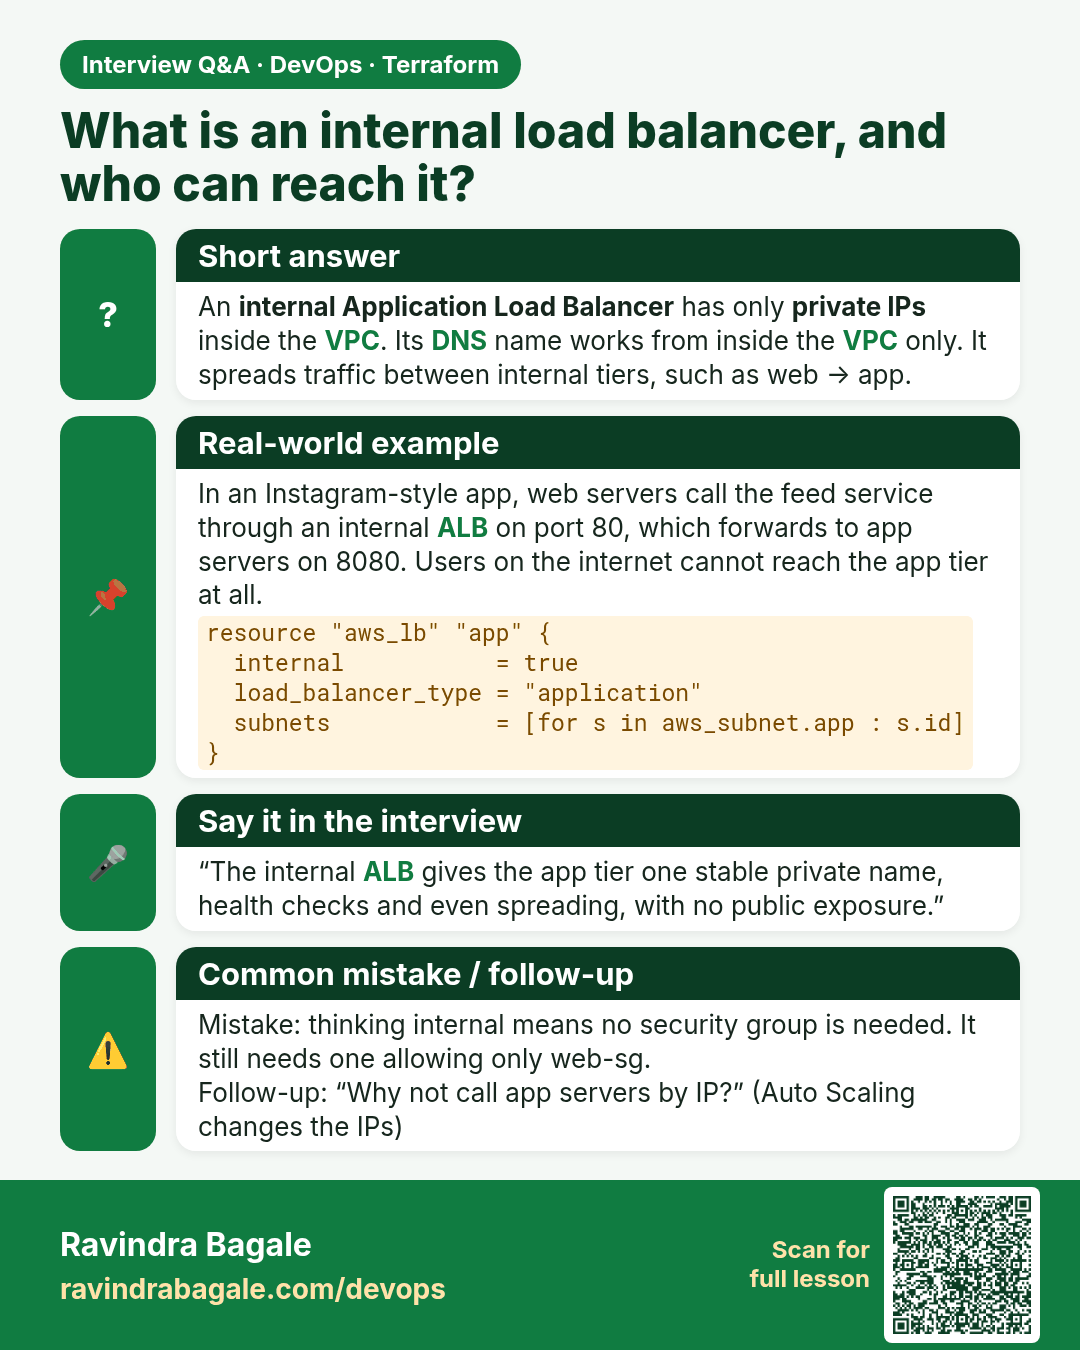
What is an internal load balancer, and who can reach it? An internal Application Load Balancer has only private IPs inside the VPC. Its DNS name works from inside the VPC only. It spreads traffic between internal tiers, such as web → app.
Interview card 6 of 8: What is an internal load balancer, and who can reach it? · Download PNG · Open card page

Lesson: 46.6 Internal ALB and app tier Auto Scaling group
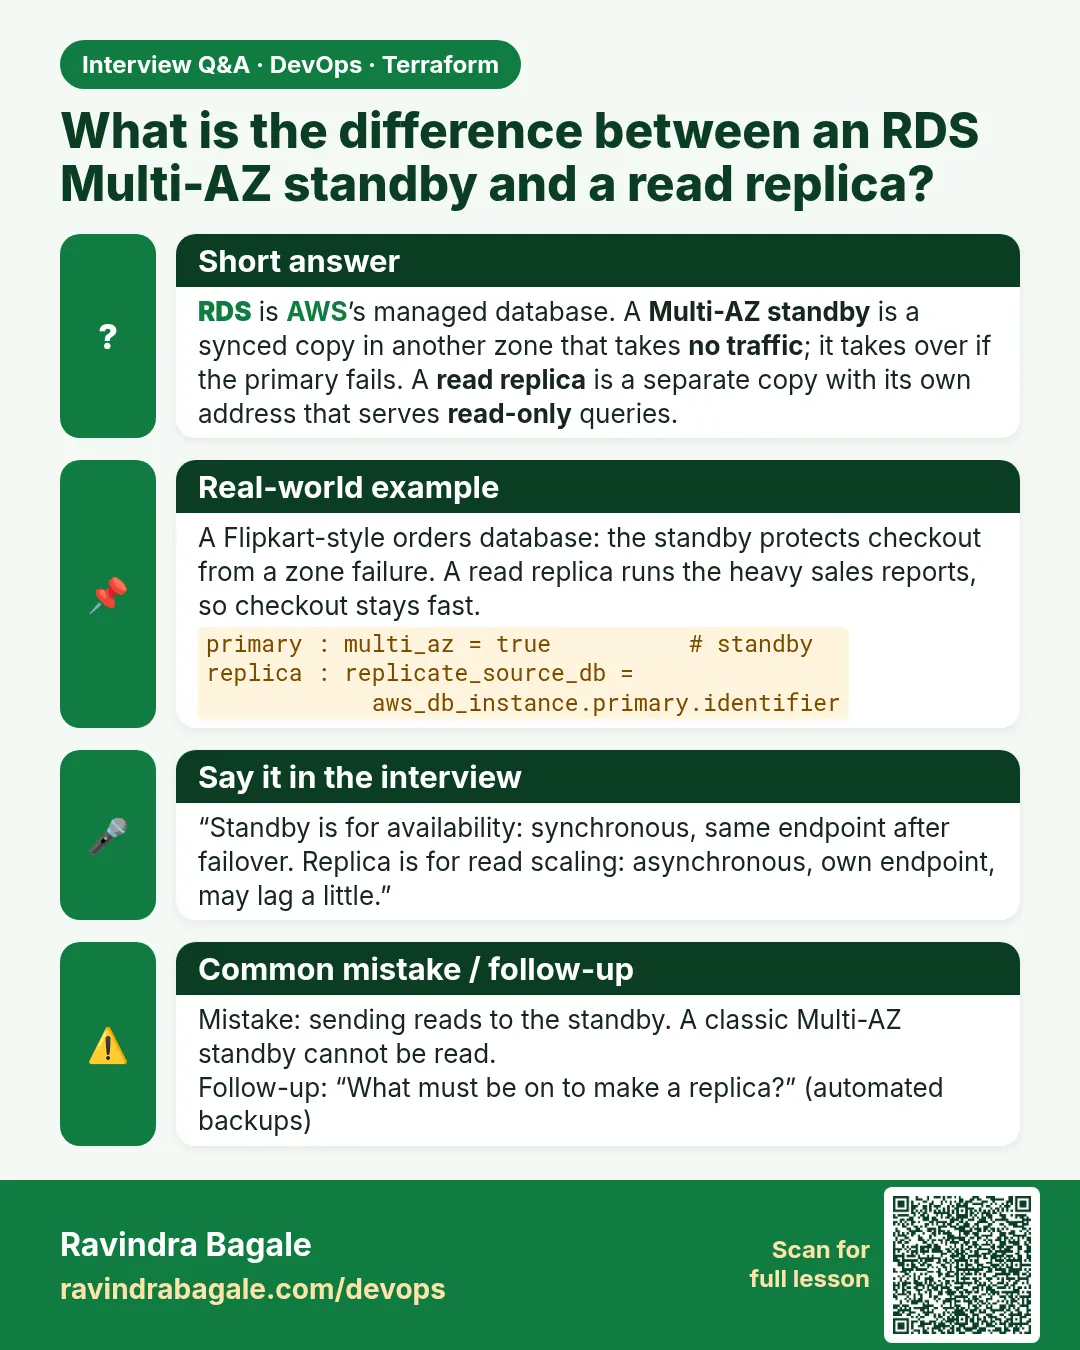
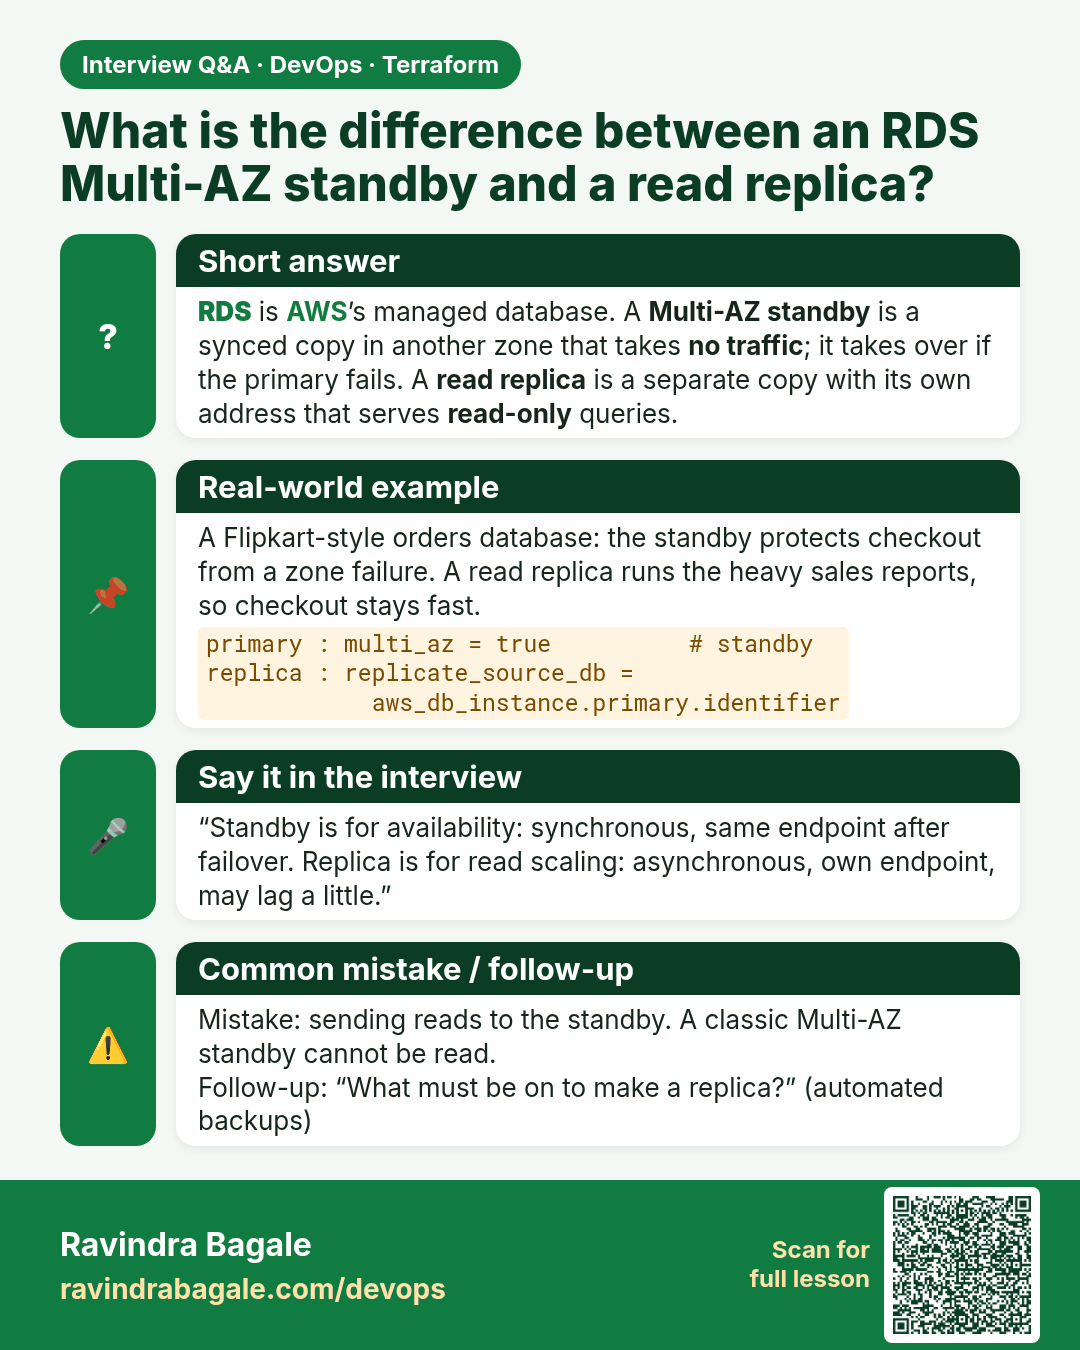
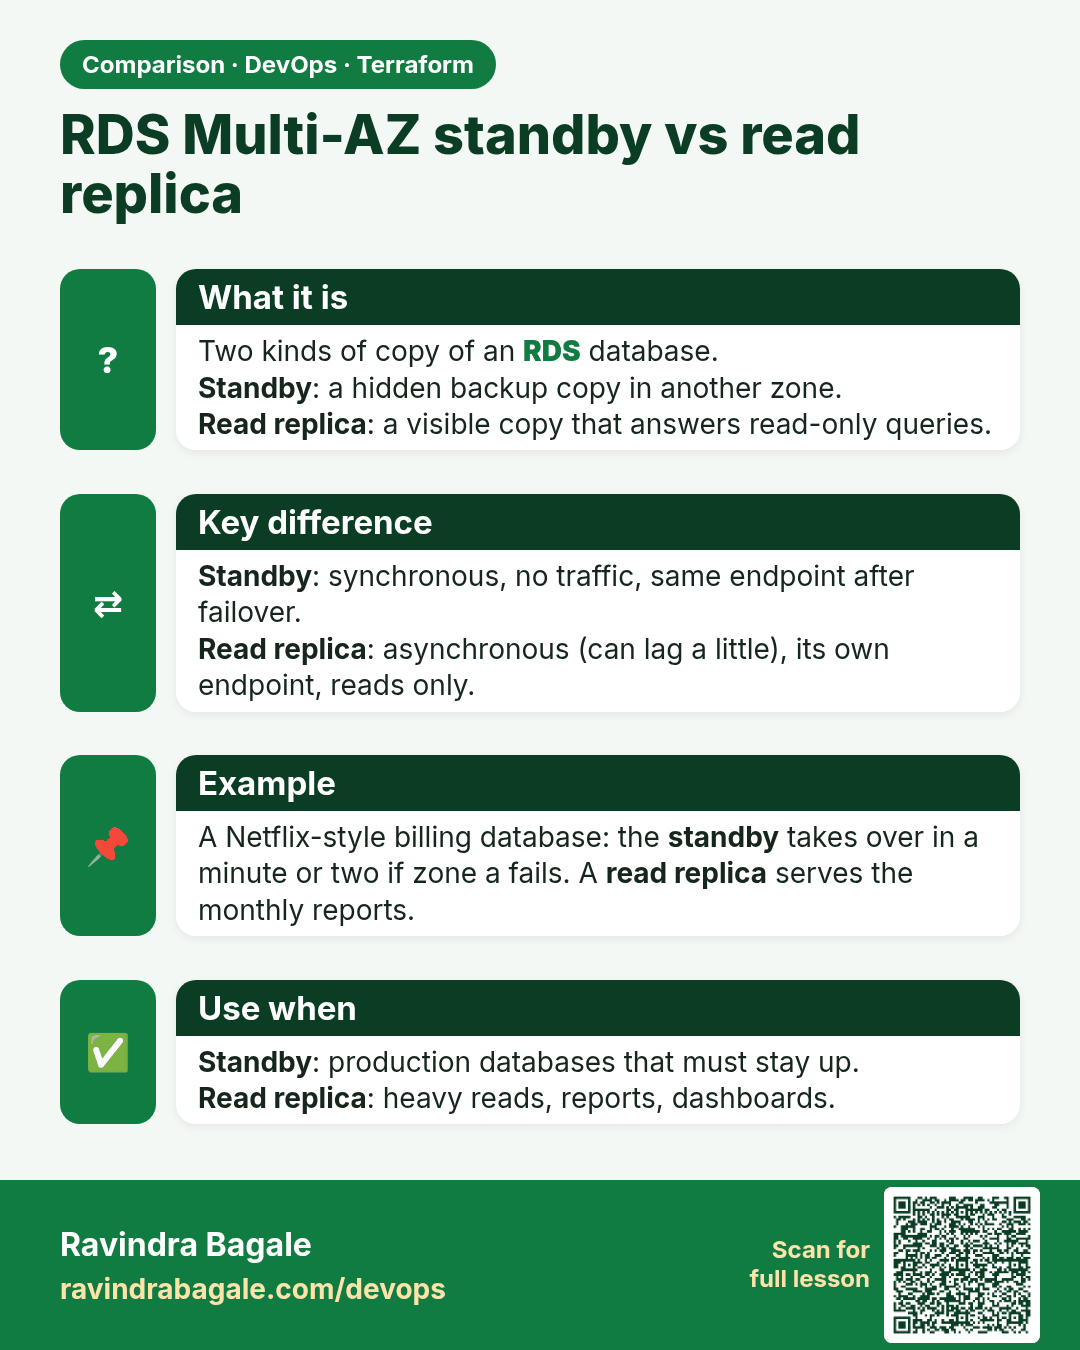
What is the difference between an RDS Multi-AZ standby and a read replica? RDS is AWS’s managed database. A Multi-AZ standby is a synced copy in another zone that takes no traffic; it takes over if the primary fails. A read replica is a separate copy with its own address that serves read-only querie
Interview card 7 of 8: What is the difference between an RDS Multi-AZ standby and a read replica? · Download PNG · Open card page

Lesson: 46.7 DB subnet group, Multi-AZ RDS standby and read replica
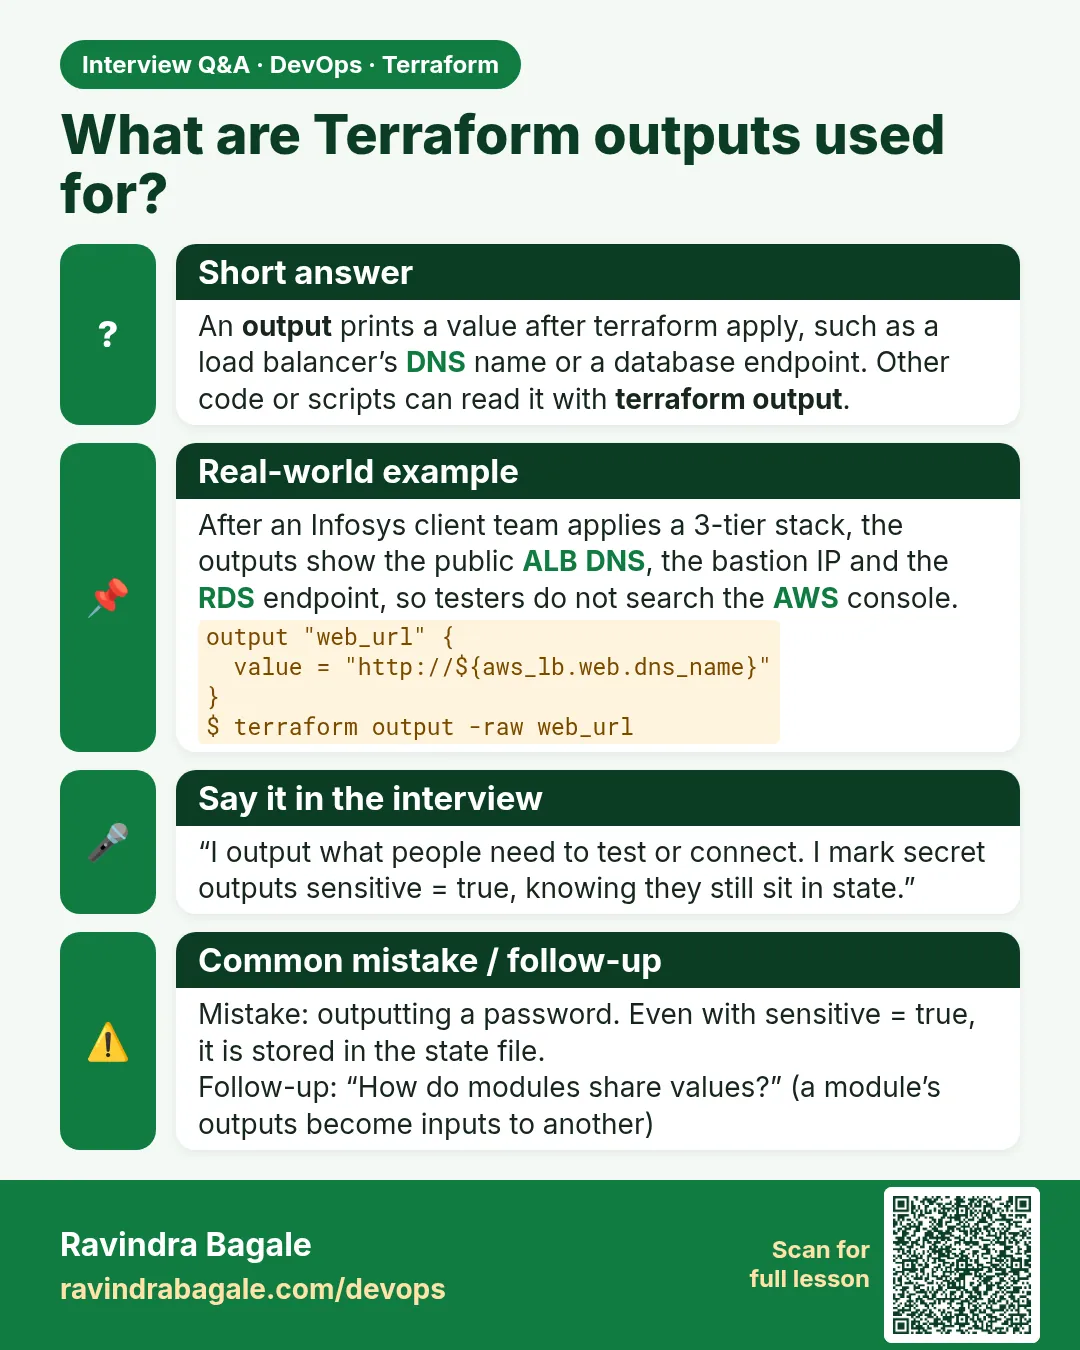
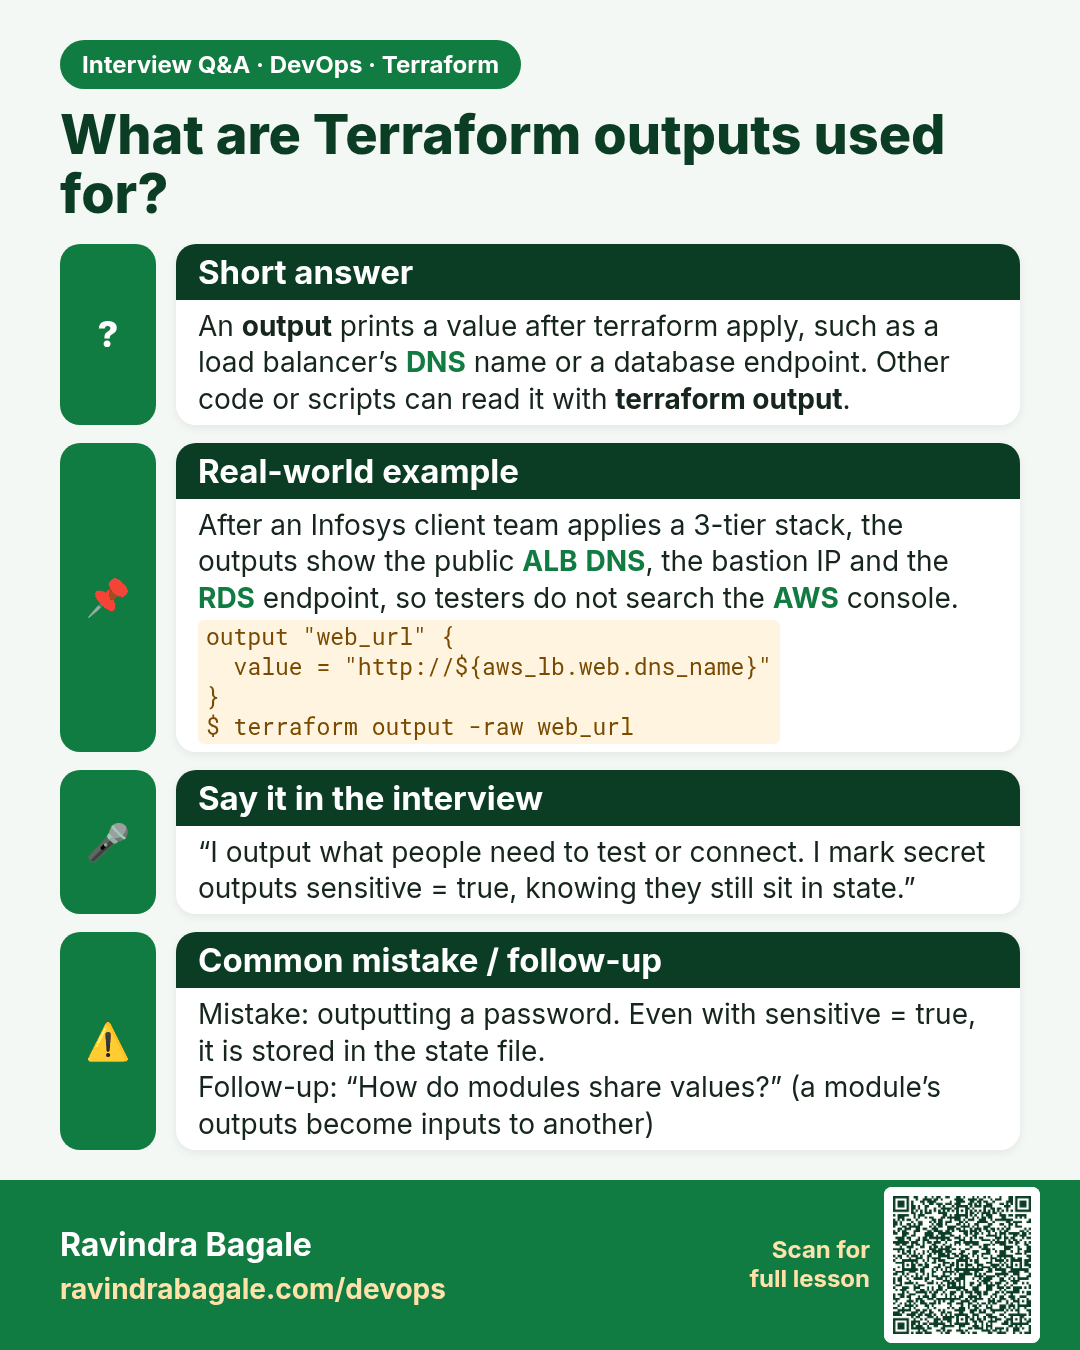
What are Terraform outputs used for? An output prints a value after terraform apply, such as a load balancer’s DNS name or a database endpoint. Other code or scripts can read it with terraform output.
Interview card 8 of 8: What are Terraform outputs used for? · Download PNG · Open card page

Lesson: 46.8 Outputs, apply, test end to end and destroy

Comparison cards
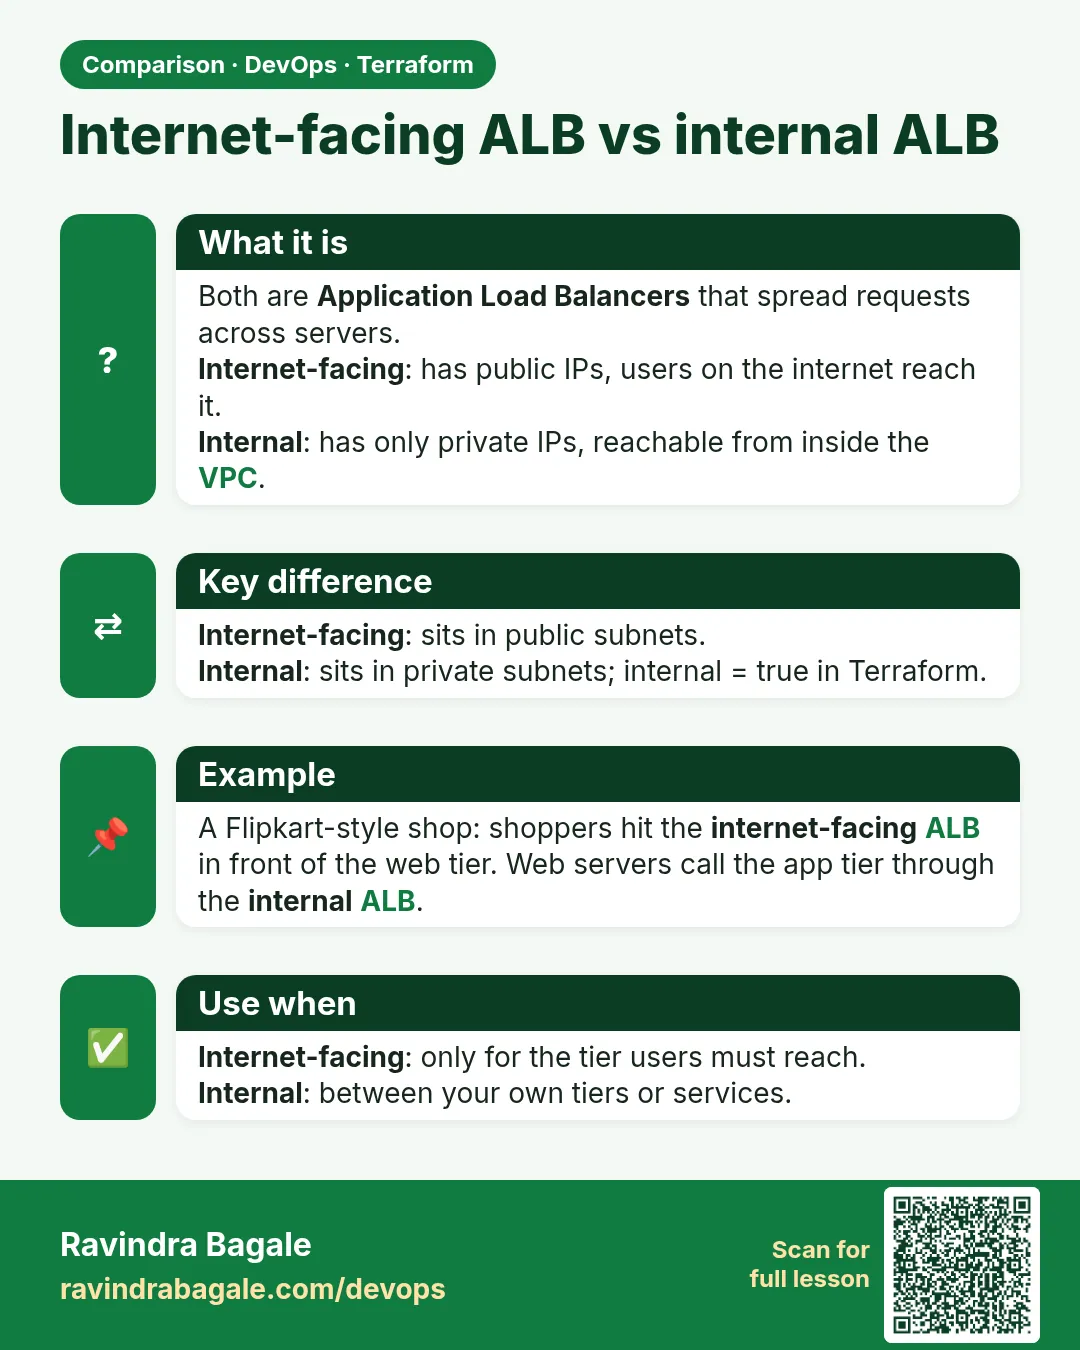
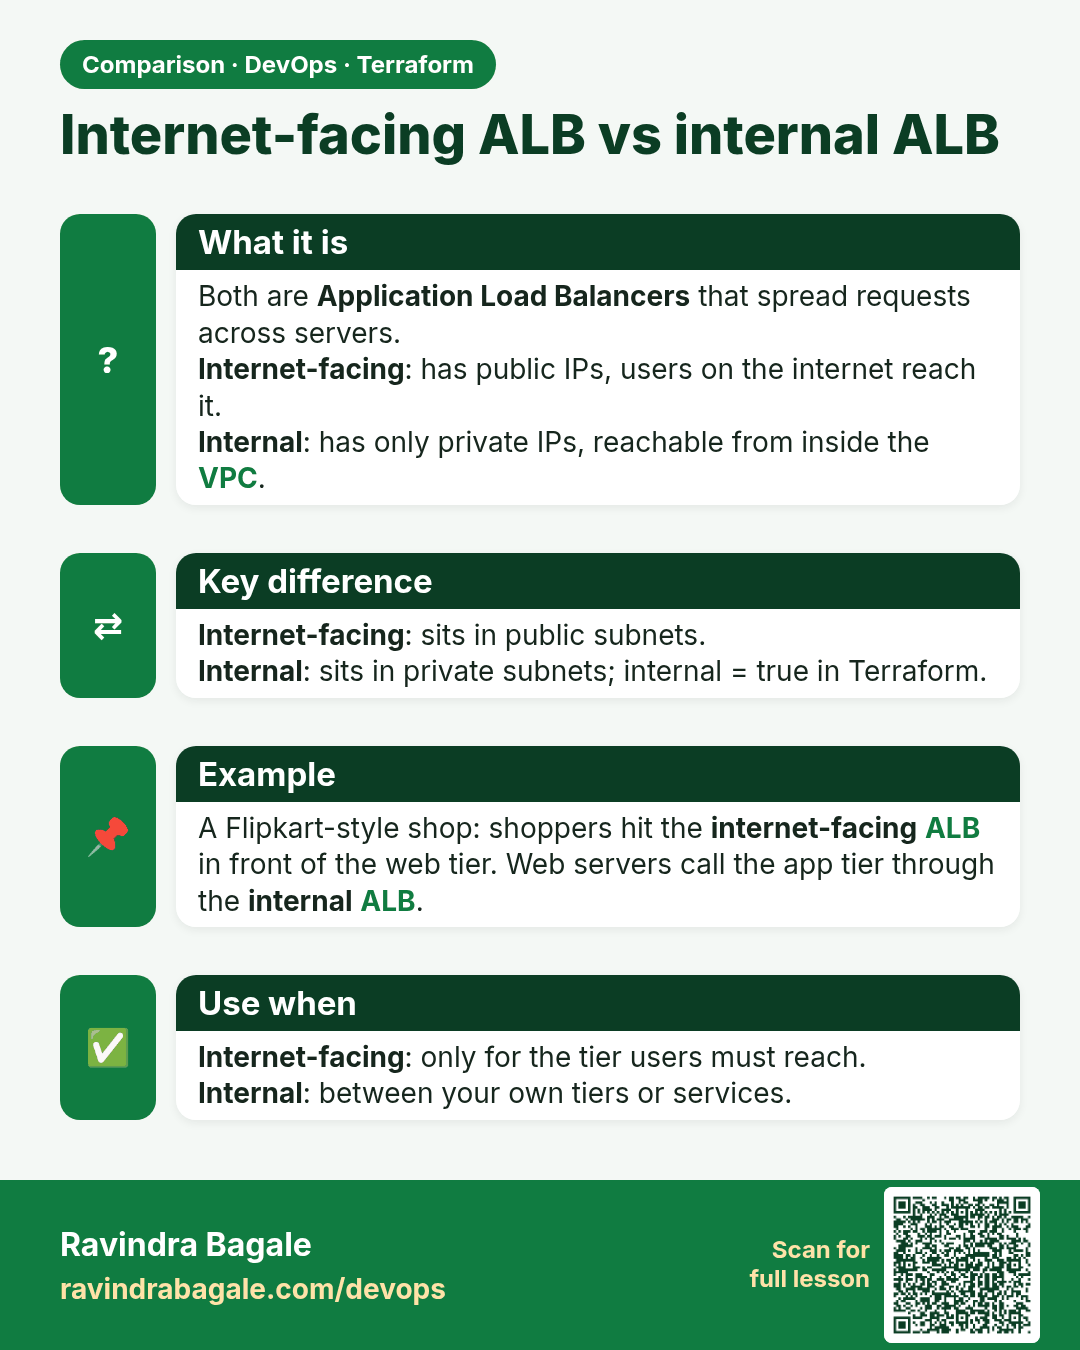
Internet-facing ALB vs internal ALB. Both are Application Load Balancers that spread requests across servers.Internet-facing: has public IPs, users on the internet reach it.Internal: has only private IPs, reachable from inside the VPC.
Comparison card 1 of 3: Internet-facing ALB vs internal ALB · Download PNG · Open card page

Lesson: Chapter 46: Terraform 3-Tier Architecture Multi-AZ with ALBs Auto Scaling Bastion NAT and RDS
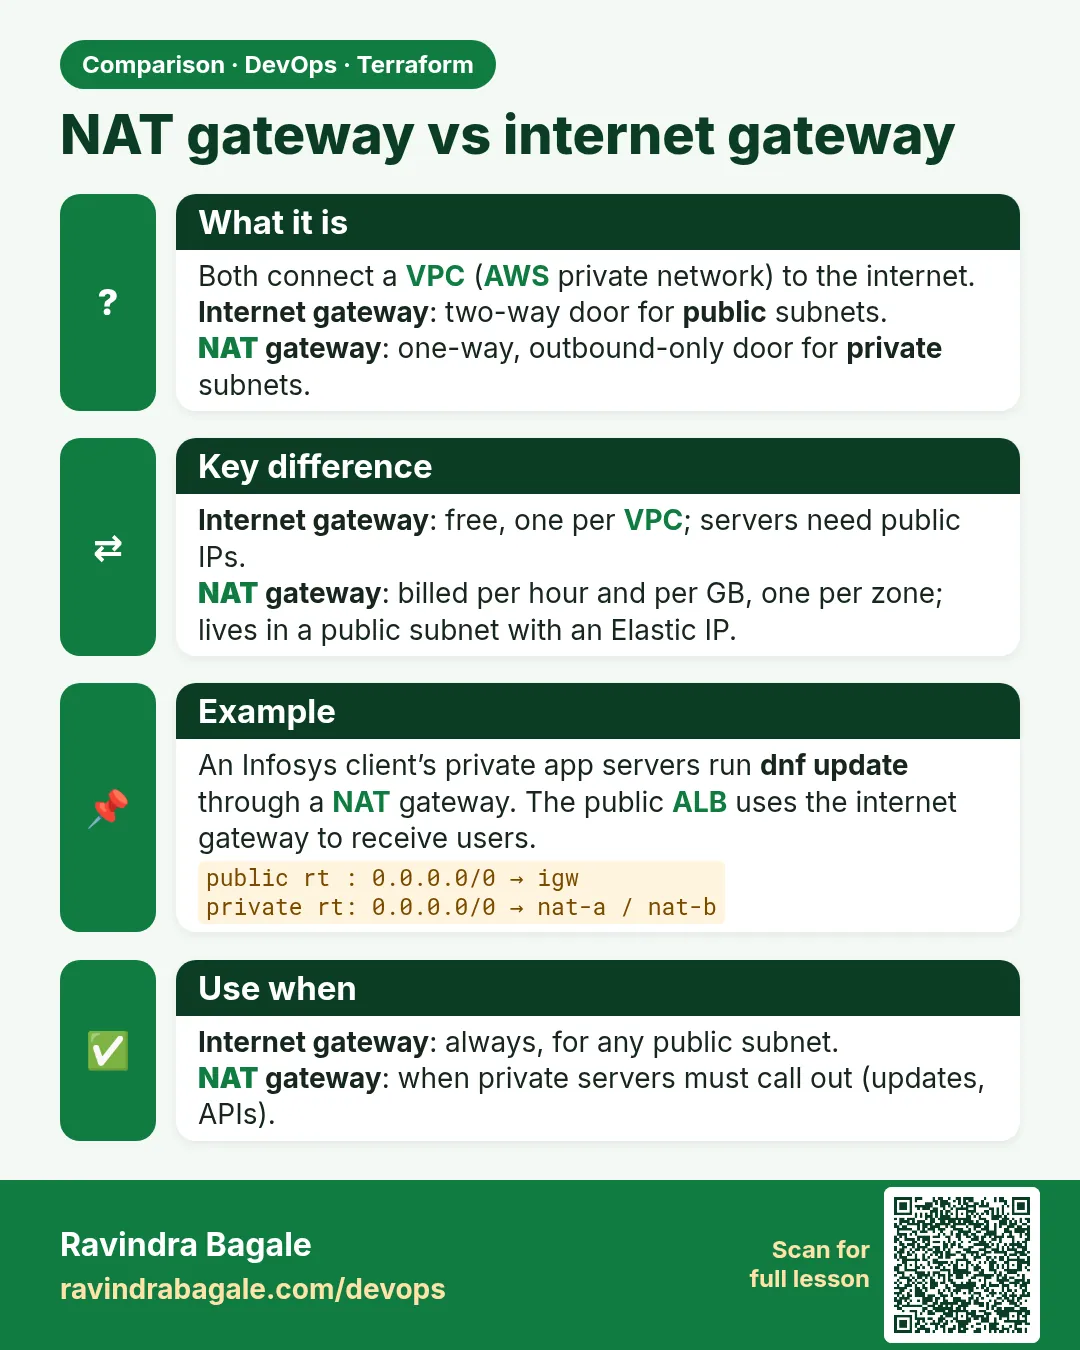
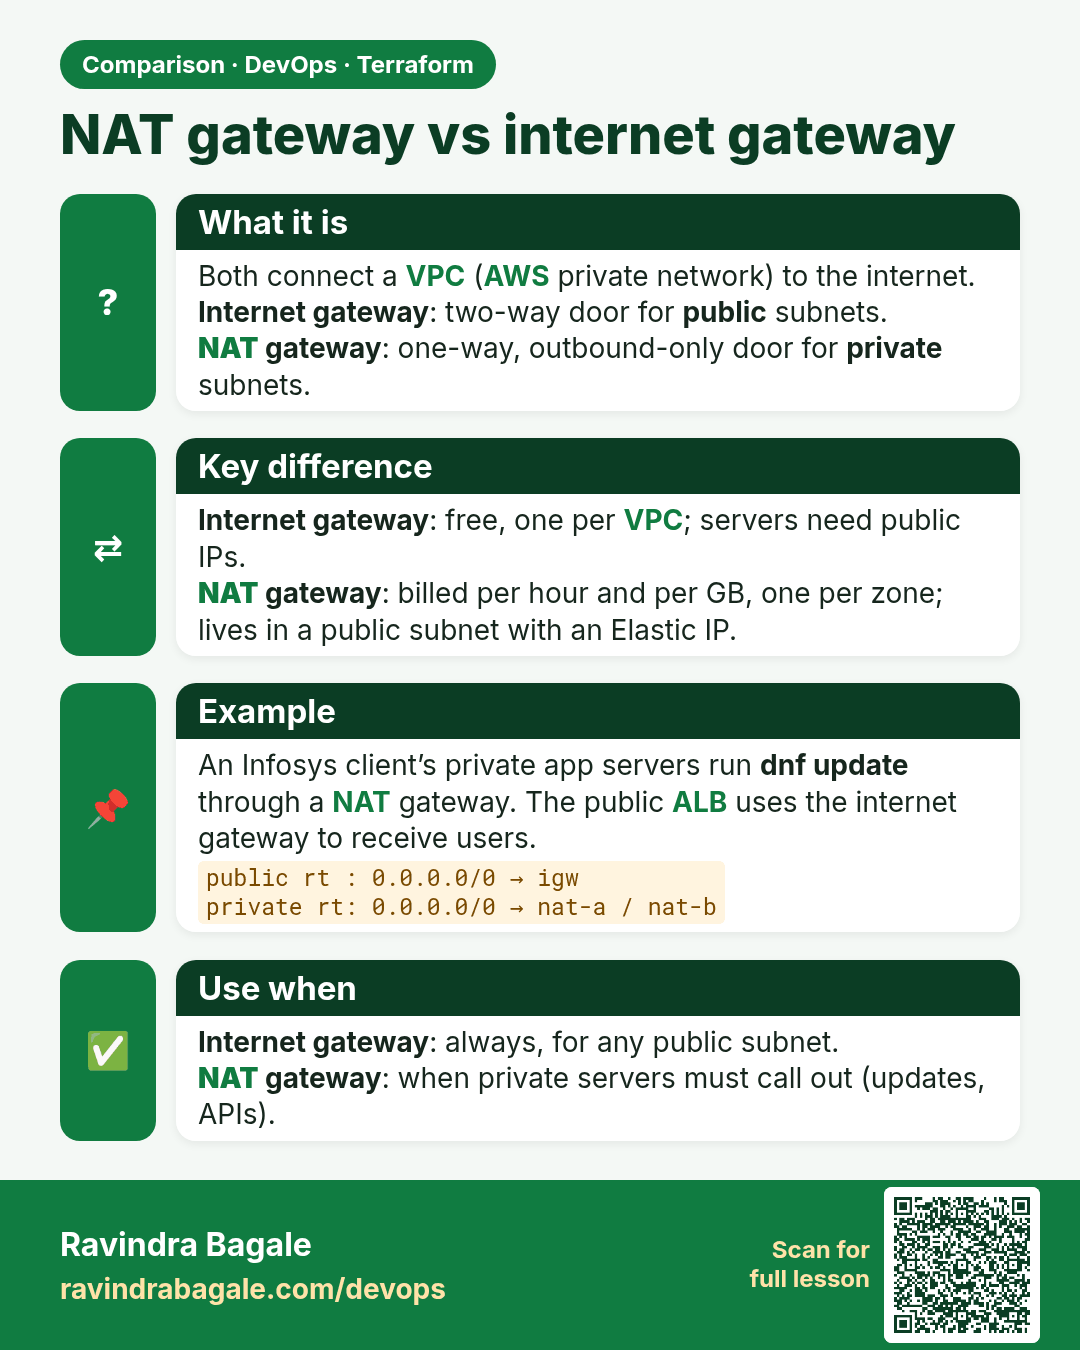
NAT gateway vs internet gateway. Both connect a VPC (AWS private network) to the internet.Internet gateway: two-way door for public subnets.NAT gateway: one-way, outbound-only door for private subnets.
Comparison card 2 of 3: NAT gateway vs internet gateway · Download PNG · Open card page

Lesson: Chapter 46: Terraform 3-Tier Architecture Multi-AZ with ALBs Auto Scaling Bastion NAT and RDS
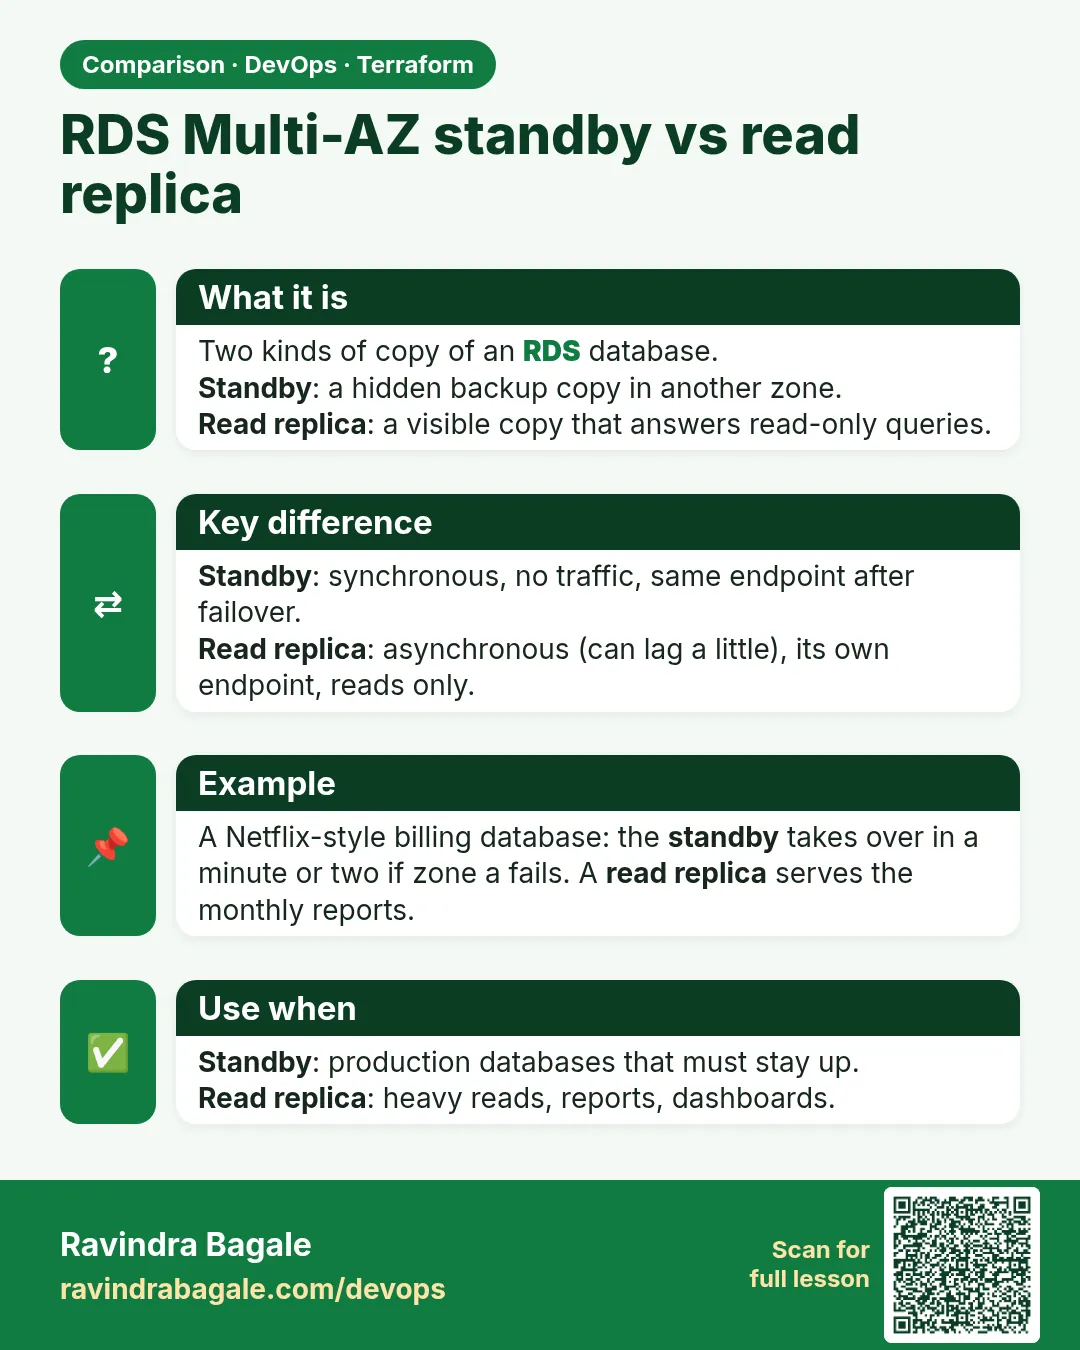
RDS Multi-AZ standby vs read replica. Two kinds of copy of an RDS database.Standby: a hidden backup copy in another zone.Read replica: a visible copy that answers read-only queries.
Comparison card 3 of 3: RDS Multi-AZ standby vs read replica · Download PNG · Open card page

Lesson: Chapter 46: Terraform 3-Tier Architecture Multi-AZ with ALBs Auto Scaling Bastion NAT and RDS