Ravindra BagaleCourses & study guides मराठी

Ravi Sir's Cards › DevOps

Chapter 39: Terraform Provisioners Secrets and Sensitive Values: Cards

मराठी cards · Open the chapter

Revision cards
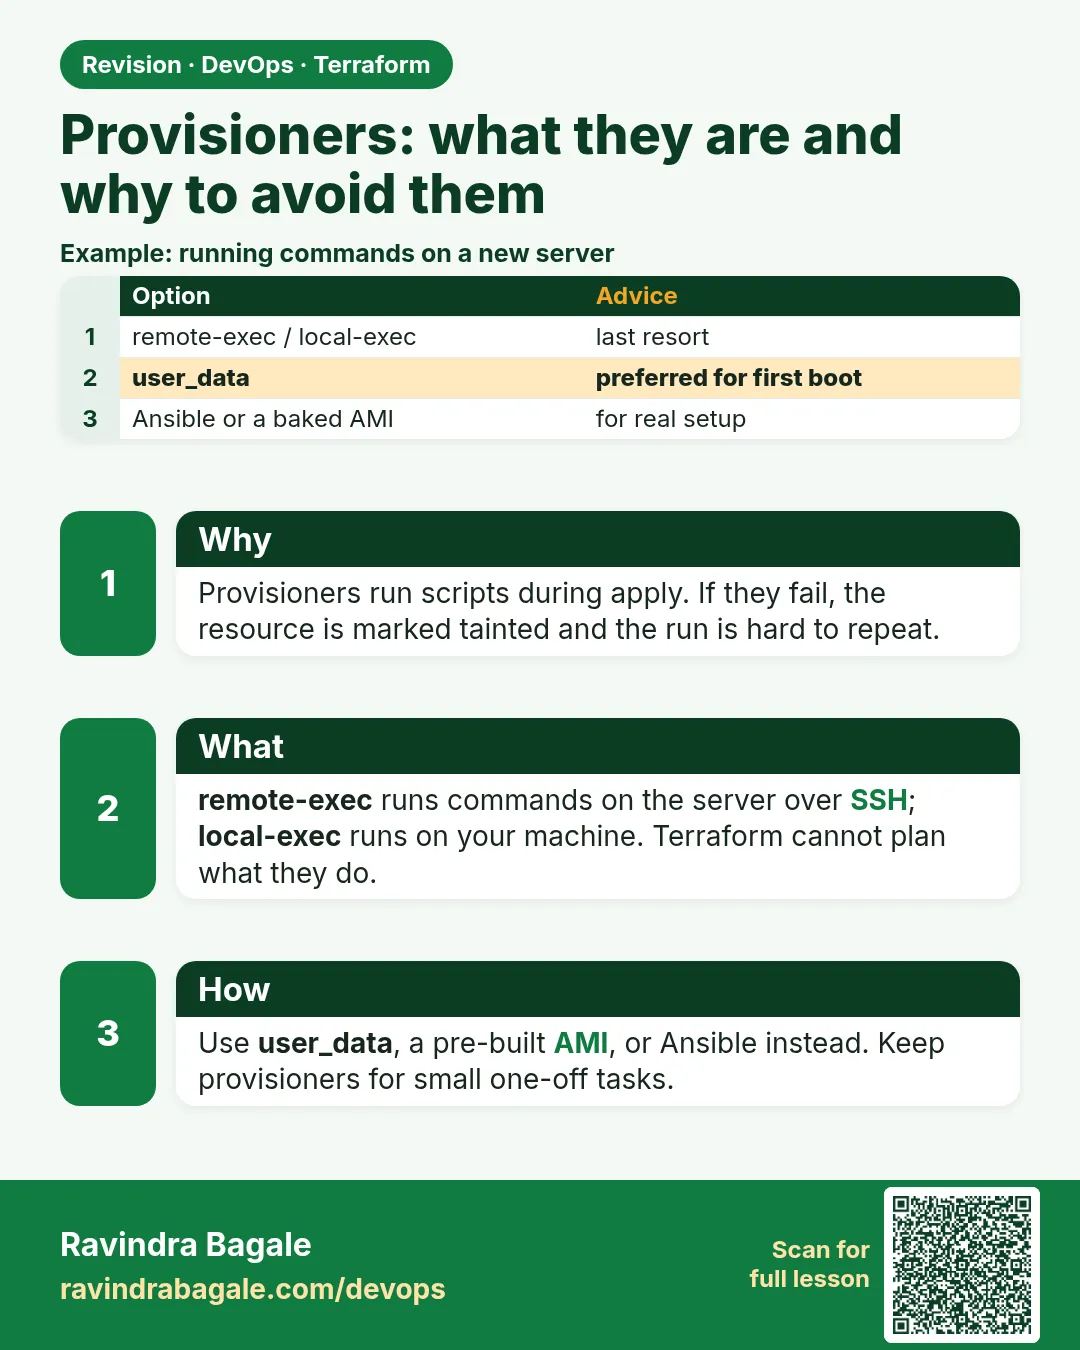
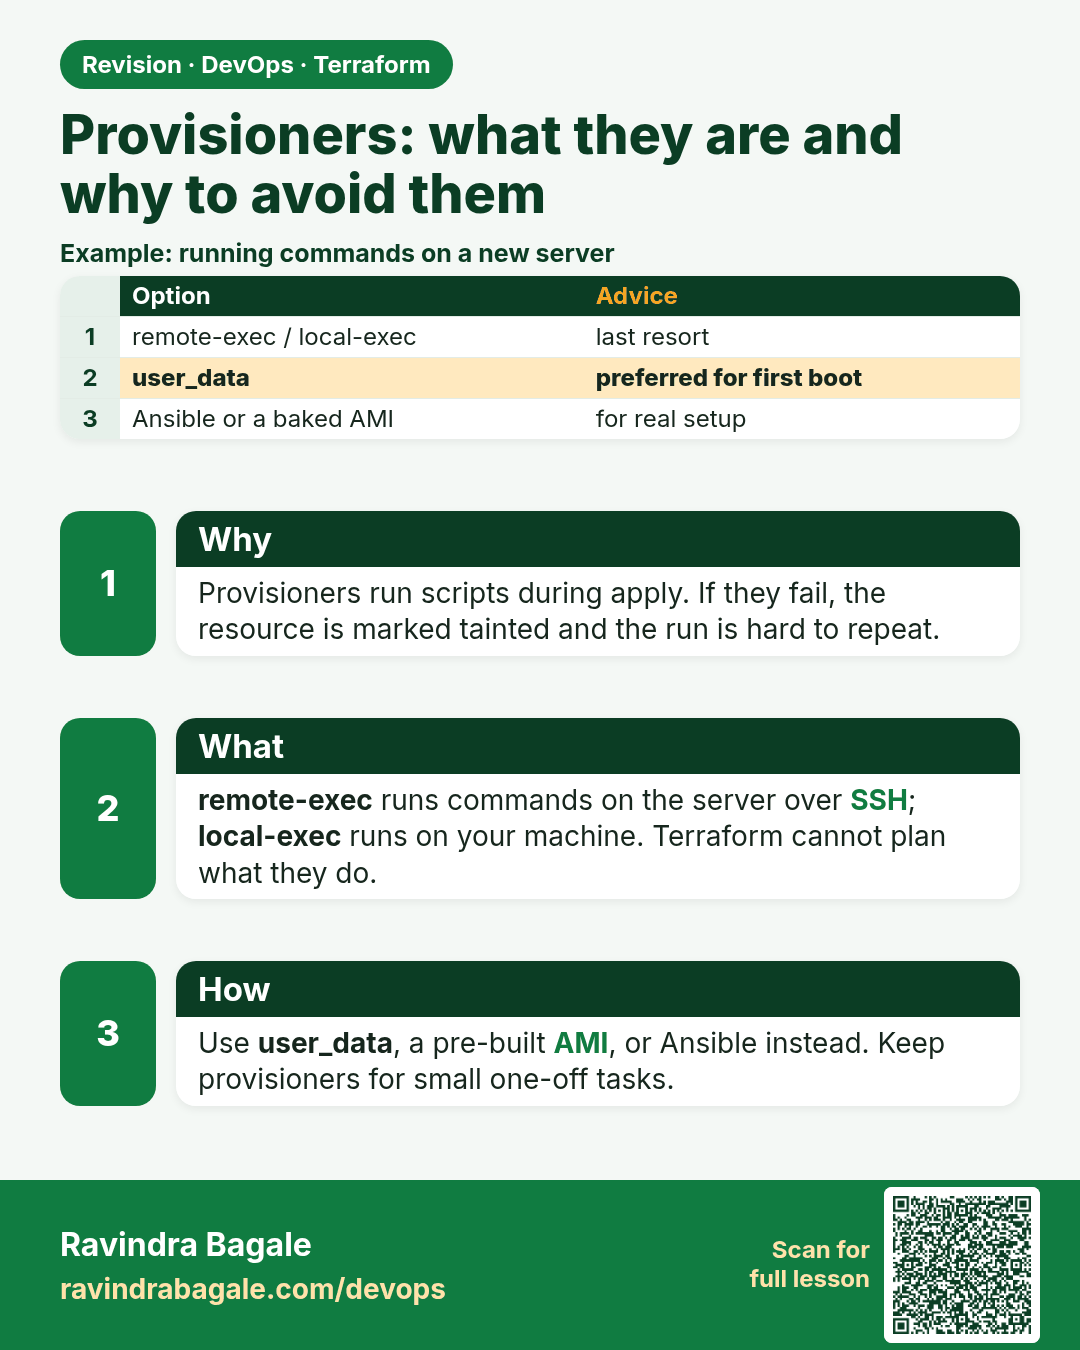
Provisioners: what they are and why to avoid them. Provisioners run scripts during apply. If they fail, the resource is marked tainted and the run is hard to repeat.
Revision card 1 of 3: Provisioners: what they are and why to avoid them · Download PNG · Open card page

Lesson: 39.1 Provisioners — what they are and why to avoid them
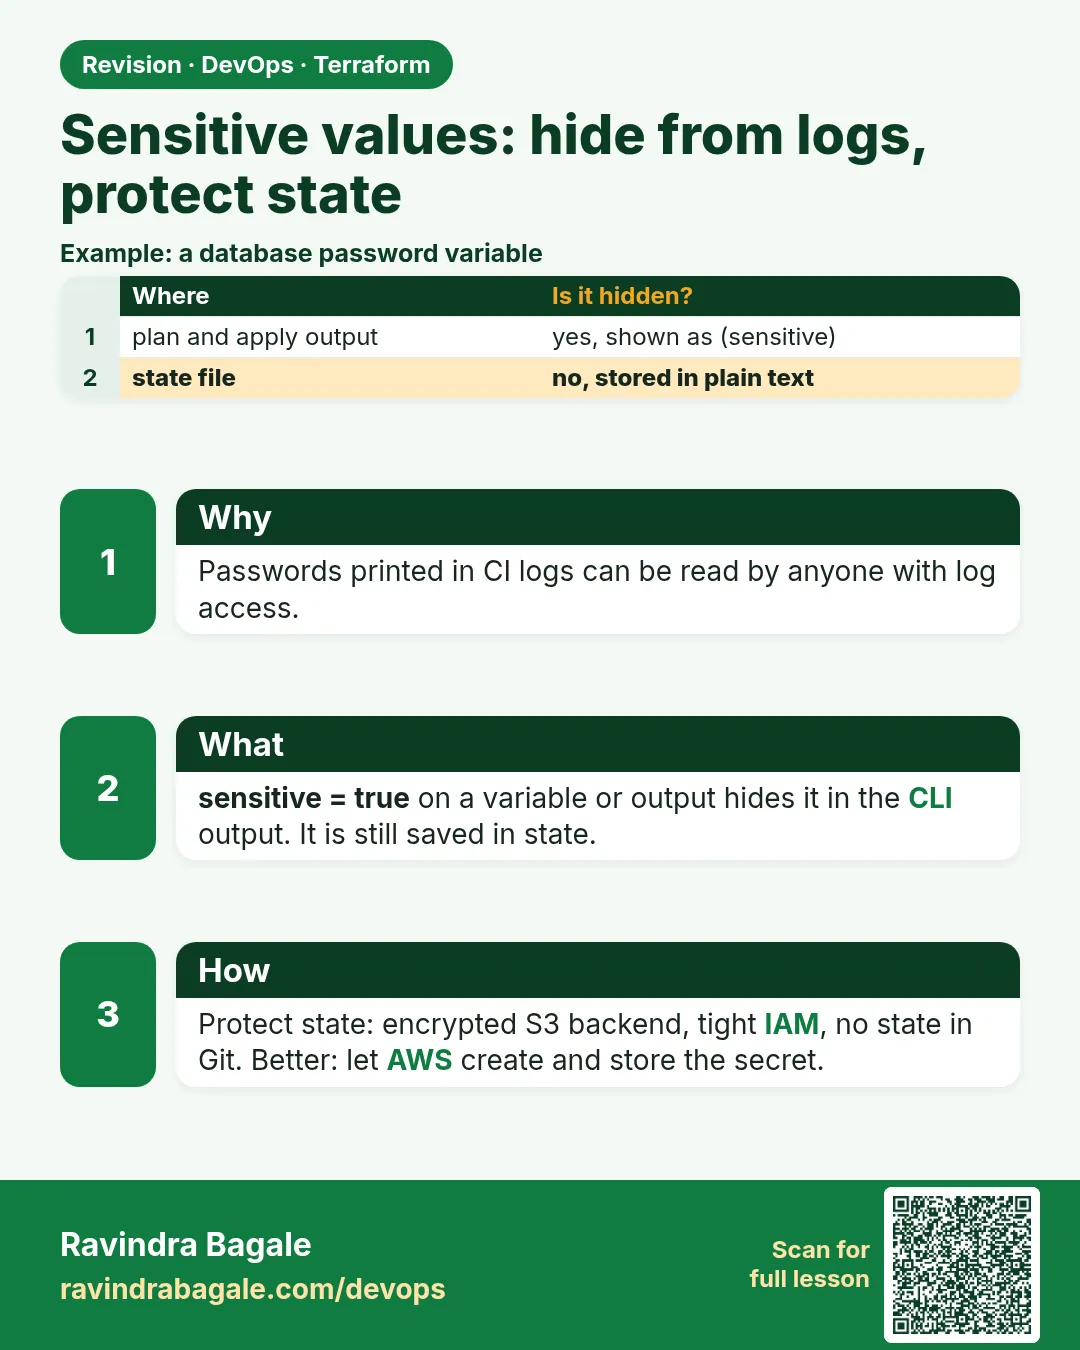
Sensitive values: hide from logs, protect state. Passwords printed in CI logs can be read by anyone with log access.
Revision card 2 of 3: Sensitive values: hide from logs, protect state · Download PNG · Open card page

Lesson: 39.2 sensitive values — hide from logs, protect state

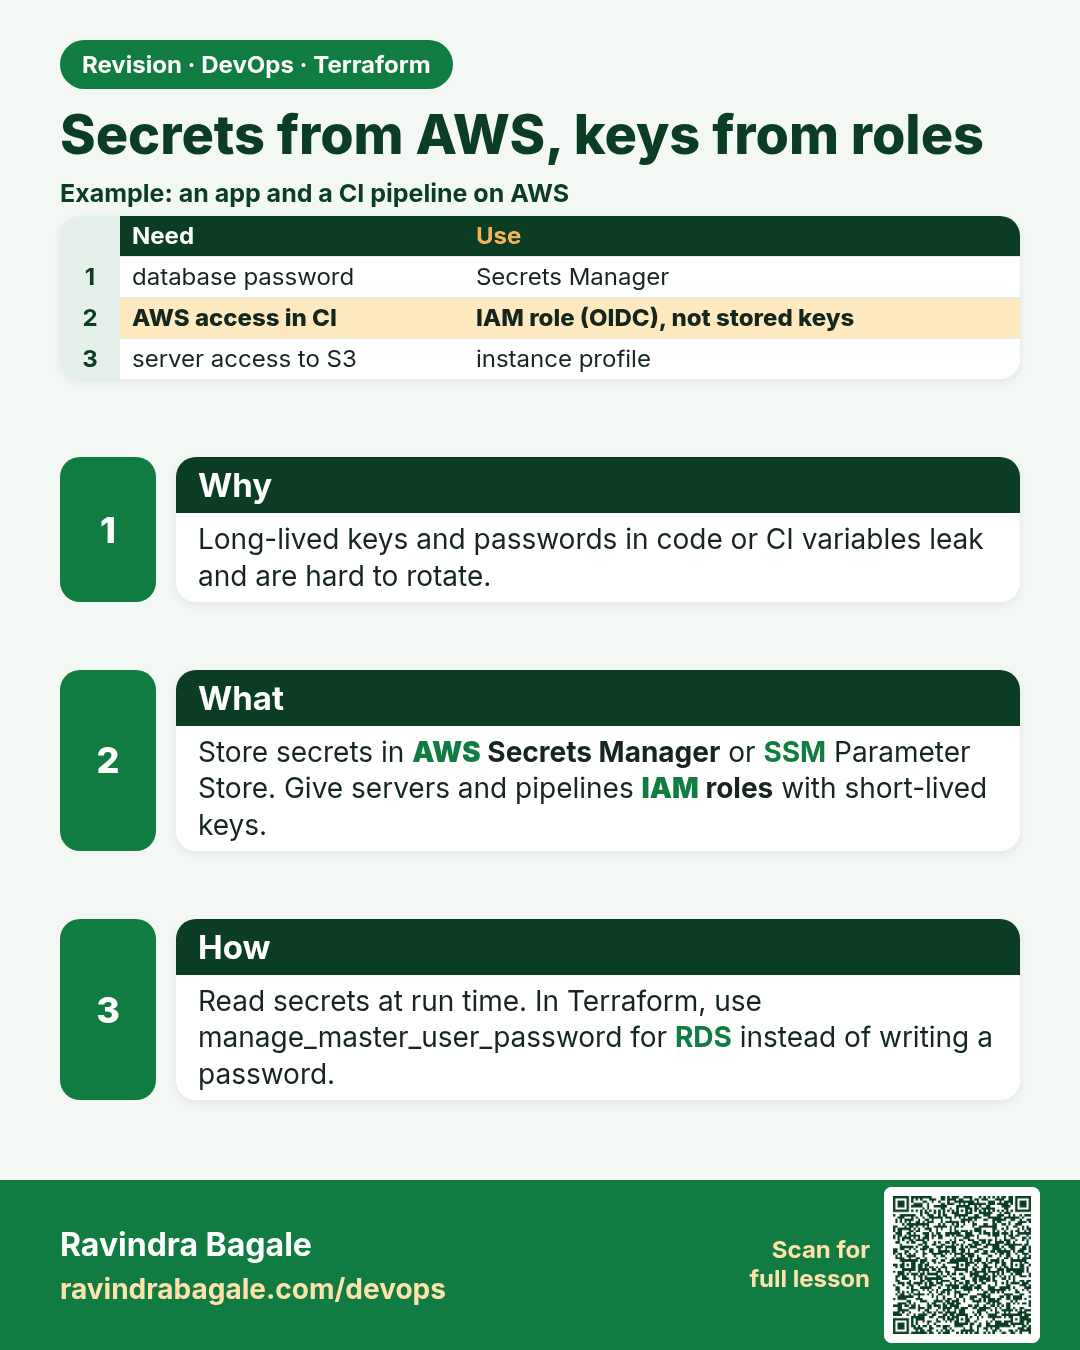
Secrets from AWS, keys from roles. Long-lived keys and passwords in code or CI variables leak and are hard to rotate.
Revision card 3 of 3: Secrets from AWS, keys from roles · Download PNG · Open card page

Lesson: 39.3 Secrets from AWS, keys from roles

Interview cards

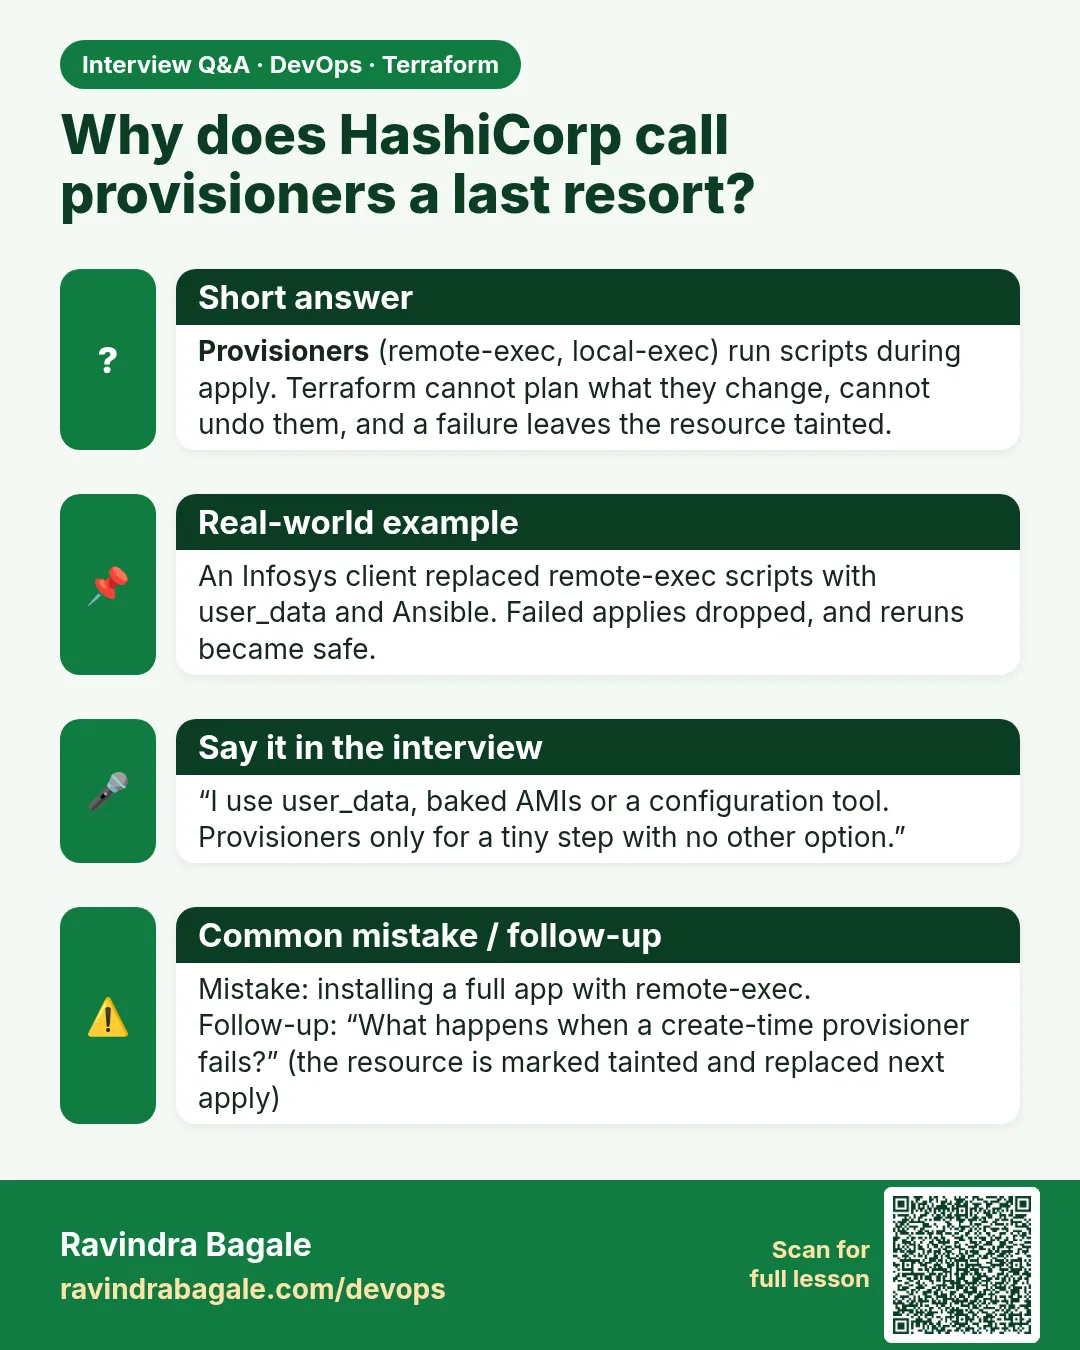
Why does HashiCorp call provisioners a last resort? Provisioners (remote-exec, local-exec) run scripts during apply. Terraform cannot plan what they change, cannot undo them, and a failure leaves the resource tainted.
Interview card 1 of 3: Why does HashiCorp call provisioners a last resort? · Download PNG · Open card page

Lesson: 39.1 Provisioners — what they are and why to avoid them
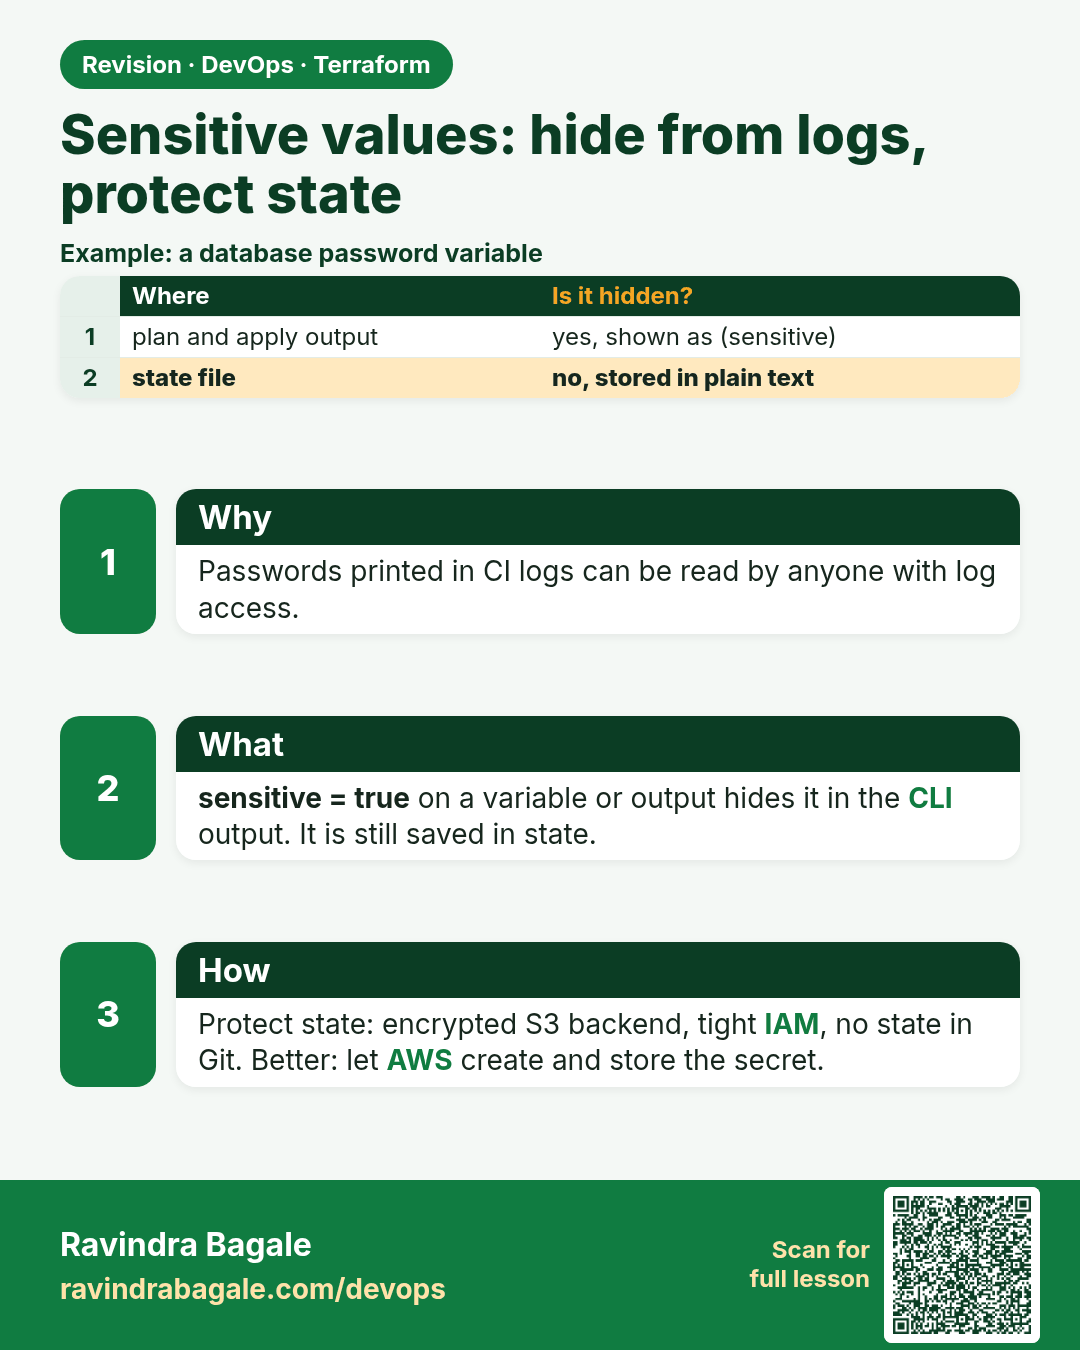
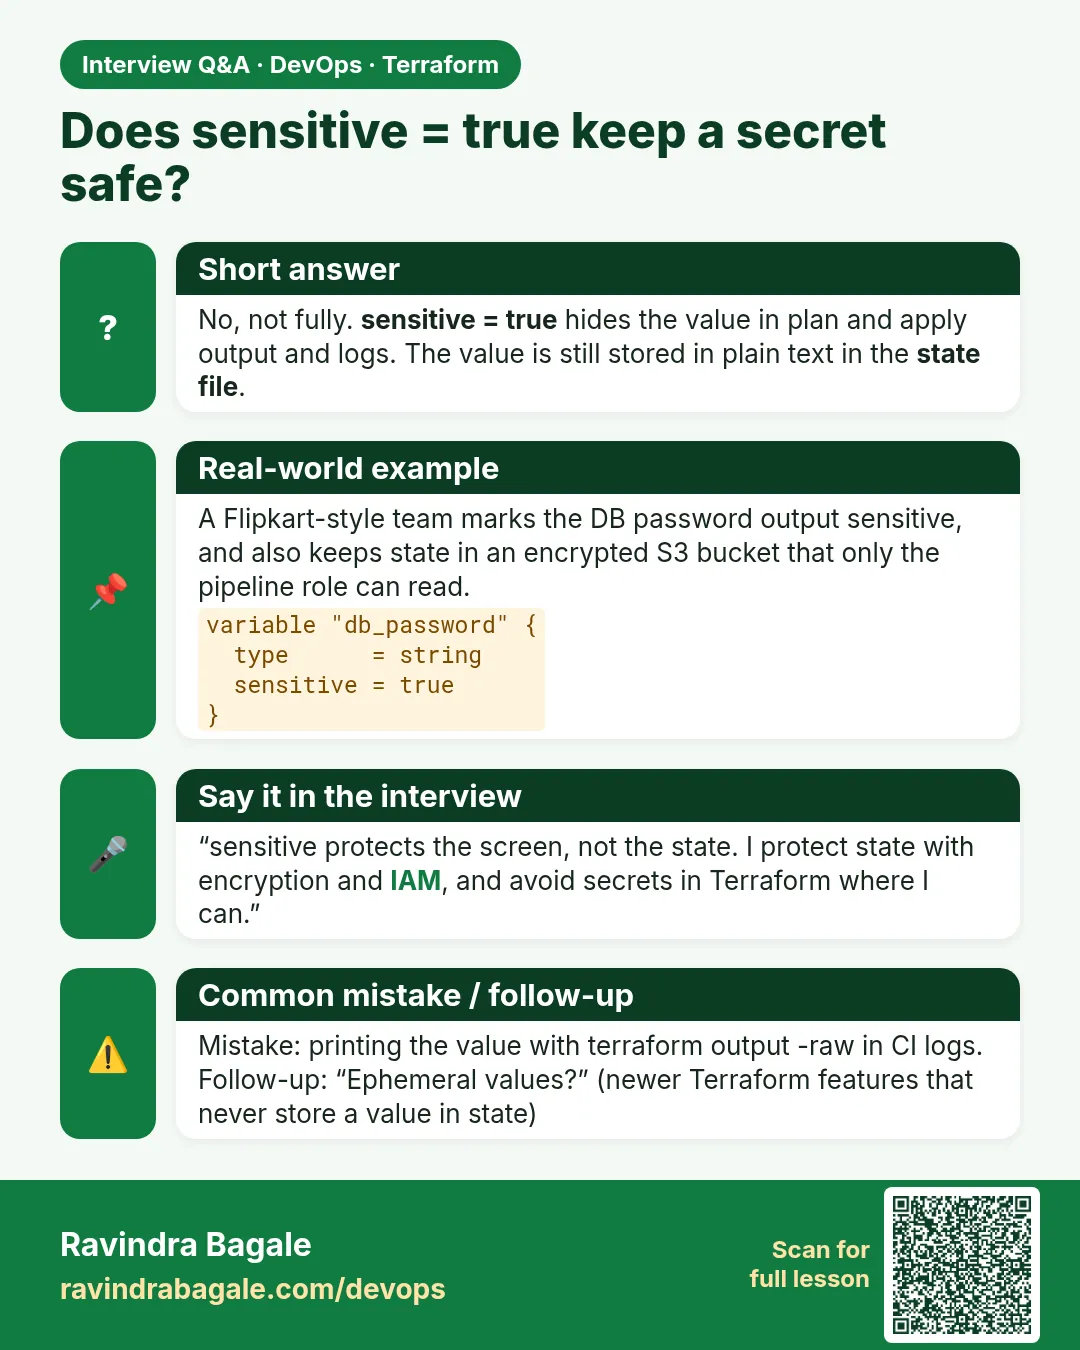
Does sensitive = true keep a secret safe? No, not fully. sensitive = true hides the value in plan and apply output and logs. The value is still stored in plain text in the state file.
Interview card 2 of 3: Does sensitive = true keep a secret safe? · Download PNG · Open card page

Lesson: 39.2 sensitive values — hide from logs, protect state
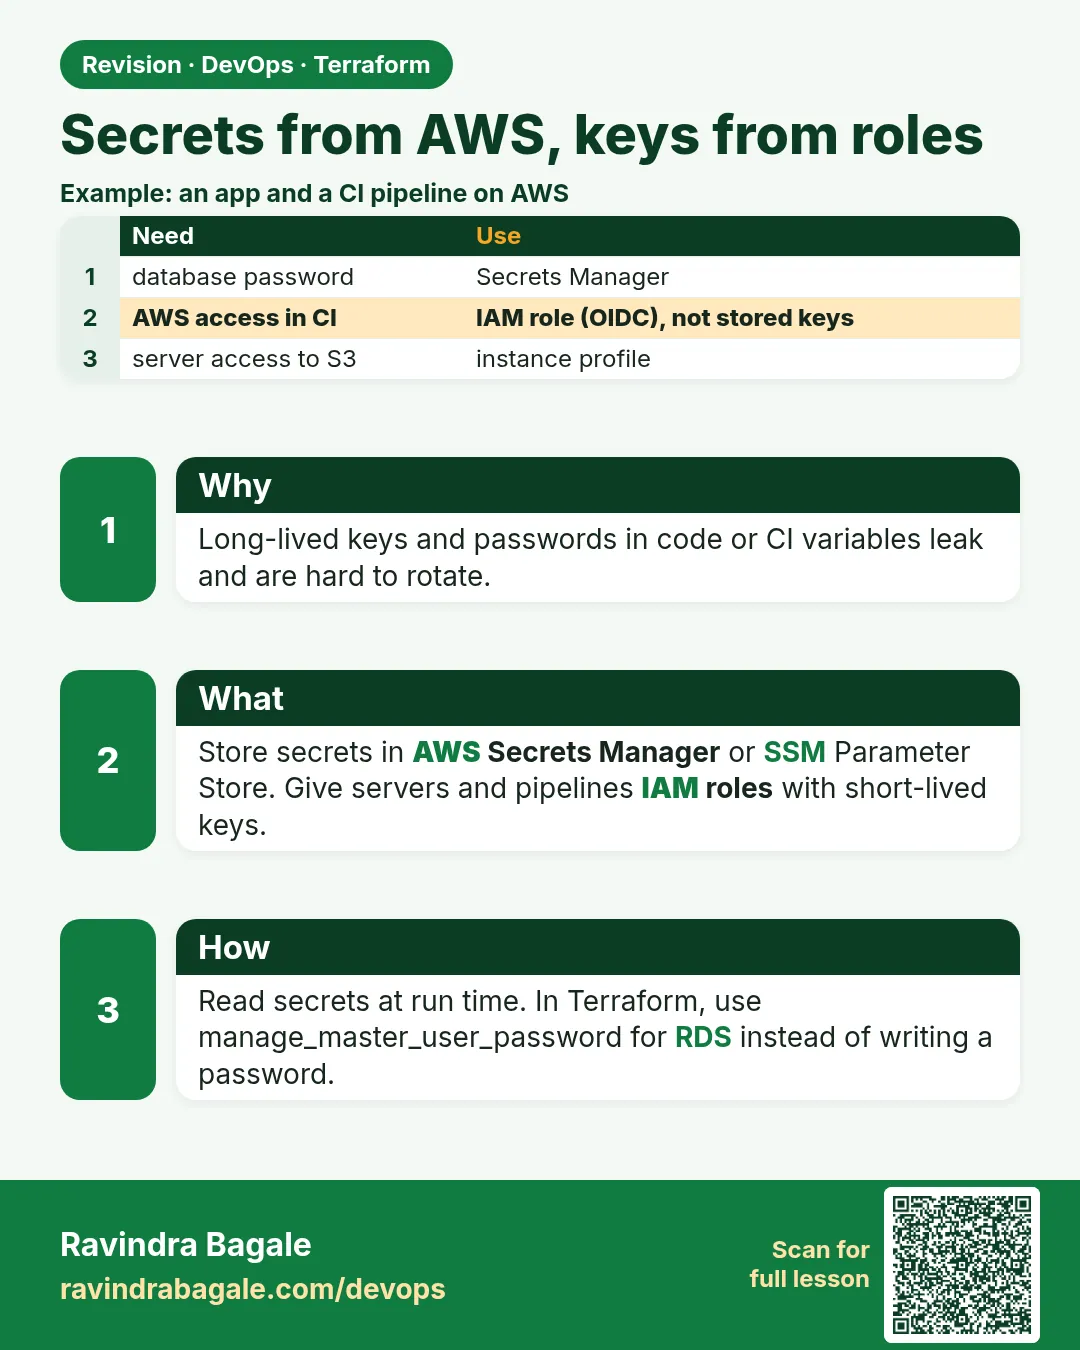
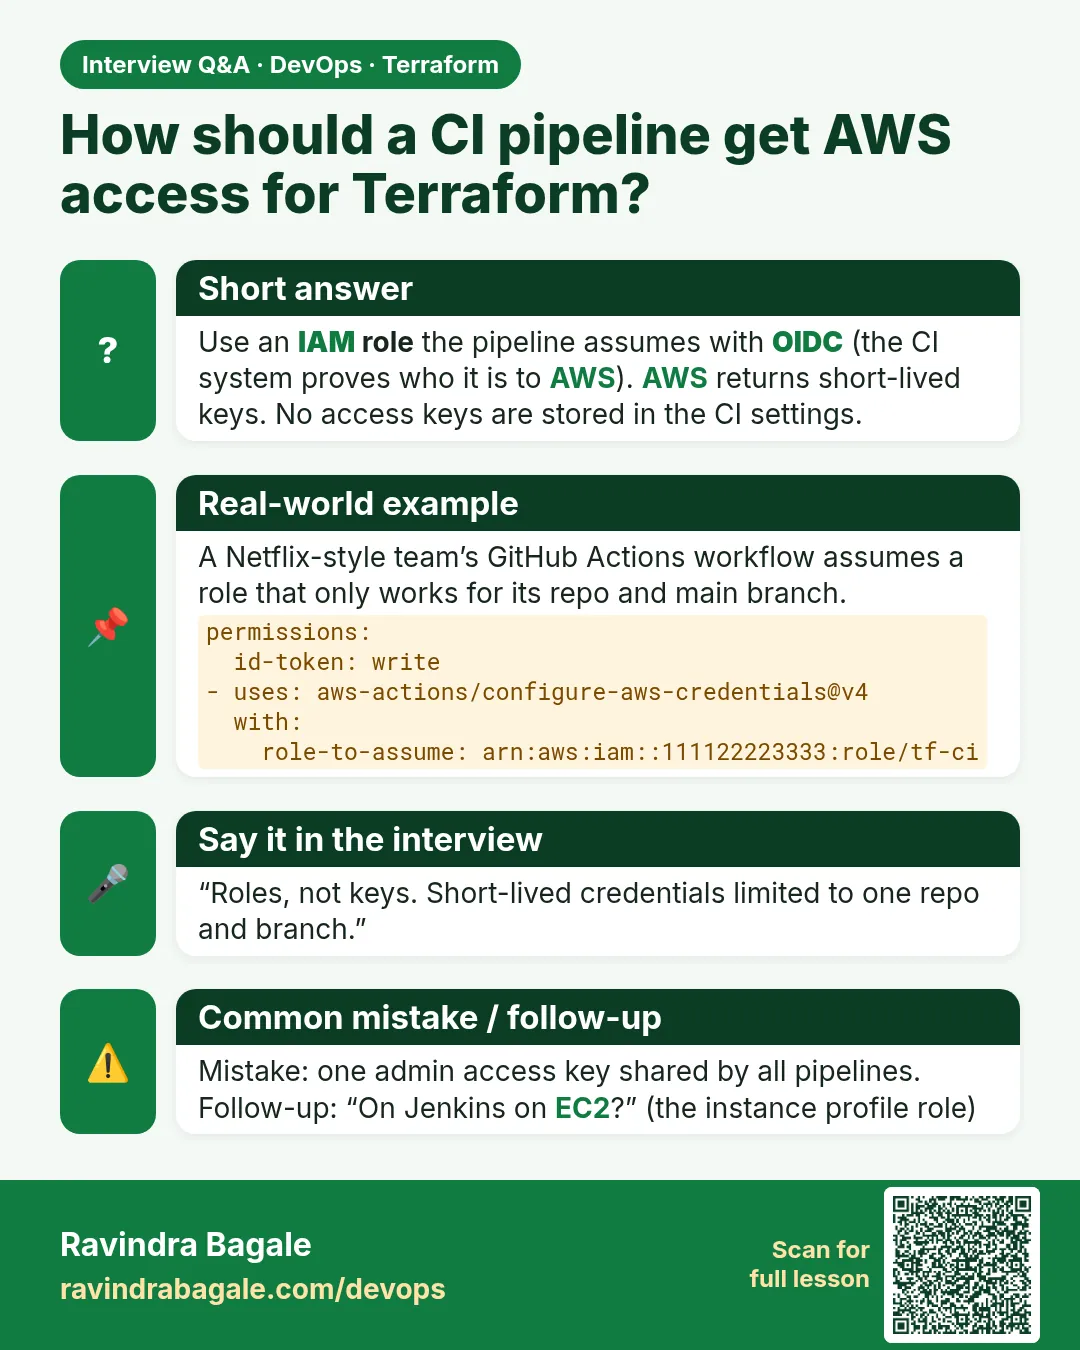
How should a CI pipeline get AWS access for Terraform? Use an IAM role the pipeline assumes with OIDC (the CI system proves who it is to AWS). AWS returns short-lived keys. No access keys are stored in the CI settings.
Interview card 3 of 3: How should a CI pipeline get AWS access for Terraform? · Download PNG · Open card page

Lesson: 39.3 Secrets from AWS, keys from roles

Comparison cards
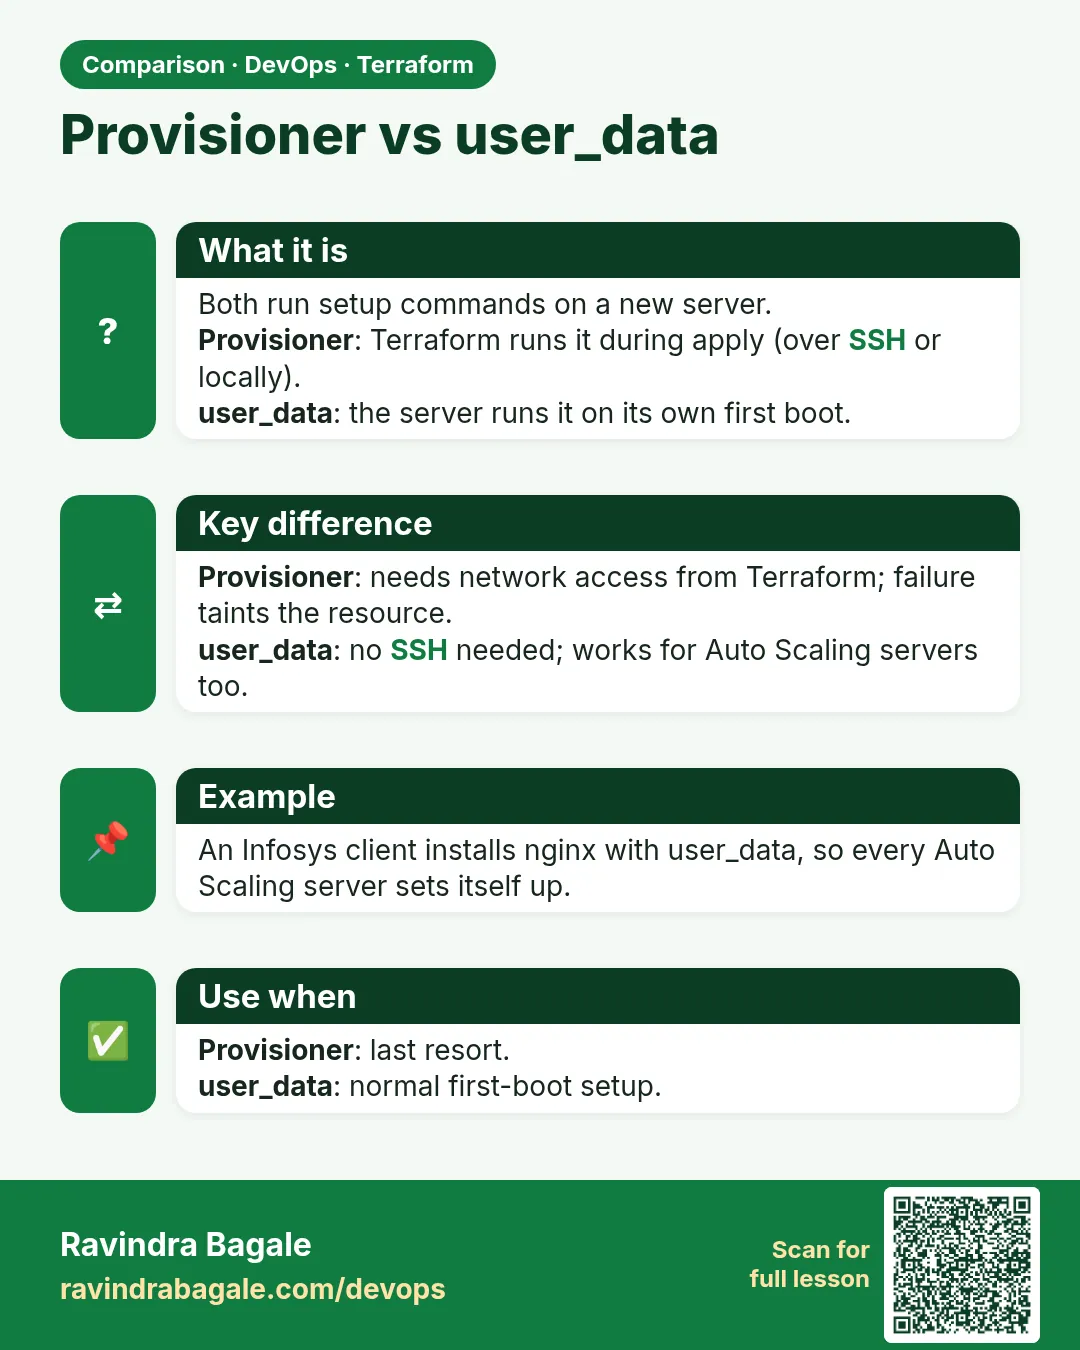
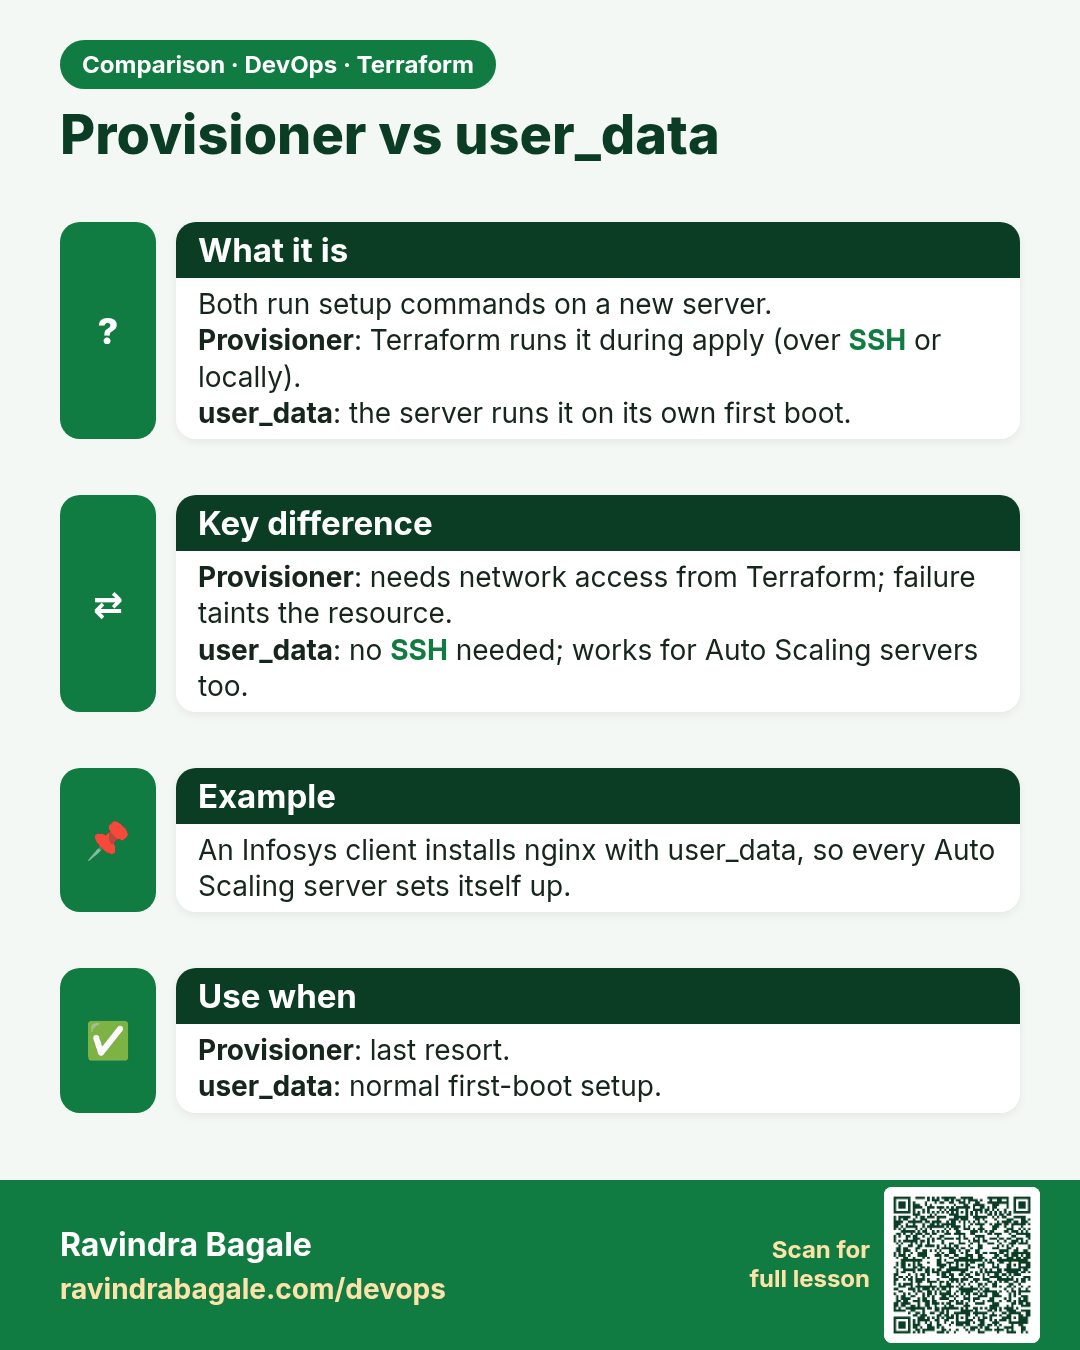
Provisioner vs user_data. Both run setup commands on a new server.Provisioner: Terraform runs it during apply (over SSH or locally).user_data: the server runs it on its own first boot.
Comparison card 1 of 3: Provisioner vs user_data · Download PNG · Open card page

Lesson: Chapter 39: Terraform Provisioners Secrets and Sensitive Values
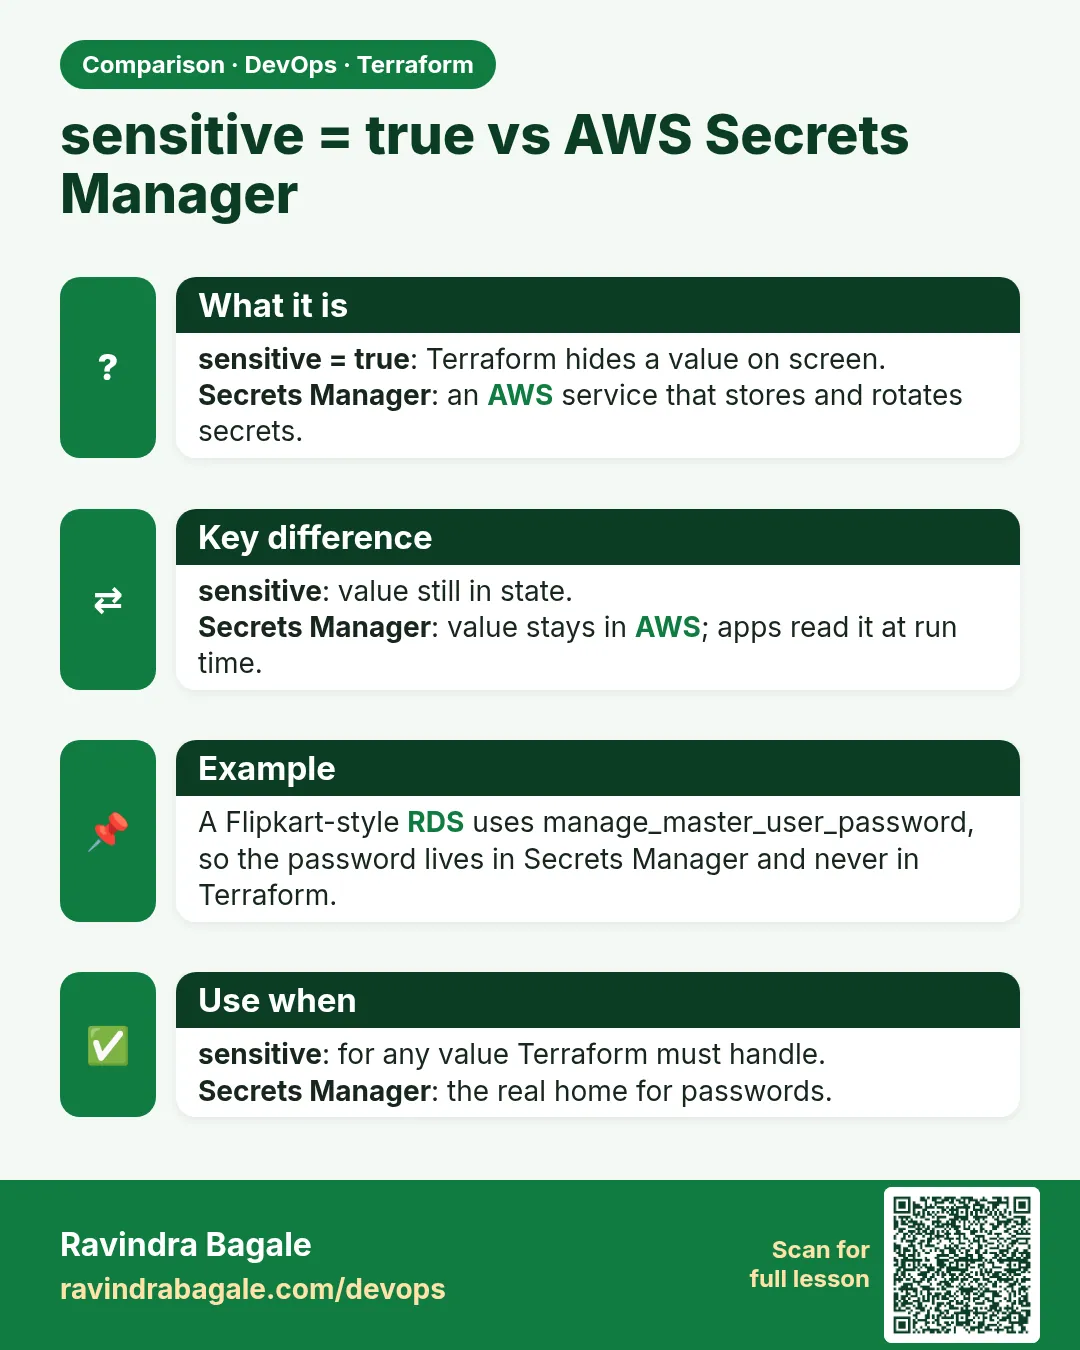
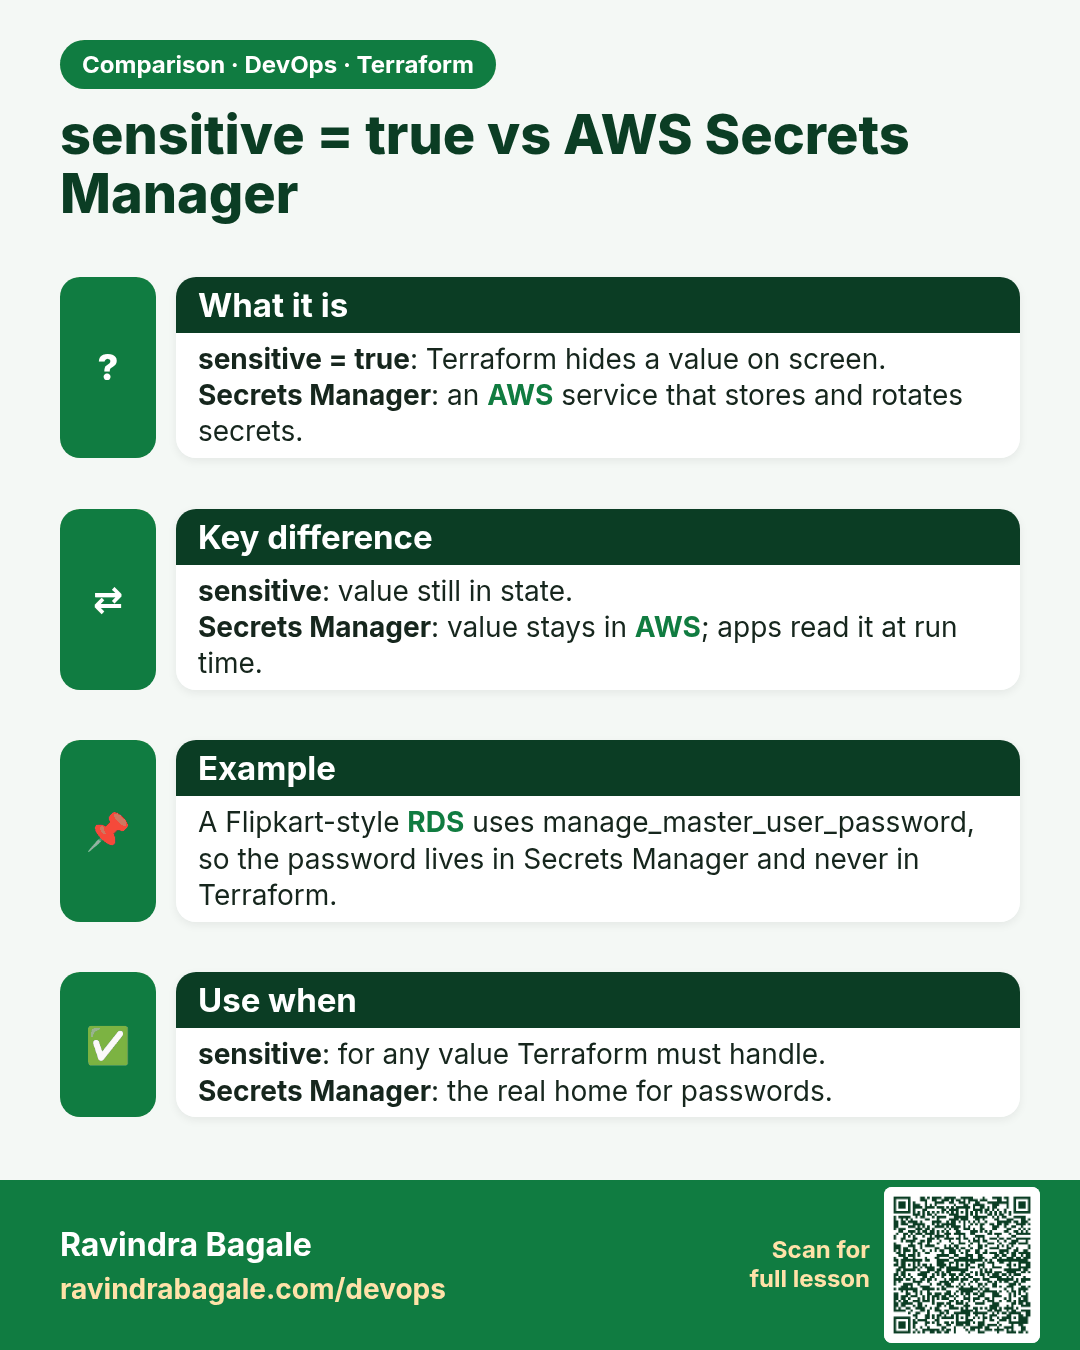
sensitive = true vs AWS Secrets Manager. sensitive = true: Terraform hides a value on screen.Secrets Manager: an AWS service that stores and rotates secrets.
Comparison card 2 of 3: sensitive = true vs AWS Secrets Manager · Download PNG · Open card page

Lesson: Chapter 39: Terraform Provisioners Secrets and Sensitive Values
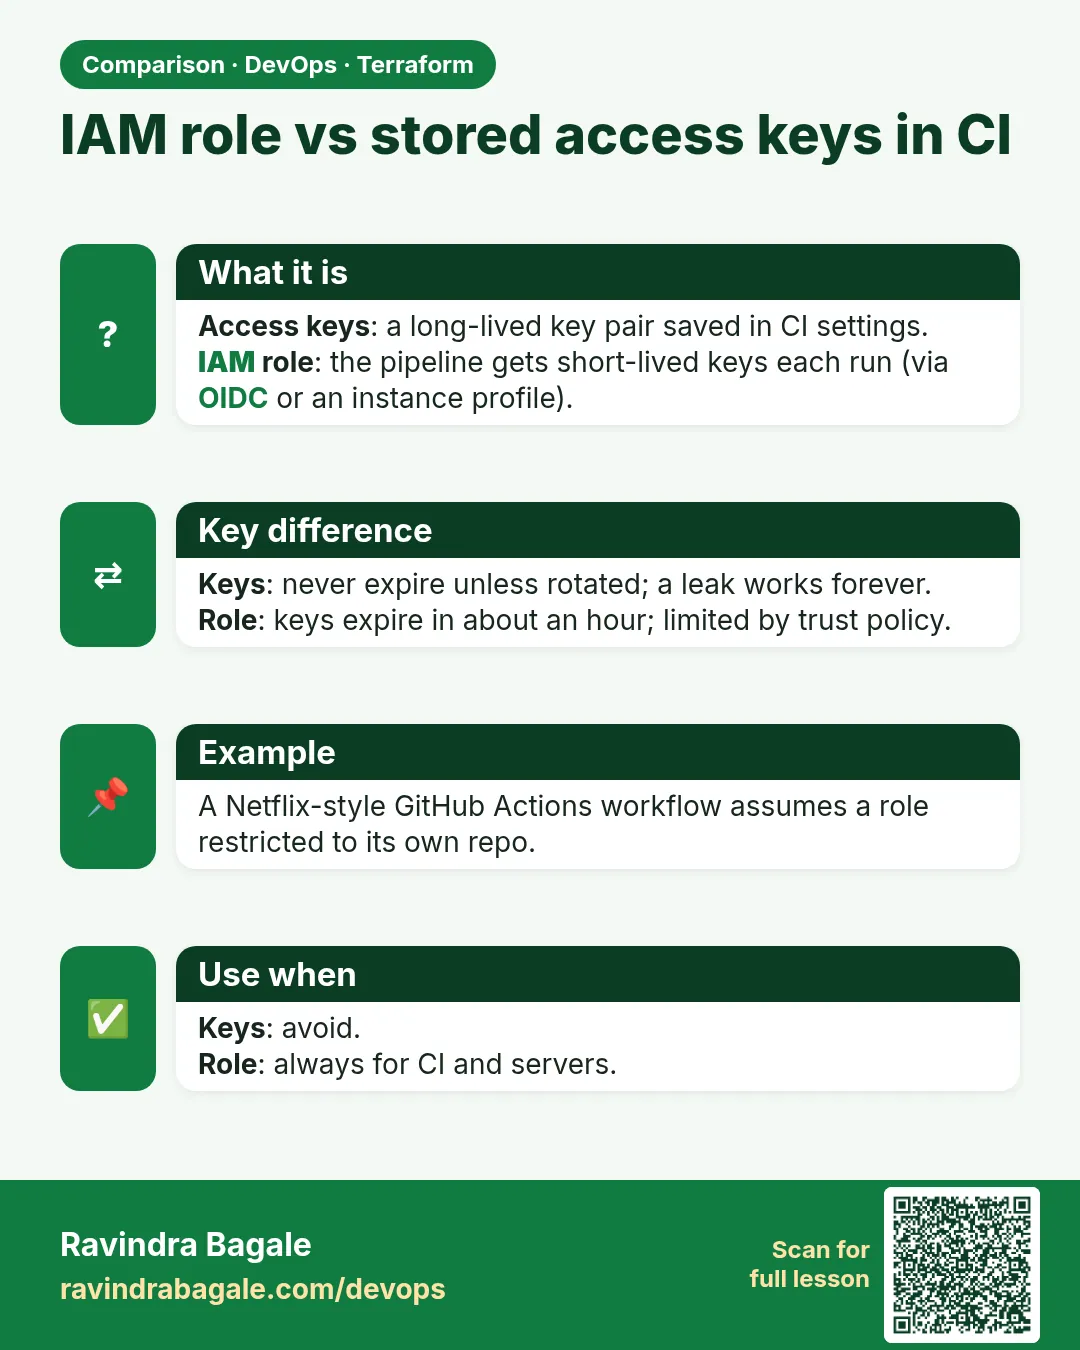
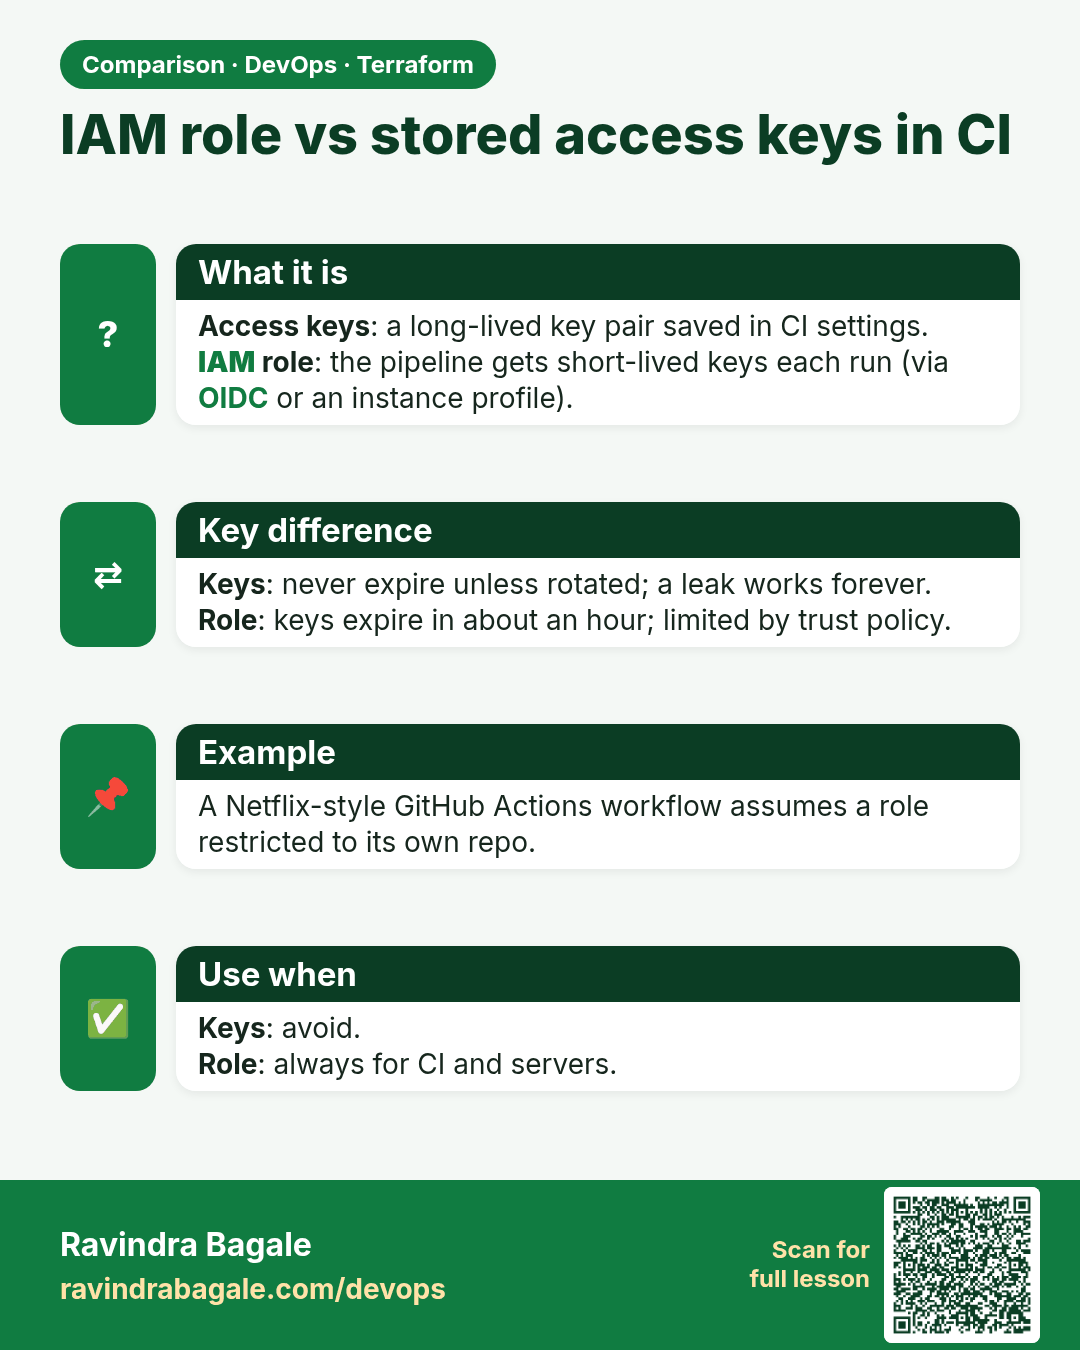
IAM role vs stored access keys in CI. Access keys: a long-lived key pair saved in CI settings.IAM role: the pipeline gets short-lived keys each run (via OIDC or an instance profile).
Comparison card 3 of 3: IAM role vs stored access keys in CI · Download PNG · Open card page

Lesson: Chapter 39: Terraform Provisioners Secrets and Sensitive Values