Ravi Sir's Cards › Chapter 44: Terraform AWS Guides EC2 RDS S3 Security Groups IAM ALB and Auto Scaling
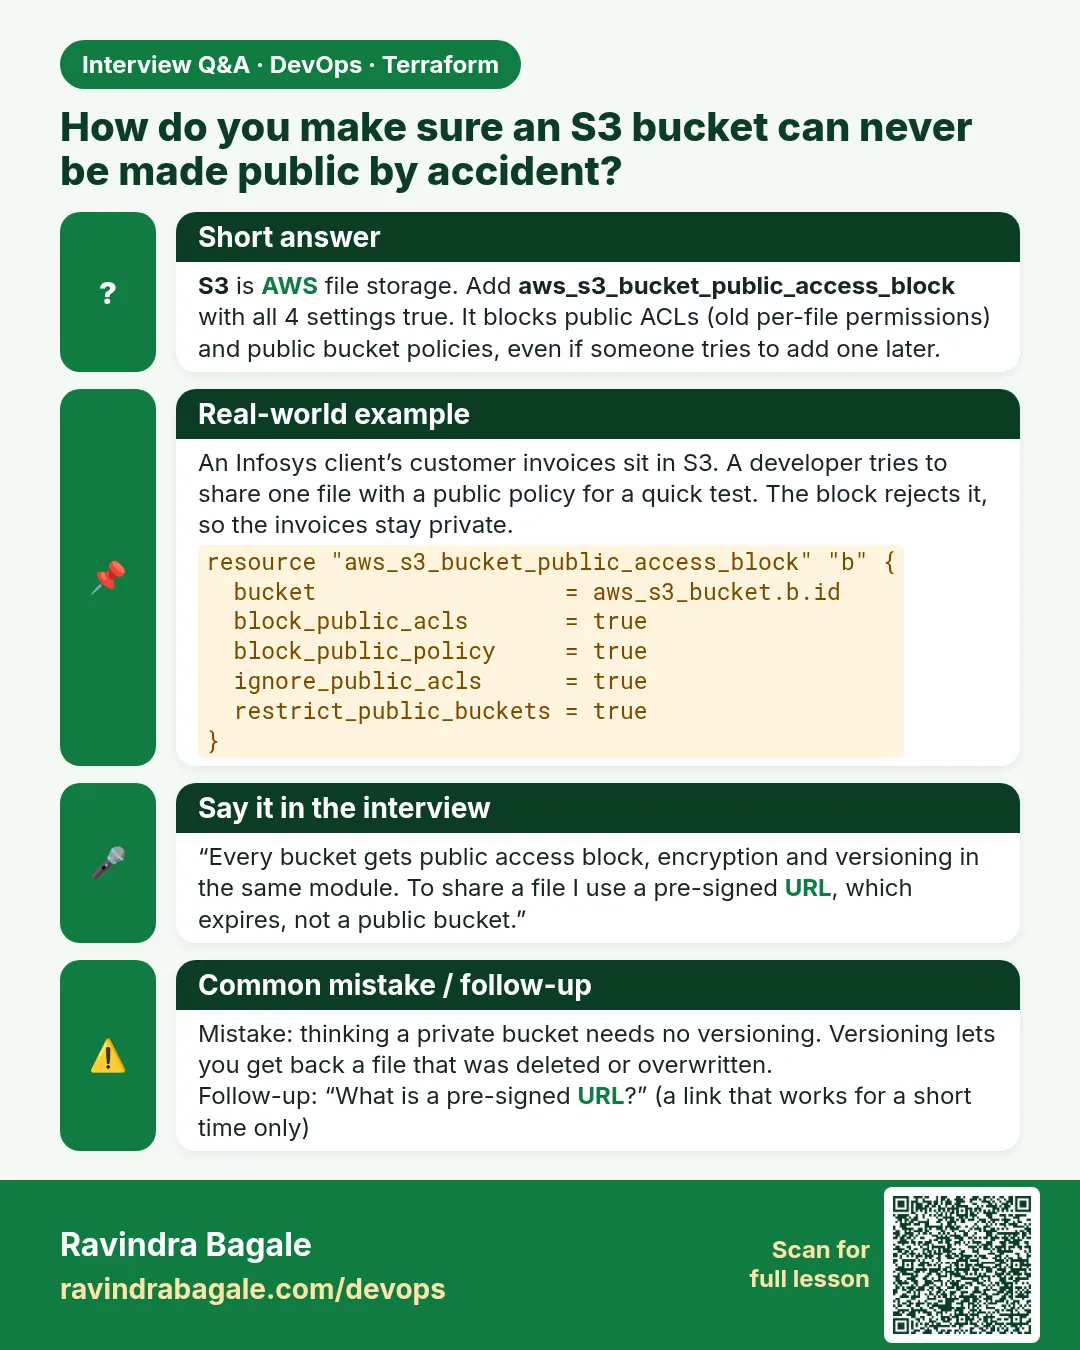
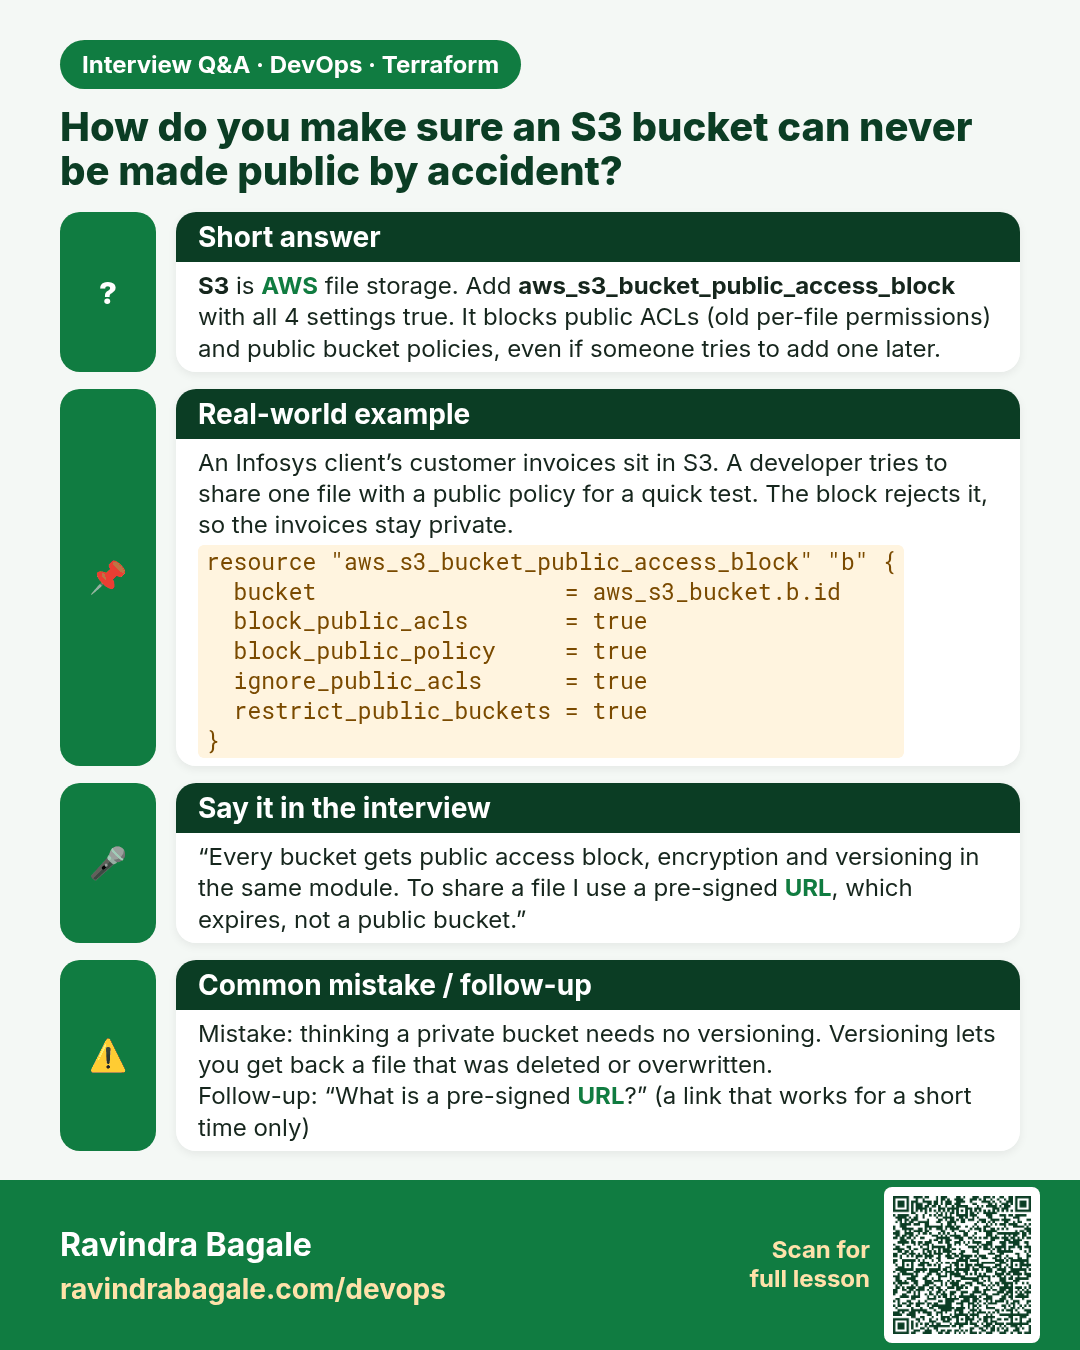
How do you make sure an S3 bucket can never be made public by accident?
How do you make sure an S3 bucket can never be made public by accident? S3 is AWS file storage. Add aws_s3_bucket_public_access_block with all 4 settings true. It blocks public ACLs (old per-file permissions) and public bucket policies, even if someone tries to add one later.
Lesson: 44.3 How to create a secure S3 bucket with Terraform · मराठी card