Ravi Sir's Cyber Security Cards › Revision Cards
Privilege Escalation Paths and Domain Admin Risks
Privilege Escalation Paths and Domain Admin Risks The common ways an attacker climbs from a normal AD user to Domain Admin . Backup Operators, Account Operators, DNS Admins and replication rights ( DCSync ). Treat them as almost as powerful as Domain Admin. Clean up nested groups. Use just-in-time a
Read card text
What this card says
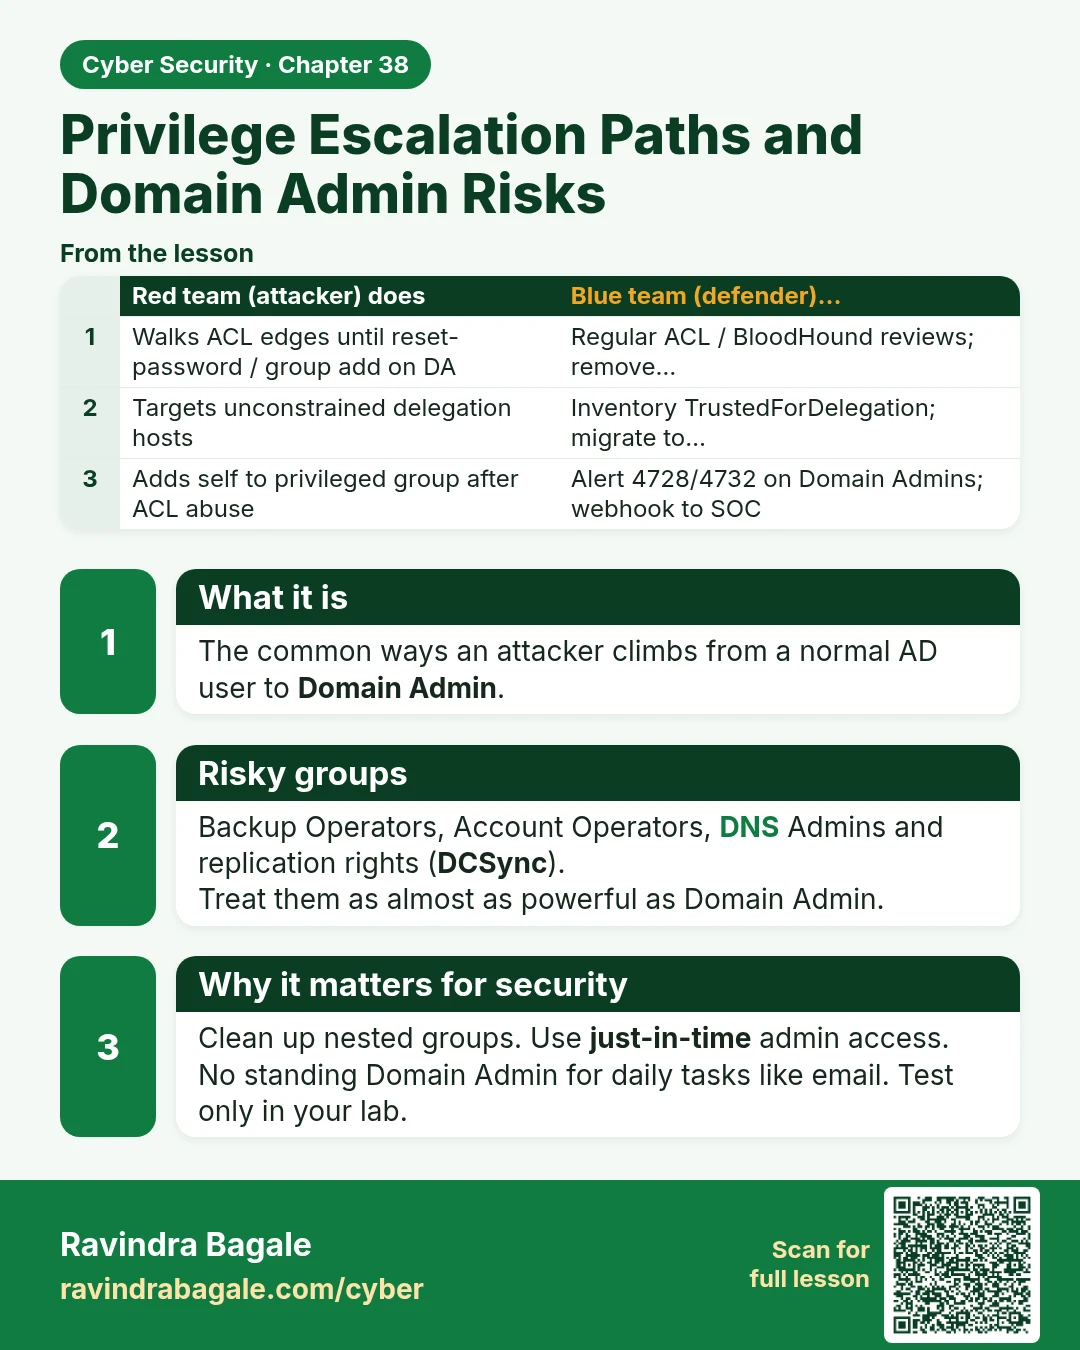
What it is
The common ways an attacker climbs from a normal AD user to Domain Admin.
Risky groups
Backup Operators, Account Operators, DNS Admins and replication rights (DCSync).
Treat them as almost as powerful as Domain Admin.
Why it matters for security
Clean up nested groups. Use just-in-time admin access.
No standing Domain Admin for daily tasks like email. Test only in your lab.
| Red team (attacker) does | Blue team (defender)… |
|---|---|
| Walks ACL edges until reset-password / group add on DA | Regular ACL / BloodHound reviews; remove… |
| Targets unconstrained delegation hosts | Inventory TrustedForDelegation; migrate to… |
| Adds self to privileged group after ACL abuse | Alert 4728/4732 on Domain Admins; webhook to SOC |
Learn more in the lesson: 38.7 Privilege Escalation Paths and Domain Admin Risks