Ravi Sir's Cyber Security Cards › Revision Cards
Your Project as the Target: Roadmap for the Next Parts
Your Project as the Target: Roadmap for the Next Parts Your own reels app and lab are the only targets you will practise on. Scan it, test the web app, try password attacks, then fix each finding. Running tools against friends’ or company websites “just to look”. That is a crime and can end your car
Read card text
What this card says
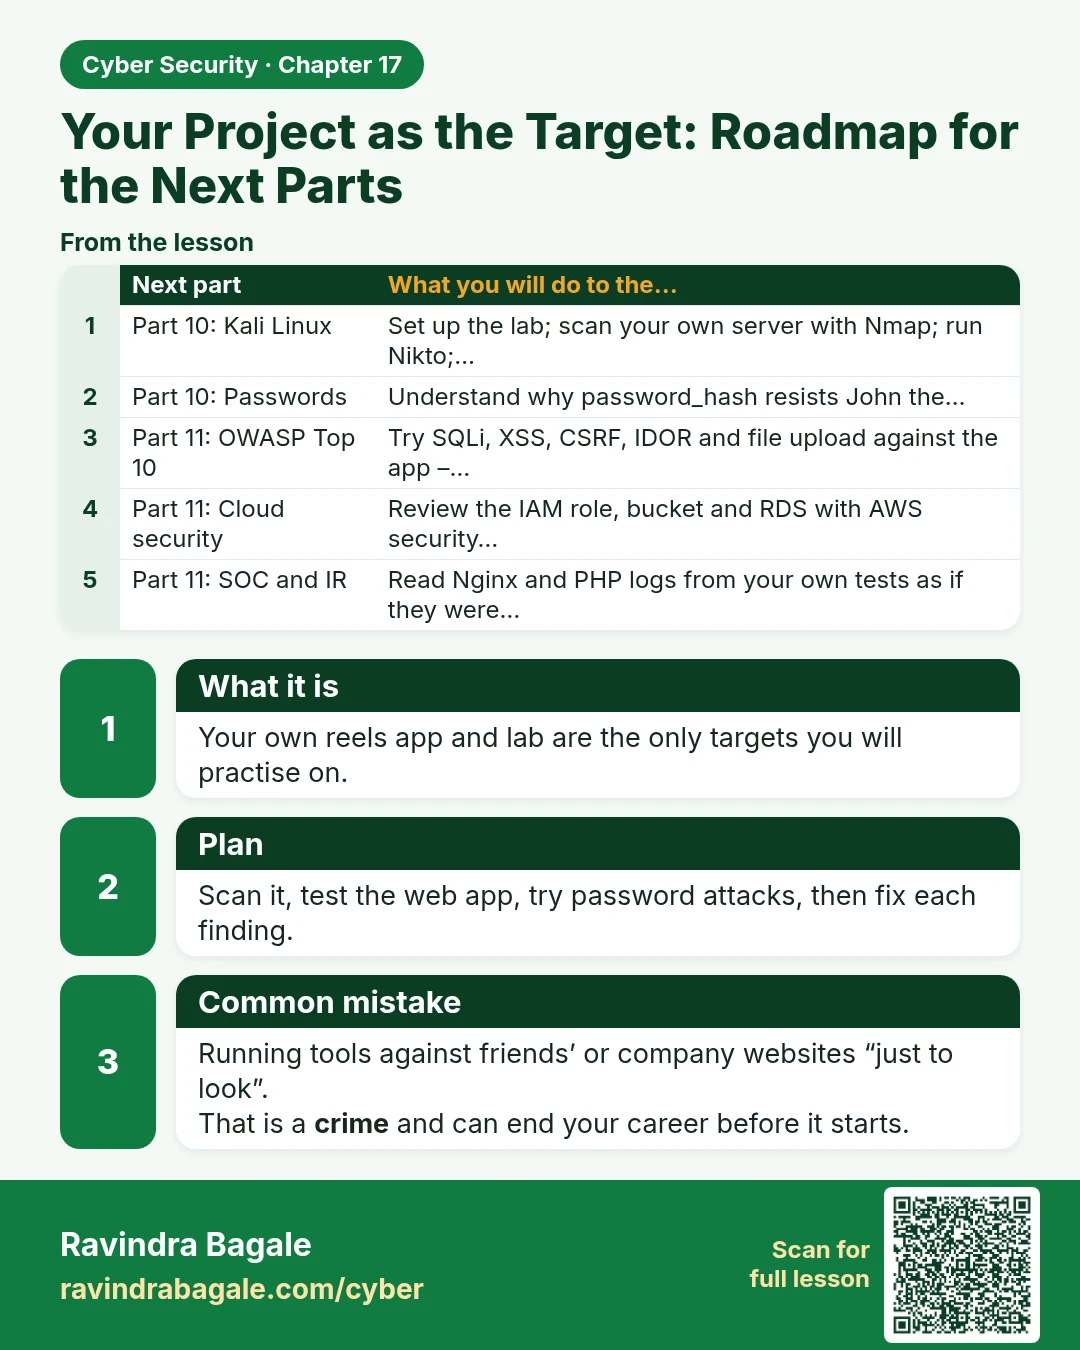
What it is
Your own reels app and lab are the only targets you will practise on.
Plan
Scan it, test the web app, try password attacks, then fix each finding.
Common mistake
Running tools against friends’ or company websites “just to look”.
That is a crime and can end your career before it starts.
| Next part | What you will do to the… |
|---|---|
| Part 10: Kali Linux | Set up the lab; scan your own server with Nmap; run Nikto;… |
| Part 10: Passwords | Understand why password_hash resists John the… |
| Part 11: OWASP Top 10 | Try SQLi, XSS, CSRF, IDOR and file upload against the app –… |
| Part 11: Cloud security | Review the IAM role, bucket and RDS with AWS security… |
| Part 11: SOC and IR | Read Nginx and PHP logs from your own tests as if they were… |
Learn more in the lesson: 17.7 Your Project as the Target: Roadmap for the Next Parts