Ravi Sir's Cyber Security Cards › Revision Cards
XSS Path to Session Cookies – Defence First
XSS Path to Session Cookies – Defence First XSS (Cross-Site Scripting) runs an attacker’s script in your browser on a trusted site. One use is stealing the session cookie. If the cookie is not HttpOnly , the script can read it and send it out. Even with HttpOnly, the script can still act as you on t
Read card text
What this card says
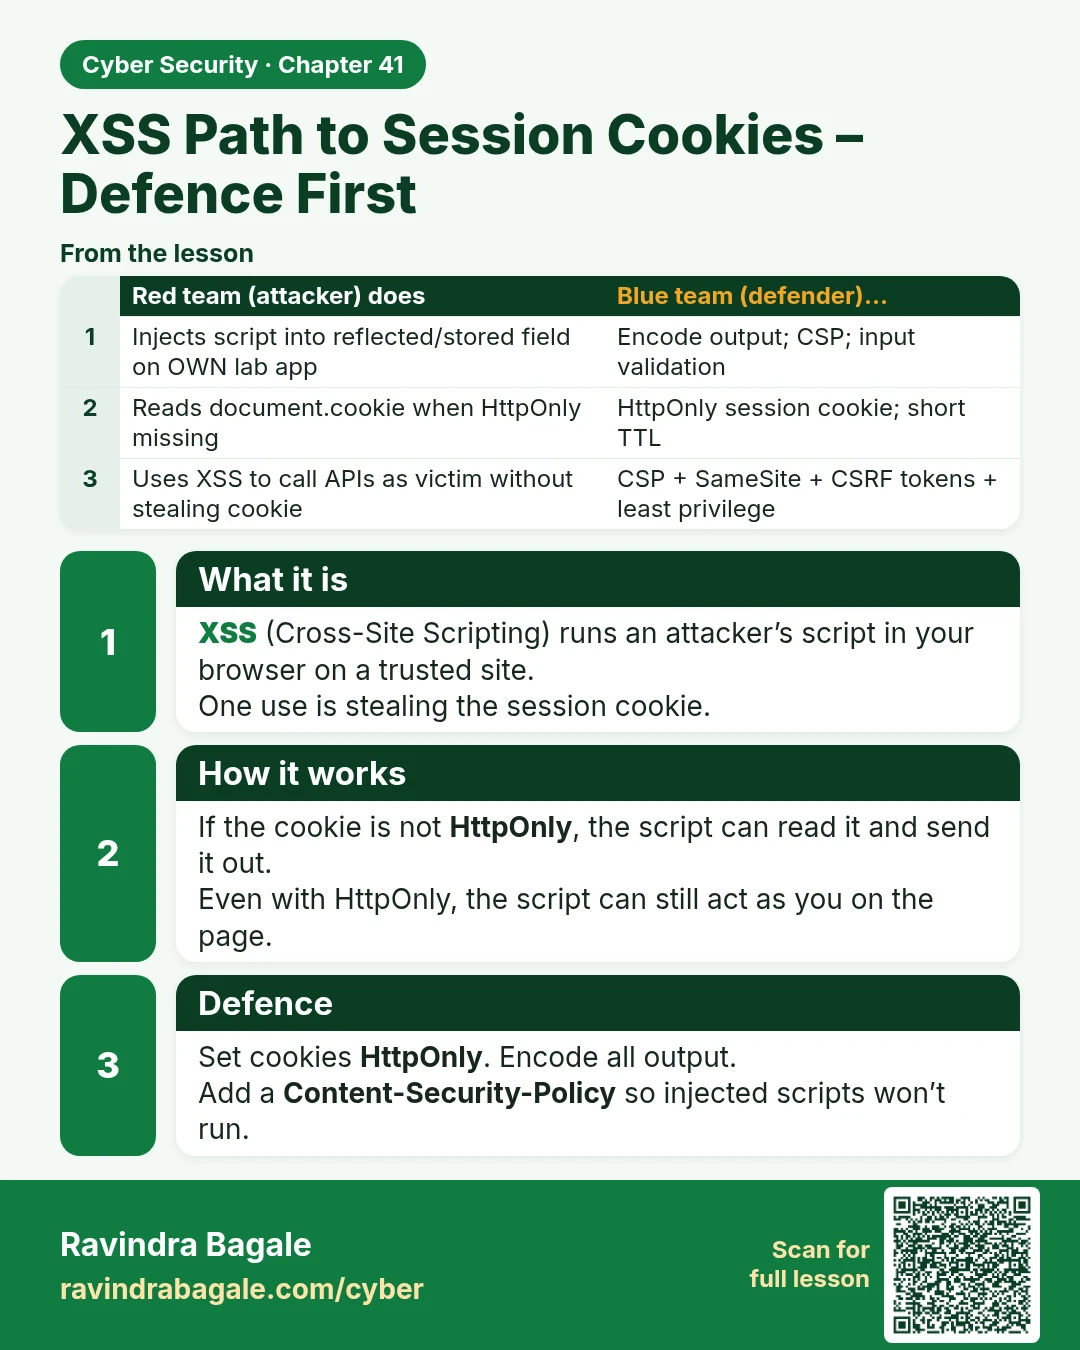
What it is
XSS (Cross-Site Scripting) runs an attacker’s script in your browser on a trusted site.
One use is stealing the session cookie.
How it works
If the cookie is not HttpOnly, the script can read it and send it out.
Even with HttpOnly, the script can still act as you on the page.
Defence
Set cookies HttpOnly. Encode all output.
Add a Content-Security-Policy so injected scripts won’t run.
| Red team (attacker) does | Blue team (defender)… |
|---|---|
| Injects script into reflected/stored field on OWN lab app | Encode output; CSP; input validation |
| Reads document.cookie when HttpOnly missing | HttpOnly session cookie; short TTL |
| Uses XSS to call APIs as victim without stealing cookie | CSP + SameSite + CSRF tokens + least privilege |
Learn more in the lesson: 41.4 XSS Path to Session Cookies – Defence First