Ravi Sir's Cyber Security Cards › Revision Cards
Writing a Vulnerability Report
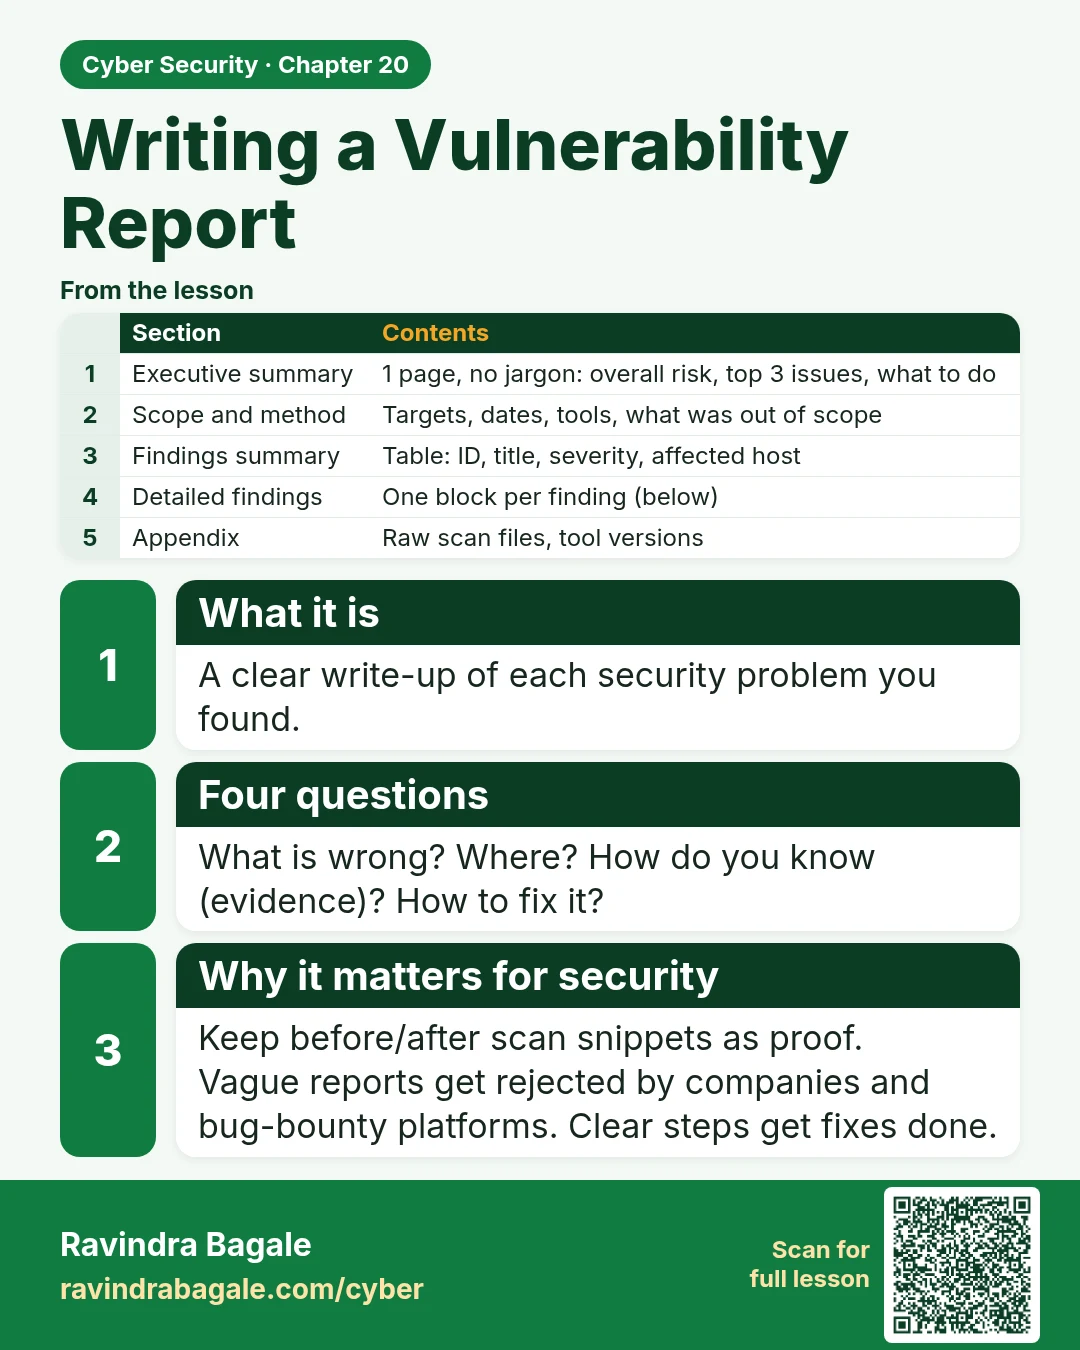
Writing a Vulnerability Report A clear write-up of each security problem you found. What is wrong? Where? How do you know (evidence)? How to fix it? Keep before/after scan snippets as proof. Vague reports get rejected by companies and bug-bounty platforms. Clear steps get fixes done.
Read card text
What this card says
What it is
A clear write-up of each security problem you found.
Four questions
What is wrong? Where? How do you know (evidence)? How to fix it?
Why it matters for security
Keep before/after scan snippets as proof.
Vague reports get rejected by companies and bug-bounty platforms. Clear steps get fixes done.
| Section | Contents |
|---|---|
| Executive summary | 1 page, no jargon: overall risk, top 3 issues, what to do |
| Scope and method | Targets, dates, tools, what was out of scope |
| Findings summary | Table: ID, title, severity, affected host |
| Detailed findings | One block per finding (below) |
| Appendix | Raw scan files, tool versions |
Learn more in the lesson: 20.7 Writing a Vulnerability Report