Ravi Sir's Cyber Security Cards › Revision Cards
Why HTTP Leaks and HTTPS Protects; ARP Spoofing
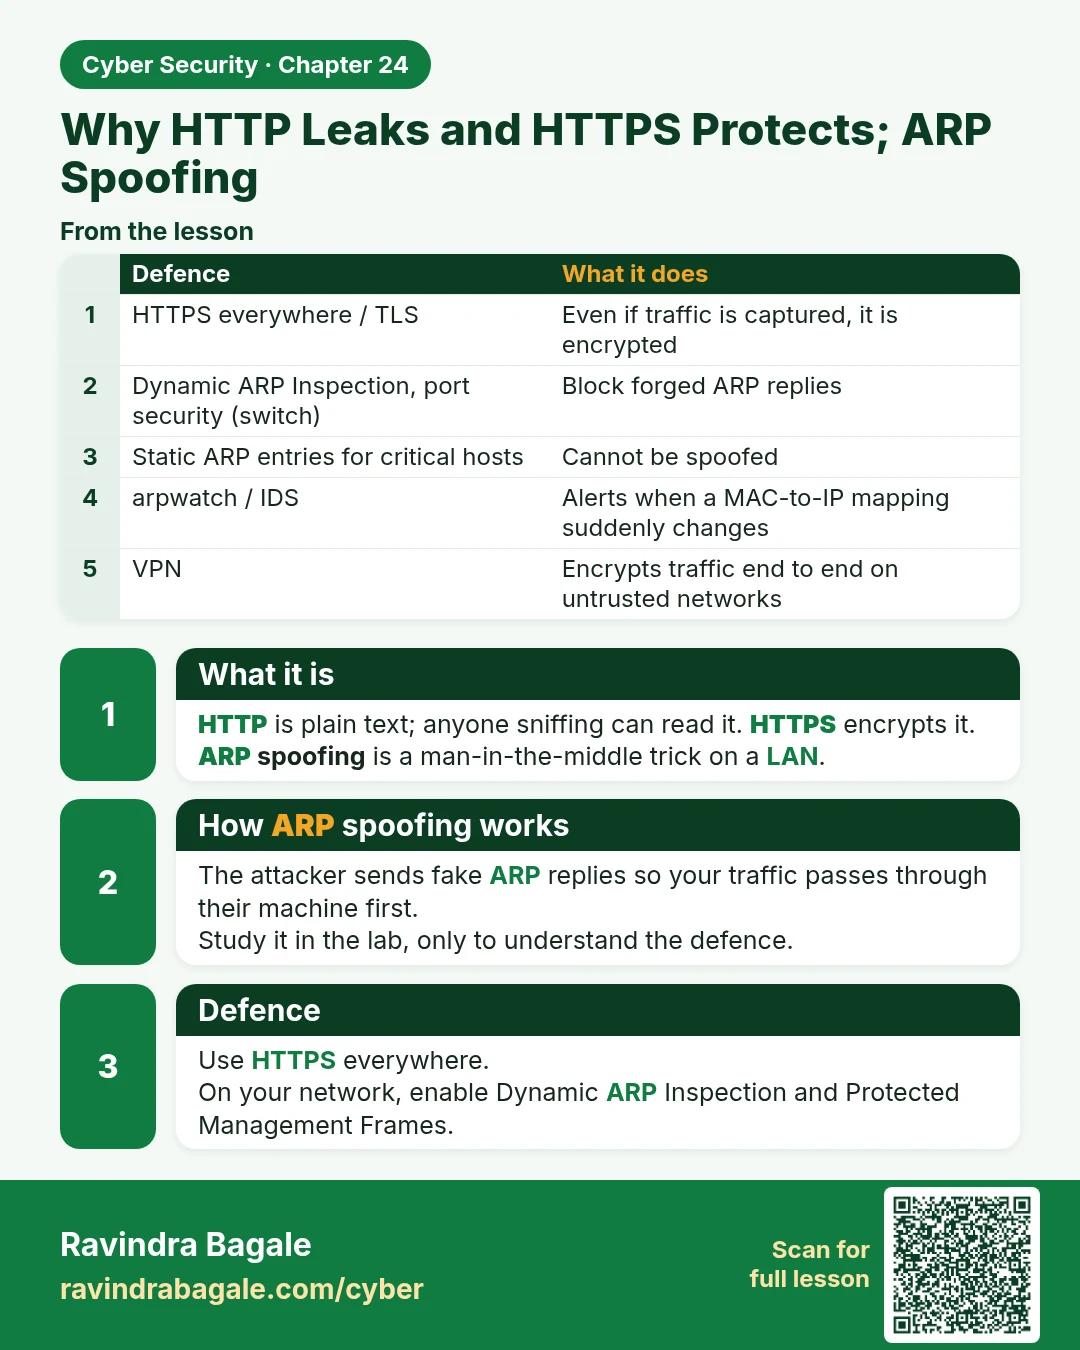
Why HTTP Leaks and HTTPS Protects; ARP Spoofing HTTP is plain text; anyone sniffing can read it. HTTPS encrypts it. ARP spoofing is a man-in-the-middle trick on a LAN. The attacker sends fake ARP replies so your traffic passes through their machine first. Study it in the lab, only to understand the
Read card text
What this card says
What it is
HTTP is plain text; anyone sniffing can read it. HTTPS encrypts it.
ARP spoofing is a man-in-the-middle trick on a LAN.
How ARP spoofing works
The attacker sends fake ARP replies so your traffic passes through their machine first.
Study it in the lab, only to understand the defence.
Defence
Use HTTPS everywhere.
On your network, enable Dynamic ARP Inspection and Protected Management Frames.
| Defence | What it does |
|---|---|
| HTTPS everywhere / TLS | Even if traffic is captured, it is encrypted |
| Dynamic ARP Inspection, port security (switch) | Block forged ARP replies |
| Static ARP entries for critical hosts | Cannot be spoofed |
| arpwatch / IDS | Alerts when a MAC-to-IP mapping suddenly changes |
| VPN | Encrypts traffic end to end on untrusted networks |
Learn more in the lesson: 24.5 Why HTTP Leaks and HTTPS Protects; ARP Spoofing