Ravi Sir's Cyber Security Cards › Revision Cards
What a SIEM Does
What a SIEM Does A SIEM collects logs from many systems into one place, so you can search and alert across all of them. EDR (watches processes on each machine). SOAR (automates response steps). IDS/IPS (watch network traffic). Reading logs server by server does not scale. A SIEM links events togethe
Read card text
What this card says
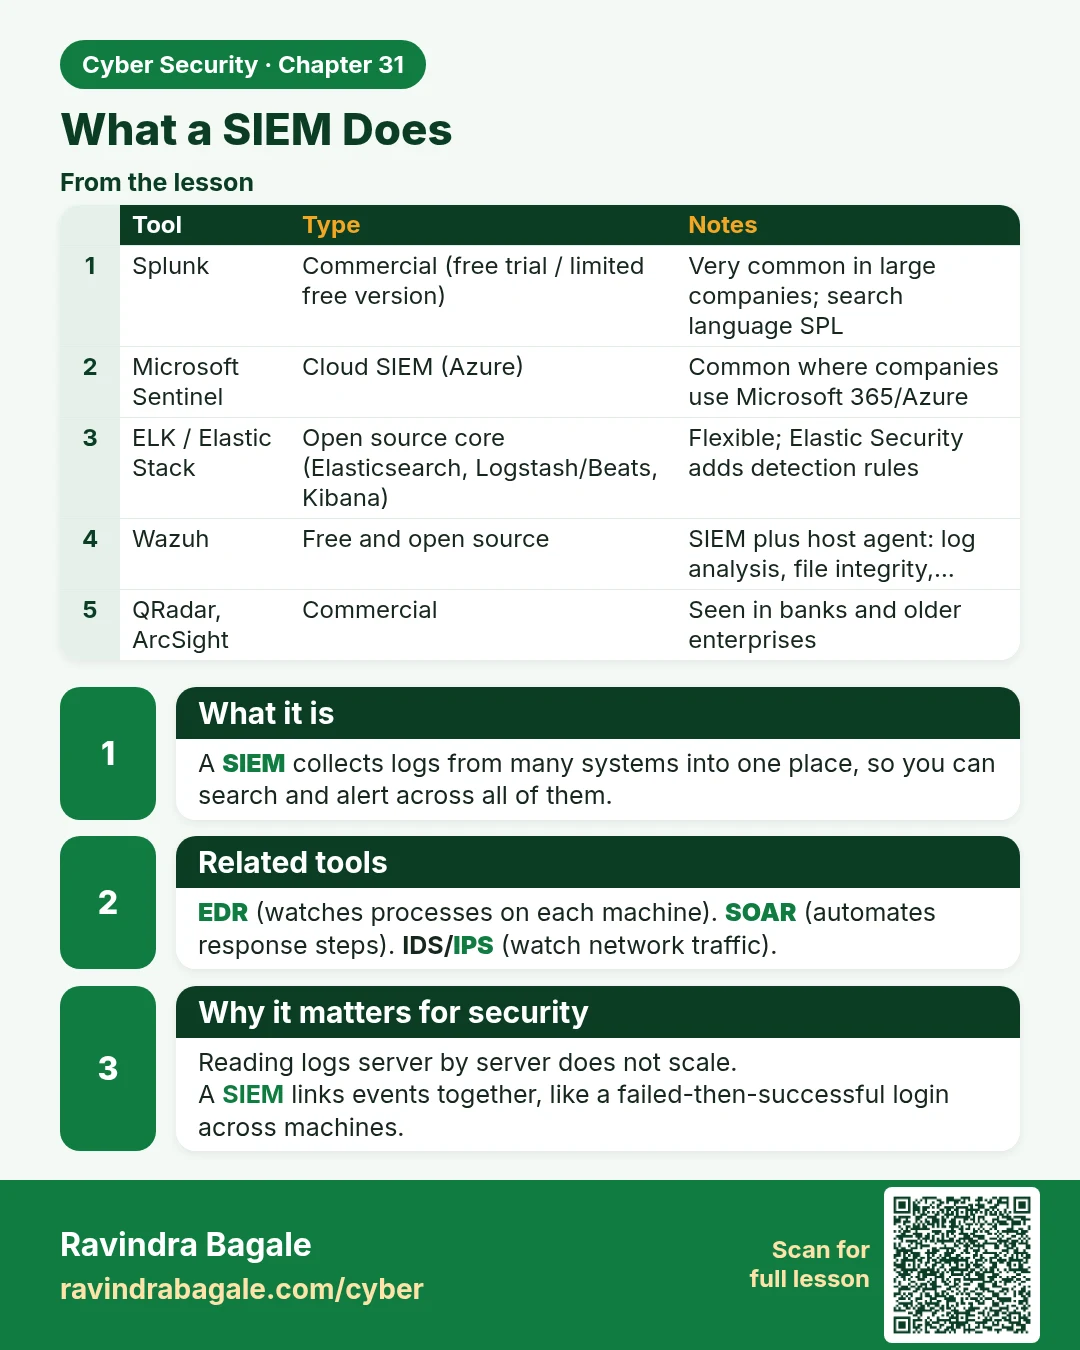
What it is
A SIEM collects logs from many systems into one place, so you can search and alert across all of them.
Related tools
EDR (watches processes on each machine). SOAR (automates response steps). IDS/IPS (watch network traffic).
Why it matters for security
Reading logs server by server does not scale.
A SIEM links events together, like a failed-then-successful login across machines.
| Tool | Type | Notes |
|---|---|---|
| Splunk | Commercial (free trial / limited free version) | Very common in large companies; search language SPL |
| Microsoft Sentinel | Cloud SIEM (Azure) | Common where companies use Microsoft 365/Azure |
| ELK / Elastic Stack | Open source core (Elasticsearch, Logstash/Beats, Kibana) | Flexible; Elastic Security adds detection rules |
| Wazuh | Free and open source | SIEM plus host agent: log analysis, file integrity,… |
| QRadar, ArcSight | Commercial | Seen in banks and older enterprises |
Learn more in the lesson: 31.3 What a SIEM Does