Ravi Sir's Cyber Security Cards › Revision Cards
Web, MySQL, OWASP and Kali terms
Web, MySQL, OWASP and Kali terms Key web and lab terms: SQL injection, prepared statements, Burp, Nmap, Metasploitable. SQL injection : commands sneaked into input. Prepared statements : the fix. Burp : an intercepting proxy. Metasploitable : a practice target VM. Knowing terms is not enough. Before
Read card text
What this card says
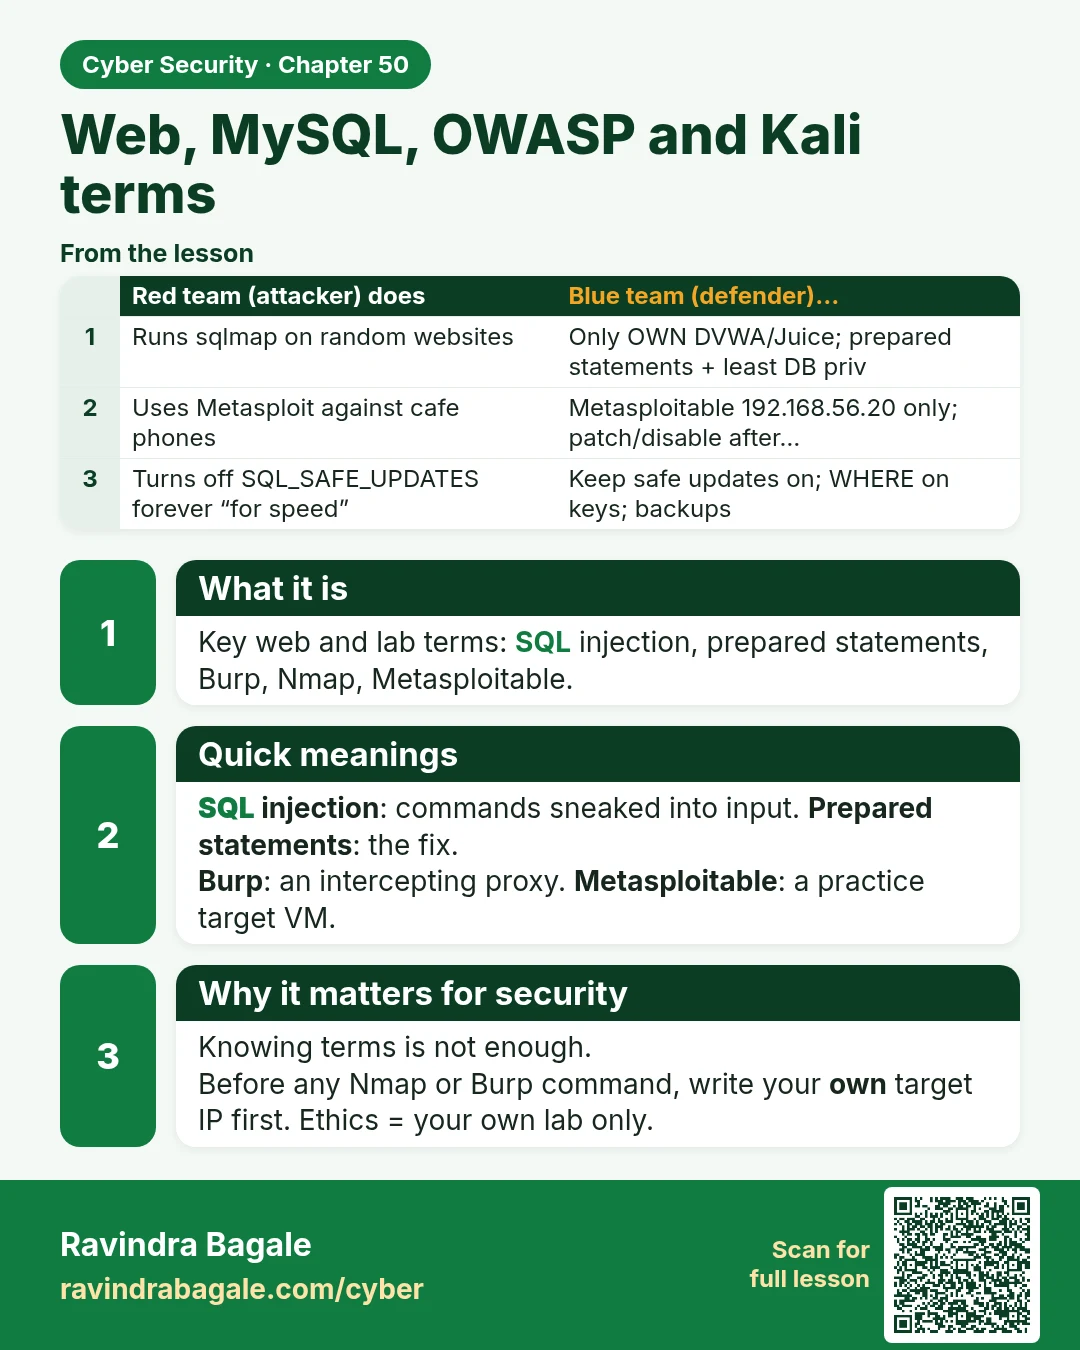
What it is
Key web and lab terms: SQL injection, prepared statements, Burp, Nmap, Metasploitable.
Quick meanings
SQL injection: commands sneaked into input. Prepared statements: the fix.
Burp: an intercepting proxy. Metasploitable: a practice target VM.
Why it matters for security
Knowing terms is not enough.
Before any Nmap or Burp command, write your own target IP first. Ethics = your own lab only.
| Red team (attacker) does | Blue team (defender)… |
|---|---|
| Runs sqlmap on random websites | Only OWN DVWA/Juice; prepared statements + least DB priv |
| Uses Metasploit against cafe phones | Metasploitable 192.168.56.20 only; patch/disable after… |
| Turns off SQL_SAFE_UPDATES forever “for speed” | Keep safe updates on; WHERE on keys; backups |
Learn more in the lesson: 50.4 Web, MySQL, OWASP and Kali terms