Ravi Sir's Cyber Security Cards › Revision Cards
Uploading Videos and Text Posts
Uploading Videos and Text Posts The upload page that saves videos to S3 and text posts to the database. Logged in? CSRF token right? Size under 50 MB? Real file type is MP4? Then save it to S3 with a new random name. Files never touch the web folder. They go to S3, and S3 never runs code. Checking o
Read card text
What this card says
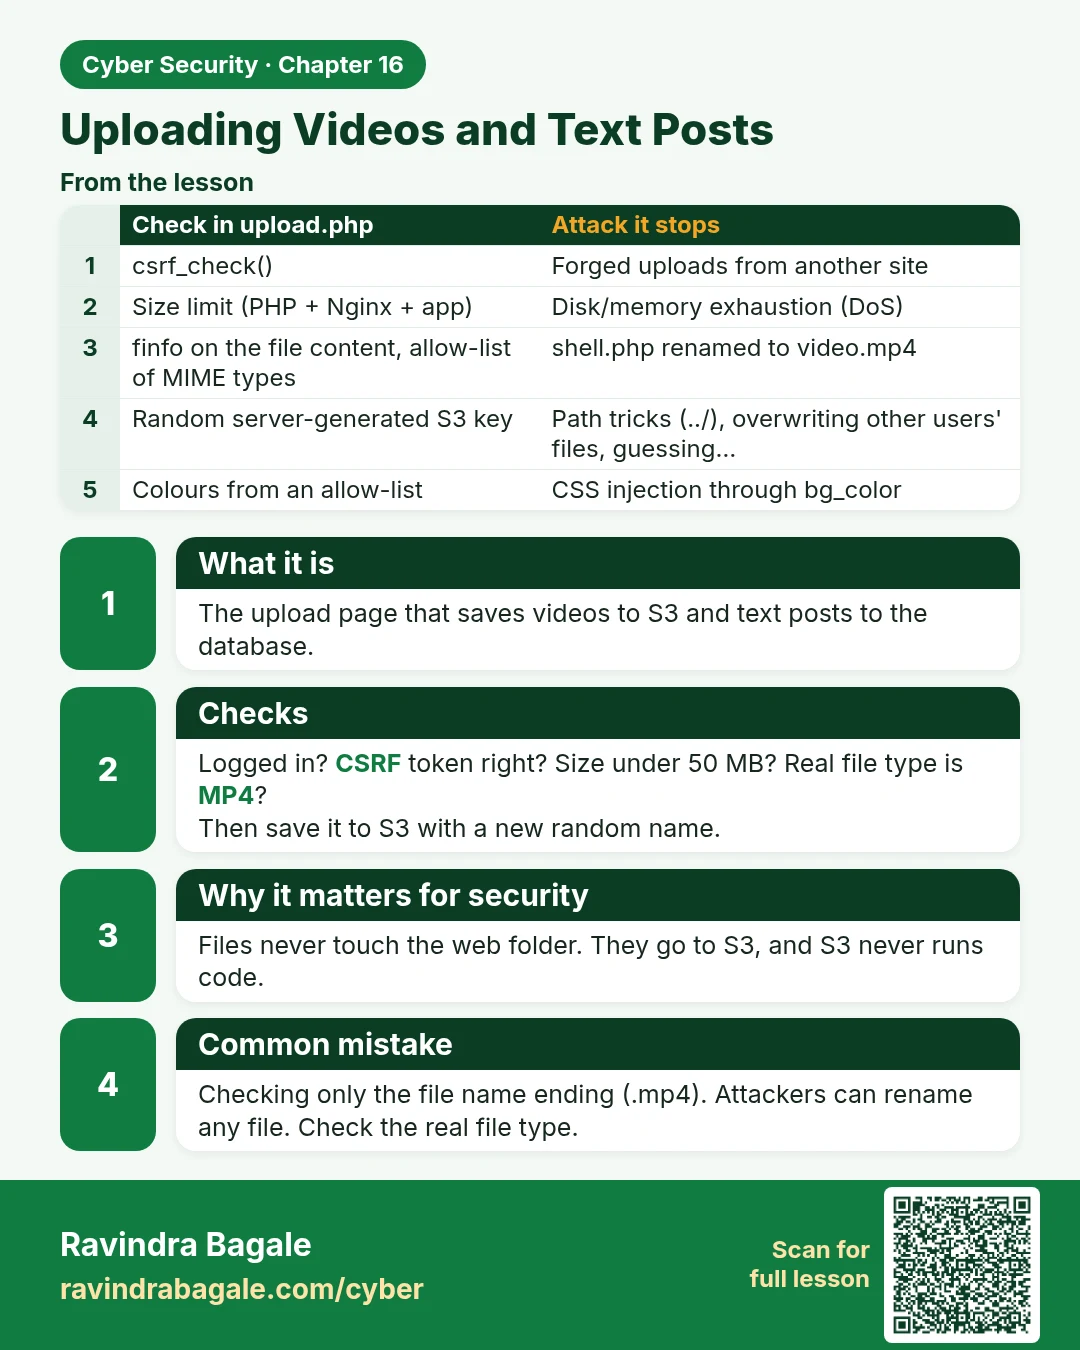
What it is
The upload page that saves videos to S3 and text posts to the database.
Checks
Logged in? CSRF token right? Size under 50 MB? Real file type is MP4?
Then save it to S3 with a new random name.
Why it matters for security
Files never touch the web folder. They go to S3, and S3 never runs code.
Common mistake
Checking only the file name ending (.mp4). Attackers can rename any file. Check the real file type.
| Check in upload.php | Attack it stops |
|---|---|
| csrf_check() | Forged uploads from another site |
| Size limit (PHP + Nginx + app) | Disk/memory exhaustion (DoS) |
| finfo on the file content, allow-list of MIME types | shell.php renamed to video.mp4 |
| Random server-generated S3 key | Path tricks (../), overwriting other users' files, guessing… |
| Colours from an allow-list | CSS injection through bg_color |
Learn more in the lesson: 16.7 Uploading Videos and Text Posts