Ravi Sir's Cyber Security Cards › Revision Cards
theHarvester and Recon-ng (Overview)
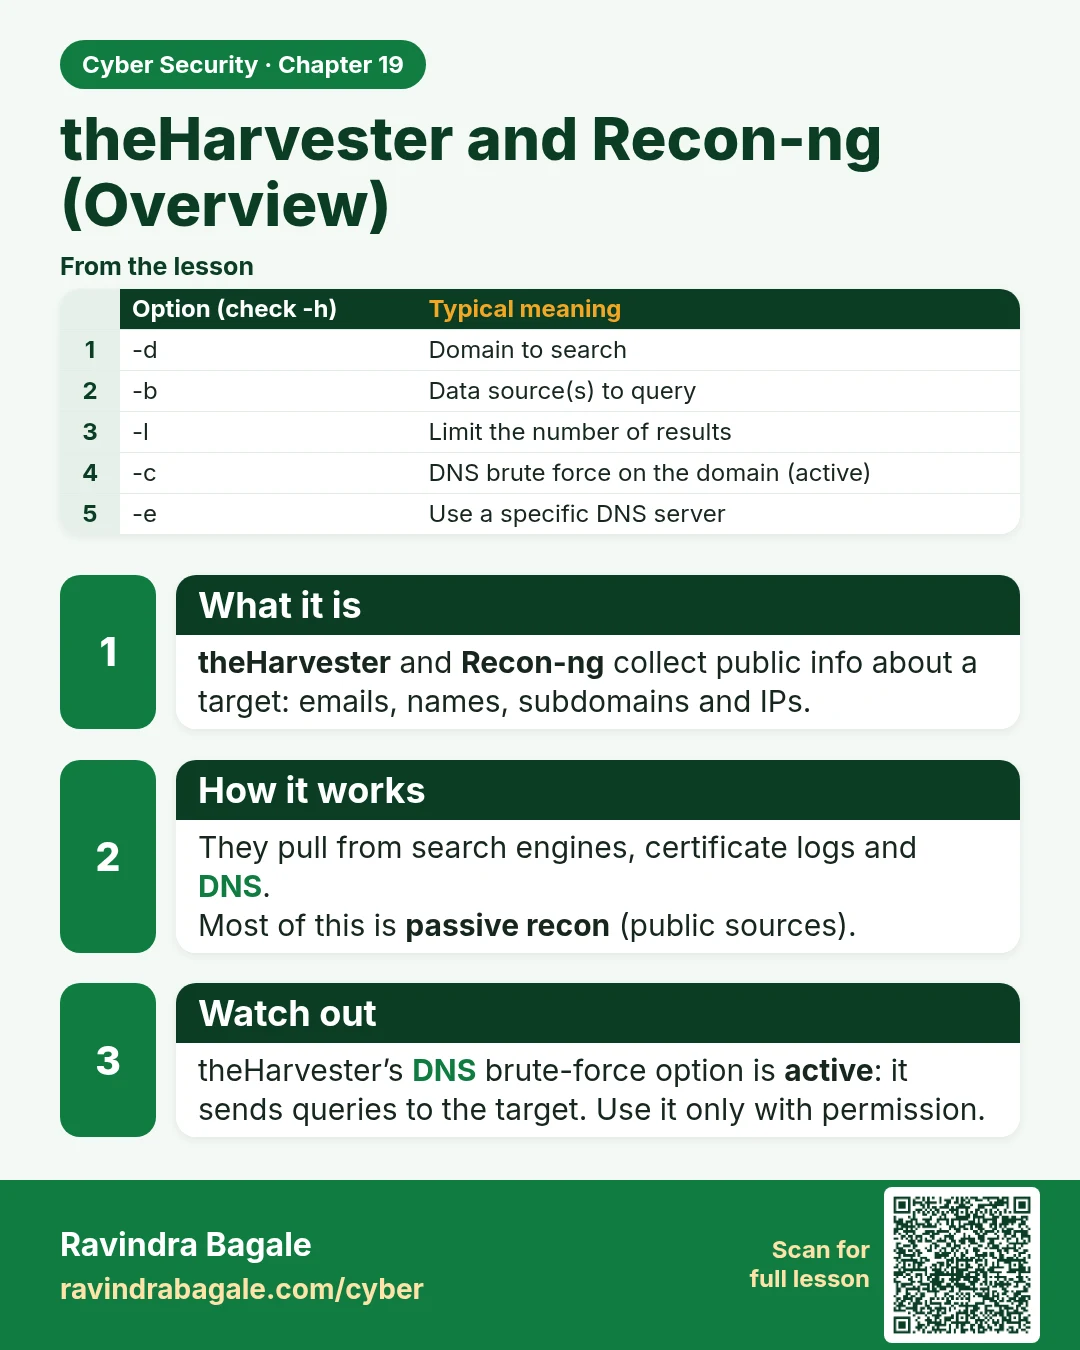
theHarvester and Recon-ng (Overview) theHarvester and Recon-ng collect public info about a target: emails, names, subdomains and IPs. They pull from search engines, certificate logs and DNS. Most of this is passive recon (public sources). theHarvester’s DNS brute-force option is active : it sends qu
Read card text
What this card says
What it is
theHarvester and Recon-ng collect public info about a target: emails, names, subdomains and IPs.
How it works
They pull from search engines, certificate logs and DNS.
Most of this is passive recon (public sources).
Watch out
theHarvester’s DNS brute-force option is active: it sends queries to the target. Use it only with permission.
| Option (check -h) | Typical meaning |
|---|---|
| -d | Domain to search |
| -b | Data source(s) to query |
| -l | Limit the number of results |
| -c | DNS brute force on the domain (active) |
| -e | Use a specific DNS server |
Learn more in the lesson: 19.3 theHarvester and Recon-ng (Overview)