Ravi Sir's Cyber Security Cards › Revision Cards
The Rest: Design, Components, Integrity, Logging, SSRF
The Rest: Design, Components, Integrity, Logging, SSRF The remaining OWASP Top 10 risks: insecure design, old components, data integrity, poor logging and SSRF . SSRF (Server-Side Request Forgery): a server is tricked into fetching a URL. Fetching http://169.254.169.254/ (AWS metadata) can leak cred
Read card text
What this card says
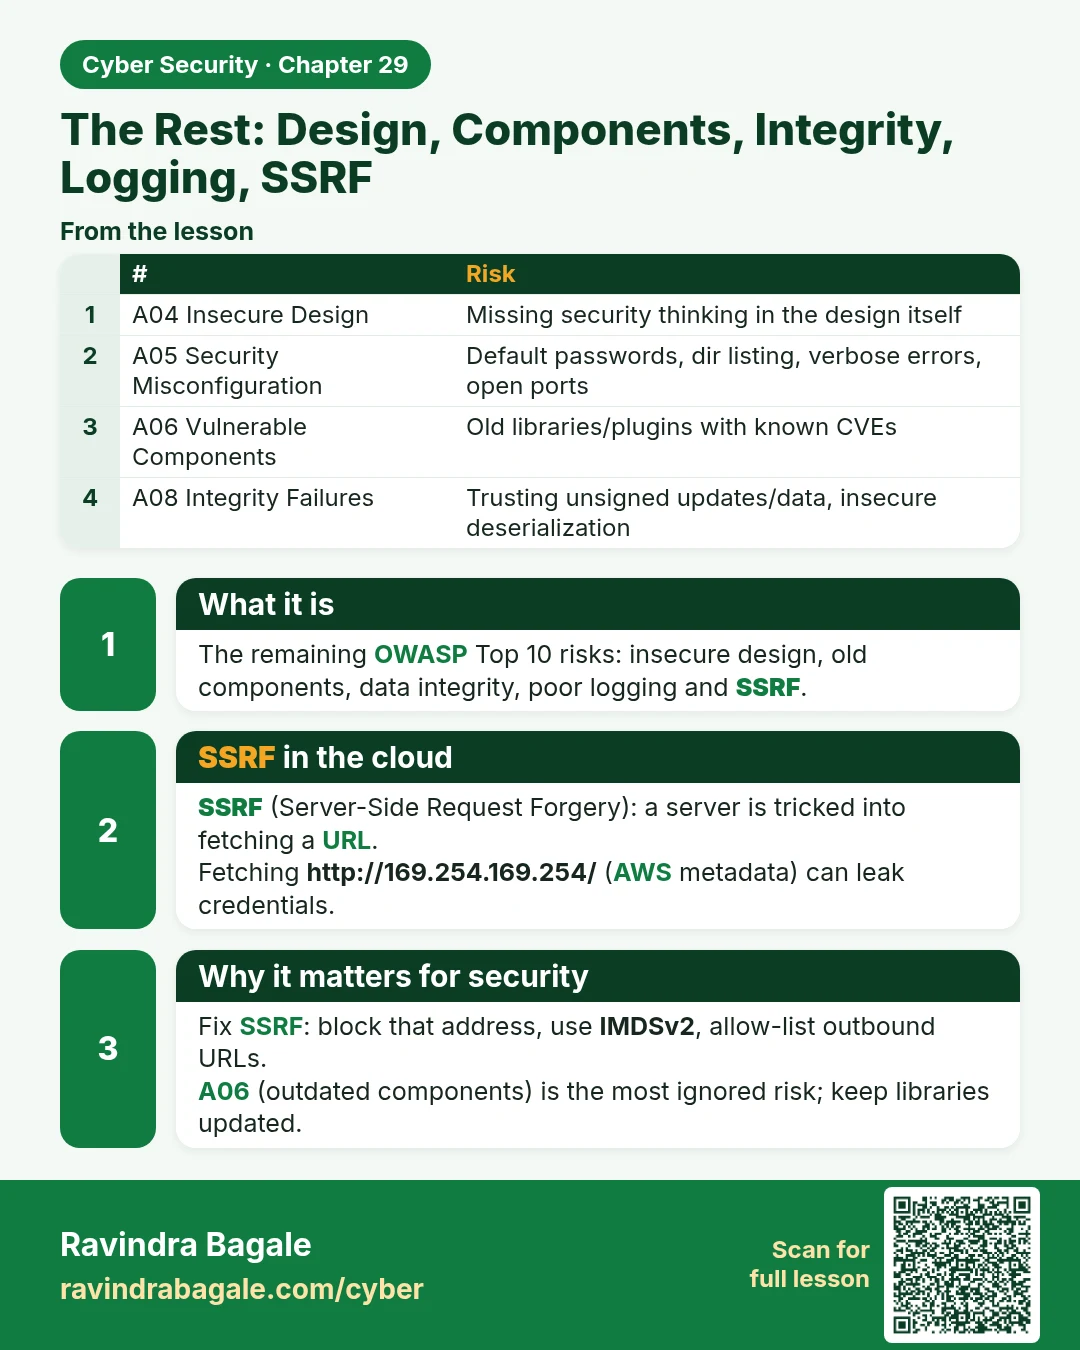
What it is
The remaining OWASP Top 10 risks: insecure design, old components, data integrity, poor logging and SSRF.
SSRF in the cloud
SSRF (Server-Side Request Forgery): a server is tricked into fetching a URL.
Fetching http://169.254.169.254/ (AWS metadata) can leak credentials.
Why it matters for security
Fix SSRF: block that address, use IMDSv2, allow-list outbound URLs.
A06 (outdated components) is the most ignored risk; keep libraries updated.
| # | Risk |
|---|---|
| A04 Insecure Design | Missing security thinking in the design itself |
| A05 Security Misconfiguration | Default passwords, dir listing, verbose errors, open ports |
| A06 Vulnerable Components | Old libraries/plugins with known CVEs |
| A08 Integrity Failures | Trusting unsigned updates/data, insecure deserialization |
| A09 Logging/Monitoring Failures | Attacks unnoticed because nothing is logged |
Learn more in the lesson: 29.7 The Rest: Design, Components, Integrity, Logging, SSRF