Ravi Sir's Cyber Security Cards › Revision Cards
The Pre-Engagement Checklist
The Pre-Engagement Checklist A checklist you run before any test, so you never hack the wrong target. Written permission? Scope (allowed targets) clear? Dates and times agreed? Contact person known? Backups of the target done? Testing from your own machine? In a job, “my own VM” becomes “the signed
Read card text
What this card says
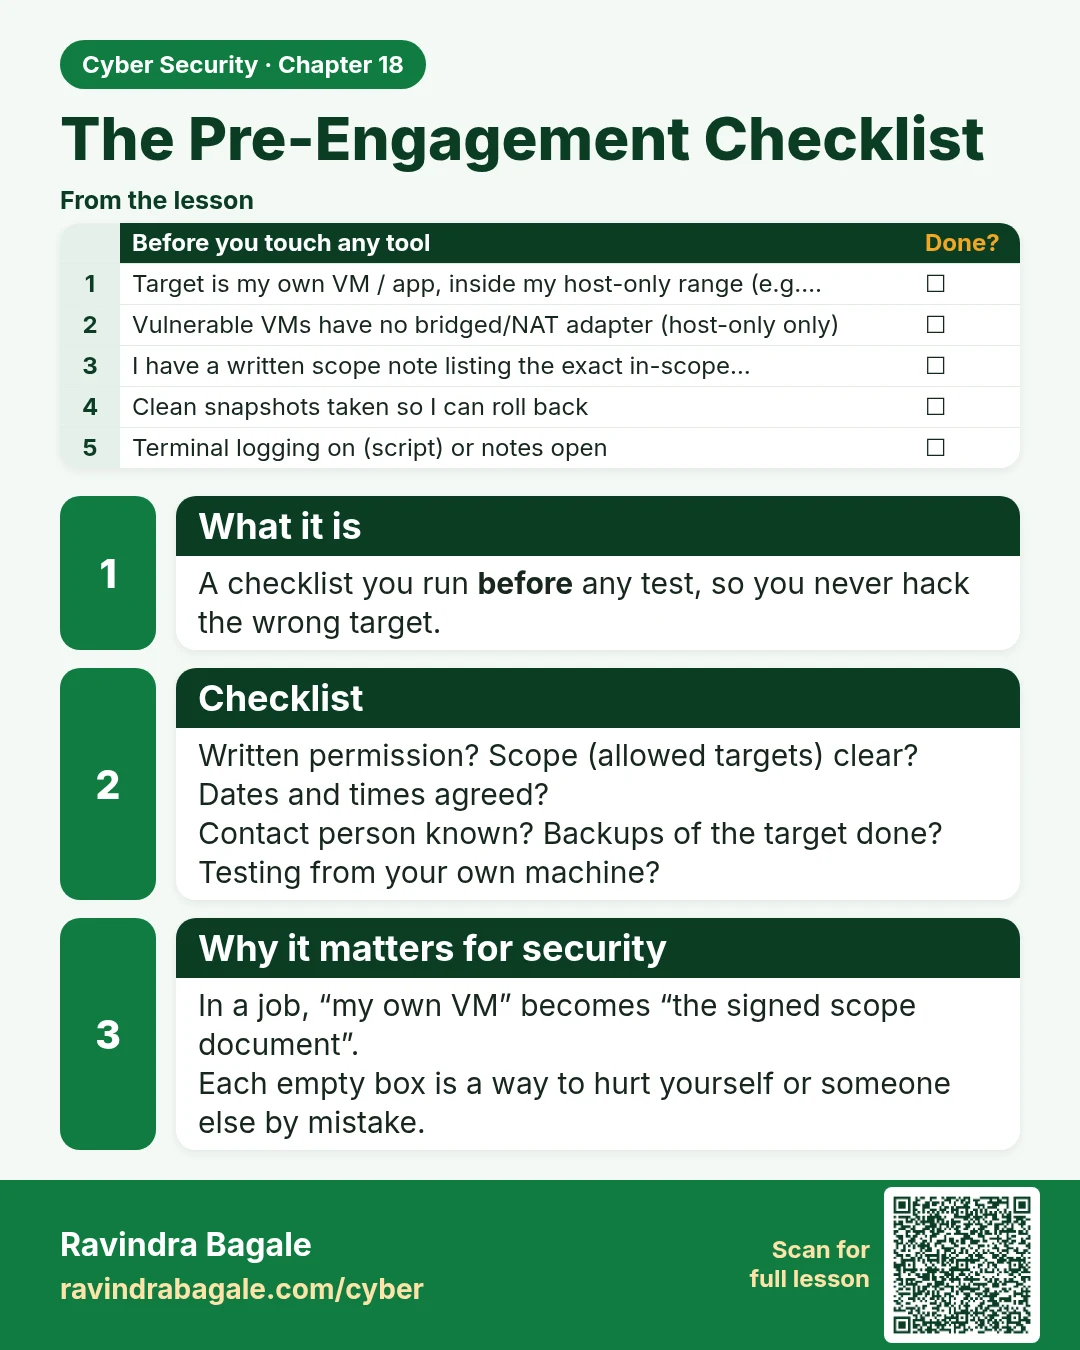
What it is
A checklist you run before any test, so you never hack the wrong target.
Checklist
Written permission? Scope (allowed targets) clear? Dates and times agreed?
Contact person known? Backups of the target done? Testing from your own machine?
Why it matters for security
In a job, “my own VM” becomes “the signed scope document”.
Each empty box is a way to hurt yourself or someone else by mistake.
| Before you touch any tool | Done? |
|---|---|
| Target is my own VM / app, inside my host-only range (e.g.… | ☐ |
| Vulnerable VMs have no bridged/NAT adapter (host-only only) | ☐ |
| I have a written scope note listing the exact in-scope… | ☐ |
| Clean snapshots taken so I can roll back | ☐ |
| Terminal logging on (script) or notes open | ☐ |
Learn more in the lesson: 18.6 The Pre-Engagement Checklist