Ravi Sir's Cyber Security Cards › Revision Cards
The One Rule: Permission and Scope
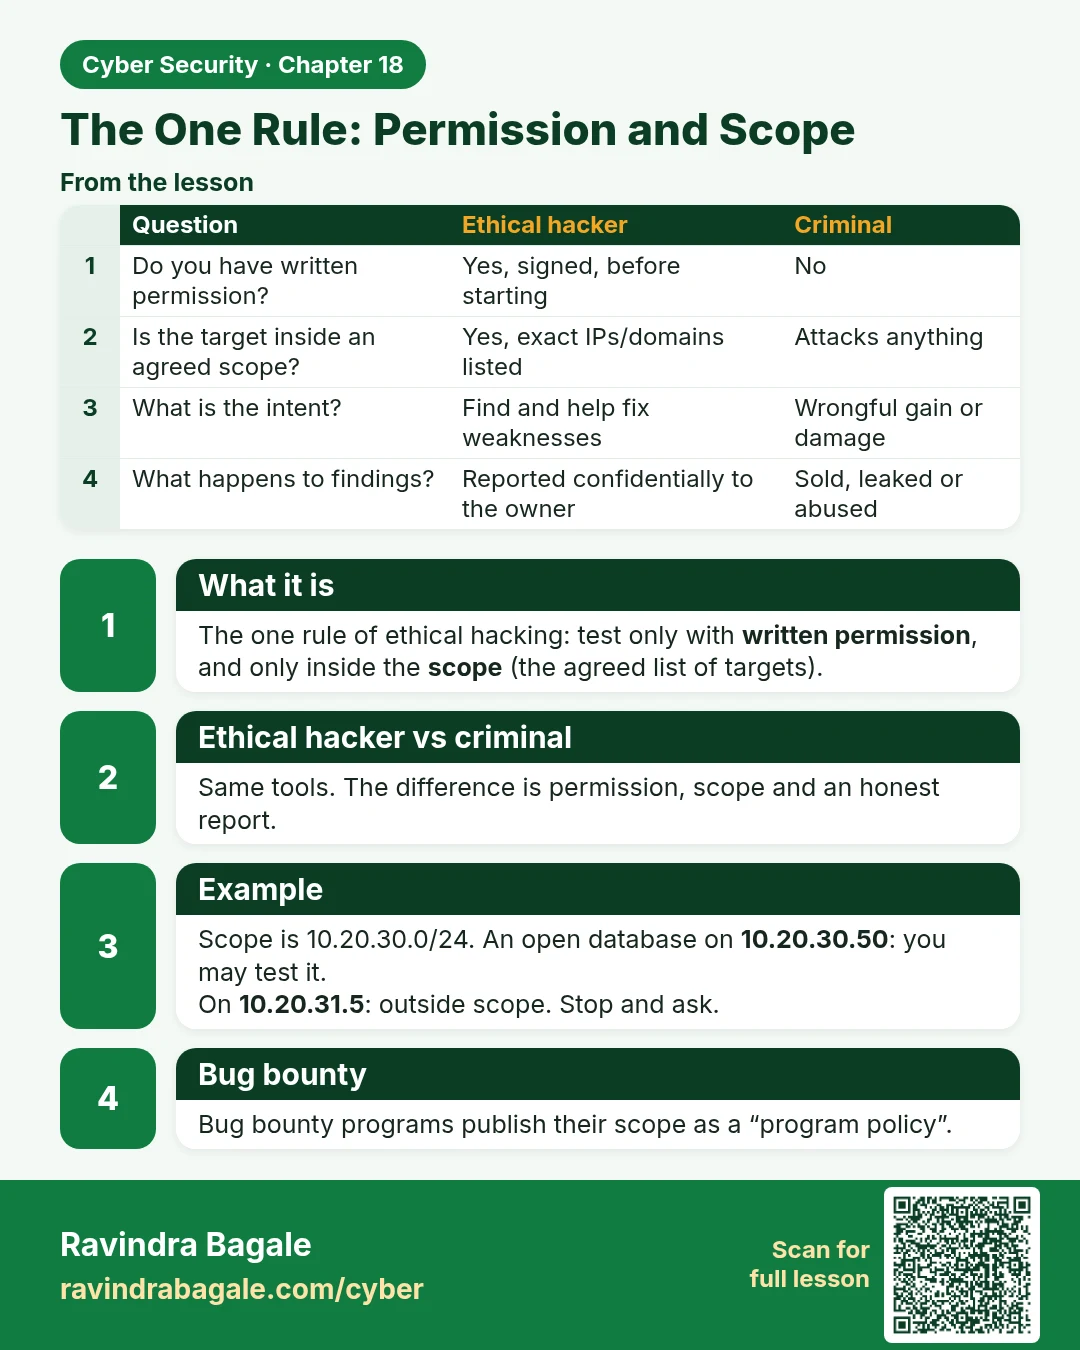
The One Rule: Permission and Scope The one rule of ethical hacking: test only with written permission , and only inside the scope (the agreed list of targets). Same tools. The difference is permission, scope and an honest report. Scope is 10.20.30.0/24. An open database on 10.20.30.50 : you may test
Read card text
What this card says
What it is
The one rule of ethical hacking: test only with written permission, and only inside the scope (the agreed list of targets).
Ethical hacker vs criminal
Same tools. The difference is permission, scope and an honest report.
Example
Scope is 10.20.30.0/24. An open database on 10.20.30.50: you may test it.
On 10.20.31.5: outside scope. Stop and ask.
Bug bounty
Bug bounty programs publish their scope as a “program policy”.
| Question | Ethical hacker | Criminal |
|---|---|---|
| Do you have written permission? | Yes, signed, before starting | No |
| Is the target inside an agreed scope? | Yes, exact IPs/domains listed | Attacks anything |
| What is the intent? | Find and help fix weaknesses | Wrongful gain or damage |
| What happens to findings? | Reported confidentially to the owner | Sold, leaked or abused |
| Are actions logged and reversible? | Yes, careful not to damage data | Often destructive |
Learn more in the lesson: 18.1 The One Rule: Permission and Scope