Ravi Sir's Cyber Security Cards › Revision Cards
sqlmap: Testing for SQL Injection
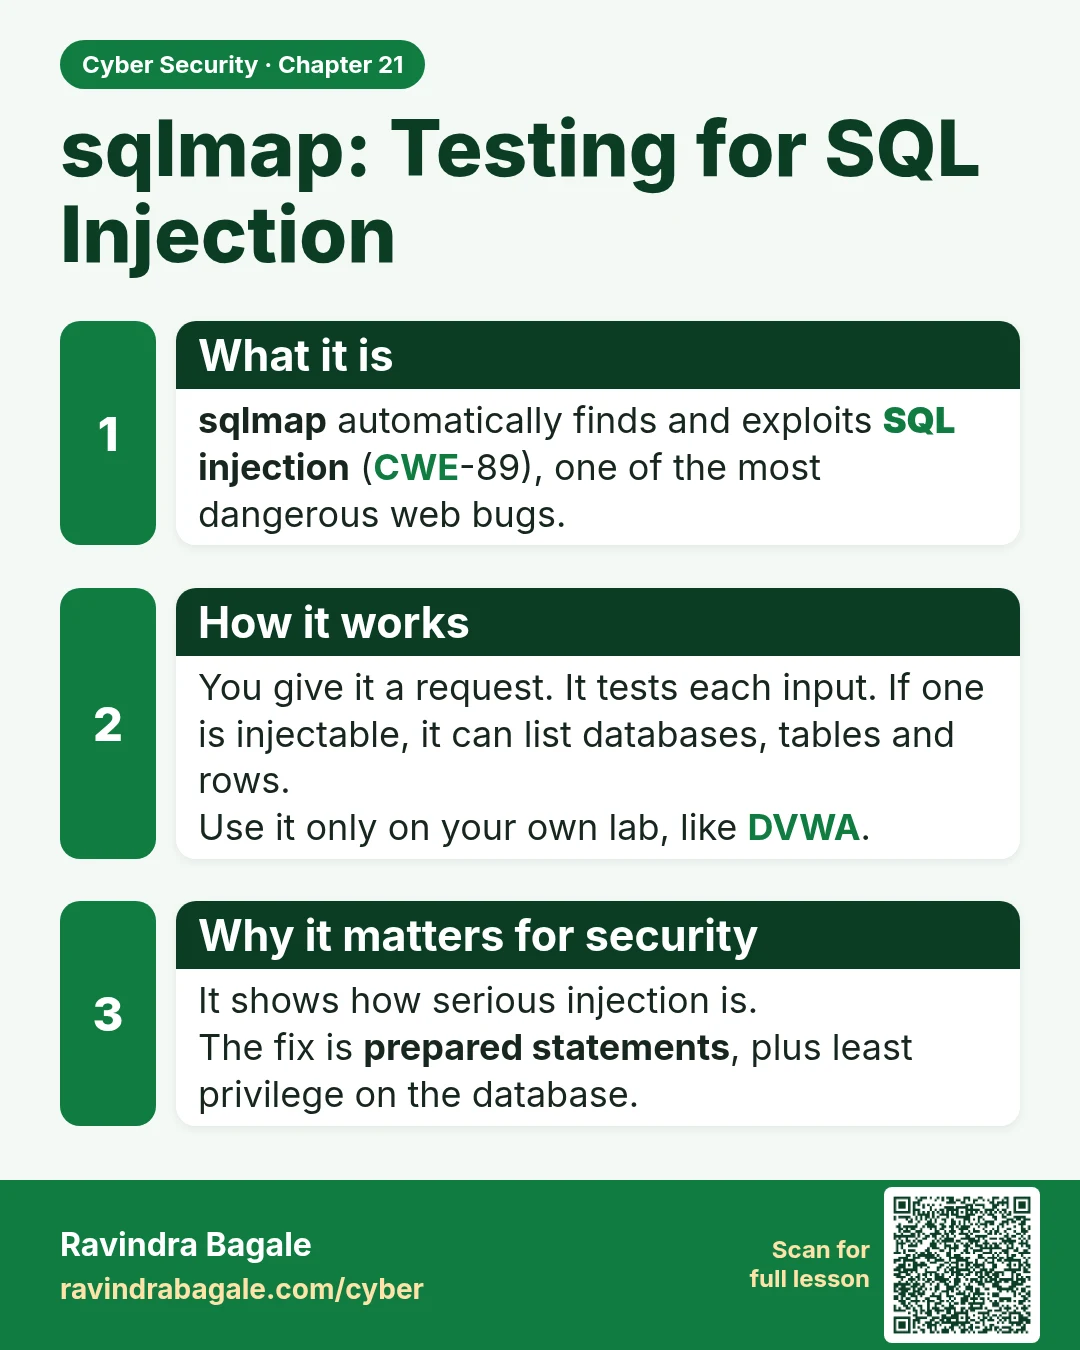
sqlmap: Testing for SQL Injection sqlmap automatically finds and exploits SQL injection (CWE-89), one of the most dangerous web bugs. You give it a request. It tests each input. If one is injectable, it can list databases, tables and rows. Use it only on your own lab, like DVWA. It shows how serious
Read card text
What this card says
What it is
sqlmap automatically finds and exploits SQL injection (CWE-89), one of the most dangerous web bugs.
How it works
You give it a request. It tests each input. If one is injectable, it can list databases, tables and rows.
Use it only on your own lab, like DVWA.
Why it matters for security
It shows how serious injection is.
The fix is prepared statements, plus least privilege on the database.
Learn more in the lesson: 21.6 sqlmap: Testing for SQL Injection