Ravi Sir's Cyber Security Cards › Revision Cards
Session Fixation and Predictable IDs
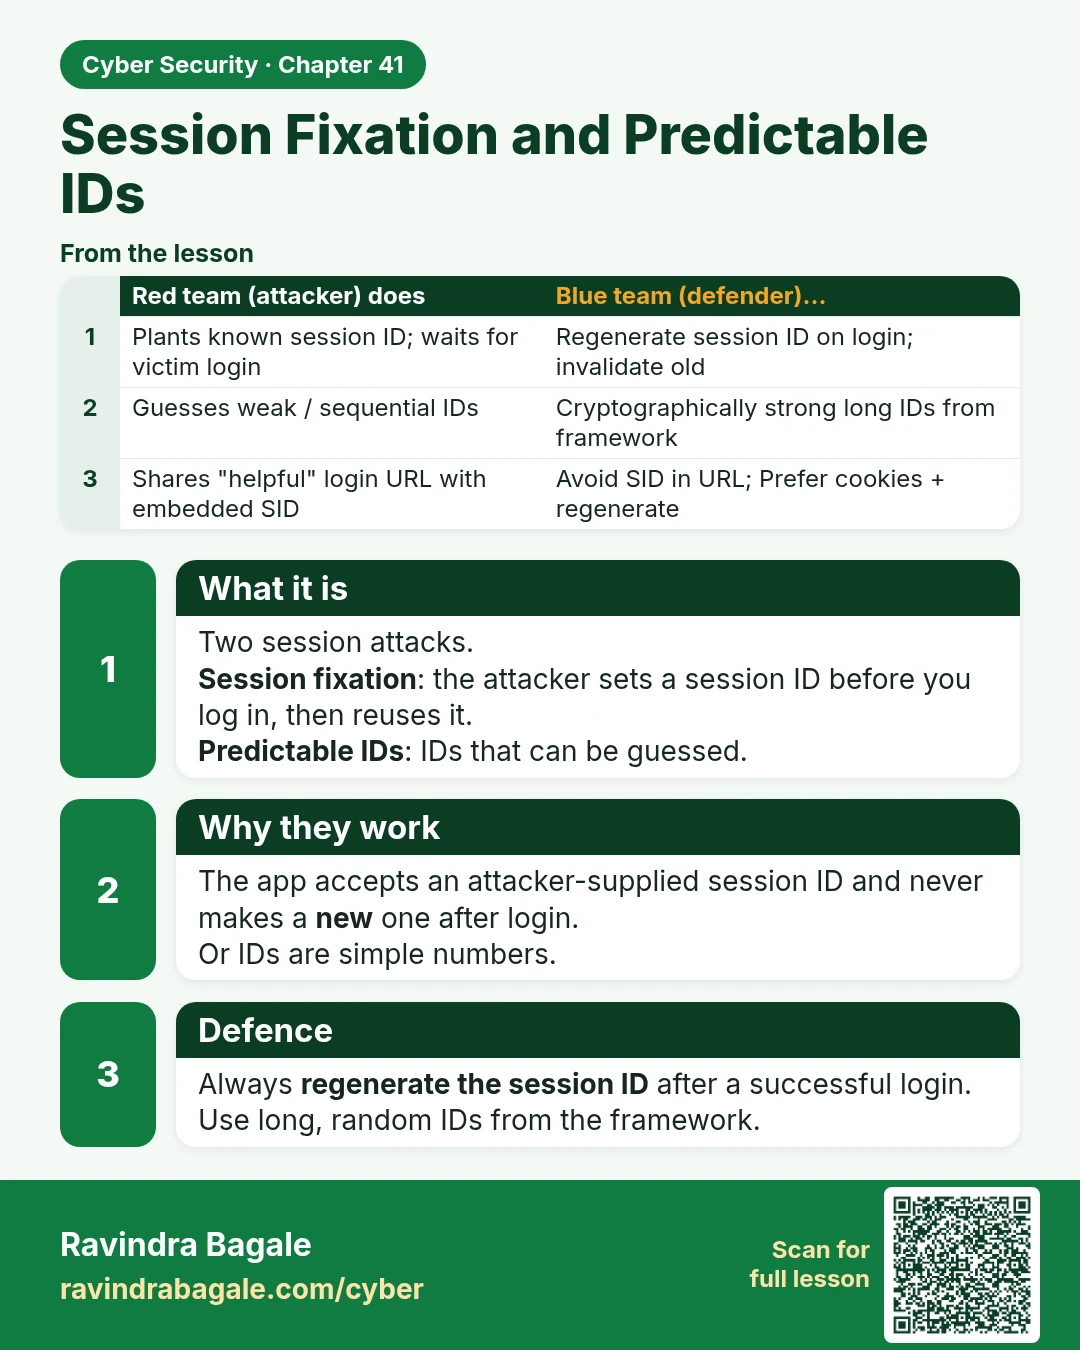
Session Fixation and Predictable IDs Two session attacks. Session fixation : the attacker sets a session ID before you log in, then reuses it. Predictable IDs : IDs that can be guessed. The app accepts an attacker-supplied session ID and never makes a new one after login. Or IDs are simple numbers.
Read card text
What this card says
What it is
Two session attacks.
Session fixation: the attacker sets a session ID before you log in, then reuses it.
Predictable IDs: IDs that can be guessed.
Why they work
The app accepts an attacker-supplied session ID and never makes a new one after login.
Or IDs are simple numbers.
Defence
Always regenerate the session ID after a successful login.
Use long, random IDs from the framework.
| Red team (attacker) does | Blue team (defender)… |
|---|---|
| Plants known session ID; waits for victim login | Regenerate session ID on login; invalidate old |
| Guesses weak / sequential IDs | Cryptographically strong long IDs from framework |
| Shares "helpful" login URL with embedded SID | Avoid SID in URL; Prefer cookies + regenerate |
Learn more in the lesson: 41.3 Session Fixation and Predictable IDs