Ravi Sir's Cyber Security Cards › Revision Cards
Secure PHP Settings
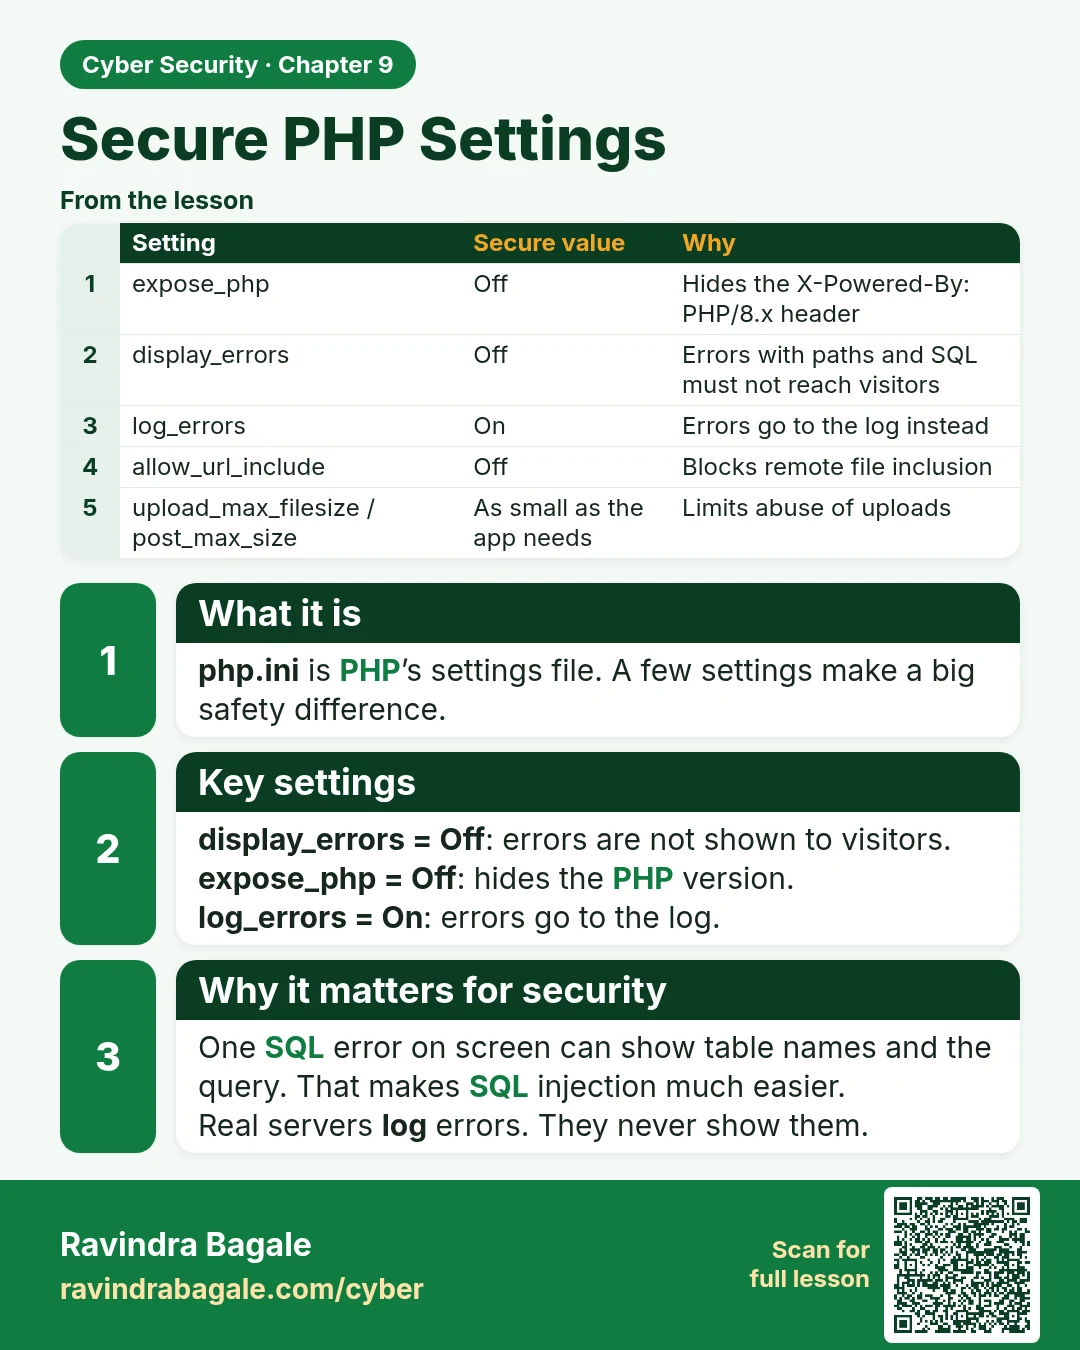
Secure PHP Settings php.ini is PHP’s settings file. A few settings make a big safety difference. display_errors = Off : errors are not shown to visitors. expose_php = Off : hides the PHP version. log_errors = On : errors go to the log. One SQL error on screen can show table names and the query. That
Read card text
What this card says
What it is
php.ini is PHP’s settings file. A few settings make a big safety difference.
Key settings
display_errors = Off: errors are not shown to visitors.
expose_php = Off: hides the PHP version.
log_errors = On: errors go to the log.
Why it matters for security
One SQL error on screen can show table names and the query. That makes SQL injection much easier.
Real servers log errors. They never show them.
| Setting | Secure value | Why |
|---|---|---|
| expose_php | Off | Hides the X-Powered-By: PHP/8.x header |
| display_errors | Off | Errors with paths and SQL must not reach visitors |
| log_errors | On | Errors go to the log instead |
| allow_url_include | Off | Blocks remote file inclusion |
| upload_max_filesize / post_max_size | As small as the app needs | Limits abuse of uploads |
Learn more in the lesson: 9.8 Secure PHP Settings