Ravi Sir's Cyber Security Cards › Revision Cards
Putting It Together – Purple Team Mindset
Putting It Together – Purple Team Mindset The purple team mindset for Active Directory: attack like Red, then fix like Blue. Enumerate like an attacker → fix the weakness like a defender → enumerate again until the attack fails. Say it clearly in interviews: “I test AD only in my own isolated lab. F
Read card text
What this card says
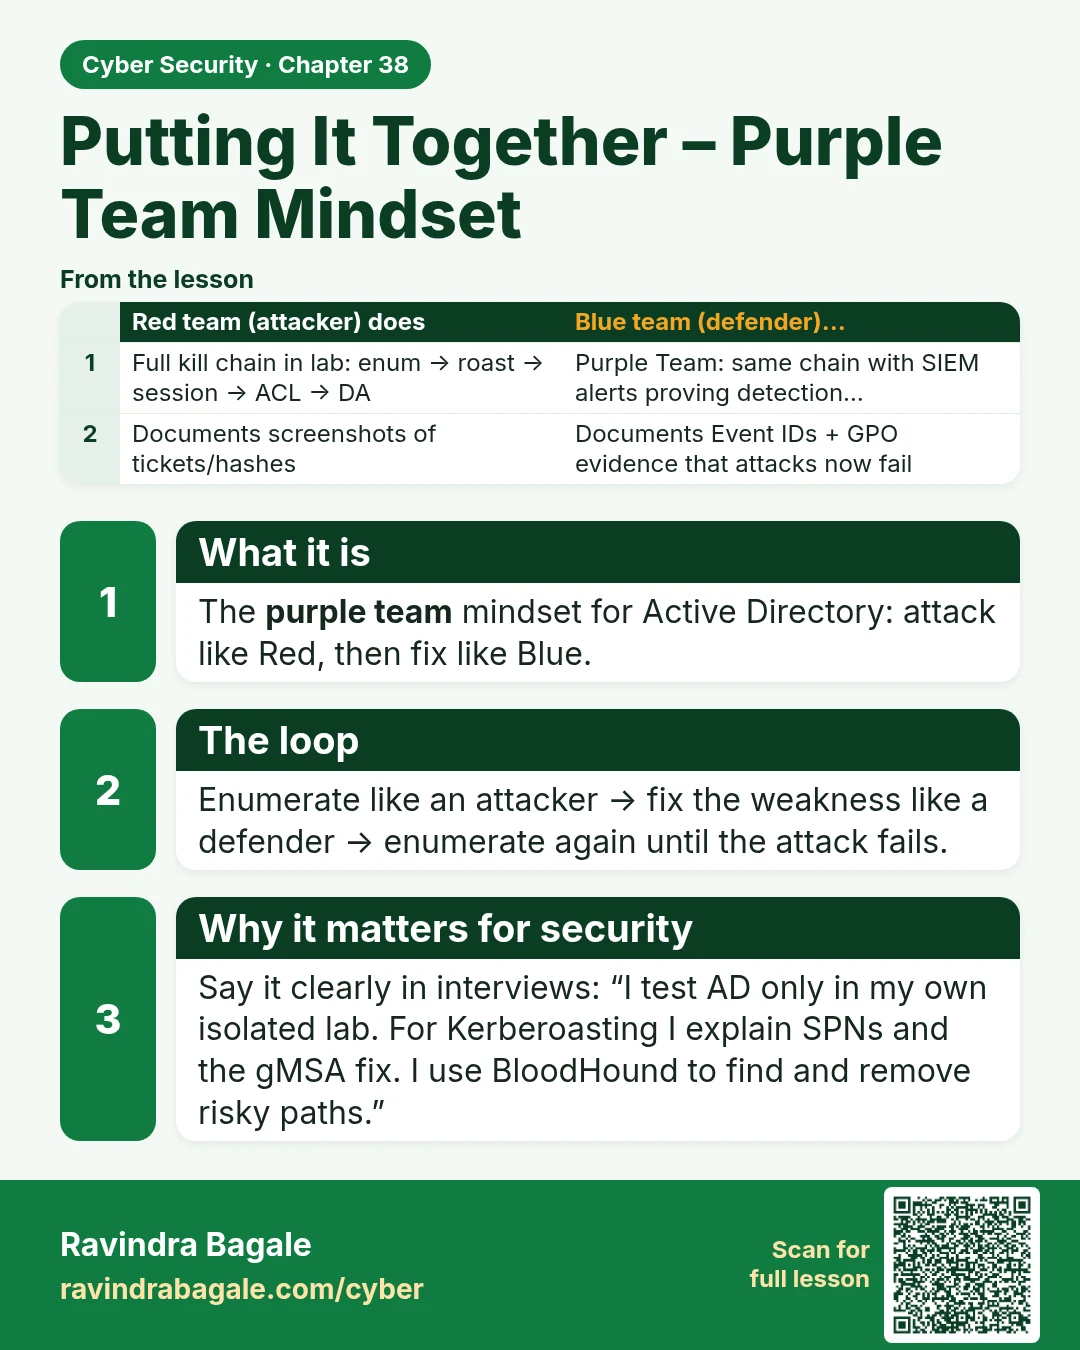
What it is
The purple team mindset for Active Directory: attack like Red, then fix like Blue.
The loop
Enumerate like an attacker → fix the weakness like a defender → enumerate again until the attack fails.
Why it matters for security
Say it clearly in interviews: “I test AD only in my own isolated lab. For Kerberoasting I explain SPNs and the gMSA fix. I use BloodHound to find and remove risky paths.”
| Red team (attacker) does | Blue team (defender)… |
|---|---|
| Full kill chain in lab: enum → roast → session → ACL → DA | Purple Team: same chain with SIEM alerts proving detection… |
| Documents screenshots of tickets/hashes | Documents Event IDs + GPO evidence that attacks now fail |
Learn more in the lesson: 38.9 Putting It Together – Purple Team Mindset