Ravi Sir's Cyber Security Cards › Revision Cards
Putting It Together + Defence Checklist
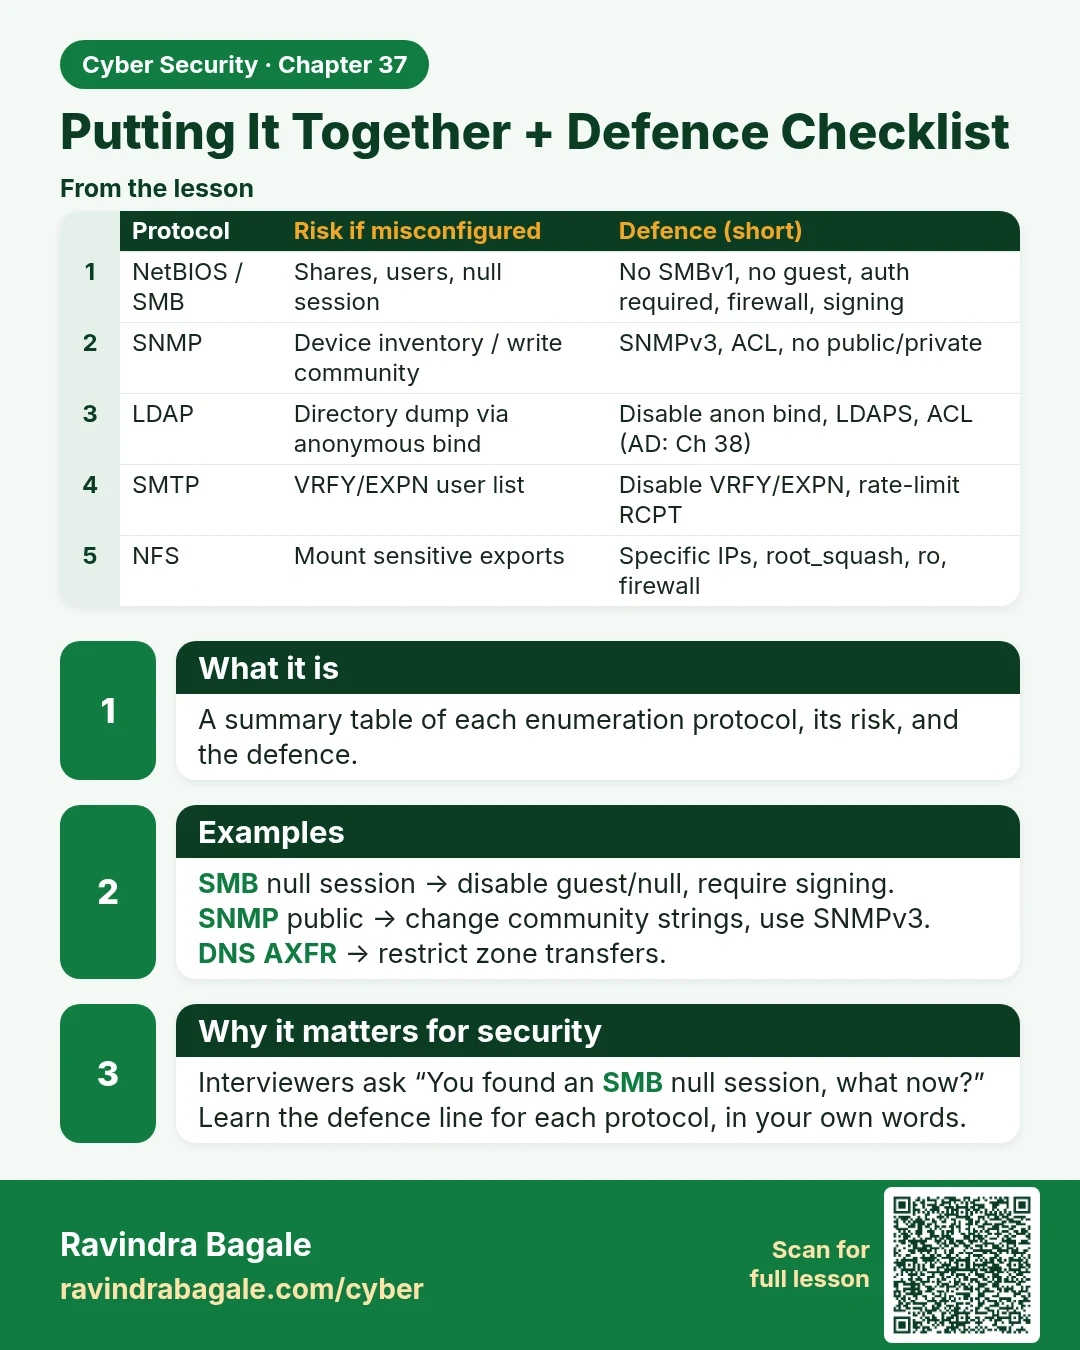
Putting It Together + Defence Checklist A summary table of each enumeration protocol, its risk, and the defence. SMB null session → disable guest/null, require signing. SNMP public → change community strings, use SNMPv3. DNS AXFR → restrict zone transfers. Interviewers ask “You found an SMB null ses
Read card text
What this card says
What it is
A summary table of each enumeration protocol, its risk, and the defence.
Examples
SMB null session → disable guest/null, require signing.
SNMP public → change community strings, use SNMPv3.
DNS AXFR → restrict zone transfers.
Why it matters for security
Interviewers ask “You found an SMB null session, what now?”
Learn the defence line for each protocol, in your own words.
| Protocol | Risk if misconfigured | Defence (short) |
|---|---|---|
| NetBIOS / SMB | Shares, users, null session | No SMBv1, no guest, auth required, firewall, signing |
| SNMP | Device inventory / write community | SNMPv3, ACL, no public/private |
| LDAP | Directory dump via anonymous bind | Disable anon bind, LDAPS, ACL (AD: Ch 38) |
| SMTP | VRFY/EXPN user list | Disable VRFY/EXPN, rate-limit RCPT |
| NFS | Mount sensitive exports | Specific IPs, root_squash, ro, firewall |
Learn more in the lesson: 37.8 Putting It Together + Defence Checklist