Ravi Sir's Cyber Security Cards › Revision Cards
Protocol Attacks – SYN Flood and Handshake Abuse
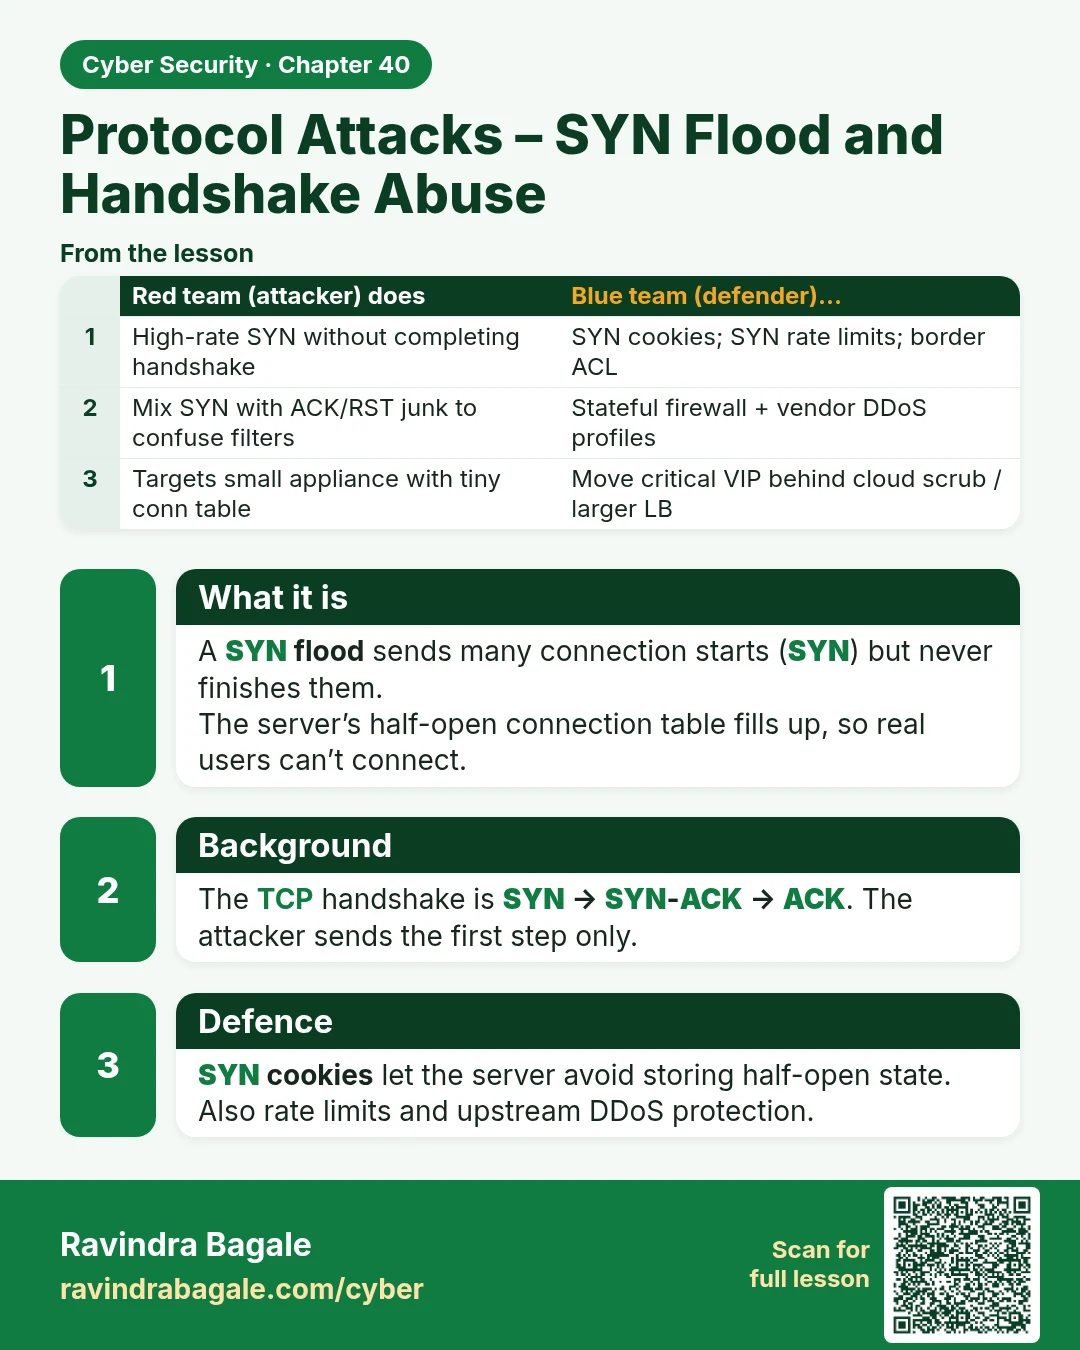
Protocol Attacks – SYN Flood and Handshake Abuse A SYN flood sends many connection starts ( SYN ) but never finishes them. The server’s half-open connection table fills up, so real users can’t connect. The TCP handshake is SYN → SYN-ACK → ACK . The attacker sends the first step only. SYN cookies let
Read card text
What this card says
What it is
A SYN flood sends many connection starts (SYN) but never finishes them.
The server’s half-open connection table fills up, so real users can’t connect.
Background
The TCP handshake is SYN → SYN-ACK → ACK. The attacker sends the first step only.
Defence
SYN cookies let the server avoid storing half-open state.
Also rate limits and upstream DDoS protection.
| Red team (attacker) does | Blue team (defender)… |
|---|---|
| High-rate SYN without completing handshake | SYN cookies; SYN rate limits; border ACL |
| Mix SYN with ACK/RST junk to confuse filters | Stateful firewall + vendor DDoS profiles |
| Targets small appliance with tiny conn table | Move critical VIP behind cloud scrub / larger LB |
Learn more in the lesson: 40.3 Protocol Attacks – SYN Flood and Handshake Abuse