Ravi Sir's Cyber Security Cards › Revision Cards
Persistence: the attacker's hidden way back
Revision card: Persistence: the attacker's hidden way back. Easy English, with a real example. Scan the QR for the full lesson.
Read card text
What this card says
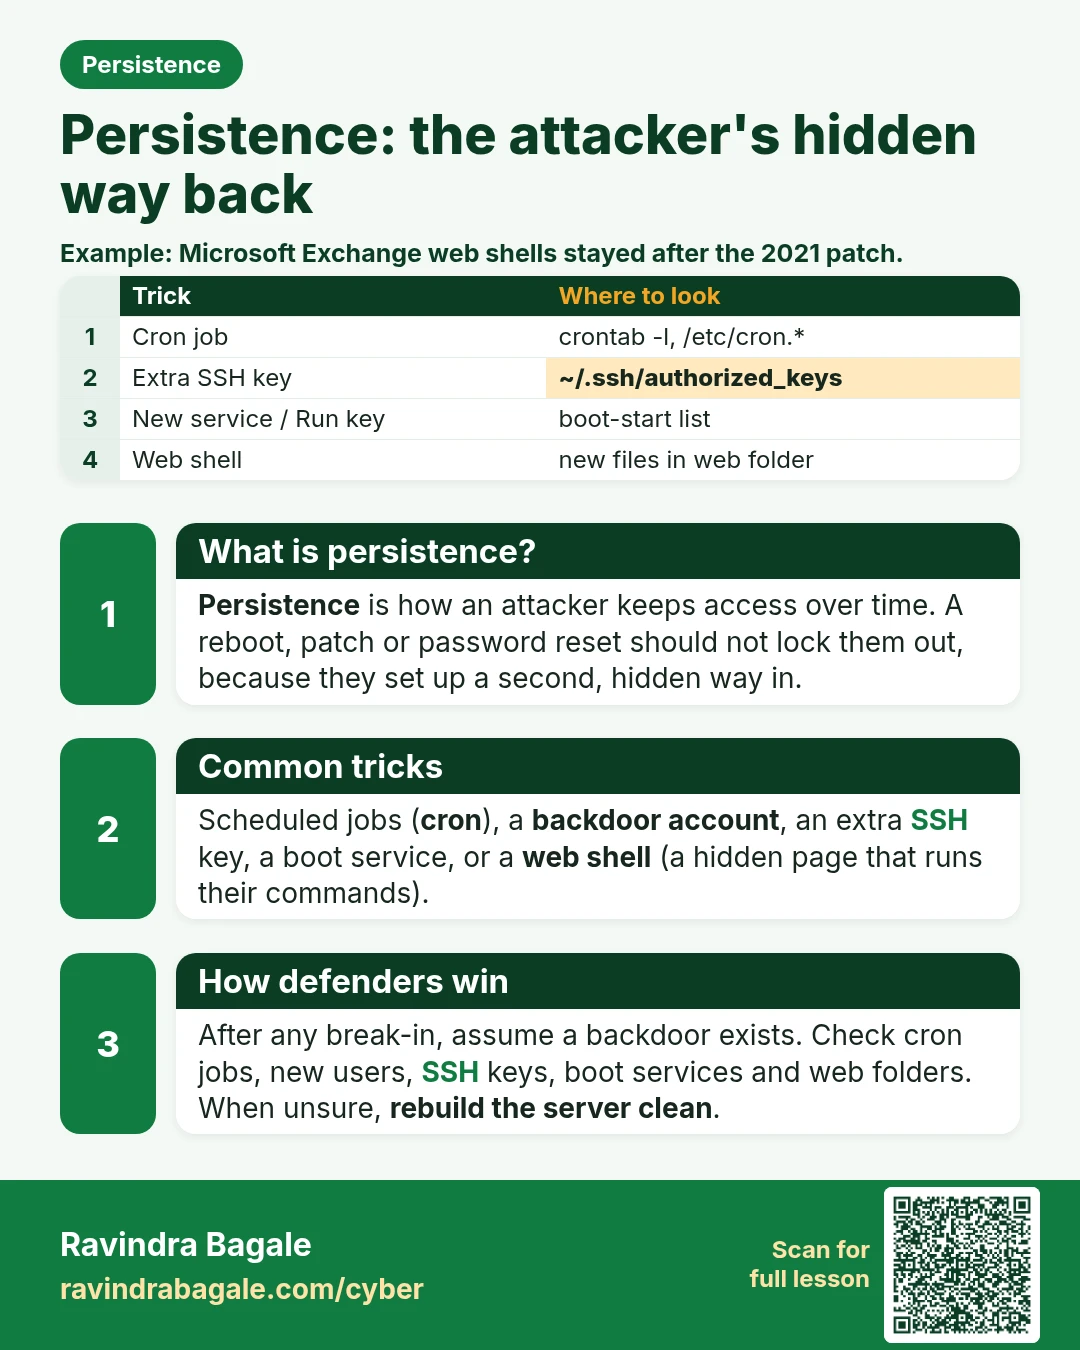
What is persistence?
Persistence is how an attacker keeps access over time. A reboot, patch or password reset should not lock them out, because they set up a second, hidden way in.
Common tricks
Scheduled jobs (cron), a backdoor account, an extra SSH key, a boot service, or a web shell (a hidden page that runs their commands).
How defenders win
After any break-in, assume a backdoor exists. Check cron jobs, new users, SSH keys, boot services and web folders. When unsure, rebuild the server clean.
| Trick | Where to look |
|---|---|
| Cron job | crontab -l, /etc/cron.* |
| Extra SSH key | ~/.ssh/authorized_keys |
| New service / Run key | boot-start list |
| Web shell | new files in web folder |
Learn more in the lesson: 23.8 Persistence: How Attackers Keep Access