Ravi Sir's Cyber Security Cards › Revision Cards
Permissions: r, w, x, chmod and chown
Permissions: r, w, x, chmod and chown Each file has an owner (u), a group (g) and others (o). Each can have read (r) , write (w) and execute (x) permission. chmod changes permissions. chown changes the owner. Example: chmod 640 file = owner read/write, group read, others nothing. A SUID-root program
Read card text
What this card says
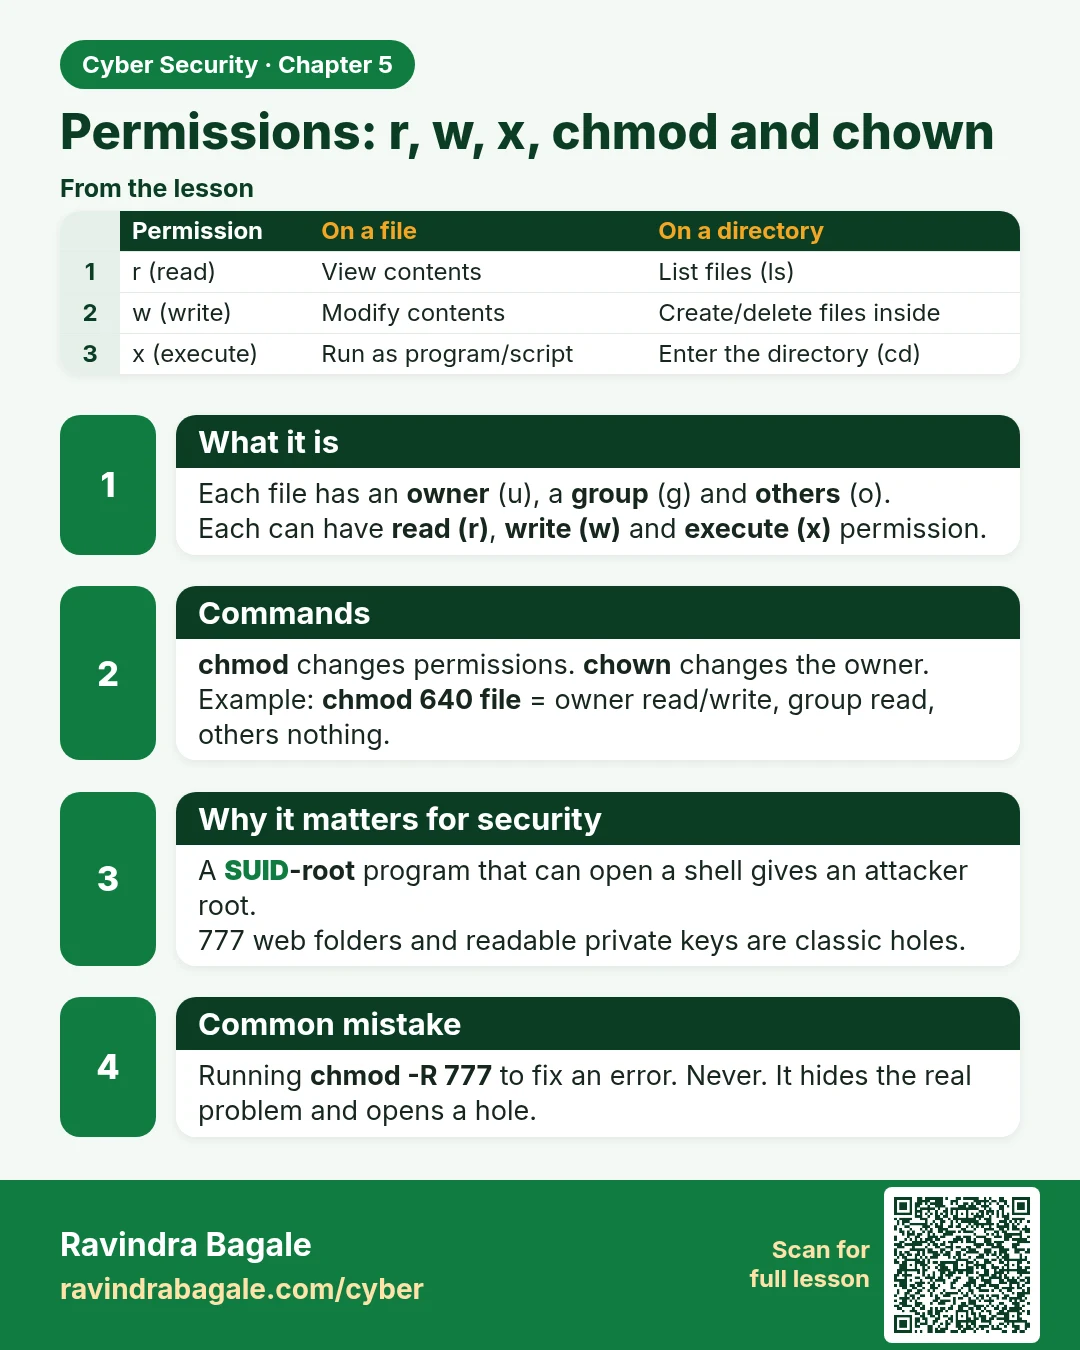
What it is
Each file has an owner (u), a group (g) and others (o).
Each can have read (r), write (w) and execute (x) permission.
Commands
chmod changes permissions. chown changes the owner.
Example: chmod 640 file = owner read/write, group read, others nothing.
Why it matters for security
A SUID-root program that can open a shell gives an attacker root.
777 web folders and readable private keys are classic holes.
Common mistake
Running chmod -R 777 to fix an error. Never. It hides the real problem and opens a hole.
| Permission | On a file | On a directory |
|---|---|---|
| r (read) | View contents | List files (ls) |
| w (write) | Modify contents | Create/delete files inside |
| x (execute) | Run as program/script | Enter the directory (cd) |
Learn more in the lesson: 5.5 Permissions: r, w, x, chmod and chown