Ravi Sir's Cyber Security Cards › Revision Cards
OWASP Top 10 – Fix What You Break (DVWA / Juice)
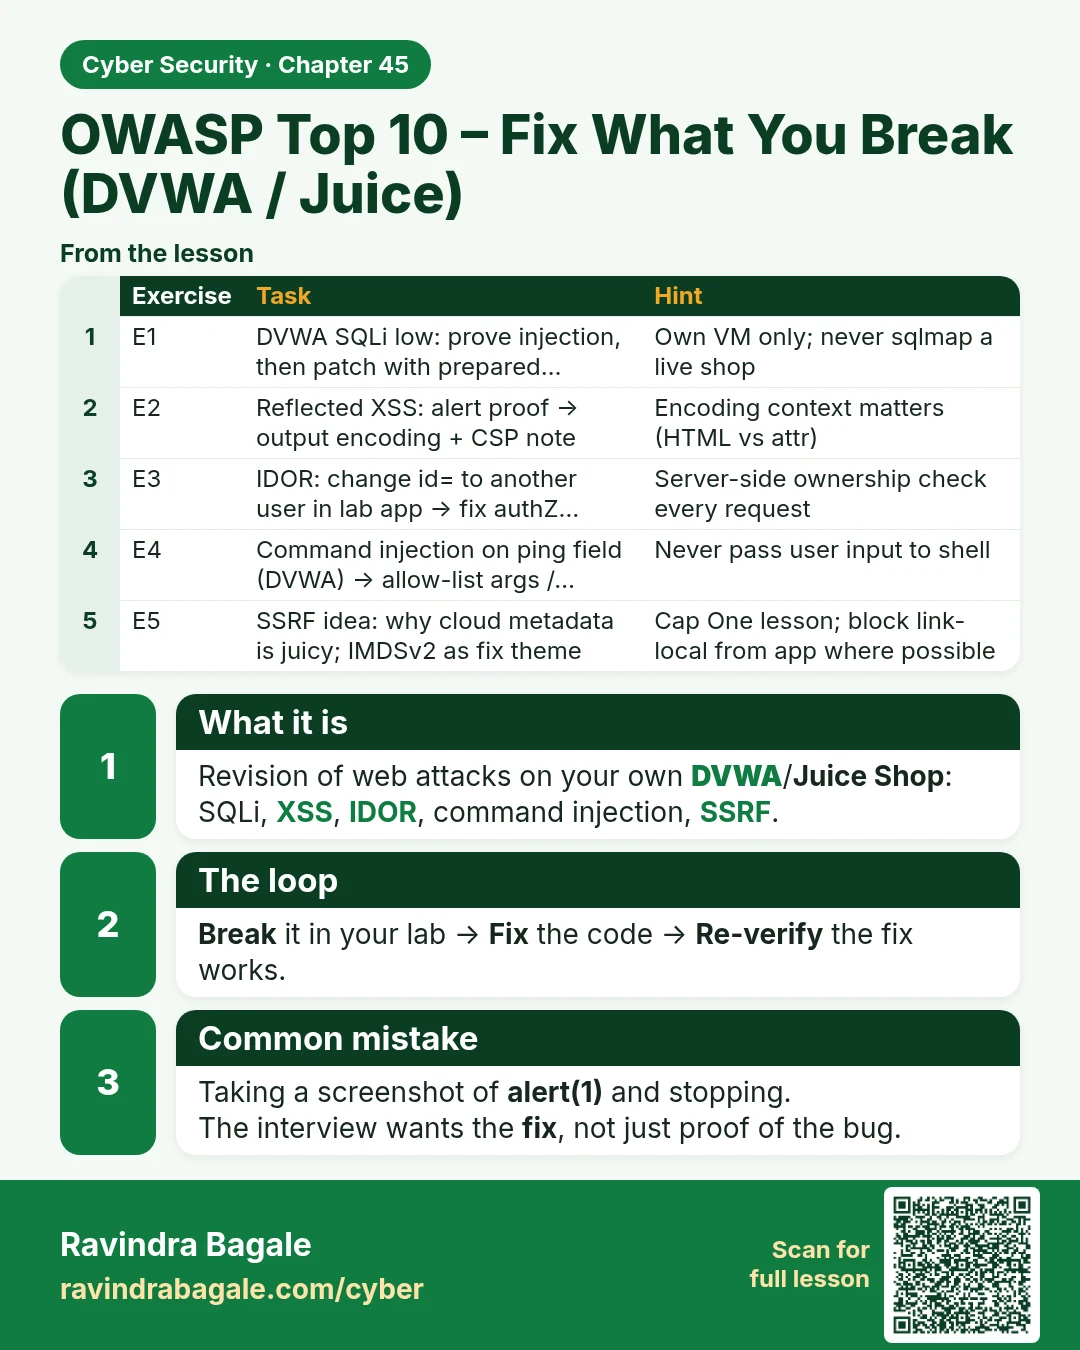
OWASP Top 10 – Fix What You Break (DVWA / Juice) Revision of web attacks on your own DVWA / Juice Shop : SQLi, XSS, IDOR, command injection, SSRF. Break it in your lab → Fix the code → Re-verify the fix works. Taking a screenshot of alert(1) and stopping. The interview wants the fix , not just proof
Read card text
What this card says
What it is
Revision of web attacks on your own DVWA/Juice Shop: SQLi, XSS, IDOR, command injection, SSRF.
The loop
Break it in your lab → Fix the code → Re-verify the fix works.
Common mistake
Taking a screenshot of alert(1) and stopping.
The interview wants the fix, not just proof of the bug.
| Exercise | Task | Hint |
|---|---|---|
| E1 | DVWA SQLi low: prove injection, then patch with prepared… | Own VM only; never sqlmap a live shop |
| E2 | Reflected XSS: alert proof → output encoding + CSP note | Encoding context matters (HTML vs attr) |
| E3 | IDOR: change id= to another user in lab app → fix authZ… | Server-side ownership check every request |
| E4 | Command injection on ping field (DVWA) → allow-list args /… | Never pass user input to shell |
| E5 | SSRF idea: why cloud metadata is juicy; IMDSv2 as fix theme | Cap One lesson; block link-local from app where possible |
Learn more in the lesson: 45.7 OWASP Top 10 – Fix What You Break (DVWA / Juice)