Ravi Sir's Cyber Security Cards › Revision Cards
NTLM Relay and Pass-the-Hash Concepts (Lab Only)
NTLM Relay and Pass-the-Hash Concepts (Lab Only) Two Windows attacks (concepts, lab only). Pass-the-Hash : reuse a stolen password hash to log in, without knowing the password. NTLM relay : capture a login and forward it to another service. Old NTLM authentication can be reused or relayed when signi
Read card text
What this card says
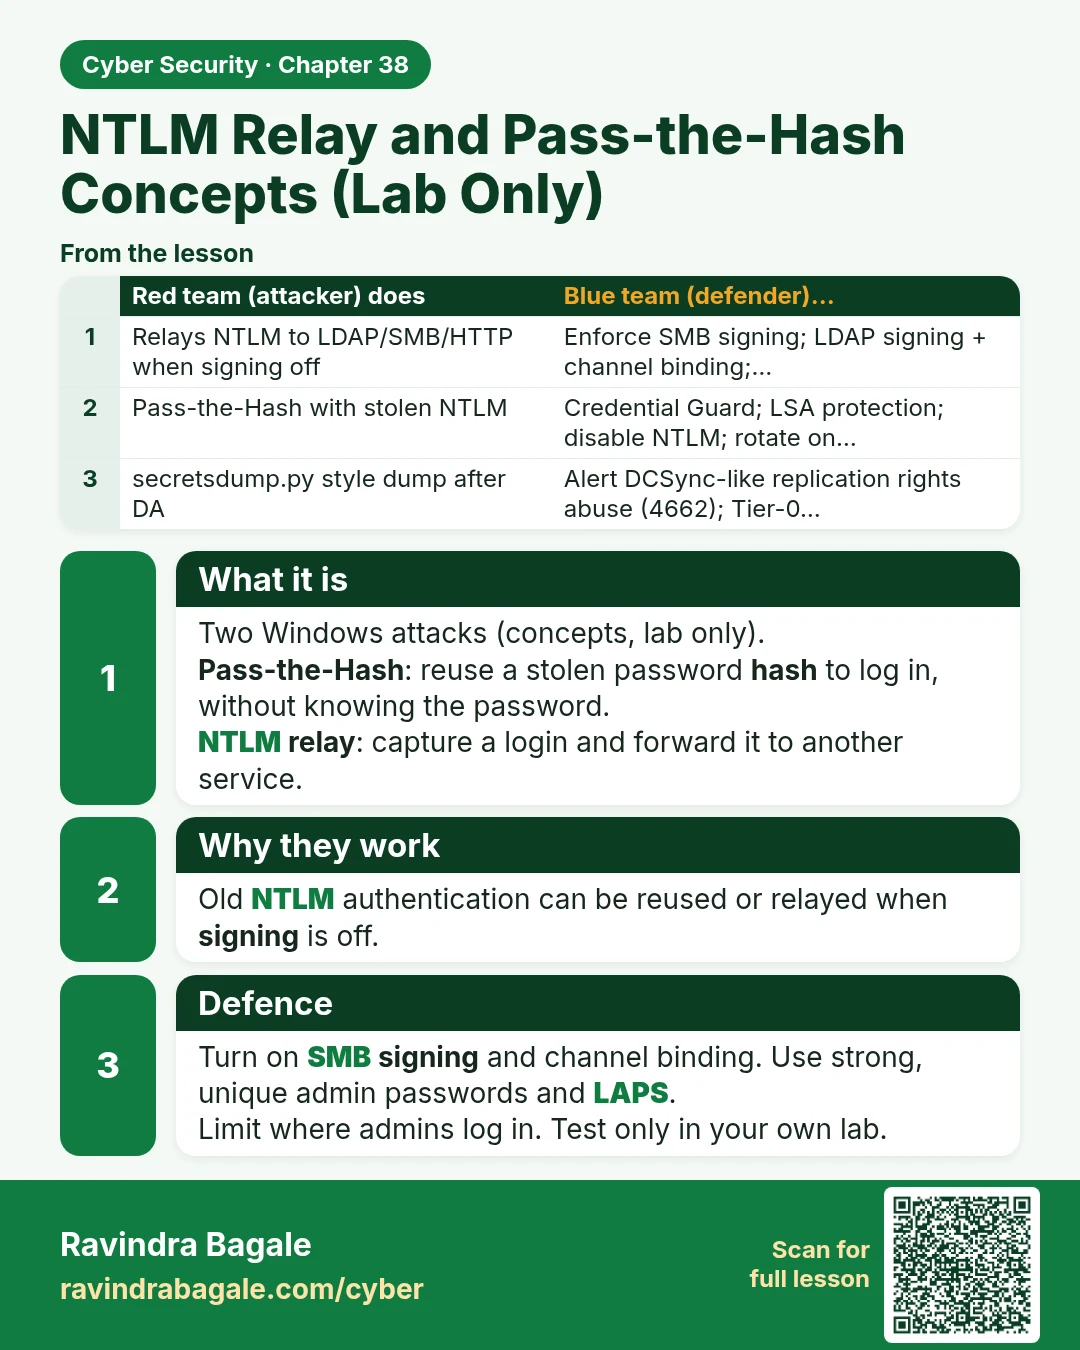
What it is
Two Windows attacks (concepts, lab only).
Pass-the-Hash: reuse a stolen password hash to log in, without knowing the password.
NTLM relay: capture a login and forward it to another service.
Why they work
Old NTLM authentication can be reused or relayed when signing is off.
Defence
Turn on SMB signing and channel binding. Use strong, unique admin passwords and LAPS.
Limit where admins log in. Test only in your own lab.
| Red team (attacker) does | Blue team (defender)… |
|---|---|
| Relays NTLM to LDAP/SMB/HTTP when signing off | Enforce SMB signing; LDAP signing + channel binding;… |
| Pass-the-Hash with stolen NTLM | Credential Guard; LSA protection; disable NTLM; rotate on… |
| secretsdump.py style dump after DA | Alert DCSync-like replication rights abuse (4662); Tier-0… |
Learn more in the lesson: 38.5 NTLM Relay and Pass-the-Hash Concepts (Lab Only)