Ravi Sir's Cyber Security Cards › Revision Cards
Nmap Cheat Sheet
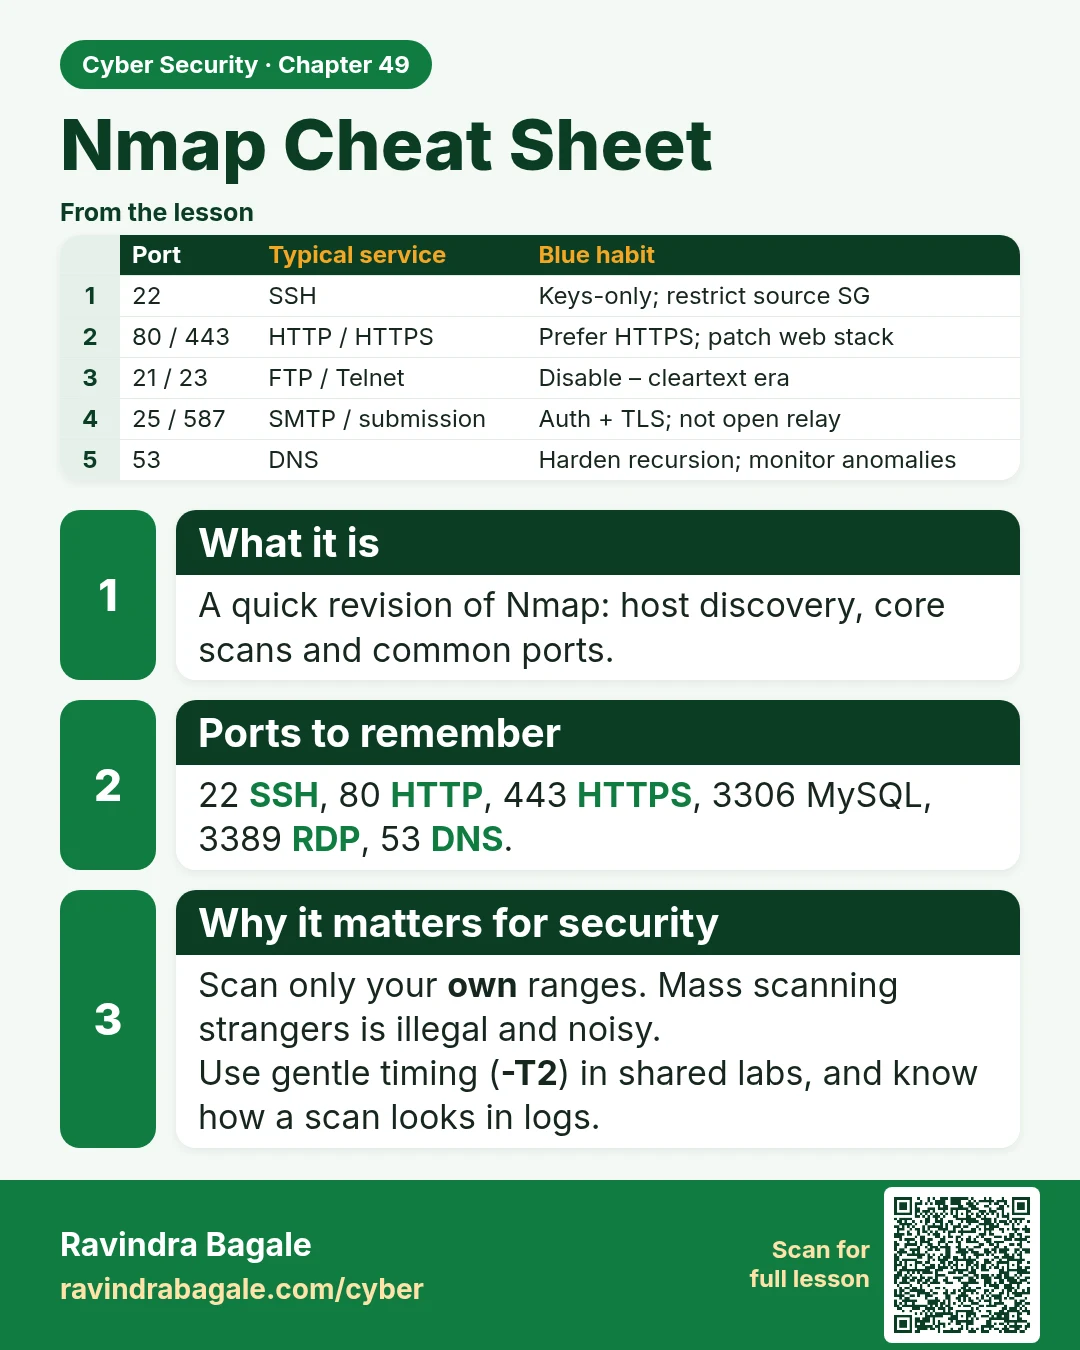
Nmap Cheat Sheet A quick revision of Nmap: host discovery, core scans and common ports. 22 SSH, 80 HTTP, 443 HTTPS, 3306 MySQL, 3389 RDP, 53 DNS. Scan only your own ranges. Mass scanning strangers is illegal and noisy. Use gentle timing ( -T2 ) in shared labs, and know how a scan looks in logs.
Read card text
What this card says
What it is
A quick revision of Nmap: host discovery, core scans and common ports.
Ports to remember
22 SSH, 80 HTTP, 443 HTTPS, 3306 MySQL, 3389 RDP, 53 DNS.
Why it matters for security
Scan only your own ranges. Mass scanning strangers is illegal and noisy.
Use gentle timing (-T2) in shared labs, and know how a scan looks in logs.
| Port | Typical service | Blue habit |
|---|---|---|
| 22 | SSH | Keys-only; restrict source SG |
| 80 / 443 | HTTP / HTTPS | Prefer HTTPS; patch web stack |
| 21 / 23 | FTP / Telnet | Disable – cleartext era |
| 25 / 587 | SMTP / submission | Auth + TLS; not open relay |
| 53 | DNS | Harden recursion; monitor anomalies |
Learn more in the lesson: 49.4 Nmap Cheat Sheet