Ravi Sir's Cyber Security Cards › Revision Cards
Network Sniffing of Sessions – Host-Only Concepts
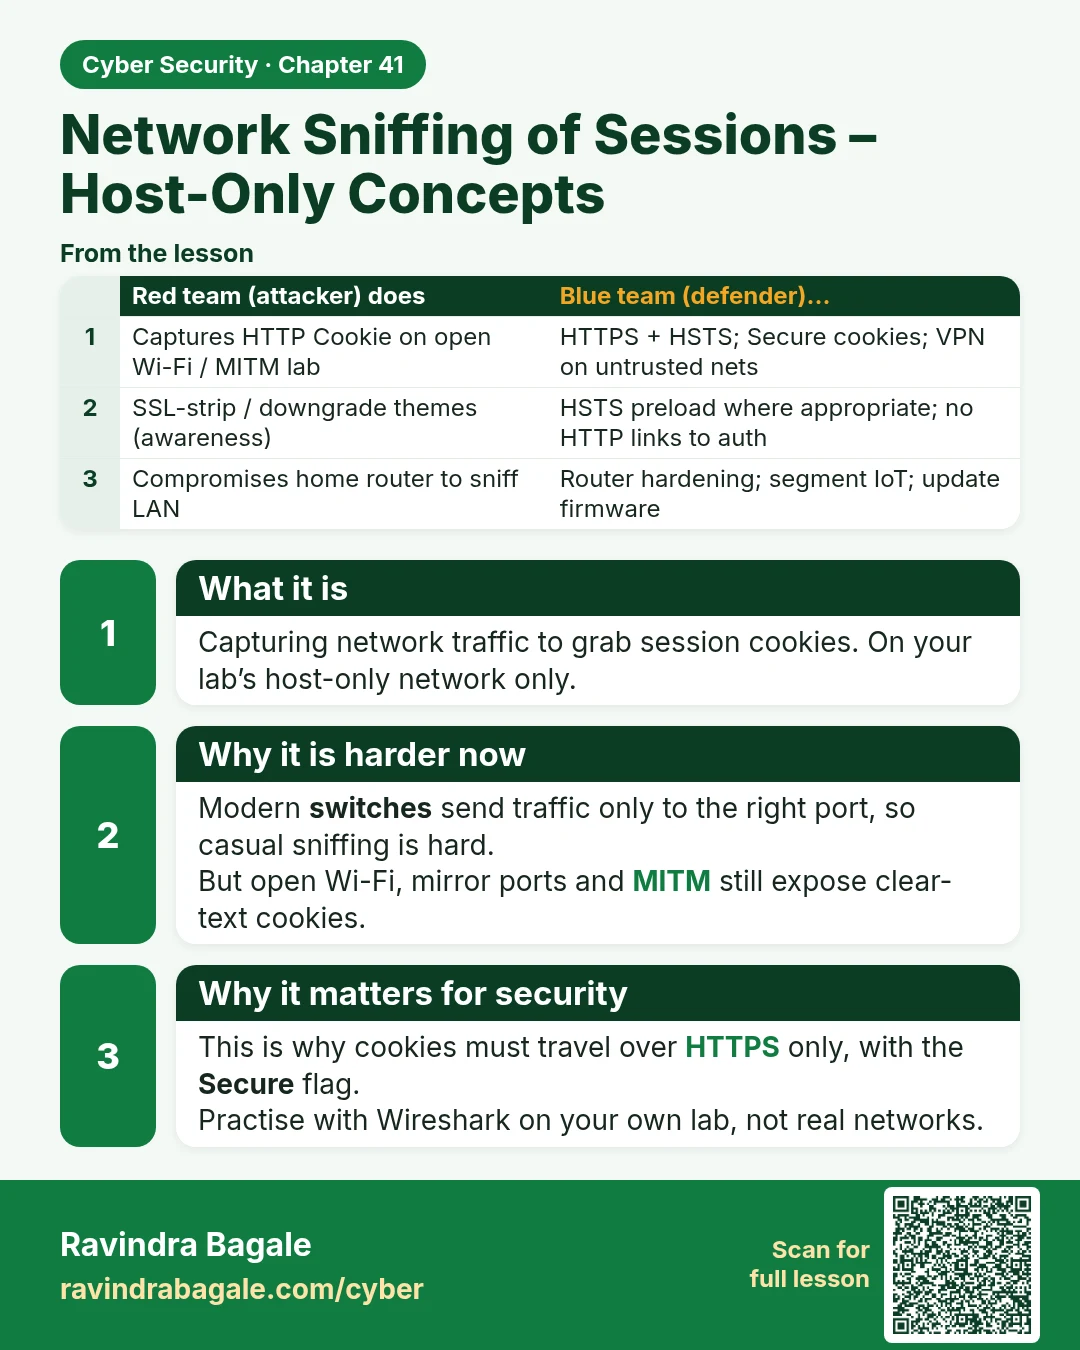
Network Sniffing of Sessions – Host-Only Concepts Capturing network traffic to grab session cookies. On your lab’s host-only network only. Modern switches send traffic only to the right port, so casual sniffing is hard. But open Wi-Fi, mirror ports and MITM still expose clear-text cookies. This is w
Read card text
What this card says
What it is
Capturing network traffic to grab session cookies. On your lab’s host-only network only.
Why it is harder now
Modern switches send traffic only to the right port, so casual sniffing is hard.
But open Wi-Fi, mirror ports and MITM still expose clear-text cookies.
Why it matters for security
This is why cookies must travel over HTTPS only, with the Secure flag.
Practise with Wireshark on your own lab, not real networks.
| Red team (attacker) does | Blue team (defender)… |
|---|---|
| Captures HTTP Cookie on open Wi-Fi / MITM lab | HTTPS + HSTS; Secure cookies; VPN on untrusted nets |
| SSL-strip / downgrade themes (awareness) | HSTS preload where appropriate; no HTTP links to auth |
| Compromises home router to sniff LAN | Router hardening; segment IoT; update firmware |
Learn more in the lesson: 41.5 Network Sniffing of Sessions – Host-Only Concepts