Ravi Sir's Cyber Security Cards › Revision Cards
Network Security in AWS
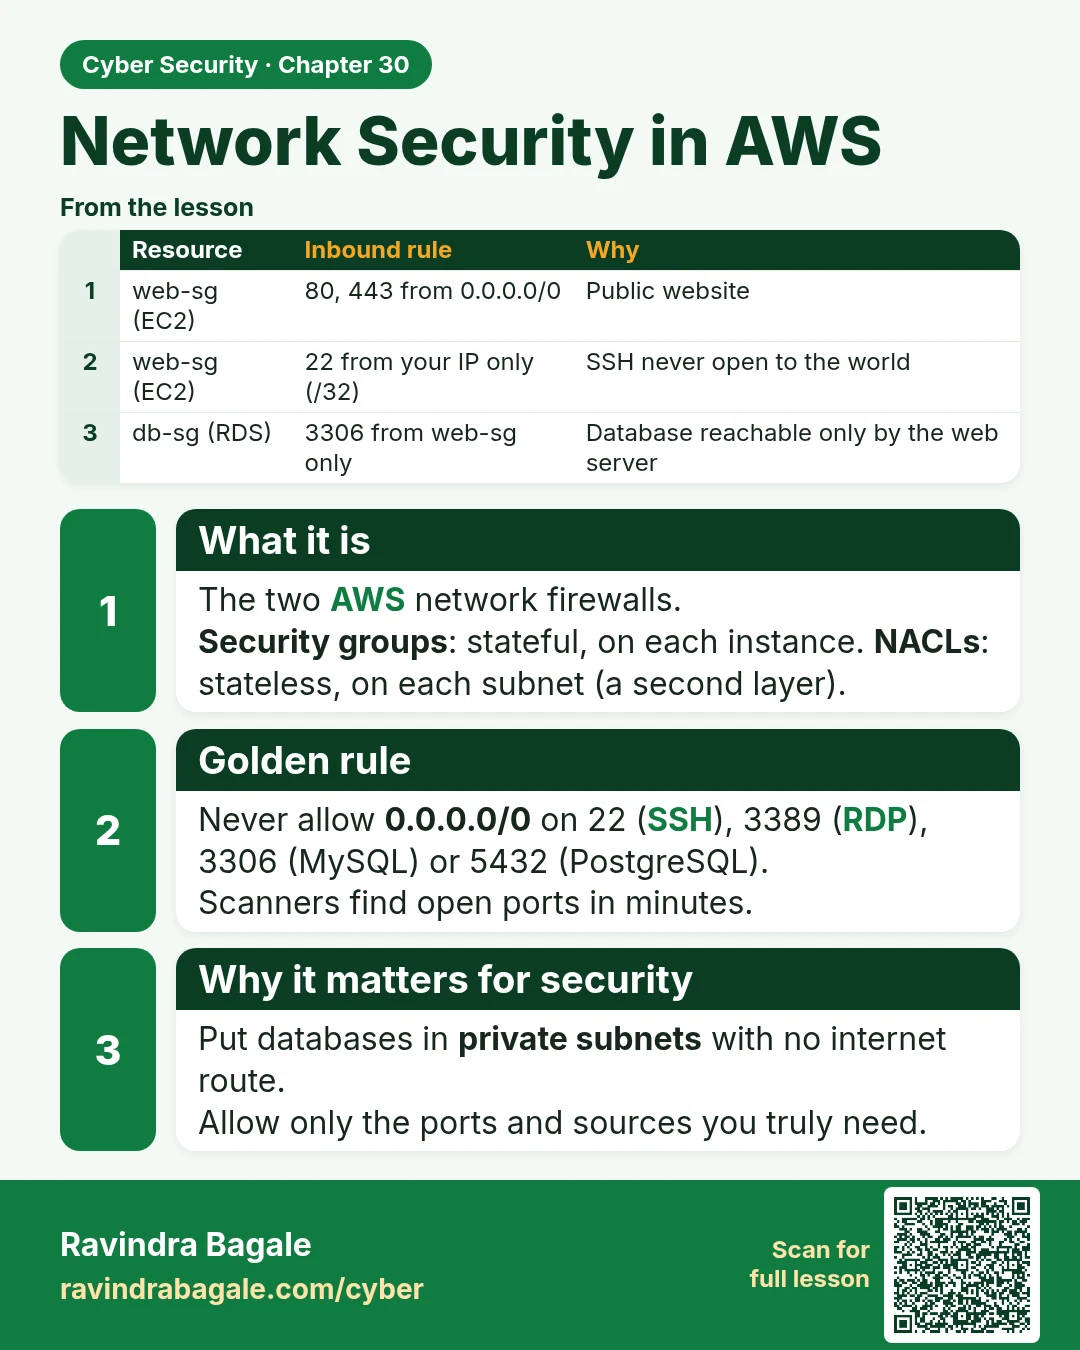
Network Security in AWS The two AWS network firewalls. Security groups : stateful, on each instance. NACLs : stateless, on each subnet (a second layer). Never allow 0.0.0.0/0 on 22 (SSH), 3389 (RDP), 3306 (MySQL) or 5432 (PostgreSQL). Scanners find open ports in minutes. Put databases in private sub
Read card text
What this card says
What it is
The two AWS network firewalls.
Security groups: stateful, on each instance. NACLs: stateless, on each subnet (a second layer).
Golden rule
Never allow 0.0.0.0/0 on 22 (SSH), 3389 (RDP), 3306 (MySQL) or 5432 (PostgreSQL).
Scanners find open ports in minutes.
Why it matters for security
Put databases in private subnets with no internet route.
Allow only the ports and sources you truly need.
| Resource | Inbound rule | Why |
|---|---|---|
| web-sg (EC2) | 80, 443 from 0.0.0.0/0 | Public website |
| web-sg (EC2) | 22 from your IP only (/32) | SSH never open to the world |
| db-sg (RDS) | 3306 from web-sg only | Database reachable only by the web server |
Learn more in the lesson: 30.3 Network Security in AWS