Ravi Sir's Cyber Security Cards › Revision Cards
Modules 16–20 Map (Wireless through Cryptography)
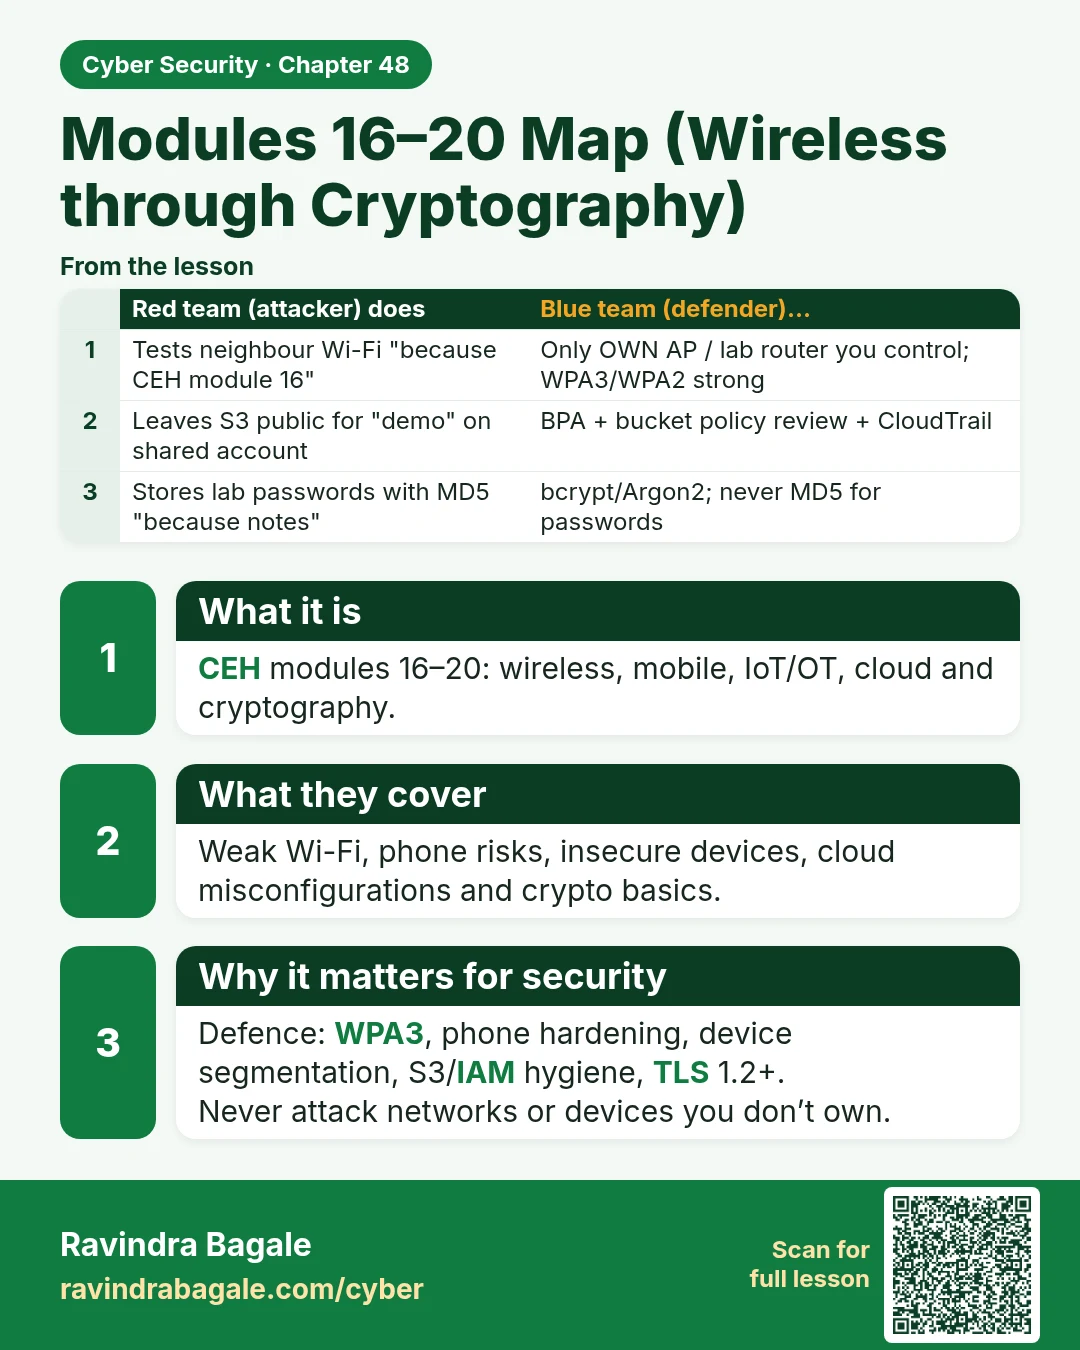
Modules 16–20 Map (Wireless through Cryptography) CEH modules 16–20: wireless, mobile, IoT/OT, cloud and cryptography. Weak Wi-Fi, phone risks, insecure devices, cloud misconfigurations and crypto basics. Defence: WPA3, phone hardening, device segmentation, S3/IAM hygiene, TLS 1.2+. Never attack net
Read card text
What this card says
What it is
CEH modules 16–20: wireless, mobile, IoT/OT, cloud and cryptography.
What they cover
Weak Wi-Fi, phone risks, insecure devices, cloud misconfigurations and crypto basics.
Why it matters for security
Defence: WPA3, phone hardening, device segmentation, S3/IAM hygiene, TLS 1.2+.
Never attack networks or devices you don’t own.
| Red team (attacker) does | Blue team (defender)… |
|---|---|
| Tests neighbour Wi-Fi "because CEH module 16" | Only OWN AP / lab router you control; WPA3/WPA2 strong |
| Leaves S3 public for "demo" on shared account | BPA + bucket policy review + CloudTrail |
| Stores lab passwords with MD5 "because notes" | bcrypt/Argon2; never MD5 for passwords |
Learn more in the lesson: 48.5 Modules 16–20 Map (Wireless through Cryptography)