Ravi Sir's Cyber Security Cards › Revision Cards
Modules 11–15 Map (Session Hijacking through SQL Injection)
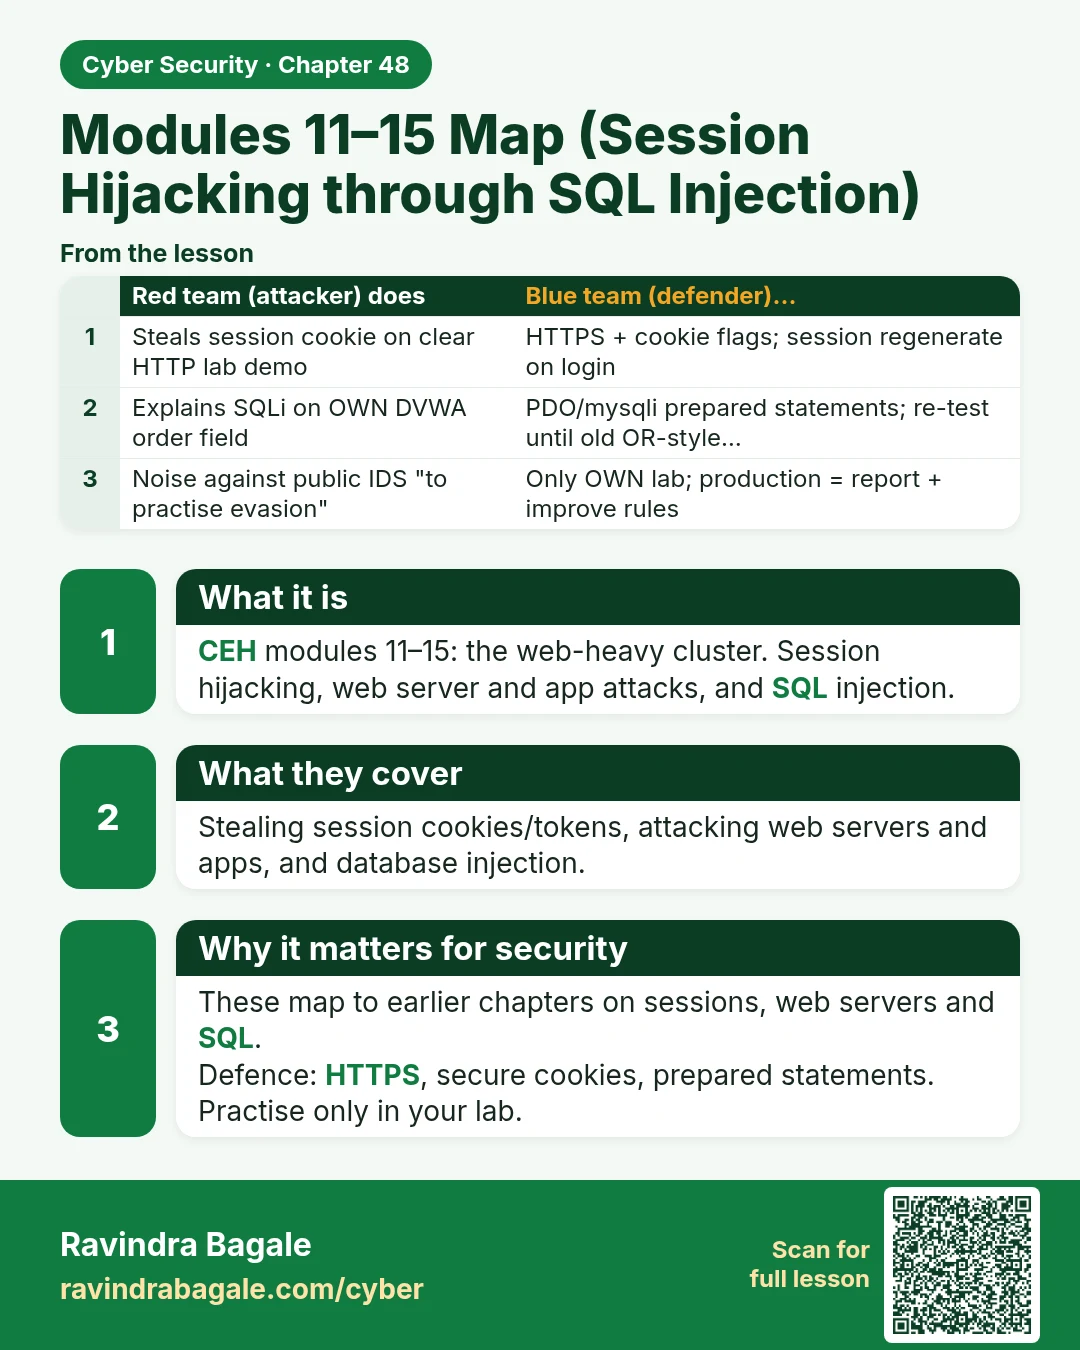
Modules 11–15 Map (Session Hijacking through SQL Injection) CEH modules 11–15: the web-heavy cluster. Session hijacking, web server and app attacks, and SQL injection. Stealing session cookies/tokens, attacking web servers and apps, and database injection. These map to earlier chapters on sessions,
Read card text
What this card says
What it is
CEH modules 11–15: the web-heavy cluster. Session hijacking, web server and app attacks, and SQL injection.
What they cover
Stealing session cookies/tokens, attacking web servers and apps, and database injection.
Why it matters for security
These map to earlier chapters on sessions, web servers and SQL.
Defence: HTTPS, secure cookies, prepared statements. Practise only in your lab.
| Red team (attacker) does | Blue team (defender)… |
|---|---|
| Steals session cookie on clear HTTP lab demo | HTTPS + cookie flags; session regenerate on login |
| Explains SQLi on OWN DVWA order field | PDO/mysqli prepared statements; re-test until old OR-style… |
| Noise against public IDS "to practise evasion" | Only OWN lab; production = report + improve rules |
Learn more in the lesson: 48.4 Modules 11–15 Map (Session Hijacking through SQL Injection)