Ravi Sir's Cyber Security Cards › Revision Cards
MITRE ATT&CK
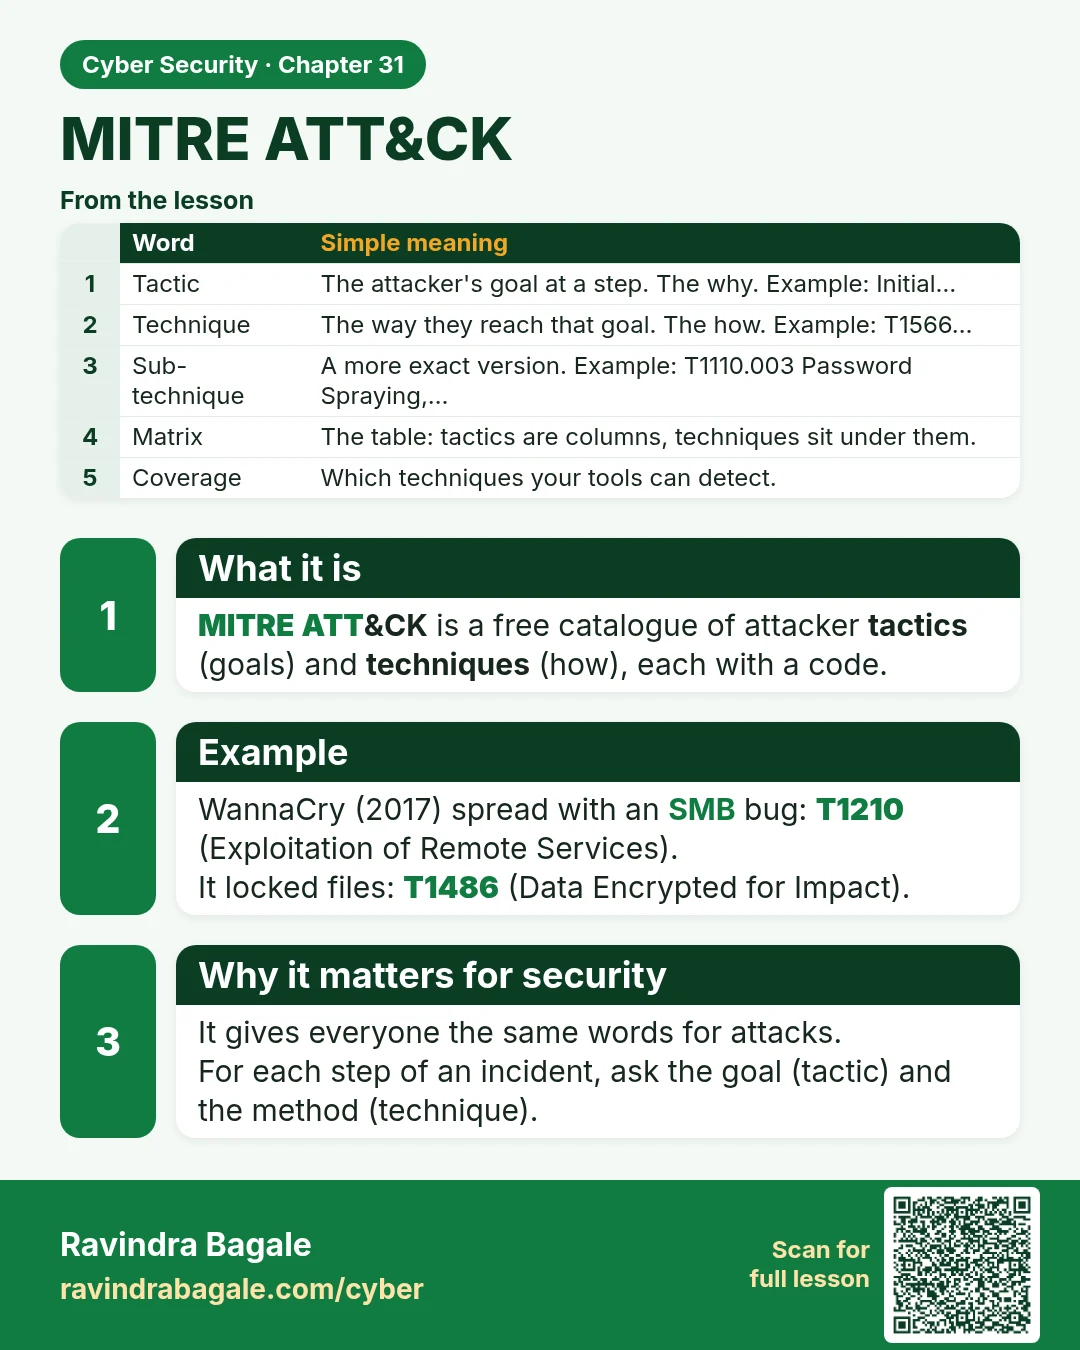
MITRE ATT&CK MITRE ATT&CK is a free catalogue of attacker tactics (goals) and techniques (how), each with a code. WannaCry (2017) spread with an SMB bug: T1210 (Exploitation of Remote Services). It locked files: T1486 (Data Encrypted for Impact). It gives everyone the same words for attacks. For eac
Read card text
What this card says
What it is
MITRE ATT&CK is a free catalogue of attacker tactics (goals) and techniques (how), each with a code.
Example
WannaCry (2017) spread with an SMB bug: T1210 (Exploitation of Remote Services).
It locked files: T1486 (Data Encrypted for Impact).
Why it matters for security
It gives everyone the same words for attacks.
For each step of an incident, ask the goal (tactic) and the method (technique).
| Word | Simple meaning |
|---|---|
| Tactic | The attacker's goal at a step. The why. Example: Initial… |
| Technique | The way they reach that goal. The how. Example: T1566… |
| Sub-technique | A more exact version. Example: T1110.003 Password Spraying,… |
| Matrix | The table: tactics are columns, techniques sit under them. |
| Coverage | Which techniques your tools can detect. |
Learn more in the lesson: 31.9 MITRE ATT&CK