Ravi Sir's Cyber Security Cards › Revision Cards
Lab-Safe PHP Cookie Demo + Ethics / IT Act
Lab-Safe PHP Cookie Demo + Ethics / IT Act A safe way to study session cookies: a small PHP demo in your own lab. Log in to your own app, view your own cookie, then turn on Secure, HttpOnly and SameSite and see the difference. Banned: Firesheep-style attacks on strangers’ Wi-Fi, phishing coworkers f
Read card text
What this card says
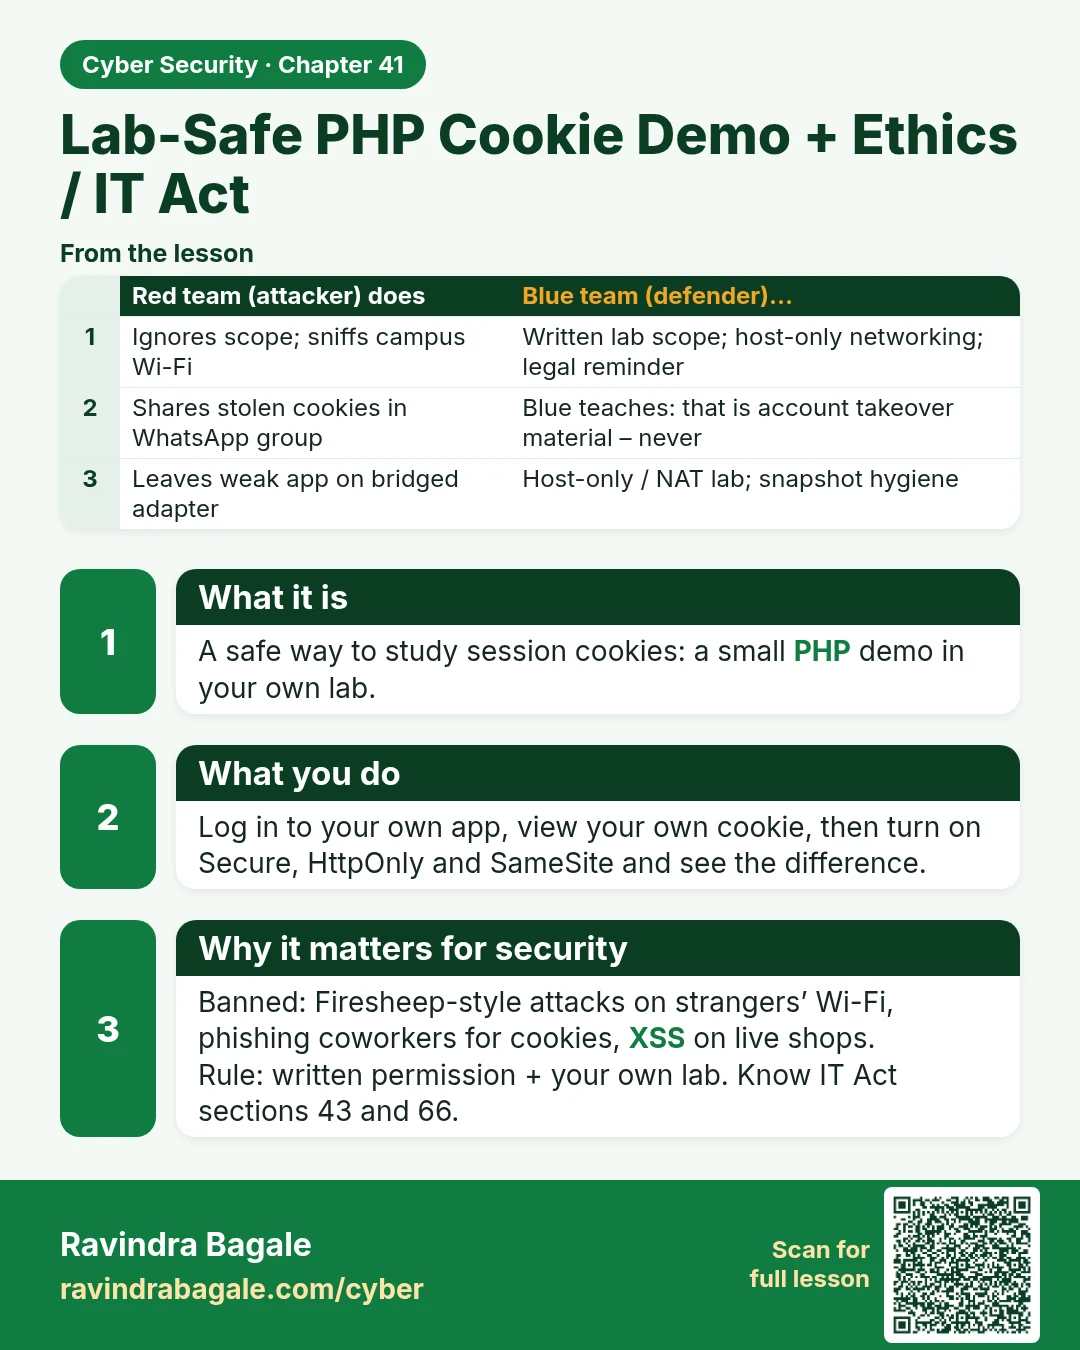
What it is
A safe way to study session cookies: a small PHP demo in your own lab.
What you do
Log in to your own app, view your own cookie, then turn on Secure, HttpOnly and SameSite and see the difference.
Why it matters for security
Banned: Firesheep-style attacks on strangers’ Wi-Fi, phishing coworkers for cookies, XSS on live shops.
Rule: written permission + your own lab. Know IT Act sections 43 and 66.
| Red team (attacker) does | Blue team (defender)… |
|---|---|
| Ignores scope; sniffs campus Wi-Fi | Written lab scope; host-only networking; legal reminder |
| Shares stolen cookies in WhatsApp group | Blue teaches: that is account takeover material – never |
| Leaves weak app on bridged adapter | Host-only / NAT lab; snapshot hygiene |
Learn more in the lesson: 41.9 Lab-Safe PHP Cookie Demo + Ethics / IT Act