Ravi Sir's Cyber Security Cards › Revision Cards
Lab – Mosquitto MQTT or Fake Camera UI on OWN VM
Lab – Mosquitto MQTT or Fake Camera UI on OWN VM A safe IoT lab on your own VM: an MQTT broker (Mosquitto) or a tiny fake “camera” web page. Start it with no password (lab), see the risk, then add a real password check and watch it block access. It shows why default-open devices are dangerous. Keep
Read card text
What this card says
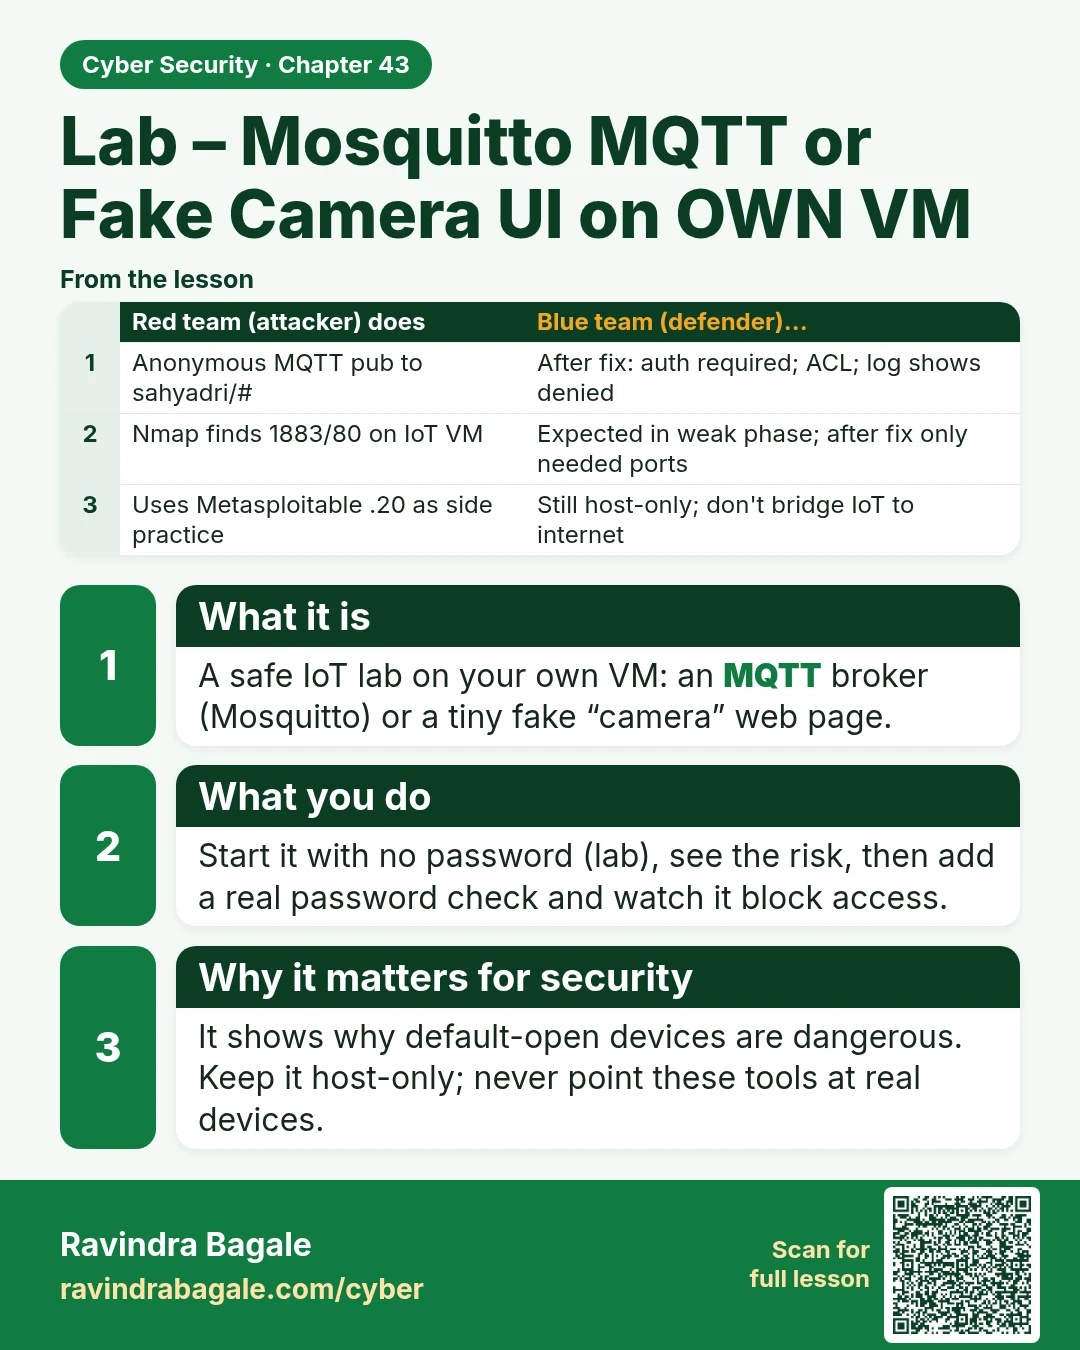
What it is
A safe IoT lab on your own VM: an MQTT broker (Mosquitto) or a tiny fake “camera” web page.
What you do
Start it with no password (lab), see the risk, then add a real password check and watch it block access.
Why it matters for security
It shows why default-open devices are dangerous.
Keep it host-only; never point these tools at real devices.
| Red team (attacker) does | Blue team (defender)… |
|---|---|
| Anonymous MQTT pub to sahyadri/# | After fix: auth required; ACL; log shows denied |
| Nmap finds 1883/80 on IoT VM | Expected in weak phase; after fix only needed ports |
| Uses Metasploitable .20 as side practice | Still host-only; don't bridge IoT to internet |
Learn more in the lesson: 43.9 Lab – Mosquitto MQTT or Fake Camera UI on OWN VM