Ravi Sir's Cyber Security Cards › Revision Cards
Kali Recon, Scan and Enum – Host-Only Only
Kali Recon, Scan and Enum – Host-Only Only Revision of recon with Kali: whois/dig, Nmap timing, and service enumeration. Host-only targets only. Use slow timing ( -T2 ) in shared labs. Save output with -oA . Never DoS a target. Recon is the first step both for attackers and defenders. Do it only on
Read card text
What this card says
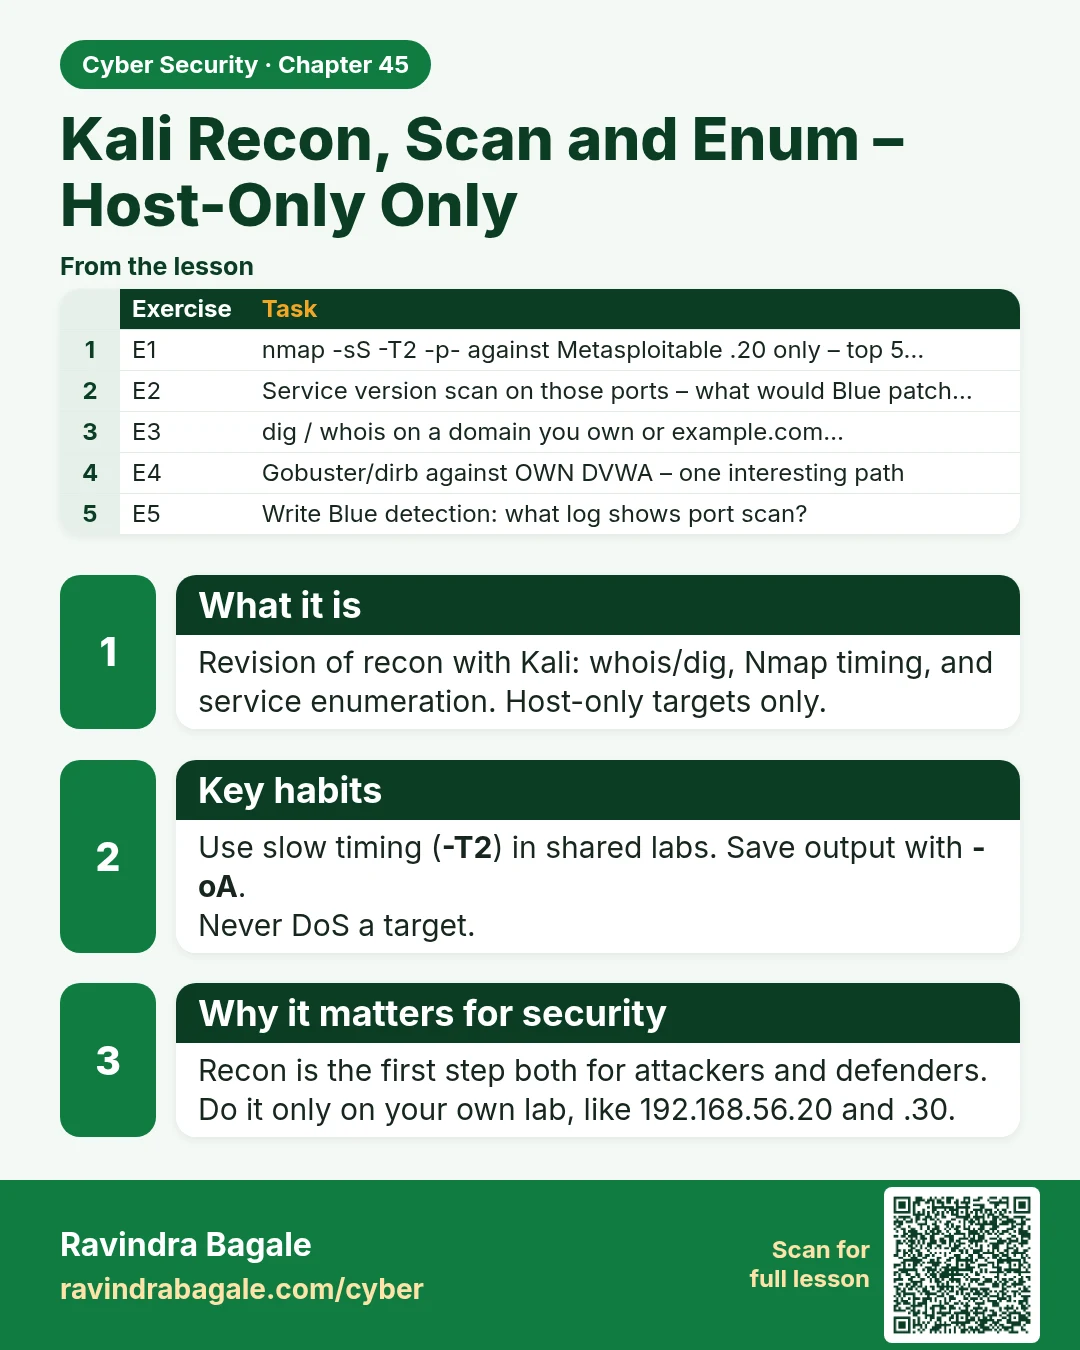
What it is
Revision of recon with Kali: whois/dig, Nmap timing, and service enumeration. Host-only targets only.
Key habits
Use slow timing (-T2) in shared labs. Save output with -oA.
Never DoS a target.
Why it matters for security
Recon is the first step both for attackers and defenders.
Do it only on your own lab, like 192.168.56.20 and .30.
| Exercise | Task |
|---|---|
| E1 | nmap -sS -T2 -p- against Metasploitable .20 only – top 5… |
| E2 | Service version scan on those ports – what would Blue patch… |
| E3 | dig / whois on a domain you own or example.com… |
| E4 | Gobuster/dirb against OWN DVWA – one interesting path |
| E5 | Write Blue detection: what log shows port scan? |
Learn more in the lesson: 45.6 Kali Recon, Scan and Enum – Host-Only Only