Ravi Sir's Cyber Security Cards › Revision Cards
Incident Response for Malware + CERT-In Awareness
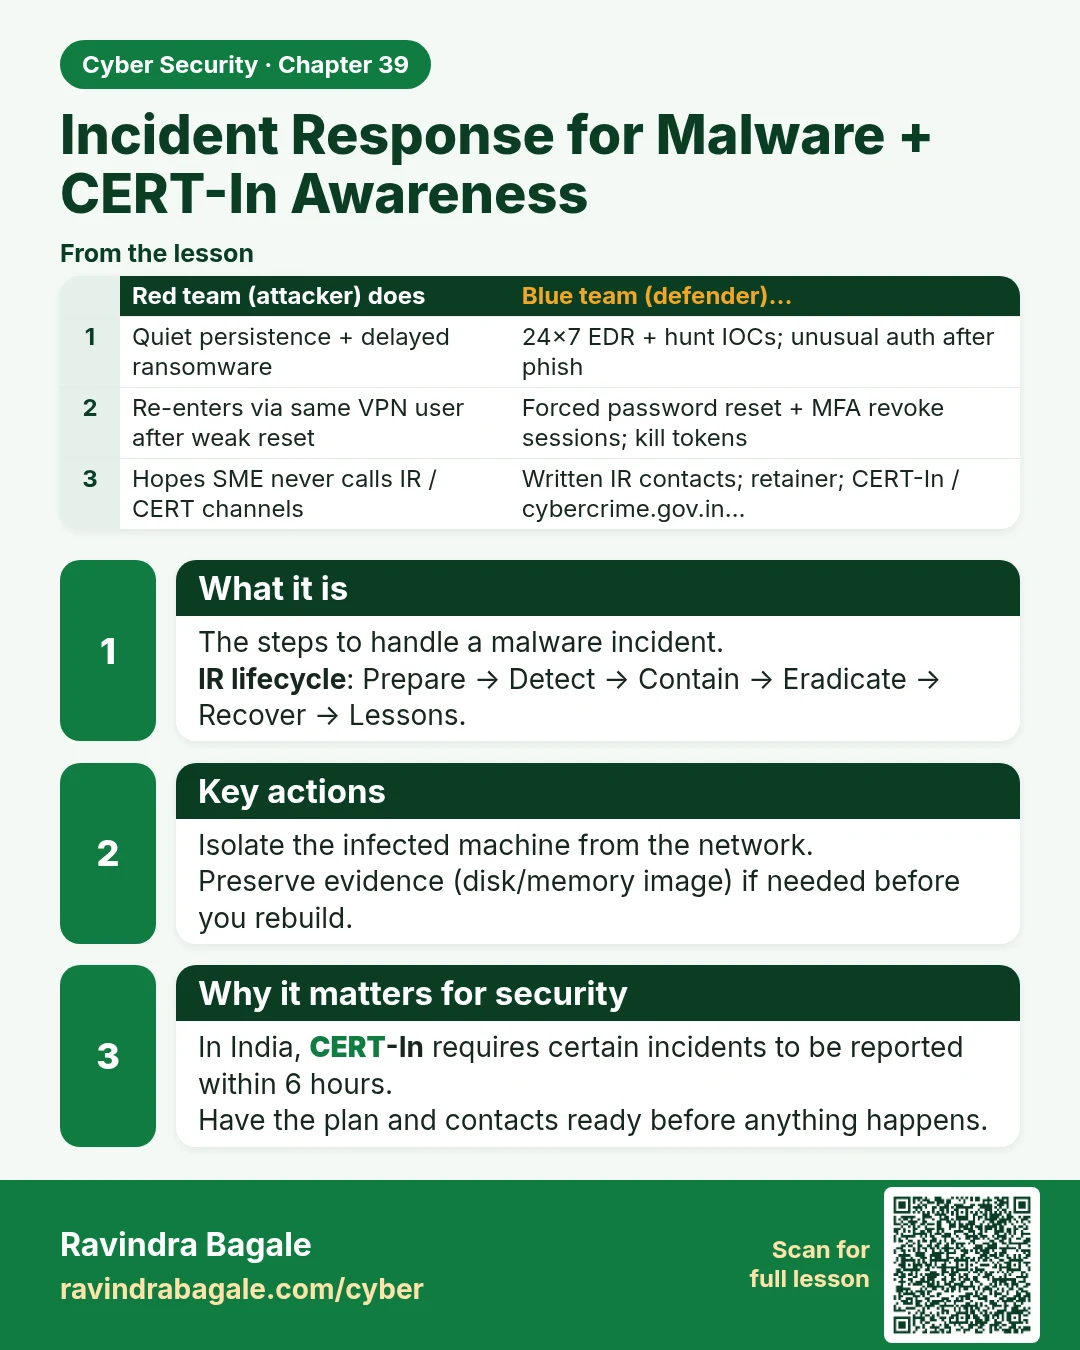
Incident Response for Malware + CERT-In Awareness The steps to handle a malware incident. IR lifecycle : Prepare → Detect → Contain → Eradicate → Recover → Lessons. Isolate the infected machine from the network. Preserve evidence (disk/memory image) if needed before you rebuild. In India, CERT-In re
Read card text
What this card says
What it is
The steps to handle a malware incident.
IR lifecycle: Prepare → Detect → Contain → Eradicate → Recover → Lessons.
Key actions
Isolate the infected machine from the network.
Preserve evidence (disk/memory image) if needed before you rebuild.
Why it matters for security
In India, CERT-In requires certain incidents to be reported within 6 hours.
Have the plan and contacts ready before anything happens.
| Red team (attacker) does | Blue team (defender)… |
|---|---|
| Quiet persistence + delayed ransomware | 24×7 EDR + hunt IOCs; unusual auth after phish |
| Re-enters via same VPN user after weak reset | Forced password reset + MFA revoke sessions; kill tokens |
| Hopes SME never calls IR / CERT channels | Written IR contacts; retainer; CERT-In / cybercrime.gov.in… |
Learn more in the lesson: 39.8 Incident Response for Malware + CERT-In Awareness