Ravi Sir's Cyber Security Cards › Revision Cards
Incident Response for Availability Attacks + CERT-In Awareness
Incident Response for Availability Attacks + CERT-In Awareness The steps to handle a DDoS. IR : Prepare → Detect → Mitigate → Communicate → Recover → Lessons. Confirm it is an attack, not a traffic spike or a broken deploy. Turn on scrubbing or CDN protection. Keep users informed. In India, CERT-In
Read card text
What this card says
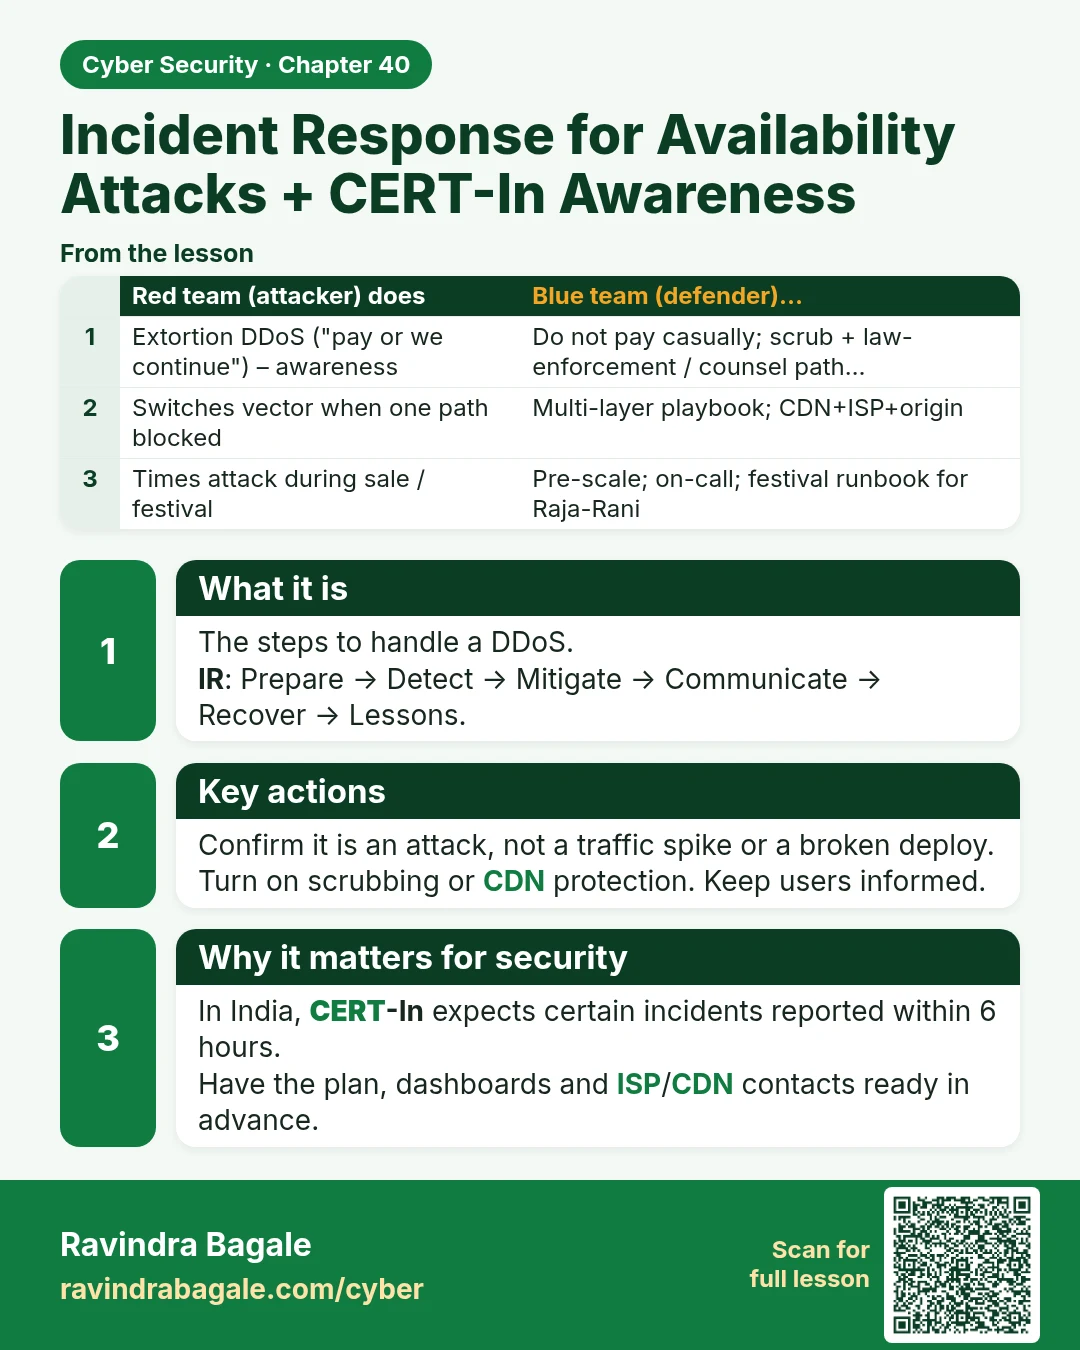
What it is
The steps to handle a DDoS.
IR: Prepare → Detect → Mitigate → Communicate → Recover → Lessons.
Key actions
Confirm it is an attack, not a traffic spike or a broken deploy.
Turn on scrubbing or CDN protection. Keep users informed.
Why it matters for security
In India, CERT-In expects certain incidents reported within 6 hours.
Have the plan, dashboards and ISP/CDN contacts ready in advance.
| Red team (attacker) does | Blue team (defender)… |
|---|---|
| Extortion DDoS ("pay or we continue") – awareness | Do not pay casually; scrub + law-enforcement / counsel path… |
| Switches vector when one path blocked | Multi-layer playbook; CDN+ISP+origin |
| Times attack during sale / festival | Pre-scale; on-call; festival runbook for Raja-Rani |
Learn more in the lesson: 40.9 Incident Response for Availability Attacks + CERT-In Awareness